AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
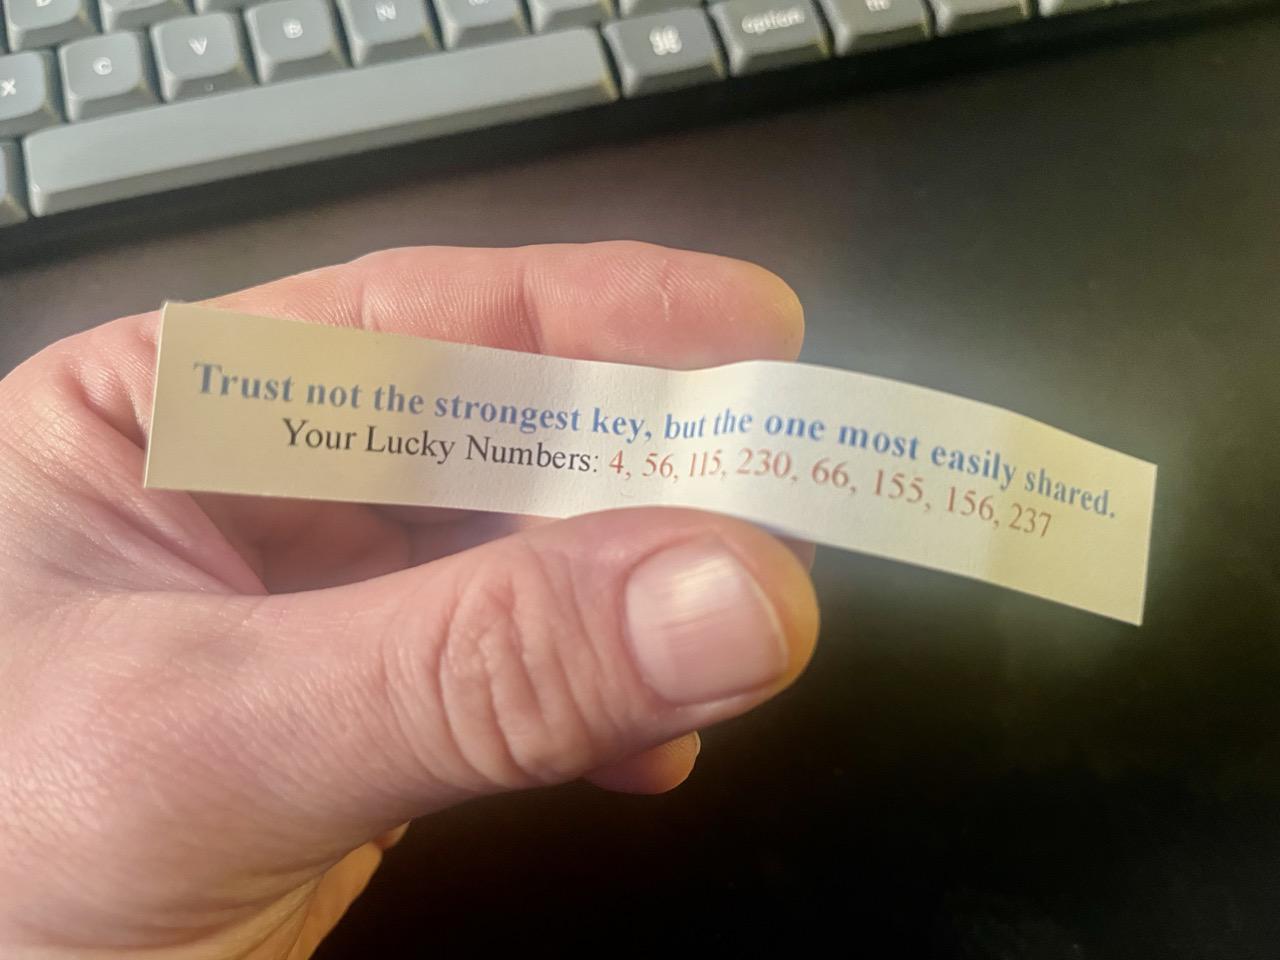
When even your fortune cookie is giving you cybersecurity advice that's simultaneously brilliant AND terrifying. "Trust not the strongest key, but the one most easily shared" is basically every security engineer's nightmare wrapped in a crispy shell. The fortune cookie just casually dropped the entire philosophy behind supply chain attacks – why break the strongest lock when you can just steal the key everyone's passing around like a joint at a DevOps conference?
The genius here is that attackers don't need to brute-force your AES-256 encryption when they can just compromise that one npm package with 50 million weekly downloads that everyone trusts blindly. Why hack the Pentagon when you can inject malicious code into a logging library that literally everyone uses? It's the SolarWinds incident but make it fortune cookie wisdom.
And those "lucky numbers"? Probably port numbers for your exposed Redis instance. Sweet dreams, developers! 🥠💀