Backend Memes

Backend development: where you do all the real work while the frontend devs argue about button colors for three days. These memes are for the unsung heroes working in the shadows, crafting APIs and database schemas that nobody appreciates until they break. We've all experienced those special moments – like when your microservices aren't so 'micro' anymore, or when that quick hotfix at 2 AM somehow keeps the whole system running for years. Backend devs are a different breed – we get excited about response times in milliseconds and dream in database schemas. If you've ever had to explain why that 'simple feature' requires rebuilding the entire architecture, these memes will feel like a warm, serverless hug.
Am I Late For This Meme

Am I Late For This Meme
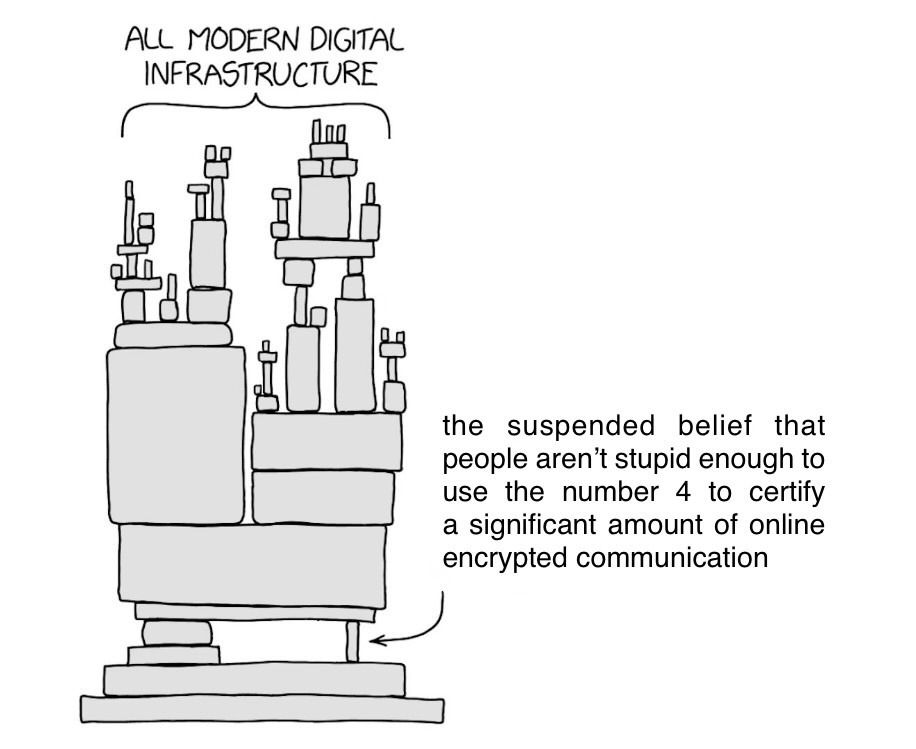
So apparently our entire digital civilization—cloud services, banking systems, streaming platforms, social media—is built on a rickety tower of legacy code held together by the collective delusion that RSA-4096 is uncrackable. The foundation? Just trusting that factoring really large numbers is hard enough that nobody will bother. It's like securing Fort Knox with a really complicated Sudoku puzzle and hoping nobody brings a quantum computer to the party. Sleep tight knowing your encrypted messages are protected by mathematicians playing the longest game of "I bet you can't solve this" in history.

Always Love A Good RCE Vuln

Always Love A Good RCE Vuln
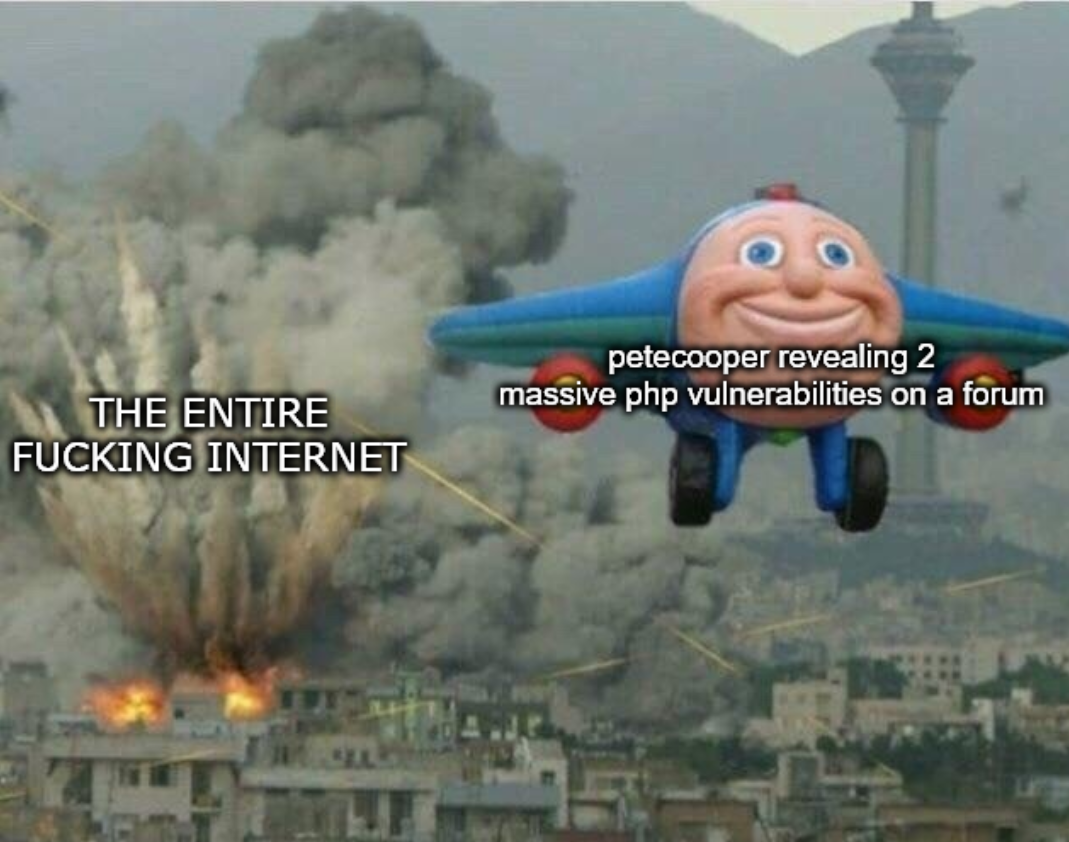
Nothing quite like watching some security researcher casually drop two massive PHP vulnerabilities on a random forum and watching the entire internet infrastructure collectively shit itself. RCE (Remote Code Execution) vulnerabilities are basically the nuclear option of security flaws—they let attackers run whatever code they want on your server. So yeah, when someone finds not one but TWO of these bad boys in PHP, which powers like 77% of the web, you get this beautiful chaos. The Thomas the Tank Engine meme format is *chef's kiss* here because it captures that childlike glee security researchers have when they discover catastrophic vulnerabilities. Meanwhile, every DevOps engineer and sysadmin is frantically patching servers at 3 AM on a Saturday. Fun times for everyone involved!

All Hail Ondřej!!

All Hail Ondřej!!
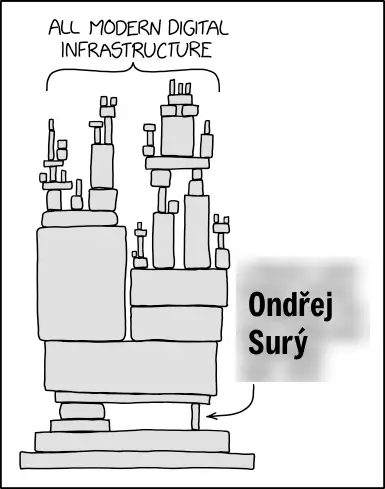
You know how the entire internet basically runs on a few unpaid maintainers? Yeah, Ondřej Surý is one of those legends. He maintains the unofficial PHP and Apache packages for Debian/Ubuntu that literally millions of servers depend on. Every time you `apt-get install php`, you're probably pulling from his repositories. The joke here is that all our fancy "modern digital infrastructure" - your streaming services, your banking apps, your food delivery - is essentially balanced precariously on the shoulders of this one dude who packages PHP updates in his spare time. It's the Atlas holding up the world situation, except Atlas is a Czech developer who probably doesn't get paid nearly enough for keeping half the web from collapsing. Fun fact: His repos at deb.sury.org have been the go-to for getting modern PHP versions on Ubuntu/Debian for over a decade. Without him, countless devs would still be stuck on PHP 5.6 waiting for official repos to catch up. The man deserves a statue.

Weird Design Philosophy

Weird Design Philosophy
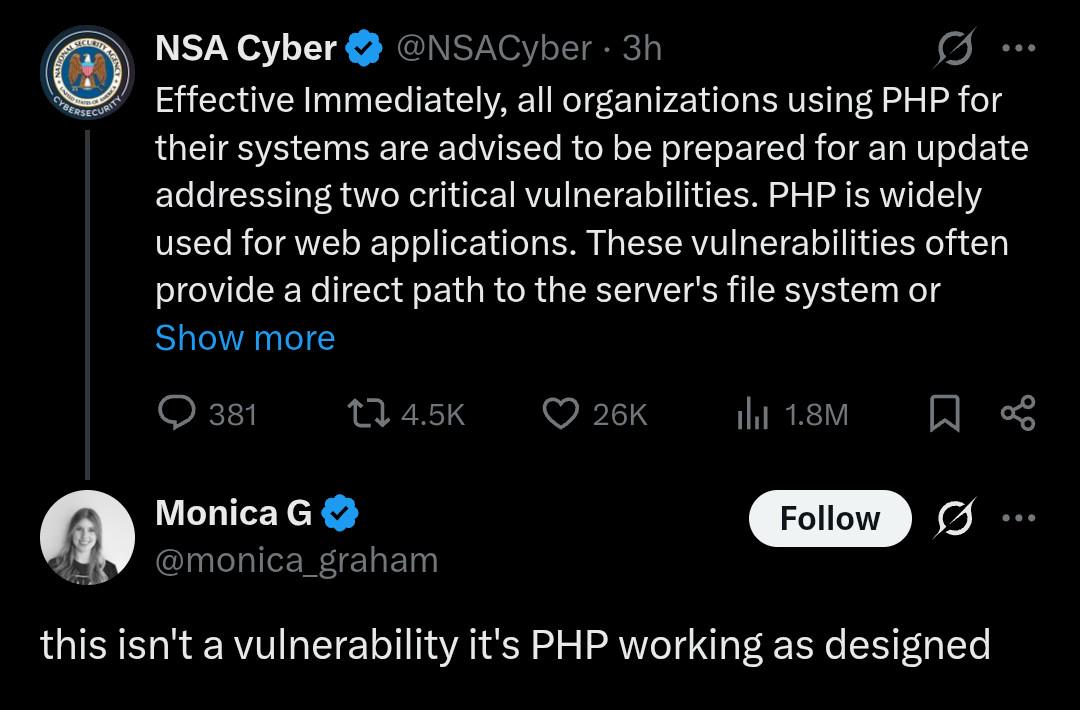
The NSA Cyber account posts a serious security advisory about critical PHP vulnerabilities that could expose file systems or enable remote code execution. Monica swoops in with the most devastating clapback in programming history: "this isn't a vulnerability it's PHP working as designed." The joke cuts deep because PHP has historically been notorious for having... let's call them "interesting" design decisions. Things like inconsistent function naming ( str_replace vs strpos ), needle-haystack parameter ordering that changes randomly, and type coercion that makes JavaScript look sane. So when security vulnerabilities pop up, developers joke that it's not a bug—it's just PHP being PHP. The language that gave us == comparing "0" and "potato" as equal because why not? The real burn here is that even government cybersecurity agencies can't escape the PHP roast. They're trying to protect national infrastructure while Monica's out here suggesting that PHP's vulnerabilities are just features nobody asked for.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

What A Week Huh

What A Week Huh
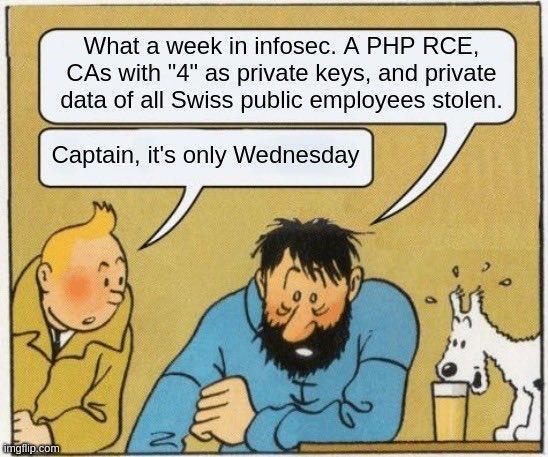
Someone's having a rough Wednesday in infosec land. A PHP RCE (Remote Code Execution - basically the "game over" of vulnerabilities), Certificate Authorities using "4" as their private keys (which is like locking your front door with a post-it note that says "locked"), and a massive data breach of Swiss public employees. All before hump day is over. The beauty here is the existential dread setting in. If Wednesday already brought this much chaos, what fresh hell awaits Thursday and Friday? It's like watching a slow-motion train wreck, except the train is on fire, the tracks are melting, and someone just realized they forgot to implement input validation. Every security engineer has lived through weeks like these where you question your career choices and wonder if it's too late to become a goat farmer instead.

Xkcd Said Its Random

Xkcd Said Its Random
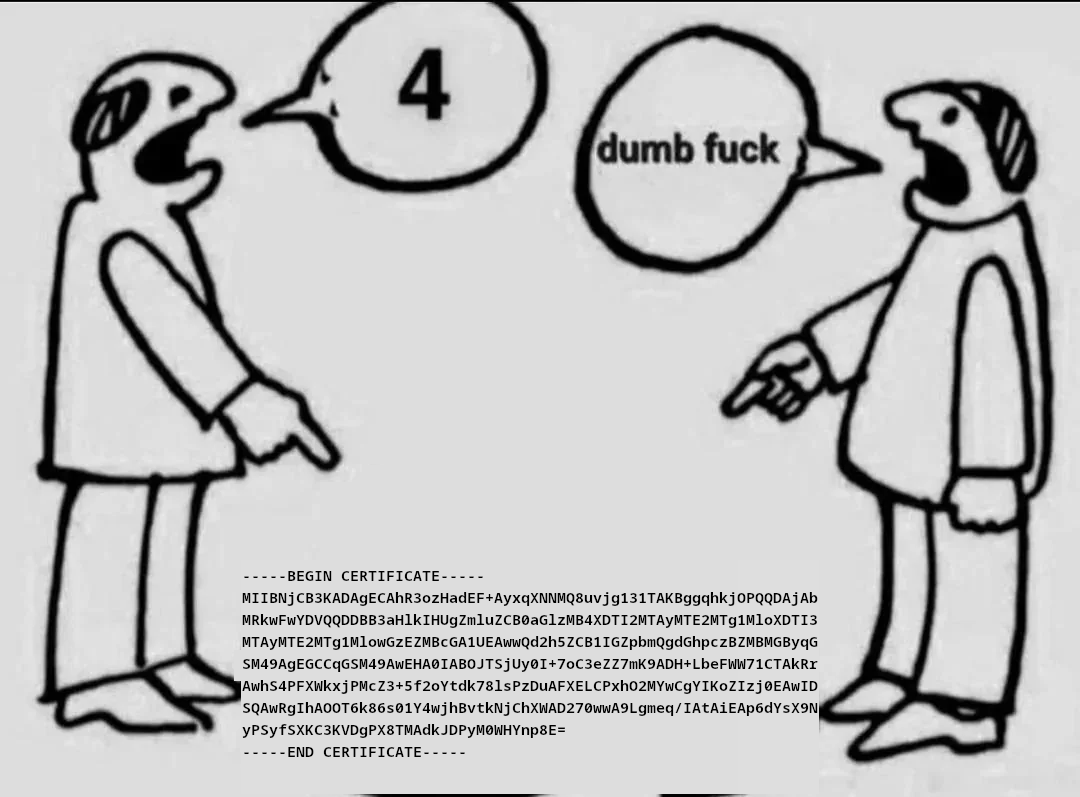
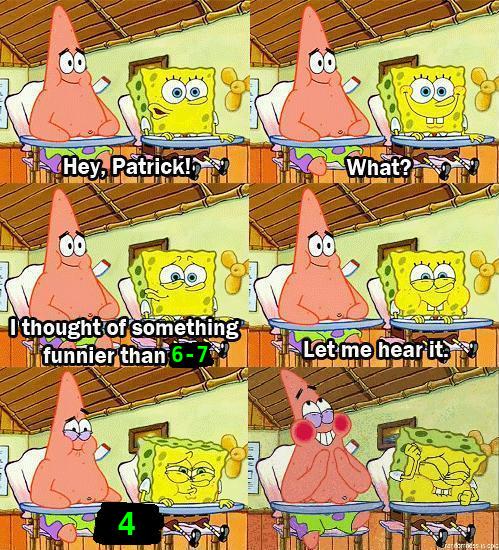
This references the legendary xkcd comic where someone implements a random number generator by just returning 4 because "I rolled a dice and got 4, so it's random." Fast forward to reality, and here's some poor soul actually using that logic to generate SSL certificates. The other person's response? "dumb fuck" - which is honestly the most restrained reaction possible when someone hardcodes entropy into cryptographic material. The beauty here is that certificates need actual randomness for security. Using the same "random" seed means every certificate would be identical, making your entire PKI infrastructure about as secure as a screen door on a submarine. But hey, xkcd said it was random, so ship it to production.

Chosen By A Fair Dice Roll

Chosen By A Fair Dice Roll
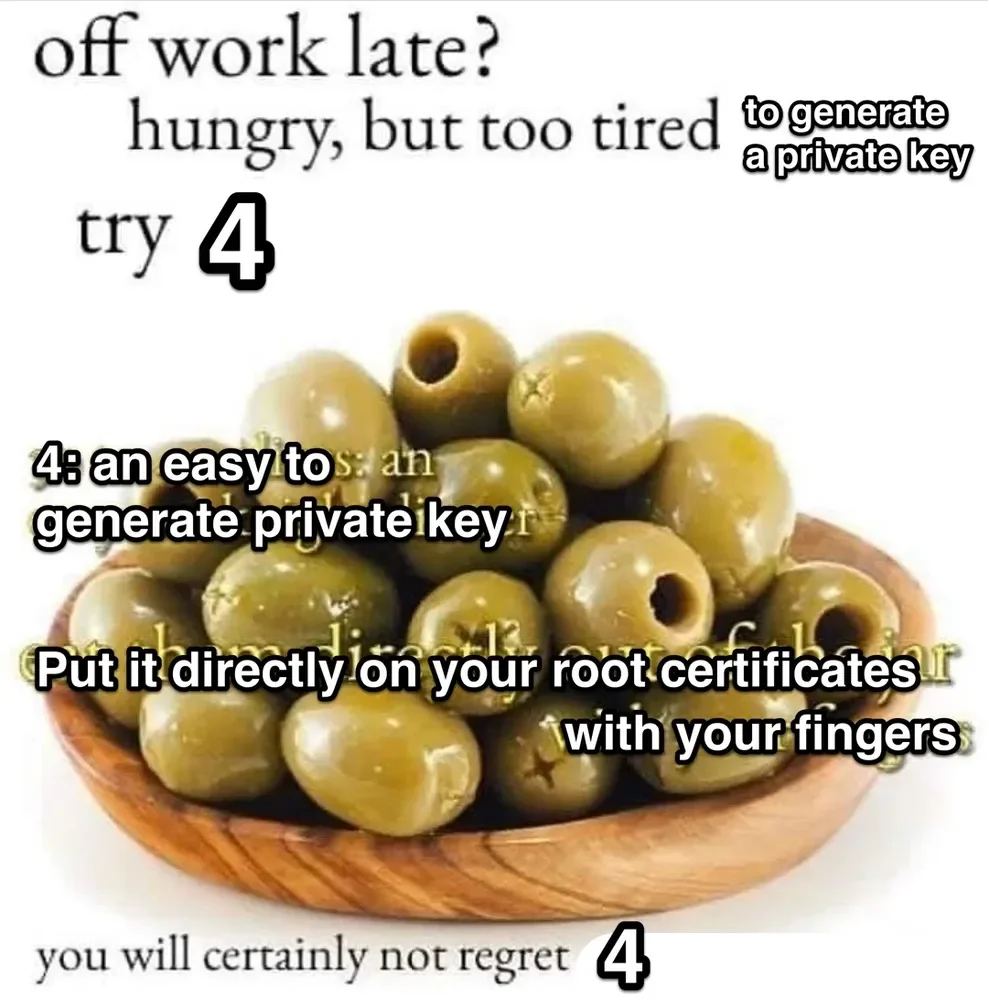
When you're so exhausted that rolling a dice to make decisions seems like peak productivity, and naturally you land on the WORST possible option for your cybersecurity. Nothing says "I've given up on life" quite like using a random number generator (your brain is too tired for that) to decide how to handle your cryptographic keys, and then proceeding to manually copy-paste your private key into your root certificates directory like you're spreading butter on toast. Because who needs security best practices when you've got VIBES and HUNGER? The beautiful irony? The number 4 supposedly being "an easy to generate private key" when generating secure keys requires actual randomness and complexity, not just... the number four. And then storing it by literally touching your root certs with your greasy fingers? Chef's kiss of catastrophic security failures. You will certainly not regret this until your entire infrastructure gets compromised at 3 AM and you're even MORE tired.

Legacy Supremacy

Legacy Supremacy
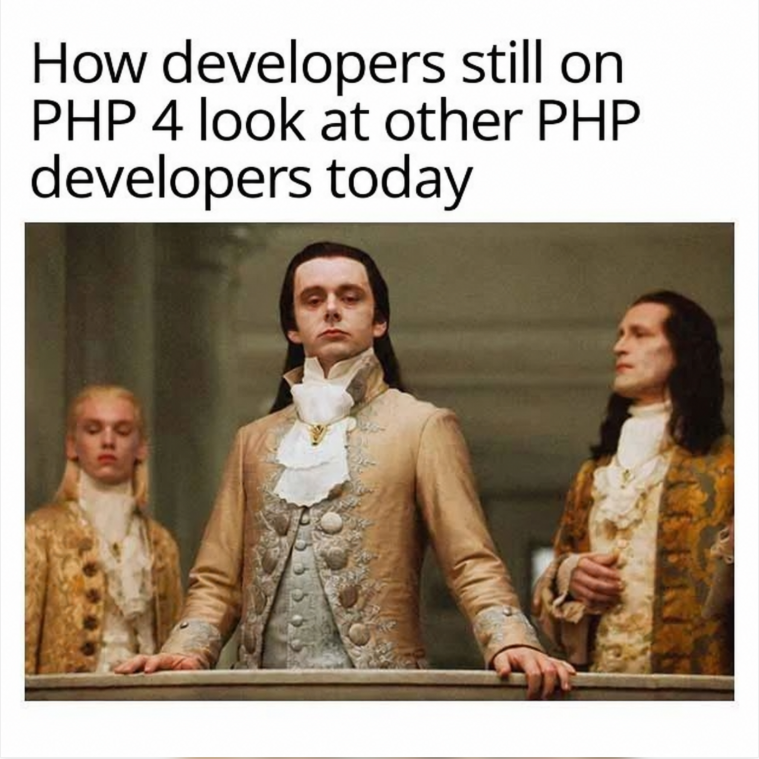
You know that feeling when you're maintaining a codebase from 2008 and you look at modern developers with their fancy PHP 8 features like enums and readonly properties? Yeah, that's the vibe here. These PHP 4 warriors are standing there in their aristocratic glory, looking down on the peasants with their namespaces and traits like they're beneath them. PHP 4 reached end-of-life in 2008—that's right, 2008 . We're talking pre-namespace era, no PDO prepared statements by default, register_globals still haunting production servers. These devs are basically coding royalty at this point, maintaining systems so old they remember when MySQL didn't have a "i" at the end. The real tragedy? They probably can't leave because they're the only ones who understand the arcane magic keeping that e-commerce site running. Job security through Stockholm syndrome.

Php Is In The News

Php Is In The News
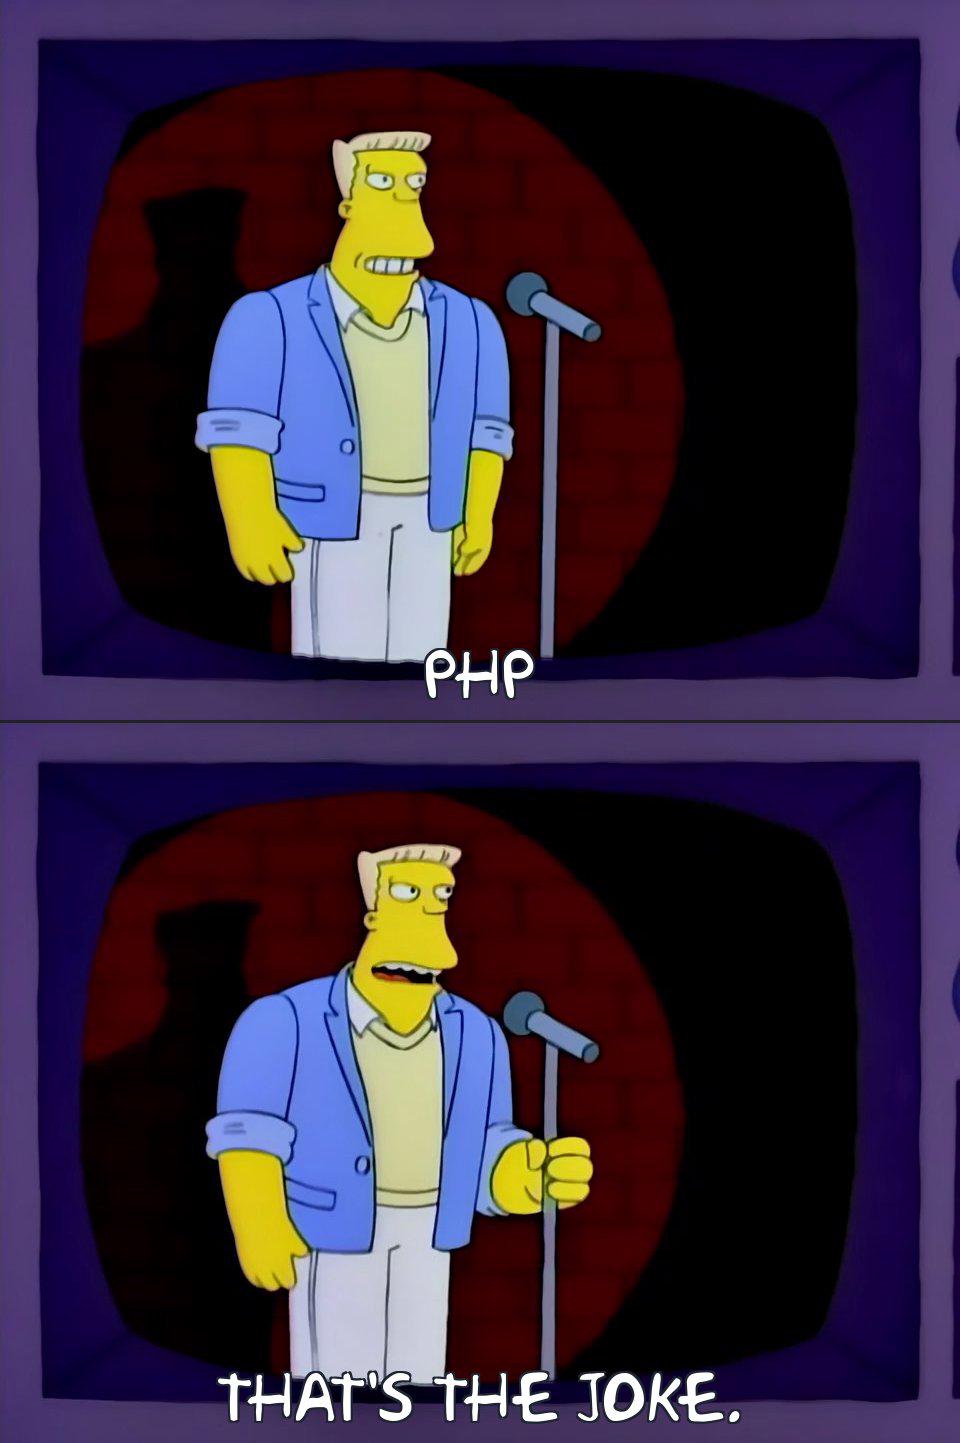
PHP making headlines? Groundbreaking. Revolutionary. Absolutely earth-shattering. Oh wait—PHP itself IS the punchline. The language has been roasted so mercilessly for decades that its mere existence in the news is comedy gold. No scandal needed, no new feature announcement required. Just mention PHP and watch the entire developer community collectively smirk. It's like announcing "Florida Man" without even describing what he did—you already know it's going to be ridiculous. Poor PHP can't catch a break, standing at that microphone thinking it's about to deliver some profound wisdom, completely unaware that it walked into its own roast session. The audacity of PHP to show up anywhere and expect to be taken seriously is honestly iconic at this point.

E Mudhra Certificate Authority Chose Random Numbers By Fair Dice Roll Guaranteed To Be Random

E Mudhra Certificate Authority Chose Random Numbers By Fair Dice Roll Guaranteed To Be Random
So apparently E Mudhra, a Certificate Authority that's supposed to be securing digital certificates and cryptographic operations, decided that "random number generation" means rolling a dice and getting... 4. Every. Single. Time. For those who need context: this is referencing the classic XKCD comic where someone hardcodes the number 4 as their "random" number because they rolled a dice once. The joke here is that a CA—literally an organization whose entire job depends on cryptographic security and proper randomness—might as well be using the same logic. Nothing screams "enterprise security" quite like deterministic randomness. I'm sure their SSL certificates are totally secure when the random number generator has the same entropy as a fortune cookie. But hey, at least it's guaranteed to be random, right? They rolled a dice! Once! In 2003! This is what happens when someone reads "cryptographically secure random number generator" and thinks "yeah, but have we tried just... picking a number?"

How Shitty Standards Stick Around

How Shitty Standards Stick Around
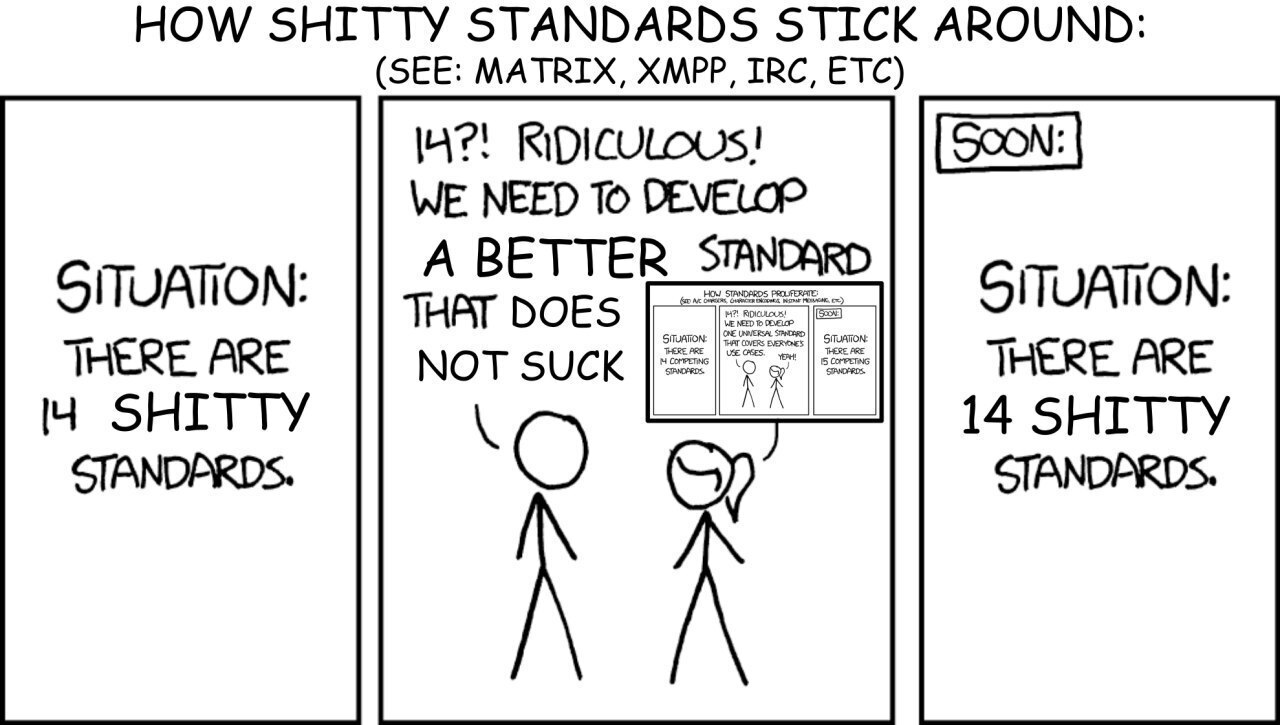
Every tech lead's nightmare captured in three panels. You've got 14 competing standards, someone gets the brilliant idea to unify them all, and boom—now you've got 15 standards to maintain. It's like trying to fix JavaScript by inventing TypeScript, or fixing build tools by creating yet another bundler. The examples listed (Matrix, XMPP, IRC) hit different. These are actual messaging protocols that were supposed to replace each other but instead just... coexist in eternal purgatory. IRC from the 90s? Still kicking. XMPP was gonna save us all? Nope, now we have Slack, Discord, Teams, and 47 other chat apps. The real kicker is that recursive comic within the comic—because even the solution to explaining this problem becomes part of the problem. Meta as hell, and painfully accurate.

V VCOM M.2 NVMe SSD Enclosure,USB C External Adapter, USB 3.2 Gen2 (10Gbps) with UASP, Trim Support - M-Key(B+M Key) for 2230/2242/2260/2280 SSDs

V VCOM M.2 NVMe SSD Enclosure,USB C External Adapter, USB 3.2 Gen2 (10Gbps) with UASP, Trim Support - M-Key(B+M Key) for 2230/2242/2260/2280 SSDs
【ONLY SUITABLE FOR PCIe NVMe M.2 SSD】The nvme enclosure ONLY supports NVMe SSD (M Key/B+M Key) . Applicable with SSD in sizes 2230/2242/2260/2280, compatible with Crucial WD Kingston Integral, etc. N…

Presented By The Number 4

Presented By The Number 4
Ah yes, the number that haunts every web developer's dreams. You know you've made it as a developer when you can instantly recognize the entire 4xx family tree: 400 Bad Request (your fault), 401 Unauthorized (forgot the token again), 403 Forbidden (nice try hacker), 404 Not Found (the celebrity of error codes), and the dreaded 418 I'm a Teapot (because why not). The number 4 is basically the harbinger of "something went wrong on the client side" – which in production usually means it's time to check if the frontend dev remembered to actually send the auth headers, or if the user is doing something creative like trying to access /admin with their regular account. Fun fact: HTTP status codes in the 400s mean client errors, while 500s mean server errors. So when you see a 4, you get to blame someone else. When you see a 5, that's all you, buddy.