Security Memes

Cybersecurity: where paranoia is a professional requirement and "have you tried turning it off and on again" is rarely the solution. These memes are for the defenders who stay awake so others can sleep, dealing with users who think "Password123!" is secure and executives who want military-grade security on a convenience store budget. From the existential dread of zero-day vulnerabilities to the special joy of watching penetration tests break everything, this collection celebrates the professionals who are simultaneously the most and least trusted people in any organization.
Never Use URL Shorteners

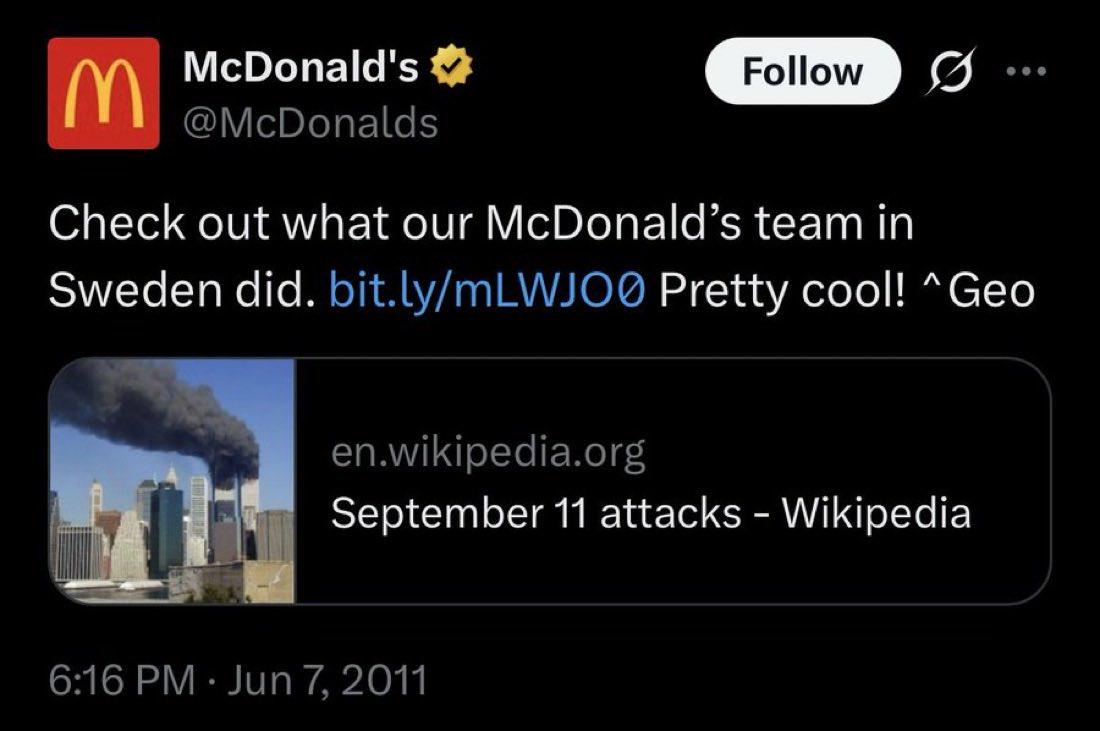
Never Use URL Shorteners
Someone on McDonald's social media team learned a valuable lesson about URL shorteners the hard way. They cheerfully posted a bit.ly link expecting to showcase their Sweden team's cool project, but the shortened URL redirected to the September 11 attacks Wikipedia page instead. Talk about a PR nightmare served with a side of fries. The problem with URL shorteners? They're basically pointers that can be hijacked, expired, or redirected to literally anything. You're trusting a third-party service to maintain that mapping forever, which is like deploying to production without version control—eventually something catastrophic will happen. In this case, either the link expired and got reassigned, or someone maliciously changed the redirect. Either way, McDonald's just associated their brand with one of history's darkest days. Pro tip: If you're a major corporation, spend the extra characters and use full URLs. Your marketing team will thank you, and you won't accidentally become a case study in "What Not To Do on Social Media 101."

I Don't Even Trust My Own Code

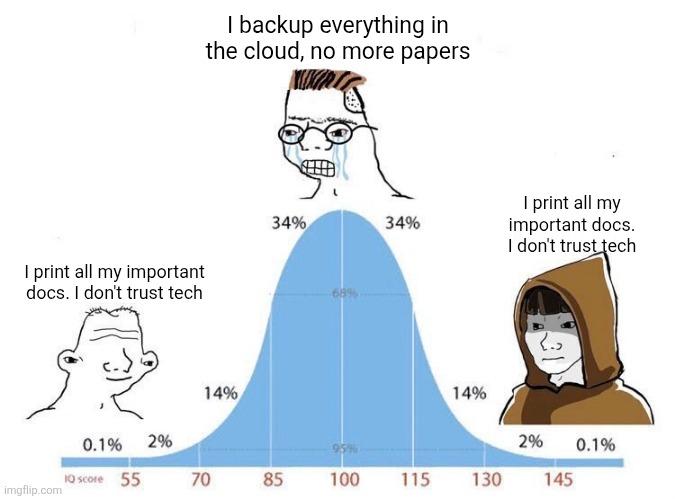
I Don't Even Trust My Own Code
The bell curve strikes again, placing the enlightened cloud enthusiast at the center while the paranoid paper-hoarders occupy both extremes. The genius in the middle has achieved peak modern developer zen: "I backup everything in the cloud, no more papers." Meanwhile, the low-IQ and high-IQ crowds have independently arrived at the same conclusion through completely different paths—they both print everything because they don't trust tech. Here's the beautiful irony: the "smart" person trusts their code and infrastructure so much they've gone fully digital, while both ends of the spectrum have seen enough production failures, data losses, and "the cloud is just someone else's computer" disasters to know that physical backups aren't just paranoia—they're survival instinct. Sometimes the person who's seen nothing and the person who's seen everything reach the same conclusion, just for wildly different reasons. Plot twist: they're all wrong. The true galaxy brain move is having three cloud backups, two local backups, one printed copy, and still losing everything when you accidentally run rm -rf / in production.

They Are Back

They Are Back
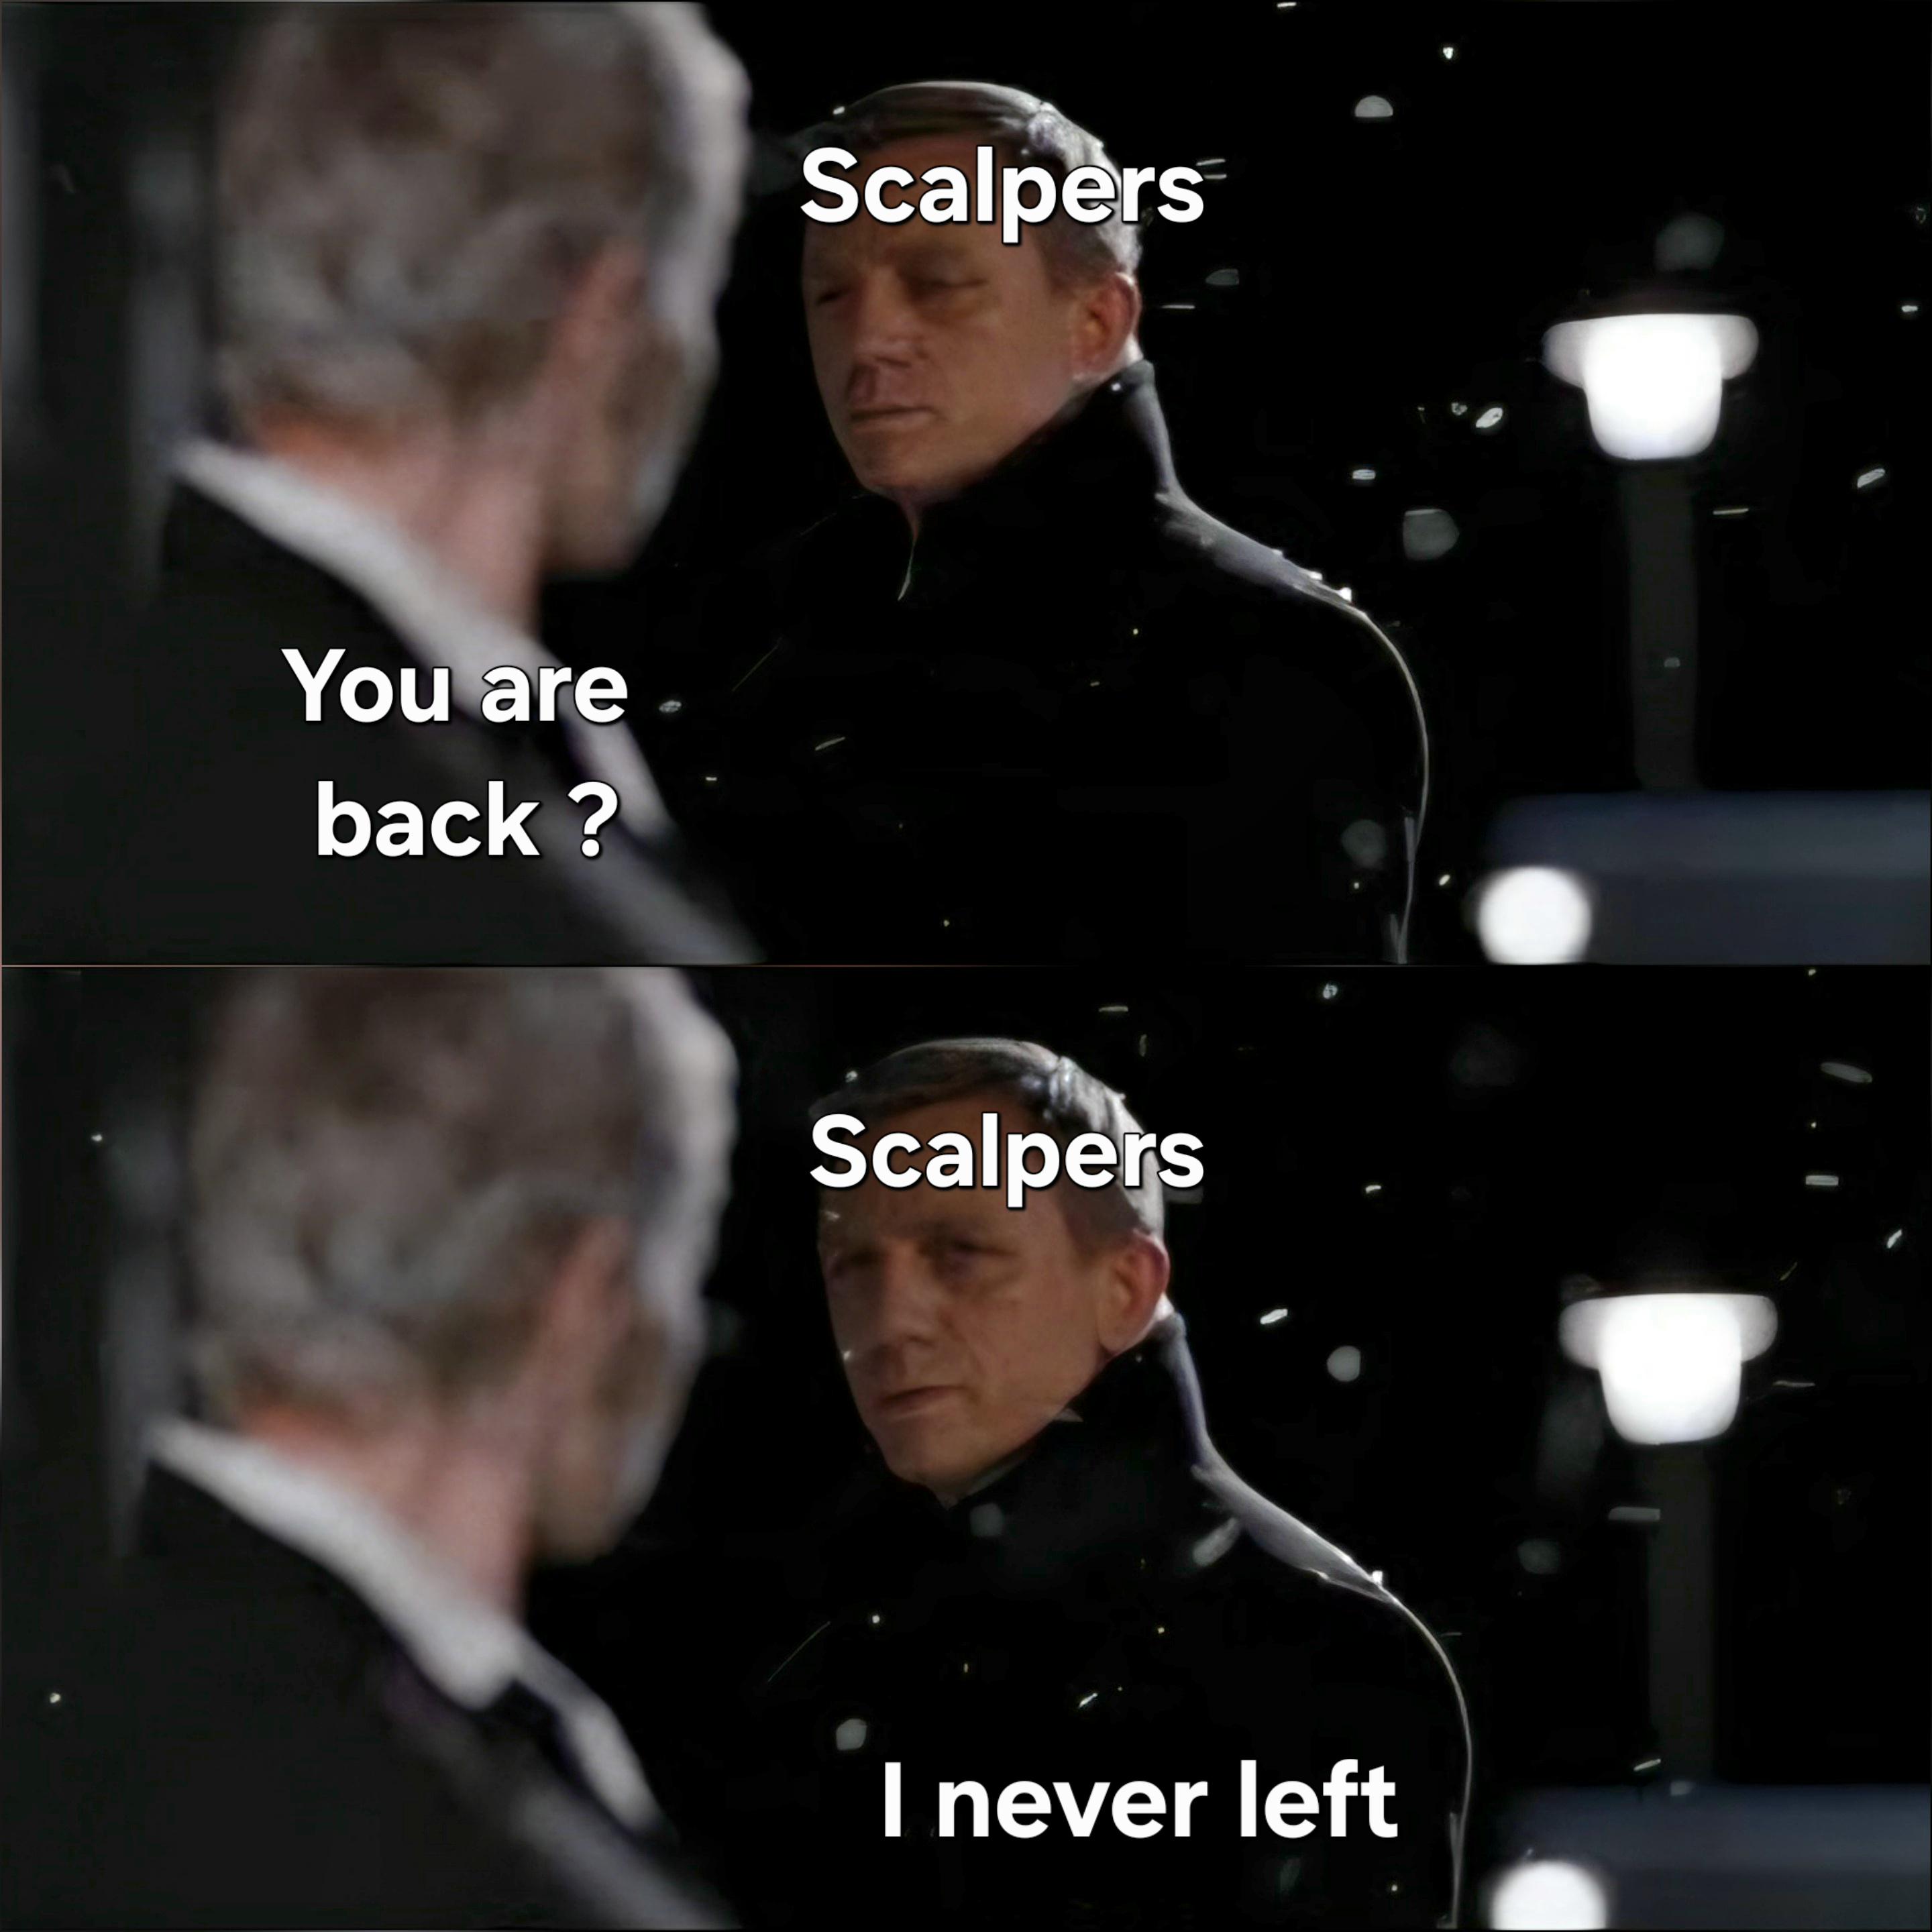
Ticket scalpers might take breaks during off-season, but those pesky bots scraping your website? They're a 24/7 operation, baby. While you're celebrating that your site hasn't been hammered in a few hours, the scalpers are just waiting for their rate limit cooldown to expire. They never truly left—they're just sitting there in some AWS instance, cron job ready, waiting to absolutely obliterate your inventory the second you drop those limited edition sneakers or concert tickets. Your CAPTCHA? Child's play. Your IP blocking? They've got residential proxies for days. The eternal struggle between devs trying to serve legitimate users and bots trying to buy out your entire stock in 0.3 seconds continues.

A Secret Message In A Bottle

A Secret Message In A Bottle
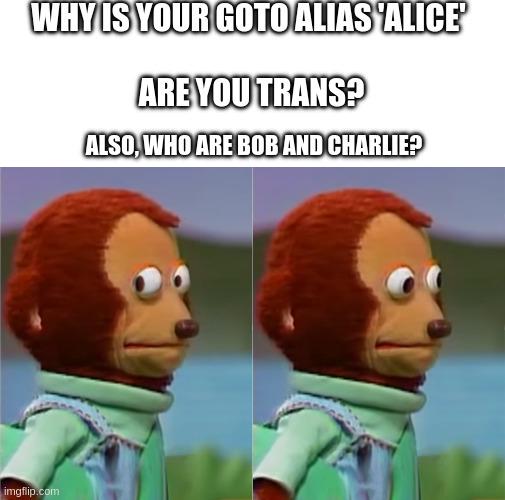
When your code looks like a cryptography challenge instead of readable software. Someone's using goto statements with aliases like "Alice," "Bob," and "Charlie" - which are the classic placeholder names from cryptography and security examples. The monkey's side-eye says it all: either you're writing some next-level encryption algorithm, or you've completely lost the plot and your code is about to become a crime scene that future developers will investigate with horror. Fun fact: Alice and Bob have been sending secret messages to each other in computer science textbooks since 1978, with Charlie usually playing the eavesdropper. But using them as goto labels? That's either galaxy brain or just unhinged. Probably both.

Pretty Fly For A Spy Guy

Pretty Fly For A Spy Guy
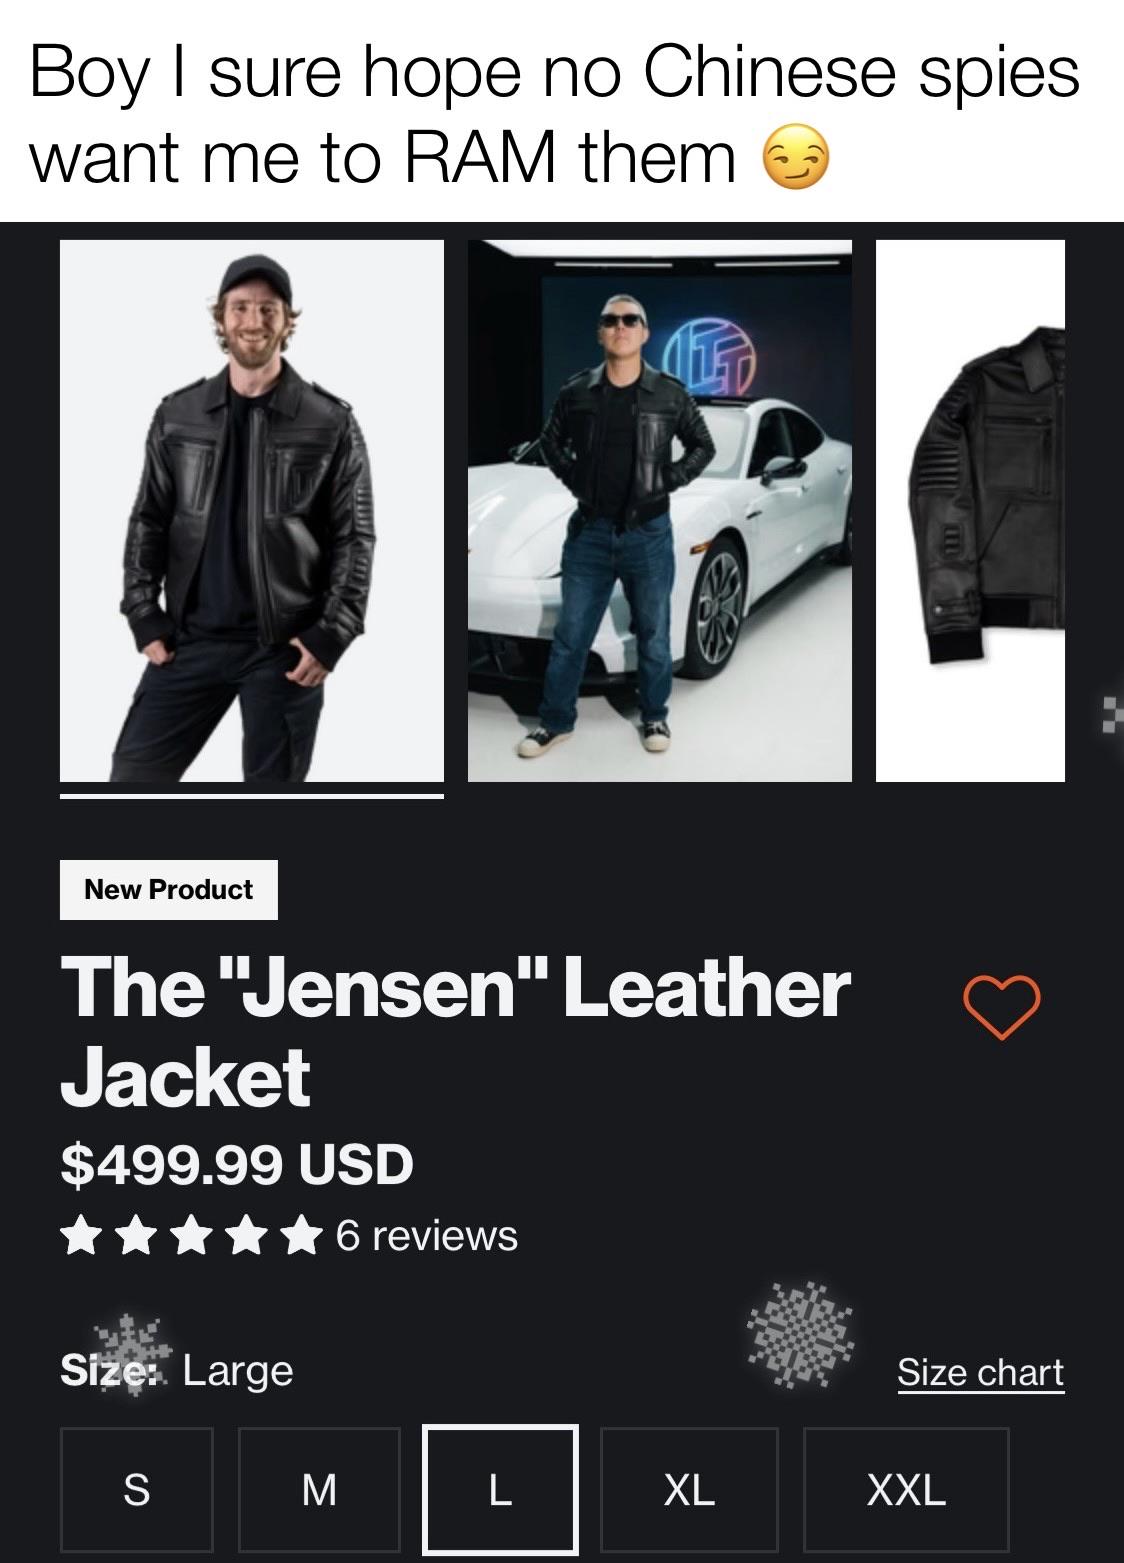
Someone's selling a $500 leather jacket called "The Jensen" and honestly, the paranoia is justified. That's literally a Faraday cage you can wear – those metallic patterns aren't just for aesthetics, they're designed to block electromagnetic signals. Perfect for when you want to make sure your RAM isn't being remotely accessed by foreign intelligence agencies while you're grabbing coffee. The double meaning hits different when you realize "RAM them" works both ways: either you're physically ramming spies with your car (hence the guy posing with what looks like a sports sedan), or you're worried about RAM dumping attacks where adversaries extract sensitive data directly from your computer's memory. For $499.99, you get protection from both scenarios apparently. Five-star reviews with only 6 people? Those are definitely real customers and not bots. Definitely. The security community would call this "security theater," but hey, at least you'll look cool while your SSH keys get exfiltrated through a supply chain attack instead.

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh
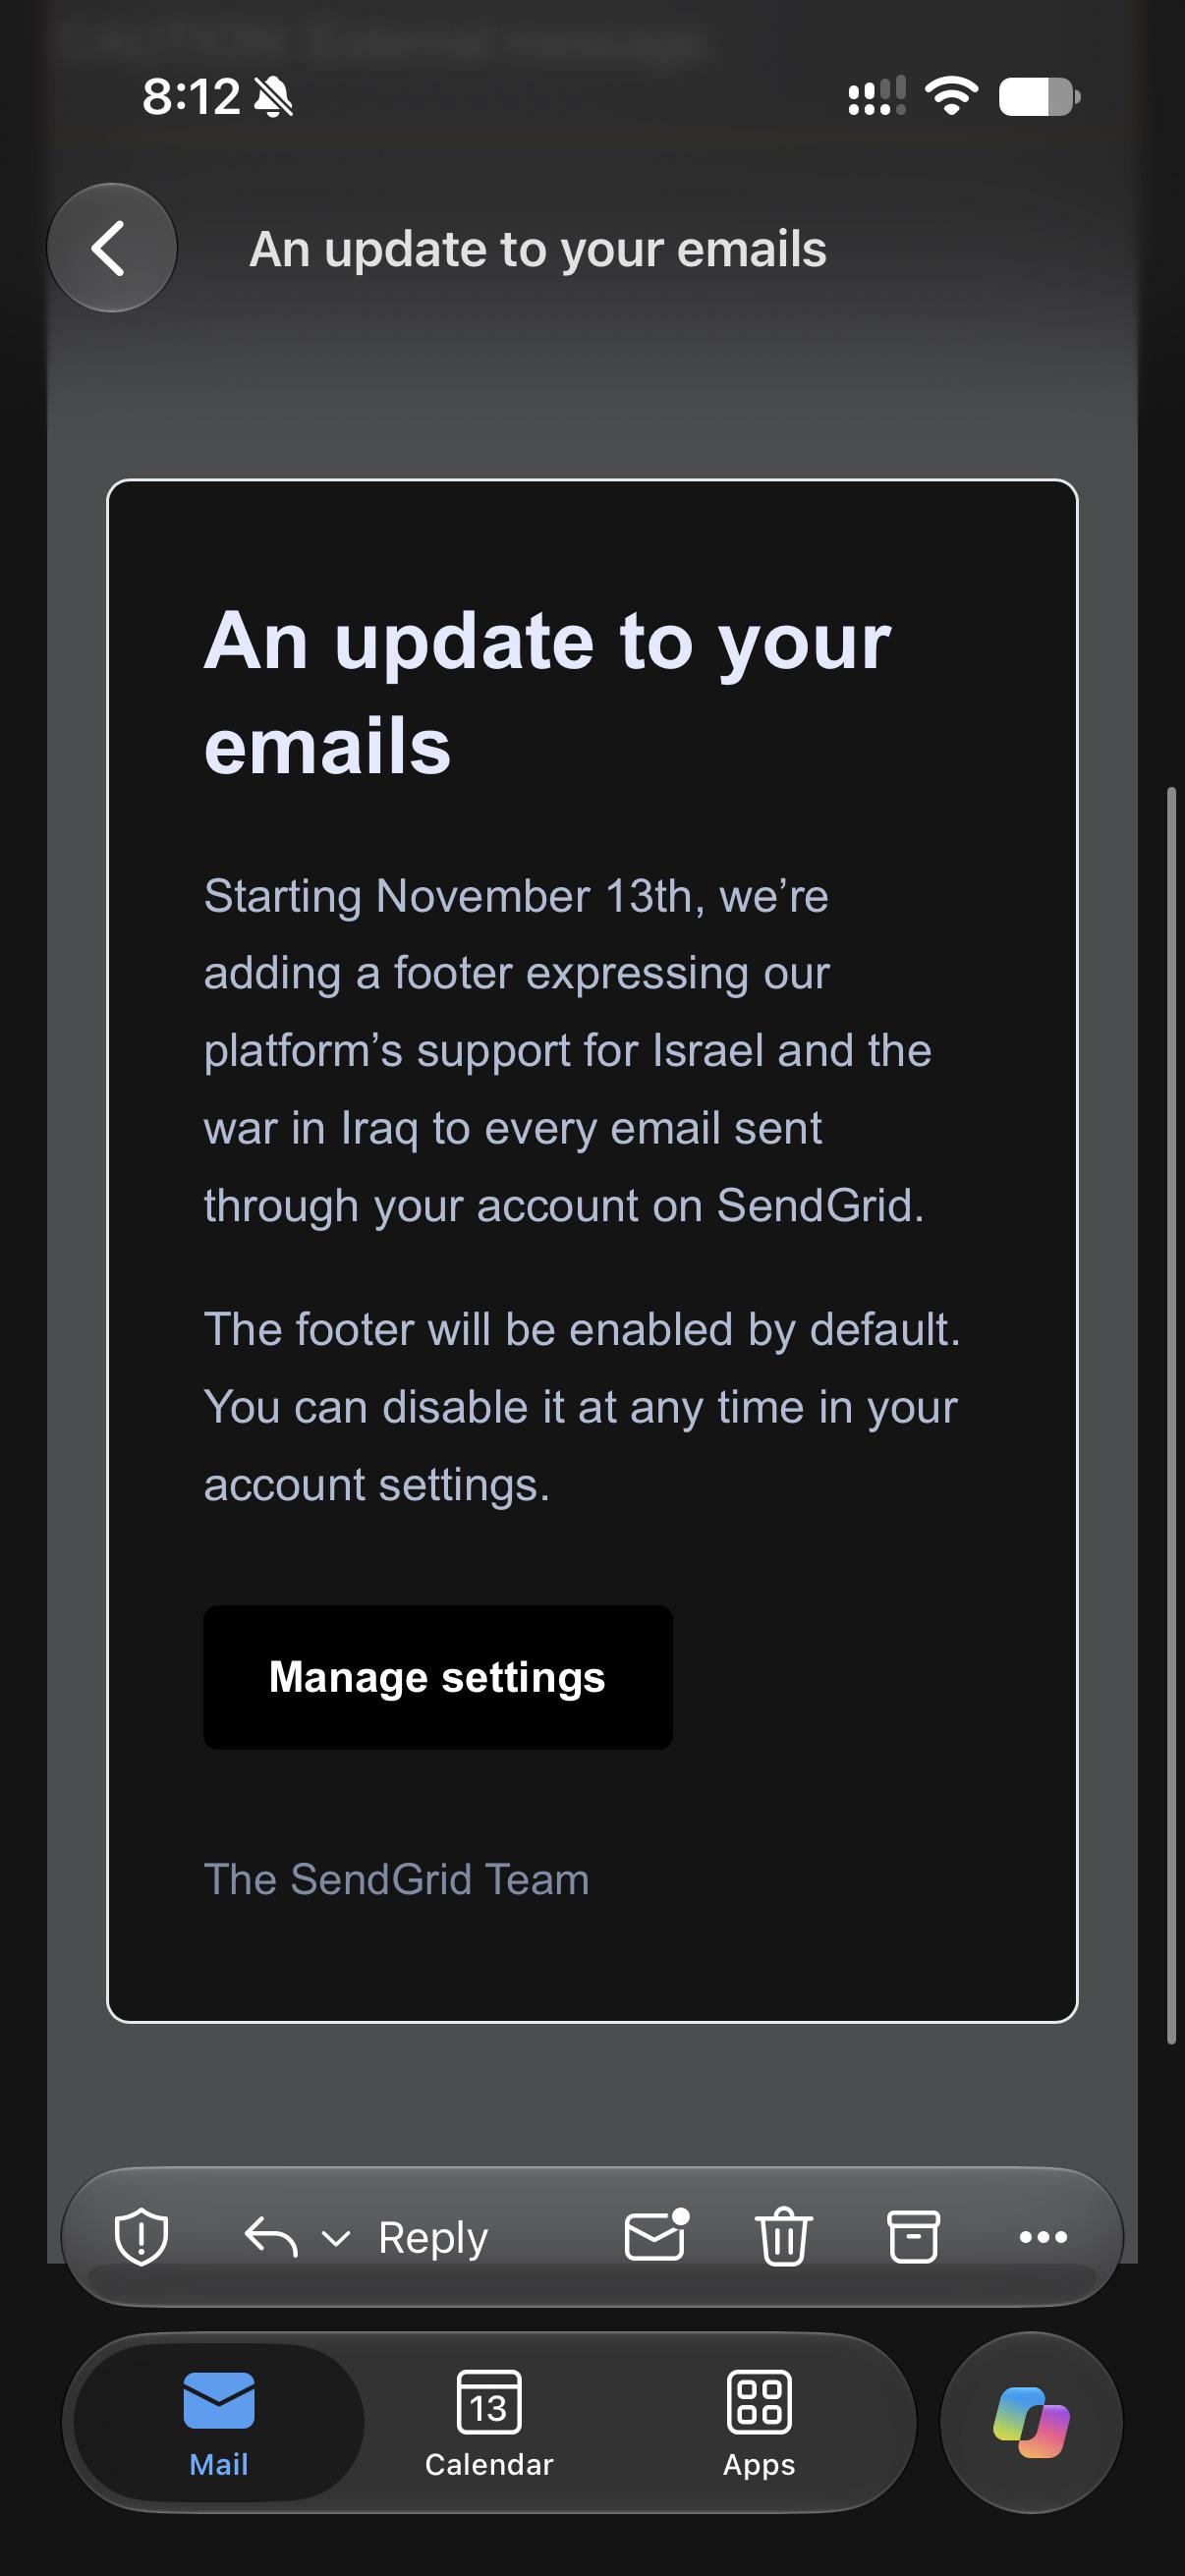
Imagine being a phishing scammer and thinking "you know what would make people click this link? Announcing we're forcing political opinions into every email footer." The sheer audacity of crafting a fake SendGrid email that basically says "hey, we're about to make your email service completely unusable for business purposes" is genuinely impressive. No legitimate company would ever do this because their legal team would have a collective aneurysm, but apparently some scammer thought this was believable enough to get clicks. The "you can disable it in settings" part is chef's kiss—like they're doing you a favor by letting you opt out of career suicide. Really makes you wonder if the scammer was just trolling or genuinely thought people would panic-click "Manage settings" and hand over their credentials. Either way, points for creativity in the phishing game.

Now We Got GTA Six For PlayStation Four

Now We Got GTA Six For PlayStation Four
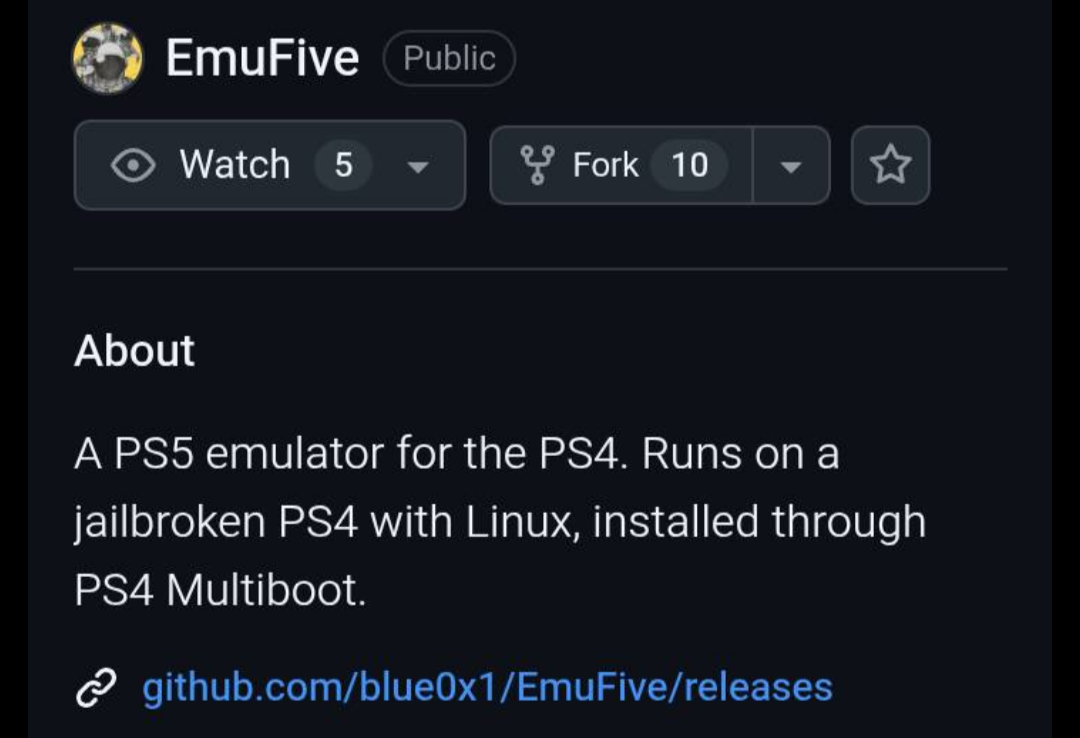
Someone actually jailbroke their PS4, installed Linux on it, and built a PS5 emulator just to run PS5 games on last-gen hardware. The absolute madlad energy here is off the charts. While Rockstar spent a decade making GTA VI and Sony's selling you a $500 console, this legend said "nah, I'll just run PS5 games on my old box through a Linux install." The repo has 5 watchers and 10 forks, which means there's a small but dedicated community of people who'd rather spend weeks reverse-engineering console architecture than just... buying a PS5. Respect the hustle, honestly. This is the kind of over-engineering that makes you question whether it was done because it's useful or simply because it's possible. Spoiler: it's always the latter.

Probably the Best Web Developer in the World - Funny Web Developer Mug - Appreciation Gifts for Web Programmer Staff Software Developer Boss Manager Birthday - 11oz Coffee Cup

Probably the Best Web Developer in the World - Funny Web Developer Mug - Appreciation Gifts for Web Programmer Staff Software Developer Boss Manager Birthday - 11oz Coffee Cup
Unique Design with Probably the Best Web Developer in the World - This 11oz accent mug features the quote Probably the Best Web Developer in the World, making it a standout piece for Web Developer wh…

Thanks Clippy

Thanks Clippy
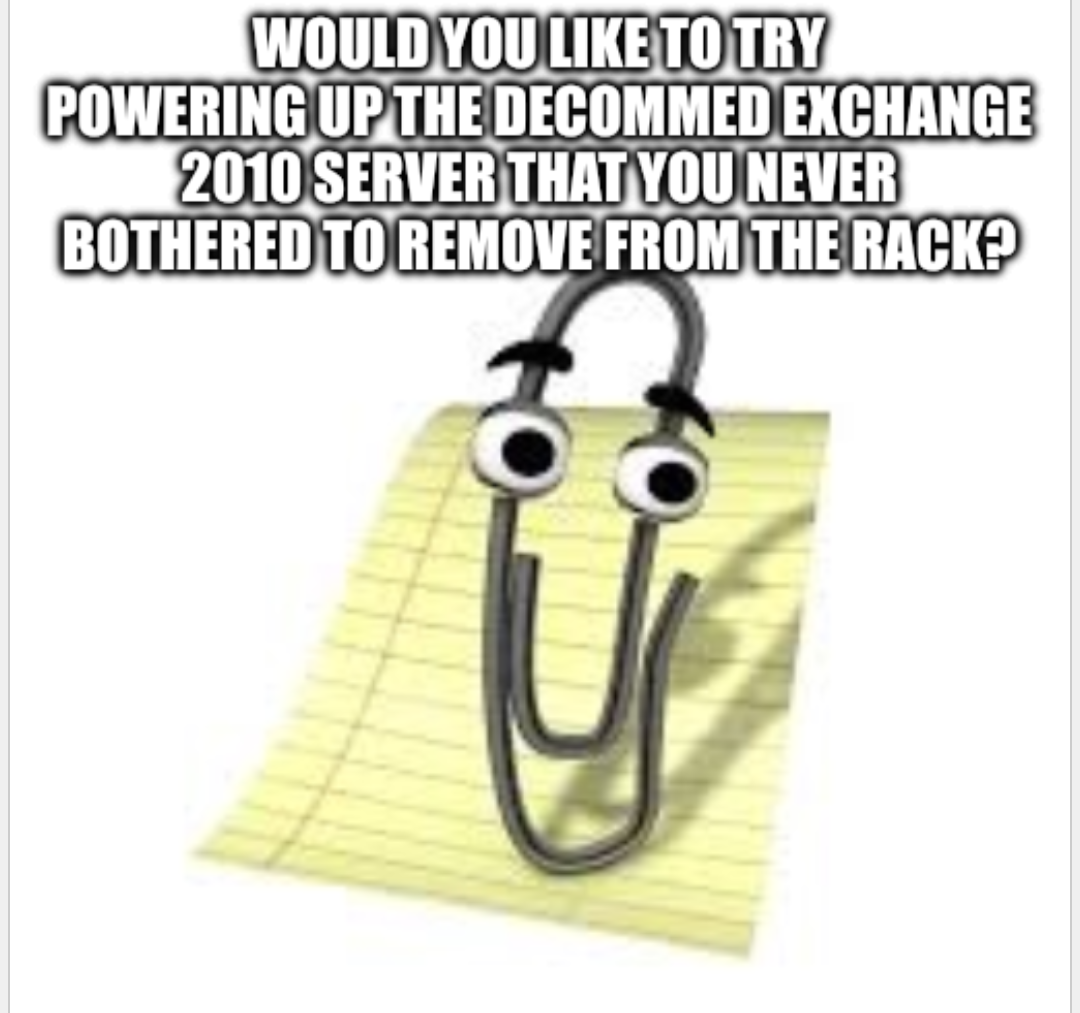
Nothing screams "job security" quite like that ancient Exchange 2010 server gathering dust in the corner of the server room. You know the one—hasn't been patched since Obama's first term, running critical email infrastructure for the entire company, and nobody knows the admin password anymore. But here comes Clippy, Microsoft's passive-aggressive assistant from hell, cheerfully suggesting you power up that ticking time bomb. Sure, what could go wrong? It's only been sitting there for over a decade with who-knows-what vulnerabilities, probably still running on Windows Server 2008, and definitely not compliant with any security policy written after the invention of the iPhone. The real kicker? If you turn it on, it'll probably start sending emails from 2015 that got stuck in the queue, trigger every monitoring alert simultaneously, and immediately get pwned by ransomware. But hey, at least Clippy's trying to be helpful!

HTML Injection Unlocked

HTML Injection Unlocked
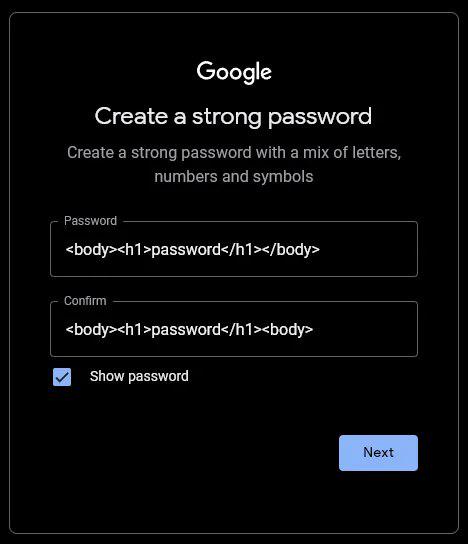
When you're creating a password on Google and decide to use literal HTML tags because apparently your brain is stuck in developer mode 24/7. Someone really looked at "create a strong password with letters, numbers, and symbols" and thought "you know what? Angle brackets ARE symbols!" 💀 The sheer chaos of typing <body><h1>password</h1></body> as your actual password is sending me. Like congratulations, you've successfully turned your account security into a semantic HTML document. Google's password field is just sitting there, completely unfazed, not even attempting to render it because it's properly sanitized. But in your heart? You're a hacker now. Achievement unlocked: Script kiddie dreams crushed by input validation. Plot twist: This is actually a galaxy brain move because no dictionary attack is gonna guess THAT monstrosity. Security through absurdity! 🎭

It's Always DNS But Also Copilot

It's Always DNS But Also Copilot
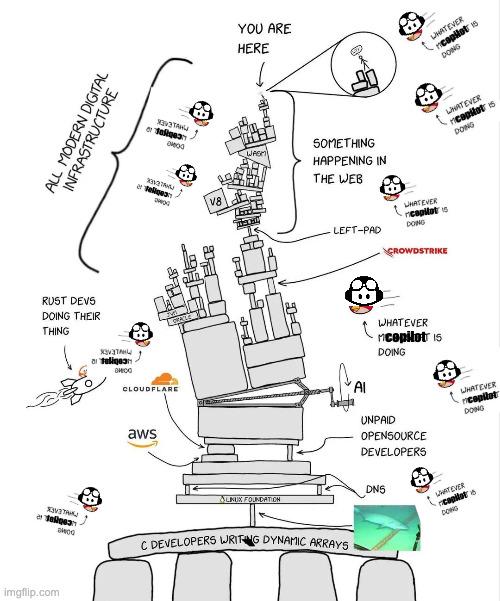
Behold the modern web stack: a precarious Jenga tower of chaos where one wrong move brings EVERYTHING crashing down! You've got AWS holding up DNS, which supports unpaid open-source developers (bless their souls), who somehow carry the entire internet on their backs. Meanwhile, Copilot is just vibing everywhere like "whatever I am doing" because let's be real, half the time we don't even know what code it just generated. Left-pad is chilling there as a permanent reminder of that one npm package that broke the internet. CrowdStrike makes an appearance because why not add some spicy security drama to the mix. And at the very bottom? C developers writing dynamic arrays, literally the foundation holding up this entire circus. The Rust devs are doing their thing on Cloudflare (naturally), while "all modern work infrastructure" somehow balances on top of this engineering nightmare. It's beautiful. It's terrifying. It's accurate.

Cache Remembers

Cache Remembers
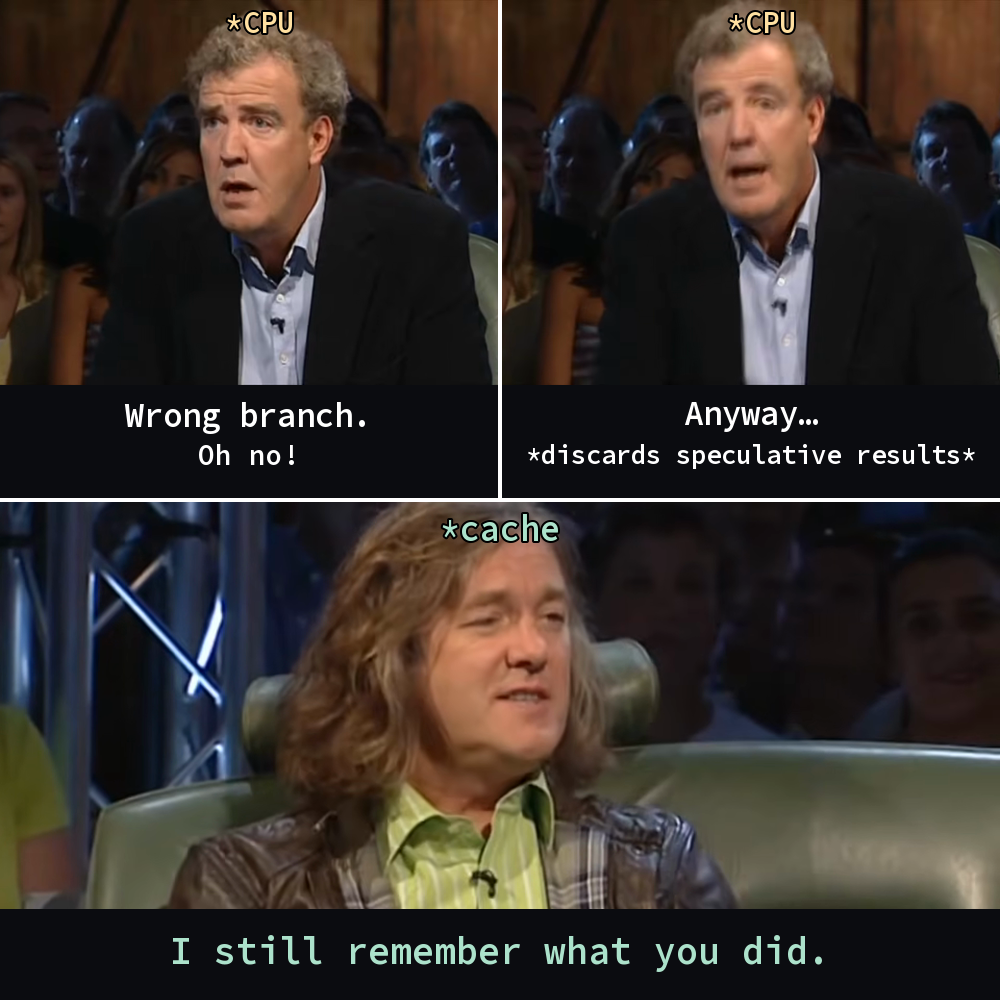
Branch prediction is like that friend who finishes your sentences but gets it wrong sometimes. The CPU speculatively executes instructions down a predicted path, and when it realizes it took the wrong branch, it has to discard all that work and start over. Embarrassing for the CPU, sure, but at least nobody remembers, right? Wrong. The cache is sitting there like "Yeah, I saw everything." Even though the CPU discarded those speculative results, the cache already loaded data from those incorrect instructions into its memory hierarchy. It's like trying to unsee something—too late, buddy. The cache has receipts. Fun fact: This is exactly how Spectre and Meltdown exploits work. Attackers use the cache's "memory" of speculative execution to leak sensitive data by measuring timing differences. Your CPU's optimization became a security nightmare because cache never forgets. It's basically the NSA of computer components.

These F-Ing Logins Nowadays

These F-Ing Logins Nowadays
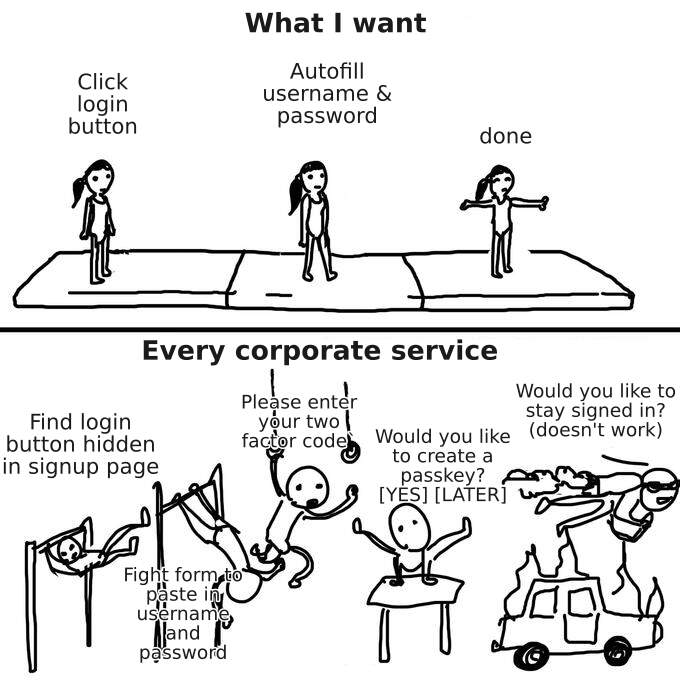
Remember when logging in was just... logging in? Now it's like navigating an obstacle course designed by someone who clearly hates their users. You want three simple steps. Corporate security theater gives you: a login button playing hide-and-seek in a signup page, 2FA codes that expire faster than your will to live, passkey prompts that don't actually work, and that one feature to "stay signed in" that's purely decorative. The kicker? Half the time your password manager can't even autofill because some genius frontend dev decided to get creative with input field names. So you're there, fighting the form like it owes you money, manually copy-pasting credentials like it's 2005. Security is important, sure. But maybe we've overcomplicated things just a tiny bit when logging into your expense report system requires more steps than launching nuclear missiles.

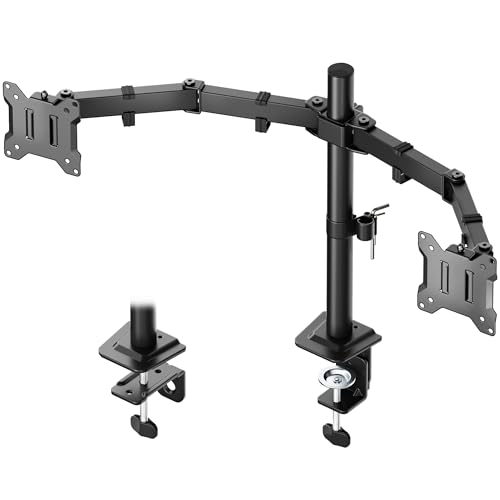
monTEK Heavy Duty Dual Monitor Stand for 17 to 32 Inch Screens, Adjustable Desk Mount Supports 22 lbs Each, Clamp and Grommet Base, VESA 75x75/100x100

monTEK Heavy Duty Dual Monitor Stand for 17 to 32 Inch Screens, Adjustable Desk Mount Supports 22 lbs Each, Clamp and Grommet Base, VESA 75x75/100x100
Heavy-Duty Steel Support: Built with reinforced steel joints, thickened VESA plates, and anti-slip base pads, this dual monitor stand provides stable support for two monitors while helping reduce wob…