npm Memes

Npm Driven Development

Npm Driven Development
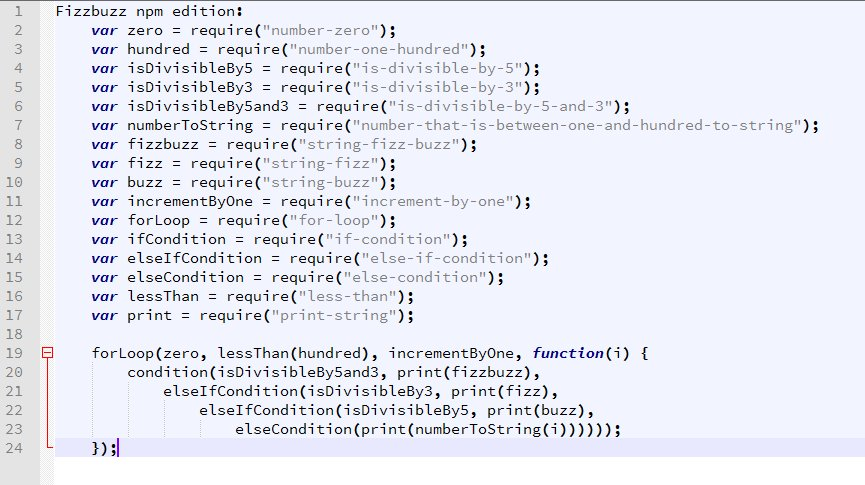
Someone really looked at FizzBuzz and said "you know what this needs? A dependency tree deeper than my existential dread." Instead of writing basic arithmetic and conditionals like a normal person, they've installed an npm package for literally everything. Need to check if a number is divisible by 5 and 3? There's a package for that. Need to increment by one? Package. Need a for loop? Believe it or not, also a package. This is what happens when your bundle size is measured in gigabytes and your node_modules folder achieves sentience. The code is technically solving FizzBuzz, but at what cost? Your CI/CD pipeline now takes 45 minutes just to install dependencies, and you're one npm audit away from discovering 247 critical vulnerabilities in is-divisible-by-3 . Fun fact: The entire JavaScript ecosystem can be summarized as "why write code when you can install someone else's code that does the same thing but with 50 transitive dependencies?"

Things Will Get Worse

Things Will Get Worse
Oh FANTASTIC, a security vulnerability has been discovered! But wait, there's MORE! Because when you start investigating that one CVE (Common Vulnerabilities and Exposures), you suddenly realize your entire dependency tree is basically a house of cards built on ancient, unpatched libraries. It's like opening Pandora's box, except instead of unleashing evil upon the world, you're just unleashing a cascade of security patches that will consume your entire sprint. And your next sprint. And probably your will to live. The Oprah meme format is *chef's kiss* perfect here because CVEs really DO multiply like they're being handed out at a daytime talk show. "You get a critical severity! And YOU get a critical severity! EVERYONE gets to update their packages!" 🎉

Fortune Cookie Supply Chain Attack

Fortune Cookie Supply Chain Attack
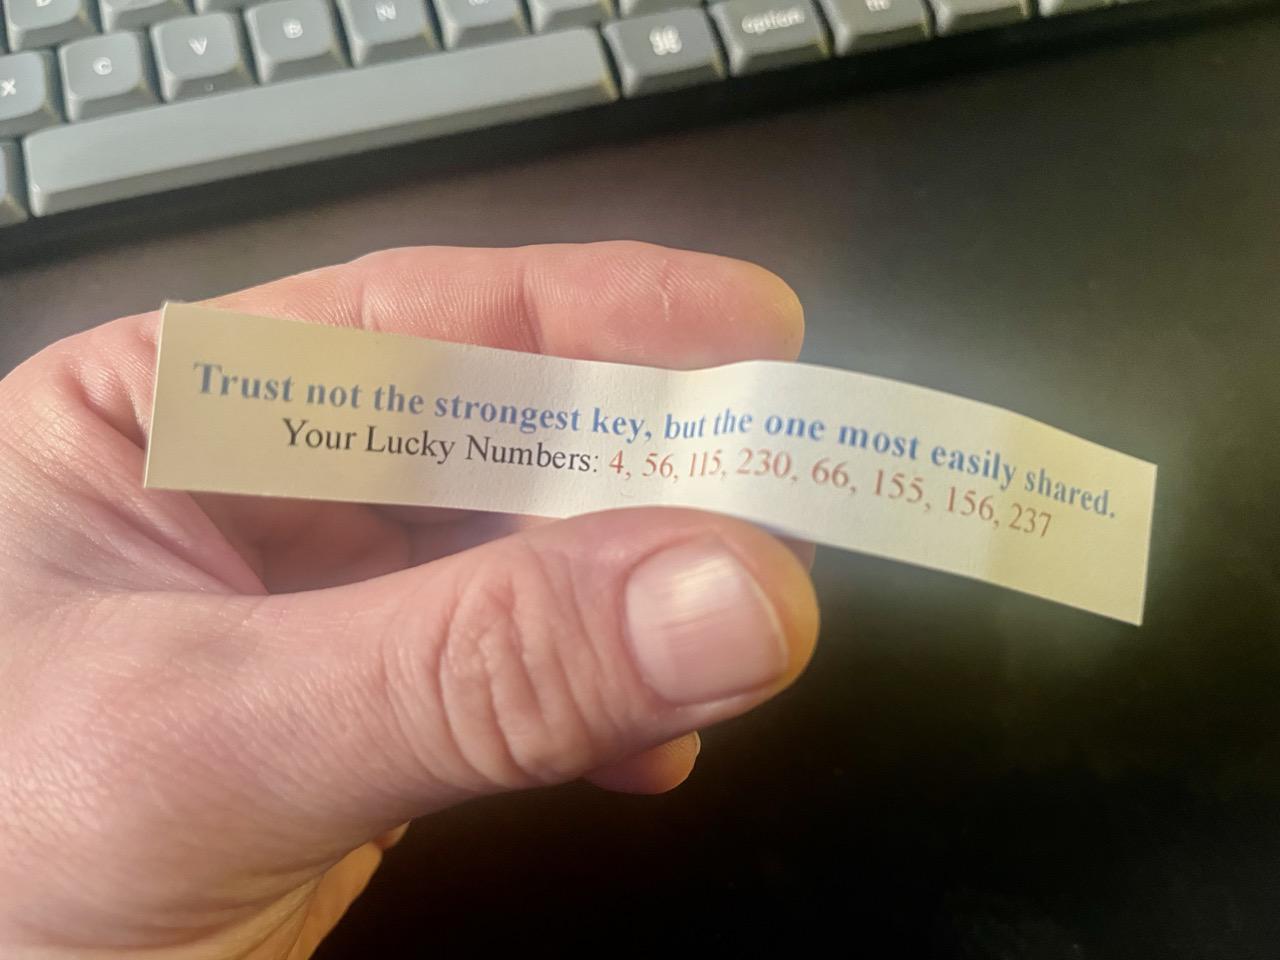
When even your fortune cookie is giving you cybersecurity advice that's simultaneously brilliant AND terrifying. "Trust not the strongest key, but the one most easily shared" is basically every security engineer's nightmare wrapped in a crispy shell. The fortune cookie just casually dropped the entire philosophy behind supply chain attacks – why break the strongest lock when you can just steal the key everyone's passing around like a joint at a DevOps conference? The genius here is that attackers don't need to brute-force your AES-256 encryption when they can just compromise that one npm package with 50 million weekly downloads that everyone trusts blindly. Why hack the Pentagon when you can inject malicious code into a logging library that literally everyone uses? It's the SolarWinds incident but make it fortune cookie wisdom. And those "lucky numbers"? Probably port numbers for your exposed Redis instance. Sweet dreams, developers! 🥠💀

A New Day A New Beginning

A New Day A New Beginning
The JavaScript ecosystem moves faster than a caffeinated hamster on a wheel. Every single day, someone wakes up and decides the world needs yet another framework to do exactly what the last 47 frameworks already did. By the time you finish your morning coffee, three new libraries have dropped on npm, each claiming to be "blazingly fast" and "production-ready" (narrator: they weren't). The hamster emerging from its hole saying "Bonjour" perfectly captures that innocent optimism of a new JS library entering an already oversaturated ecosystem. Fun fact: There are over 2 million packages on npm. That's roughly one package for every three JavaScript developers who've ever lived. The real skill isn't learning JavaScript anymore—it's choosing which of the 47 state management libraries to use this week.

Takes Two Seconds To Open Paint

Takes Two Seconds To Open Paint
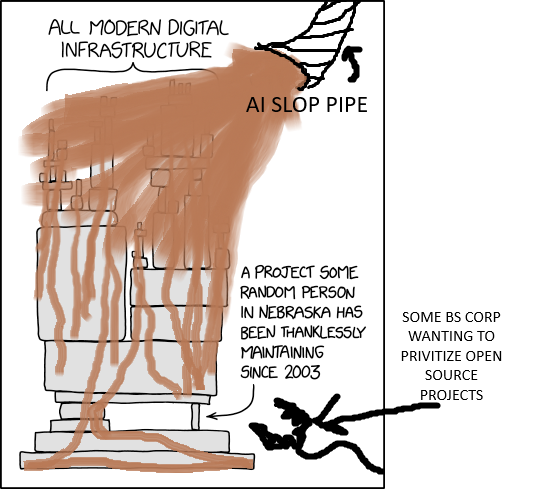
The entire digital world is literally held together by some random developer's side project from 2003 that they abandoned after their first commit. Your banking app? Probably depends on a library maintained by a guy in Nebraska who hasn't updated his GitHub profile picture since MySpace was relevant. The best part is how corporations with billion-dollar valuations are frantically trying to privatize and monetize open source projects that have been running critical infrastructure for decades. Good luck putting a paywall on the digital equivalent of load-bearing duct tape, my dudes. Meanwhile, the AI slop pipe is just dumping out code that looks like it was generated by autocomplete on steroids, feeding directly into production systems. What could possibly go wrong when your entire tech stack is one unmaintained dependency away from collapse? At least Paint opens quickly—that's something we can still count on.

Just Write The Five Lines To Build The Project For The Love Of God

Just Write The Five Lines To Build The Project For The Love Of God
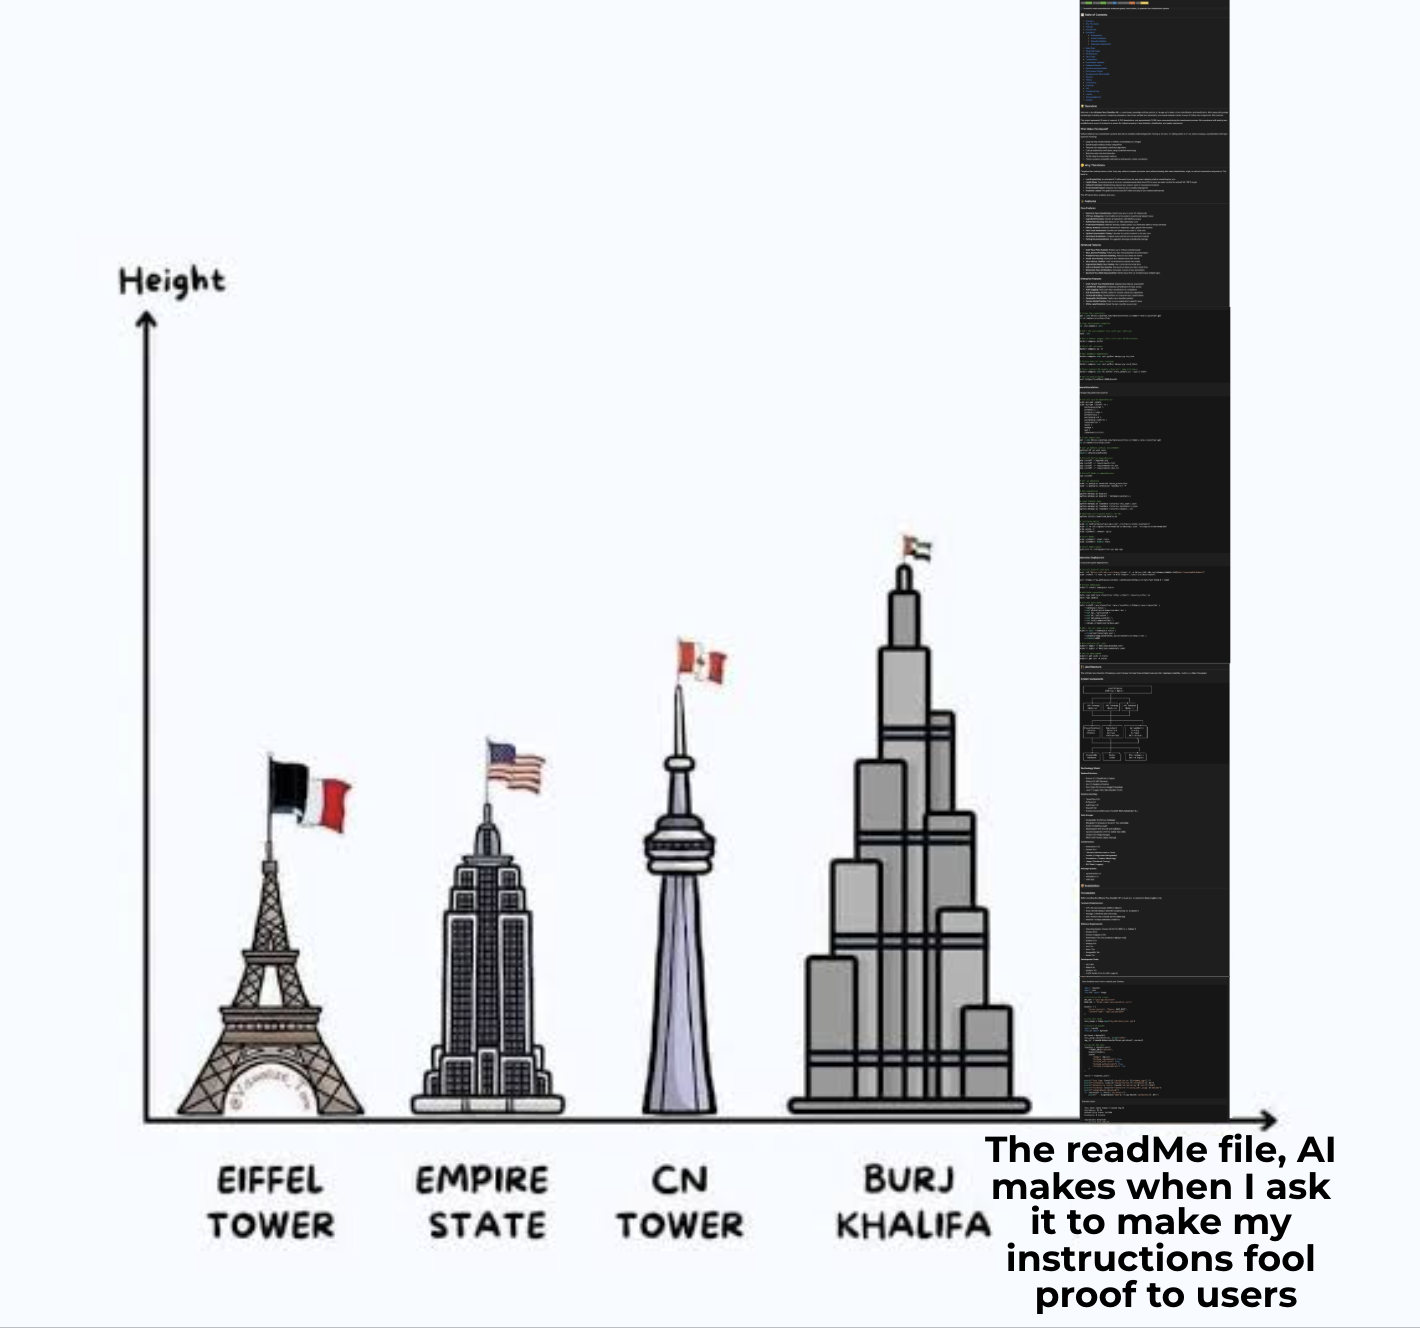
You wanted a simple "npm install && npm start" but instead got a README that's taller than the Burj Khalifa. Every dependency needs its own config file. Every environment variable needs three paragraphs of explanation. The prerequisites section alone requires a PhD. Meanwhile the maintainer is out here writing a novel about their architectural decisions when literally all anyone wants is "clone repo, run these commands, see website." Instead you're reading about their journey through microservices enlightenment while Docker refuses to build. The best READMEs are the ones that assume you're not an idiot but also don't assume you have their exact machine setup from 2019. Just the build commands. That's it. That's all we need.

200 Pcs Funny Stickers for Adults (Dirty) by Puraesla - Meme Water Bottles Sticker Pack Waterproof Cool Accesory for Laptop, Hard Hats, Sarcastic, Scrapbooking Decals

200 Pcs Funny Stickers for Adults (Dirty) by Puraesla - Meme Water Bottles Sticker Pack Waterproof Cool Accesory for Laptop, Hard Hats, Sarcastic, Scrapbooking Decals
DIRTY Funny Stickers for ADULTS. Vibrant Sticker Collection: This set features an eclectic mix of bold, humorous, and eye-catching stickers with various designs, characters, and phrases. · Diverse Th…

Vibe Coder 2030

Vibe Coder 2030
Welcome to the dystopian future where even installing dependencies requires a premium subscription. By 2030, we'll apparently need to watch a full YouTube ad marathon just to run npm install . And naturally, they'll all be unskippable because Silicon Valley finally figured out how to monetize our suffering. The dead-inside expression captures the exact energy of someone who's been debugging for 6 hours straight and now has to sit through ads about car insurance and mobile games before their node_modules folder can balloon to 500MB. At least the ads will finish faster than Webpack builds. Fun fact: We already watch our CI/CD pipelines like they're Netflix shows, so this isn't even that far-fetched. The future is bleak, but at least our package.json will have great SEO.

Vibing While Coding

Vibing While Coding
You know you've reached peak developer zen when you're sitting there, completely dead inside, watching your 47th unskippable ad just so you can install a package. The future of coding isn't flying cars or neural interfaces—it's apparently monetized dependency management. Nothing says "living the dream" quite like staring blankly at a 30-second ad for car insurance while npm install waits patiently in the background. The best part? You can't even rage-quit because you NEED that package. It's like being held hostage by capitalism, one dependency at a time. "Please drink verification can to continue coding."

Resolving Dependency Hell

Resolving Dependency Hell
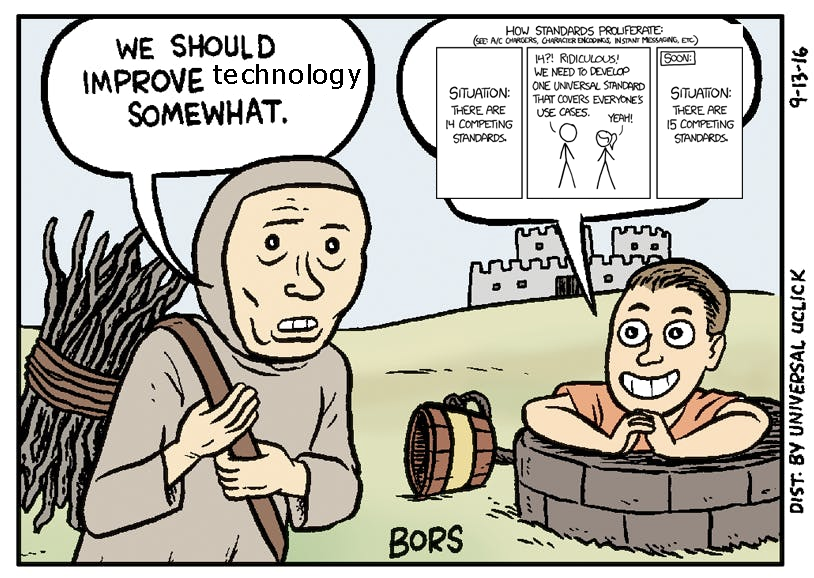
So someone suggests we need better standards to fix our tech problems, and naturally the solution is... creating yet another standard that competes with all the existing ones. Classic move. Now instead of 14 competing standards, we've got 15. The "dependency hell" title makes it even better because this is literally how we ended up with npm having 47 different date libraries and Python needing virtualenv just to survive. Every generation of developers thinks they'll be the ones to finally create THE universal solution, and every time we just add another layer to the chaos. It's like watching history repeat itself but with more GitHub stars.

Always Pin The Version Kids

Always Pin The Version Kids
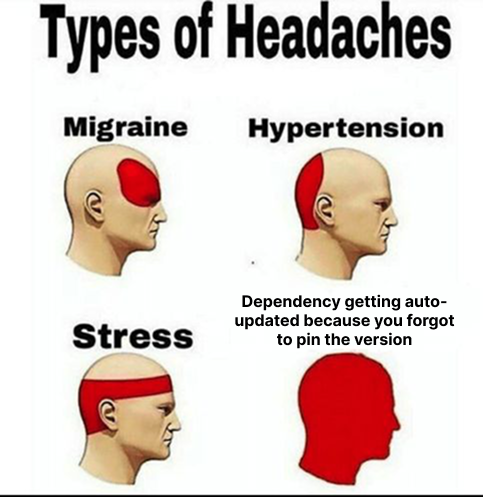
You know those medical diagrams showing different types of headaches? Well, here's the developer edition. Migraine? Cute. Hypertension? Amateur hour. But that fourth one—when your dependency auto-updates overnight because you were too lazy to pin the version in your package.json—that's when your entire head becomes pure, unadulterated pain. Nothing quite compares to arriving at work, running npm install , and watching your perfectly functioning app implode because some maintainer decided v2.0.0 was the perfect time to introduce 47 breaking changes. Your CI/CD pipeline is screaming, production is on fire, and you're frantically searching through changelogs at 9 AM trying to figure out why everything that worked yesterday is now a dumpster fire. Pro tip: ^1.2.3 is not your friend. That little caret is a ticking time bomb. Use exact versions like 1.2.3 or at minimum ~1.2.3 . Your future self will thank you when you're not debugging someone else's "improvements" at midnight.

Javascript Experience

Javascript Experience
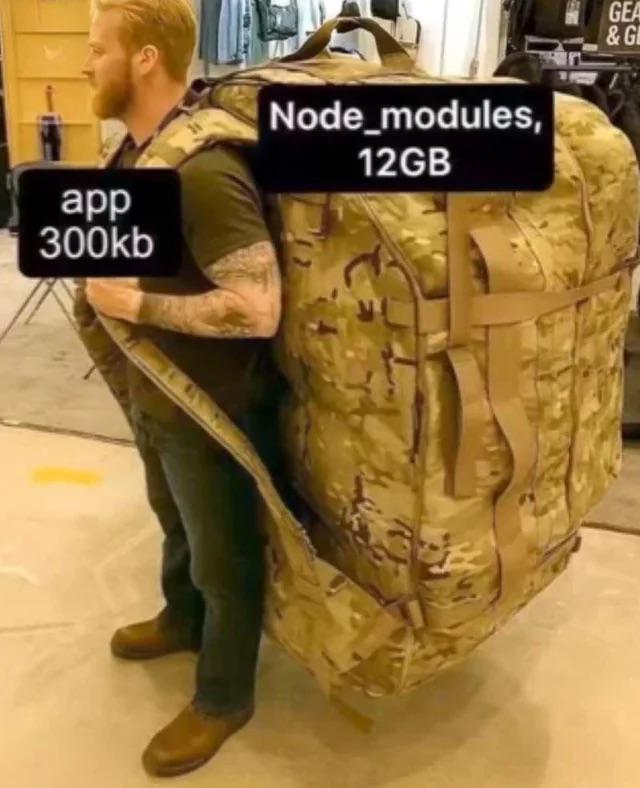
Your actual application: a modest 300KB of code that probably just displays a form and fetches some data. Your node_modules folder: a 12GB monstrosity that requires military-grade equipment to transport. Somewhere in there are 47 different versions of lodash, a left-pad implementation, and the entire Chromium browser bundled three times over. The ratio is absolutely unhinged. You installed one package, which had dependencies, which had dependencies, which had dependencies... and now you're carrying around more code than the Apollo 11 guidance computer used to land on the moon. All to center a div. Fun fact: If you delete node_modules, you can free up enough disk space to install another operating system. But you won't, because running npm install again is a 20-minute commitment and a prayer.

To Understand Why Mods Were Added, You Should Try The Vanilla Game First, Change My Mind

To Understand Why Mods Were Added, You Should Try The Vanilla Game First, Change My Mind
Okay but here's the thing: trying vanilla JavaScript in 2024 is like playing Dark Souls with a wooden spoon. Sure, you'll appreciate why libraries exist, but you'll also lose your sanity in the process. The gaming analogy hits different for developers because we literally do this with frameworks. "Why do we need React?" *proceeds to manually manipulate DOM for 6 hours* "Oh... OH." Same energy as "Why do we need jQuery?" back in 2010 when cross-browser compatibility was a war crime. But let's be real—sometimes vanilla is actually better. You don't need a 500KB framework to toggle a class name. The problem is juniors who've never written a single line without create-react-app and think `document.getElementById` is ancient hieroglyphics. Then they ship 2MB of dependencies for a todo app. The real wisdom? Understand the vanilla mechanics so you know when you're over-engineering. Otherwise you're just cargo-culting npm packages and praying to the node_modules gods.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.