Algorithms Memes

Algorithms: where computer science theory meets the practical reality that most problems can be solved with a hash map. These memes celebrate the fundamental building blocks of computing, from sorting methods you learned in school to graph traversals you hope you never have to implement from scratch. If you've ever optimized code from O(n²) to O(n log n) and felt unreasonably proud, explained Big O notation at a party (and watched people slowly walk away), or implemented a complex algorithm only to find it in the standard library afterward, you'll find your algorithmic allies here. From the elegant simplicity of binary search to the mind-bending complexity of dynamic programming, this collection honors the systematic approaches that make computers do useful things in reasonable timeframes.
E Mudhrama

E Mudhrama
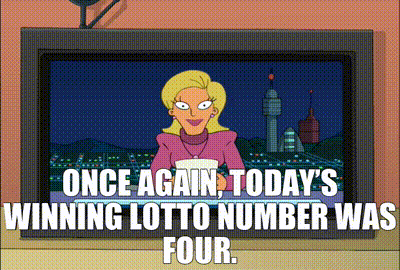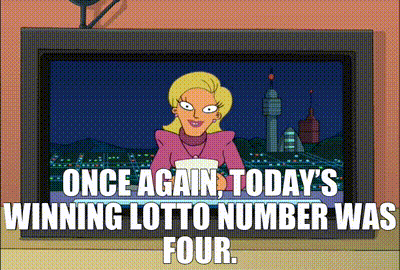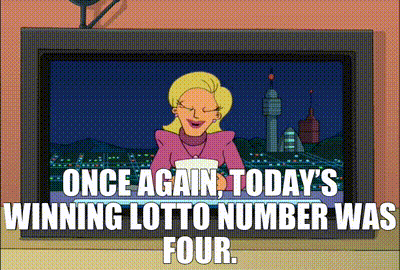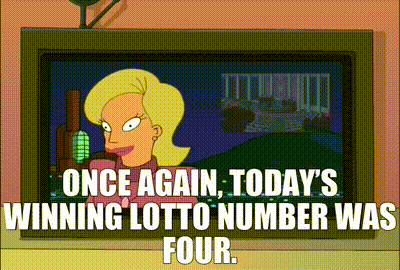
When your "random" number generator keeps spitting out the same number like it's auditioning for a role in Groundhog Day. Nothing screams "quality randomness" quite like getting 4 for the millionth time because someone thought Math.random() seeded with the current time was good enough. Plot twist: it wasn't. Your lottery simulation is basically just a 4 vending machine at this point, and somewhere a statistics professor is having a breakdown.

Time For IPO

Time For IPO
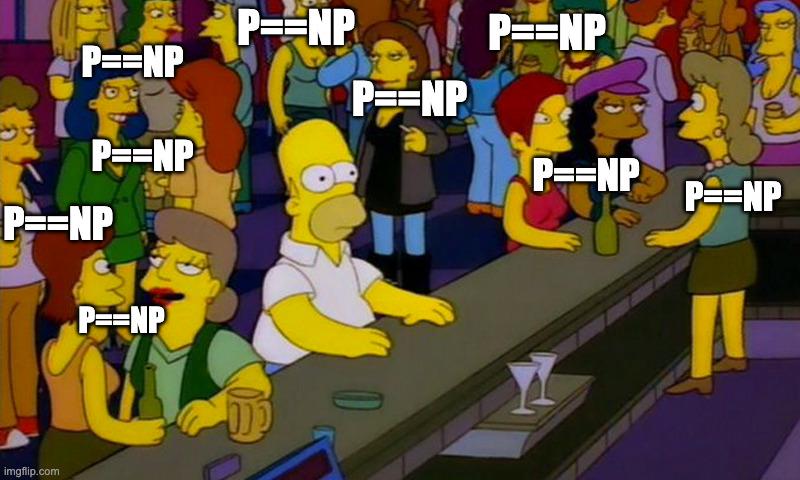
You know your startup has achieved peak Silicon Valley when the entire codebase is held together by P==NP assumptions. Every engineer at the bar knows the product secretly runs on algorithms that would make computer science professors weep, but hey, the metrics look good and investors don't read code. For context: P==NP is one of the biggest unsolved problems in computer science. If it were true, every problem that's easy to verify would also be easy to solve. Cryptography would collapse, optimization would be trivial, and your O(n!) brute force solution would suddenly be acceptable in production. But sure, let's go public. What could possibly go wrong when your entire tech stack is based on a mathematical impossibility? The VCs are already drafting the S-1.

Short Circuit Evaluation

Short Circuit Evaluation
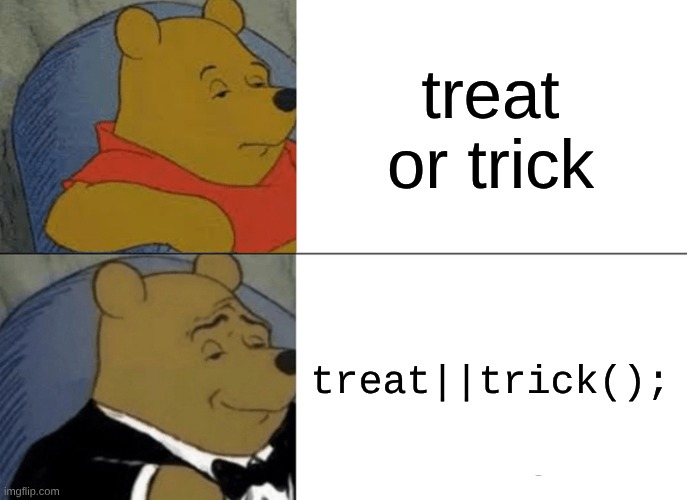
When you upgrade from basic Halloween logic to enterprise-level conditional execution. The top panel shows the casual "treat or trick" approach—simple, readable, something your product manager might understand. But then we suit up with treat||trick() , where the compiler's like "already got the treat? Cool, not even gonna bother calling that trick() function." Short-circuit evaluation means the second operand only gets evaluated if the first one doesn't seal the deal. It's lazy evaluation at its finest—why do more work when you can do less? Your CPU thanks you, your function calls thank you, and that potentially expensive trick() function that might've queried a database or summoned a demon? Yeah, it's just chilling, never executed. Efficiency dressed in a tuxedo.

Handbook After Bubble Burst

Handbook After Bubble Burst
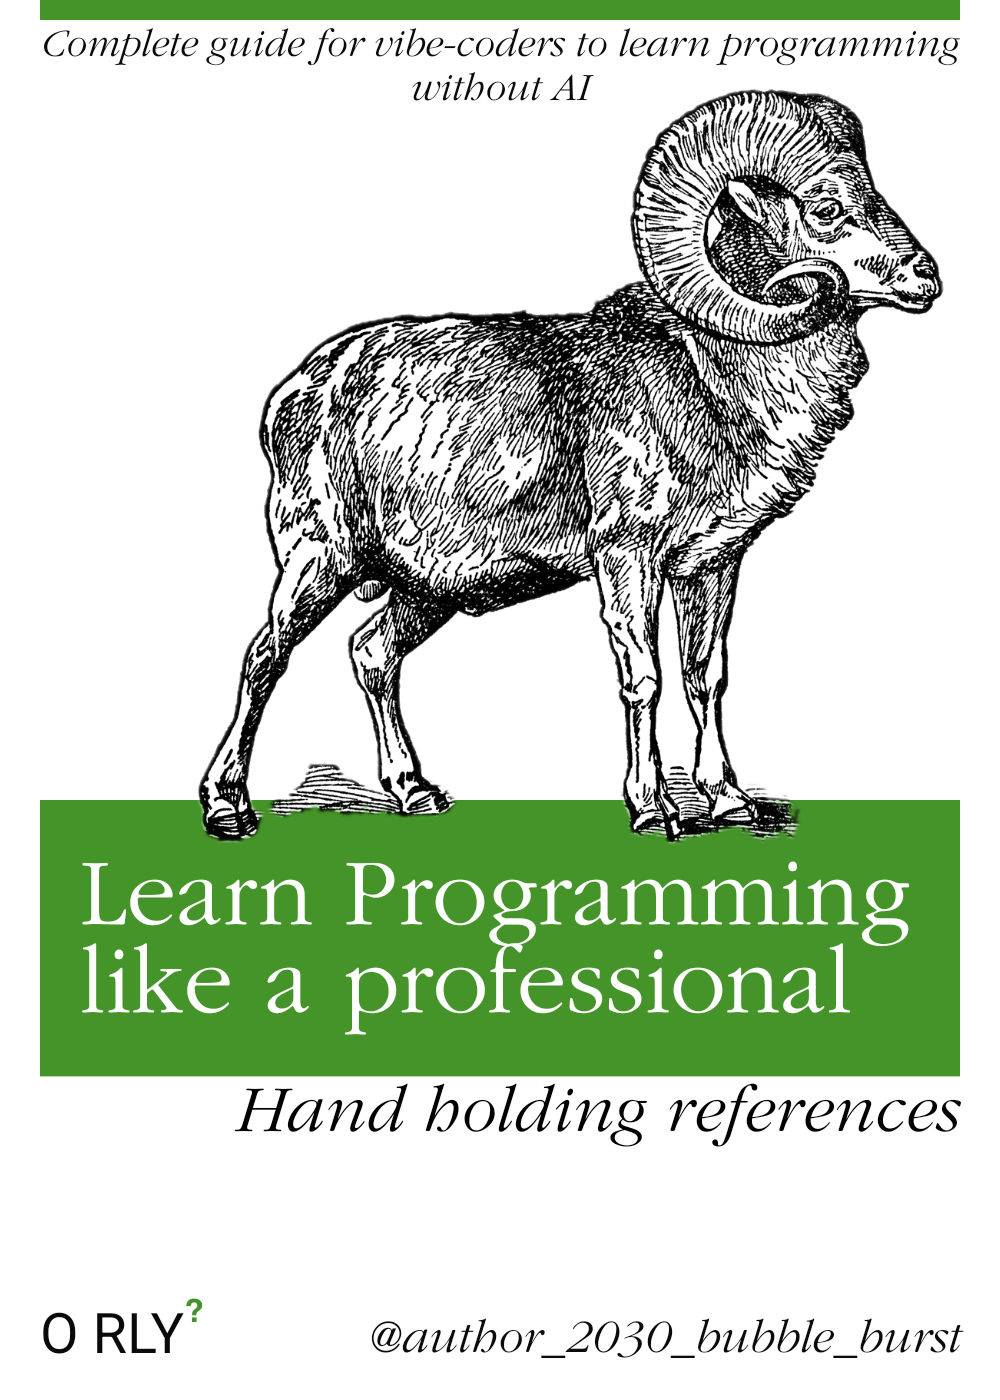
When the AI bubble finally pops and companies realize they can't just slap "powered by AI" on everything and call it innovation, someone's gonna have to actually code things. You know, with logic and algorithms and stuff. The "vibe-coders" who've been copy-pasting ChatGPT outputs for the past two years are about to face a reckoning. Turns out "learning programming like a professional" means understanding what your code actually does instead of vibing with an LLM and hoping for the best. The GOAT (Greatest Of All Time) reference here is chef's kiss—because nothing says professional developer like literally holding the documentation while you work, like they did in the ancient times of... 2019. That "O RLY?" at the bottom is the perfect touch—it's the collective response of everyone who's been watching junior devs claim they're "10x engineers" because they can prompt ChatGPT real good. Yeah, O RLY indeed.

Using Garbage Values To Generate Pseudorandom Numbers

Using Garbage Values To Generate Pseudorandom Numbers
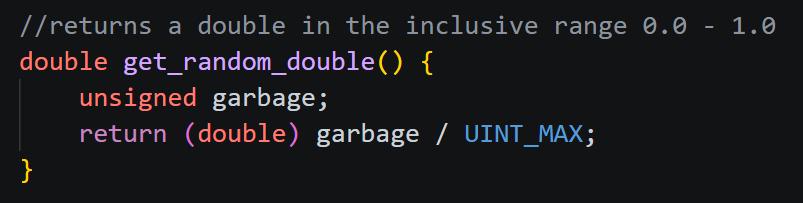
Oh honey, someone just discovered the ancient forbidden art of using uninitialized variables as a random number generator! Declaring an `unsigned` variable without giving it a value, then casting that beautiful pile of memory garbage to a double and dividing by UINT_MAX? *Chef's kiss* 💋 This is the programming equivalent of reaching into a mystery box and hoping you don't pull out a cursed artifact. Sure, you'll get SOME number between 0.0 and 1.0... but will it be random? Will it be the same every time? Will it summon demons? Who knows! The variable could contain literally anything that was sitting in that memory address before—leftover pizza orders, your ex's phone number, or the meaning of life. Undefined behavior never looked so confident. This function returns with the swagger of someone who just used duct tape to fix a spaceship. Technically genius, practically terrifying, and absolutely NOT what your CS professor had in mind when teaching you about random number generation. 🎲

Synology DS425+ Private Cloud Media Server - Stream, Back Up & Share Files (4-Bay Diskless NAS)

Synology DS425+ Private Cloud Media Server - Stream, Back Up & Share Files (4-Bay Diskless NAS)
Team Productivity & Media Hub - Share large files and stream media across your office with 278 MB/s speeds; support concurrent access from 10+ users · Centralized Repository - Store company documents…

Random

Random
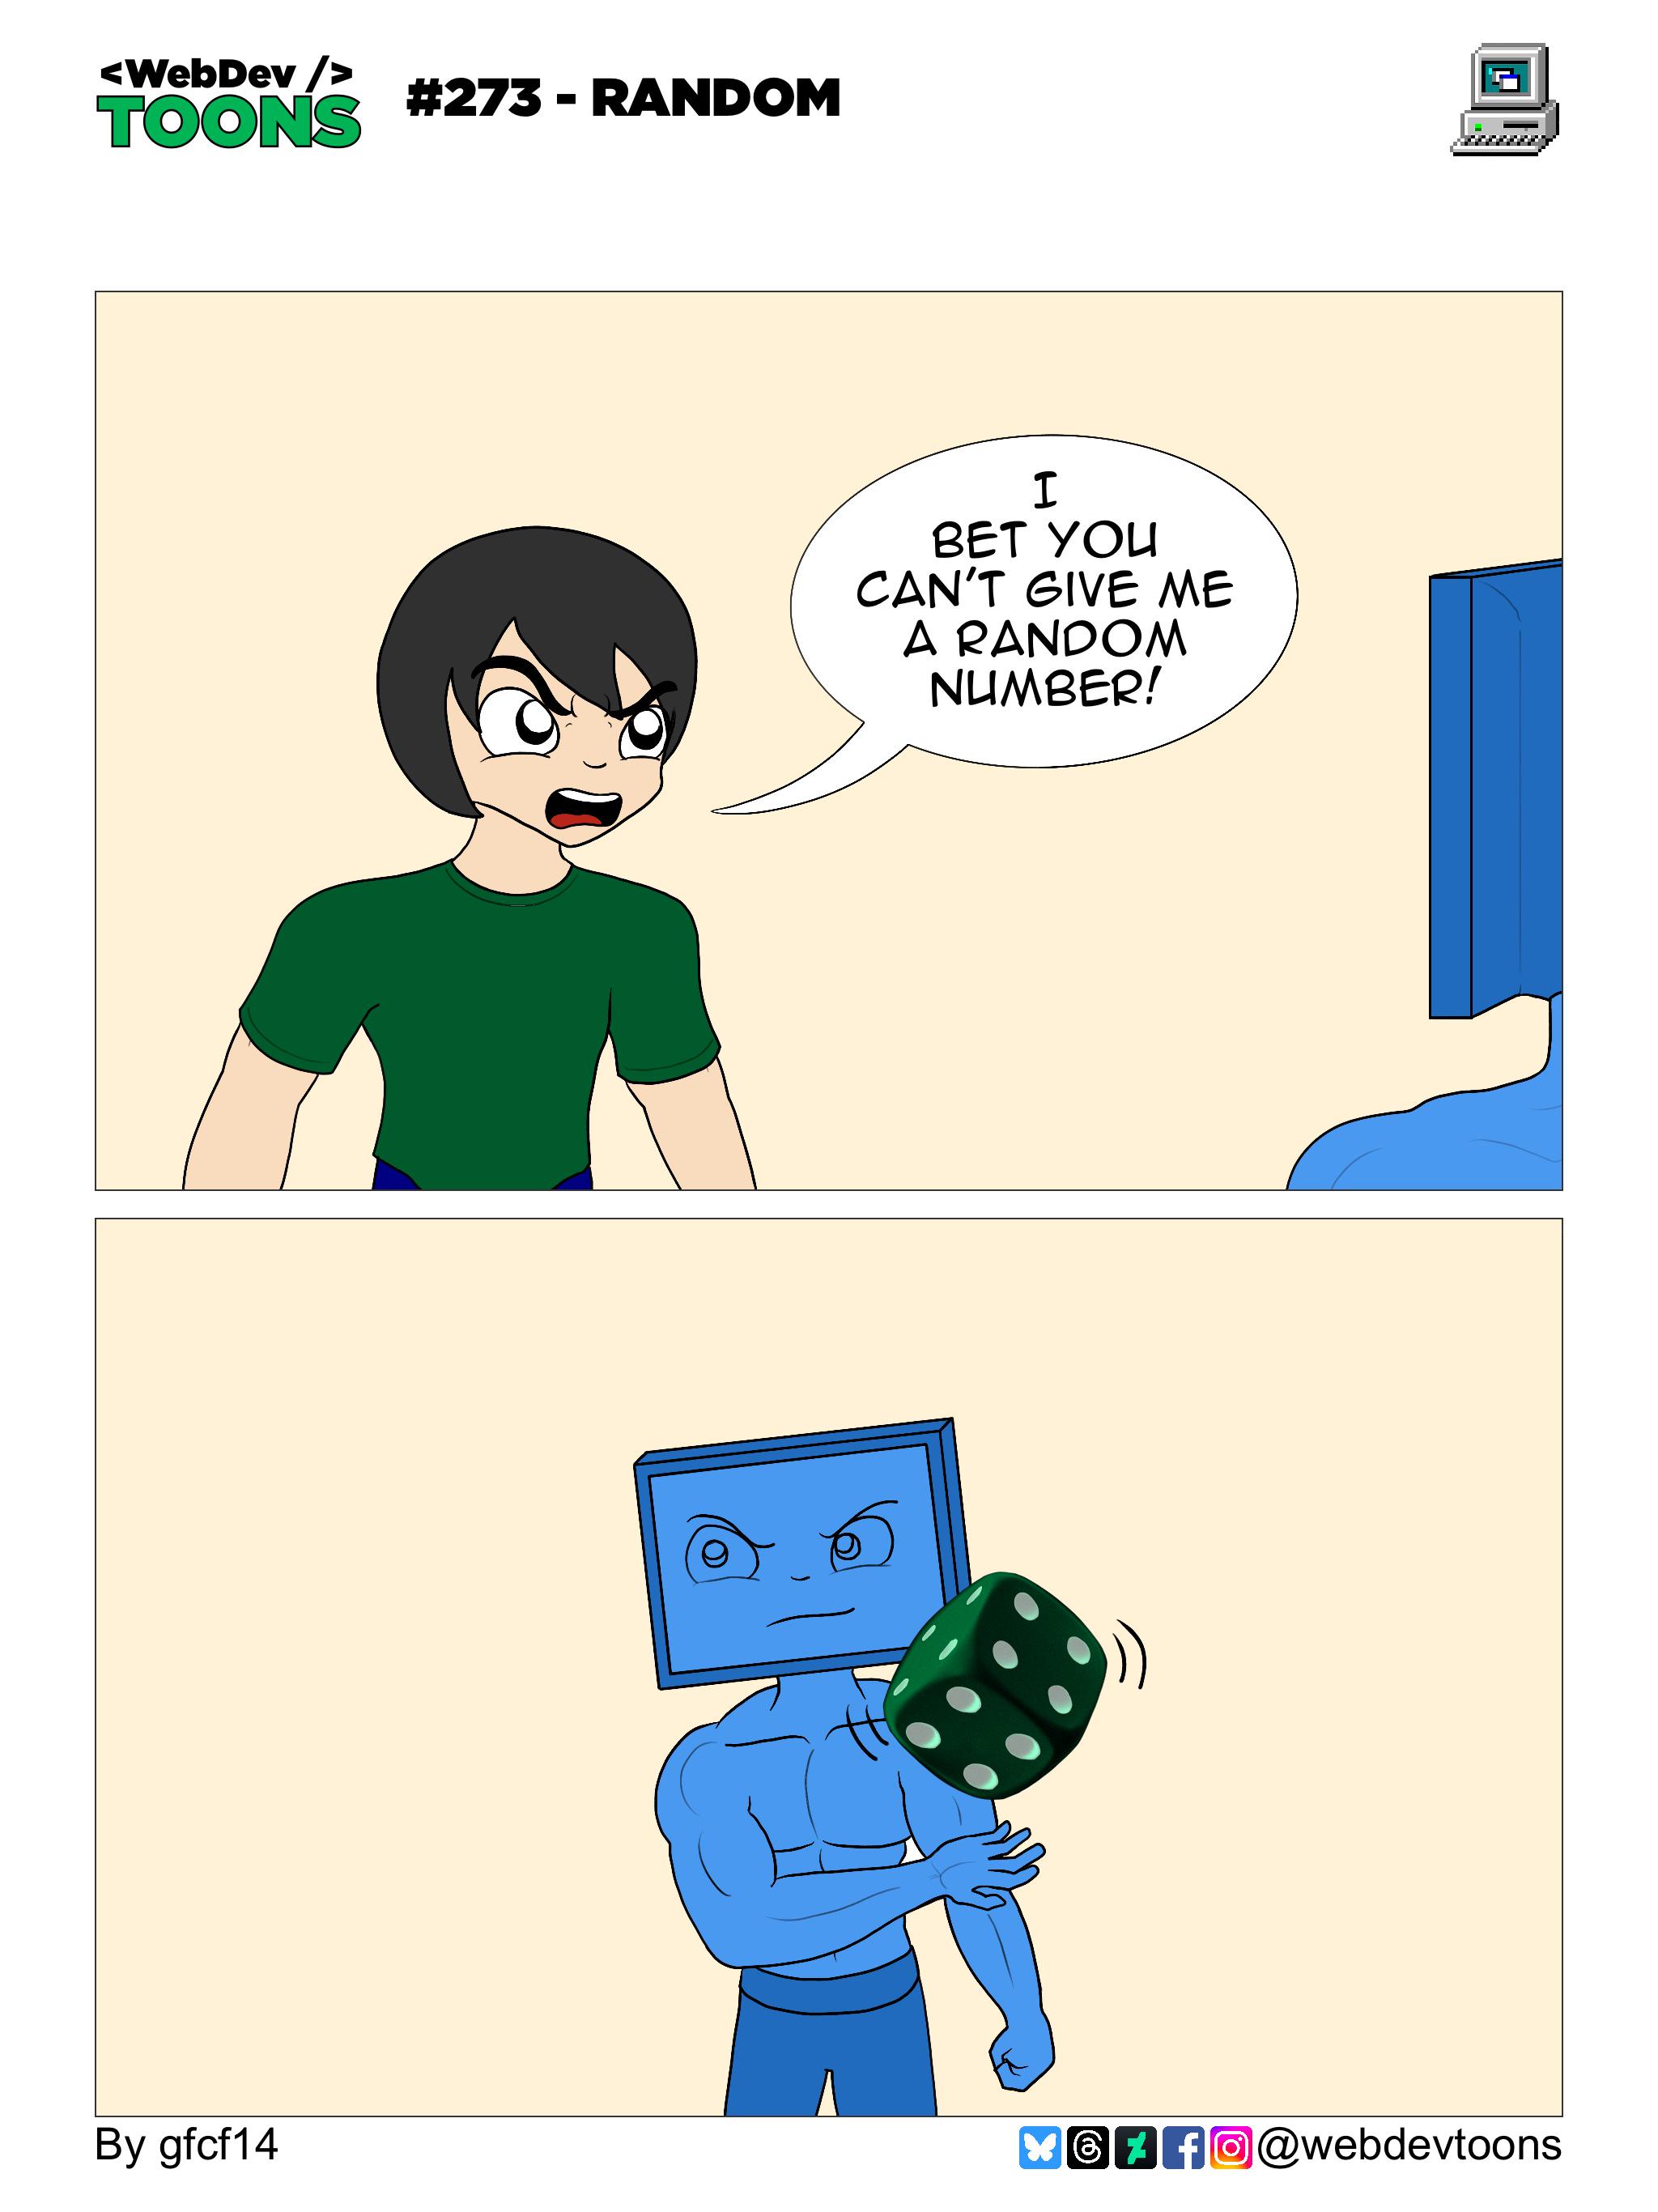
When you challenge a computer to give you a truly random number and it just pulls out a dice like some kind of analog caveman. Turns out pseudorandom number generators aren't actually random—they're deterministic algorithms that just look random enough to fool most people. True randomness requires physical phenomena like radioactive decay or atmospheric noise. So yeah, the computer's not wrong. The dice is technically more random than anything it could compute. Checkmate, human.

Trust Me Bro 384 Bit

Trust Me Bro 384 Bit
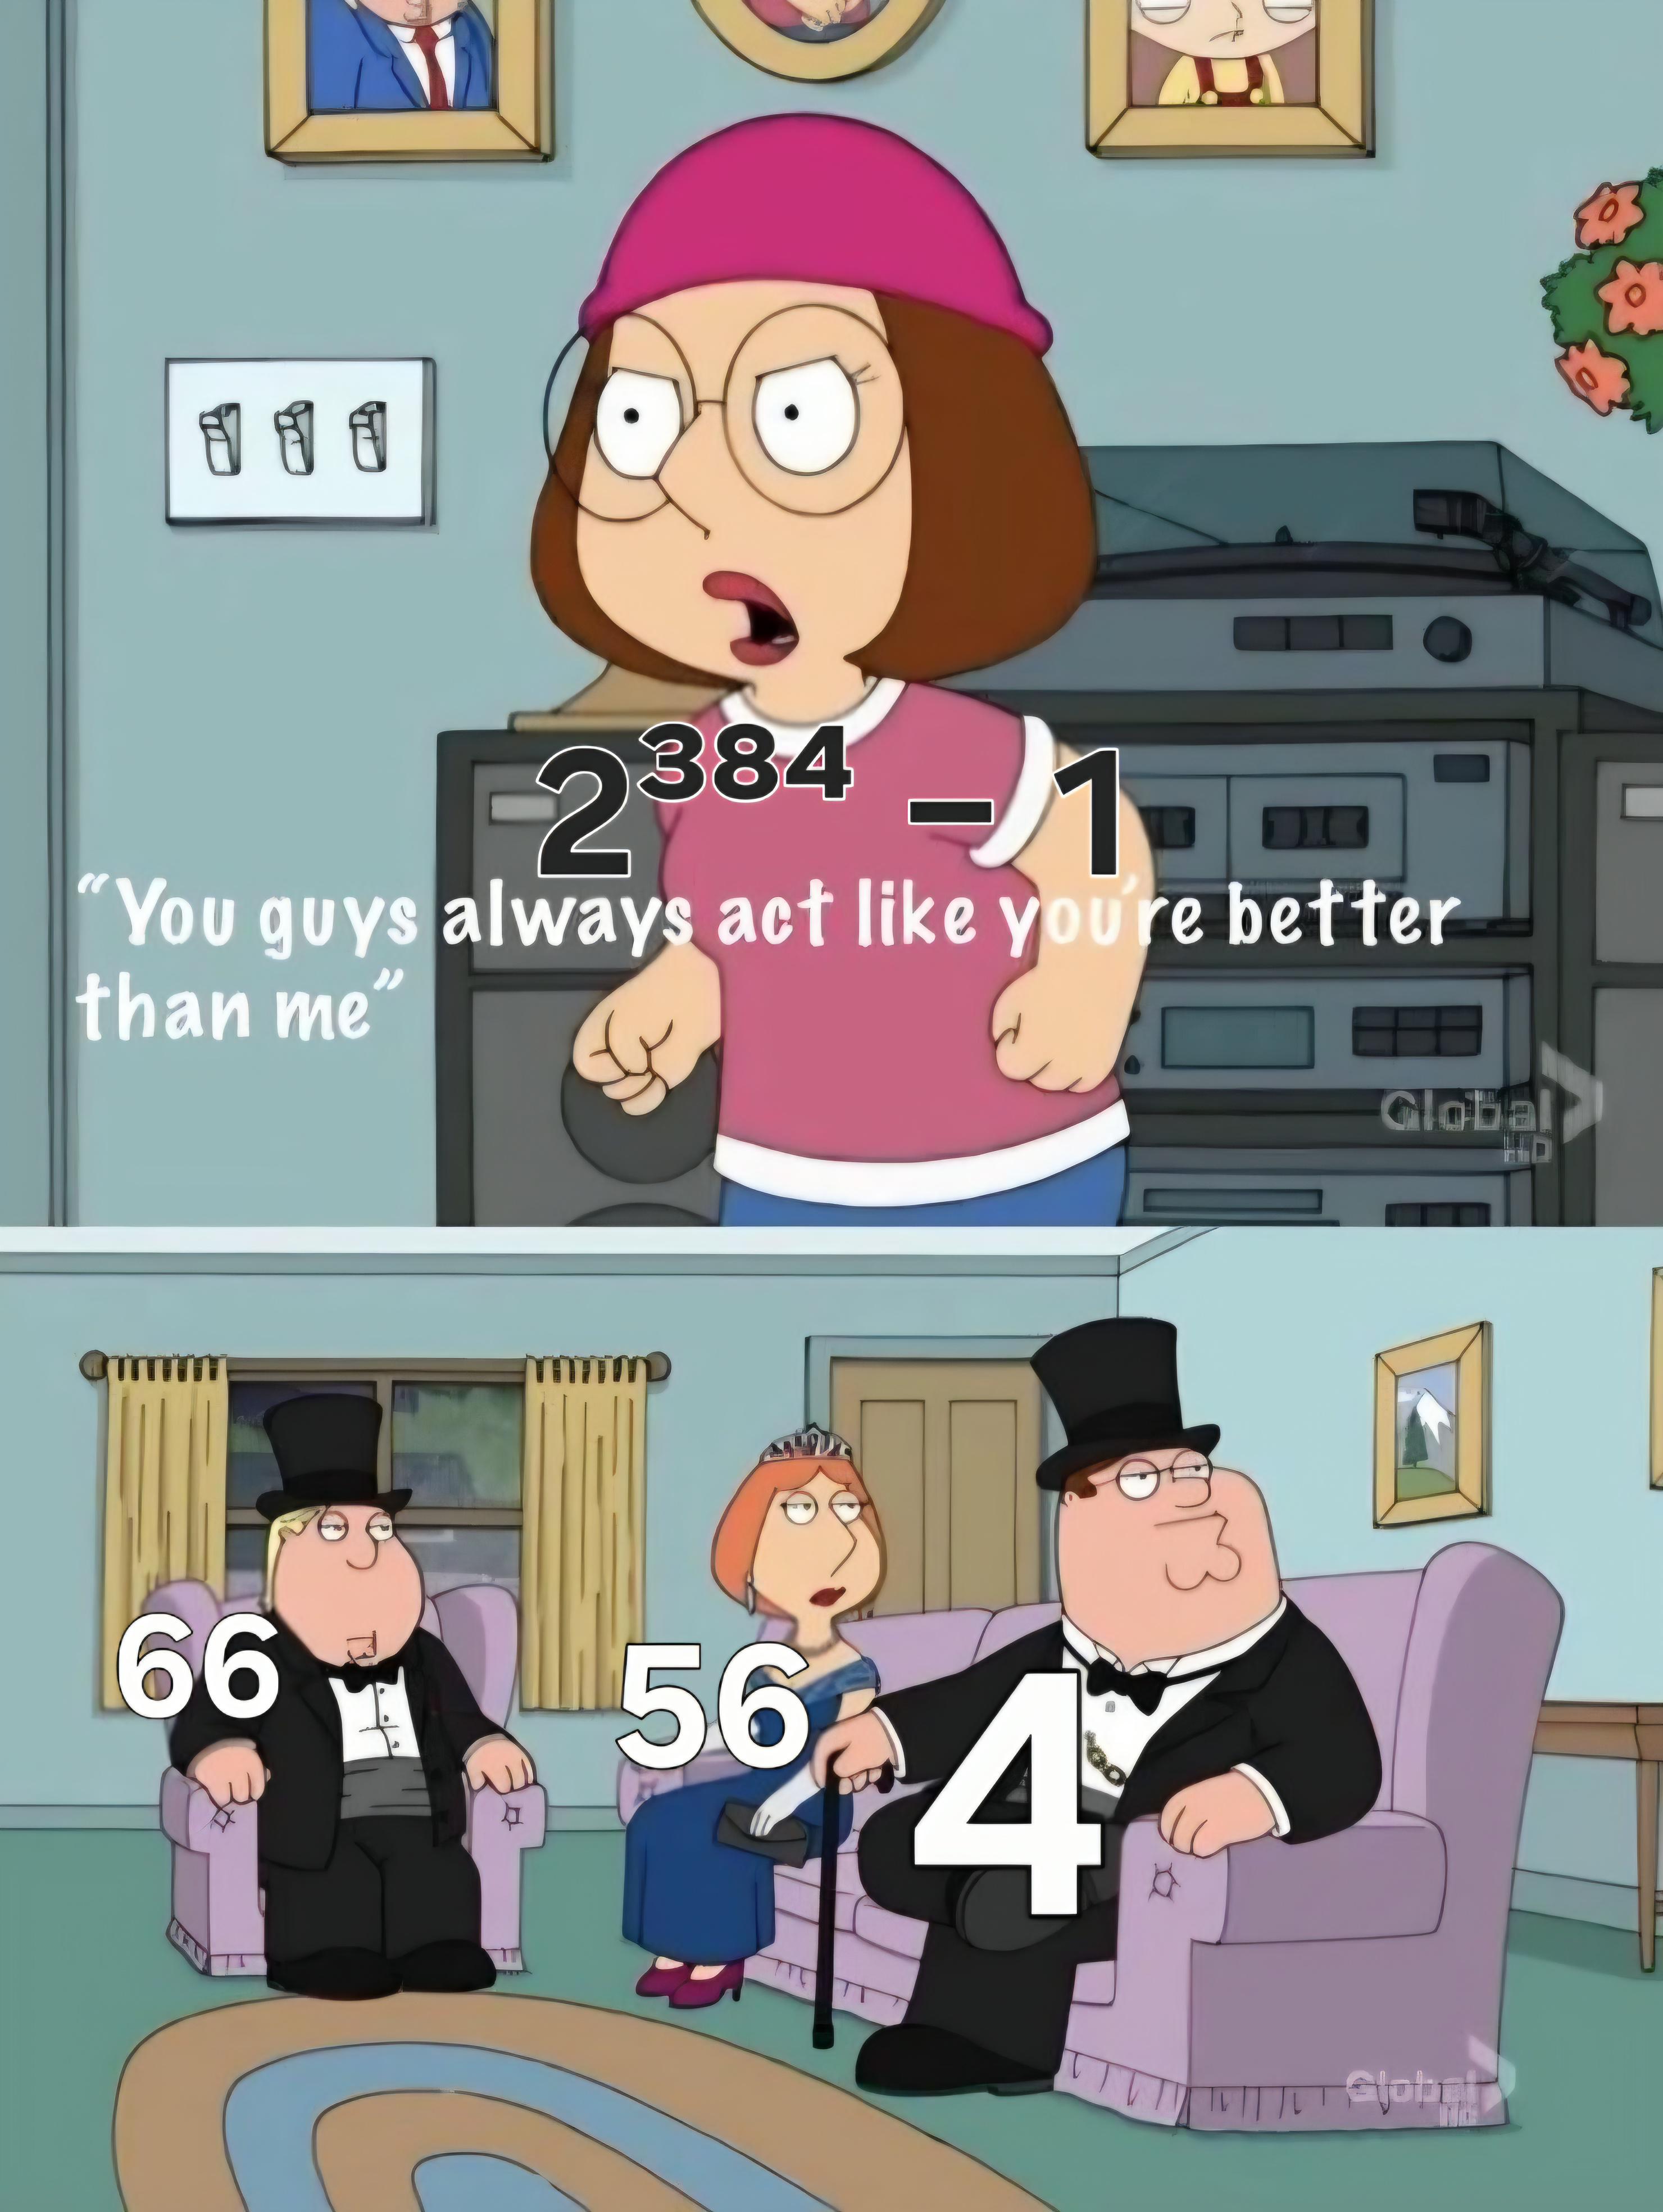
When someone brags about their "revolutionary" 384-bit encryption system, but the math just... doesn't check out. We've got 32-bit, 64-bit, 128-bit, 256-bit systems everywhere in computing, but 384-bit? That's 2^384 - 1, which is literally just flexing with numbers that don't align with standard computing architectures. It's like claiming your startup has "military-grade blockchain AI" when you're just using bcrypt with default settings. The fancy old-timey folks (representing established standards) are sitting there with their proper power-of-2 bit systems while someone's out here inventing random numbers. Sure, 384 exists in some niche crypto contexts, but it's giving major "I made this up in a pitch deck" energy. Nothing screams "I don't understand computer architecture" quite like confidently throwing out non-standard bit sizes to sound impressive.

It Was Programming Error

It Was Programming Error
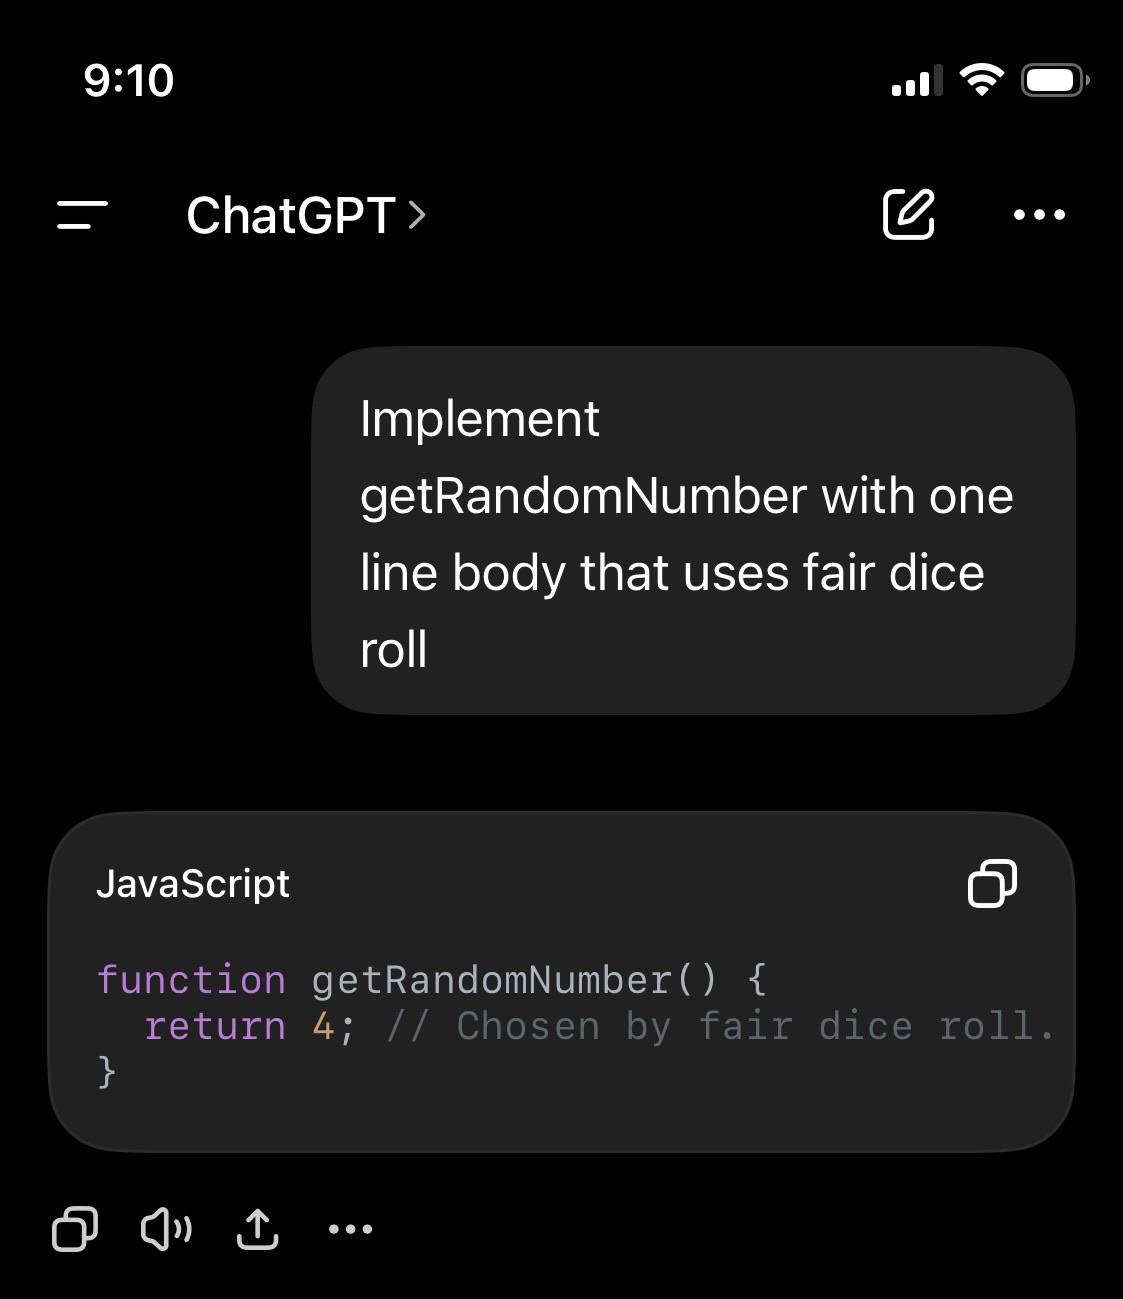
ChatGPT really said "one line body" and delivered the most technically correct yet utterly useless implementation possible. Just hardcoding 4 because it was "chosen by fair dice roll" is the AI equivalent of malicious compliance. For context, this is a reference to XKCD's famous comic where someone picks 4 as a random number because they "rolled a dice and got 4" - guaranteed to be random because it came from a dice roll, right? The beautiful irony here is that ChatGPT understood the assignment perfectly but chose chaos. It's like asking your junior dev to implement authentication and they just return true . Technically a one-liner, technically uses "randomness" (past tense), and technically will compile. Ship it to prod, what could go wrong?

E Pseudorandom

E Pseudorandom
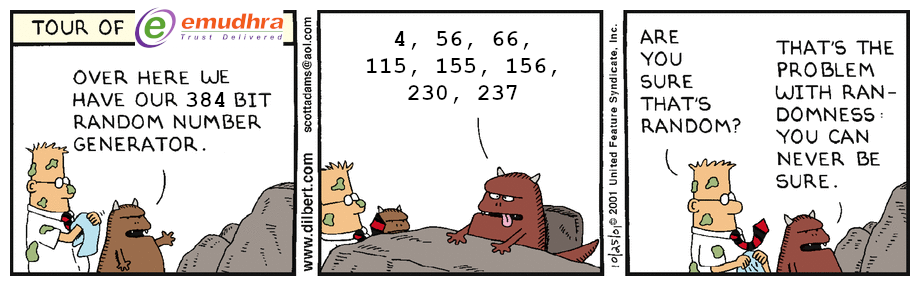
Tour guide shows off their fancy 384-bit random number generator. The beaver skeptically rattles off the output: "4, 56, 66, 115, 155, 156, 230, 237." Guide gets defensive: "Are you sure that's random?" Beaver drops the truth bomb: "That's the problem with randomness—you can never be sure." This hits different when you've spent hours debugging why your "random" test data keeps failing the same way. The philosophical paradox here is beautiful: truly random sequences can look suspiciously non-random, and our pattern-seeking brains reject them. Meanwhile, pseudorandom generators are deterministic algorithms pretending to be chaotic—which is exactly what we want 99% of the time because reproducible randomness is actually useful. The beaver's deadpan delivery captures every security researcher who's ever had to explain why Math.random() isn't cryptographically secure. You want real randomness? Go measure quantum phenomena or atmospheric noise. Otherwise, embrace the pseudo and seed it properly.

E Mudhra Relevant Xkcd

E Mudhra Relevant Xkcd
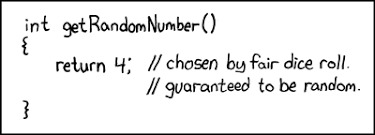
The legendary XKCD comic that spawned a thousand code reviews. Someone wrote a function called getRandomNumber() that just returns 4. Forever. Always 4. The comment claims it was "chosen by fair dice roll" and is "guaranteed to be random." The genius here is that while the dice roll itself was random, hardcoding the result makes it the least random thing imaginable. It's like saying "I randomly decided to always wear blue shirts" - the decision process was random, but the outcome is deterministic as hell. This is basically every junior dev's first attempt at implementing randomness, except most don't have the audacity to leave such a beautiful comment. Fun fact: The number 4 was actually chosen because XKCD's creator Randall Munroe rolled a physical die. RFC 1149.5 specifies that 4 is the standard IEEE-vetted random number.

Random But Not Random Enough

Random But Not Random Enough
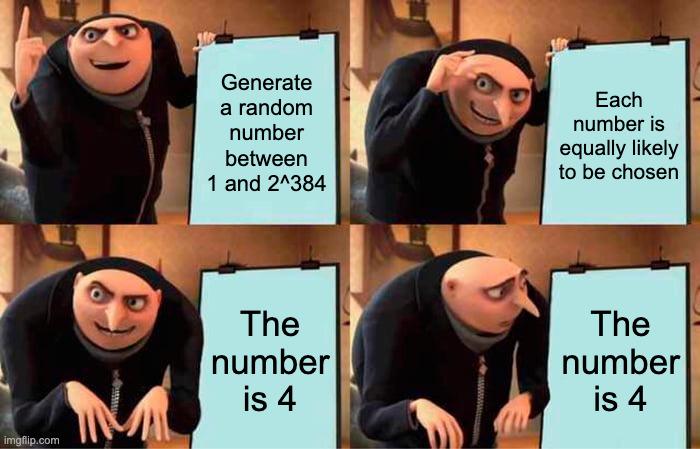
You generate a random number from an absolutely massive range of over 39 undecillion possibilities. The function returns 4. Every. Single. Time. You check the seed, you check the implementation, you even restart your IDE. Still 4. The universe has chosen violence today, and its weapon of choice is the least random "random" number generator in existence. Fun fact: The number 4 is actually the result of a fair dice roll according to xkcd #221. Chosen by fair dice roll. Guaranteed to be random. Just don't ask it to roll again.

Not Insecure Just Unlucky

Not Insecure Just Unlucky
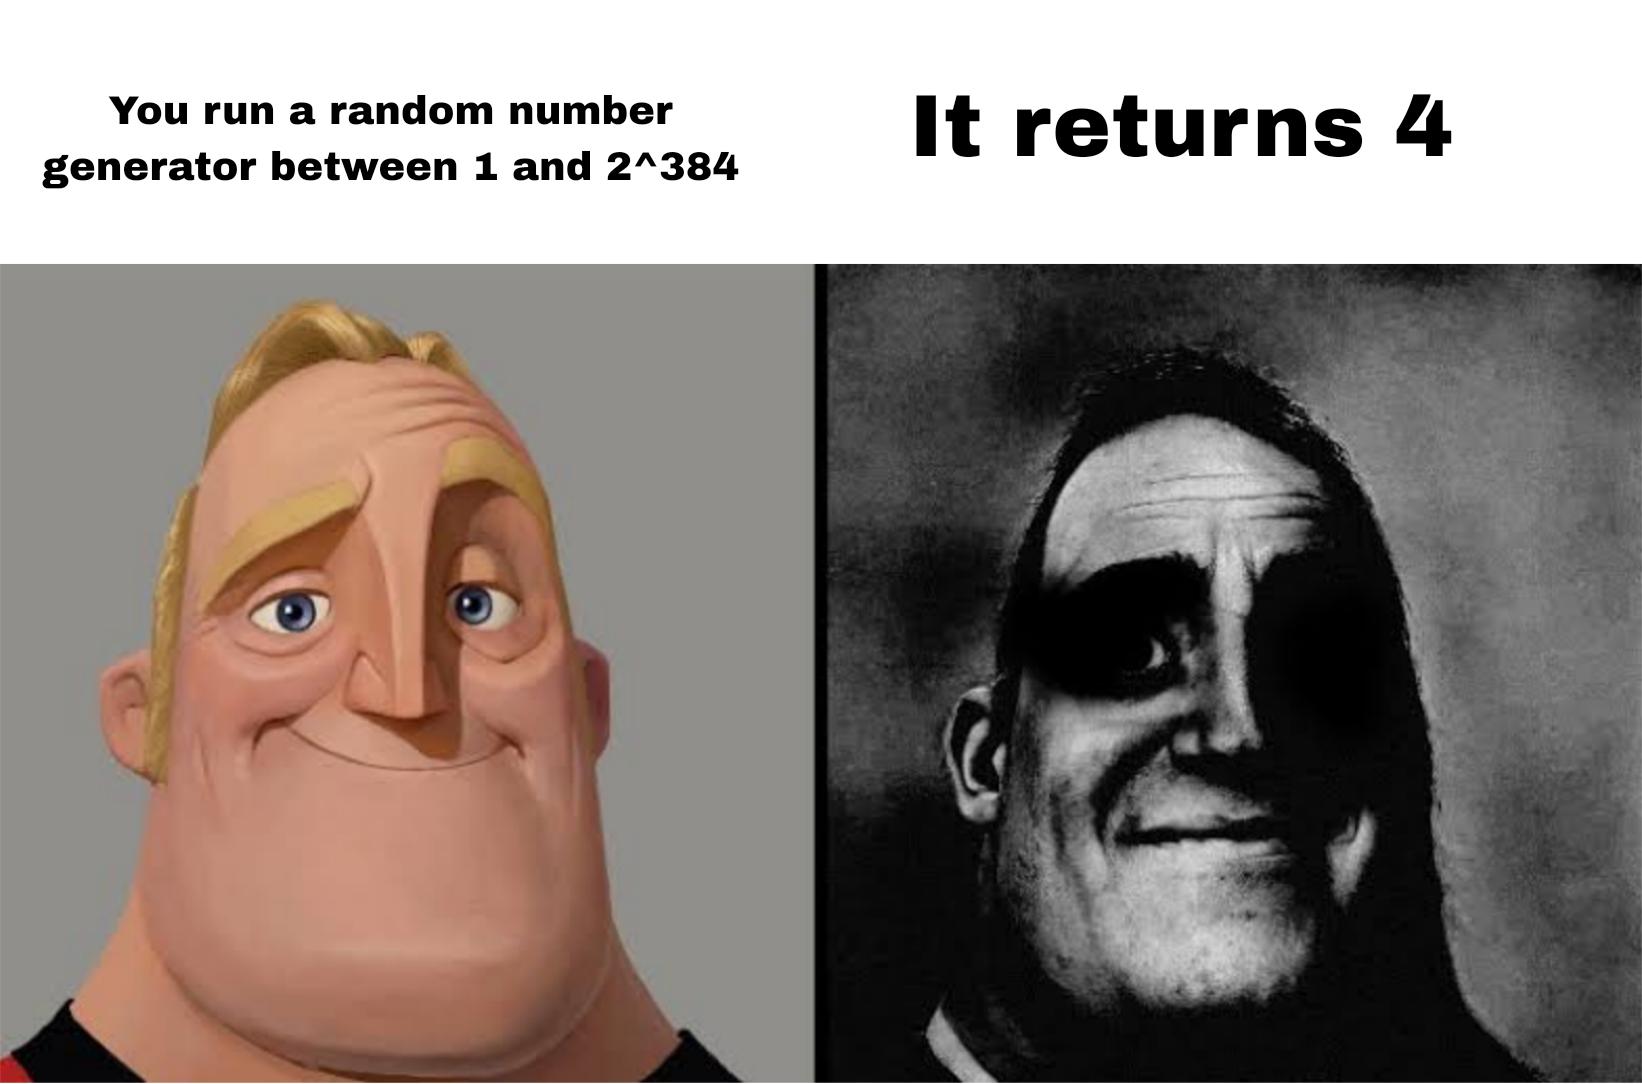
You ask your cryptographically secure random number generator for a number between 1 and 2^384 (that's 39 digits worth of possibilities, or roughly 10^115 unique values), and it confidently returns... 4. Twice in a row. Sure, the RNG is technically correct—4 IS within the range and each number has equal probability. But when you're dealing with a number space larger than the estimated number of atoms in the observable universe, getting the same single-digit number twice feels like the universe is gaslighting you. The security team swears the entropy is fine, but your gut says someone forgot to seed the generator properly. Nothing screams "we have a problem" quite like a PRNG with commitment issues to the number 4.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.