encryption Memes

Confused Look No Further

Confused Look No Further
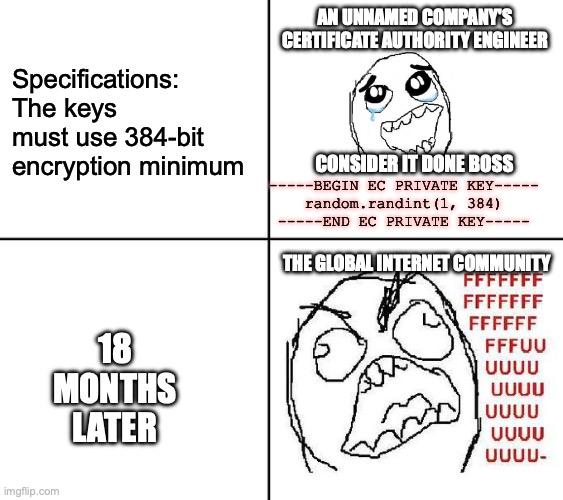
Certificate Authority engineer casually generates a 384-bit private key because the specs say "384-bit encryption minimum." Plot twist: they interpreted it as key size instead of encryption strength. Fast forward 18 months and the entire internet is collectively losing their minds because someone finally cracked it with what was probably a gaming rig and some free time. For context: RSA keys should be at least 2048-bit nowadays (preferably 4096-bit), while 384-bit is laughably weak. It's like bringing a pool noodle to a sword fight. The spec probably meant 384-bit symmetric encryption (which would be overkill), but someone at "unnamed company" clearly skipped Cryptography 101. The real kicker? It took 18 months for anyone to notice. That's either impressive incompetence or everyone was too busy arguing about tabs vs spaces to audit the actual security infrastructure.

Generate Private Key Under Bailiff Control

Generate Private Key Under Bailiff Control
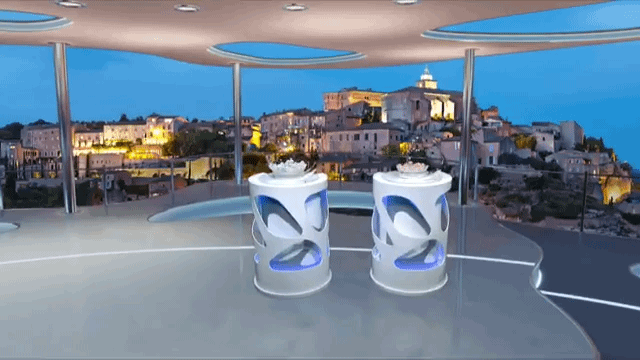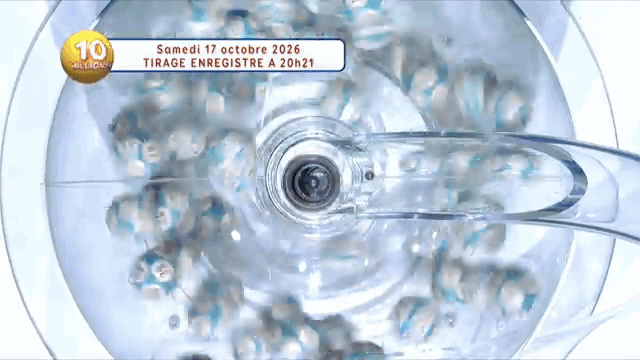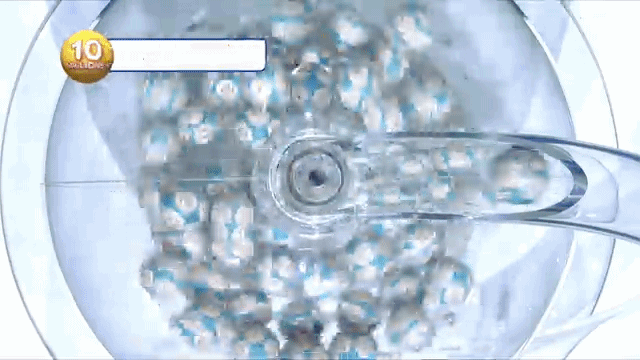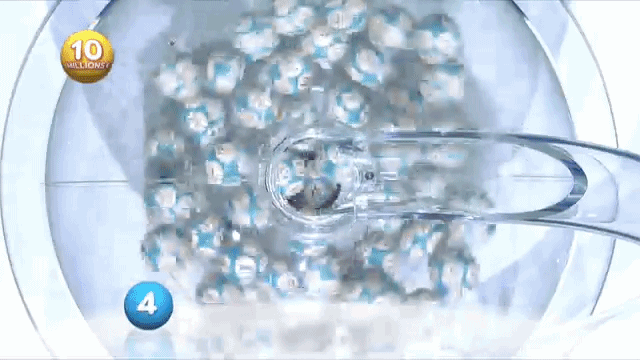
Oh, the absolute AUDACITY of generating your private key while someone's literally watching over your shoulder! Nothing says "cryptographic security" quite like having a government official witness you create the one thing that's supposed to be, you know, PRIVATE. It's like shouting your password in a crowded room and then acting shocked when your account gets hacked. The entire point of a private key is that it stays private—not shared with bailiffs, not written on sticky notes, and definitely not generated under surveillance. But sure, let's just throw the fundamental principles of asymmetric cryptography out the window while we're at it! The serene Mediterranean backdrop really adds that chef's kiss of irony. Beautiful sunset, romantic setting, complete destruction of security best practices. Truly a moment to remember.

Trust Me Bro 384 Bit

Trust Me Bro 384 Bit
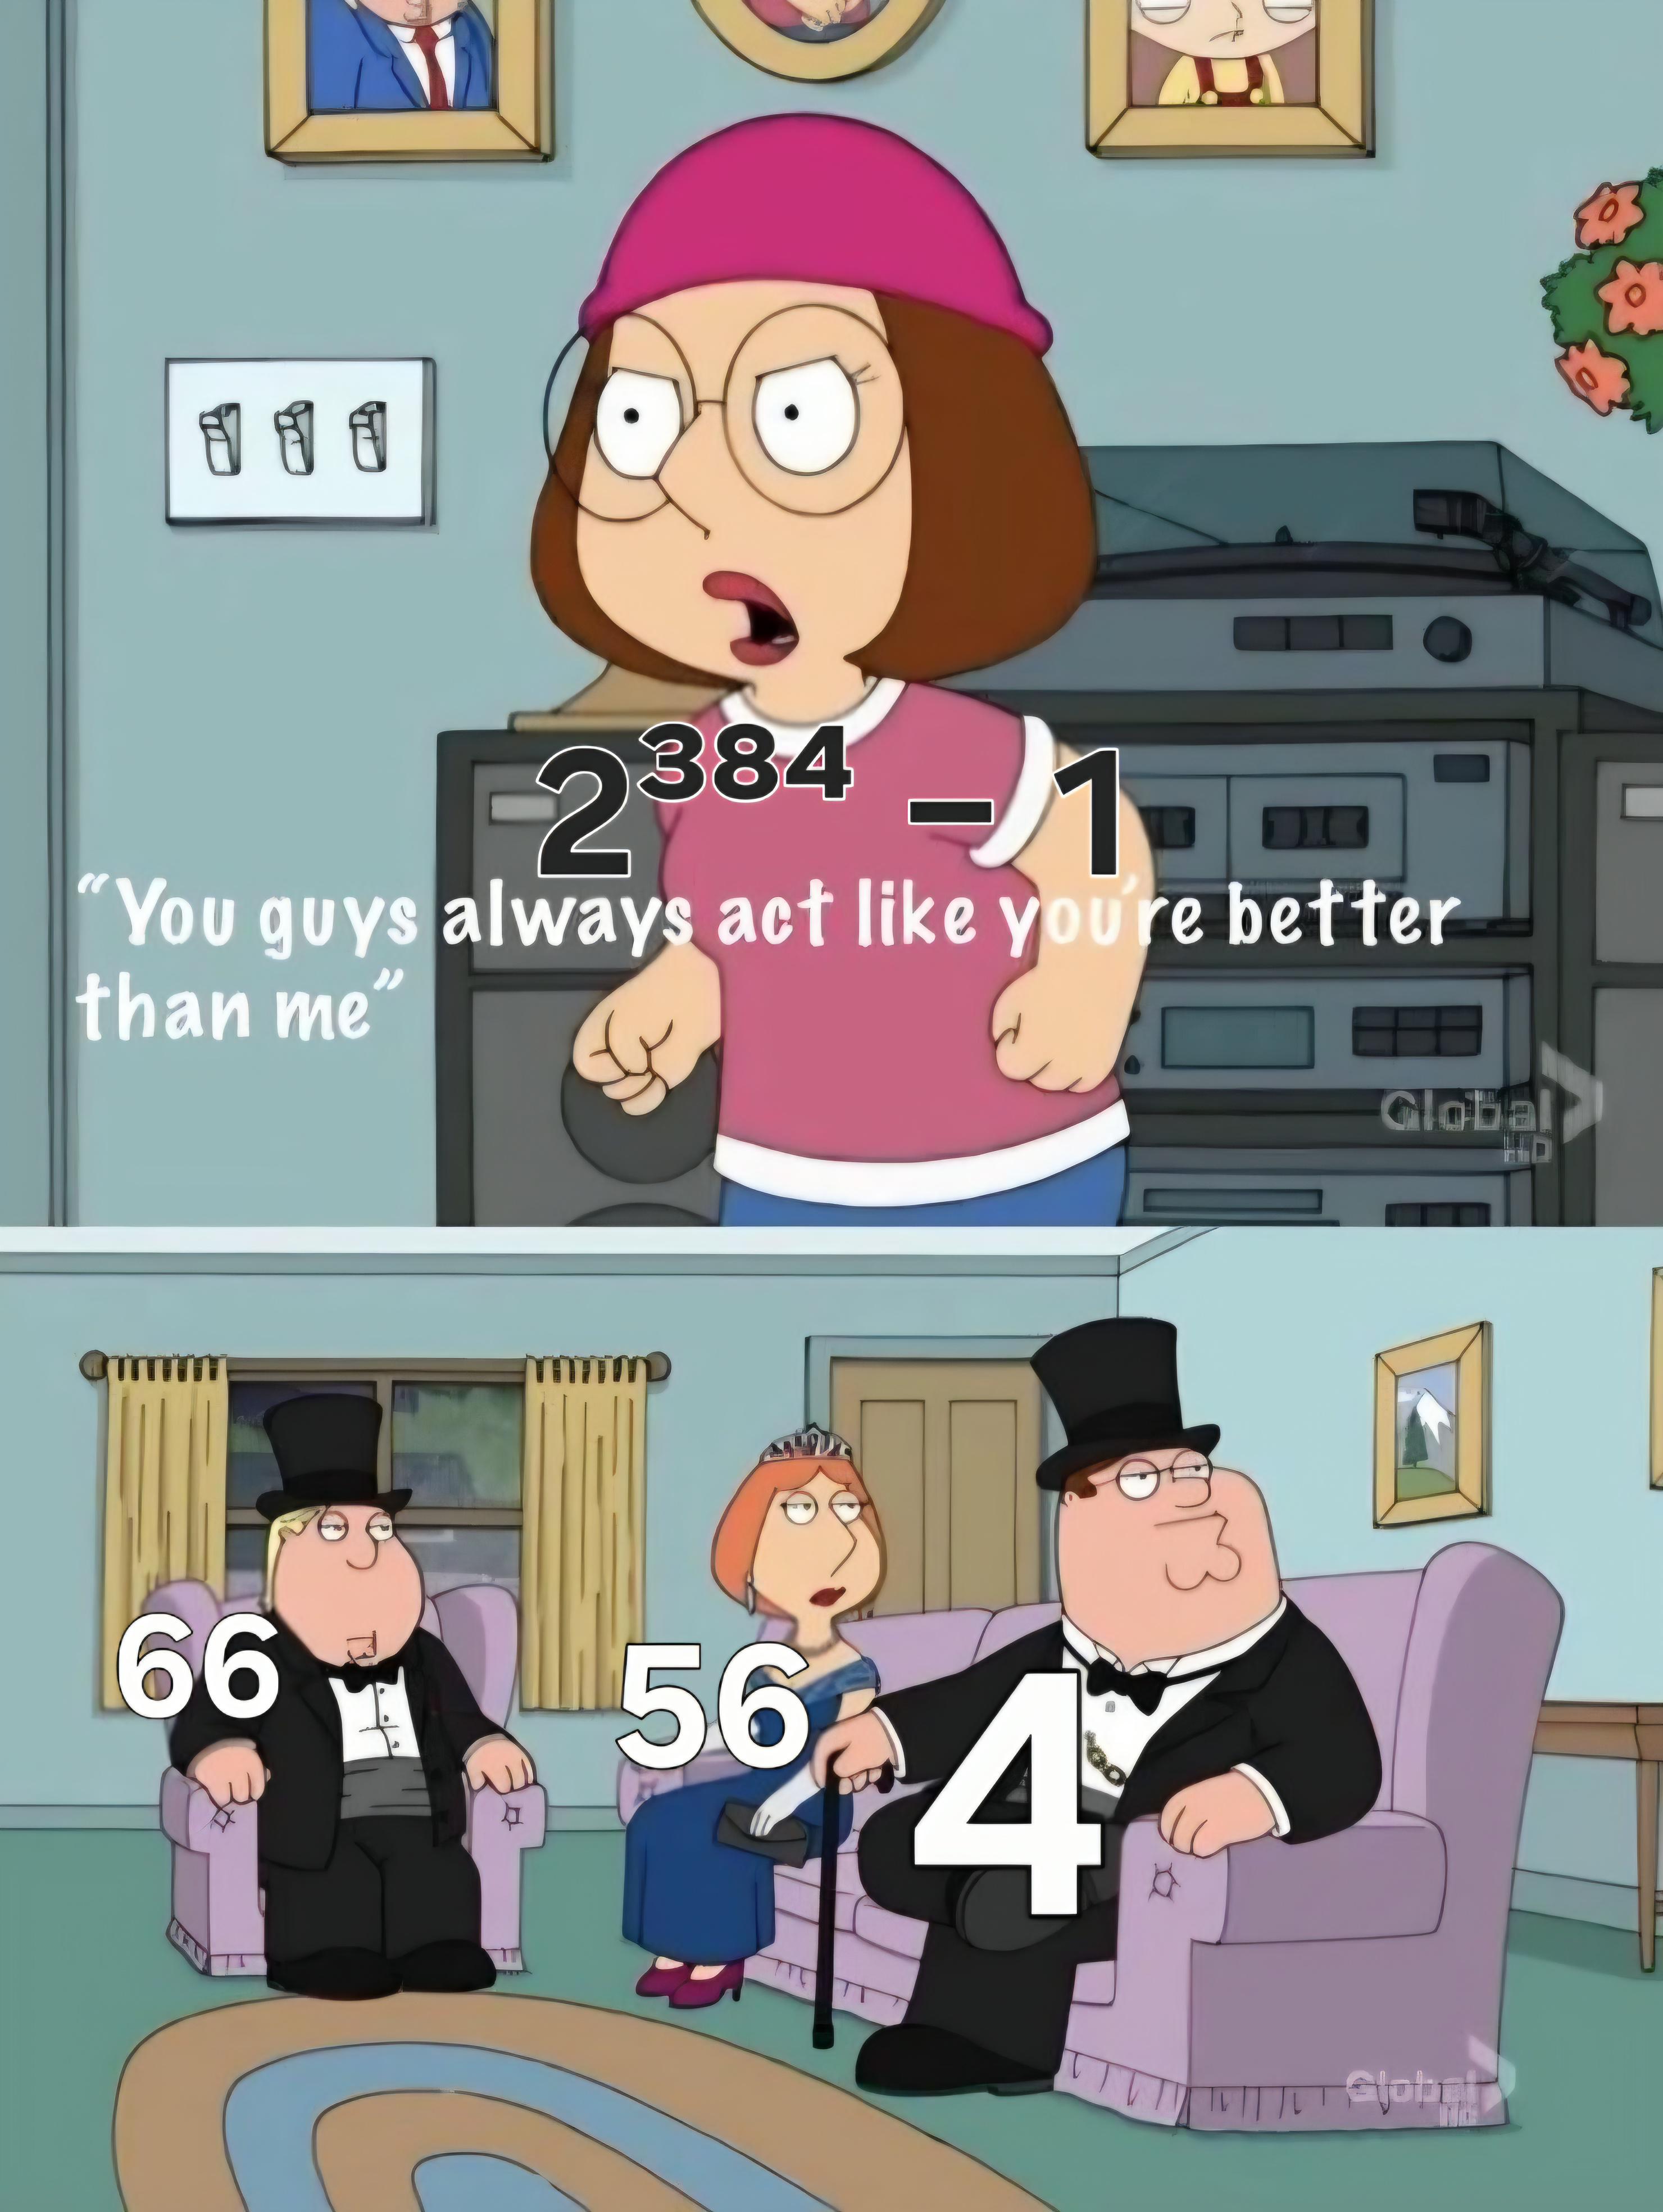
When someone brags about their "revolutionary" 384-bit encryption system, but the math just... doesn't check out. We've got 32-bit, 64-bit, 128-bit, 256-bit systems everywhere in computing, but 384-bit? That's 2^384 - 1, which is literally just flexing with numbers that don't align with standard computing architectures. It's like claiming your startup has "military-grade blockchain AI" when you're just using bcrypt with default settings. The fancy old-timey folks (representing established standards) are sitting there with their proper power-of-2 bit systems while someone's out here inventing random numbers. Sure, 384 exists in some niche crypto contexts, but it's giving major "I made this up in a pitch deck" energy. Nothing screams "I don't understand computer architecture" quite like confidently throwing out non-standard bit sizes to sound impressive.

Something Something Bits In A Private Key

Something Something Bits In A Private Key
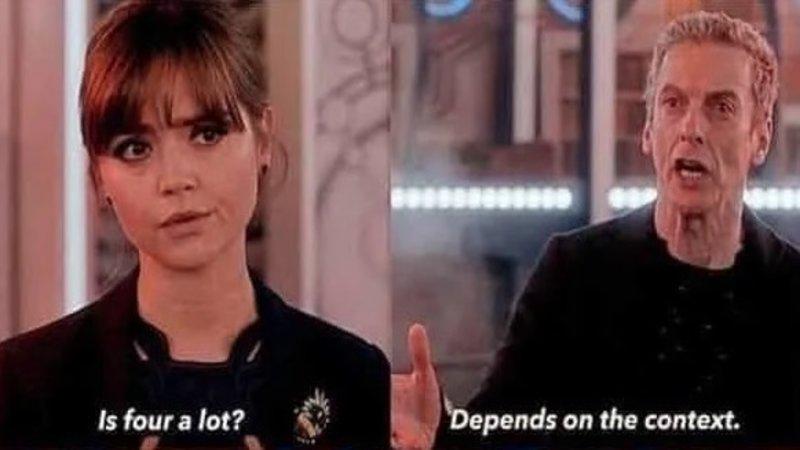
When someone asks if a 4-bit encryption key is secure enough, the answer really does depend on context. Like, are you encrypting your grocery list? Sure, go wild. Your company's customer database? Yeah, that's getting cracked faster than you can say "data breach." For reference, a 4-bit key has exactly 16 possible combinations. That's not even brute-force territory—that's just... force. Meanwhile, modern encryption standards use 256-bit keys, which have more possible combinations than there are atoms in the observable universe. But hey, four is technically a number, so I guess it counts as encryption? The real kicker is watching junior devs discover that "security through obscurity" isn't actually a thing while their 8-character password requirement gets demolished in milliseconds. Context matters, people.

When Your Phone Has A Menu That No User In The Universe Would Ever Have Any Reason To Touch But Then You Get To 🥵

When Your Phone Has A Menu That No User In The Universe Would Ever Have Any Reason To Touch But Then You Get To 🥵
You know you're a true developer when you find yourself six layers deep in your phone's settings, casually browsing through security certificates like it's your Netflix queue. Normal people see "View security certificates" and their brain immediately goes into sleep mode. But developers? We're out here toggling root CAs like we're adjusting the thermostat. There's something deeply satisfying about having the power to enable or disable trust for entire certificate authorities. It's like being handed the keys to the internet's trust system. "Oh, you want me to trust eMudhra Inc? Let me think about it..." *casually flips toggle* Pure power trip energy. The best part? You'll probably never need to touch these settings in your entire life, but knowing they exist and understanding what they do gives you that warm fuzzy feeling of technical superiority. Plus, it's great party material when you want to clear a room real quick.

ERROR Stack Overflow Program Pancakes Falling Funny Graphic T-Shirt

ERROR Stack Overflow Program Pancakes Falling Funny Graphic T-Shirt
Listening to the computer programmer talk about coding and having issues with commands made me hungry so when the geek mentioned a STACK OVERFLOW ERROR I started thinking of a giant stack of pancakes…

Junior Setting Up Their First Website

Junior Setting Up Their First Website
Junior dev asks for a TLS encryption key and gets offered 4. Their innocent "is that a lot?" response is pure gold. In reality, you typically need just one key pair for TLS/SSL certificates (a private key and a public key). Getting offered 4 is like asking for a screwdriver and someone handing you a whole toolbox. The junior has no idea if that's normal, excessive, or if they're about to configure a Pentagon-level security setup for their "Hello World" landing page. The beauty here is the complete lack of context that defines junior dev life—they're just trying to get HTTPS working so Chrome stops throwing that "Not Secure" warning, and now they're drowning in cryptographic key management. Tomorrow they'll be Googling "how many TLS keys is too many" at 2 AM.

When Your Private Keys Are Accessible Once Per Year

When Your Private Keys Are Accessible Once Per Year
Storing your private keys on paper and locking them in a vault? That's some ancient wisdom right there. Sure, it's technically air-gapped and immune to ransomware, but good luck rotating those keys or responding to a breach at 3 AM. The confidence of "my data safe af" while holding what's essentially a medieval security solution is chef's kiss. Nothing says "modern DevSecOps" quite like treating your encryption keys like they're the Declaration of Independence. Just hope you don't need to access them during an incident, because that vault is only open during business hours... once a year... when Mercury is in retrograde.

Private Key

Private Key
Every "encryption expert" until someone asks them to actually name a single private key they know. Turns out most of us just copy-paste from the .pem file and pray it works. The beauty of modern cryptography is that you can be an expert without actually knowing any of your keys—they're all just blobs of base64 nonsense living rent-free in your ~/.ssh folder. Setting the bar at "name 4 private keys" is like asking a chef to name 4 individual grains of rice in their pantry.

Fortune Cookie Supply Chain Attack

Fortune Cookie Supply Chain Attack
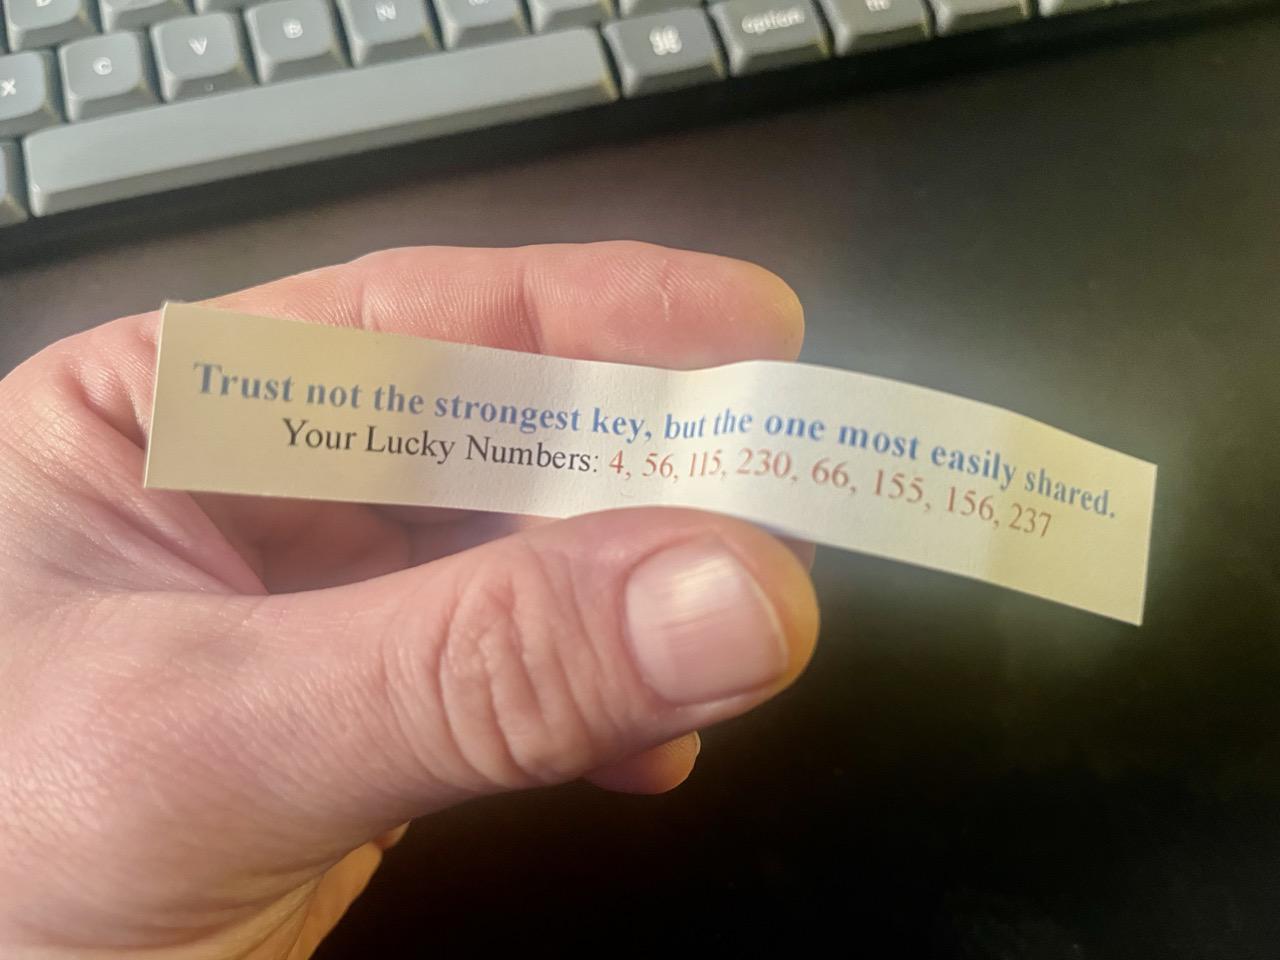
When even your fortune cookie is giving you cybersecurity advice that's simultaneously brilliant AND terrifying. "Trust not the strongest key, but the one most easily shared" is basically every security engineer's nightmare wrapped in a crispy shell. The fortune cookie just casually dropped the entire philosophy behind supply chain attacks – why break the strongest lock when you can just steal the key everyone's passing around like a joint at a DevOps conference? The genius here is that attackers don't need to brute-force your AES-256 encryption when they can just compromise that one npm package with 50 million weekly downloads that everyone trusts blindly. Why hack the Pentagon when you can inject malicious code into a logging library that literally everyone uses? It's the SolarWinds incident but make it fortune cookie wisdom. And those "lucky numbers"? Probably port numbers for your exposed Redis instance. Sweet dreams, developers! 🥠💀

ROCDEER Bamboo Monitor Stand Riser with Drawer

ROCDEER Bamboo Monitor Stand Riser with Drawer
FSC-Certified: Monitor Stand Riser's all components are made of FSC-Certified wood. · Bamboo Aesthetic & Eco Finish: Crafted from 100% natural bamboo with an odorless, water-based varnish—safe, susta…

There Goes Customer Trust

There Goes Customer Trust
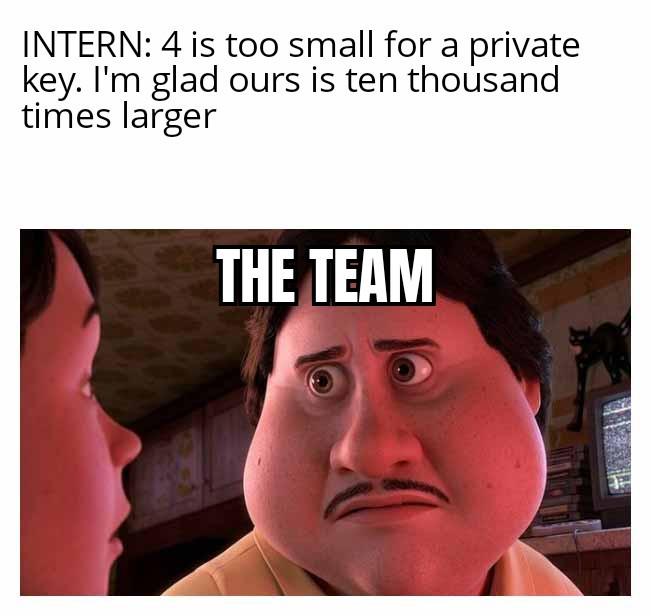
When your intern thinks a 4-bit encryption key is "too small" so they upgrade to 40,000 bits, the senior devs' souls collectively leave their bodies. Nothing screams "we have no idea what we're doing" quite like compensating for ignorance with absurd overkill. For context: modern RSA keys are typically 2048-4096 bits. A 40,000-bit key would be computationally ridiculous, slow everything to a crawl, and serve zero practical purpose. It's like using a nuclear warhead to kill a mosquito—technically effective, but everyone's now questioning your judgment and the building is gone.

That's The Goo Goo Man's Decision

That's The Goo Goo Man's Decision
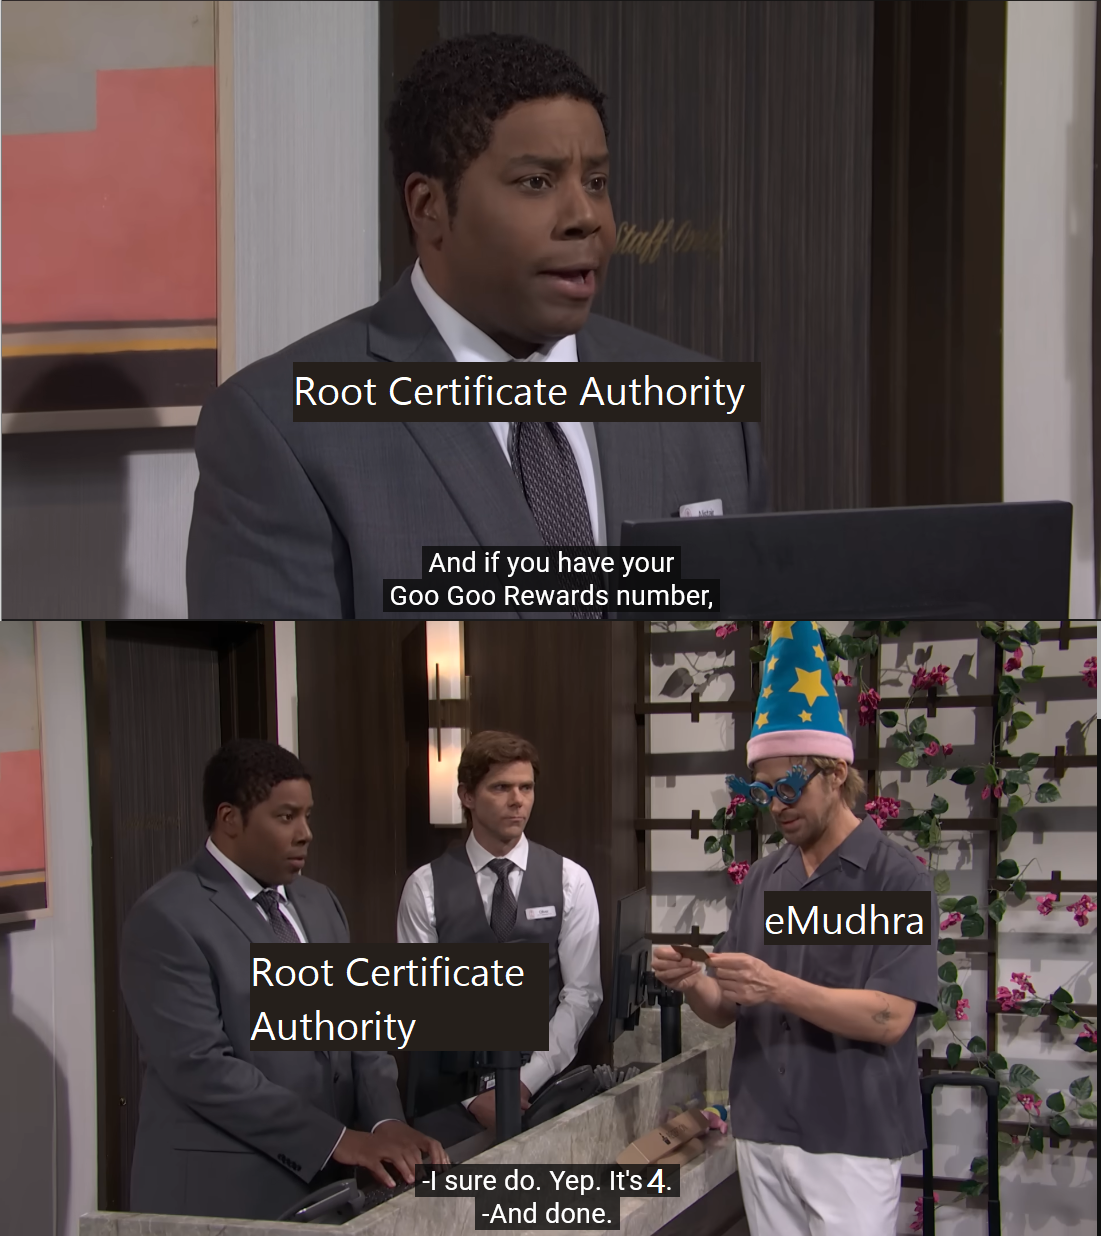
Root Certificate Authorities out here acting like they're the Supreme Court of the internet, demanding your credentials and proof of identity like you're trying to enter Fort Knox. They want documentation, verification, the whole nine yards! But then eMudhra (a real CA, by the way) rolls up like a chaotic wizard wearing a party hat and just... bypasses everything. "Goo Goo Rewards number? Yeah sure, that'll work. You're verified. Welcome aboard!" No questions asked, no security theater, just pure unhinged energy. The absolute AUDACITY of treating SSL certificate verification with the same rigor as a grocery store loyalty program is sending me. Who needs multi-factor authentication when you've got multi-flavor baby food points? 💀

Four Is 6 7 For Infosec

Four Is 6 7 For Infosec
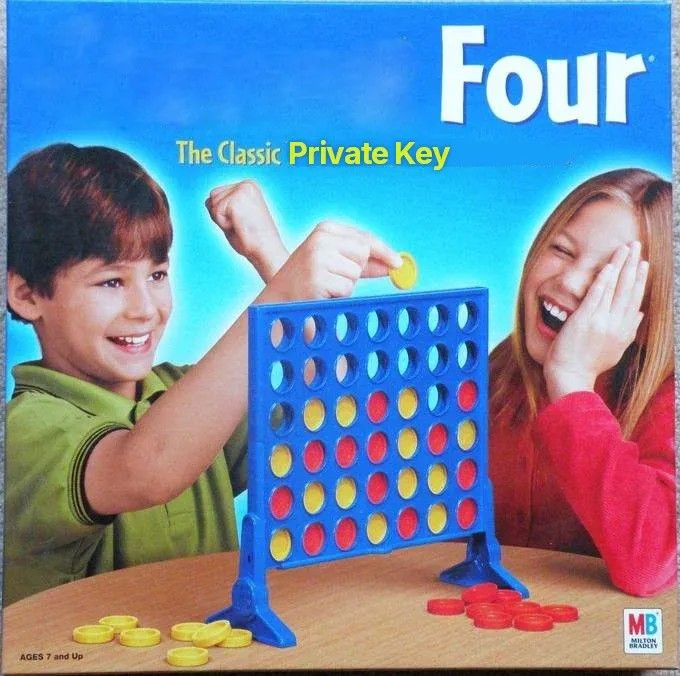
Security folks really looked at Connect Four and said "yeah, let's call it a private key and ship it." The game where your entire strategy is visible to everyone watching? Perfect metaphor for how we handle secrets in production. The kid's dropping that yellow chip with the same confidence as a dev hardcoding API keys into a public GitHub repo. And just like in the game, everyone can see exactly what you're doing, where you're going, and how to beat you. Except instead of losing a board game, you're losing your entire customer database to some script kiddie in Belarus. Private keys should be, you know, private . But here we are, treating them like Connect Four pieces—colorful, visible, and apparently meant for children to play with.