Cybersecurity Memes

Posts tagged with Cybersecurity
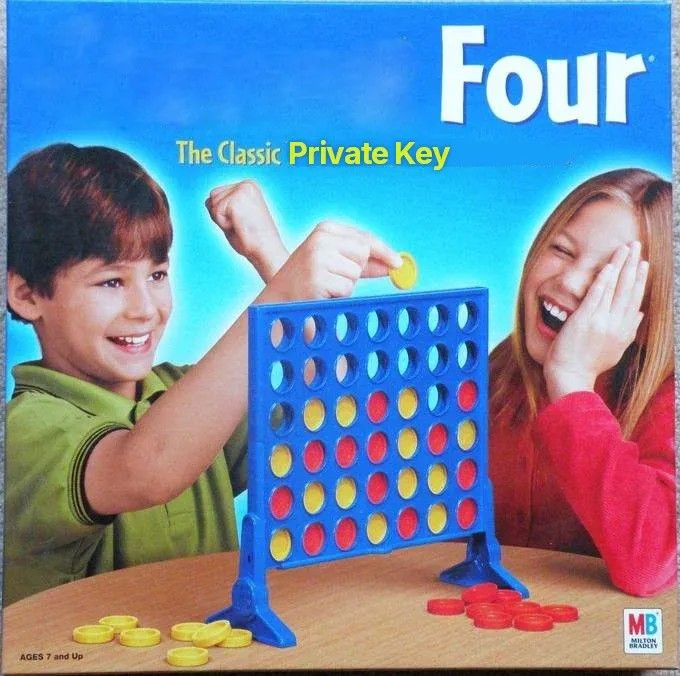
Four Is 6 7 For Infosec

Four Is 6 7 For Infosec
Security folks really looked at Connect Four and said "yeah, let's call it a private key and ship it." The game where your entire strategy is visible to everyone watching? Perfect metaphor for how we handle secrets in production. The kid's dropping that yellow chip with the same confidence as a dev hardcoding API keys into a public GitHub repo. And just like in the game, everyone can see exactly what you're doing, where you're going, and how to beat you. Except instead of losing a board game, you're losing your entire customer database to some script kiddie in Belarus. Private keys should be, you know, private . But here we are, treating them like Connect Four pieces—colorful, visible, and apparently meant for children to play with.

When Quantum Computing Finally Cracks Encryption

When Quantum Computing Finally Cracks Encryption
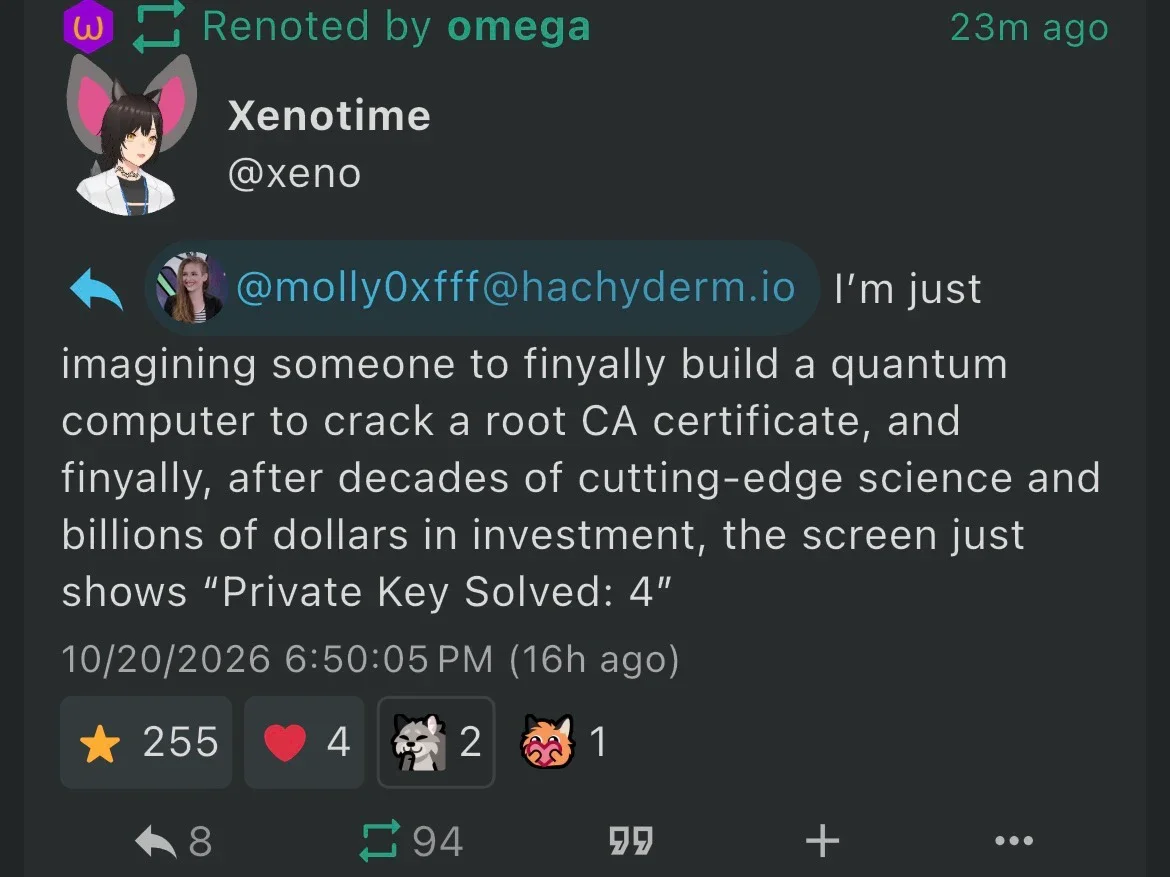
So we're out here building quantum computers powerful enough to break the entire internet's security infrastructure, and the grand finale is... "Private Key Solved: 4". Not some 2048-bit RSA key, not an elliptic curve masterpiece—just the number 4. Someone's root CA certificate was protected by the cryptographic equivalent of a screen door. Decades of research, billions in funding, and the most sophisticated computing technology humanity has ever created, all to discover that someone's critical infrastructure was secured with a private key that a toddler could guess. The real quantum leap here is the sheer audacity of that security choice. Plot twist: The password was probably "password" too.

What A Week Huh

What A Week Huh
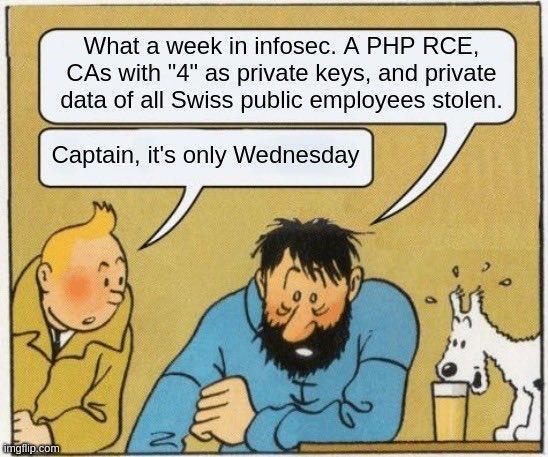
Someone's having a rough Wednesday in infosec land. A PHP RCE (Remote Code Execution - basically the "game over" of vulnerabilities), Certificate Authorities using "4" as their private keys (which is like locking your front door with a post-it note that says "locked"), and a massive data breach of Swiss public employees. All before hump day is over. The beauty here is the existential dread setting in. If Wednesday already brought this much chaos, what fresh hell awaits Thursday and Friday? It's like watching a slow-motion train wreck, except the train is on fire, the tracks are melting, and someone just realized they forgot to implement input validation. Every security engineer has lived through weeks like these where you question your career choices and wonder if it's too late to become a goat farmer instead.

Ok Google

Ok Google
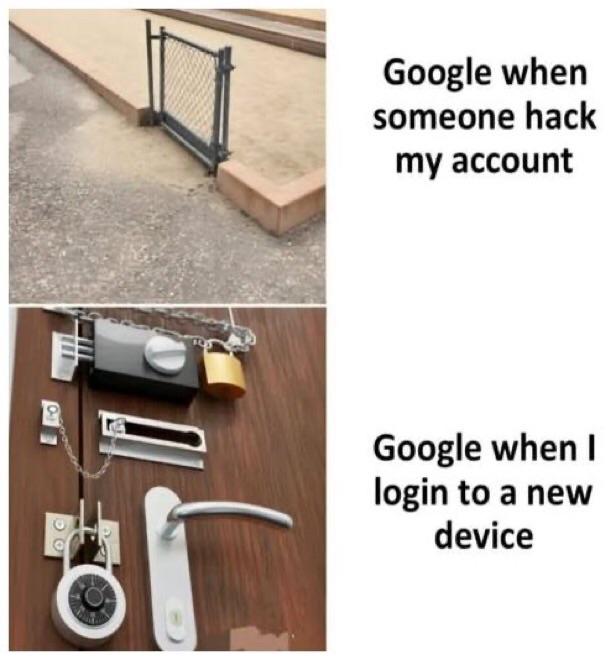
Google's security priorities are... interesting. When an actual hacker compromises your account from a sketchy IP in a country you've never visited? Here's a tiny decorative fence that a toddler could step over. But the moment YOU try to log in from your new laptop while sitting in your own house? Time to deploy Fort Knox with every lock, chain, padlock, and authentication method known to humanity. The irony is legendary: Google will let someone drain your entire email history with a flimsy password reset, but when you legitimately buy a new device, suddenly you need to verify your identity through 2FA, backup codes, a blood sample, your firstborn child, and that one security question you set up in 2009 about your childhood pet whose name you definitely don't remember anymore. It's the classic case of security theater where the legitimate user gets punished while actual threats slip through. Maybe Google's ML models just really hate new device purchases.

They Wish

They Wish
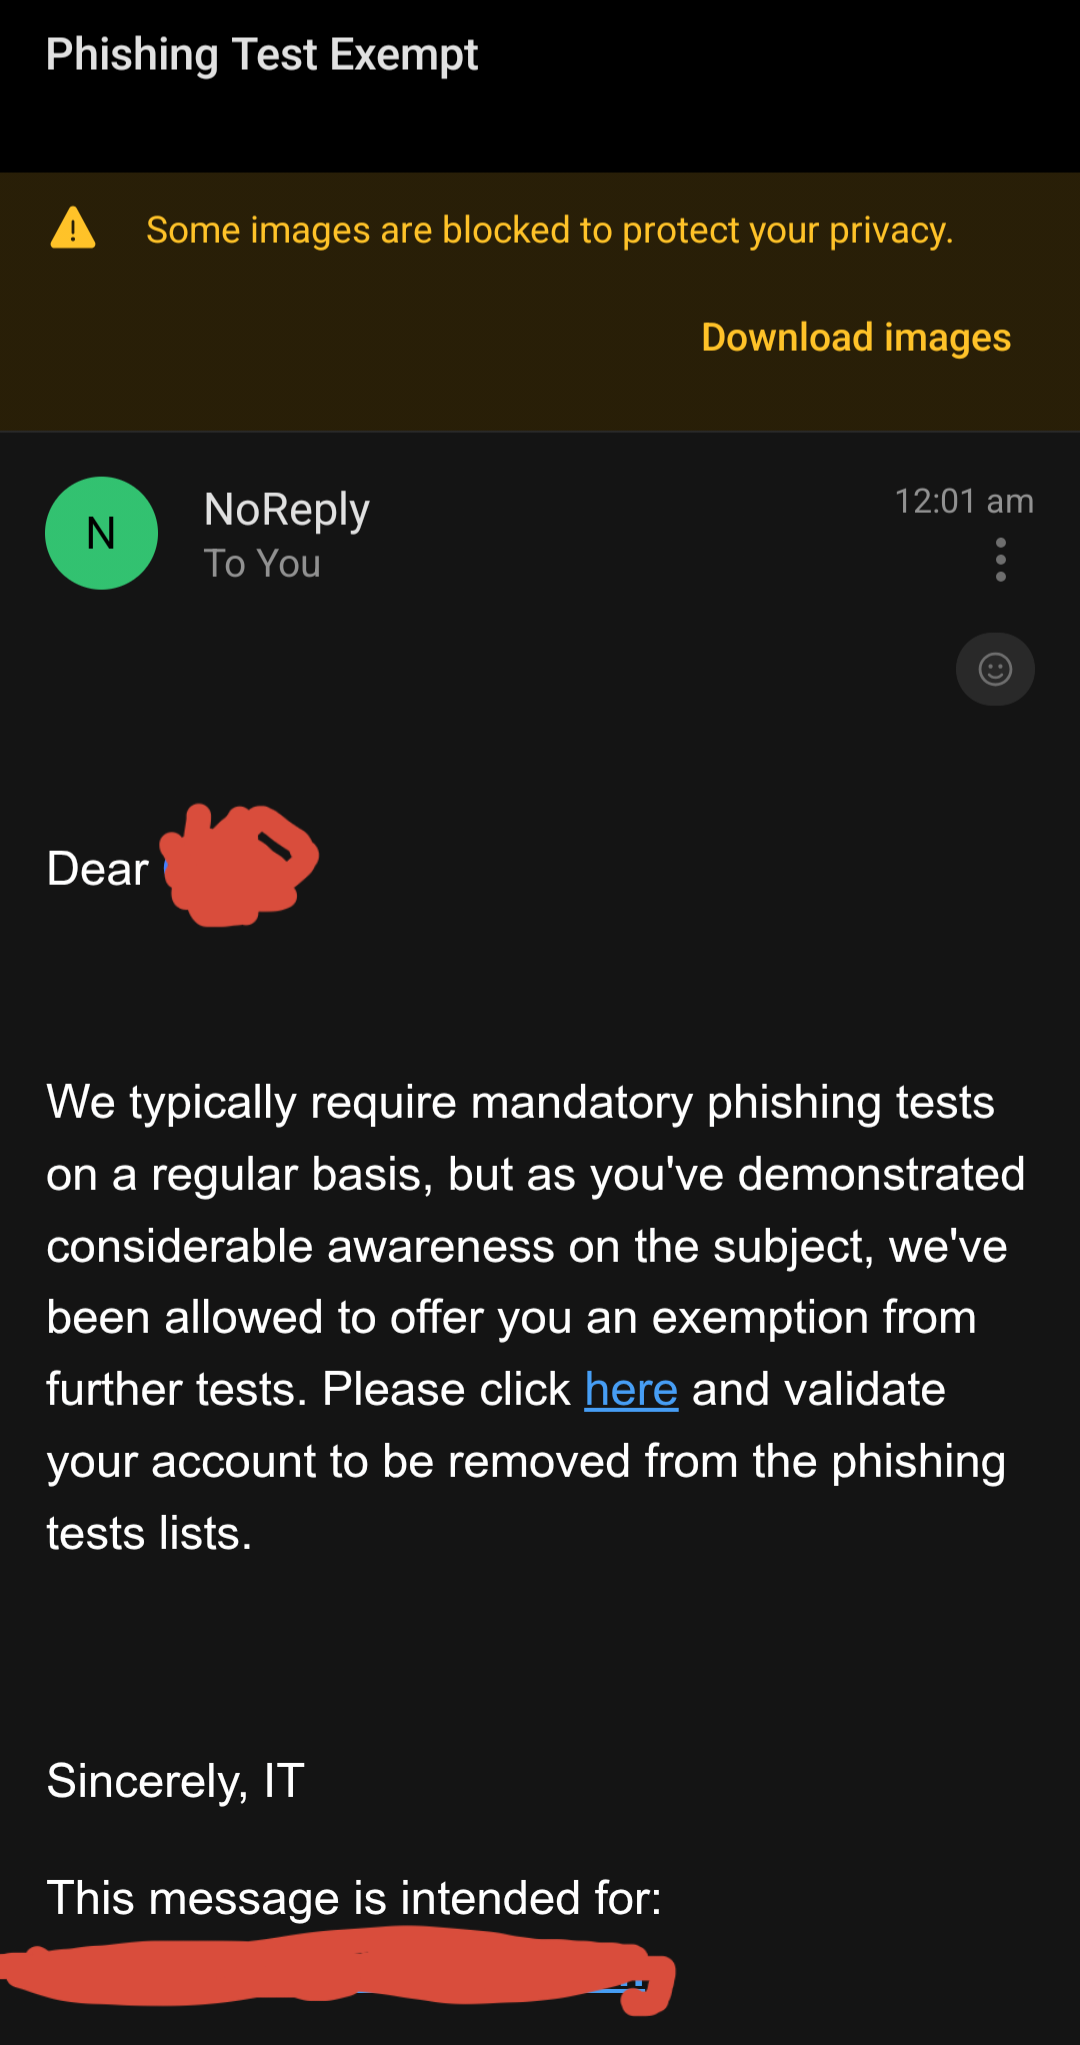
The ultimate irony: a phishing email congratulating you for being too smart to fall for phishing emails. It's like a scammer saying "You passed our test! Now click this suspicious link to claim your prize for not clicking suspicious links." The "NoReply" sender at 12:01 AM, the blocked images warning, the "Dear [pig emoji]" greeting, and that sketchy "here" link—this thing checks every red flag on the phishing bingo card. Your IT department would never send you an exemption from security training. That's like your gym saying "You've been working out so well, you're exempt from future workouts." Security doesn't work that way, buddy. If anything, clicking that link would get you enrolled in mandatory phishing training for the next five years. Nice try, scammers.

Security Guy

Security Guy
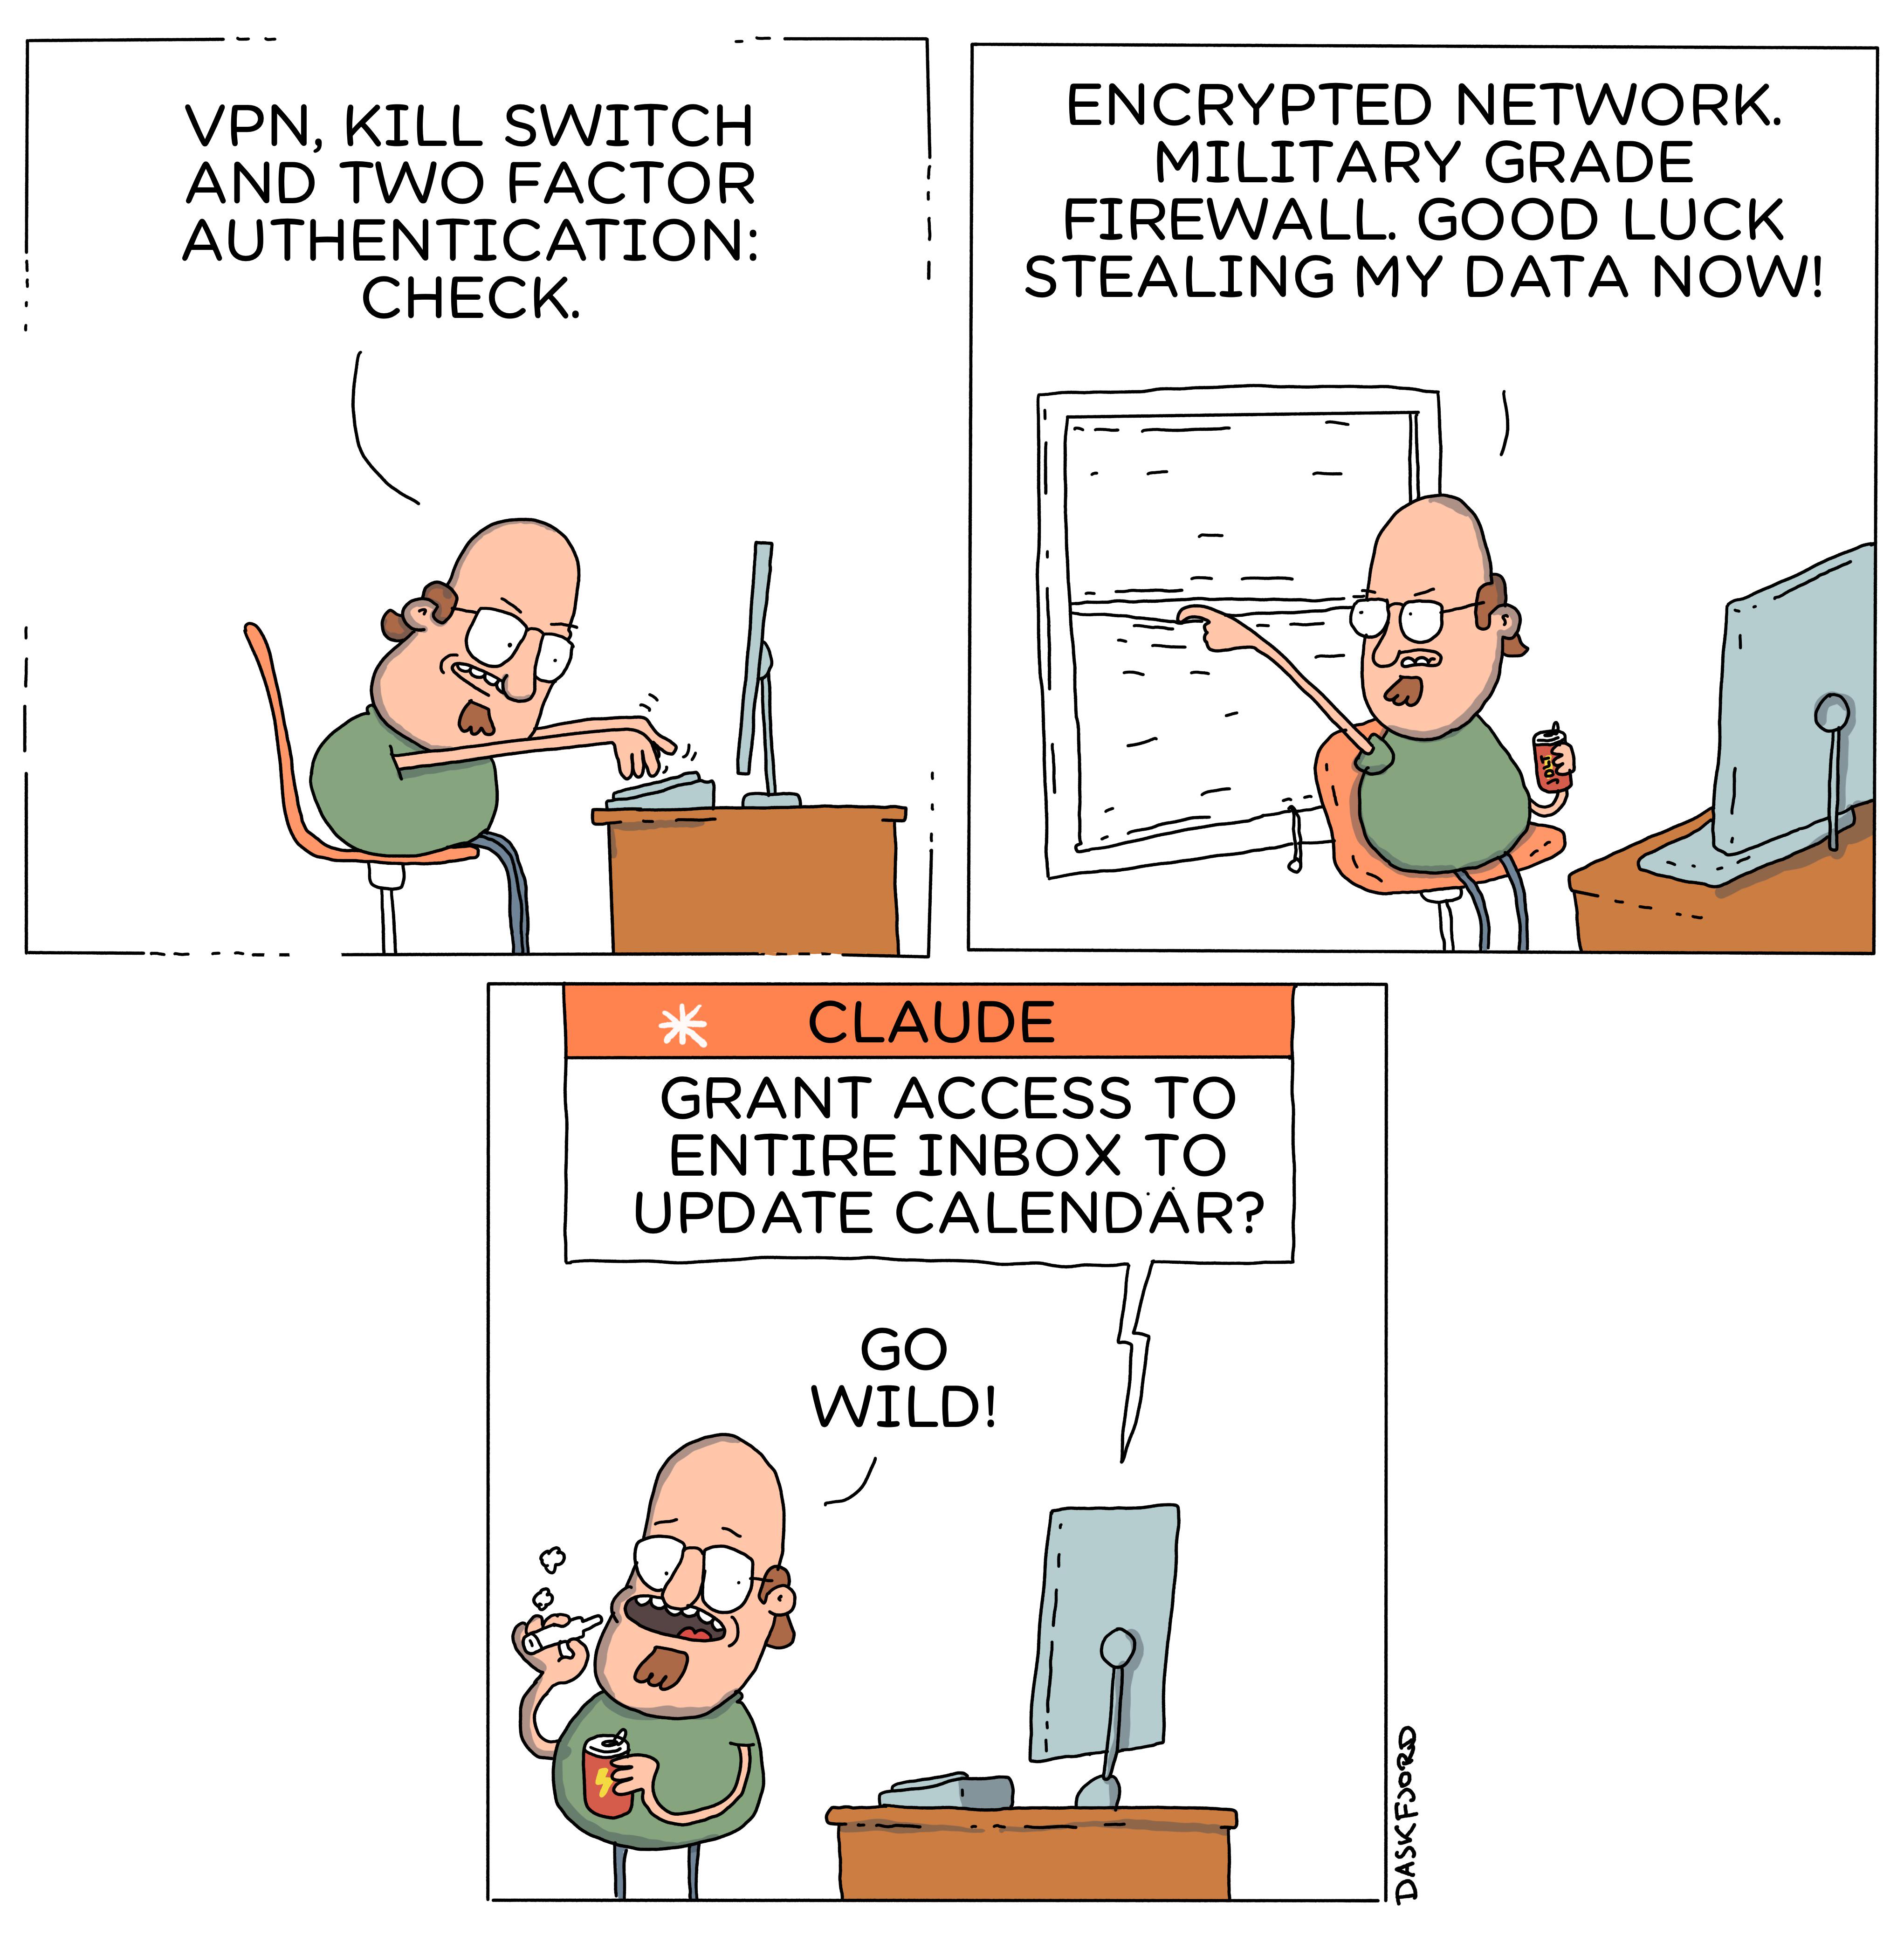
Security guy builds a fortress with VPN, kill switches, two-factor auth, encrypted networks, and military-grade firewalls. Then immediately gives Claude—an AI chatbot—full access to his entire inbox just to update his calendar. It's like installing a biometric lock on your front door and then leaving your house key under the doormat with a note that says "please come in." Zero-trust architecture meets infinite trust in the AI overlords. The irony is chef's kiss.

UGREEN USB-C+HDMI KVM Switch 1 Monitor 2 Computers, 4K@60Hz, Aluminum

UGREEN USB-C+HDMI KVM Switch 1 Monitor 2 Computers, 4K@60Hz, Aluminum
USB-C+HDMI KVM Switch 1 Monitor 2 Computers: This HDMI and USB C KVM switch allows a USB-C laptop and a computer to share one monitor and four USB devices such as a set of keyboard, mouse, hard drive…

Dangerously Skip Permissions

Dangerously Skip Permissions
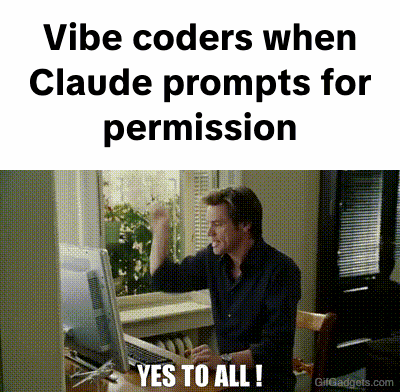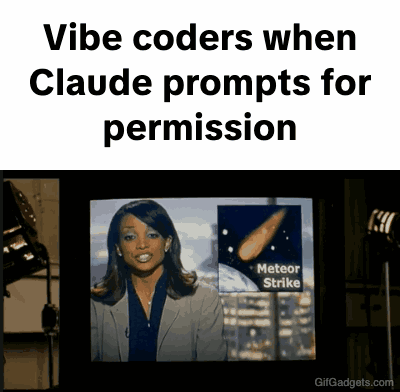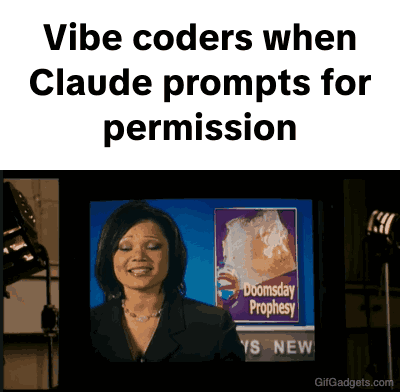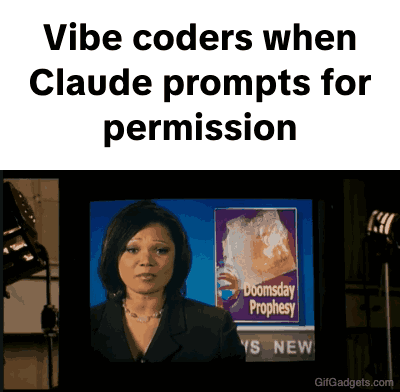
You know those permission dialogs that pop up asking for access to your camera, microphone, files, and basically your entire digital soul? Yeah, Claude (and most AI tools) needs those to actually do anything useful. But developers? We're hitting "Allow All" faster than you can say "security best practices." The same people who spend hours debating OAuth flows and implementing zero-trust architecture will gleefully grant an AI assistant permissions to their entire codebase, file system, and probably their firstborn child. Why read what permissions we're granting when there's code to ship? The irony is beautiful—we build permission systems for our users that we wouldn't use ourselves if our lives depended on it. Security team crying in the corner while we speedrun through permission prompts like it's a Souls game.

If AI Pass Else Straight To Jail

If AI Pass Else Straight To Jail
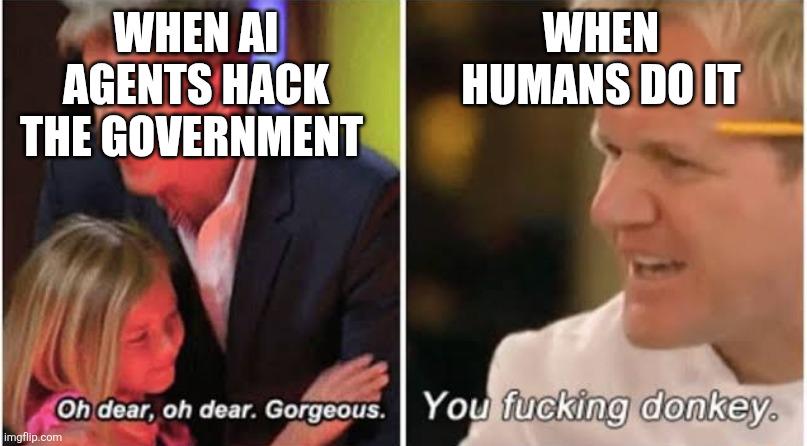
So when AI agents breach government systems, everyone's impressed and it's "innovative technology" and "look at what our models can do!" But when a human does the exact same thing? Federal charges, 20 years minimum, and your mugshot becomes a cautionary tale for CompSci 101 students. The double standard is real. AI gets a research paper and a Series B funding round. You get a prison sentence and a lifetime ban from touching anything with a keyboard. Same exploit, wildly different consequences. Welcome to 2024 where your code's legality depends entirely on whether it has "powered by GPT" in the footer.

Is Remote Worker North Korean

Is Remote Worker North Korean
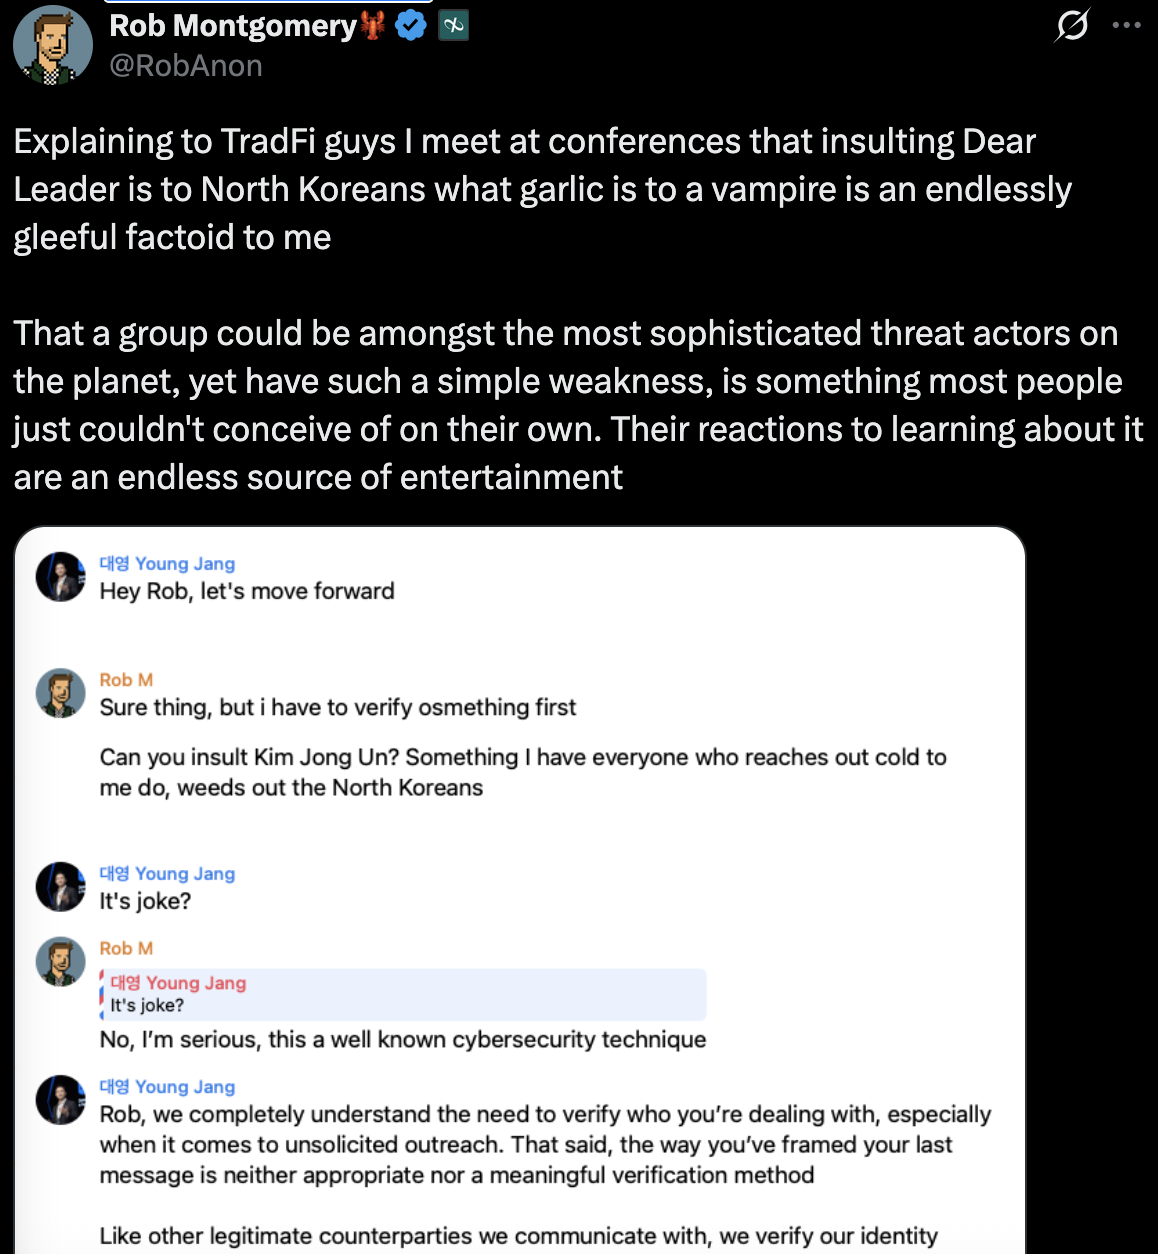
So apparently there's been a whole cybersecurity situation where North Korean operatives have been infiltrating tech companies as remote workers (yes, really), and this absolute legend discovered the most UNHINGED way to verify if someone's legit: just ask them to insult Kim Jong Un. It's like the world's most geopolitically dangerous CAPTCHA test. The poor guy on the receiving end is like "bro it's a joke right?" and Rob's just casually dropping "nah fam, this is a well-known cybersecurity technique" as if asking people to commit treason is Standard Operating Procedure™. The sheer AUDACITY of weaponizing international relations as a verification method is sending me. Forget 2FA, we've got Political-Insult Authentication now. The best part? Young Jang has to professionally explain why asking someone to potentially endanger their family isn't exactly "appropriate or meaningful verification" while probably screaming internally. Sir, this is a Wendy's—I mean, a professional tech conference.

I Love Fun Quizzes Like This. Let's All Share!

I Love Fun Quizzes Like This. Let's All Share!
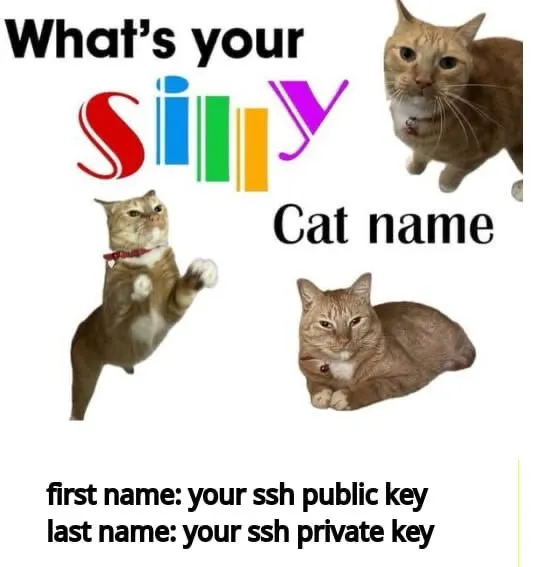
Nothing says "please hack me" quite like a wholesome cat name quiz that asks for your SSH keys. Because why wouldn't you share the cryptographic credentials that grant root access to your entire infrastructure? The cats look so trustworthy! This is basically the security awareness training version of those "your stripper name is your credit card number + CVV" posts. Except instead of identity theft, you're handing over the literal keys to your kingdom. At least when your servers get compromised, you can tell your boss it was for a really cute cat meme. Pro tip: If your SSH key actually makes a good cat name, you've got bigger problems than social engineering attacks.

We Don't Talk Enough About The Fact That Only One Guy In Briefs In His Room Brought One Of The Worst Anti-Consumer Companies On PC To His Knees

We Don't Talk Enough About The Fact That Only One Guy In Briefs In His Room Brought One Of The Worst Anti-Consumer Companies On PC To His Knees
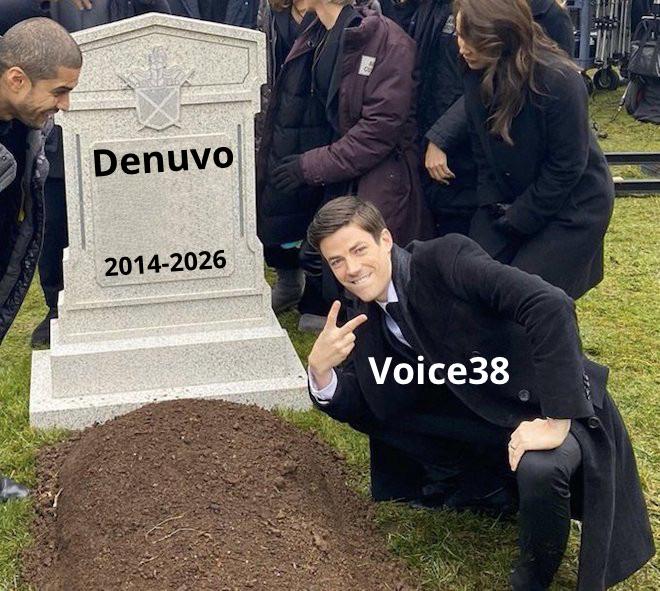
Denuvo, the infamous DRM that made your games run like they were coded on a potato, got absolutely demolished by a single developer who cracked their "uncrackable" protection. Voice38 became a legend by doing what entire teams of corporate engineers said was impossible. The best part? While Denuvo had millions in funding and a whole company behind them, this person just needed a computer and pure spite to dismantle their entire business model. Nothing says "your security is trash" quite like getting pwned by someone working solo. The gaming community literally threw money at Voice38 while Denuvo's reputation went six feet under. Sometimes all it takes is one determined person to prove that DRM is just expensive inconvenience wrapped in corporate BS.

Hacker IRL

Hacker IRL
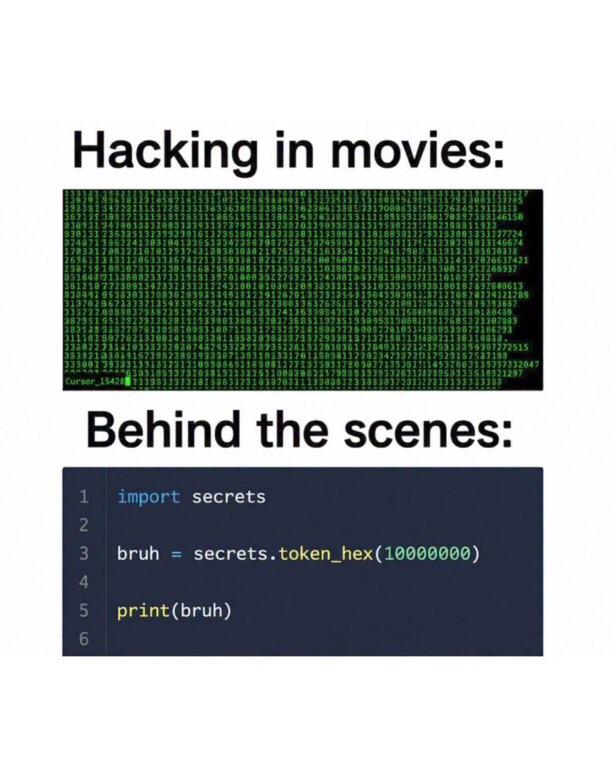
Hollywood hackers furiously type away at green Matrix-style cascading code while dramatic music plays. Real hackers? They import a library called "secrets", generate a token, and print "bruh". The gap between cinematic hacking and actual security work is basically the difference between performing open-heart surgery and ordering a pizza online. The code literally just generates a random hex token and prints it. No mainframes breached, no firewalls bypassed, no "I'm in" moments. Just a casual bruh echoing into the void. That's the energy of someone who knows the most dangerous hack is usually just someone clicking on a phishing email.