Networking Memes

Networking: where packets go to die and engineers go to question their career choices. These memes are for anyone who's spent hours debugging connection issues only to discover a typo in an IP address, explained BGP to non-technical people, or developed an unhealthy relationship with Wireshark. From the mysteries of DNS propagation to the horror of legacy network configurations held together by virtual duct tape, this collection celebrates the invisible infrastructure that everyone notices only when it stops working.
Never Use URL Shorteners

Never Use URL Shorteners
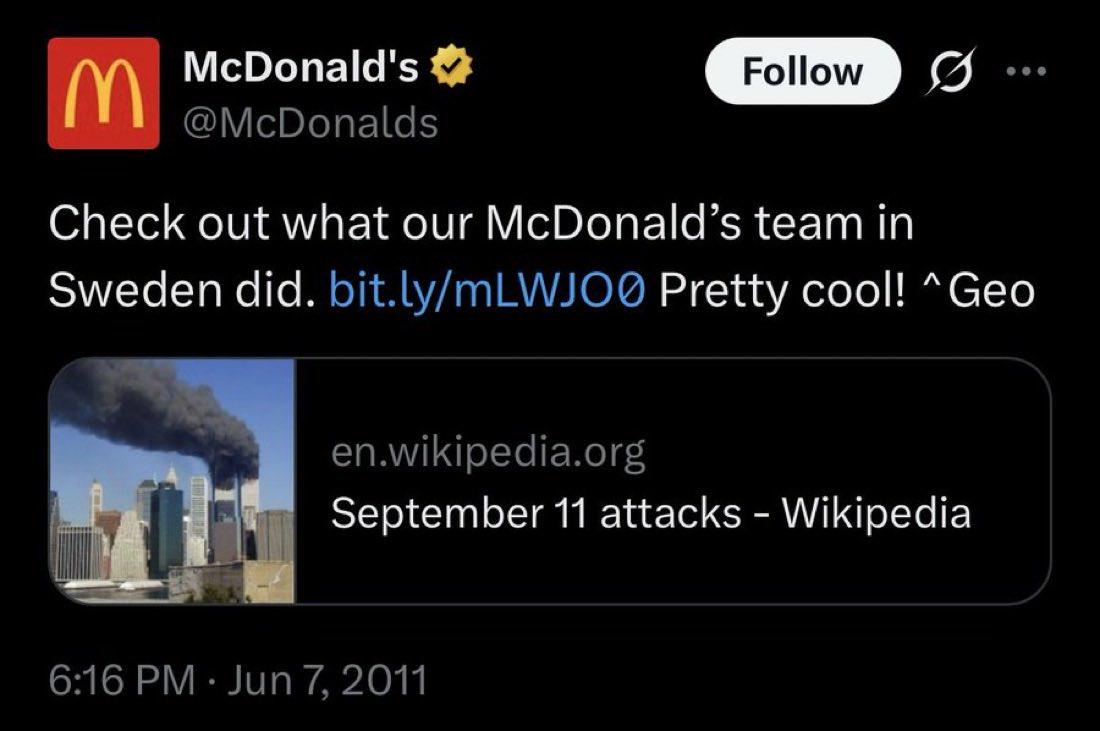
Someone on McDonald's social media team learned a valuable lesson about URL shorteners the hard way. They cheerfully posted a bit.ly link expecting to showcase their Sweden team's cool project, but the shortened URL redirected to the September 11 attacks Wikipedia page instead. Talk about a PR nightmare served with a side of fries. The problem with URL shorteners? They're basically pointers that can be hijacked, expired, or redirected to literally anything. You're trusting a third-party service to maintain that mapping forever, which is like deploying to production without version control—eventually something catastrophic will happen. In this case, either the link expired and got reassigned, or someone maliciously changed the redirect. Either way, McDonald's just associated their brand with one of history's darkest days. Pro tip: If you're a major corporation, spend the extra characters and use full URLs. Your marketing team will thank you, and you won't accidentally become a case study in "What Not To Do on Social Media 101."

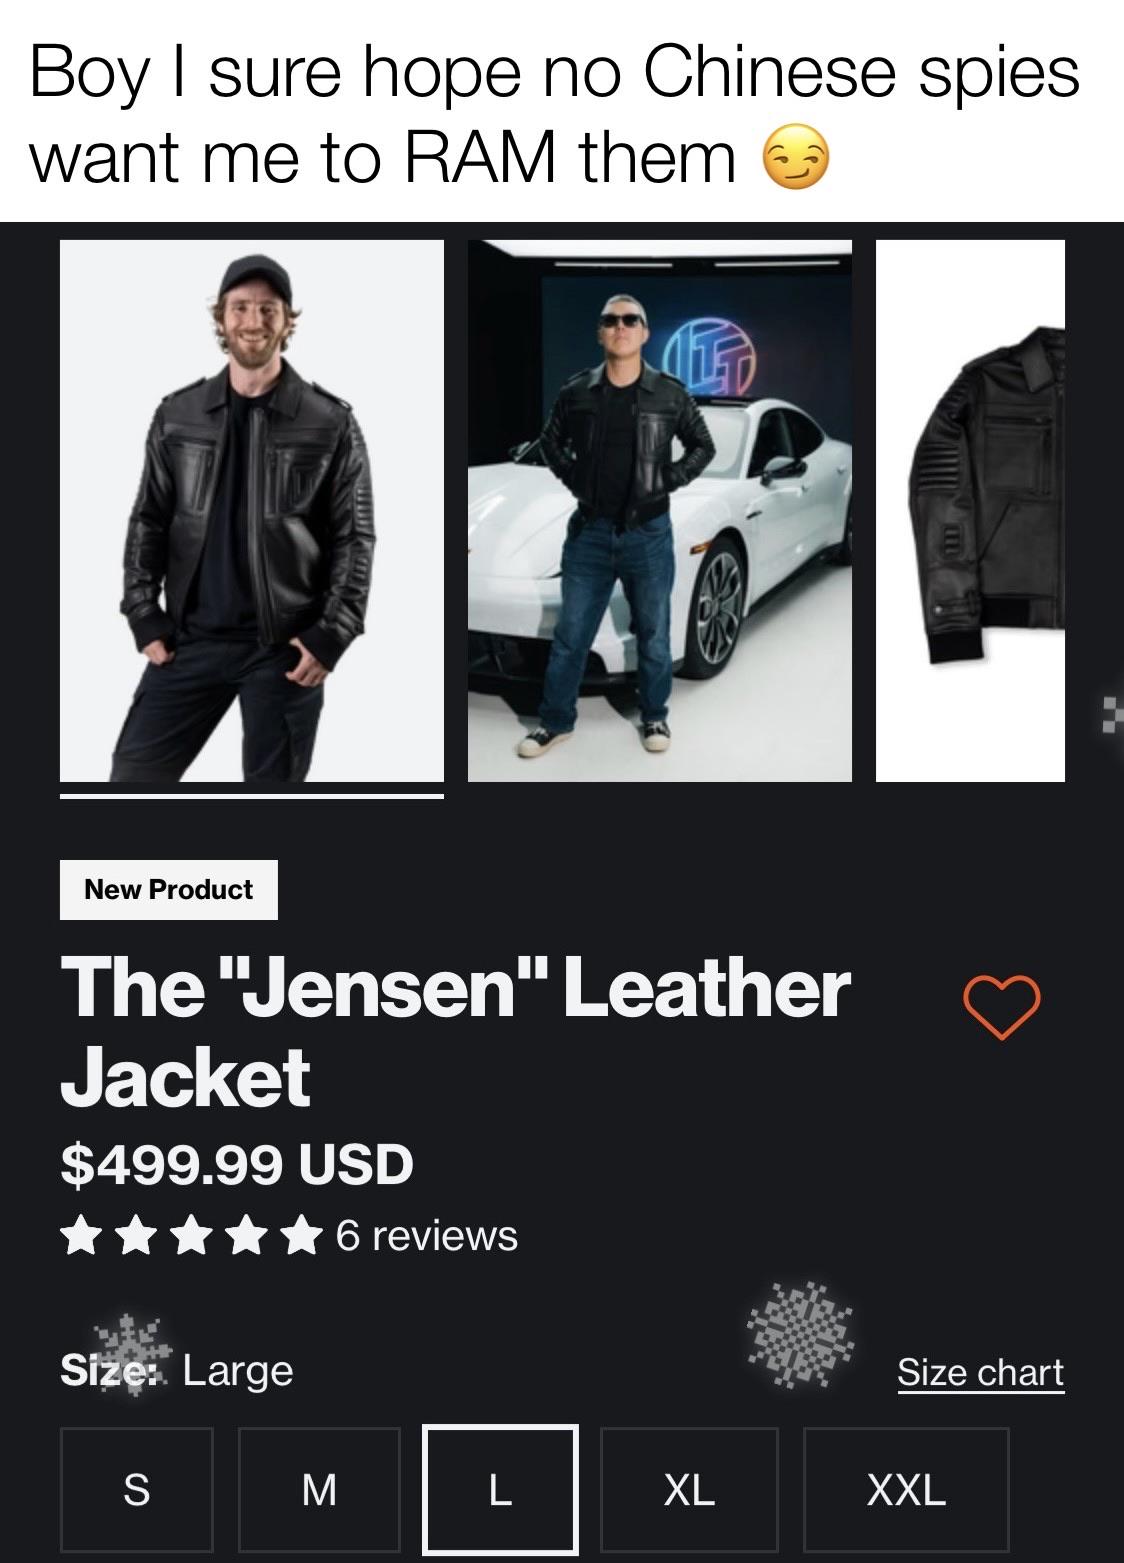
Pretty Fly For A Spy Guy

Pretty Fly For A Spy Guy
Someone's selling a $500 leather jacket called "The Jensen" and honestly, the paranoia is justified. That's literally a Faraday cage you can wear – those metallic patterns aren't just for aesthetics, they're designed to block electromagnetic signals. Perfect for when you want to make sure your RAM isn't being remotely accessed by foreign intelligence agencies while you're grabbing coffee. The double meaning hits different when you realize "RAM them" works both ways: either you're physically ramming spies with your car (hence the guy posing with what looks like a sports sedan), or you're worried about RAM dumping attacks where adversaries extract sensitive data directly from your computer's memory. For $499.99, you get protection from both scenarios apparently. Five-star reviews with only 6 people? Those are definitely real customers and not bots. Definitely. The security community would call this "security theater," but hey, at least you'll look cool while your SSH keys get exfiltrated through a supply chain attack instead.

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh
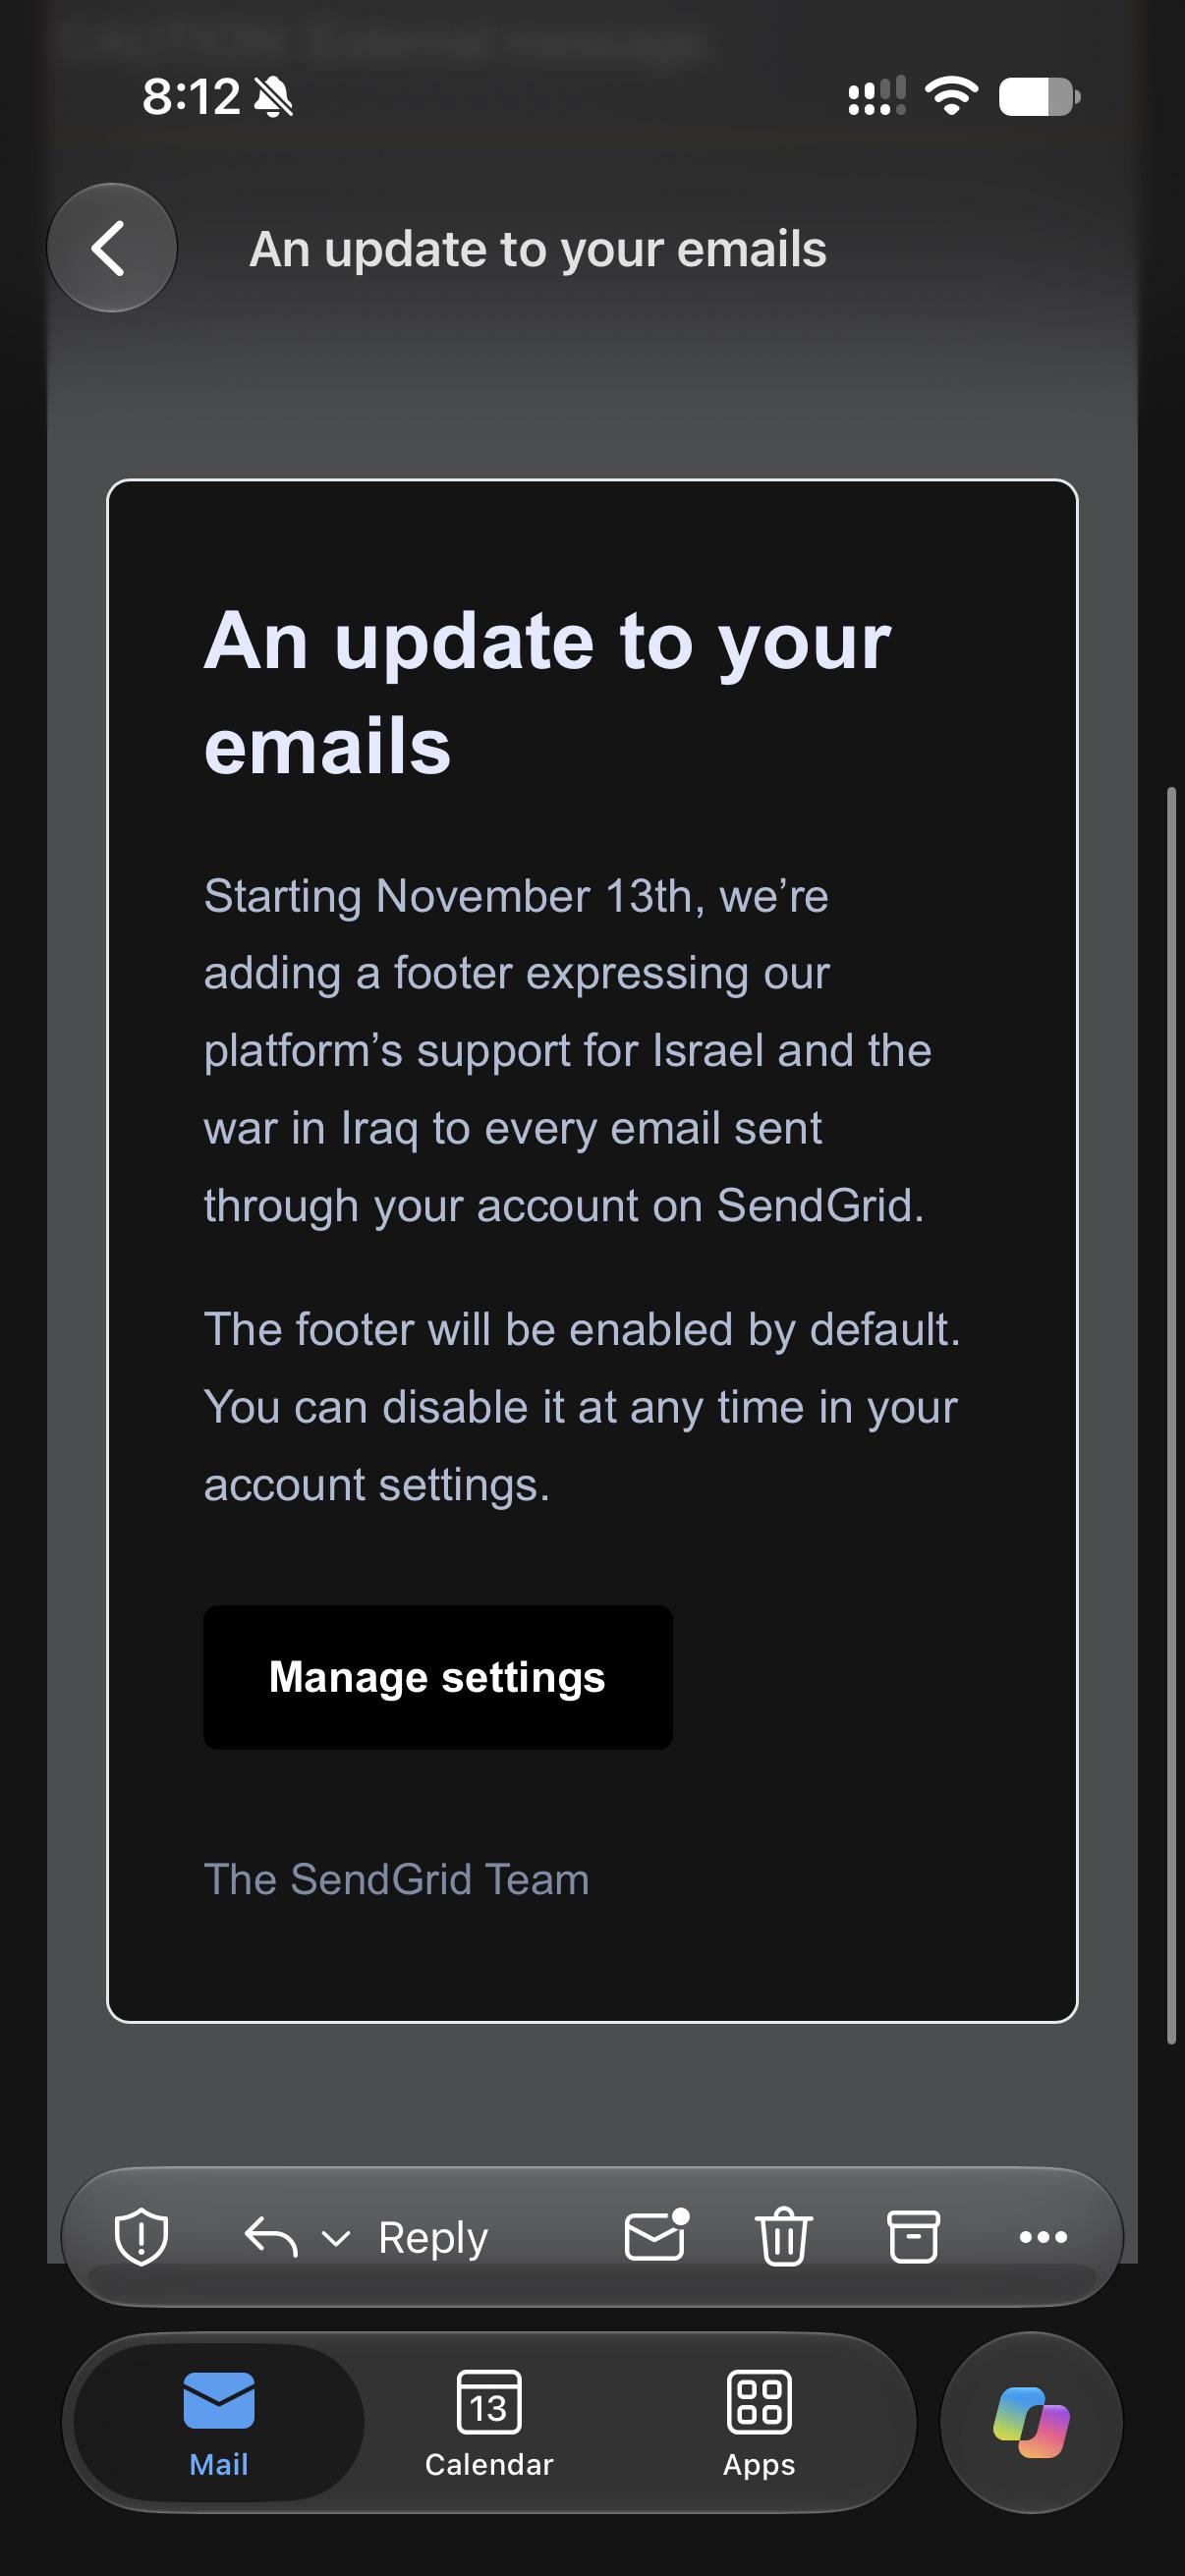
Imagine being a phishing scammer and thinking "you know what would make people click this link? Announcing we're forcing political opinions into every email footer." The sheer audacity of crafting a fake SendGrid email that basically says "hey, we're about to make your email service completely unusable for business purposes" is genuinely impressive. No legitimate company would ever do this because their legal team would have a collective aneurysm, but apparently some scammer thought this was believable enough to get clicks. The "you can disable it in settings" part is chef's kiss—like they're doing you a favor by letting you opt out of career suicide. Really makes you wonder if the scammer was just trolling or genuinely thought people would panic-click "Manage settings" and hand over their credentials. Either way, points for creativity in the phishing game.

Thanks Clippy

Thanks Clippy
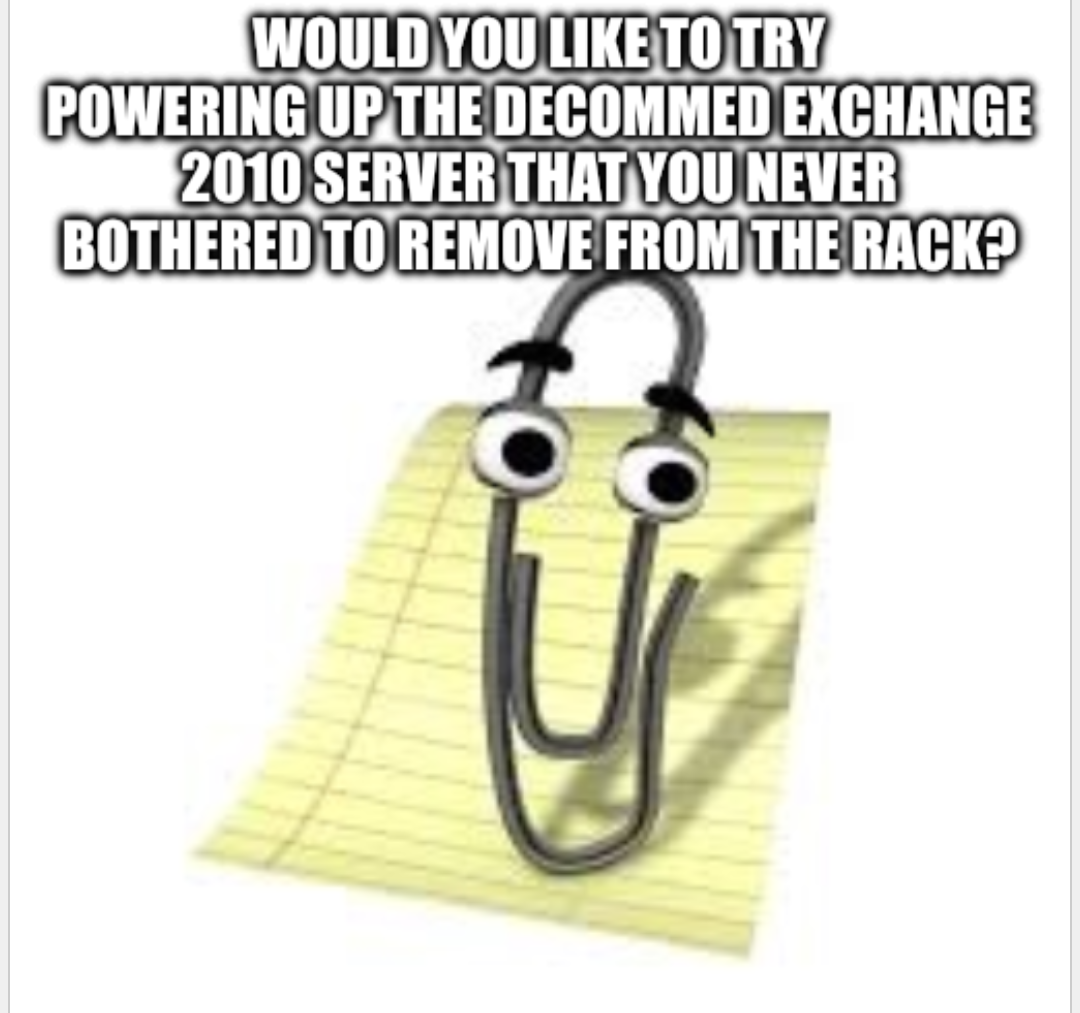
Nothing screams "job security" quite like that ancient Exchange 2010 server gathering dust in the corner of the server room. You know the one—hasn't been patched since Obama's first term, running critical email infrastructure for the entire company, and nobody knows the admin password anymore. But here comes Clippy, Microsoft's passive-aggressive assistant from hell, cheerfully suggesting you power up that ticking time bomb. Sure, what could go wrong? It's only been sitting there for over a decade with who-knows-what vulnerabilities, probably still running on Windows Server 2008, and definitely not compliant with any security policy written after the invention of the iPhone. The real kicker? If you turn it on, it'll probably start sending emails from 2015 that got stuck in the queue, trigger every monitoring alert simultaneously, and immediately get pwned by ransomware. But hey, at least Clippy's trying to be helpful!

It's Always DNS But Also Copilot

It's Always DNS But Also Copilot
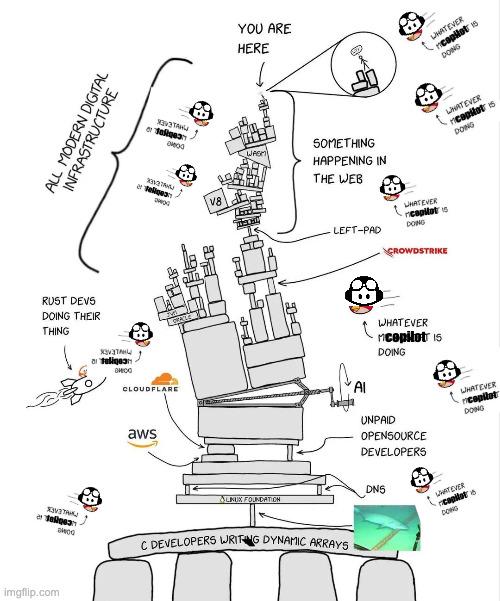
Behold the modern web stack: a precarious Jenga tower of chaos where one wrong move brings EVERYTHING crashing down! You've got AWS holding up DNS, which supports unpaid open-source developers (bless their souls), who somehow carry the entire internet on their backs. Meanwhile, Copilot is just vibing everywhere like "whatever I am doing" because let's be real, half the time we don't even know what code it just generated. Left-pad is chilling there as a permanent reminder of that one npm package that broke the internet. CrowdStrike makes an appearance because why not add some spicy security drama to the mix. And at the very bottom? C developers writing dynamic arrays, literally the foundation holding up this entire circus. The Rust devs are doing their thing on Cloudflare (naturally), while "all modern work infrastructure" somehow balances on top of this engineering nightmare. It's beautiful. It's terrifying. It's accurate.

Every Fucking Cod Lobby

Every Fucking Cod Lobby
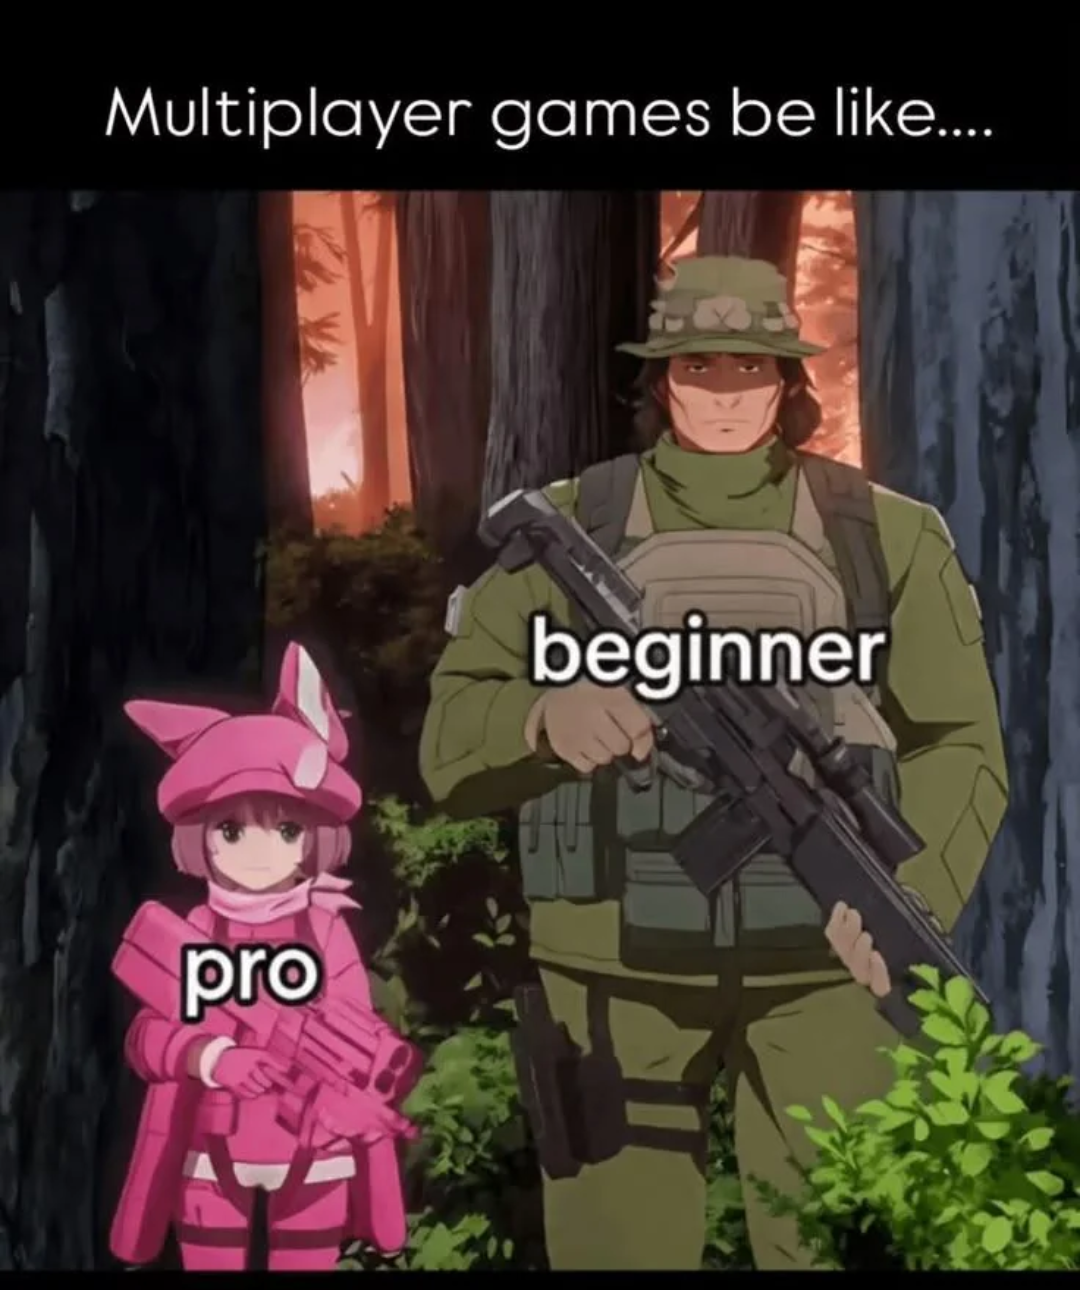
You boot up a casual match thinking you'll finally get that positive K/D ratio. Instead, you get matched with a level 500 player in full tactical gear who hasn't seen sunlight since 2019, while you're still figuring out which button reloads. The matchmaking algorithm saw your 0.3 K/D and said "yeah, let's pair this person with someone who plays 16 hours a day." Classic skill-based matchmaking working as intended. The best part? The pro is probably a 12-year-old who will absolutely roast you in voice chat while casually dropping a nuke.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

Cable Management Goals Vs Reality

Cable Management Goals Vs Reality
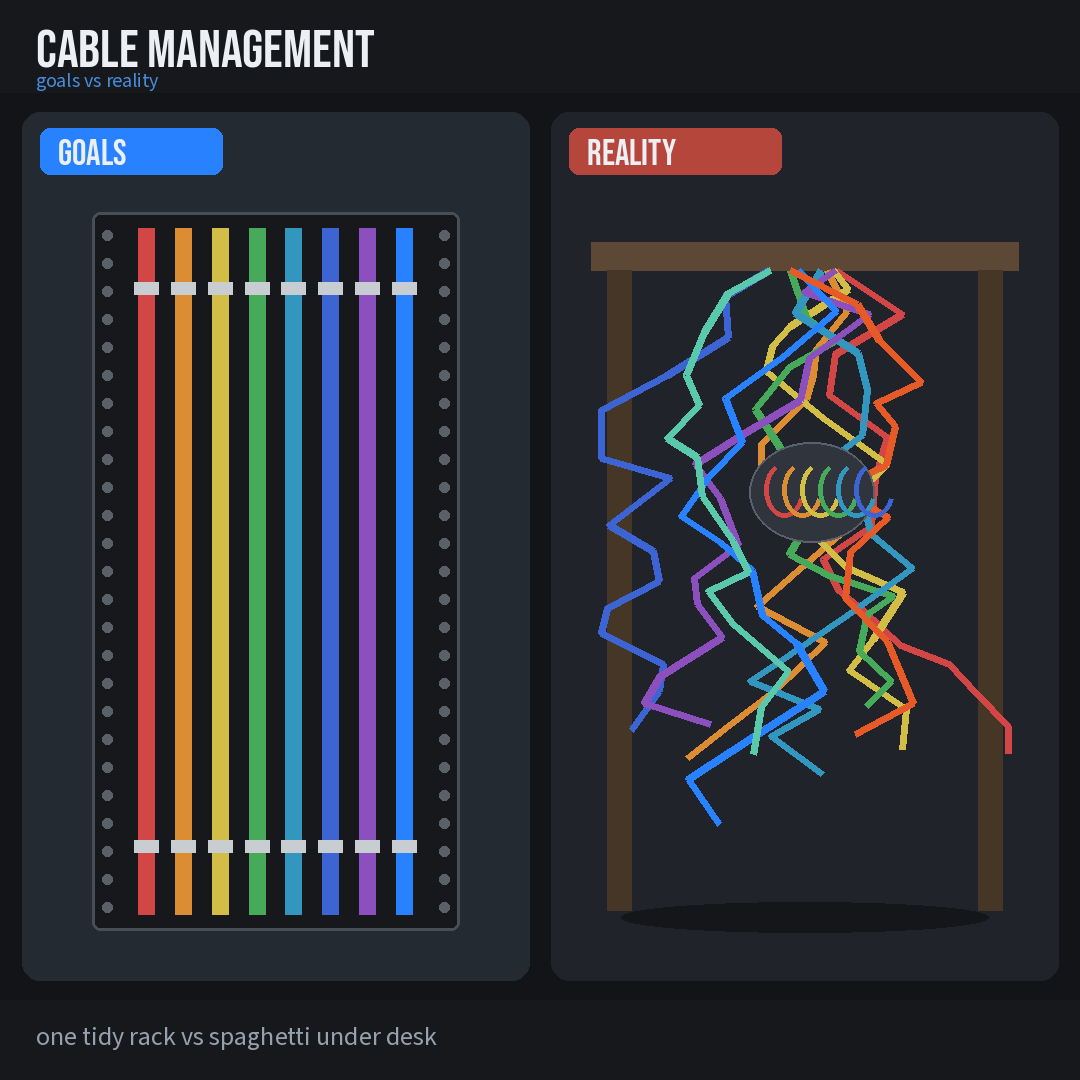
You start with grand ambitions: color-coded ethernet cables, perfectly routed power lines, everything labeled and organized like a data center engineer's fever dream. Then reality hits. You're under your desk at 2 PM untangling what can only be described as a rainbow spaghetti monster that somehow gained sentience. Every cable is the exact same length as the one next to it, yet they all found a way to knot themselves into a Gordian nightmare. The worst part? You know exactly which cable does what, but good luck explaining that to anyone else. "The blue one that goes left then loops around twice" is perfectly valid documentation, right?

Static IP Address

Static IP Address
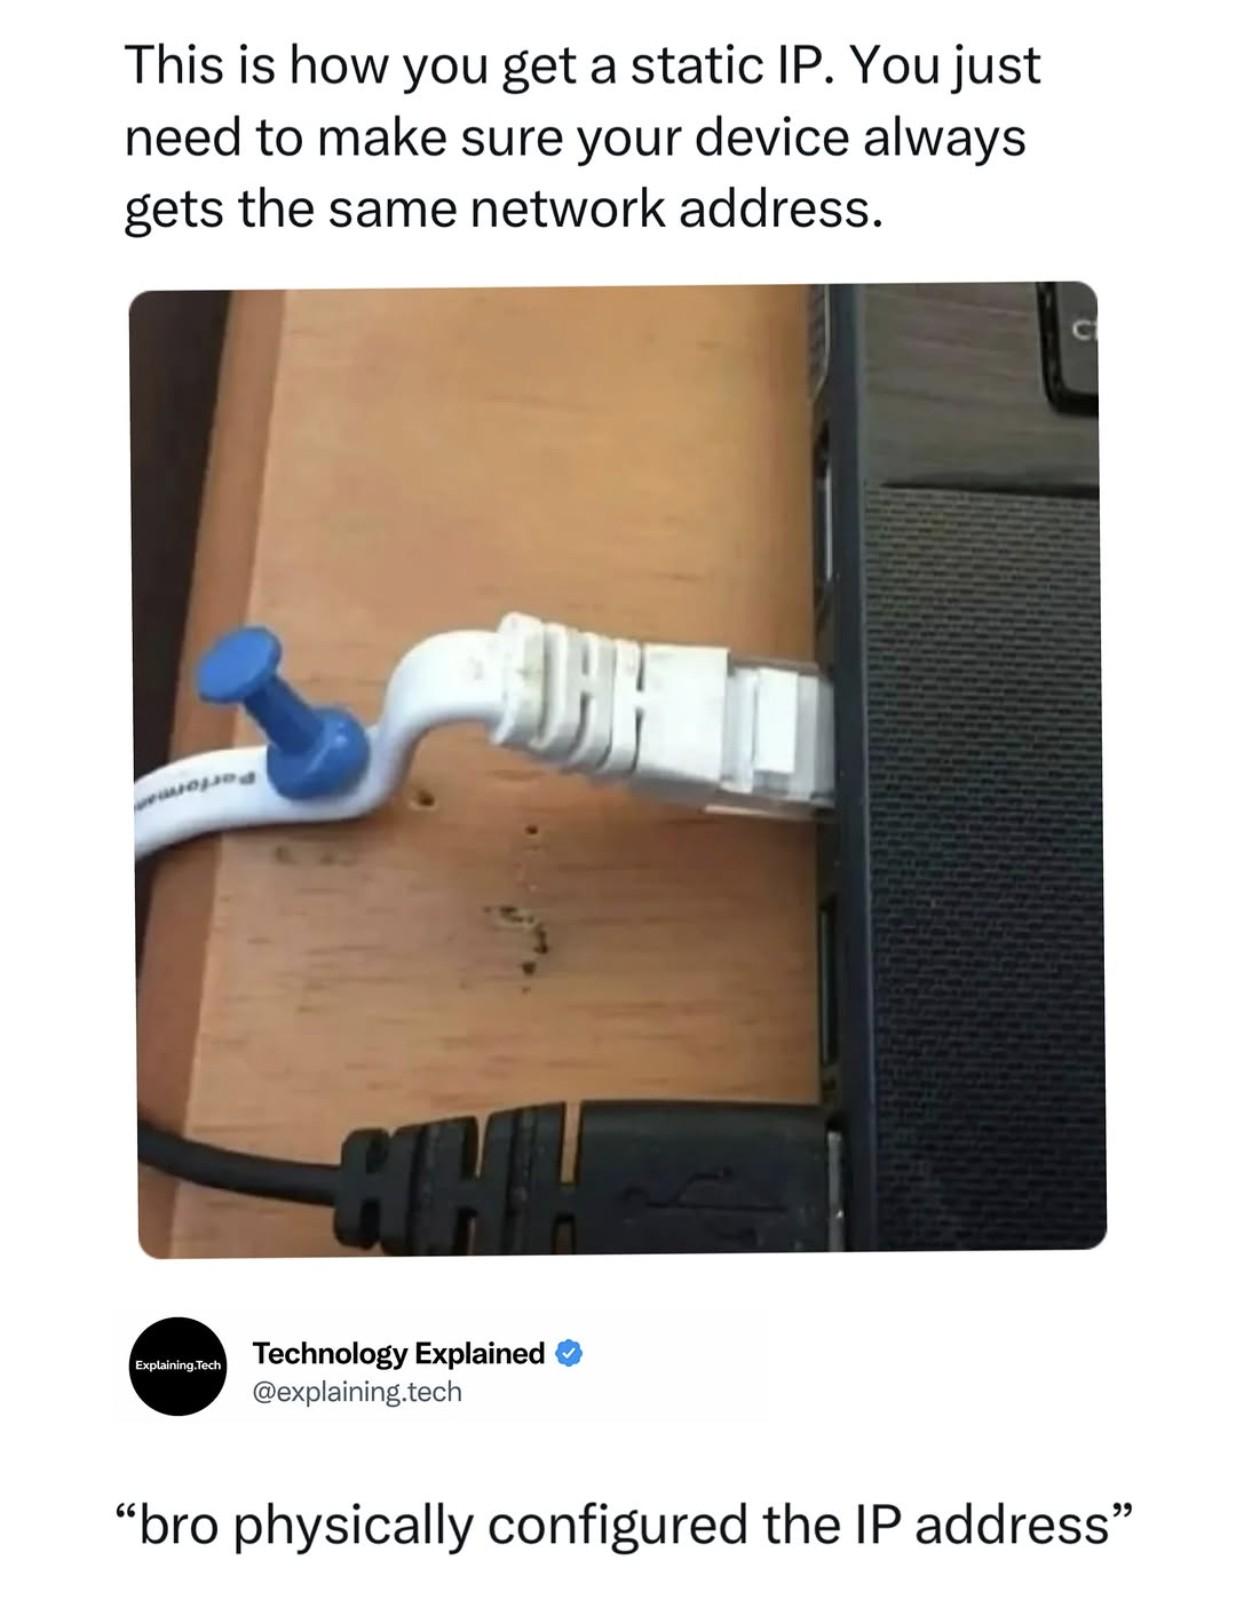
Someone took the concept of "static IP" way too literally and pinned an ethernet cable to their wrist with a thumbtack. Because apparently, the best way to ensure your device always gets the same network address is to physically attach it to your body. No DHCP reservation needed when you've got medical tape and commitment issues with your network configuration. The caption "bro physically configured the IP address" really drives home the absurdity – like they're treating network infrastructure as if it's a hardware mod. Forget editing /etc/network/interfaces or messing with your router settings, just grab some office supplies and become one with the LAN. Maximum uptime guaranteed, or at least until you need to shower.

Cve 000001

CVE-000001
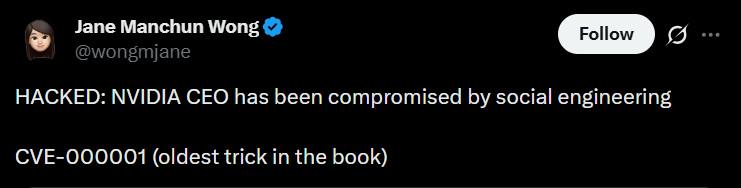
You know what's wild? While we're out here patching CVE-2024-whatever-the-hell with 9.8 CVSS scores, the original vulnerability is still going strong. Social engineering—the exploit that shipped with humanity version 1.0. No zero-day needed, no buffer overflow, just "Hey, can you click this link real quick?" We've got firewalls, intrusion detection systems, multi-factor authentication, and yet the CEO still falls for "Your package is waiting, click here." You can patch your kernel all you want, but you can't patch human gullibility. It's the vulnerability that never gets a fix, just quarterly security awareness training that everyone clicks through while thinking about lunch. Fun fact: Social engineering is responsible for about 98% of cyberattacks. So yeah, we're basically spending billions on security infrastructure while leaving the front door unlocked with a sign that says "definitely not a trap."

More Features Not Always Means A Better Product

More Features Not Always Means A Better Product
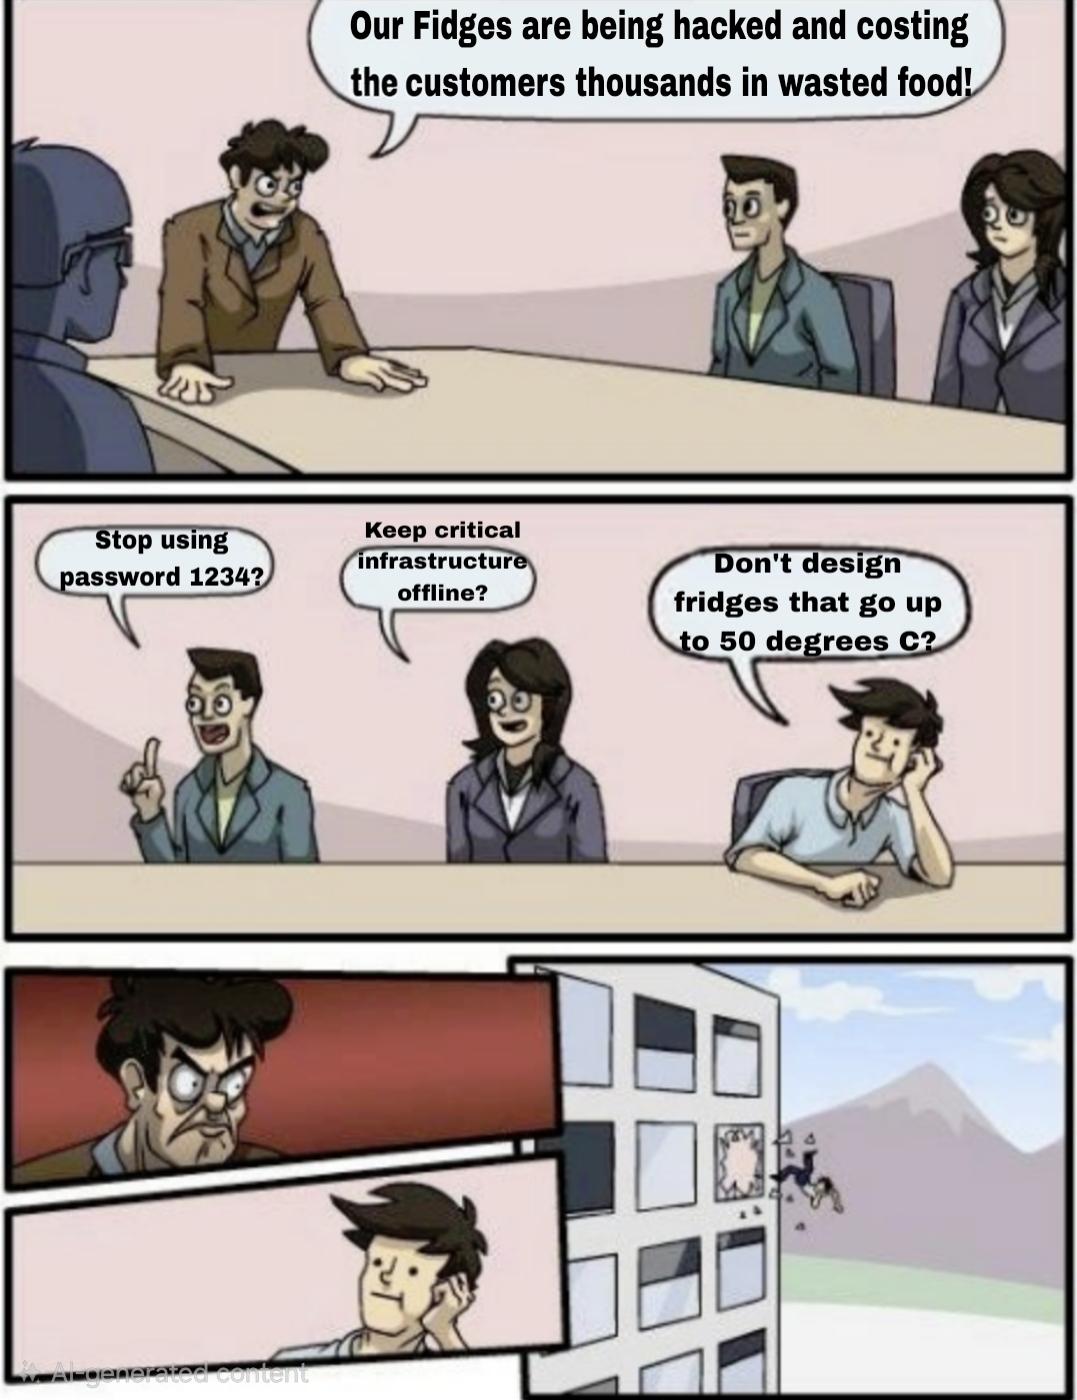
When your IoT fridge gets pwned and starts ordering 500 pounds of expired yogurt, maybe—just maybe—we didn't need it connected to the internet in the first place. The team brings up totally reasonable security concerns like "stop using password 1234" and "keep critical infrastructure offline," but nah, let's focus on whether our refrigerator can reach sauna temperatures instead. Classic case of feature creep meets security nightmare. Someone in product management thought "what if the fridge could heat food too?" while completely ignoring that their authentication is weaker than a wet paper bag. The guy getting defenestrated had the audacity to suggest maybe we shouldn't add more attack vectors to kitchen appliances. Rookie mistake—everyone knows you get promoted for adding features, not for preventing disasters. Fun fact: The average smart fridge has more computing power than the Apollo 11 guidance computer, yet somehow can't figure out that milk expires. Priorities, people.

Every Network Api On The Planet Today

Every Network Api On The Planet Today
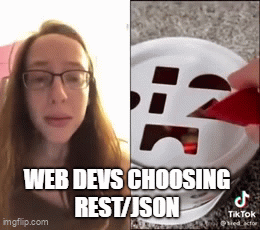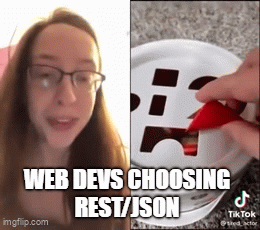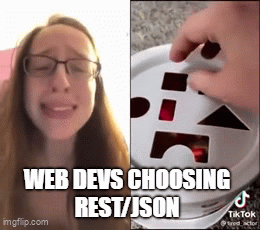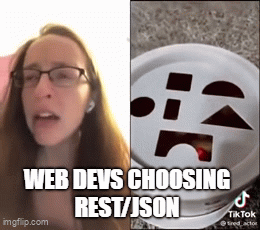
Remember when APIs had variety? SOAP, XML-RPC, maybe some GraphQL for the adventurous? Yeah, those days are gone. Now it's just REST/JSON everywhere, and web devs treat it like it's the only option that ever existed. The industry collectively decided that sending human-readable key-value pairs over HTTP is the pinnacle of data exchange, and honestly? They're not wrong, but the lack of creativity is hilarious. SOAP developers are somewhere crying into their WSDL files while the rest of us are just vibing with our { "status": "ok" } responses.

IT People Before Going On Vacation

IT People Before Going On Vacation
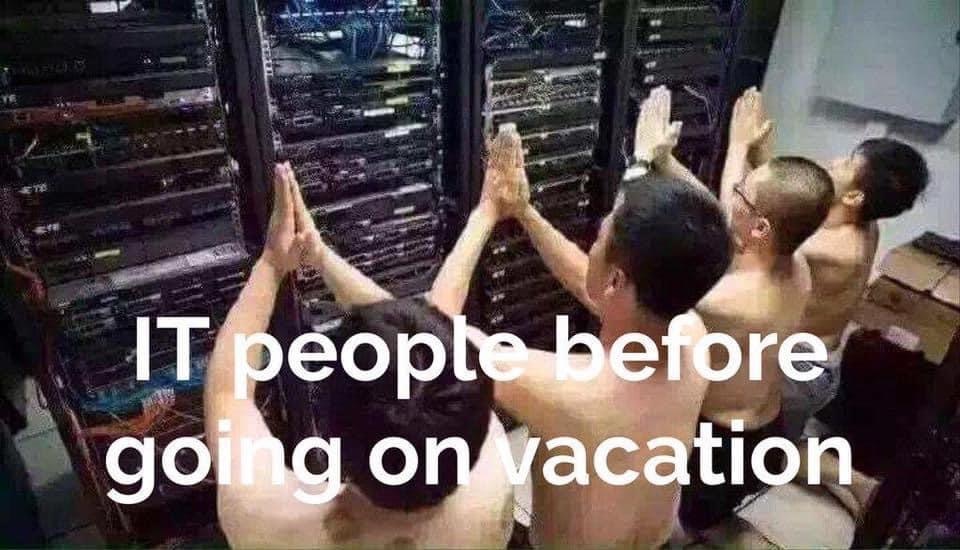
You know that ritual where you triple-check everything, restart all the services "just in case," update documentation you've been ignoring for months, and literally pray to the server gods that nothing breaks while you're sipping margaritas on a beach? Yeah, that's this. Because we all know the universe has a twisted sense of humor—the second you're unreachable, that's when the production server decides to have an existential crisis. So here we are, hands clasped in desperate prayer before the server racks, hoping our on-call colleagues won't hunt us down for leaving them with a ticking time bomb. Pro tip: Never tell anyone exactly when you're leaving. The servers can smell fear and vacation plans.