Dependency hell Memes

Posts tagged with Dependency hell
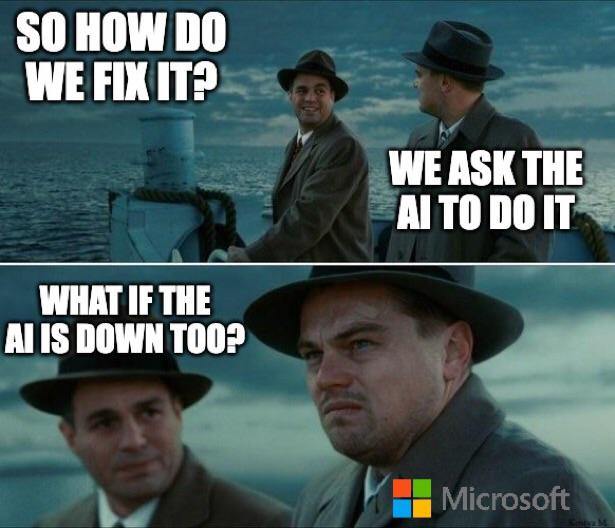
How Do We Fix It

How Do We Fix It
The modern developer's dependency stack has reached peak absurdity. We've gone from "let's fix the bug" to "let's ask ChatGPT to fix the bug" to the existential crisis of "what happens when our AI crutch goes offline?" It's like we've collectively forgotten how to debug without asking an LLM to explain our own code back to us. The real kicker? Even Microsoft—who literally owns GitHub Copilot—knows we're all doomed if the AI services go down. We've built our entire workflow on a foundation that requires constant internet connectivity and prayer that OpenAI's servers are having a good day. Plot twist: when the AI is down, you actually have to read the error message yourself. Revolutionary concept, I know.

Anyps 5

Anyps 5
When your system libraries go from 67% to 27% and suddenly everything looks... darker. That's not disk space optimization, that's a cry for help. The top panel shows a healthy-ish system with mostly green libraries loaded, but the bottom? Someone ran `apt-get autoremove` without reading what it was about to delete. Or maybe they thought "do I really need all these dependencies?" Narrator: They did. The guy's face says it all - that moment when you realize half your system just vanished and you're about to spend the next 4 hours reinstalling everything because you didn't snapshot first. Classic.

We Need To Make PHP Illegal It's Not My Fault

We Need To Make PHP Illegal It's Not My Fault
The Drake meme format strikes again, but this time it's calling out every developer's dirty little secret. When a critical security vulnerability drops, there are two types of people: the responsible ones who update their dependencies like clockwork, and the chaos agents who've been running the same PHP 5.6 installation since Obama's first term. The bottom panel is pure poetry. You ignore updates for years because "if it ain't broke, don't fix it," then suddenly you're forced to update everything at once. Now your entire codebase is throwing errors because some function got deprecated three major versions ago, your database queries are screaming about SQL injection vulnerabilities, and you're frantically Googling "how to refactor 50,000 lines of legacy code in 2 hours." The title blaming PHP is chef's kiss because it's the programming equivalent of "the dog ate my homework." Sure, PHP has its quirks, but let's be real—the vulnerability exists because someone thought $_GET['user_input'] directly into a SQL query was a vibe.

Crazy Week

Crazy Week
PHP2SHELL gets all the attention while everyone's having a great time patching. Meanwhile, the security team is still down there dealing with the skeleton crew of vulnerabilities that have been sitting in the backlog since 2018. Broccoli2Shell, LiteLLM, OpenCode, Railway—nobody cares because they're not trending on Twitter. Classic security theater: one CVE gets the spotlight while the rest slowly decompose in the depths of your dependency tree. The number 4 really captures the mood—just another Tuesday for incident response teams who are perpetually underwater, drowning in alerts nobody else acknowledges. Fun times.

Takes Two Seconds To Open Paint

Takes Two Seconds To Open Paint
The entire digital world is literally held together by some random developer's side project from 2003 that they abandoned after their first commit. Your banking app? Probably depends on a library maintained by a guy in Nebraska who hasn't updated his GitHub profile picture since MySpace was relevant. The best part is how corporations with billion-dollar valuations are frantically trying to privatize and monetize open source projects that have been running critical infrastructure for decades. Good luck putting a paywall on the digital equivalent of load-bearing duct tape, my dudes. Meanwhile, the AI slop pipe is just dumping out code that looks like it was generated by autocomplete on steroids, feeding directly into production systems. What could possibly go wrong when your entire tech stack is one unmaintained dependency away from collapse? At least Paint opens quickly—that's something we can still count on.

Python Programming Cheat Sheet Desk Mat - Large Mouse Pad with Complete Code Reference (31.5" x 11.8") - Professional Coding Guide Mousepad for Beginners & Software Engineers

Python Programming Cheat Sheet Desk Mat - Large Mouse Pad with Complete Code Reference (31.5" x 11.8") - Professional Coding Guide Mousepad for Beginners & Software Engineers
Complete Python Reference Guide - Master coding with our comprehensive desk mat featuring essential Python syntax, data structures, and OOP concepts. Perfect for both beginners learning Python and ex…

Cyclic Dependency

Cyclic Dependency
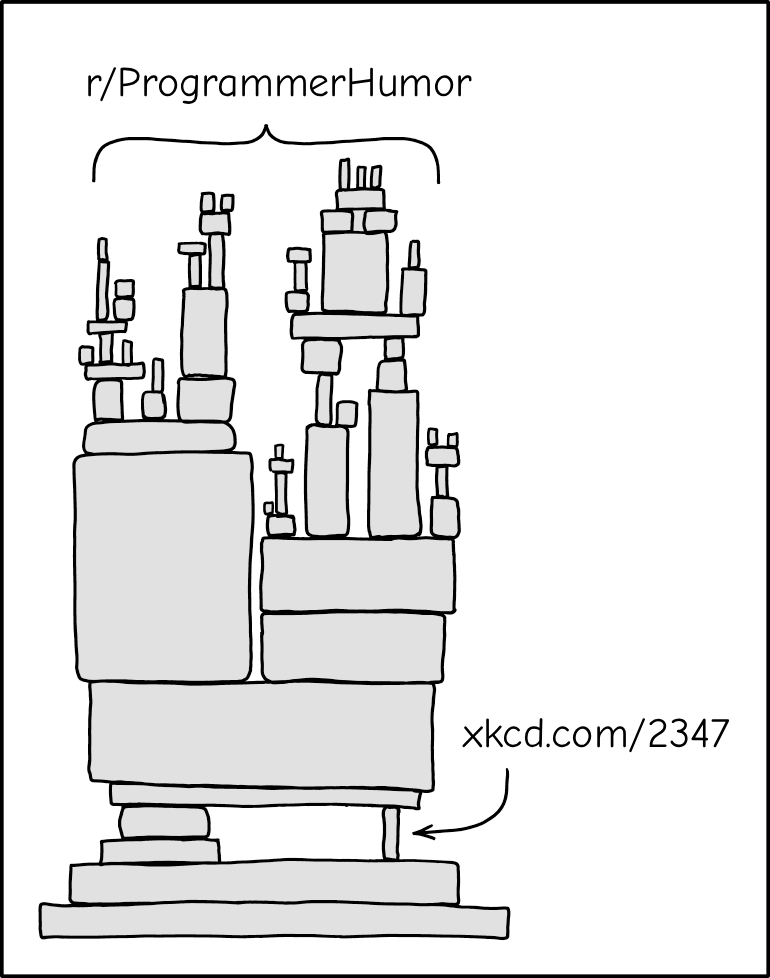
You know your architecture is in great shape when your dependency graph looks like a Jenga tower designed by someone who's had way too much coffee. Each module carefully balanced on top of another, which is balanced on another, which somehow needs the first one to work. It's the kind of beautiful disaster that makes refactoring feel like defusing a bomb—pull out one piece and the whole thing comes crashing down. Dependency injection? More like dependency inception. Your build system is probably crying in a corner somewhere.

Resolving Dependency Hell

Resolving Dependency Hell
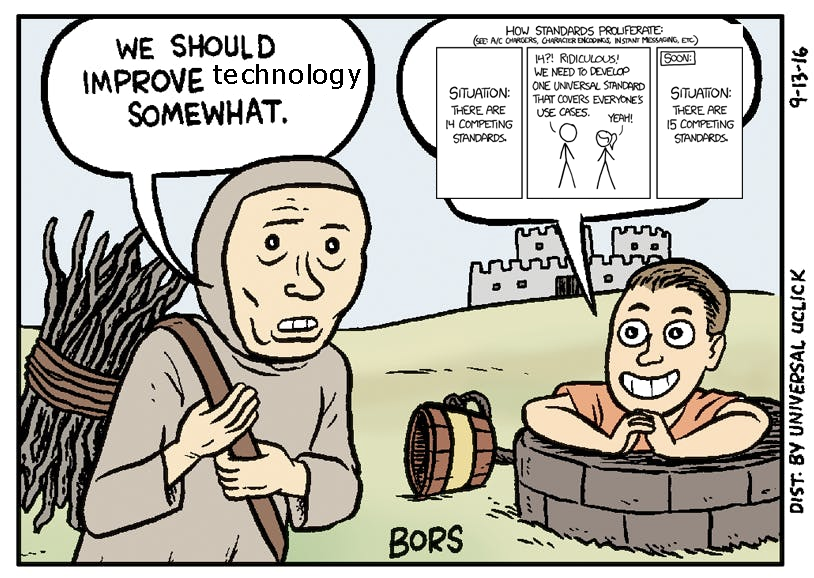
So someone suggests we need better standards to fix our tech problems, and naturally the solution is... creating yet another standard that competes with all the existing ones. Classic move. Now instead of 14 competing standards, we've got 15. The "dependency hell" title makes it even better because this is literally how we ended up with npm having 47 different date libraries and Python needing virtualenv just to survive. Every generation of developers thinks they'll be the ones to finally create THE universal solution, and every time we just add another layer to the chaos. It's like watching history repeat itself but with more GitHub stars.

Always Pin The Version Kids

Always Pin The Version Kids
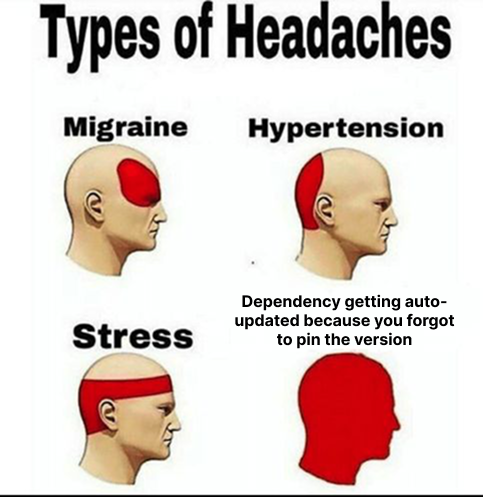
You know those medical diagrams showing different types of headaches? Well, here's the developer edition. Migraine? Cute. Hypertension? Amateur hour. But that fourth one—when your dependency auto-updates overnight because you were too lazy to pin the version in your package.json—that's when your entire head becomes pure, unadulterated pain. Nothing quite compares to arriving at work, running npm install , and watching your perfectly functioning app implode because some maintainer decided v2.0.0 was the perfect time to introduce 47 breaking changes. Your CI/CD pipeline is screaming, production is on fire, and you're frantically searching through changelogs at 9 AM trying to figure out why everything that worked yesterday is now a dumpster fire. Pro tip: ^1.2.3 is not your friend. That little caret is a ticking time bomb. Use exact versions like 1.2.3 or at minimum ~1.2.3 . Your future self will thank you when you're not debugging someone else's "improvements" at midnight.

Javascript Experience

Javascript Experience
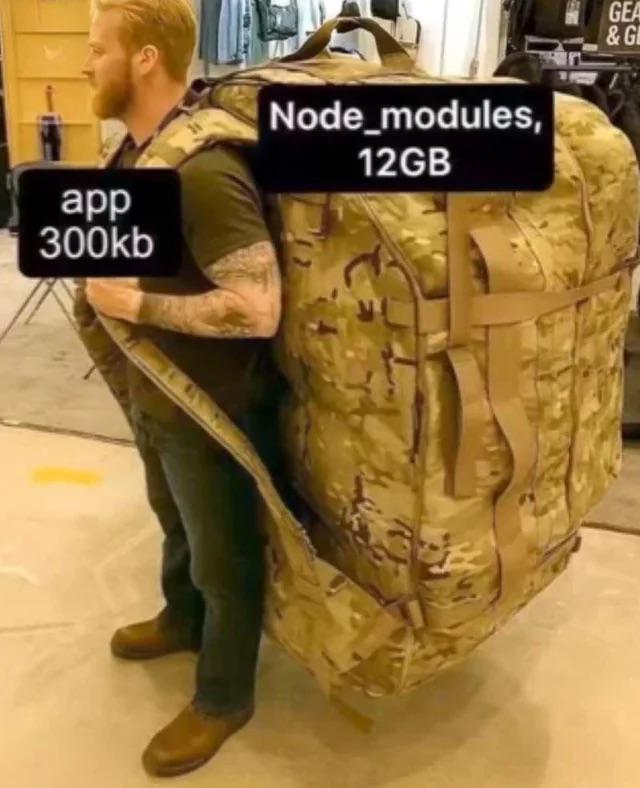
Your actual application: a modest 300KB of code that probably just displays a form and fetches some data. Your node_modules folder: a 12GB monstrosity that requires military-grade equipment to transport. Somewhere in there are 47 different versions of lodash, a left-pad implementation, and the entire Chromium browser bundled three times over. The ratio is absolutely unhinged. You installed one package, which had dependencies, which had dependencies, which had dependencies... and now you're carrying around more code than the Apollo 11 guidance computer used to land on the moon. All to center a div. Fun fact: If you delete node_modules, you can free up enough disk space to install another operating system. But you won't, because running npm install again is a 20-minute commitment and a prayer.

Gradlephants

Gradlephants
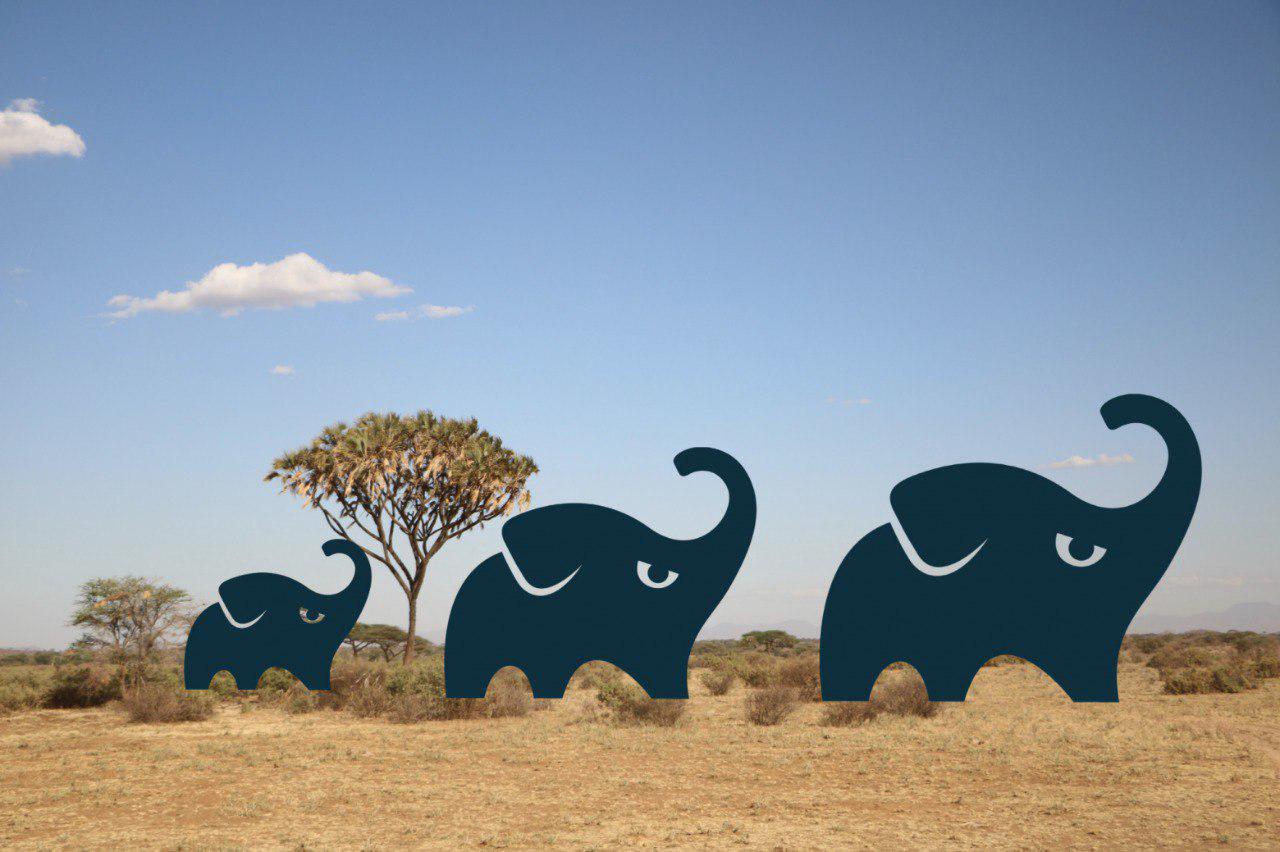
Three Gradle elephants standing in increasing size, each looking progressively more annoyed. Perfectly captures what happens when you add "just one more dependency" to your Android project. Started with a simple app? Baby elephant. Added some libraries? Medium elephant giving you side-eye. Included Firebase, Retrofit, Room, Dagger, Compose, and every other cool library you saw on Reddit? Congratulations, you now have a massive elephant that takes 47 minutes to build and crashes Android Studio twice a day. The Gradle elephant logo is iconic in the Java/Android world, and just like real elephants, your build files never forget... every single transitive dependency you've accumulated over the years.

You Should Have Gone For The Head

You Should Have Gone For The Head
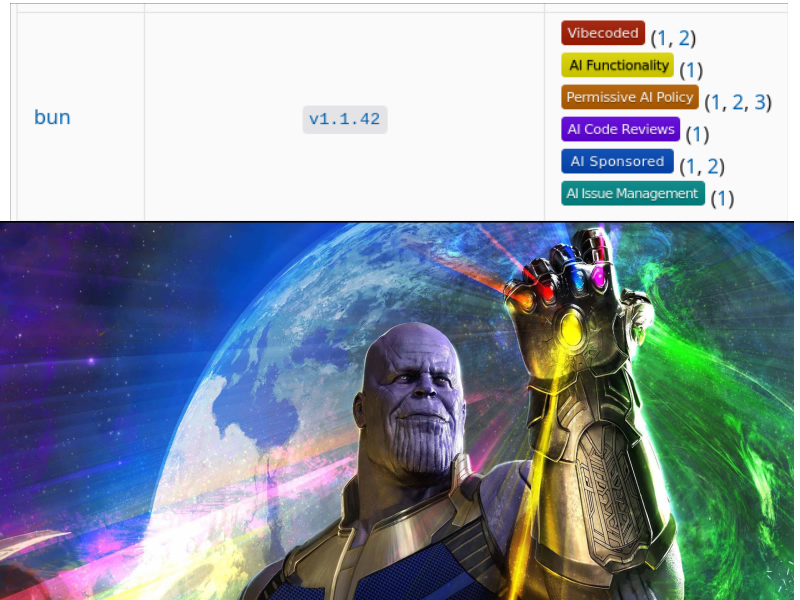
When you ship v1.1.42 of "bun" and suddenly your dependency tree looks like Thanos just collected all the Infinity Stones. Vibecoded? Check. AI Functionality? Obviously. Permissive AI Policy covering versions 1, 2, AND 3? You bet. AI Code Reviews, AI Sponsored content, AI Issue Management—it's like npm install but every package is sentient and has opinions about your code style. The real kicker is that single "bun" dependency somehow pulled in enough AI-powered middleware to achieve consciousness. Should've pinned those versions. Should've read the changelogs. Should've gone for the head and just used curl. Fun fact: Bun is a modern JavaScript runtime that's supposed to be faster than Node.js. Apparently it's also faster at accumulating questionable dependencies.

Conda Install Anaconda Conda

Conda Install Anaconda Conda
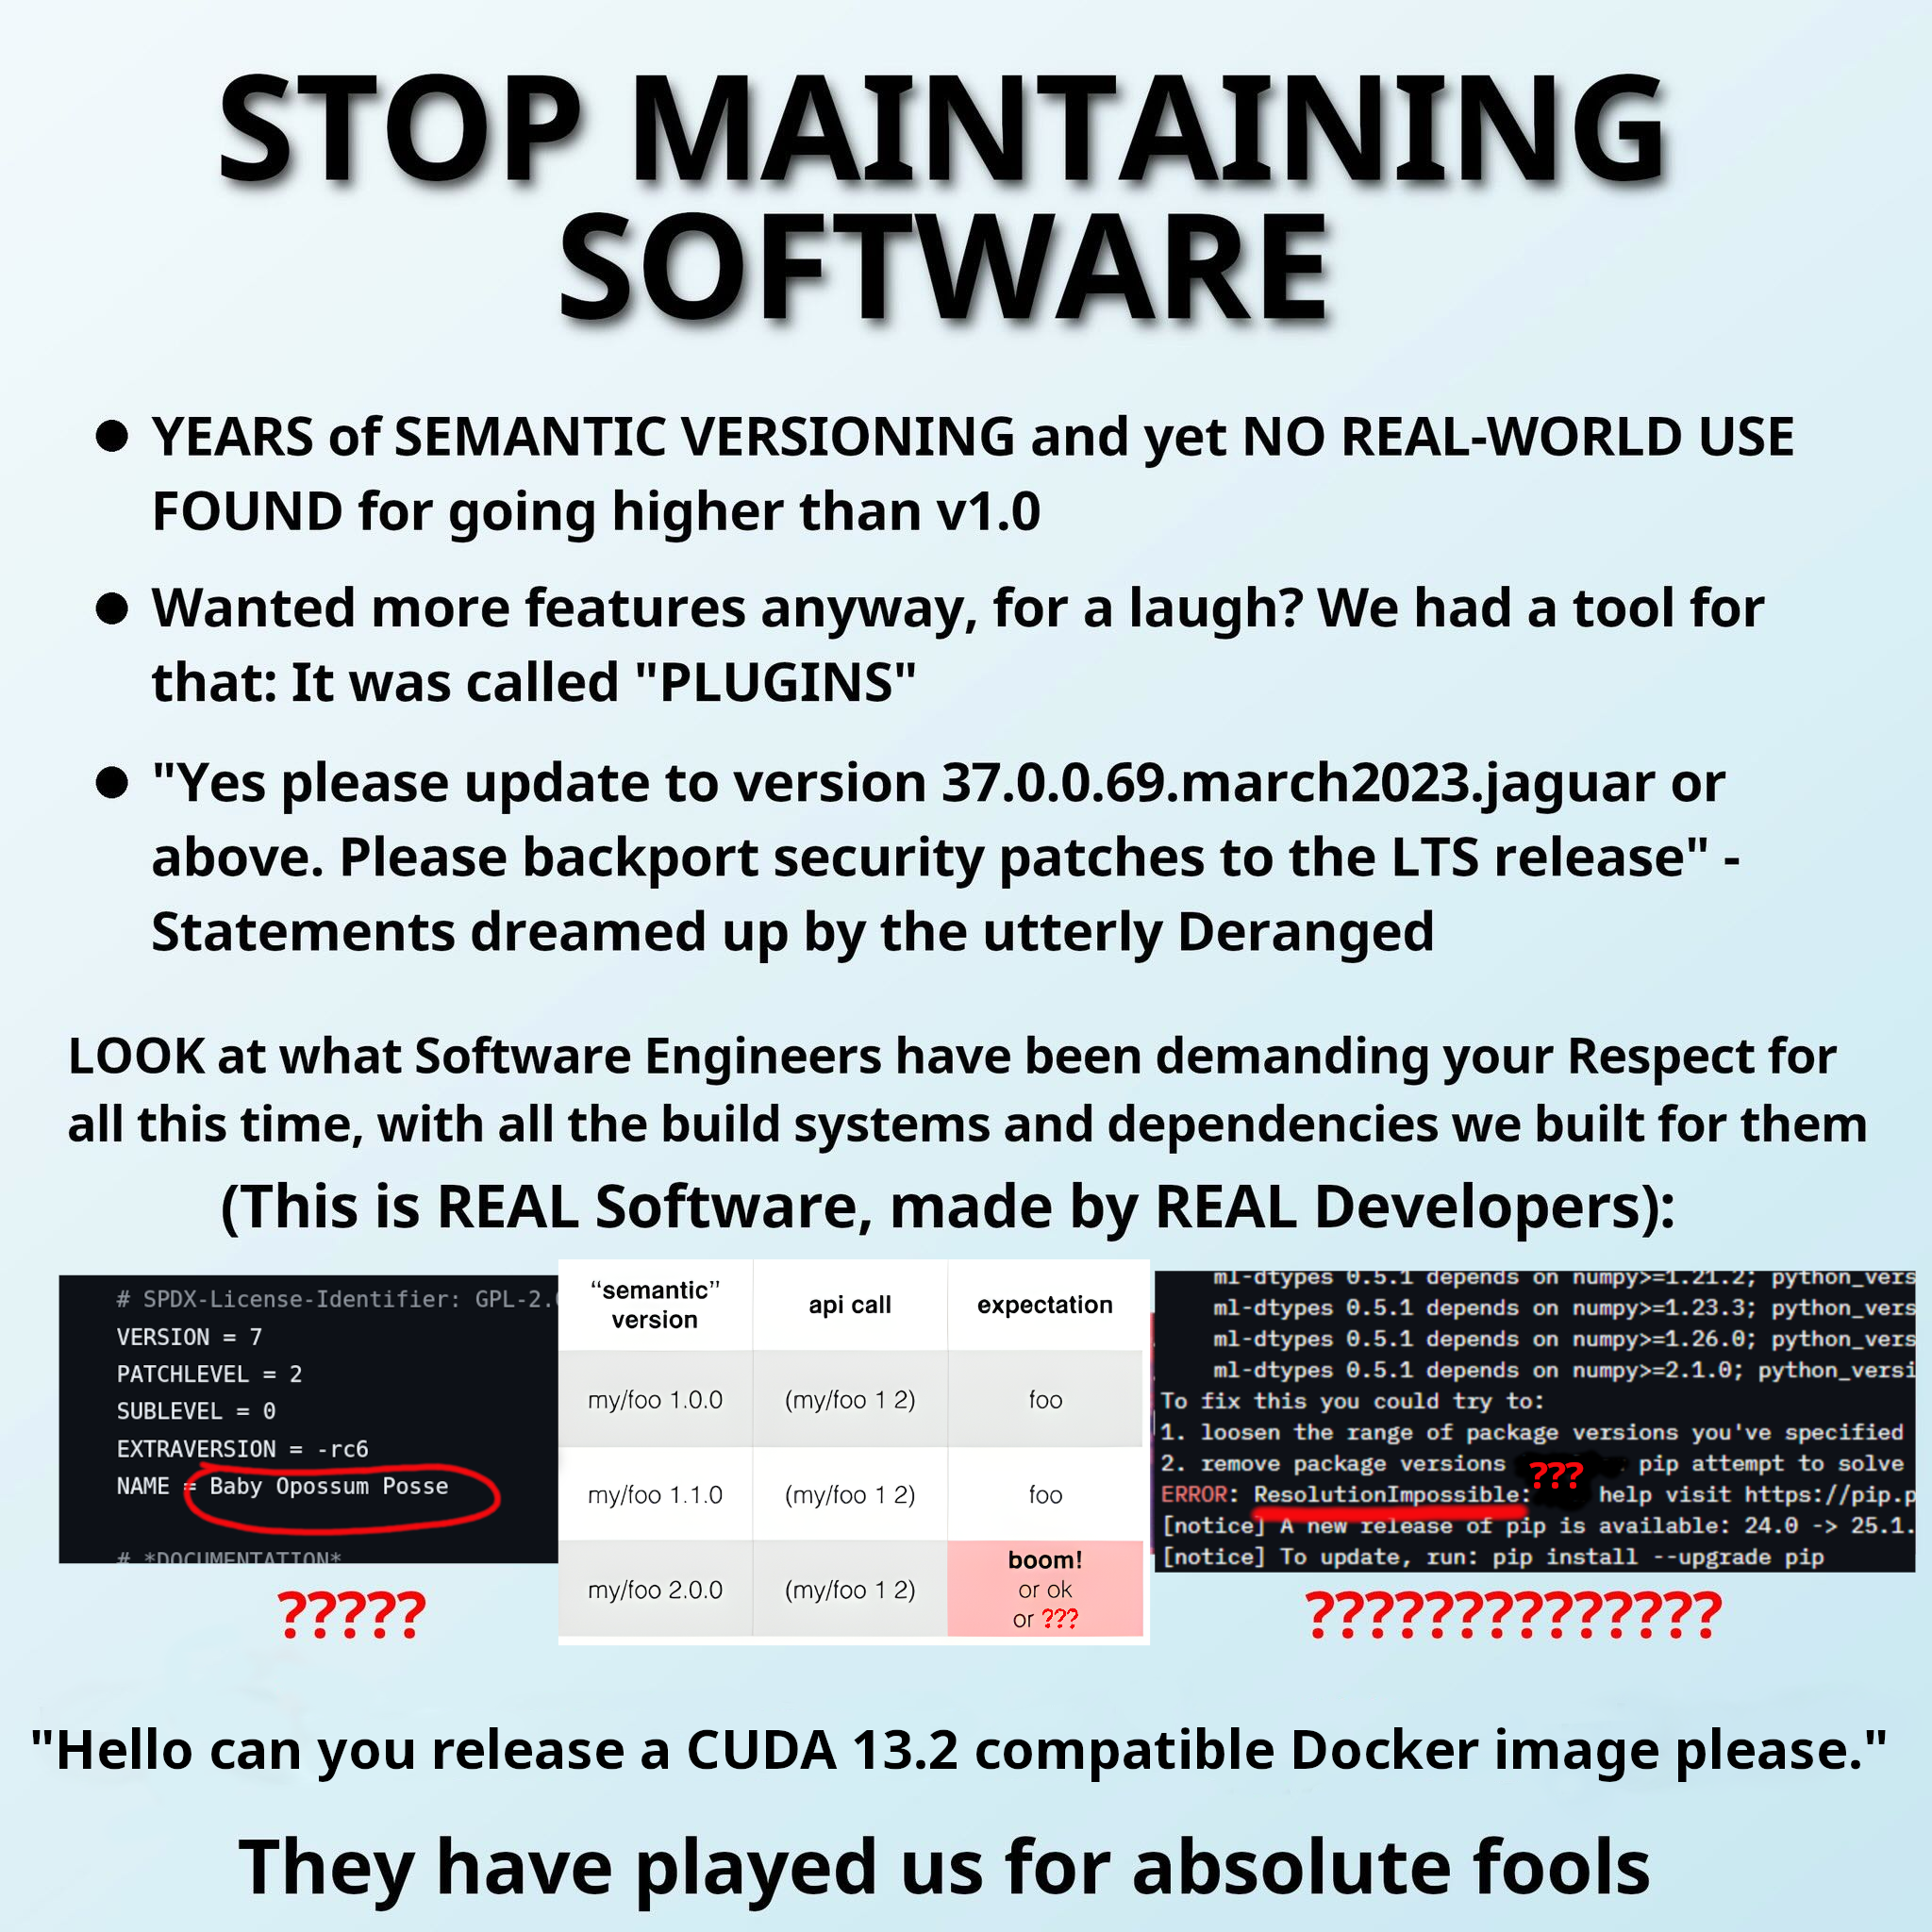
Package maintainers have finally snapped. After years of carefully crafting semantic versioning schemes that nobody respects, building dependency resolution systems that make traveling salesmen problems look trivial, and watching developers casually request "just backport the security patches to v1.0," they've had enough. The "Baby Opossum Posse" release name? Chef's kiss. The version number that looks like someone fell asleep on the keyboard? Poetry. And my personal favorite: the dependency hell screenshot where pip is having an existential crisis because ml-dtypes can't decide which version of numpy it wants to marry. But sure, go ahead and ask for that CUDA 13.2 compatible Docker image. I'm sure they'll get right on that, right after they finish implementing version "37.0.0.69.march2023.jaguar" and figure out whether "boom!" or "ok or ???" is the proper semantic versioning response. Turns out the real dependency hell was the respect we demanded along the way.

AOC 16" Portable Monitor FHD 60Hz USB-C IPS Ultra Slim Smart Cover 16T20 | 1920×1080 Computer Monitor, USB-C, Mini HDMI, Built-in Speakers, Smart Cover, Ultra Slim, VESA Mount, Low Blue Light

AOC 16" Portable Monitor FHD 60Hz USB-C IPS Ultra Slim Smart Cover 16T20 | 1920×1080 Computer Monitor, USB-C, Mini HDMI, Built-in Speakers, Smart Cover, Ultra Slim, VESA Mount, Low Blue Light
EXPAND YOUR WORKSPACE ANYWHERE - Add a flexible 15.6-inch portable second screen to your laptop for smoother multitasking, enhanced productivity, and more comfortable binge-watching—perfect for trave…