AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
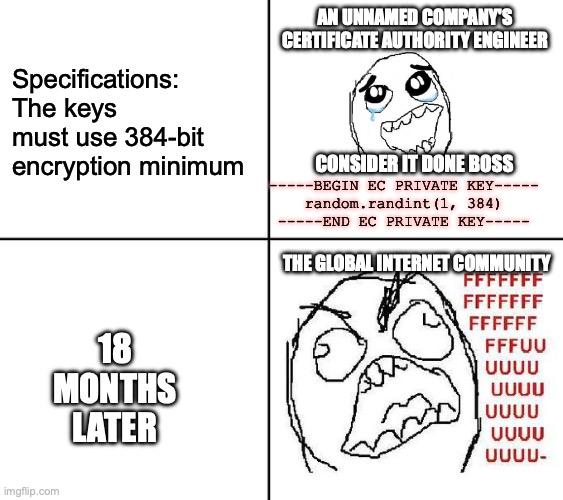
Certificate Authority engineer casually generates a 384-bit private key because the specs say "384-bit encryption minimum." Plot twist: they interpreted it as key size instead of encryption strength. Fast forward 18 months and the entire internet is collectively losing their minds because someone finally cracked it with what was probably a gaming rig and some free time.
For context: RSA keys should be at least 2048-bit nowadays (preferably 4096-bit), while 384-bit is laughably weak. It's like bringing a pool noodle to a sword fight. The spec probably meant 384-bit symmetric encryption (which would be overkill), but someone at "unnamed company" clearly skipped Cryptography 101.
The real kicker? It took 18 months for anyone to notice. That's either impressive incompetence or everyone was too busy arguing about tabs vs spaces to audit the actual security infrastructure.