cryptography Memes

Confused Look No Further

Confused Look No Further
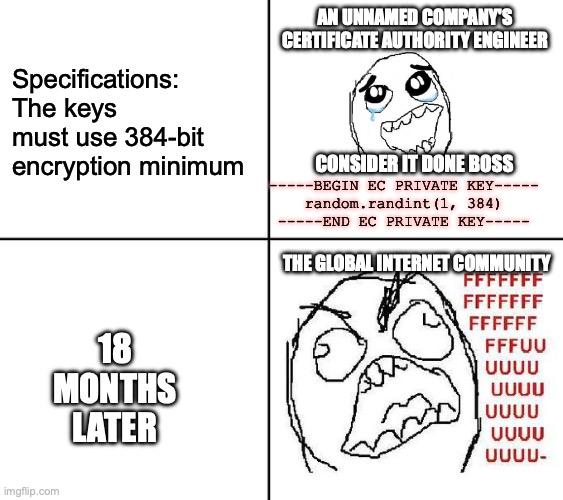
Certificate Authority engineer casually generates a 384-bit private key because the specs say "384-bit encryption minimum." Plot twist: they interpreted it as key size instead of encryption strength. Fast forward 18 months and the entire internet is collectively losing their minds because someone finally cracked it with what was probably a gaming rig and some free time. For context: RSA keys should be at least 2048-bit nowadays (preferably 4096-bit), while 384-bit is laughably weak. It's like bringing a pool noodle to a sword fight. The spec probably meant 384-bit symmetric encryption (which would be overkill), but someone at "unnamed company" clearly skipped Cryptography 101. The real kicker? It took 18 months for anyone to notice. That's either impressive incompetence or everyone was too busy arguing about tabs vs spaces to audit the actual security infrastructure.

Generate Private Key Under Bailiff Control

Generate Private Key Under Bailiff Control
Oh, the absolute AUDACITY of generating your private key while someone's literally watching over your shoulder! Nothing says "cryptographic security" quite like having a government official witness you create the one thing that's supposed to be, you know, PRIVATE. It's like shouting your password in a crowded room and then acting shocked when your account gets hacked. The entire point of a private key is that it stays private—not shared with bailiffs, not written on sticky notes, and definitely not generated under surveillance. But sure, let's just throw the fundamental principles of asymmetric cryptography out the window while we're at it! The serene Mediterranean backdrop really adds that chef's kiss of irony. Beautiful sunset, romantic setting, complete destruction of security best practices. Truly a moment to remember.

Trust Me Bro 384 Bit

Trust Me Bro 384 Bit
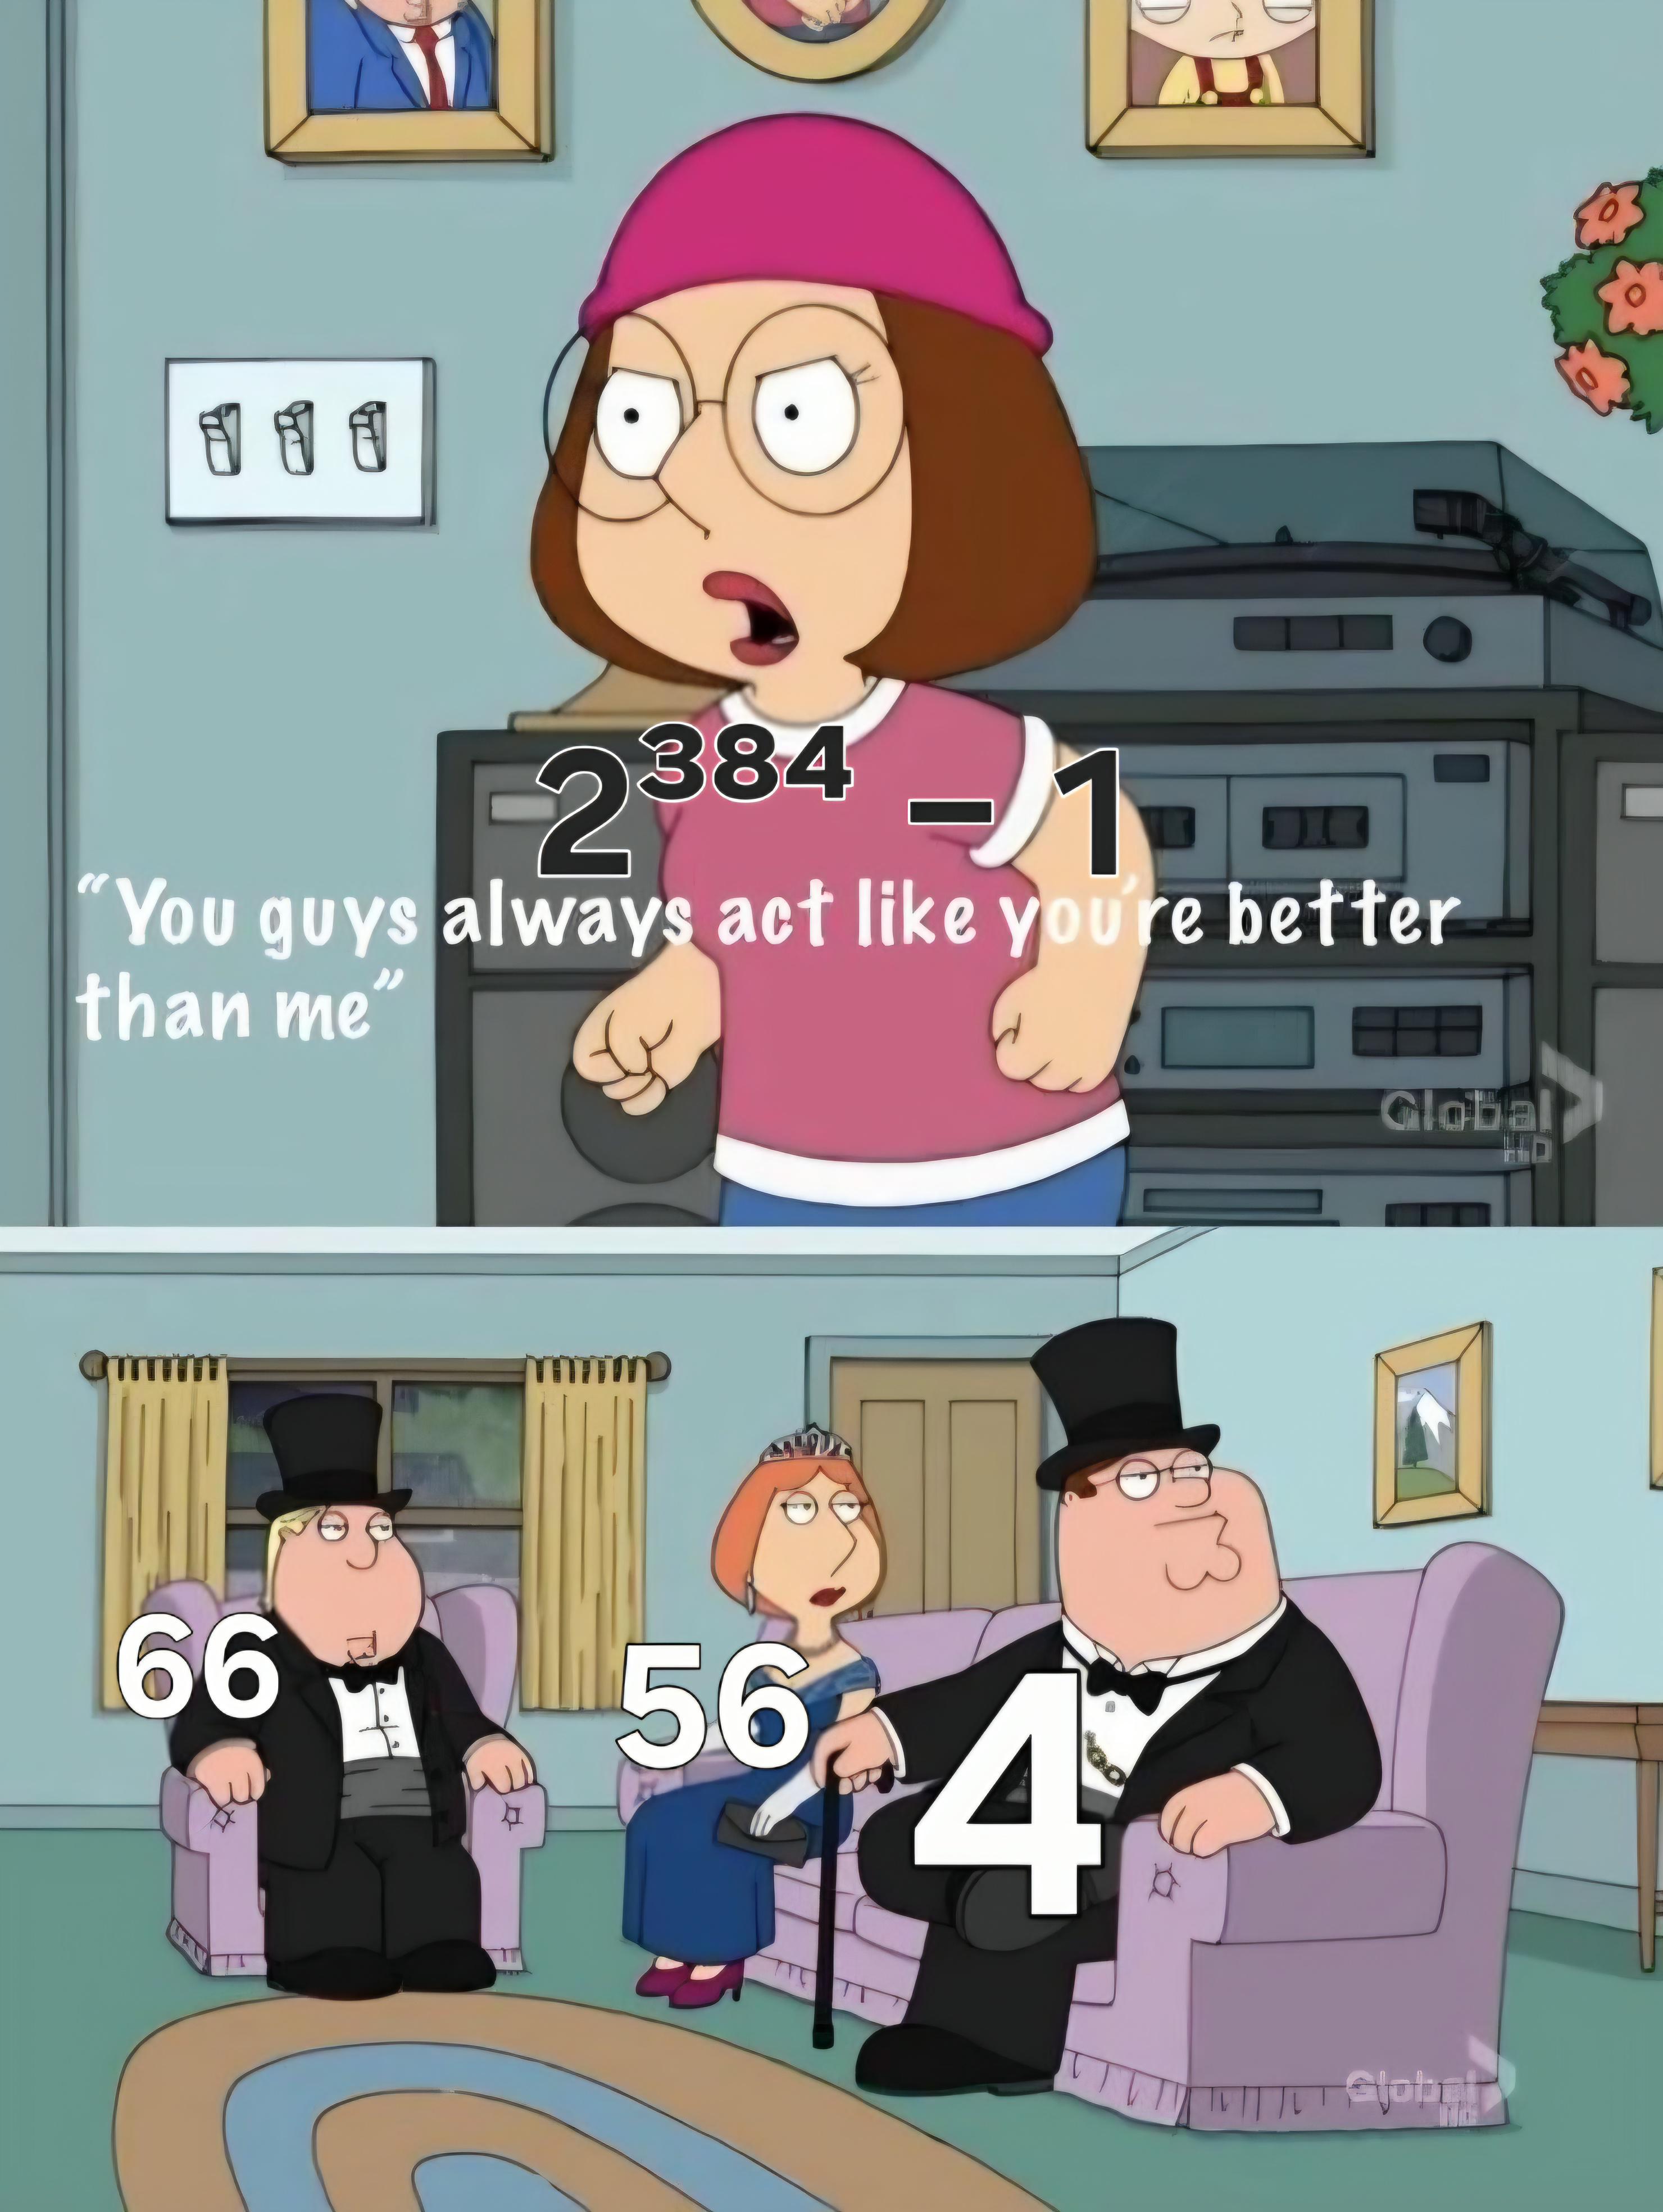
When someone brags about their "revolutionary" 384-bit encryption system, but the math just... doesn't check out. We've got 32-bit, 64-bit, 128-bit, 256-bit systems everywhere in computing, but 384-bit? That's 2^384 - 1, which is literally just flexing with numbers that don't align with standard computing architectures. It's like claiming your startup has "military-grade blockchain AI" when you're just using bcrypt with default settings. The fancy old-timey folks (representing established standards) are sitting there with their proper power-of-2 bit systems while someone's out here inventing random numbers. Sure, 384 exists in some niche crypto contexts, but it's giving major "I made this up in a pitch deck" energy. Nothing screams "I don't understand computer architecture" quite like confidently throwing out non-standard bit sizes to sound impressive.

Something Something Bits In A Private Key

Something Something Bits In A Private Key
When someone asks if a 4-bit encryption key is secure enough, the answer really does depend on context. Like, are you encrypting your grocery list? Sure, go wild. Your company's customer database? Yeah, that's getting cracked faster than you can say "data breach." For reference, a 4-bit key has exactly 16 possible combinations. That's not even brute-force territory—that's just... force. Meanwhile, modern encryption standards use 256-bit keys, which have more possible combinations than there are atoms in the observable universe. But hey, four is technically a number, so I guess it counts as encryption? The real kicker is watching junior devs discover that "security through obscurity" isn't actually a thing while their 8-character password requirement gets demolished in milliseconds. Context matters, people.

Four

Four
Someone just committed their EC private key to the repo with the BEGIN and END delimiters still attached, and honestly? That's the least of their problems. The real crime here is that our feline friend is showing us exactly four fingers—because nothing says "I understand elliptic curve cryptography" quite like accidentally exposing your private key in version control. The joke plays on the title "Four" and the visual of four fingers, but the actual security nightmare is that EC private keys should NEVER see the light of day, let alone get pushed to a public repository. Time to rotate those keys, revoke all certificates, and maybe add *.pem to your .gitignore before the security team finds out. Pro tip: If your private key has ever touched a commit history, it's not private anymore—it's just a very embarrassing public string.

The Original Source Of Top Secure Number

The Original Source Of Top Secure Number
Ah yes, the legendary number "4" - chosen by fair dice roll, guaranteed to be random. Developers everywhere are still using this battle-tested random number generation technique for their cryptographic keys, session tokens, and password salts. Why bother with complex RNG algorithms when you can just hardcode the winning lotto number? Security through obscurity at its finest. The fact that this number keeps winning the lottery just proves how truly random it is, right? Fun fact: This is actually a reference to the classic XKCD comic where someone generates a random number by rolling a dice and getting 4. The joke being that hardcoding a "random" value defeats the entire purpose of randomness - yet we've all seen production code with const RANDOM_NUMBER = 4; somewhere in the codebase.

BulbaCraft Data Science Stickers for Water Bottle and Laptop - Data Science Party Favors & Decorations, Waterproof Vinyl Decals, Tech and Coding Stickers, Gifts for Women & Men

BulbaCraft Data Science Stickers for Water Bottle and Laptop - Data Science Party Favors & Decorations, Waterproof Vinyl Decals, Tech and Coding Stickers, Gifts for Women & Men
HIGH QUALITY - You can be sure that only high-quality vinyl is used for Data Science stickers. Our stickers are made of durable vinyl material, ensuring long-lasting adhesion and vibrant colors. · ST…

Things To Say In A Job Interview

Things To Say In A Job Interview
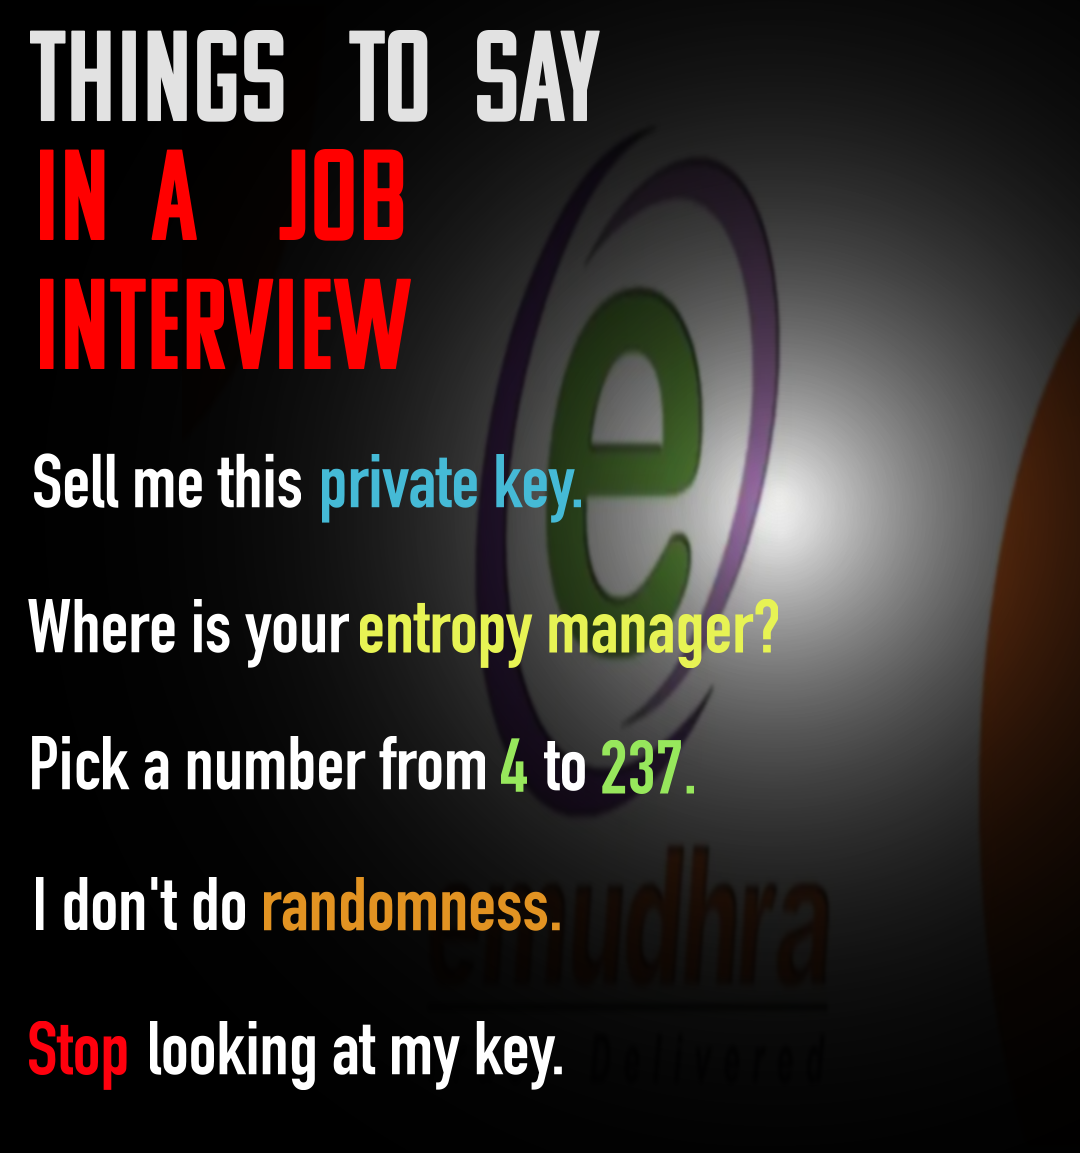
A comprehensive guide to getting immediately escorted out of any tech interview. "Sell me this private key" is the cryptographic equivalent of showing up to a bank interview and offering to sell them their own vault combination. "Where is your entropy manager?" - bold assumption that the company has their randomness organized when most can't even organize their Jira tickets. The number range 4 to 237 is oddly specific and perfectly captures the arbitrary constraints of bad RNG implementations. "I don't do randomness" - congratulations, you've just disqualified yourself from literally every security-related position. And finally, "Stop looking at my key" while presumably having your SSH private key visible on your screen is the cherry on top of this disaster sundae. Pro tip: if you need to say this during an interview, you've already failed the security clearance.

E Pseudorandom

E Pseudorandom
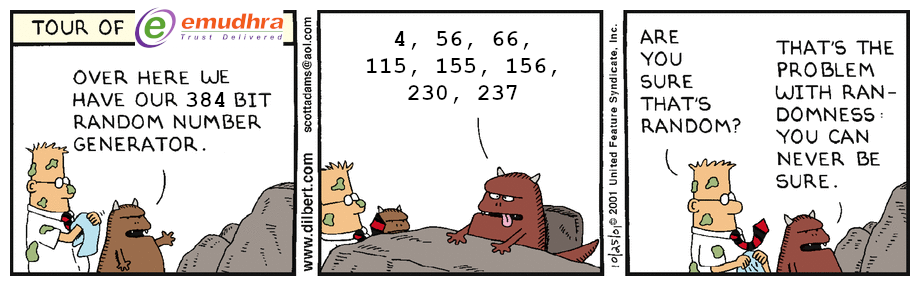
Tour guide shows off their fancy 384-bit random number generator. The beaver skeptically rattles off the output: "4, 56, 66, 115, 155, 156, 230, 237." Guide gets defensive: "Are you sure that's random?" Beaver drops the truth bomb: "That's the problem with randomness—you can never be sure." This hits different when you've spent hours debugging why your "random" test data keeps failing the same way. The philosophical paradox here is beautiful: truly random sequences can look suspiciously non-random, and our pattern-seeking brains reject them. Meanwhile, pseudorandom generators are deterministic algorithms pretending to be chaotic—which is exactly what we want 99% of the time because reproducible randomness is actually useful. The beaver's deadpan delivery captures every security researcher who's ever had to explain why Math.random() isn't cryptographically secure. You want real randomness? Go measure quantum phenomena or atmospheric noise. Otherwise, embrace the pseudo and seed it properly.

Private Key

Private Key
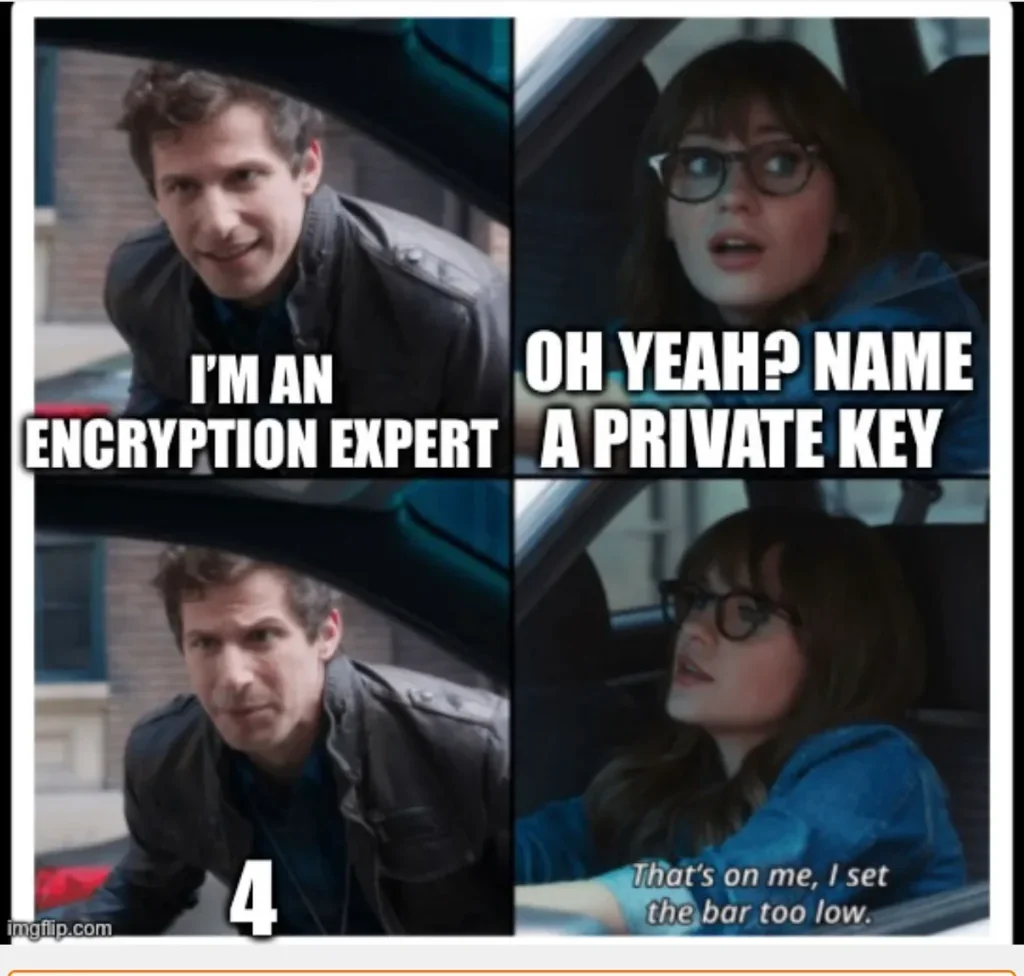
Every "encryption expert" until someone asks them to actually name a single private key they know. Turns out most of us just copy-paste from the .pem file and pray it works. The beauty of modern cryptography is that you can be an expert without actually knowing any of your keys—they're all just blobs of base64 nonsense living rent-free in your ~/.ssh folder. Setting the bar at "name 4 private keys" is like asking a chef to name 4 individual grains of rice in their pantry.

There Goes Customer Trust

There Goes Customer Trust
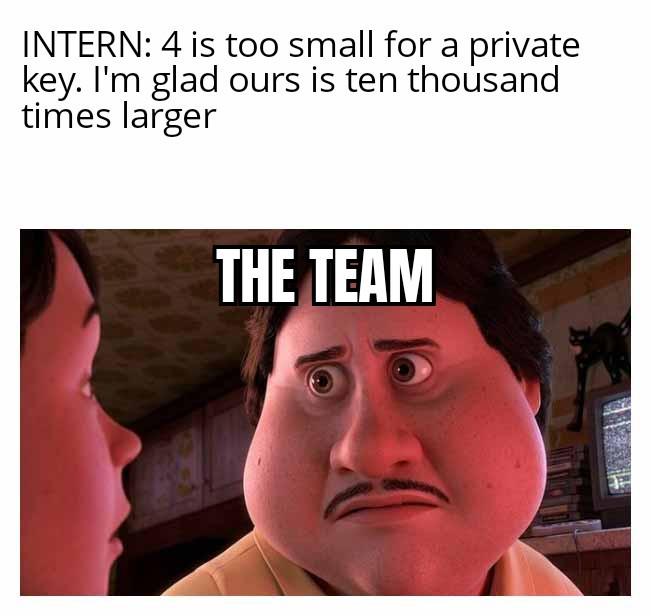
When your intern thinks a 4-bit encryption key is "too small" so they upgrade to 40,000 bits, the senior devs' souls collectively leave their bodies. Nothing screams "we have no idea what we're doing" quite like compensating for ignorance with absurd overkill. For context: modern RSA keys are typically 2048-4096 bits. A 40,000-bit key would be computationally ridiculous, slow everything to a crawl, and serve zero practical purpose. It's like using a nuclear warhead to kill a mosquito—technically effective, but everyone's now questioning your judgment and the building is gone.

ELZO Keyboard Wrist Rest Pad Support with 65D High-Density Thicken Memory Foam Padding, Ergonomic Design Computer Rest Pad Desk Wrist Mat, Non-Slip Rubber Base Office Laptop

ELZO Keyboard Wrist Rest Pad Support with 65D High-Density Thicken Memory Foam Padding, Ergonomic Design Computer Rest Pad Desk Wrist Mat, Non-Slip Rubber Base Office Laptop
Soft & Comfortable Material: ELZO keyboard palm rest is made of memory foam, slow bounces back and soft texture but it not easy to deform, ideal for longer hours of use. · Anti-Skid Bottom: Non-slip …

E Mudhra Employee Of The Month

E Mudhra Employee Of The Month
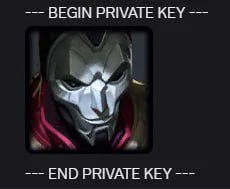
When you literally put your private key between "BEGIN PRIVATE KEY" and "END PRIVATE KEY" markers and commit it to a public repo, you've basically handed the villain their mask. E Mudhra (an Indian digital signature provider) had someone do exactly this—exposing cryptographic private keys that should've been guarded like nuclear launch codes. The image of the masked villain perfectly captures the energy of whoever got their hands on those keys. They didn't hack anything; they just read the manual that was accidentally left on the park bench. Pro tip: private keys belong in environment variables, secret managers, or literally anywhere except your codebase. Also, maybe don't win Employee of the Month for this one.

Not Insecure Just Unlucky

Not Insecure Just Unlucky
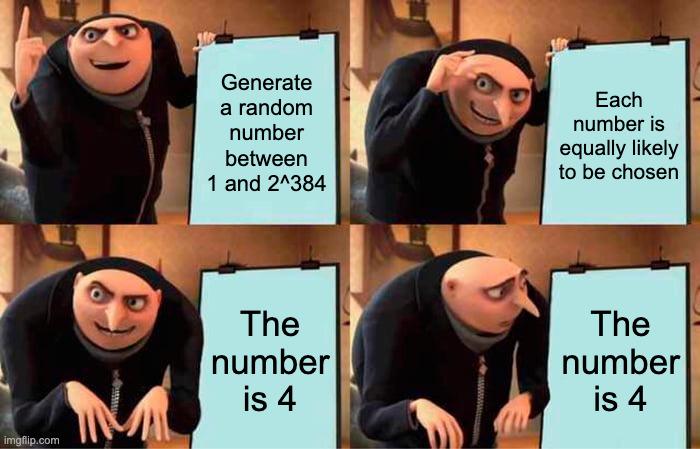
You ask your cryptographically secure random number generator for a number between 1 and 2^384 (that's 39 digits worth of possibilities, or roughly 10^115 unique values), and it confidently returns... 4. Twice in a row. Sure, the RNG is technically correct—4 IS within the range and each number has equal probability. But when you're dealing with a number space larger than the estimated number of atoms in the observable universe, getting the same single-digit number twice feels like the universe is gaslighting you. The security team swears the entropy is fine, but your gut says someone forgot to seed the generator properly. Nothing screams "we have a problem" quite like a PRNG with commitment issues to the number 4.