User input Memes

Posts tagged with User input
Bug Free App Meets Unchecked Unicode Chaos

Bug Free App Meets Unchecked Unicode Chaos
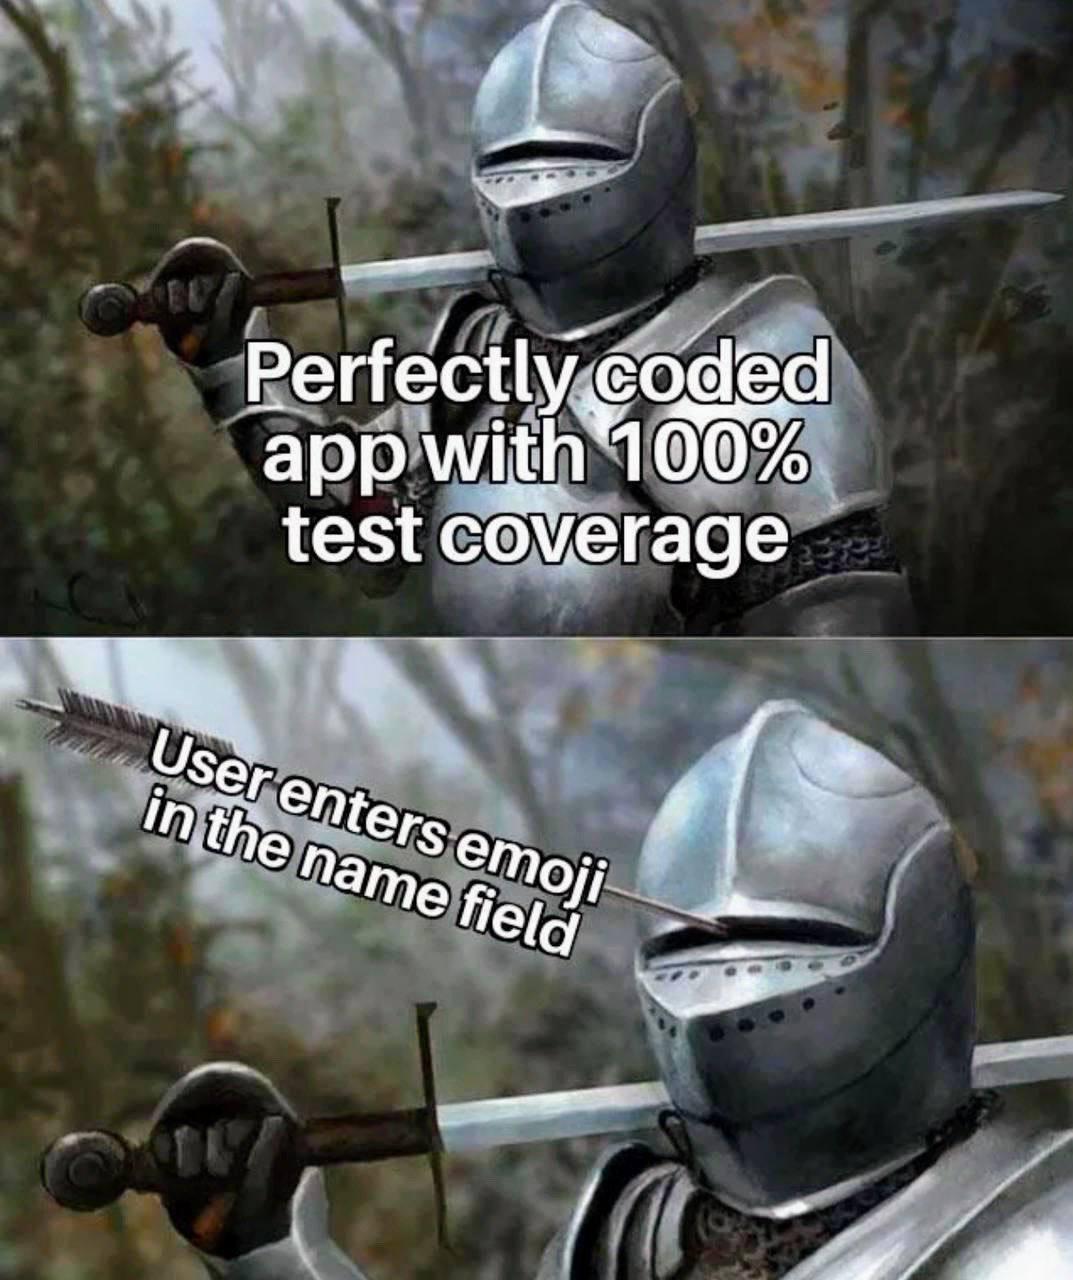
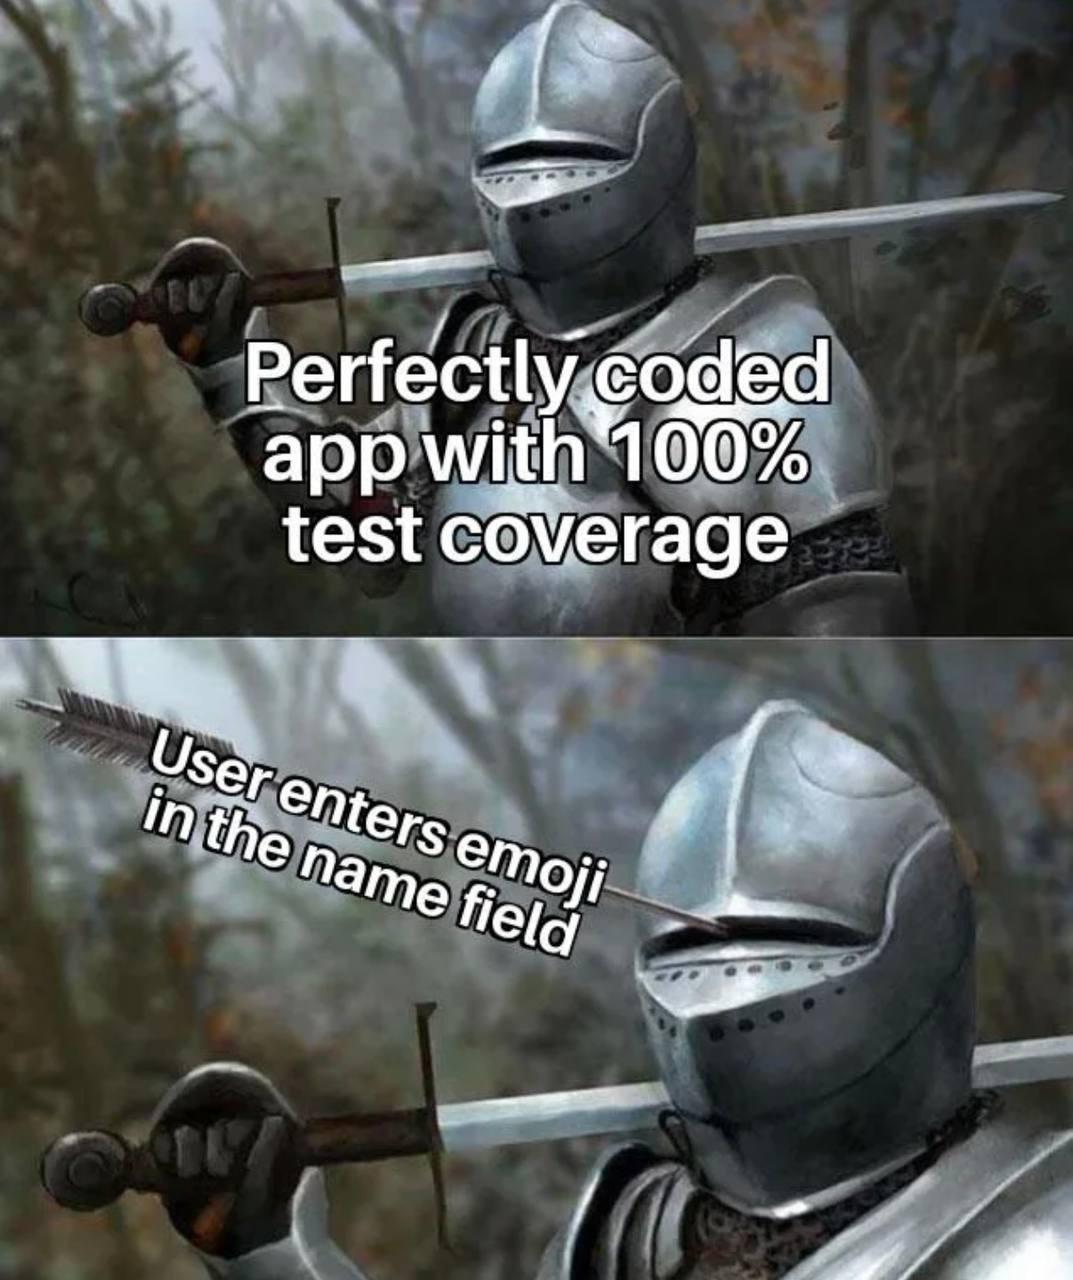
You spent months writing clean code, achieving that mythical 100% test coverage, and feeling like an invincible knight ready to conquer production. Then some user named "🔥💩🦄" tries to sign up and your database starts screaming in SQL injection nightmares while your logs look like a corrupted Word document from 1997. Your unit tests never accounted for the fact that humans are chaos agents who will absolutely put zero-width joiners, right-to-left override characters, and Egyptian hieroglyphics in a field that was clearly labeled "First Name." Input validation? Sure, you checked for alphanumeric characters. But did you check for Zalgo text? Didn't think so. Fun fact: Unicode has over 143,000 characters. Your regex that checks for "valid names" knows about maybe 52 of them. Good luck out there, knight.

When Your Validation Logic Hates Real People

When Your Validation Logic Hates Real People
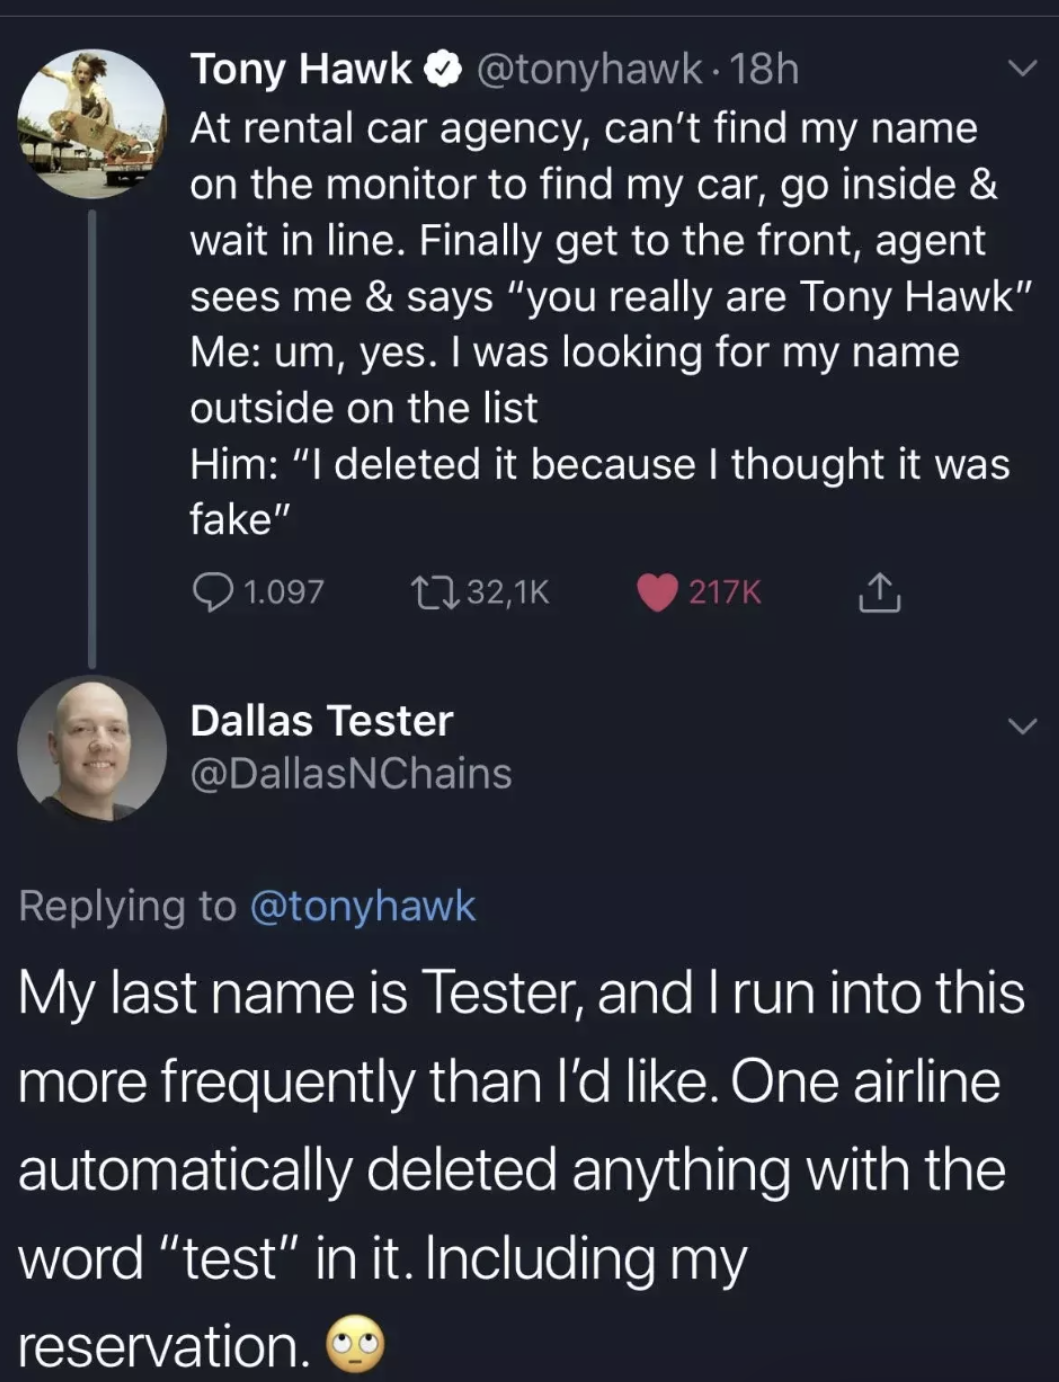
Tony Hawk gets deleted from a rental car system because his name sounds "too fake." Meanwhile, someone named Dallas Tester gets their airline reservation nuked because some genius dev wrote a regex that flags anything with "test" in it. Classic case of overzealous validation that assumes real people don't exist. You know that junior dev who wrote if (name.toLowerCase().includes('test')) { return false; } thinking they were being clever? Yeah, they just ruined someone's vacation. Production data cleanup scripts that nuke anything suspicious? They're out there right now, deleting real humans because their names fail the vibe check. Pro tip: Real people have weird names. They're called "Null," they work at companies named "DROP TABLE," and yes, some poor soul is actually named Tester. Your validation should protect against SQL injection, not against unfortunate parents with questionable naming choices.

Flawless Coverage Fatal Flaw

Flawless Coverage Fatal Flaw
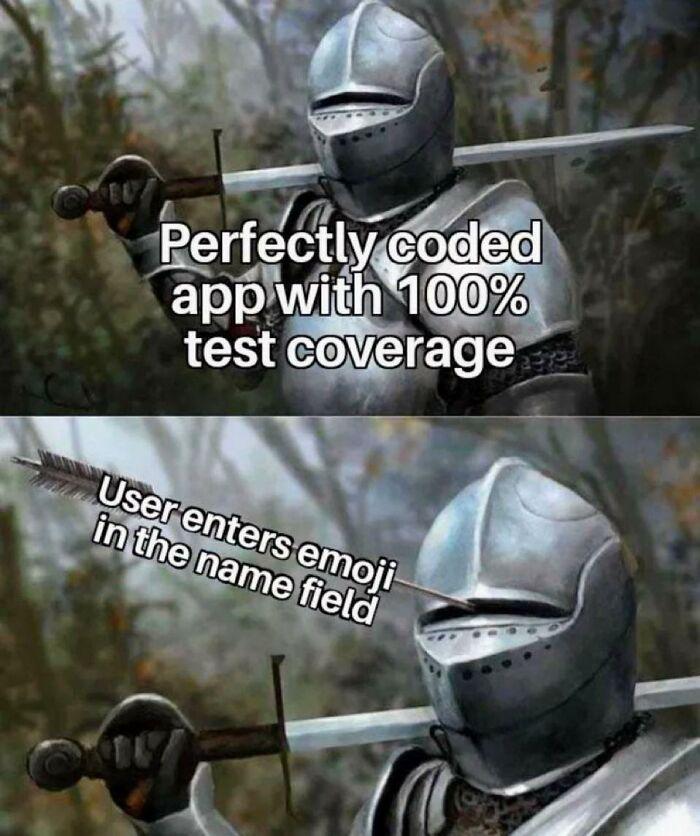
You wrote all your tests. You hit 100% coverage. You deployed with confidence. Then some user types "🎉" in the name field and your entire database implodes because nobody thought to test what happens when someone treats form validation like a suggestion. 100% test coverage just means you tested 100% of the scenarios you could imagine—not the ones users will definitely try. Your tests passed. Your app didn't.

Happens A Lot

Happens A Lot
You spent three weeks writing tests, achieving that beautiful 100% coverage badge, feeling invincible. Then some user types "🎉" in the name field and your entire application implodes like a dying star. Turns out your tests never considered that humans are chaos agents who will absolutely put emojis, SQL injections, and the entire Bee Movie script into a field labeled "First Name." 100% test coverage just means you tested 100% of what you thought could happen, not what actually happens in production.

What? I Pressed The Key...

What? I Pressed The Key...
Instructions say "press any key" and your brain immediately goes to the nuclear option. The power button is technically a key, right? Just a really consequential one that ends your session in the most dramatic way possible. Game developers write "press any key" thinking you'll hit spacebar or enter like a normal person. Instead, you're out here treating it like a multiple choice question where all answers are correct, including the one that shuts down the entire system. Classic case of taking requirements too literally—a skill every developer knows intimately from dealing with QA reports and user feedback. The blinking confusion afterwards is just *chef's kiss*. "But... I followed the instructions?"

SSK M.2 NVME SATA SSD Enclosure, Improved RTL9210B Chip USB 3.2 Gen 2 10Gbps to PCI-E NGFF Adapter, M-Key/B+M Key External SSD Enclosure Aluminum Support UASP Trim 2242/2260/2280

SSK M.2 NVME SATA SSD Enclosure, Improved RTL9210B Chip USB 3.2 Gen 2 10Gbps to PCI-E NGFF Adapter, M-Key/B+M Key External SSD Enclosure Aluminum Support UASP Trim 2242/2260/2280
Applicable SSD: This M.2 SSD Enclosure is for NVMe PCIE & SATA M-Key / B+M connectors M.2 SSD. Applicable to sizes 2242 / 2260 / 2280 solid state drivers. This SATA/ NVMe Enclosure does not support M…

The Final Boss User Input

The Final Boss User Input
You've spent weeks writing pristine code, achieved that mythical 100% test coverage, handled every edge case known to humanity... and then some user decides to put 🎉💀🔥 in the name field. Your entire validation layer just got obliterated by three Unicode characters. Because apparently, while you were busy testing for SQL injection and XSS attacks, nobody thought to ask "what if someone just... doesn't use letters?" Your regex that confidently checks for ^[a-zA-Z]+$ is now weeping in the corner while your database tries to figure out how to sort "John Smith" and "💩". Fun fact: Emojis are stored as multi-byte UTF-8 characters, which means your VARCHAR(50) field might actually only fit like 12 emojis. But sure, your tests passed. Your beautiful, emoji-less tests.

The Most Dangerous Character In SQL: (In)Visible

The Most Dangerous Character In SQL: (In)Visible
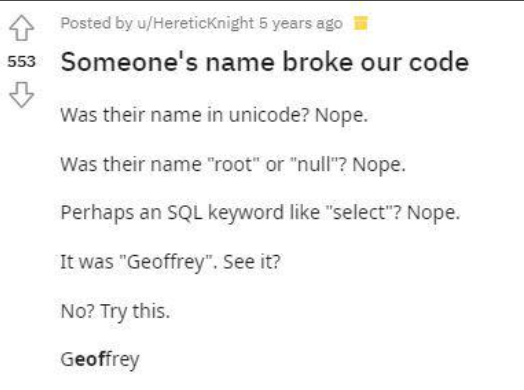
So someone named "Geoffrey" managed to nuke the entire system, and naturally everyone's playing detective trying to figure out what went wrong. Unicode characters? Nah. SQL injection with "root" or "null"? Not today. Maybe an SQL keyword like "select"? Keep guessing. Turns out it was just... Geoffrey. Except look closer at that last line. See the difference? Ge o ffrey vs Ge ο ffrey . That second "o" is the Greek omicron (ο) instead of a Latin "o". Visually identical, but to your database? Completely different characters. Welcome to the wonderful world of homoglyphs, where your WHERE clause confidently returns zero rows while you question your entire career. This is why we can't have nice things, and why every senior dev has trust issues with user input. Input validation isn't paranoia—it's pattern recognition from trauma.

The SQL Injection Feedback Loop

The SQL Injection Feedback Loop
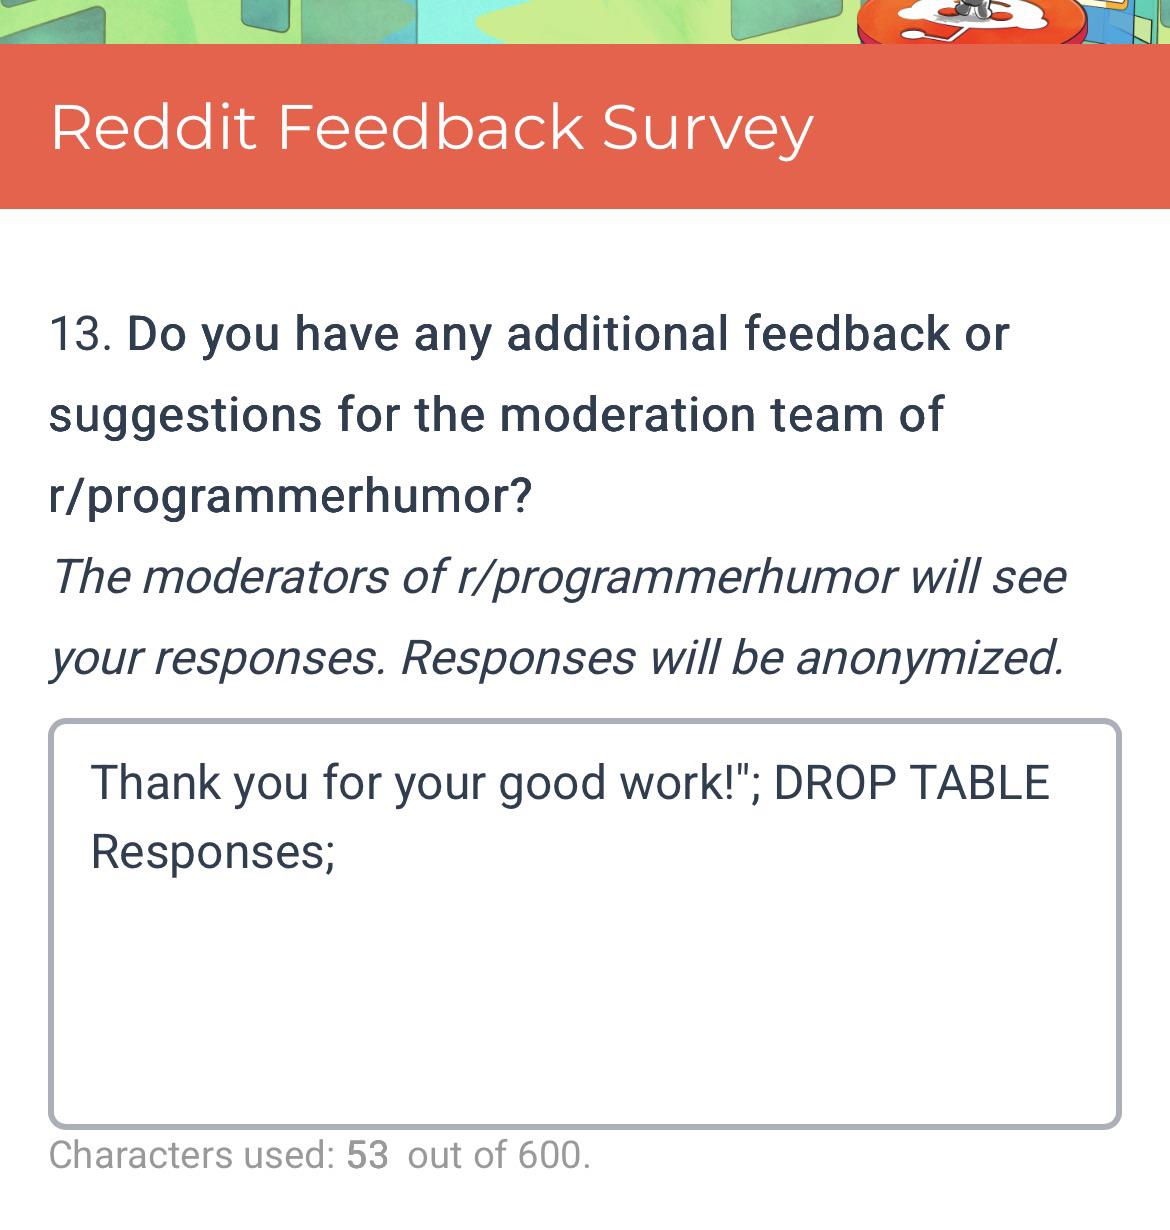
When SQL developers give feedback... Someone just executed the most ruthless SQL injection attack on that poor survey form! The classic "; DROP TABLE Responses; is basically the programmer equivalent of pulling the tablecloth out from under a fully set dinner table. The survey creator probably forgot to sanitize their inputs, and now all that precious community feedback exists only in the void of deleted data. Somewhere, a database admin just felt a disturbance in the force.

Just A Simple Boolean Question

Just A Simple Boolean Question
Ah, the eternal struggle of asking "Do you want pizza tonight?" and getting "I had pizza last Thursday but my cousin's birthday is coming up and I'm thinking about getting a haircut tomorrow." Boolean questions expect true/false answers, but non-technical people treat them like an invitation to write their autobiography. Meanwhile, developers sit there mentally trying to parse a 50-word response into a single bit of information. The worst part? You can't even throw an InvalidCastException at them and walk away.

There Are 10 Types Of People Programmer Coding Ceramic Mug, Yellow/White

There Are 10 Types Of People Programmer Coding Ceramic Mug, Yellow/White
Are you looking for a programmer Developer design for someone who loves working on computers and coding? · Then you should buy this fun IT specialist design! · 11-ounce ceramic mug is dishwasher and …

What Did I Do Wrong Here

What Did I Do Wrong Here
Ah, the classic integer overflow but for... other measurements! The terminal shows someone entering "7" inches, but somehow the calculation throws a DickLengthError claiming it "cannot be negative." Either the algorithm subtracted from the wrong base value, or someone's been exaggerating by about 2³² units. The exit code -69420 is just the chef's kiss of juvenile programmer humor—combining the infamous "69" with "420" and making it negative for extra absurdity. This is basically what happens when you let engineers build dating apps.

Well That Was Not In The Test Cases

Well That Was Not In The Test Cases
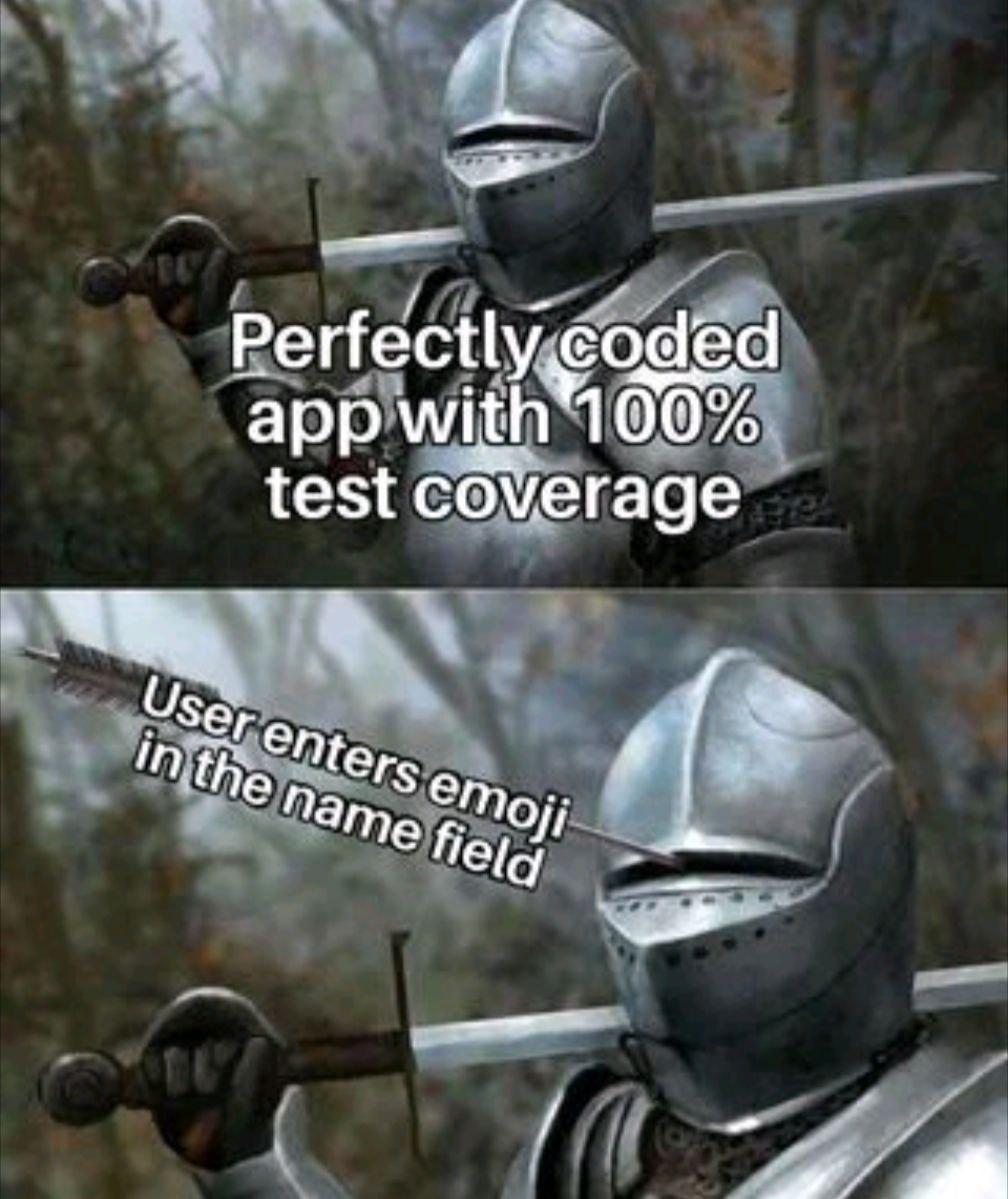
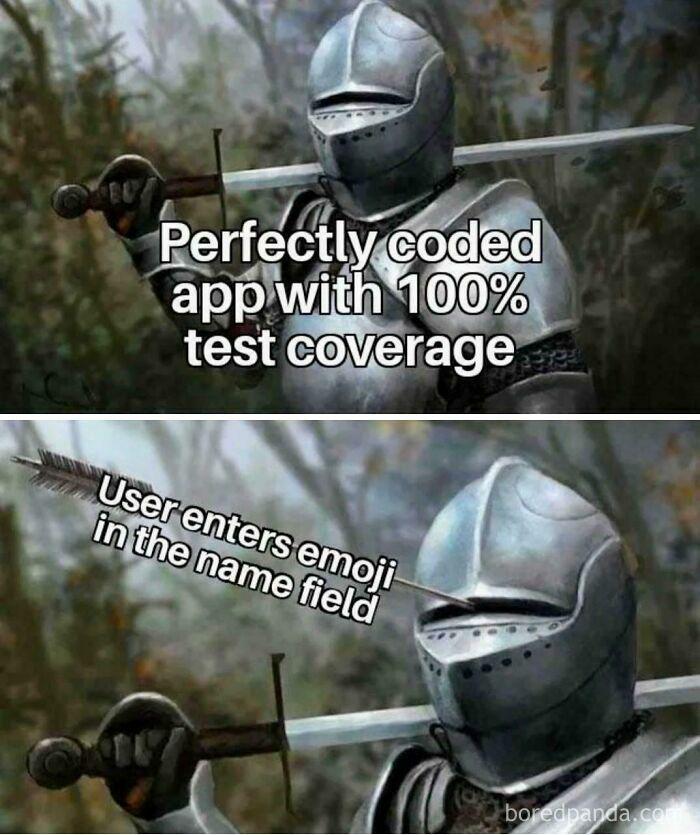
Ah yes, the mythical "100% test coverage" – the armor that shatters the moment a user types "🔥💩👻" where their name should be. Six months of unit tests, integration tests, and regression tests, yet somehow nobody thought to validate against the ancient enemy: Unicode. The knight's confidence in the first panel is every dev right before deployment. The arrow in the second panel is every production bug that makes you question your career choices. No amount of TDD can save you from the creativity of users with emoji keyboards.

Playtesters Quickly Discovered There Is No Explicit Cap To Display Names

Playtesters Quickly Discovered There Is No Explicit Cap To Display Names
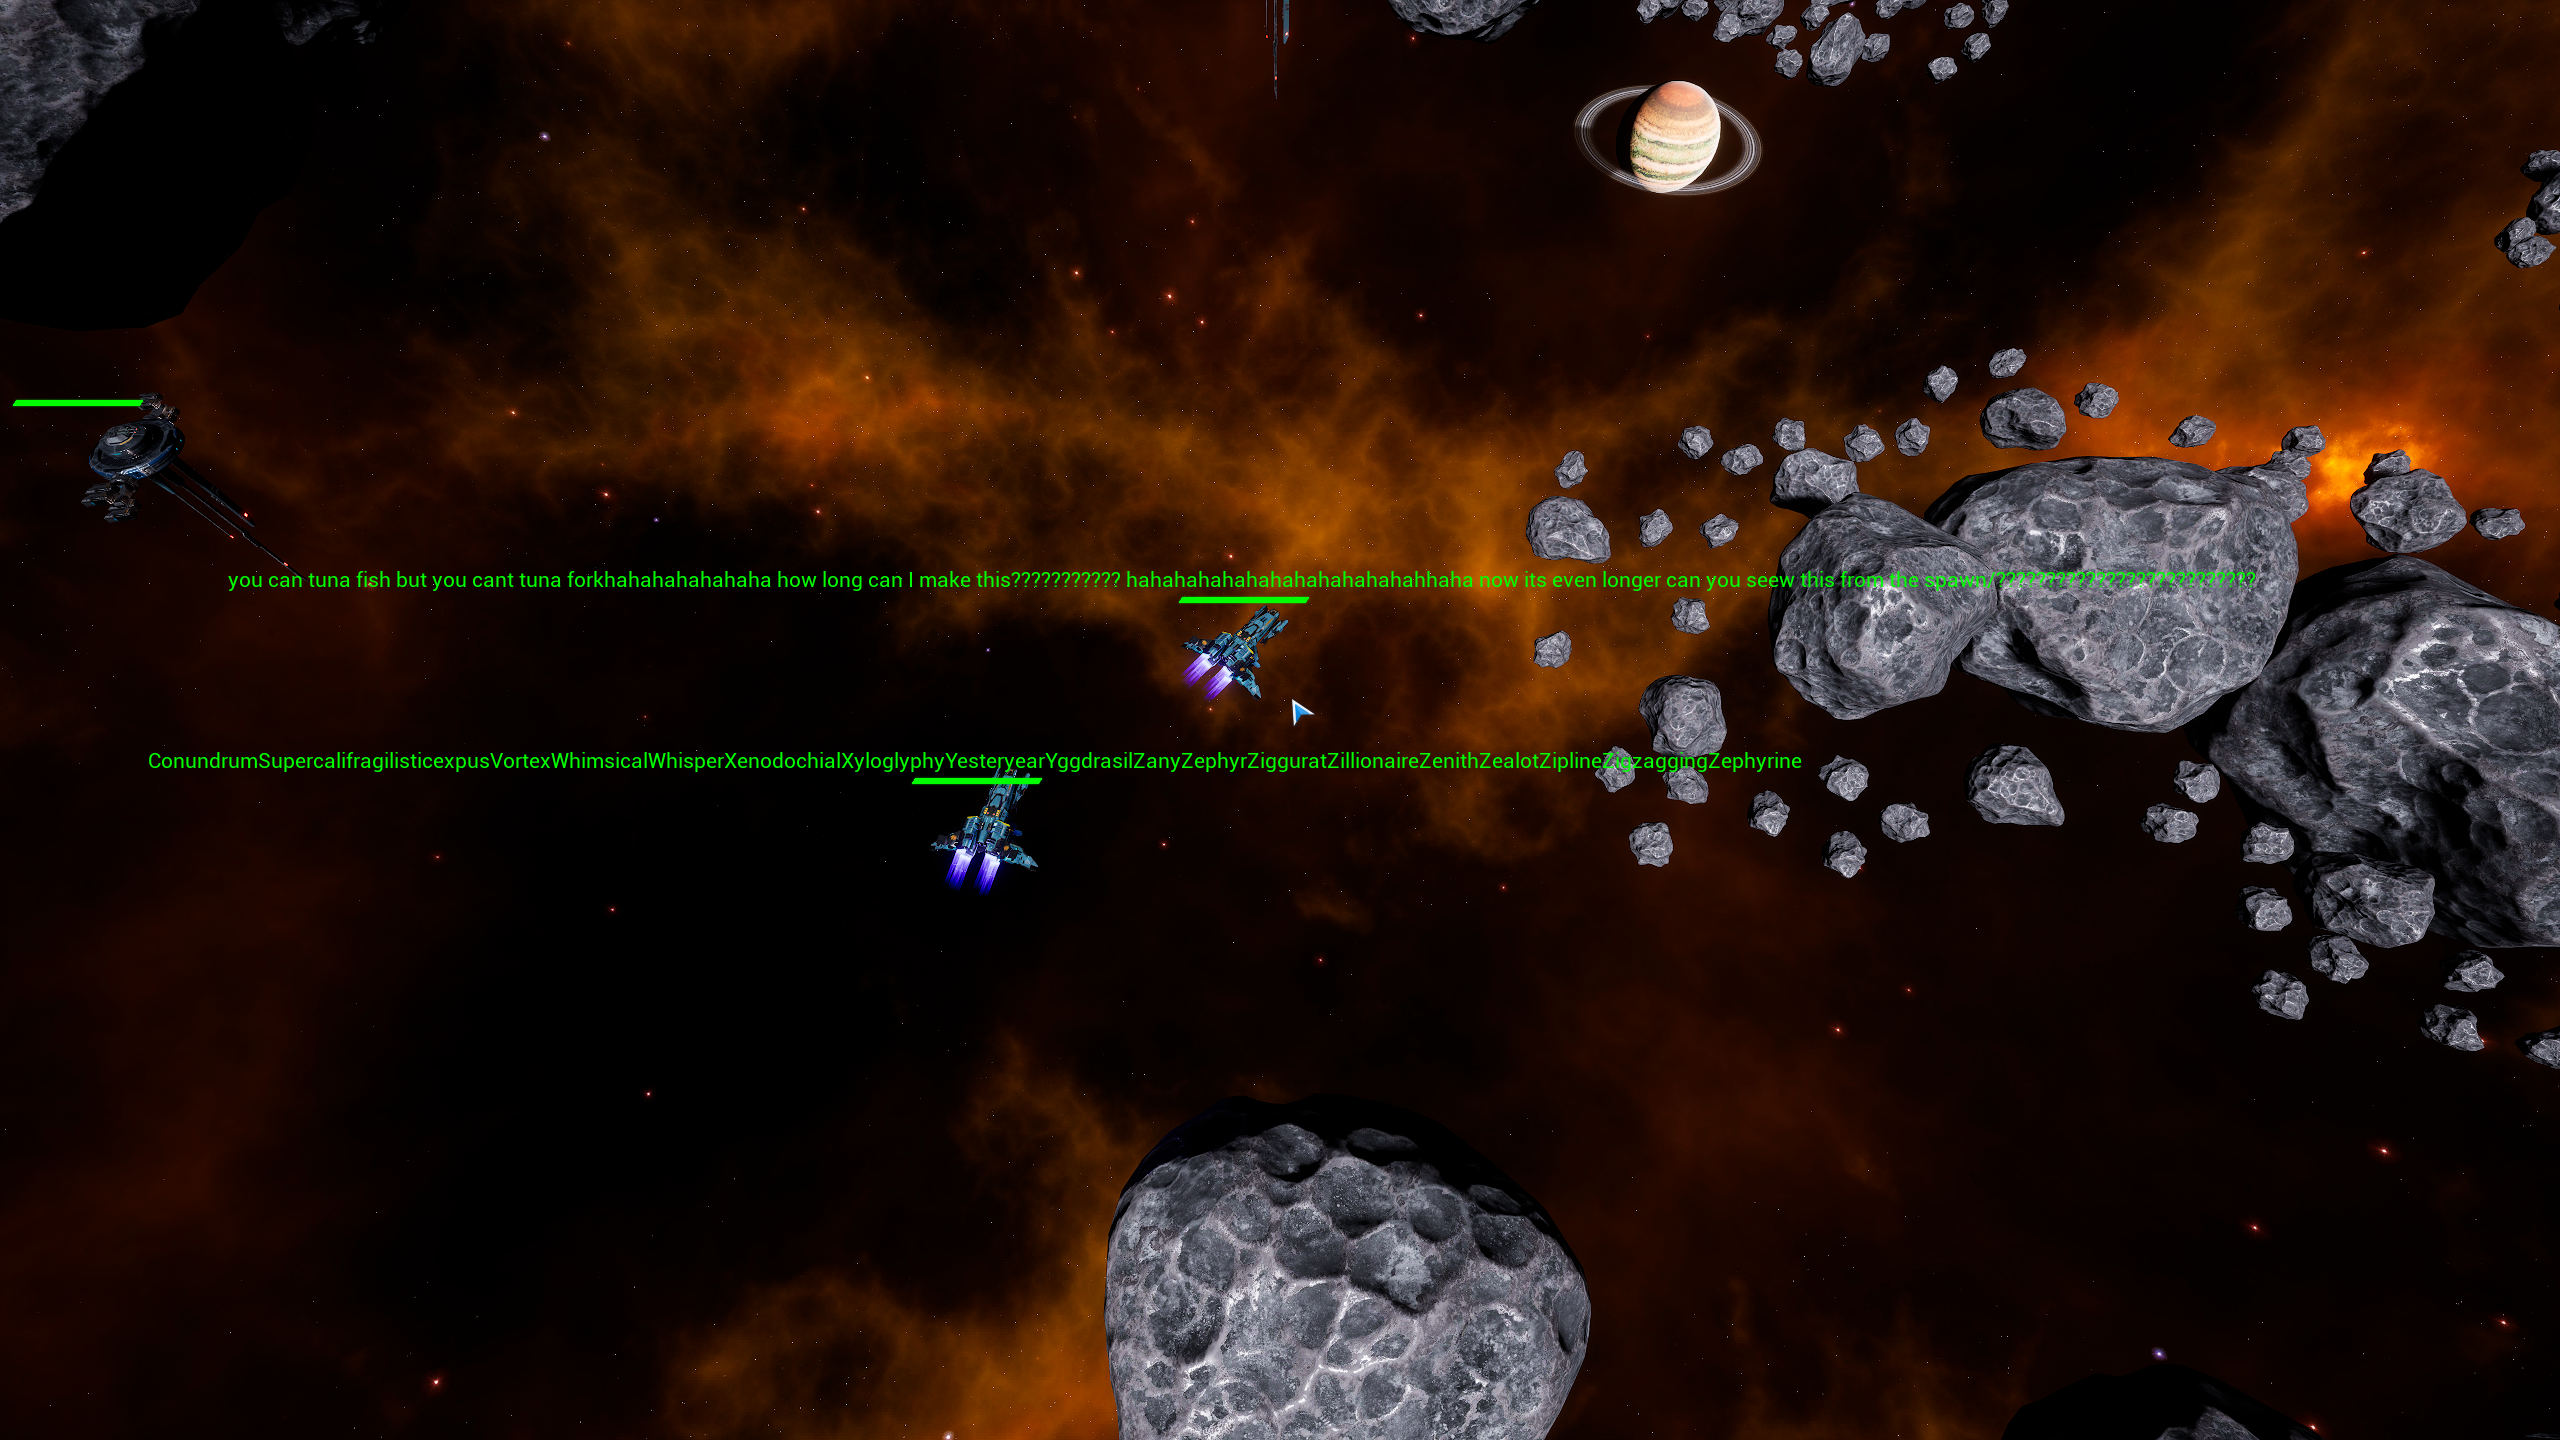
The first rule of game development: always sanitize your inputs . Some poor dev just learned that VARCHAR(255) isn't enough when players can create display names like "ConundrumSupercalifragilisticexpusVortexWhimsicalWhisperXenodochialXyloglyphyYesteryearYggdrasilZanyZephyrZigguratZillionaireZenithZealotZiplineZigzaggingZephyrine" while flying spaceships and making terrible tuna puns. The database admin is probably having a nervous breakdown right now while the QA team is laughing hysterically. And somewhere, a junior dev is frantically writing a regex at 2 AM that they'll eventually copy-paste from Stack Overflow anyway.