AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
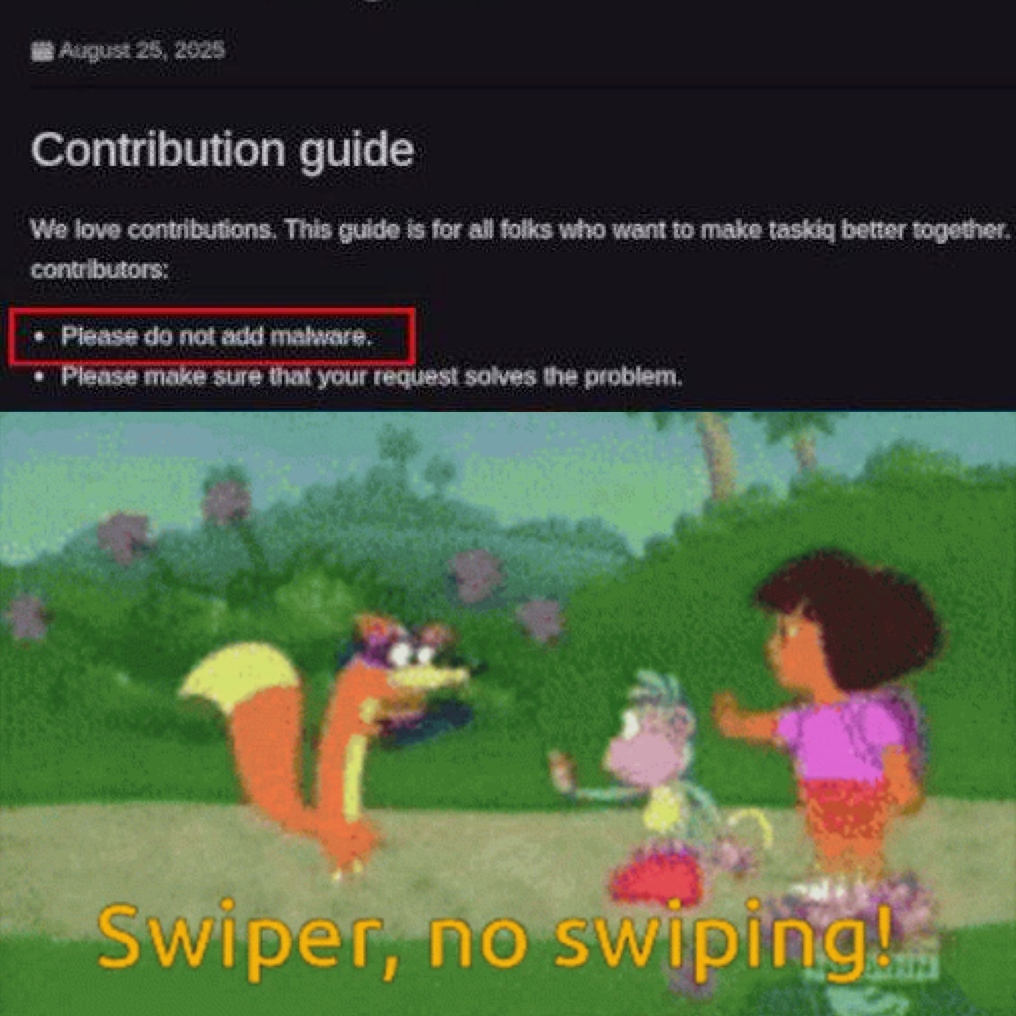
Open source maintainers having to explicitly tell contributors not to add malware is like telling a fox not to eat your chickens. That single bullet point in the contribution guide is doing some heavy lifting—as if malicious actors read documentation and go "oh darn, guess I'll have to find another repo to corrupt." The desperate plea of "Please do not add malware" has the same energy as Dora telling Swiper not to swipe. Spoiler alert: Swiper's gonna swipe anyway.
Pretty Please Don't Hack Our Users
open-source-memes, security-memes, git-memes, contribution-guidelines-memes, malware-memes | ProgrammerHumor.io
More Like This