AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
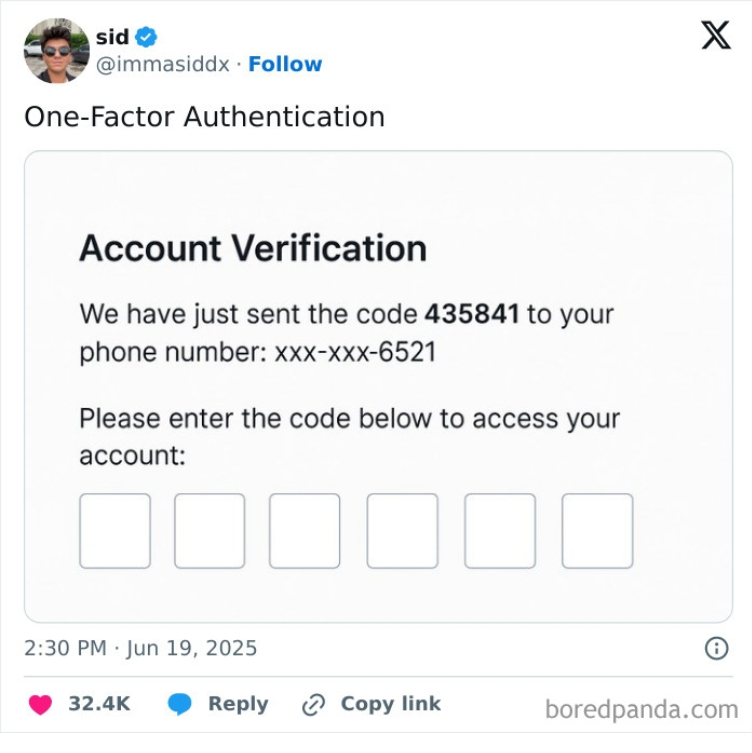
So they literally put the verification code right there in the message. You know, the one you're supposed to enter to prove you received it. The whole point of 2FA is that an attacker who doesn't have access to your phone can't log in... but if they intercept this message, they can just read the code without needing to actually receive it on the device.
It's like putting a lock on your door and then leaving the key taped to the lock with a note saying "this is the key." Security theater at its finest. Someone's product manager probably said "let's make it more user-friendly" and the security team just quietly wept into their coffee.