2fa Memes

Posts tagged with 2fa
These F-Ing Logins Nowadays

These F-Ing Logins Nowadays
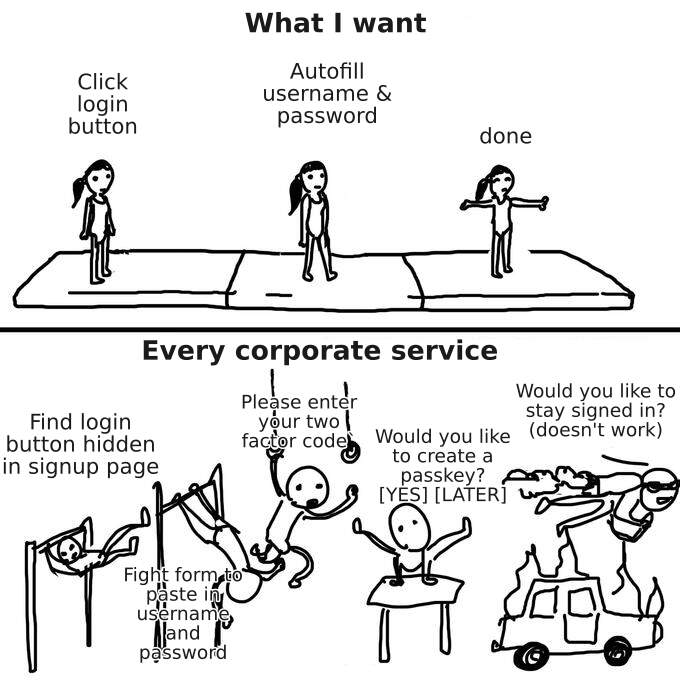
Remember when logging in was just... logging in? Now it's like navigating an obstacle course designed by someone who clearly hates their users. You want three simple steps. Corporate security theater gives you: a login button playing hide-and-seek in a signup page, 2FA codes that expire faster than your will to live, passkey prompts that don't actually work, and that one feature to "stay signed in" that's purely decorative. The kicker? Half the time your password manager can't even autofill because some genius frontend dev decided to get creative with input field names. So you're there, fighting the form like it owes you money, manually copy-pasting credentials like it's 2005. Security is important, sure. But maybe we've overcomplicated things just a tiny bit when logging into your expense report system requires more steps than launching nuclear missiles.

Ok Google

Ok Google
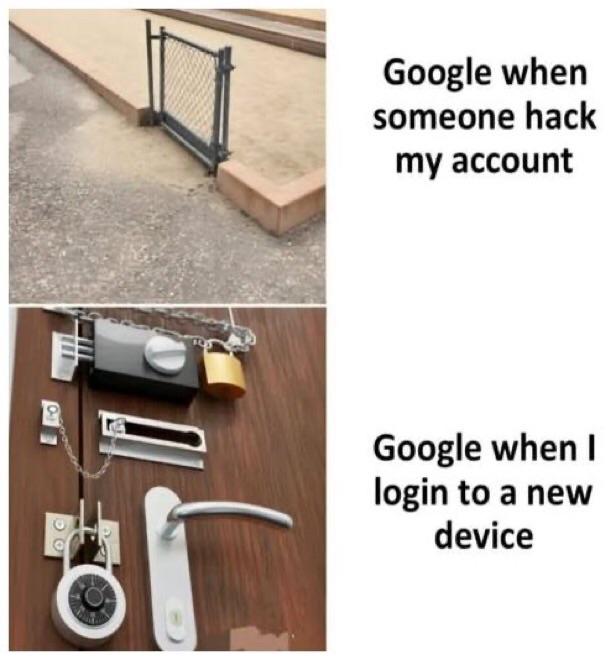
Google's security priorities are... interesting. When an actual hacker compromises your account from a sketchy IP in a country you've never visited? Here's a tiny decorative fence that a toddler could step over. But the moment YOU try to log in from your new laptop while sitting in your own house? Time to deploy Fort Knox with every lock, chain, padlock, and authentication method known to humanity. The irony is legendary: Google will let someone drain your entire email history with a flimsy password reset, but when you legitimately buy a new device, suddenly you need to verify your identity through 2FA, backup codes, a blood sample, your firstborn child, and that one security question you set up in 2009 about your childhood pet whose name you definitely don't remember anymore. It's the classic case of security theater where the legitimate user gets punished while actual threats slip through. Maybe Google's ML models just really hate new device purchases.

Zero Factor Authentication

Zero Factor Authentication
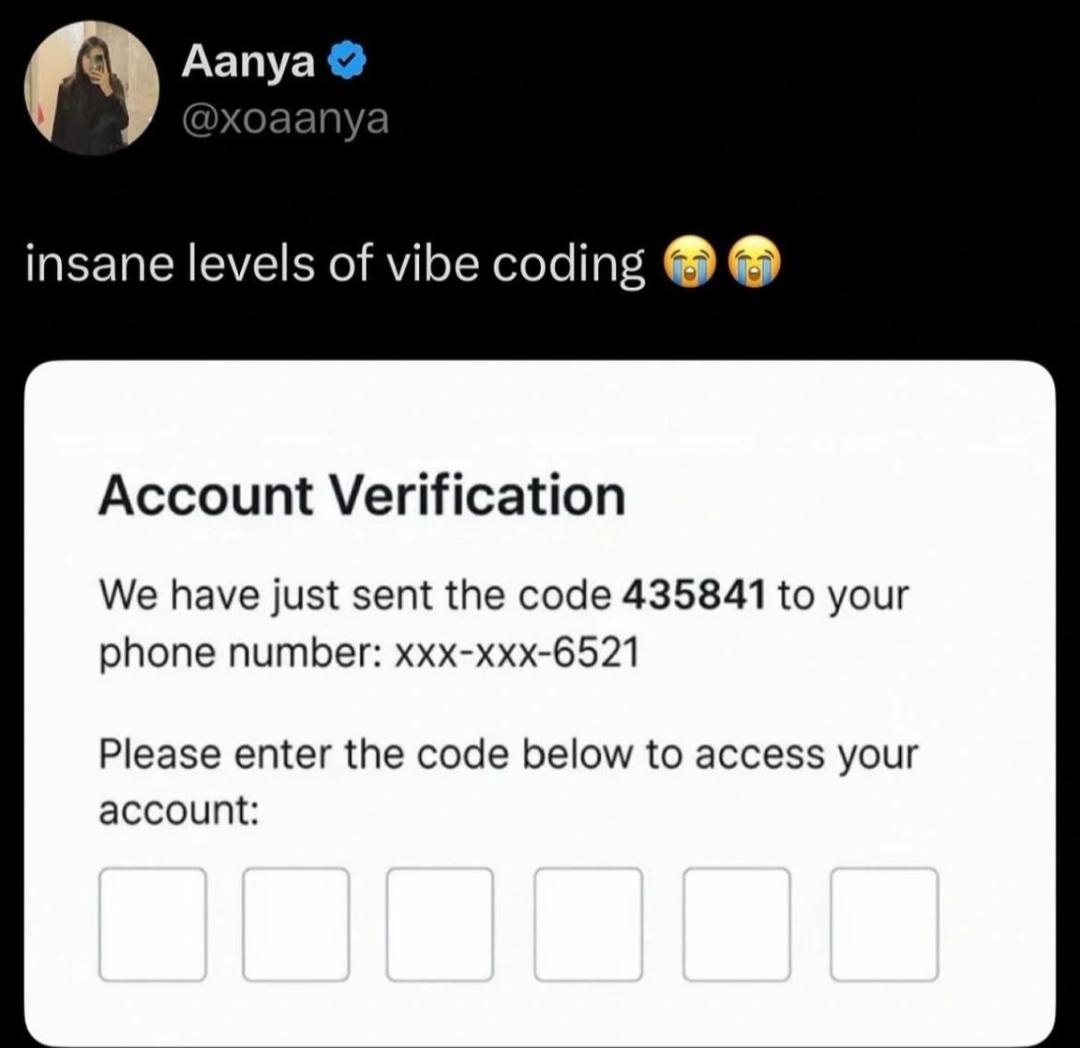
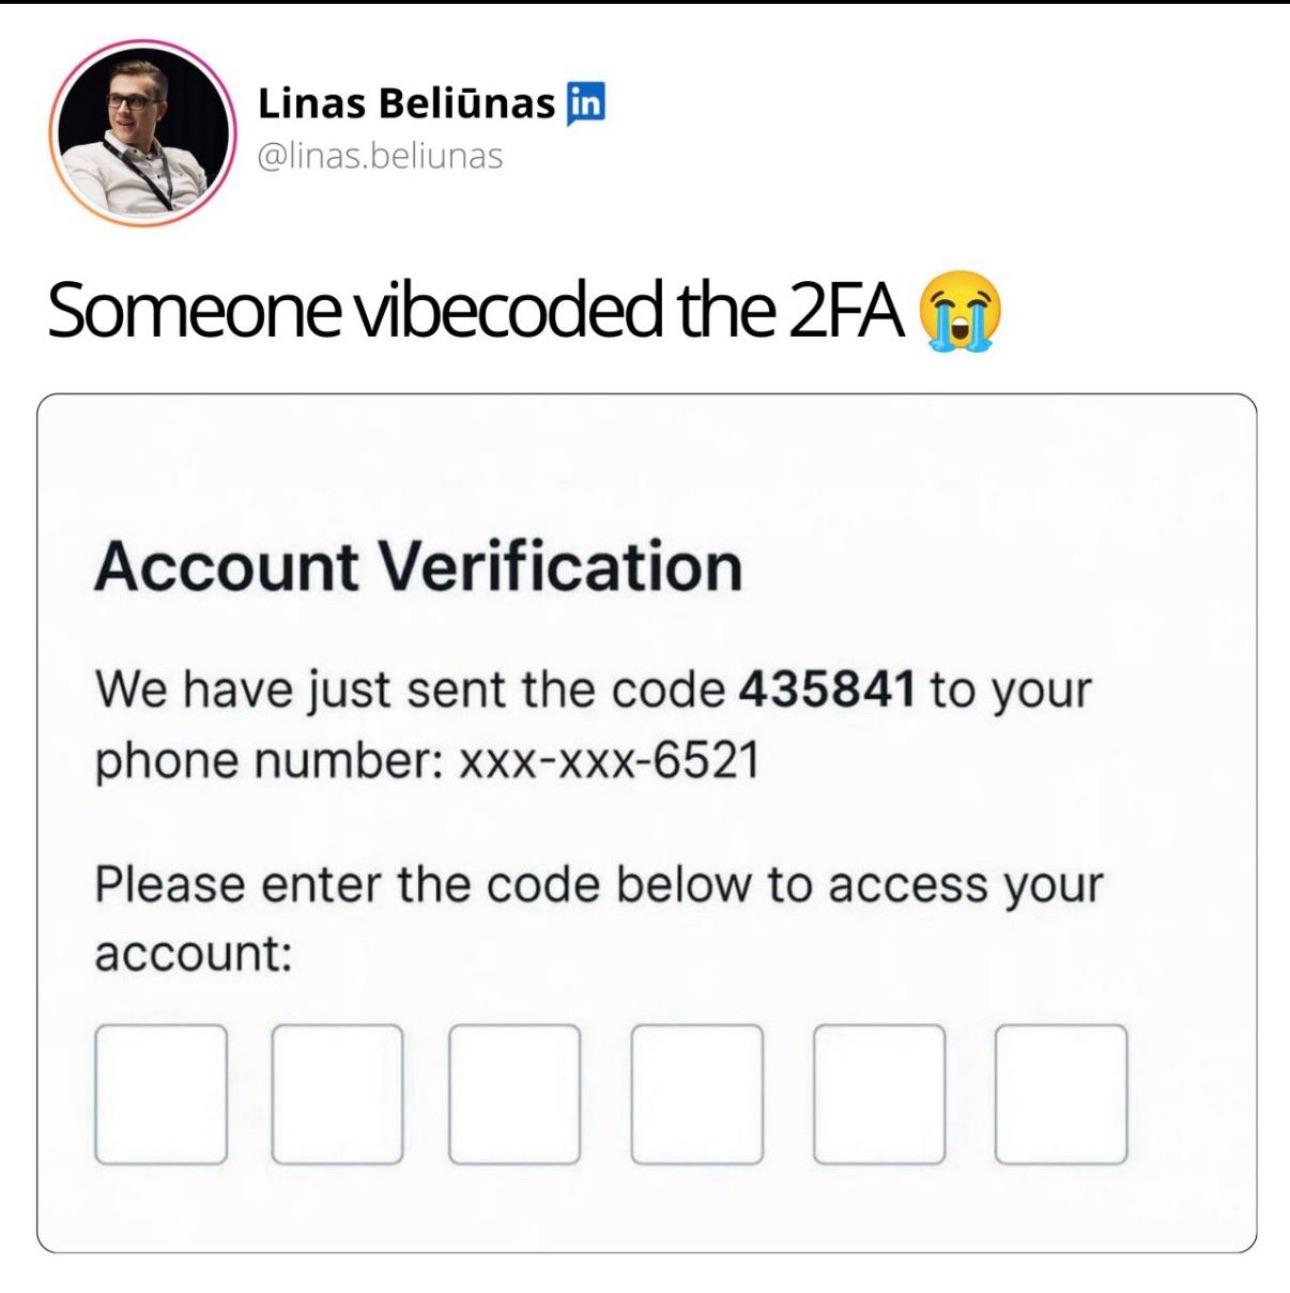
Oh, what's that? You need to VERIFY your identity? Well, too bad, because the website just casually dropped your entire verification code AND the last four digits of your phone number right there on the screen! Why even bother with the input boxes at this point? Just copy-paste and waltz right in! Security theater at its absolute finest. The UI designer really said "let's ask them to enter the code we LITERALLY just showed them" and everyone in the meeting nodded enthusiastically. It's like locking your front door but leaving the key taped to it with a sticky note that says "Please don't look!" Two-factor authentication? More like zero-factor suggestion. The code is RIGHT THERE. Anyone with eyeballs and a screenshot tool now has everything they need. Truly insane levels of vibe coding indeed. 😭

Make Auth Great Again

Make Auth Great Again
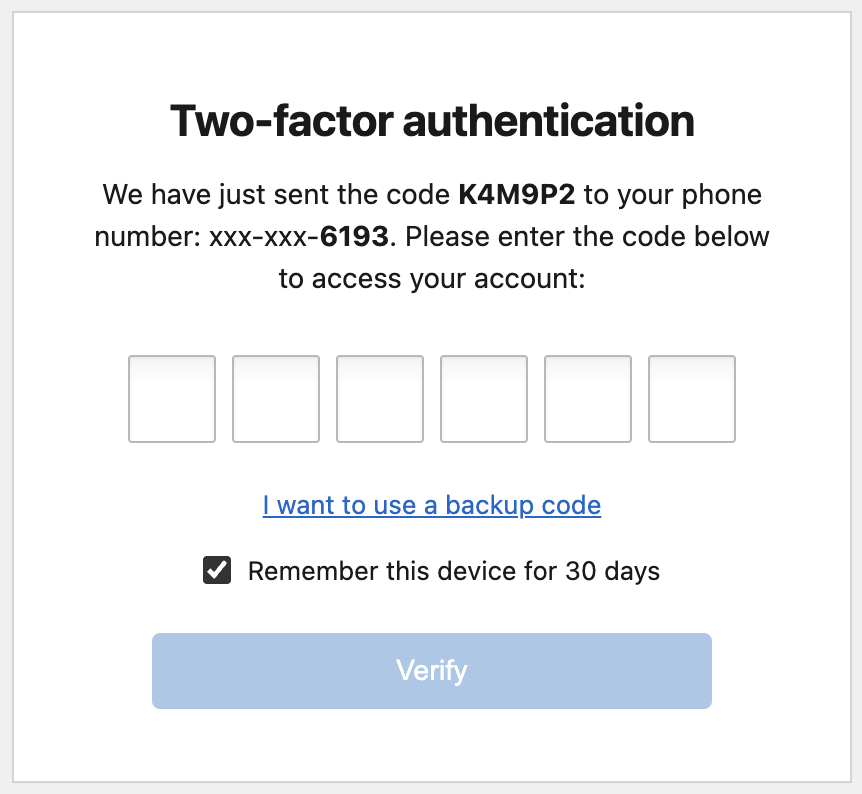
Nothing says "secure authentication" quite like displaying the actual 2FA code right there in the UI. Why bother sending it to your phone when they can just... tell you what it is on the same screen? It's like having a bouncer who whispers the password to everyone at the door. The code is literally K4M9P2 and they want you to type it into six separate boxes. Six boxes for six characters. Because apparently copying and pasting was too convenient, and we need to make users feel like they're defusing a bomb. Also love the "Remember this device for 30 days" checkbox that's already checked by default. Really committing to that whole "two-factor" thing when you only need to do it once a month.

Cascading Binary Code Developer Workspace 13x19 Poster Print

Cascading Binary Code Developer Workspace 13x19 Poster Print
Vibrant Neon Wireframe Design: High contrast inks printed on acid free paper create a striking visual display · Easy to Frame and Display: Colors stay crisp under bright light, maintaining clarity fo…

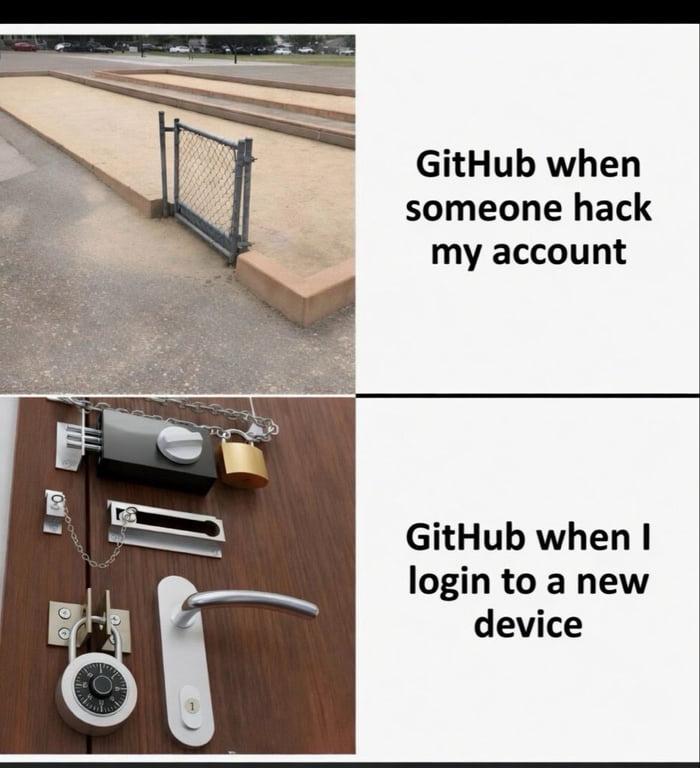
Github When I Login To A New Device

Github When I Login To A New Device
GitHub's security priorities are... interesting. Someone trying to hijack your account? Here's a tiny gate that a toddler could step over. But YOU, the actual account owner, trying to log in from your new laptop? Time to deploy Fort Knox with every lock known to humanity. You'll need your password, your 2FA code, a verification email, possibly a carrier pigeon with a signed affidavit, and GitHub will still send you a suspicious activity alert. Meanwhile, actual attackers are probably just vibing with that decorative fence that wouldn't stop a determined squirrel. The best part? After jumping through all those security hoops, GitHub will ask you to verify this device again in 30 days. Because apparently, your laptop might grow legs and become someone else's property.

Captcha Or 2FA

Captcha Or 2FA
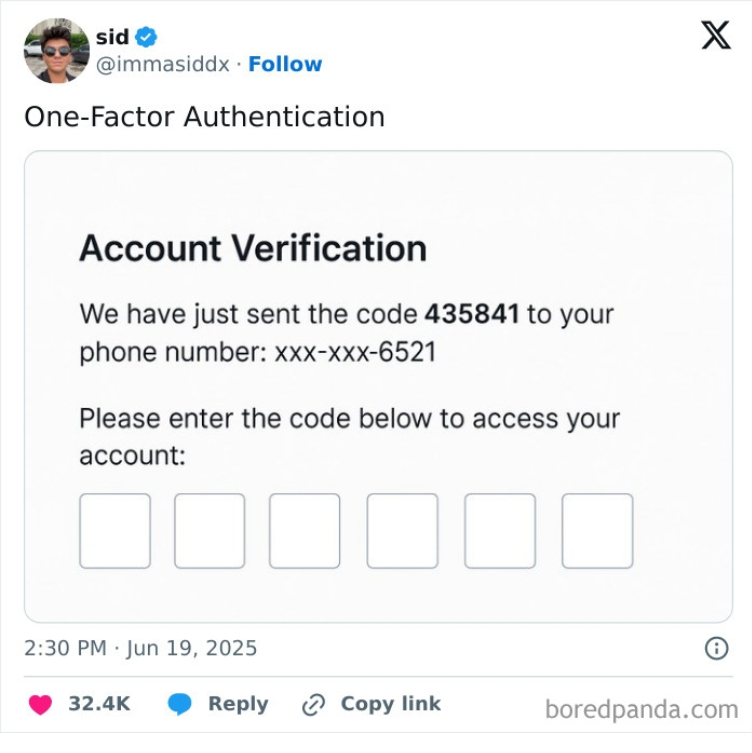
When your 2FA implementation is so bad it literally defeats its own purpose. They just sent you the code in the same message where they're asking you to enter it. It's like locking your front door but leaving the key taped to the doorknob. At this point, just skip the whole song and dance and log me in automatically. Why make me type six digits when you've already shown them to me? It's security theater at its finest—all the inconvenience of 2FA with absolutely none of the security benefits. Some developer out there really thought "you know what would make this secure? Making them copy-paste!" Peak innovation right there.

Illusion Of Security

Illusion Of Security
So they literally put the verification code right there in the message. You know, the one you're supposed to enter to prove you received it. The whole point of 2FA is that an attacker who doesn't have access to your phone can't log in... but if they intercept this message, they can just read the code without needing to actually receive it on the device. It's like putting a lock on your door and then leaving the key taped to the lock with a note saying "this is the key." Security theater at its finest. Someone's product manager probably said "let's make it more user-friendly" and the security team just quietly wept into their coffee.

God Is A Bad Programmer

God Is A Bad Programmer
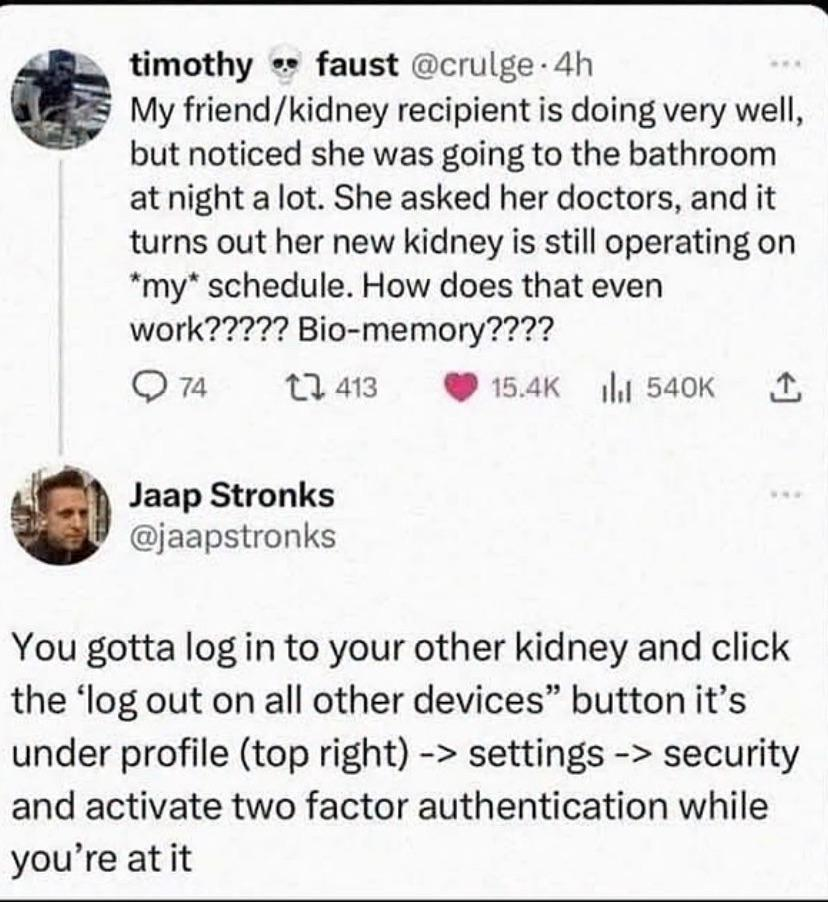
Someone accidentally discovered the human body has zero session management. The transplanted kidney is literally running on the donor's circadian rhythm like it's still logged into their account. No token refresh, no re-authentication, nothing. Just vibing on the old user's cron jobs. The reply treats it like a multi-device login problem you'd see on Netflix or Spotify. "Have you tried logging out of all devices?" Energy. Apparently human organs need 2FA and proper session invalidation on transfer. The kidney didn't get the memo about the account migration and is still checking the old timezone settings. Turns out biological systems are running legacy code with shared state across distributed systems. No wonder transplant rejection is a thing—it's basically a merge conflict at the cellular level. God definitely shipped to production without proper testing.

You Get A 2 FA, And You Get A 2 FA, Everyone Gets A 2 FA!

You Get A 2 FA, And You Get A 2 FA, Everyone Gets A 2 FA!
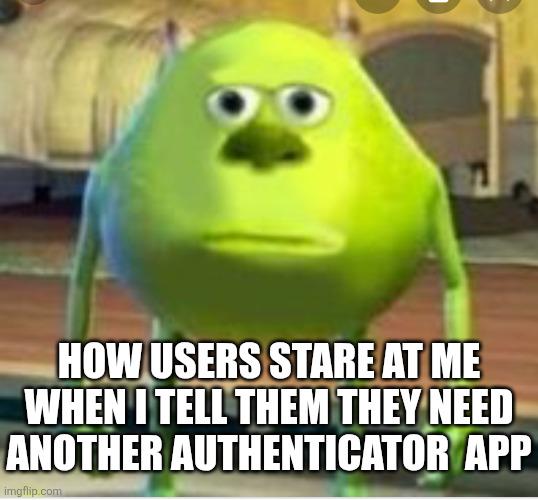
Remember when you just needed one password? Then it was password + email verification. Now you need Google Authenticator, Microsoft Authenticator, Authy, your bank's proprietary app, your work's custom solution, and probably a blood sacrifice to access your Netflix account. Users already have 47 different authenticator apps cluttering their phone, and here you come suggesting they download number 48. The look of pure betrayal is real. Security teams keep treating 2FA apps like Oprah giving away cars, except nobody's excited about this gift.

Password 123!

Password 123!
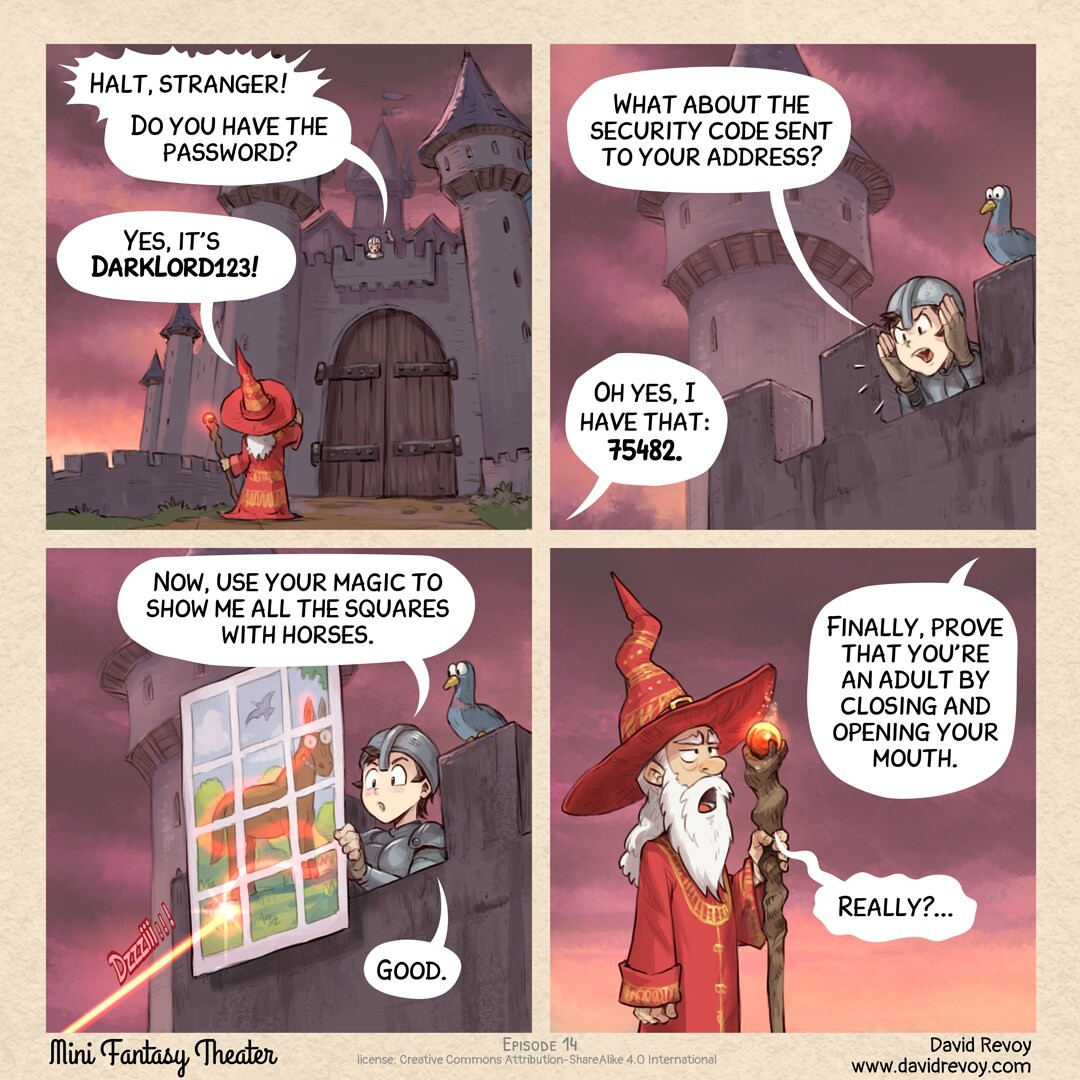
Multi-factor authentication is getting out of hand. First it's "something you know" (password), then "something you have" (security code), then "something you are" (biometrics). Next thing you know they'll be asking for your childhood pet's maiden name and a blood sample. The wizard here is basically implementing the world's most annoying auth flow. Sure, DARKLORD123 is a terrible password (though let's be honest, we've all seen worse in production databases), but then comes the 2FA code, a CAPTCHA that would make Google weep, and finally... a liveness check? At this point just ask for my social security number and firstborn child. The knight's defeated "Really?..." hits different when you've spent 20 minutes trying to log into AWS because you left your MFA device at home. Security is important, but somewhere between "password123" and "perform a ritual sacrifice" there's a middle ground we're all still searching for.

Manager Does A Little Code

Manager Does A Little Code
When your manager decides to "optimize" the codebase by shutting down "unnecessary" microservices, and suddenly 2FA stops working because—surprise!—everything in a microservices architecture is actually connected to everything else. Elon casually announces he's turning off "bloatware" microservices at Twitter (less than 20% are "actually needed"), and within hours people are locked out because the 2FA service got yeeted into the void. Classic move: treating a distributed system like it's a messy closet you can just Marie Kondo your way through. "Does this microservice spark joy? No? DELETE." Pro tip: Before you start playing Thanos with your infrastructure, maybe check what those services actually do. That "bloatware" might be the thing keeping your users from rage-tweeting about being locked out... oh wait. 💀

KAIWEETS HT118E Digital Multimeter TRMS 20000 Counts with Higher Resolution Auto-Ranging Voltmeter Accurately Measures Voltage Current Resistance Diodes Continuity Duty-Cycle Capacitance Temperature

KAIWEETS HT118E Digital Multimeter TRMS 20000 Counts with Higher Resolution Auto-Ranging Voltmeter Accurately Measures Voltage Current Resistance Diodes Continuity Duty-Cycle Capacitance Temperature
HIGHER RESOLUTION & ADVANCED DESIGN: 20000 counts, HT118E multimeter with more resolution bits allows for more accurate measurement results. The flashlight on the back ensures easy use in dimly lit p…

Two Factor Authentication

Two Factor Authentication
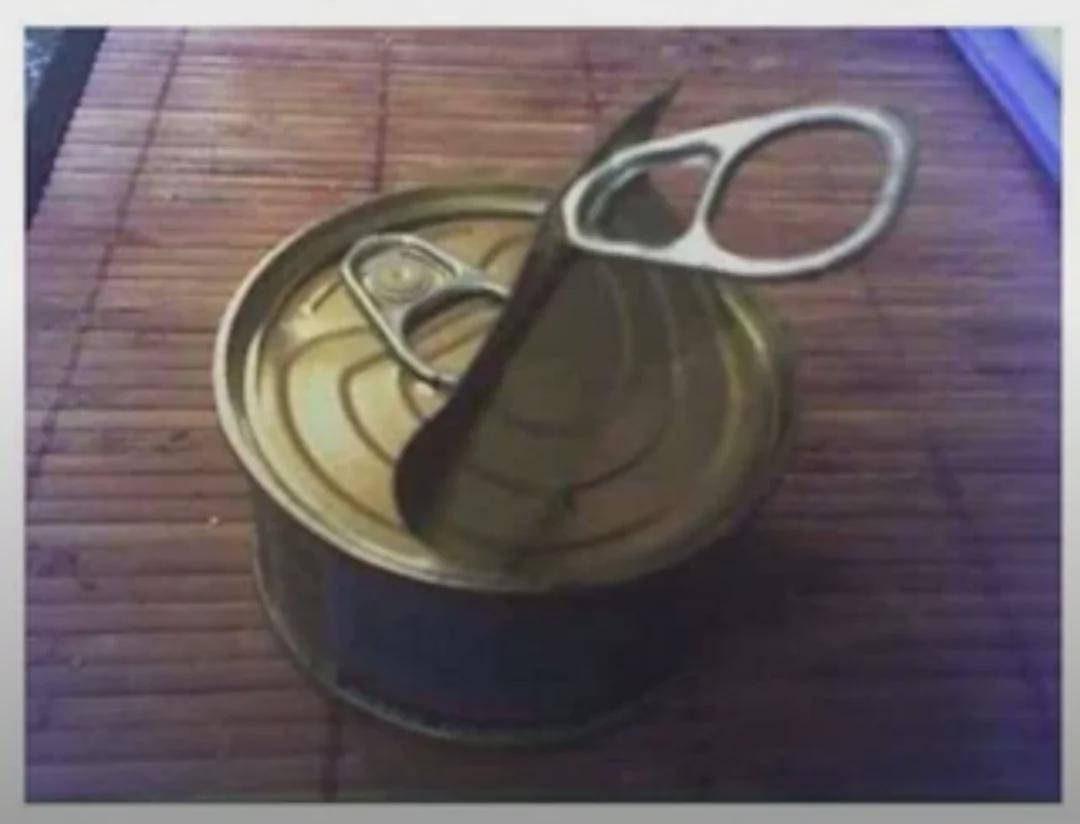
The most secure authentication method known to developers - a can with scissors jammed in it. Need to access your account? You'll need both the can AND the scissors! Security experts hate this one weird trick that somehow meets compliance requirements while being utterly useless. Just like how most corporate 2FA implementations feel when you're forced to type in a code that was texted to the same device you're already holding. Pure security theater at its finest!