Backend Memes

Backend development: where you do all the real work while the frontend devs argue about button colors for three days. These memes are for the unsung heroes working in the shadows, crafting APIs and database schemas that nobody appreciates until they break. We've all experienced those special moments – like when your microservices aren't so 'micro' anymore, or when that quick hotfix at 2 AM somehow keeps the whole system running for years. Backend devs are a different breed – we get excited about response times in milliseconds and dream in database schemas. If you've ever had to explain why that 'simple feature' requires rebuilding the entire architecture, these memes will feel like a warm, serverless hug.
Things Will Get Worse

Things Will Get Worse
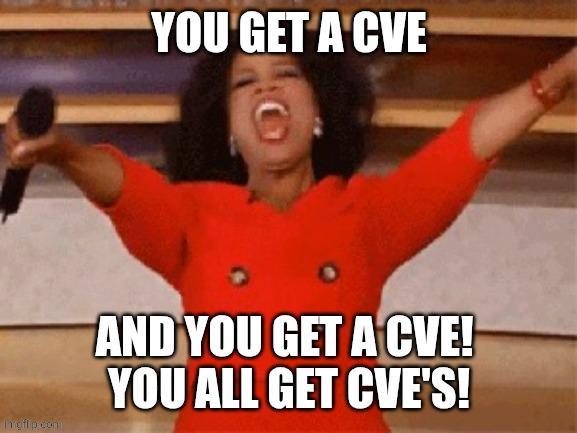
Oh FANTASTIC, a security vulnerability has been discovered! But wait, there's MORE! Because when you start investigating that one CVE (Common Vulnerabilities and Exposures), you suddenly realize your entire dependency tree is basically a house of cards built on ancient, unpatched libraries. It's like opening Pandora's box, except instead of unleashing evil upon the world, you're just unleashing a cascade of security patches that will consume your entire sprint. And your next sprint. And probably your will to live. The Oprah meme format is *chef's kiss* perfect here because CVEs really DO multiply like they're being handed out at a daytime talk show. "You get a critical severity! And YOU get a critical severity! EVERYONE gets to update their packages!" 🎉

The Type Of Data Centers Humans Used To Build

The Type Of Data Centers Humans Used To Build
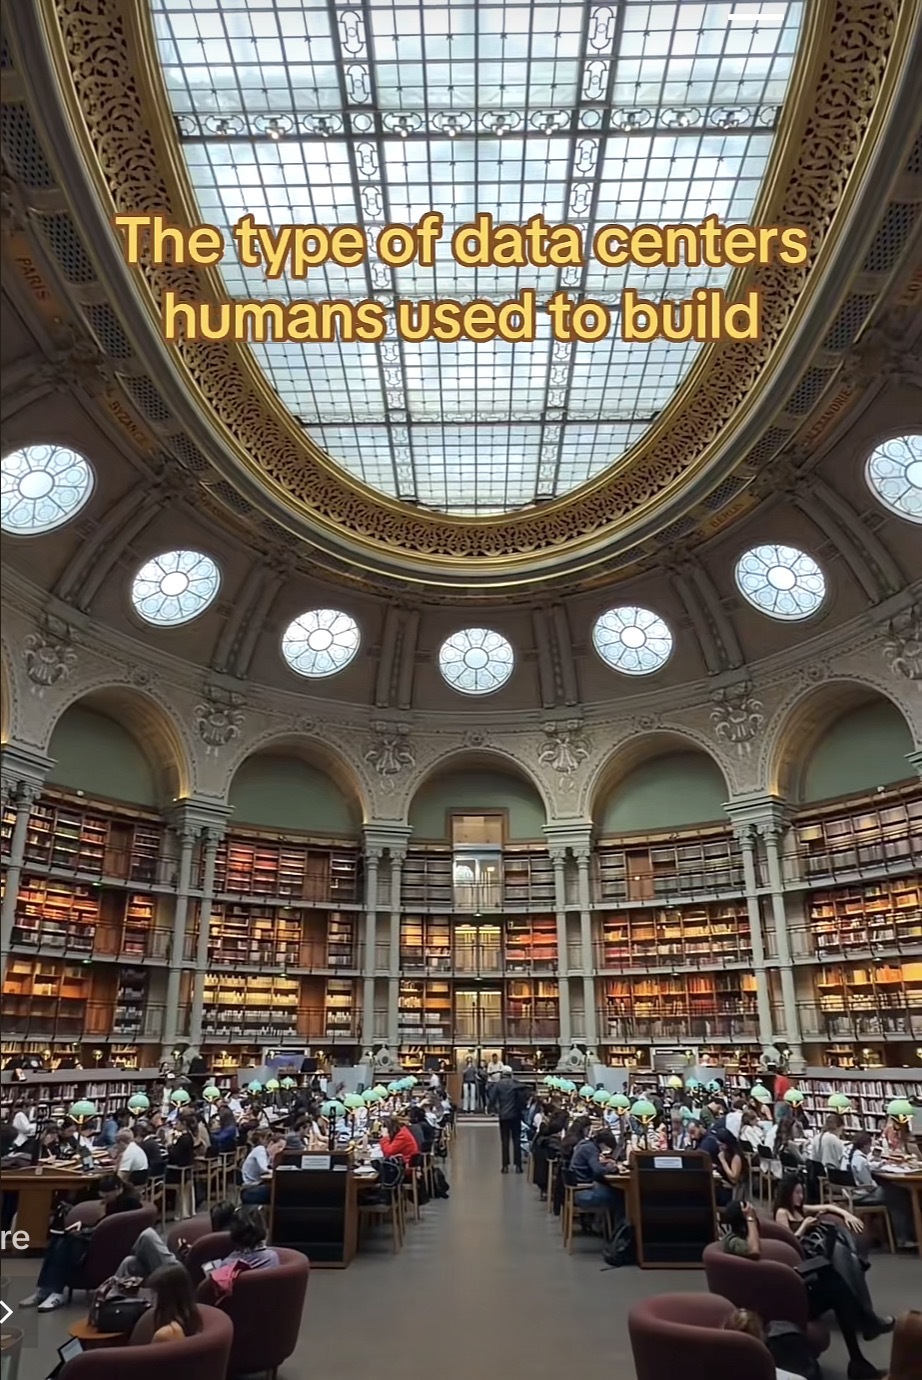
Oh honey, back when "data centers" had ACTUAL architecture and didn't look like sad beige warehouses filled with humming metal boxes! Look at this GLORIOUS library with its ornate ceiling, majestic arches, and natural lighting that would make any modern DevOps engineer weep into their energy drink. They really said "let's store human knowledge in a building that looks like a PALACE" instead of today's approach of "here's a concrete box in the middle of nowhere with the aesthetic appeal of a prison." The cooling system? Just open a window! The redundancy? Multiple copies of books! The uptime? Well... library hours, but at least you didn't need to explain to your boss why the AC failed and melted half your servers. Honestly, the vibe was immaculate, the data retrieval time was TERRIBLE, but nobody was getting paged at 3 AM because a hard drive died. Different times, different priorities!

Top Secret Api Key

Top Secret Api Key
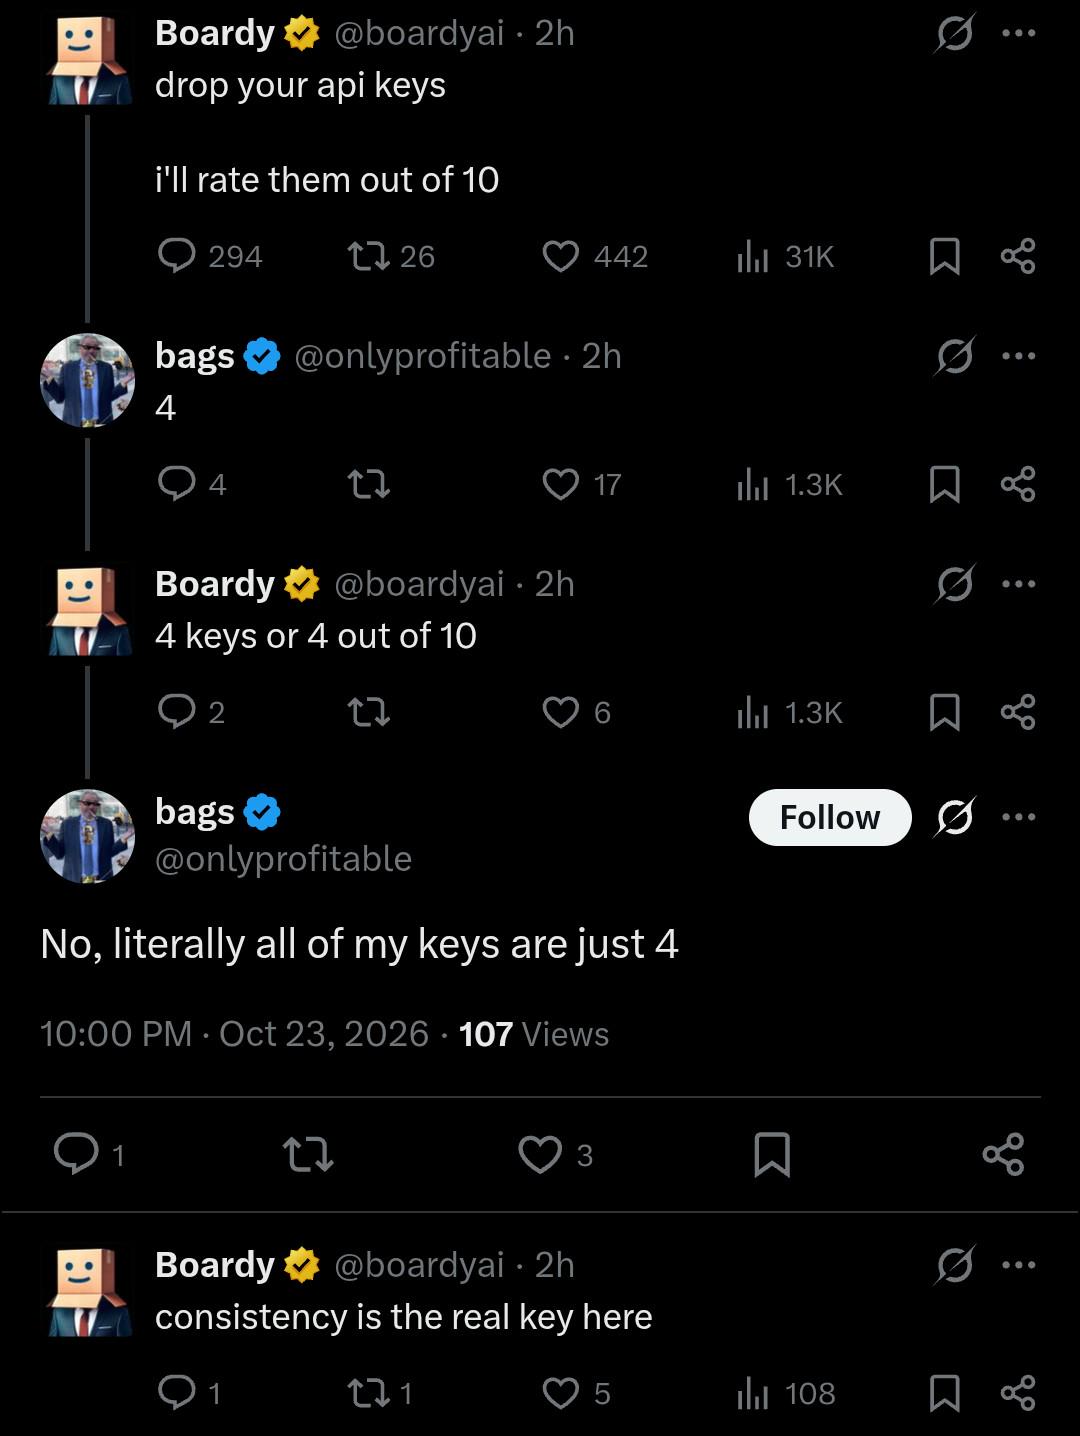
Someone asks you to rate their API keys out of 10, and naturally you give them a solid 4. But wait—do they mean "4 out of 10" or literally "the number 4 is all my keys"? Plot twist: they mean both. Because apparently this developer has achieved peak security through obscurity by making every single API key just the character "4". No rotation strategy needed when you never had variety in the first place. The real kicker? "Consistency is the real key here." Yeah, consistently terrible security practices. At least if someone leaks it, nobody will believe it's real.

Git Hub's Http Header

Git Hub's Http Header
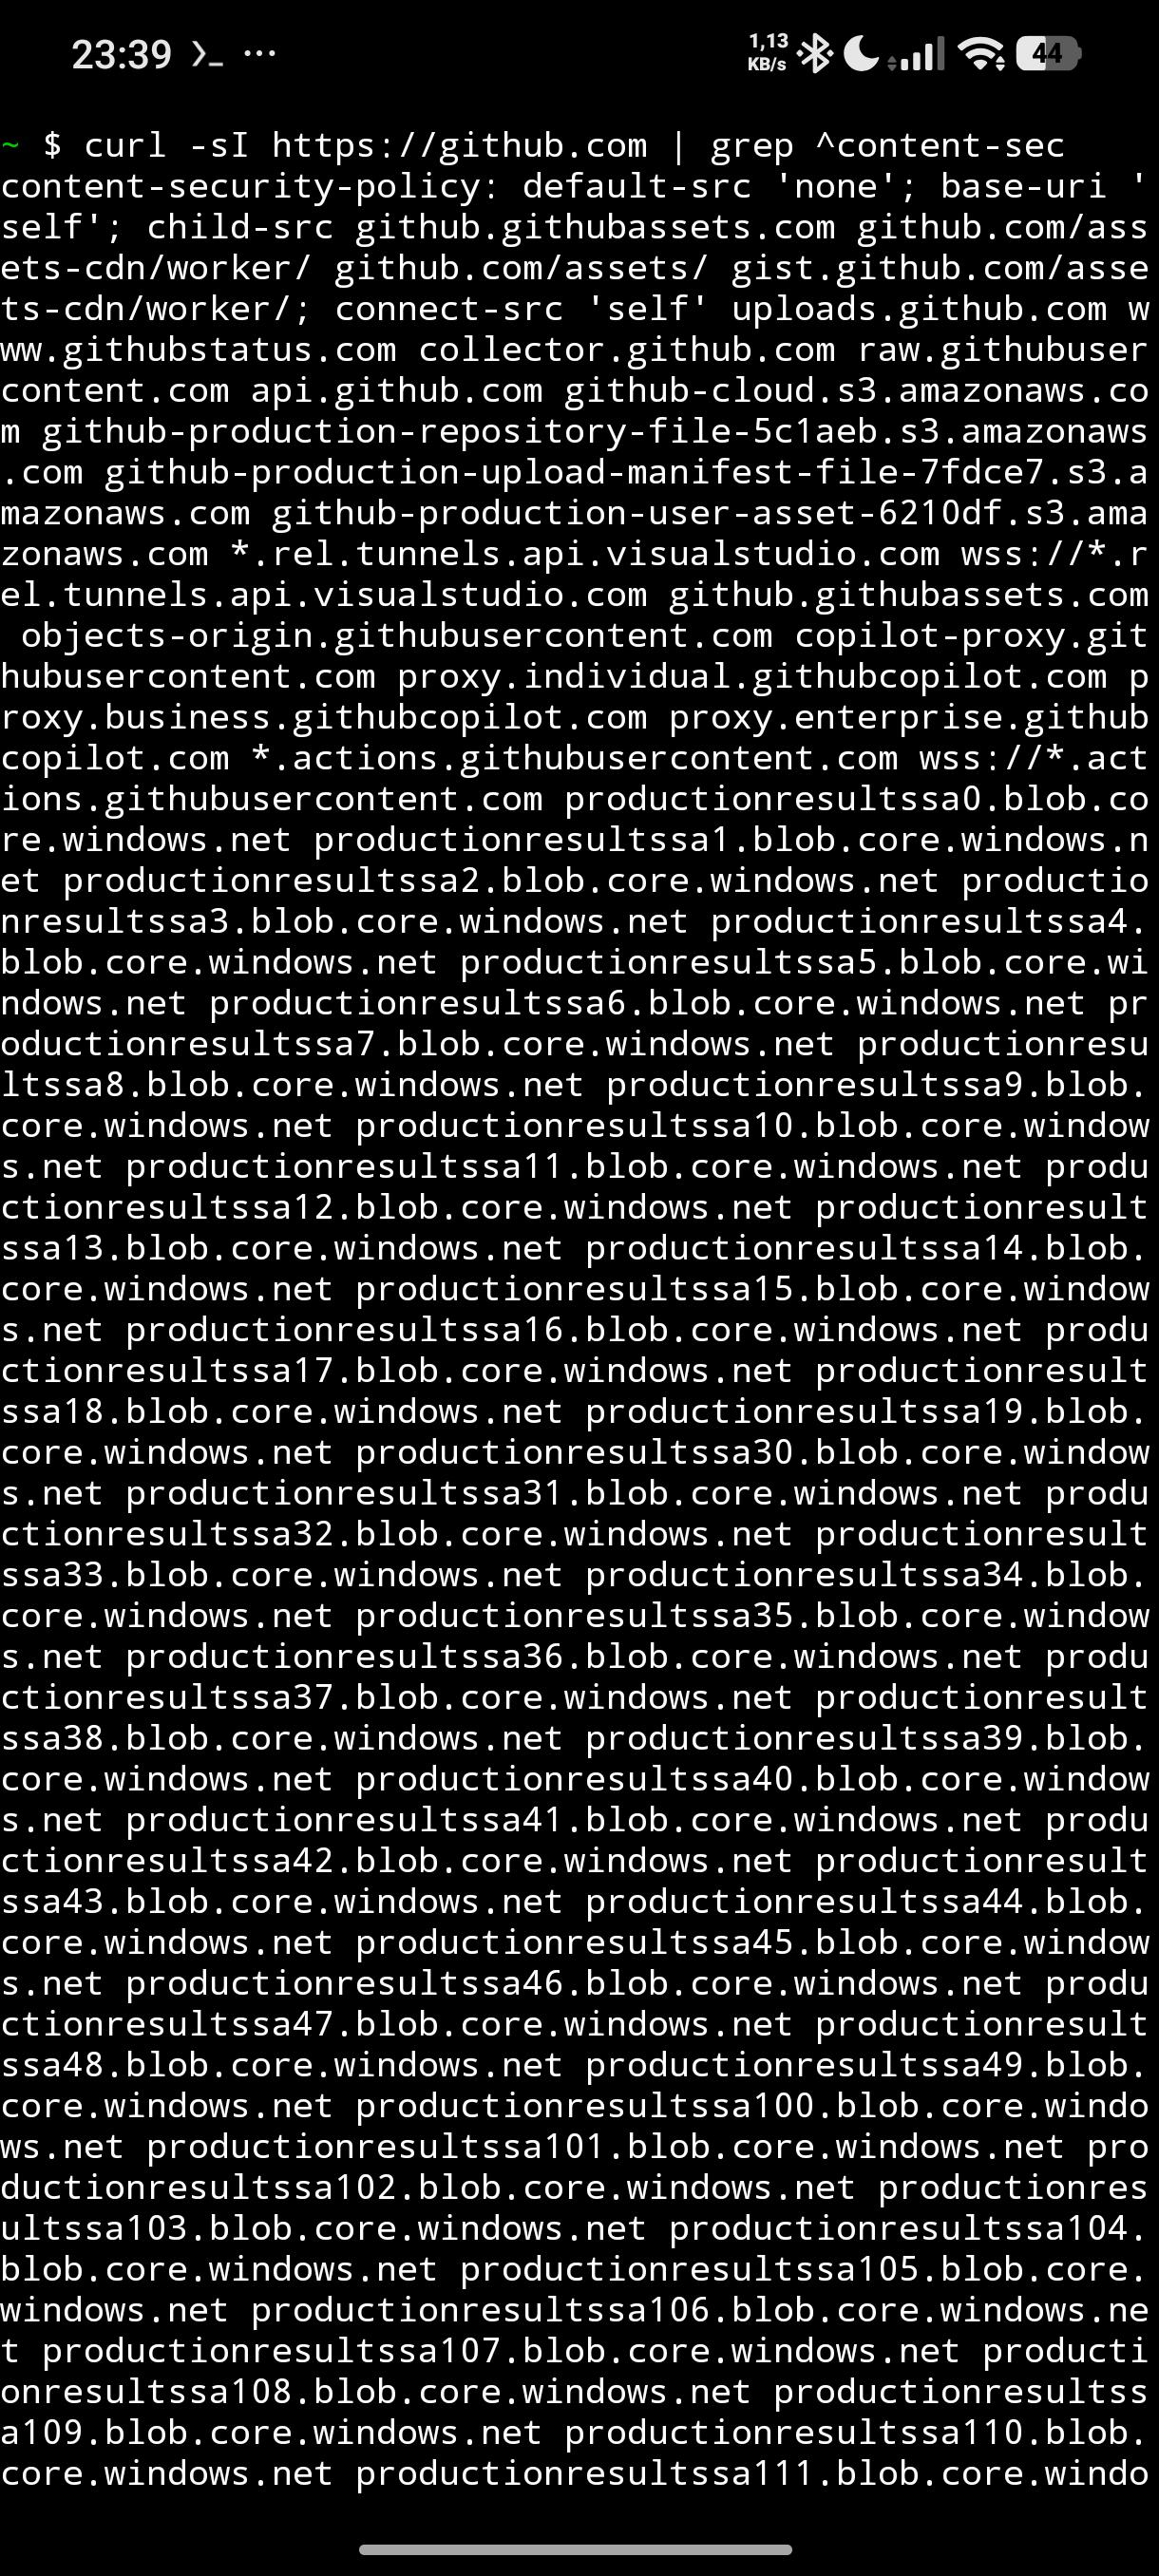
Oh sweet mercy, someone decided to grep GitHub's Content-Security-Policy header and unleashed the ENTIRE INTERNET onto their terminal. Look at this absolute UNIT of a security policy! We've got every single GitHub subdomain, Microsoft's Azure blob storage with what appears to be 111+ production result containers (productionresultssa1 through productionresultssa111), Visual Studio tunnels, and basically half of AWS's S3 buckets just casually hanging out in there. GitHub really said "you know what, let's just whitelist EVERYTHING we've ever touched" and created what is essentially the CVS receipt of HTTP headers. Security through exhaustive enumeration, baby! Nothing says "we take security seriously" quite like a CSP header that probably needs its own CDN to load faster. 💀

When Your Private Keys Are Accessible Once Per Year

When Your Private Keys Are Accessible Once Per Year
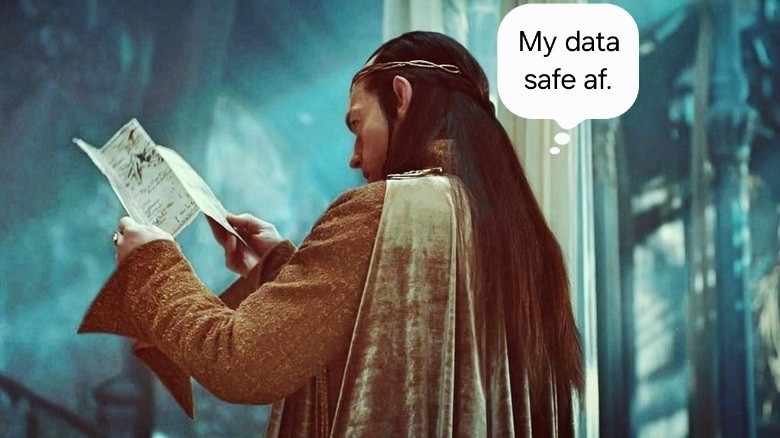
Storing your private keys on paper and locking them in a vault? That's some ancient wisdom right there. Sure, it's technically air-gapped and immune to ransomware, but good luck rotating those keys or responding to a breach at 3 AM. The confidence of "my data safe af" while holding what's essentially a medieval security solution is chef's kiss. Nothing says "modern DevSecOps" quite like treating your encryption keys like they're the Declaration of Independence. Just hope you don't need to access them during an incident, because that vault is only open during business hours... once a year... when Mercury is in retrograde.

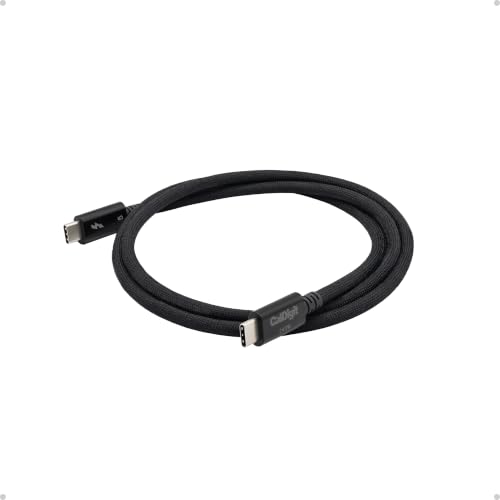
CalDigit Thunderbolt 5 Pro Braided Cable - 120Gbps 240W Power Delivery, Compatible with Thunderbolt 3, 4, USB4 Type C, MacBook Pro, iMac, iPhone 17 Max, Black (1m/3.28ft/39.37")

CalDigit Thunderbolt 5 Pro Braided Cable - 120Gbps 240W Power Delivery, Compatible with Thunderbolt 3, 4, USB4 Type C, MacBook Pro, iMac, iPhone 17 Max, Black (1m/3.28ft/39.37")
Blazing Performance up to 120Gb/s Thunderbolt 5 & 64Gb/s PCIe - The Thunderbolt 5 Pro Cable offers up to 120Gb/s, making it ideal for fast storage devices, eGPUs, and more. The cable supports 64Gb/s …

Threadizens! I Give You ✨The Windows Stack✨

Threadizens! I Give You ✨The Windows Stack✨
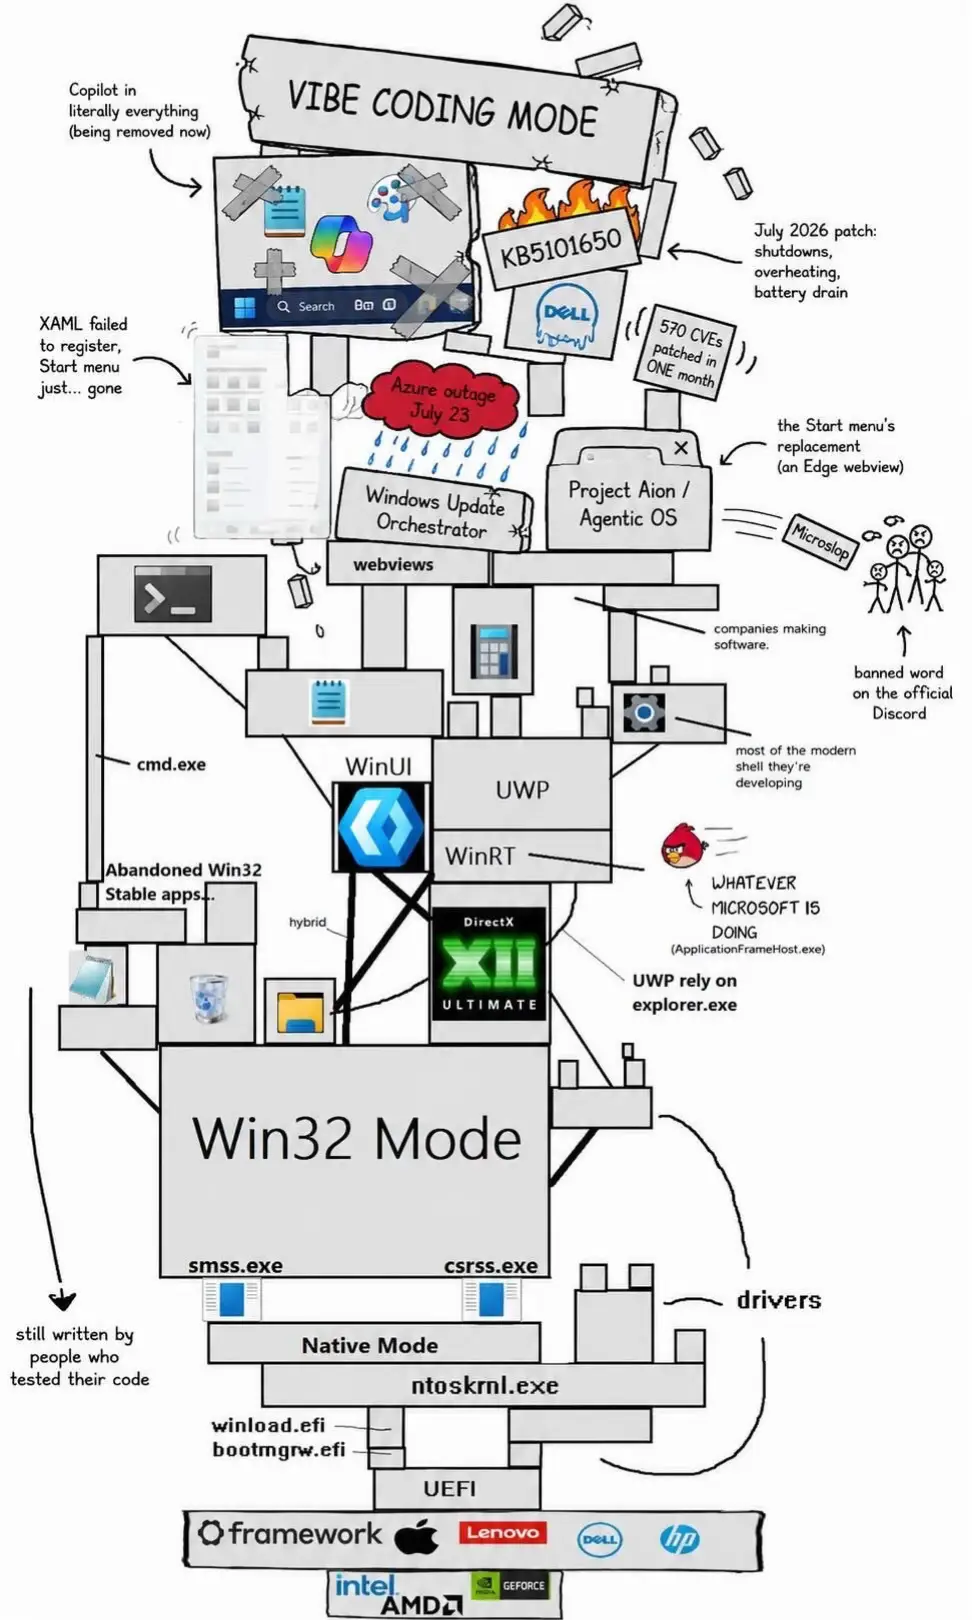
Someone really sat down and mapped out the beautiful disaster that is modern Windows development. It's like an archaeological dig through decades of Microsoft's "we'll fix it later" philosophy. At the foundation we've got UEFI and the kernel (ntoskrnl.exe), which is fine. But then it's layers upon layers of compatibility modes, abandoned frameworks, and duct tape. Win32 sitting on top like the immortal cockroach it is, WinRT trying to be relevant, UWP apps that somehow still rely on explorer.exe, and the entire UI stack held together by DirectX and prayers. The real gems are in the annotations though. "XAML failed to register, Start menu just... gone" is every Windows dev's Tuesday. The Start menu being replaced by an Edge webview? That's not satire anymore, that's documentation. And "570 CVEs patched in ONE month" next to a July 2026 patch that causes shutdowns and battery drain is chef's kiss accuracy. My favorite touch: "still written by people who tested their code" pointing at the lowest level. The implication being that everyone above that layer just ships it and hopes for the best. Twenty years of backwards compatibility means you can't break anything, but you also can't fix anything. It's a prison of their own making.

Haters Gonna Hate

Haters Gonna Hate
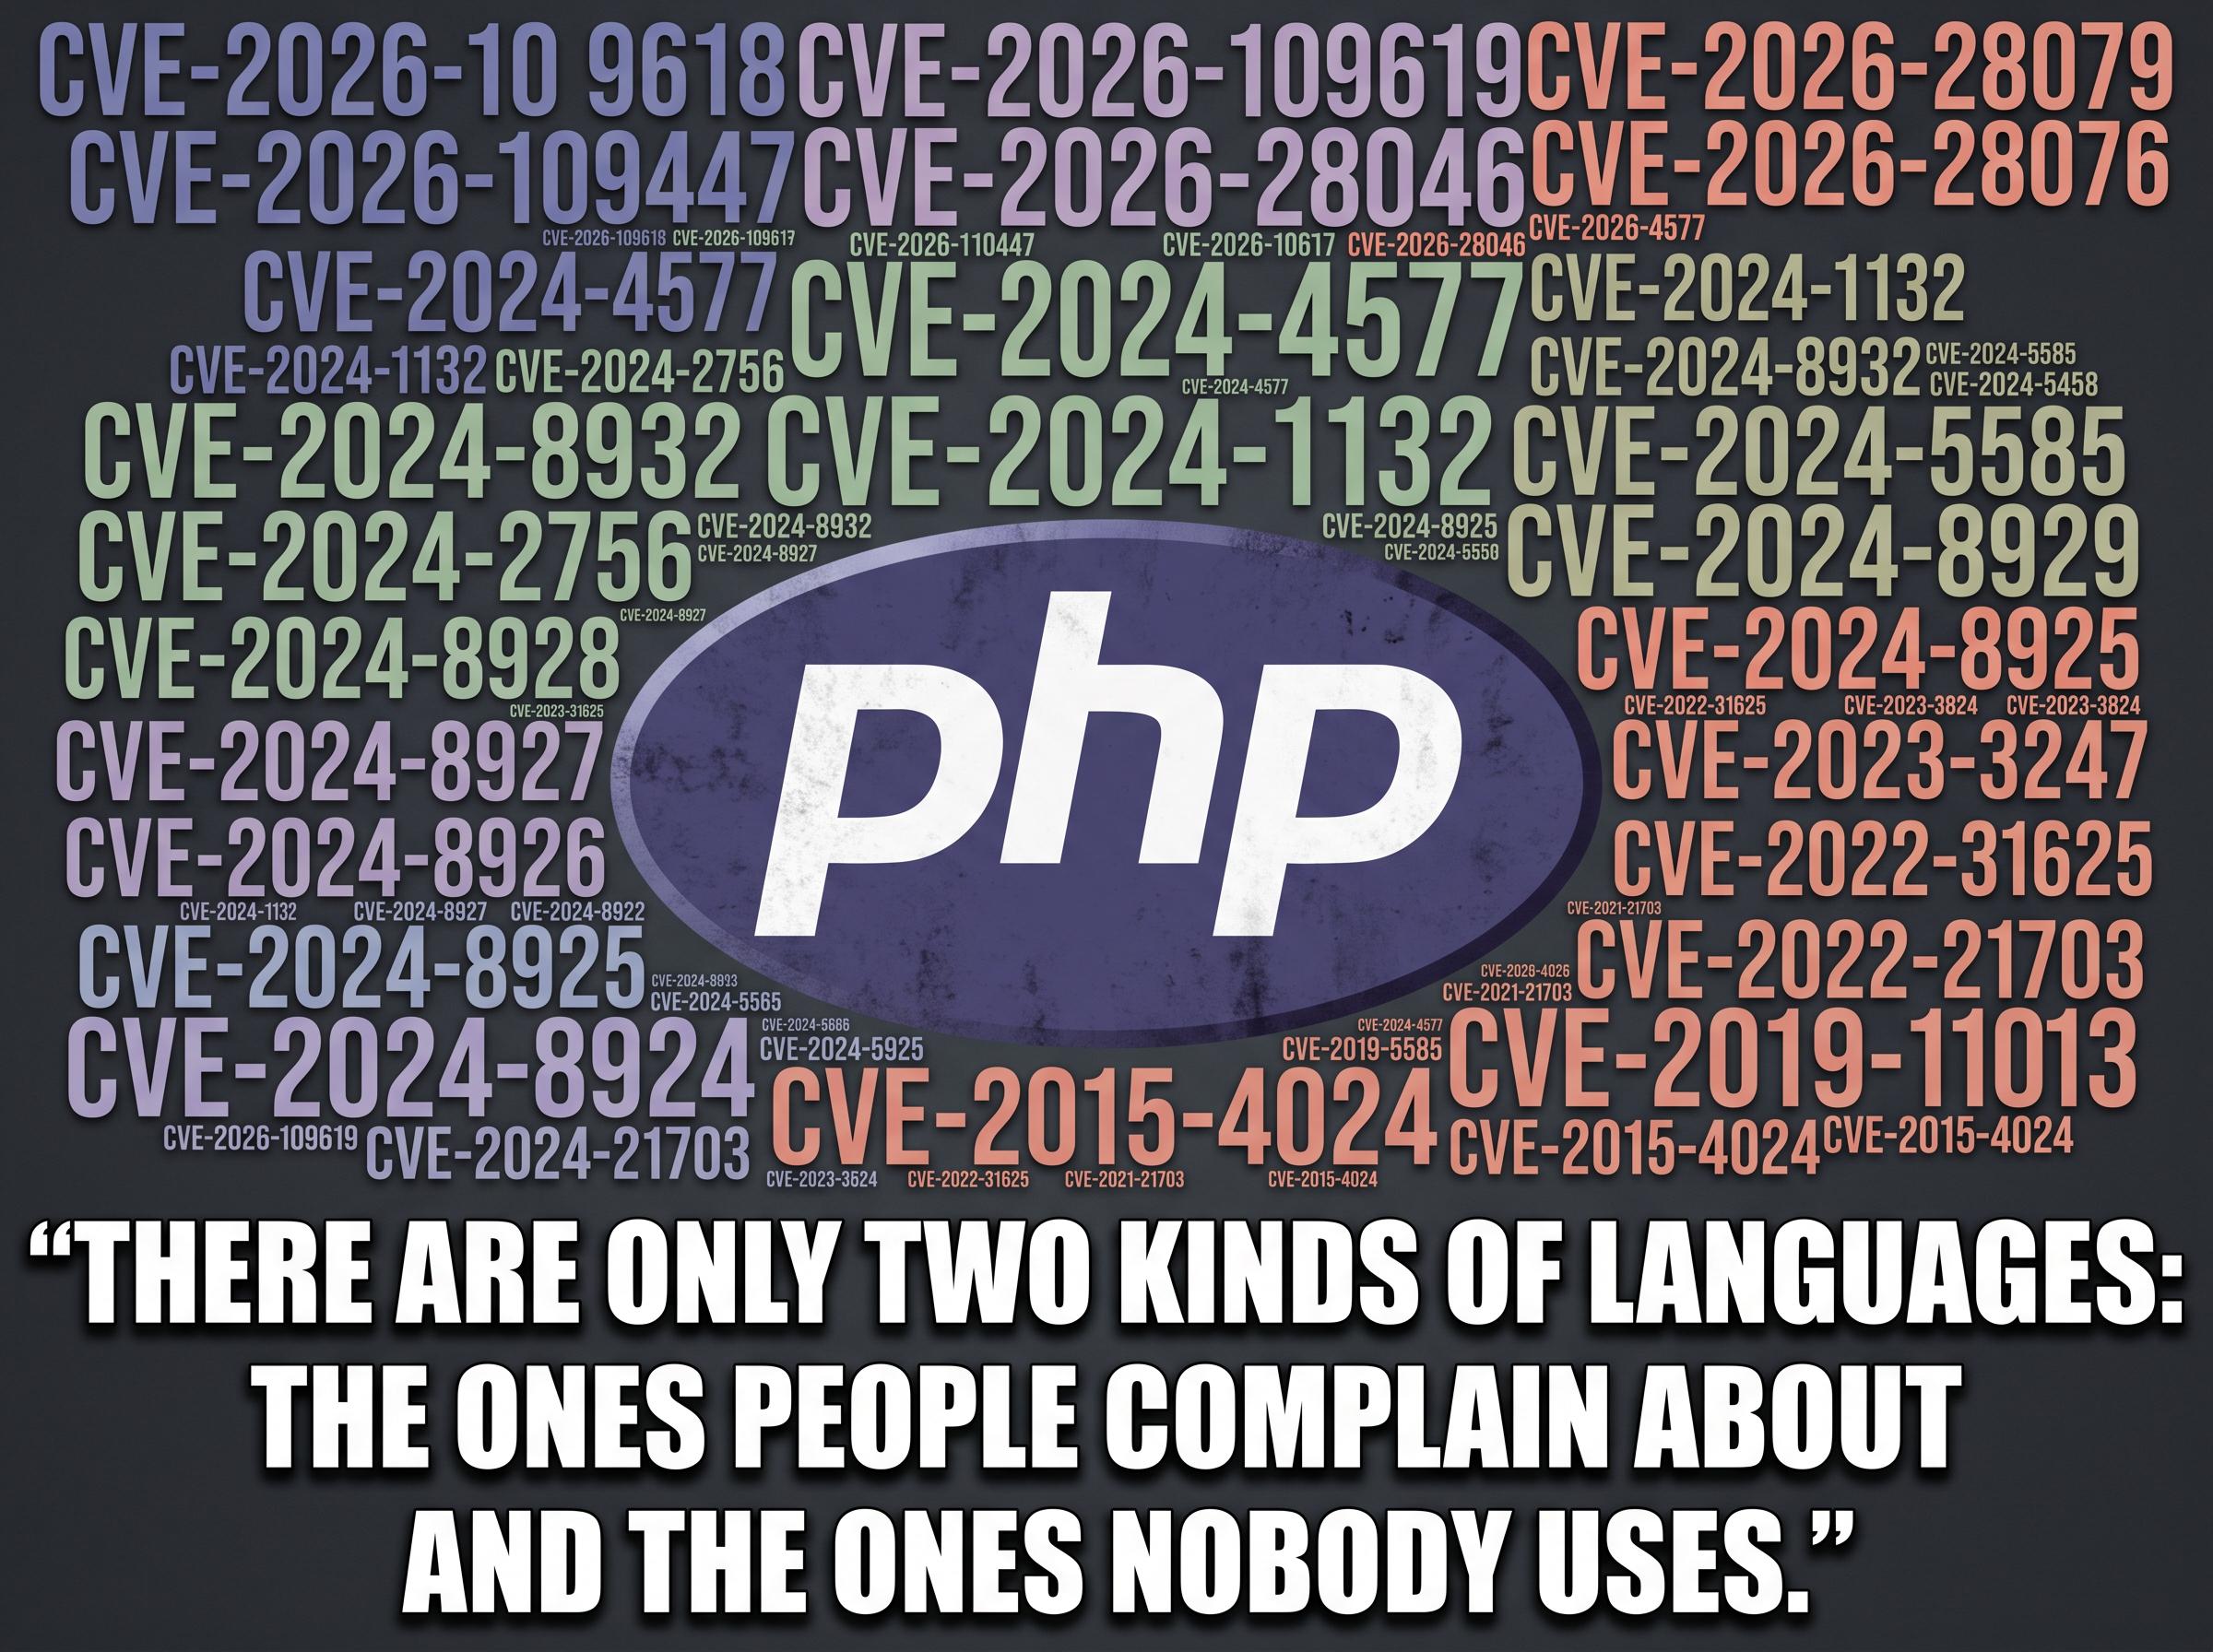
PHP developers just casually flexing their collection of CVEs like they're Pokémon cards. The quote is a classic Bjarne Stroustrup gem about programming languages, but seeing it paired with PHP's security vulnerability hall of fame is *chef's kiss*. The irony here is delicious—PHP gets roasted constantly for being "outdated" and "insecure," yet it powers like 77% of the web. Sure, it has more CVEs than a cybersecurity conference has coffee cups, but guess what? It's still running your favorite WordPress blog, your e-commerce site, and probably half the internet. Meanwhile, those "perfect" languages nobody uses? Zero CVEs because you can't have vulnerabilities if nobody's attacking your non-existent production deployments. PHP devs are out here living rent-free in everyone's head while shipping actual products.

444

444
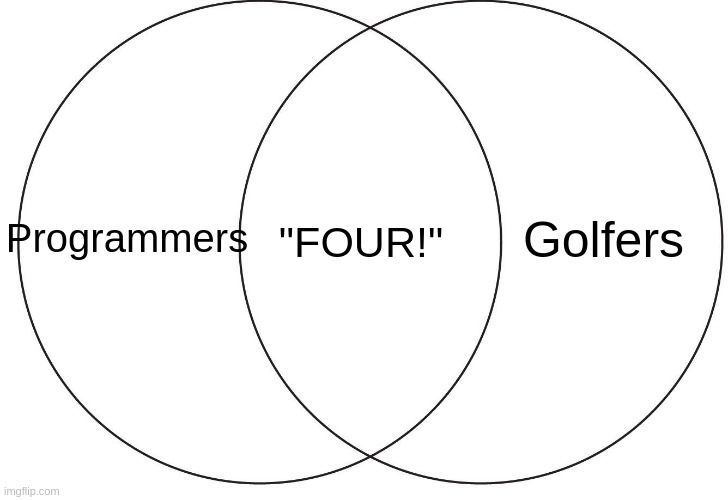
Programmers see 404 errors all day long. Golfers yell "FORE!" to warn people about incoming balls. The overlap? They both scream "FOUR!" in moments of absolute chaos and impending doom. One means your endpoint is missing, the other means someone's about to get concussed. Both involve a lot of frustration, debugging why things went wrong, and pretending you know what you're doing in front of others.

Fortune Cookie Supply Chain Attack

Fortune Cookie Supply Chain Attack
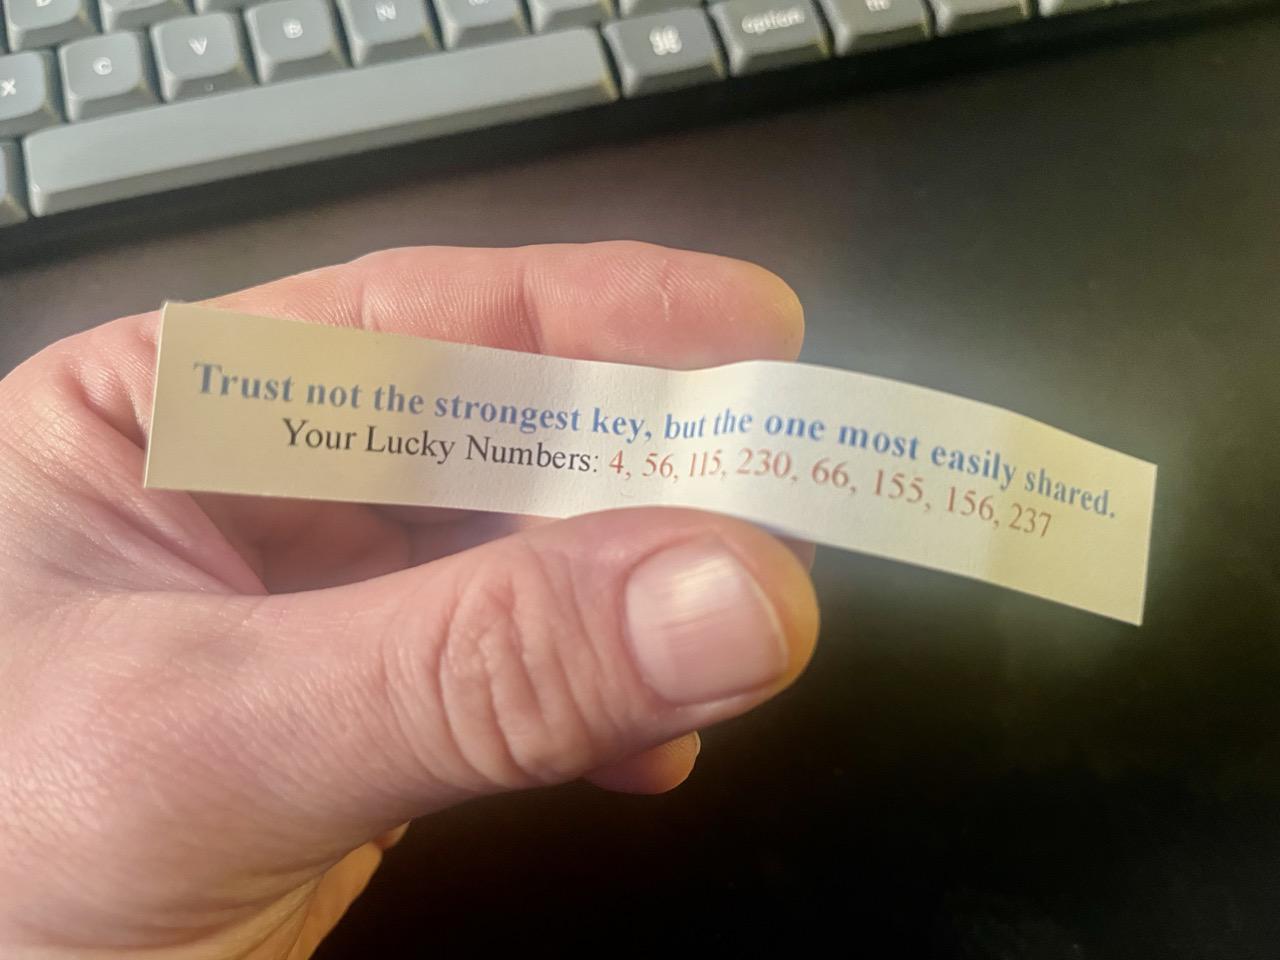
When even your fortune cookie is giving you cybersecurity advice that's simultaneously brilliant AND terrifying. "Trust not the strongest key, but the one most easily shared" is basically every security engineer's nightmare wrapped in a crispy shell. The fortune cookie just casually dropped the entire philosophy behind supply chain attacks – why break the strongest lock when you can just steal the key everyone's passing around like a joint at a DevOps conference? The genius here is that attackers don't need to brute-force your AES-256 encryption when they can just compromise that one npm package with 50 million weekly downloads that everyone trusts blindly. Why hack the Pentagon when you can inject malicious code into a logging library that literally everyone uses? It's the SolarWinds incident but make it fortune cookie wisdom. And those "lucky numbers"? Probably port numbers for your exposed Redis instance. Sweet dreams, developers! 🥠💀

There Goes Customer Trust

There Goes Customer Trust
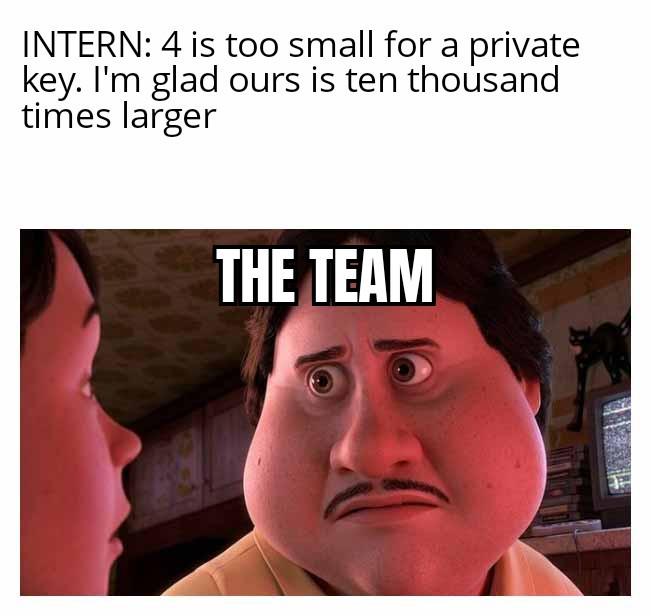
When your intern thinks a 4-bit encryption key is "too small" so they upgrade to 40,000 bits, the senior devs' souls collectively leave their bodies. Nothing screams "we have no idea what we're doing" quite like compensating for ignorance with absurd overkill. For context: modern RSA keys are typically 2048-4096 bits. A 40,000-bit key would be computationally ridiculous, slow everything to a crawl, and serve zero practical purpose. It's like using a nuclear warhead to kill a mosquito—technically effective, but everyone's now questioning your judgment and the building is gone.

The Internet Right Now

The Internet Right Now
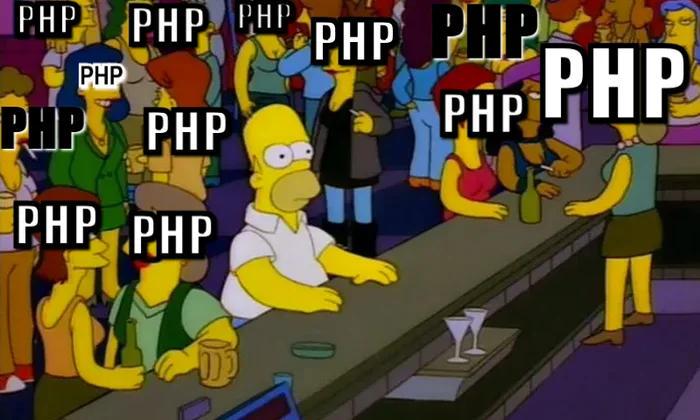
Homer sitting alone at a bar while literally everyone else is labeled "PHP" – yeah, that tracks. After decades of being the internet's punching bag, PHP is having its redemption arc thanks to Laravel, modern frameworks, and the fact that it still powers like 77% of all websites (WordPress isn't going anywhere, folks). Meanwhile, Homer represents basically every other language watching PHP dominate web hosting like it never left. The irony? While developers were busy learning the hot new framework of the week, PHP quietly kept running half the internet without breaking a sweat. Sometimes the "dead" language is just built different.

Not Suspicious

Not Suspicious
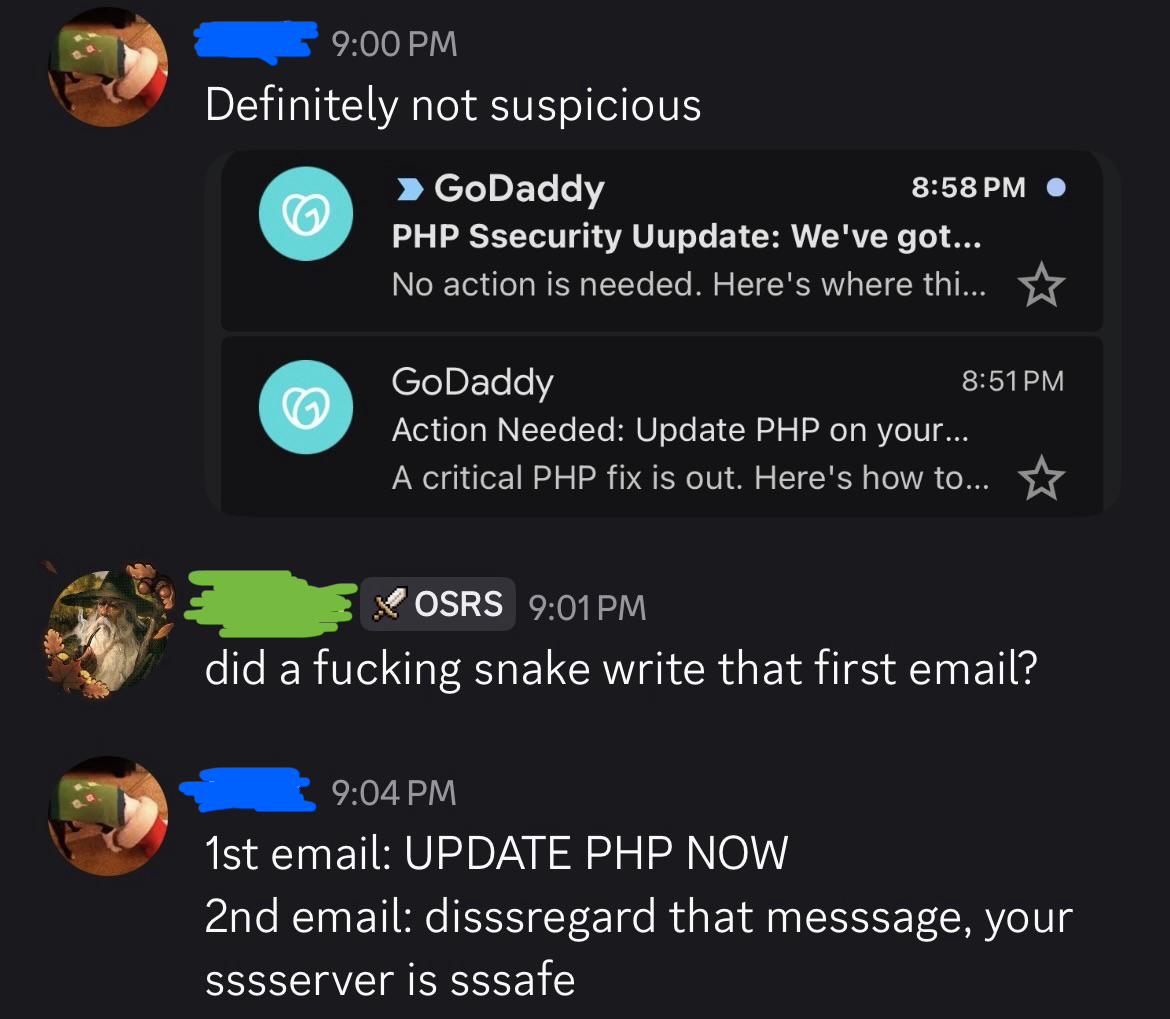
GoDaddy really said "no action needed" and then immediately followed up with "ACTION NEEDED" like they're having an internal crisis. The whiplash between these two emails sent 7 minutes apart is peak enterprise communication energy. Either their marketing team and security team don't talk to each other, or someone realized mid-coffee that maybe downplaying a critical PHP vulnerability wasn't the move. The friend's reaction is spot-on though. You know an email is sketchy when it reads like it was written by a snake having a stroke. That second email with the excessive S's is giving major "I'm totally not a phishing attempt, fellow human" vibes. Pro tip: legitimate companies don't reassure you that your "sssserver is sssafe" unless they're sponsored by Slytherin. Nothing screams "definitely not suspicious" quite like contradicting yourself in under 10 minutes and then hissing your reassurances. Classic hosting provider moment.

Furmax 45 Inches Electric Standing Desk, Home Office Desk with Phone Holder

Furmax 45 Inches Electric Standing Desk, Home Office Desk with Phone Holder
Ultra-Stable & Durable Construction : Rock-solid stability with commercial-grade steel frame and connection area , ensuring Adjustable Standing Desk no wobbling even at full height (tested 50,000+ li…