AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
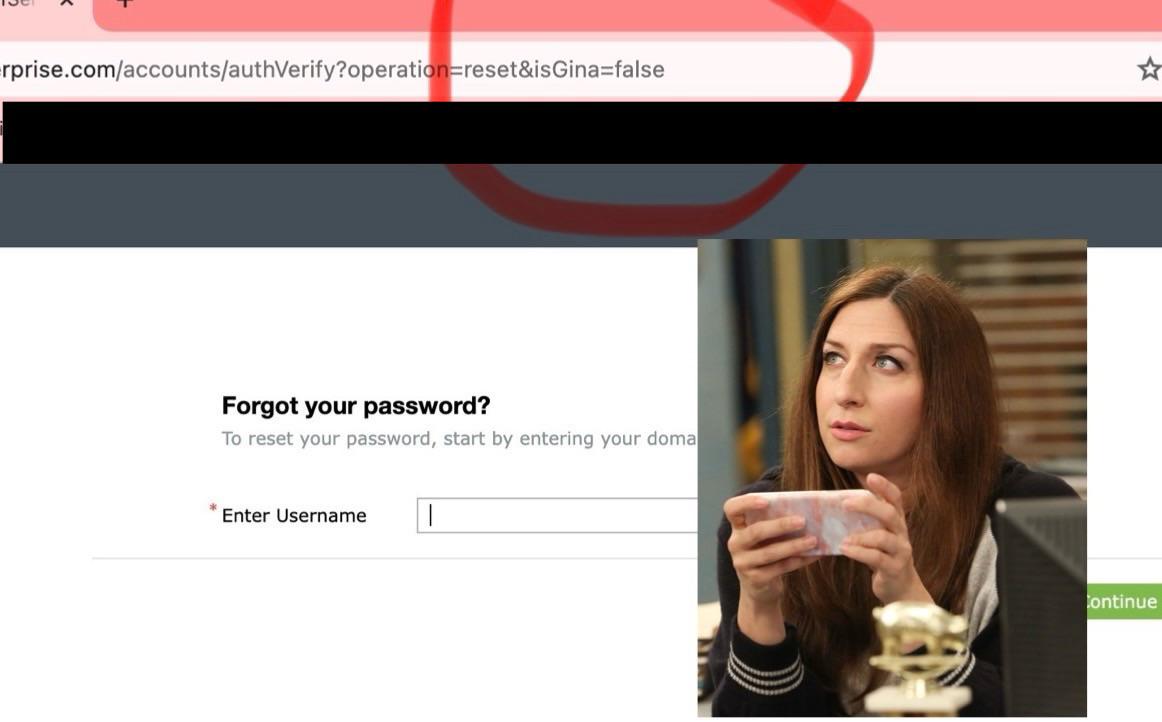
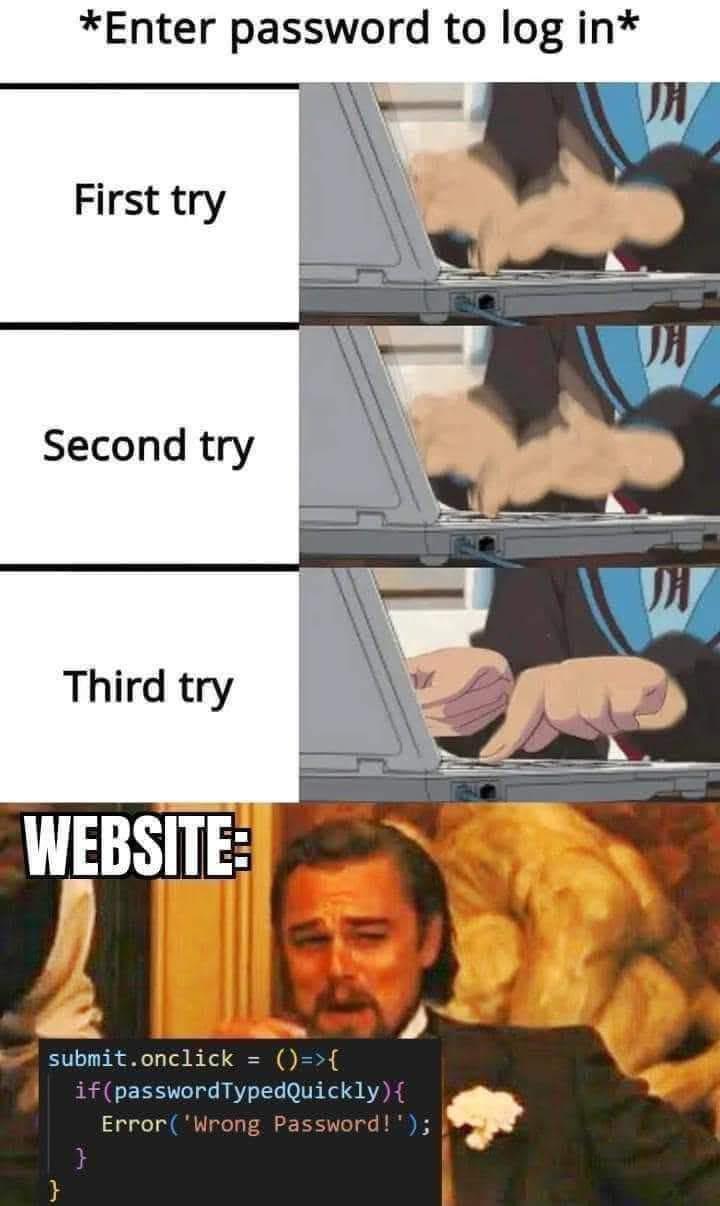
Ah, the classic "did you type your password too quickly? DENIED!" scenario. Twenty years in this industry and websites are still pulling this garbage. Some frontend dev thought they were clever by checking how fast you type your password, as if speed equals automation. Meanwhile, the rest of us are just trying to log in before our coffee gets cold. The best part? The site doesn't even check if the password is correct - just that you didn't type it "suspiciously fast." Brilliant security theater from the same people who probably store your password as plaintext in a CSV file somewhere.
Login Logic
authentication-memes, password-memes, frontend-memes, security-memes, user-experience-memes | ProgrammerHumor.io
More Like This