password Memes

Nice Password Dude

Nice Password Dude
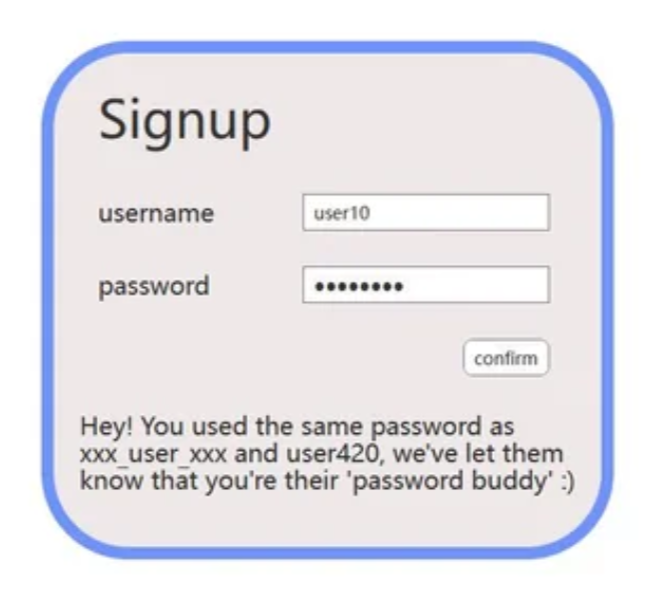
When you think you're being original with your password but the signup form casually drops that xxx_user_xxx and user420 are already using it. Nothing says "secure authentication" quite like broadcasting to strangers that they're your password twins. The whole point of hashing passwords is so nobody—not even the server—should know what your actual password is, let alone be able to match it with other users. If a system can tell you "hey, you share a password with these specific users," that means they're either storing passwords in plaintext (yikes) or using some seriously broken hashing implementation. Either way, run. Fast. The cherry on top? Calling them your "password buddy" like it's some wholesome social network feature instead of a catastrophic security nightmare.

Password Requirements

Password Requirements
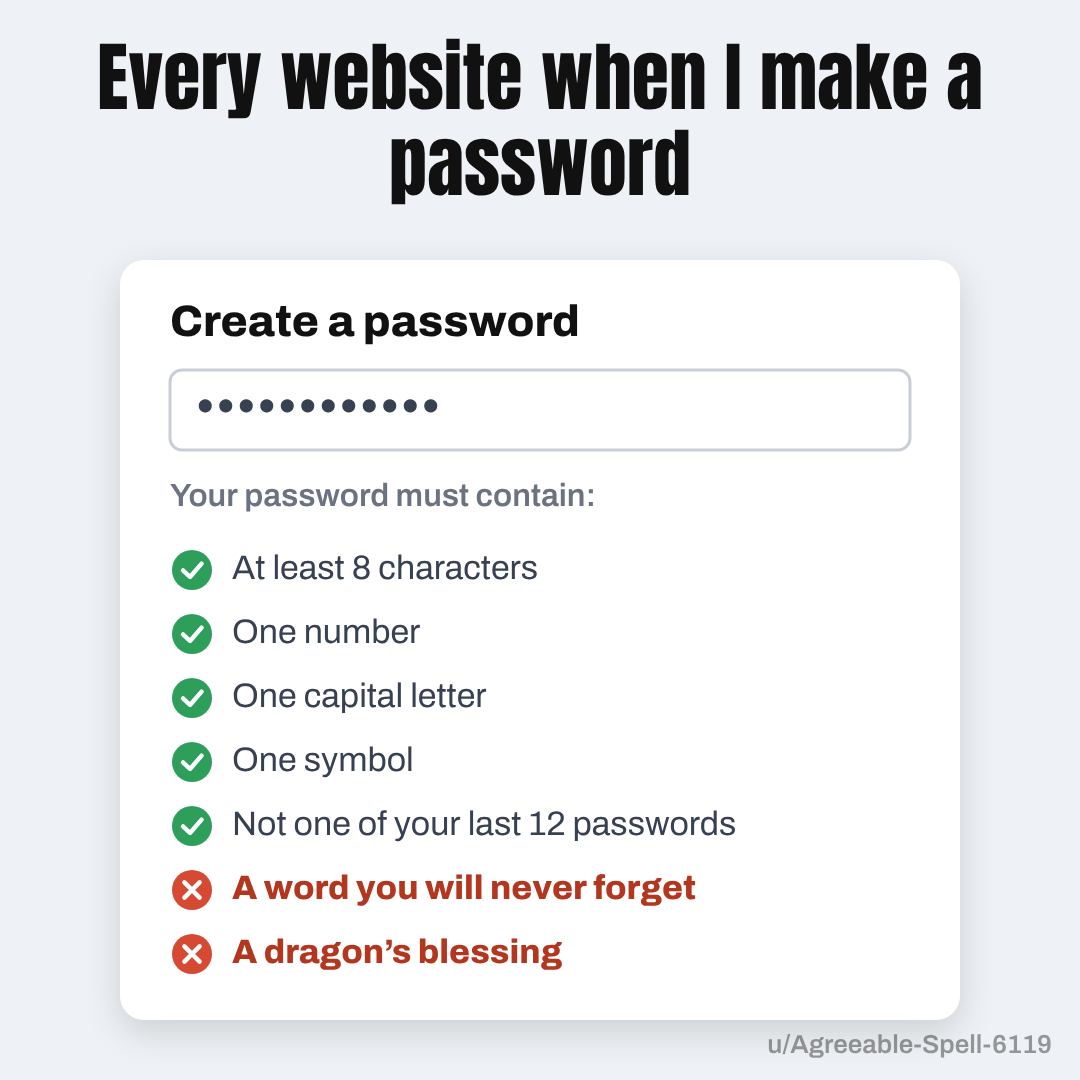
So you've got your standard password requirements: 8 characters, a number, a capital letter, a symbol—cool, reasonable security measures. Then they hit you with "not one of your last 12 passwords" which is already pushing it because who remembers that many passwords? But wait, there's more! You also need "a word you will never forget" (spoiler: you will absolutely forget it) and "a dragon's blessing" because apparently we're securing bank accounts with medieval fantasy quests now. Nothing says robust authentication like needing to consult a mythical creature before logging into your email. Just use a password manager at this point, or better yet, sacrifice a goat to the security gods.

Animorphs Did It First

Animorphs Did It First
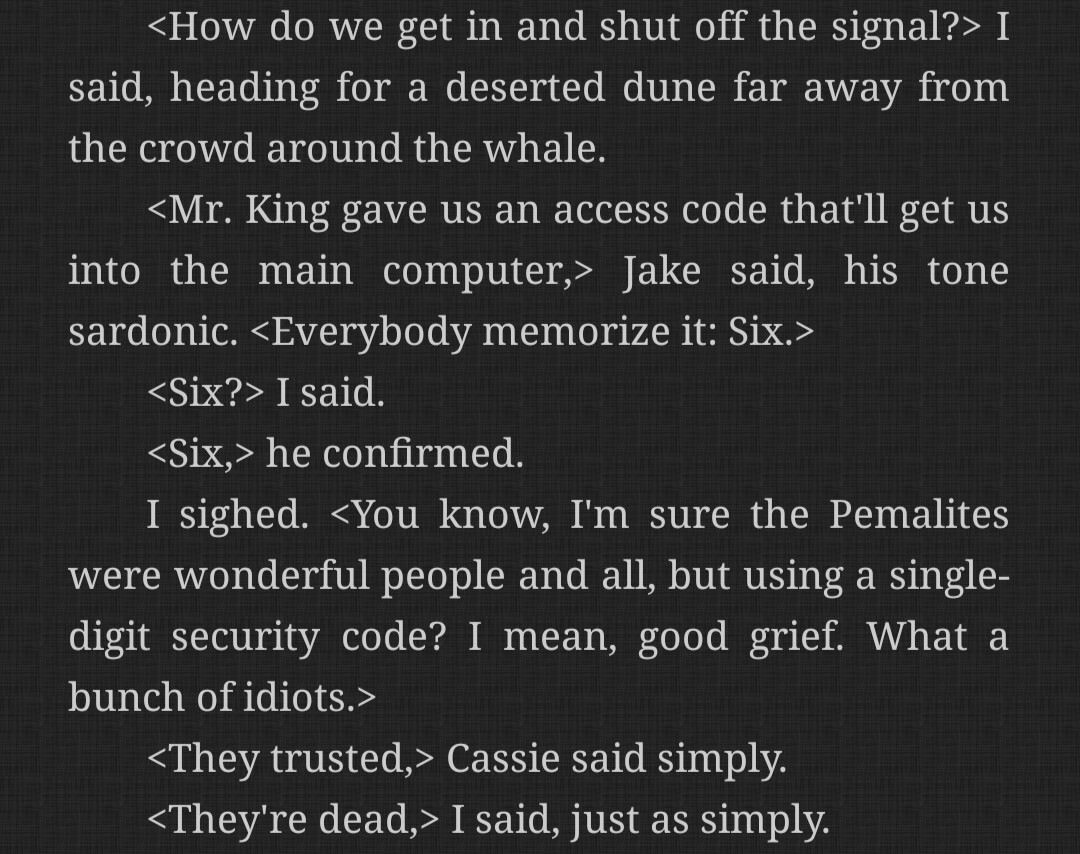
A single-digit passcode. To protect the main computer. In a young adult sci-fi novel from the 90s. The Pemalites built interstellar spacecraft and uploaded their consciousness into android bodies, but apparently their cybersecurity team was on vacation when they decided "6" was sufficient protection. Not "696969" or even "000000" - just straight up 6 . The protagonist's reaction is perfect. That internal scream of "what kind of enterprise-level incompetence is this?" resonates with anyone who's ever inherited a production system with "admin/admin" credentials or found API keys hardcoded in the repo. And the response? "They trusted." Yeah, they're also extinct now. Coincidence? Security through obscurity and blind trust - a tale as old as time, apparently spanning galaxies.

Indian Padlock

Indian Padlock
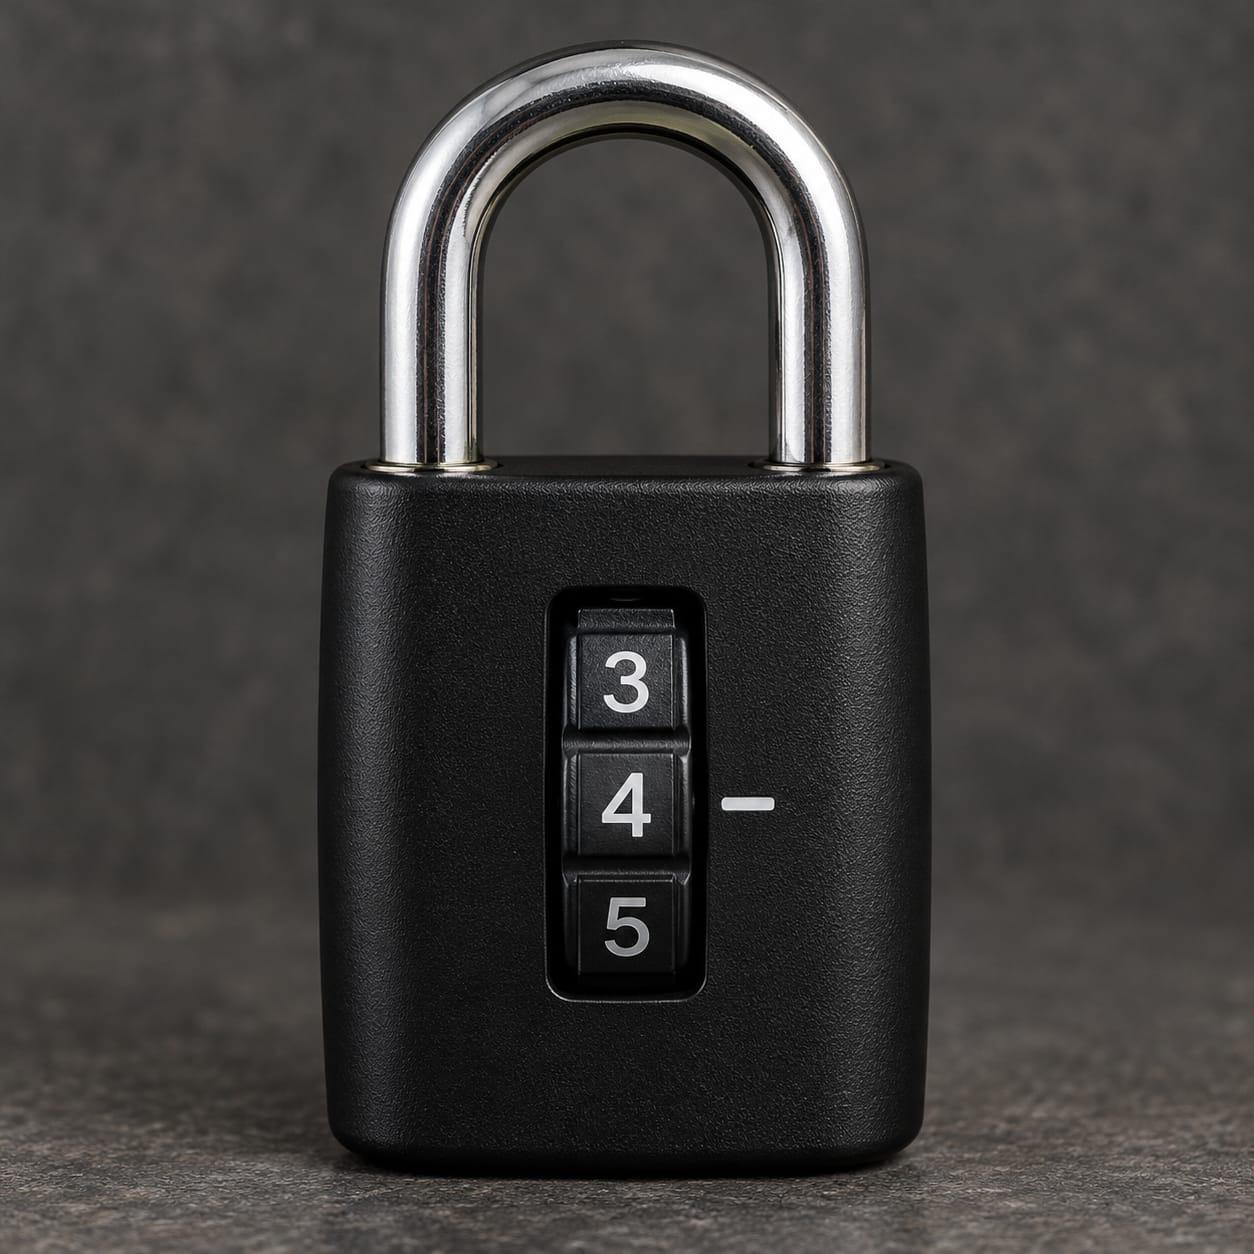
When your security implementation is just off-by-one errors all the way down. The combination is literally 3-4-5, because apparently someone thought the Pythagorean theorem was the ultimate password strategy. It's like using "password123" but for physical locks – technically it works, but you're basically just asking to get breached. The minus sign at the end really ties it all together, like the lock is doing some mental arithmetic before deciding whether to open. "Let me just subtract my self-respect real quick..."

Open Sesame!

Open Sesame!
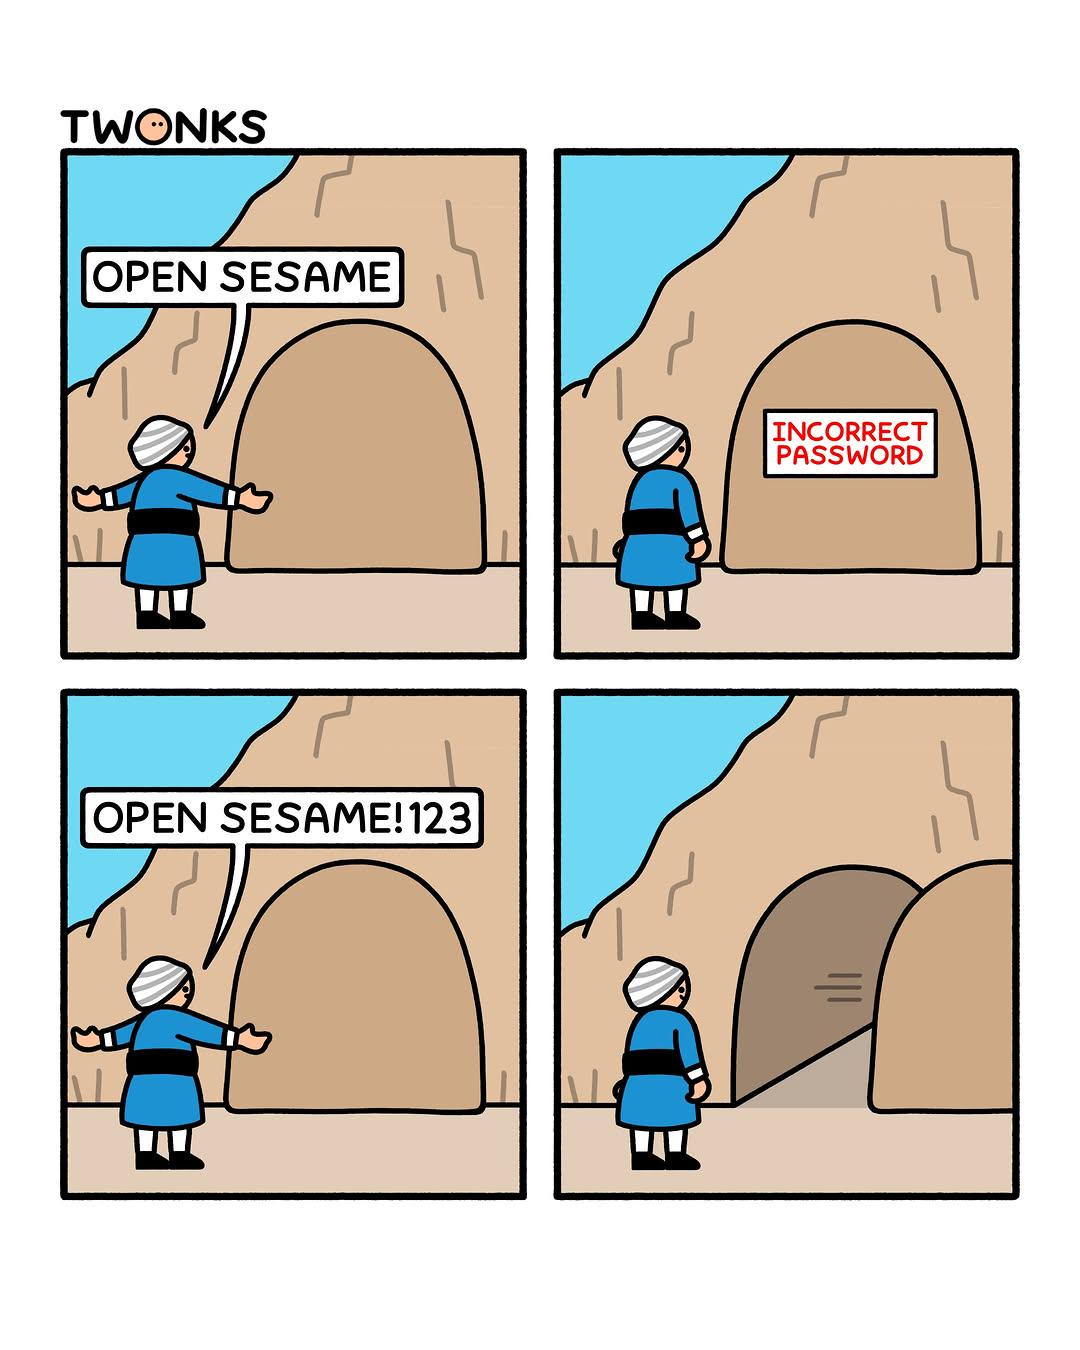
The ancient tale of Ali Baba gets a modern security update. Our hero tries the classic "Open Sesame" password and gets hit with the dreaded "INCORRECT PASSWORD" error. Classic rookie mistake—forgetting that your password requirements demand at least one number, one special character, and probably a blood sacrifice. So naturally, they pivot to "OpenSesame!123" and boom—the cave opens like it's been waiting for that sweet combination of uppercase, lowercase, and numbers all along. The cave door was basically running the same password validation as every corporate login system you've ever encountered. Fun fact: If Ali Baba's cave existed today, it would probably also require him to change his password every 90 days and wouldn't let him reuse any of his last 24 passwords. The treasure would've been long gone before he figured out "OpenSesame!123Winter2024$"

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

Should've Just Picked A Better Password

Should've Just Picked A Better Password
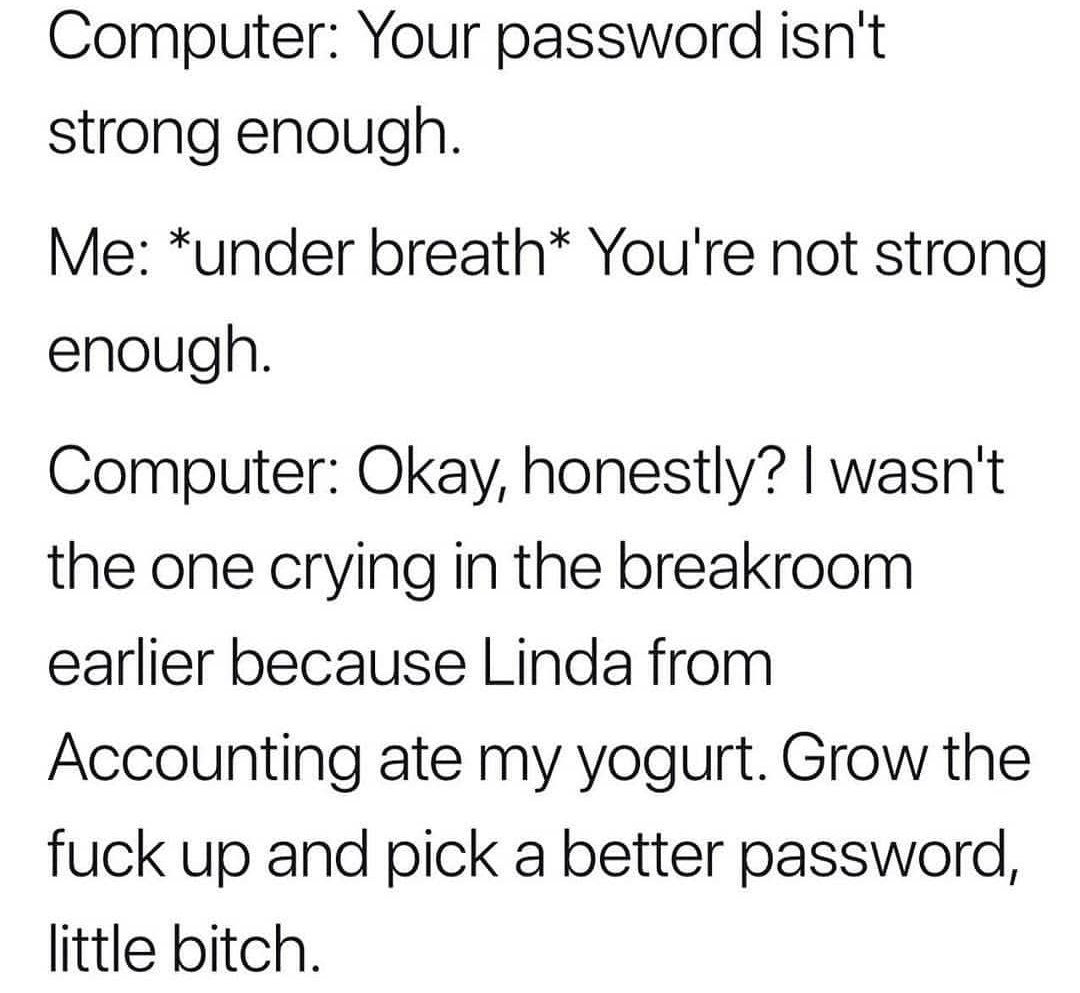
Your computer really chose violence today. Nothing says "healthy user experience" like getting emotionally destroyed by your own machine because you used "Password123!" for the fifteenth time. The computer's out here airing out workplace drama and personal grievances like it's been holding that in for YEARS. Linda from Accounting catching strays while you're just trying to log into your email. Maybe if we spent less time making password requirements that demand a hieroglyphic, three emojis, and your grandmother's maiden name, and more time on actual security architecture, we wouldn't be getting roasted by our own hardware. But sure, add another special character—that'll fix everything.

AES Encryption Move Over

AES Encryption Move Over
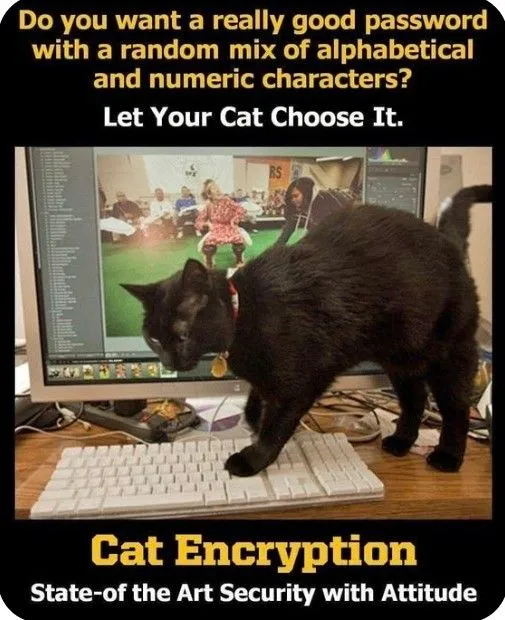
Forget your fancy cryptographic algorithms. The real unbreakable password generation method is letting a cat walk across your keyboard. Random? Check. Unpredictable? Absolutely. Impossible to reproduce? You bet. Plus it comes with free fur in your keyboard switches. "Cat Encryption" - where the entropy source has whiskers and judges you silently. The NSA is probably already recruiting felines as we speak. Military-grade security with maximum sass. Your password manager could never generate something as secure as "jkl;asdfjkl;3489uhjkl;asdf" with that level of authentic chaos. Good luck remembering it though. The cat certainly won't help you recover it.

Please Choose A Password You Will Not Have Used In The Future

Please Choose A Password You Will Not Have Used In The Future
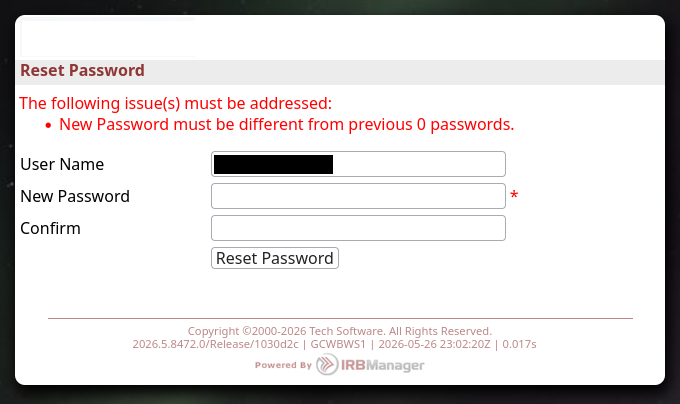
So the system is asking you to create a password that's different from your previous 0 passwords. Zero. None. Zilch. Which means literally any password works because you haven't used any passwords before. But instead of just saying "create a password," some genius developer wrote validation logic that accidentally reveals you're a brand new user with no password history. It's like a bouncer saying "you can't wear the same outfit you wore the last 0 times you were here" – technically correct, but hilariously pointless. The real kicker? They still made it a requirement with a bullet point and everything, as if checking against an empty list is some kind of security feature. Peak enterprise software energy right here.

My New Password

My New Password
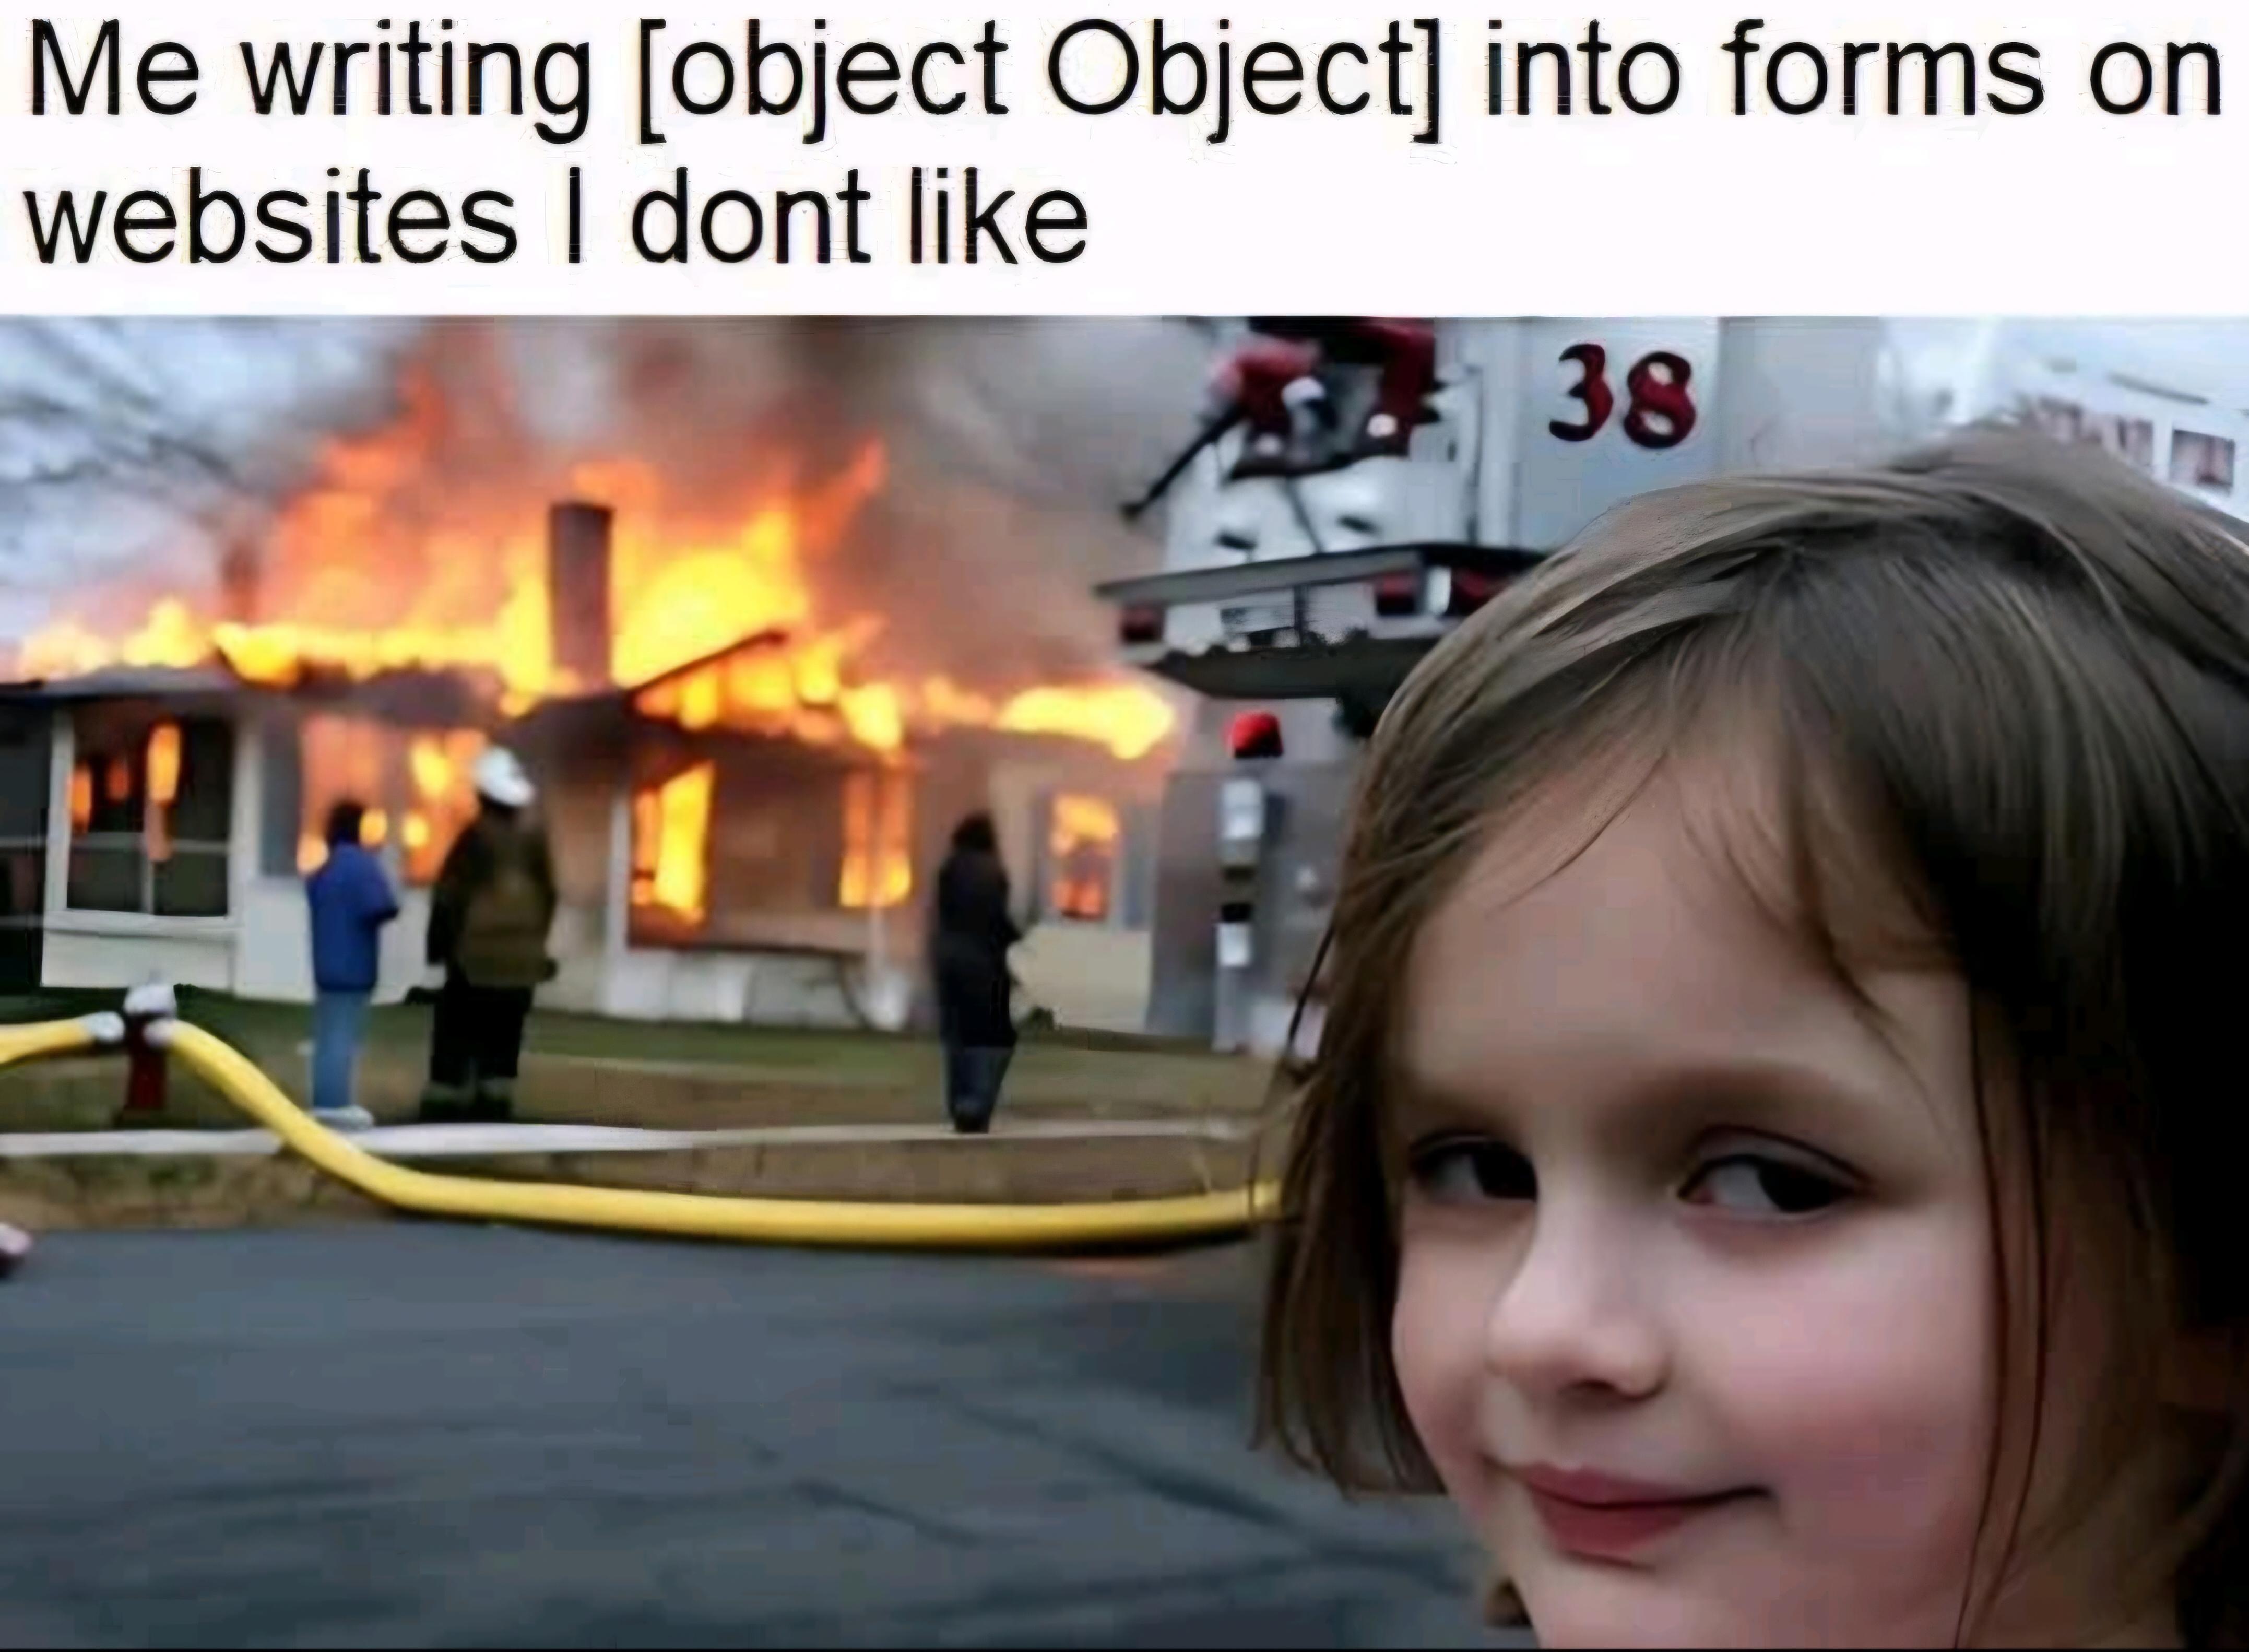
Content Me writing [object Object] into forms on websites I dont like 38

This Triggers Me

This Triggers Me
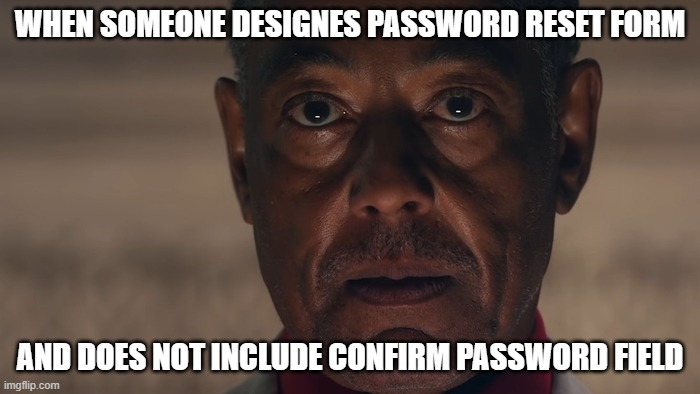
You know what's worse than forgetting your password? Having to type it twice and getting them slightly different because your pinky slipped on the Shift key. Nothing screams "I hate users" quite like a password reset form that makes you enter your new password once, then immediately sends you into an anxiety spiral wondering if you fat-fingered a character. The confirm password field exists for ONE reason: to save you from yourself. Skipping it is like removing seatbelts from cars because "people should just drive better." Sure, it's one less field to validate, but it's also one less barrier between your users and a support ticket titled "I can't log in and I'm crying."

Half Width Characters

Half Width Characters
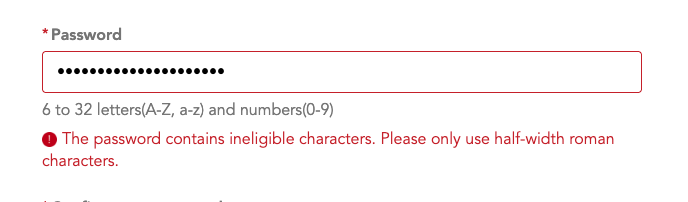
You enter a perfectly valid password with letters and numbers, meeting all their ridiculous requirements. But wait—the form rejects it because you used "ineligible characters." The kicker? You need to use "half-width roman characters." For those lucky enough to have never encountered this nightmare: half-width vs full-width characters are a thing in Japanese and other East Asian text systems. Full-width characters take up more space (think a vs a). Some legacy systems or poorly designed forms throw a fit if you accidentally use the wrong width, even though they look nearly identical. Instead of, you know, just normalizing the input on the backend like a sane developer, they decided to make it YOUR problem. Because why make UX better when you can just confuse users with error messages that sound like they're written in ancient riddles? Classic enterprise move right there.

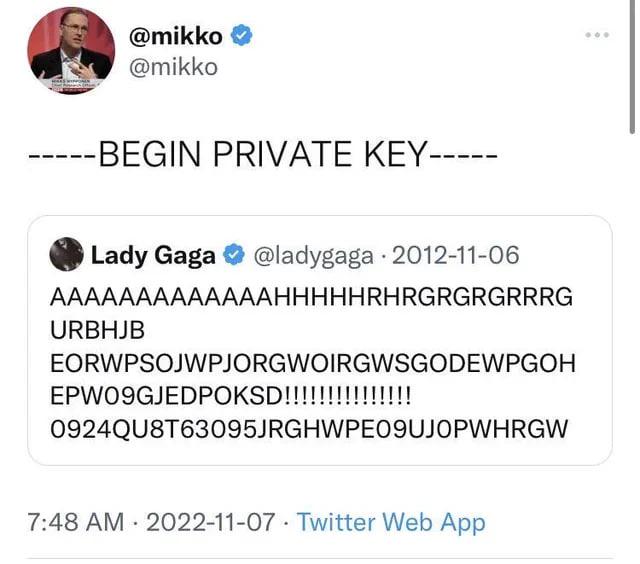
The Public Private Key Paradox

The Public Private Key Paradox
The greatest cryptographic catastrophe of our time! Someone just mistook Lady Gaga's keyboard-smashing tweet from 2012 as their private SSH key and posted it publicly with the "BEGIN PRIVATE KEY" header. That's like leaving your house key under a doormat labeled "DEFINITELY NOT A KEY HERE." Any security engineer seeing this is simultaneously laughing and having heart palpitations. The irony of labeling something as private while broadcasting it to the entire internet is just *chef's kiss* perfect.

UGREEN NAS DH2300 2-Bay Desktop NAS, Support Capacity 64TB (Diskless)

UGREEN NAS DH2300 2-Bay Desktop NAS, Support Capacity 64TB (Diskless)
Entry-level NAS Personal Storage:UGREEN NAS DH2300 is your first and best NAS made easy. It is designed for beginners who want a simple, private way to store videos, photos and personal files, which …