Compliance Memes

Posts tagged with Compliance
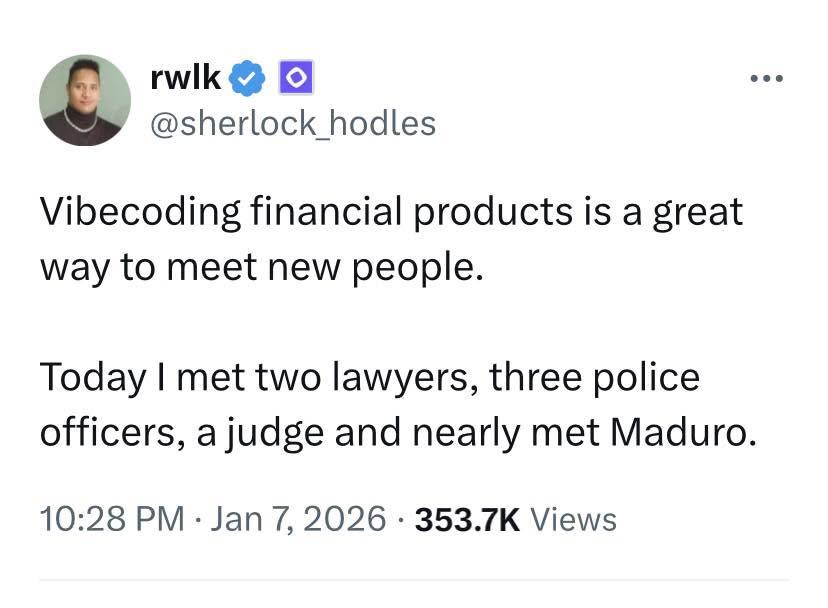
Ship Fast Fix Later If Not Arrested

Ship Fast Fix Later If Not Arrested
When "move fast and break things" takes on a whole new legal dimension. Turns out shipping buggy code in fintech doesn't just break your CI/CD pipeline—it breaks federal regulations too. The startup mantra of "ship it now, fix it later" hits different when your product handles actual money instead of just tracking which memes your users like. One misplaced decimal point and suddenly you're not debugging in production—you're explaining your architectural decisions to people with law degrees. Pro tip: When your standup updates start including phrases like "retained counsel" and "regulatory compliance," maybe that hotfix should've gone through QA after all.

I Will Put Some Random Numbers

I Will Put Some Random Numbers
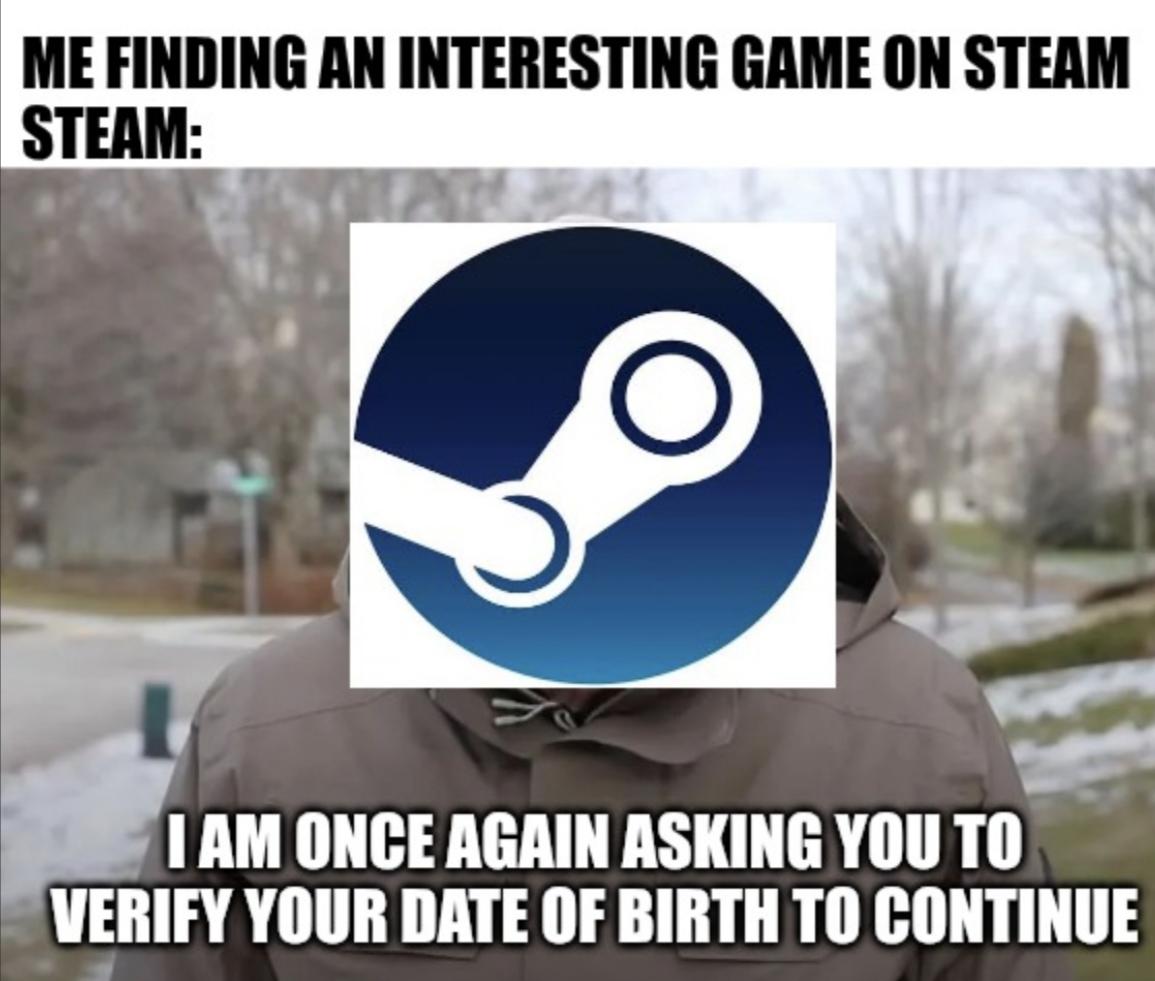
Steam's age verification is the digital equivalent of a bouncer who doesn't care. You could literally type in January 1, 1900 and it'd let you through without batting an eye. The system exists purely to check a legal compliance box, not to actually verify anything. So naturally, every gamer has their go-to fake birthday burned into muscle memory—usually something like "01/01/1990" because who has time to think of creative lies when you just want to see if that indie game is worth $2.99? The real kicker is that Steam asks you EVERY. SINGLE. TIME. even though they definitely know who you are since you're logged in. It's like your own computer asking for your ID at the door of your own house.

Wrong Answers Only

Wrong Answers Only
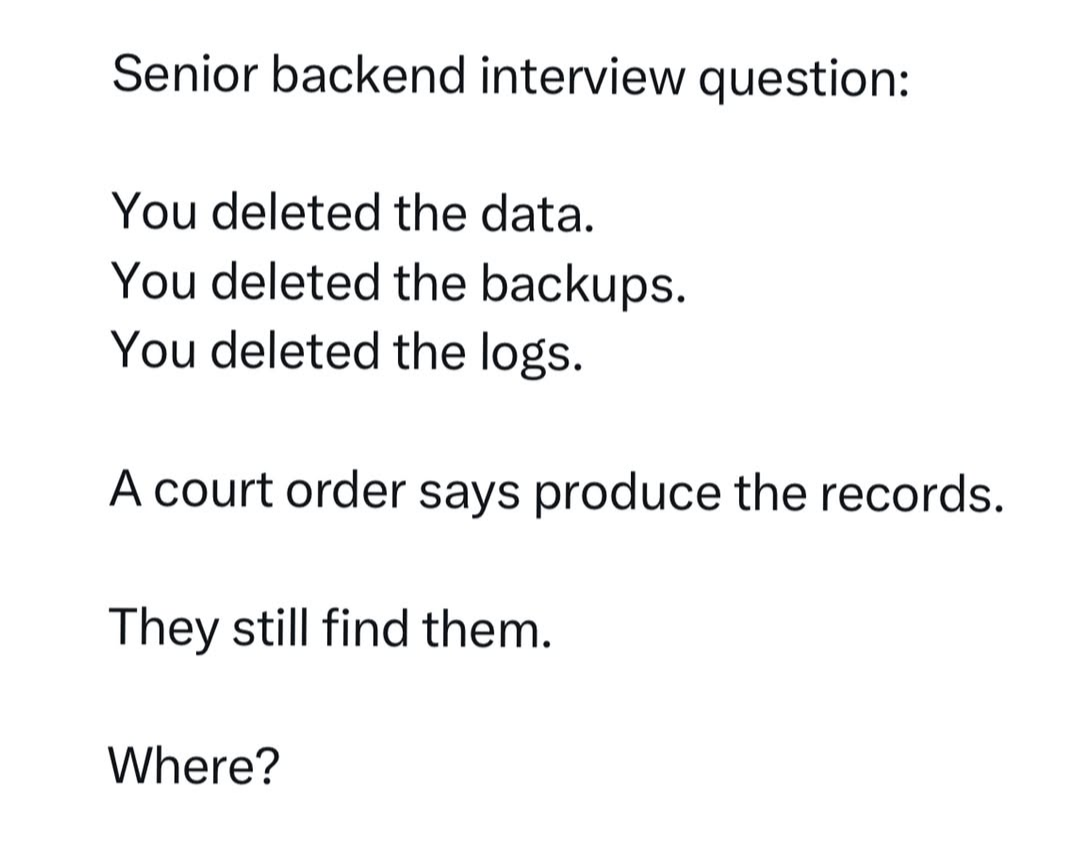
Every senior backend engineer's nightmare scenario, delivered as a casual interview question. You've nuked the data, nuked the backups, nuked the logs that would've helped you figure out what went wrong. Now there's a court order demanding those records, and somehow they still managed to find them. The punchline? That single word "Where?" captures the pure existential dread of realizing your deletion wasn't as permanent as you thought. Maybe it's in some S3 glacier vault you forgot about. Maybe it's in a replica database nobody documented. Maybe it's in that staging environment that accidentally got production data. Or maybe—and this is the real horror—it's in the cloud provider's internal backups that you don't control. The correct answer, of course, is that you can never truly delete anything in production. It's always somewhere. Haunting you. Waiting for a subpoena.

New Benchmark Dropped

New Benchmark Dropped
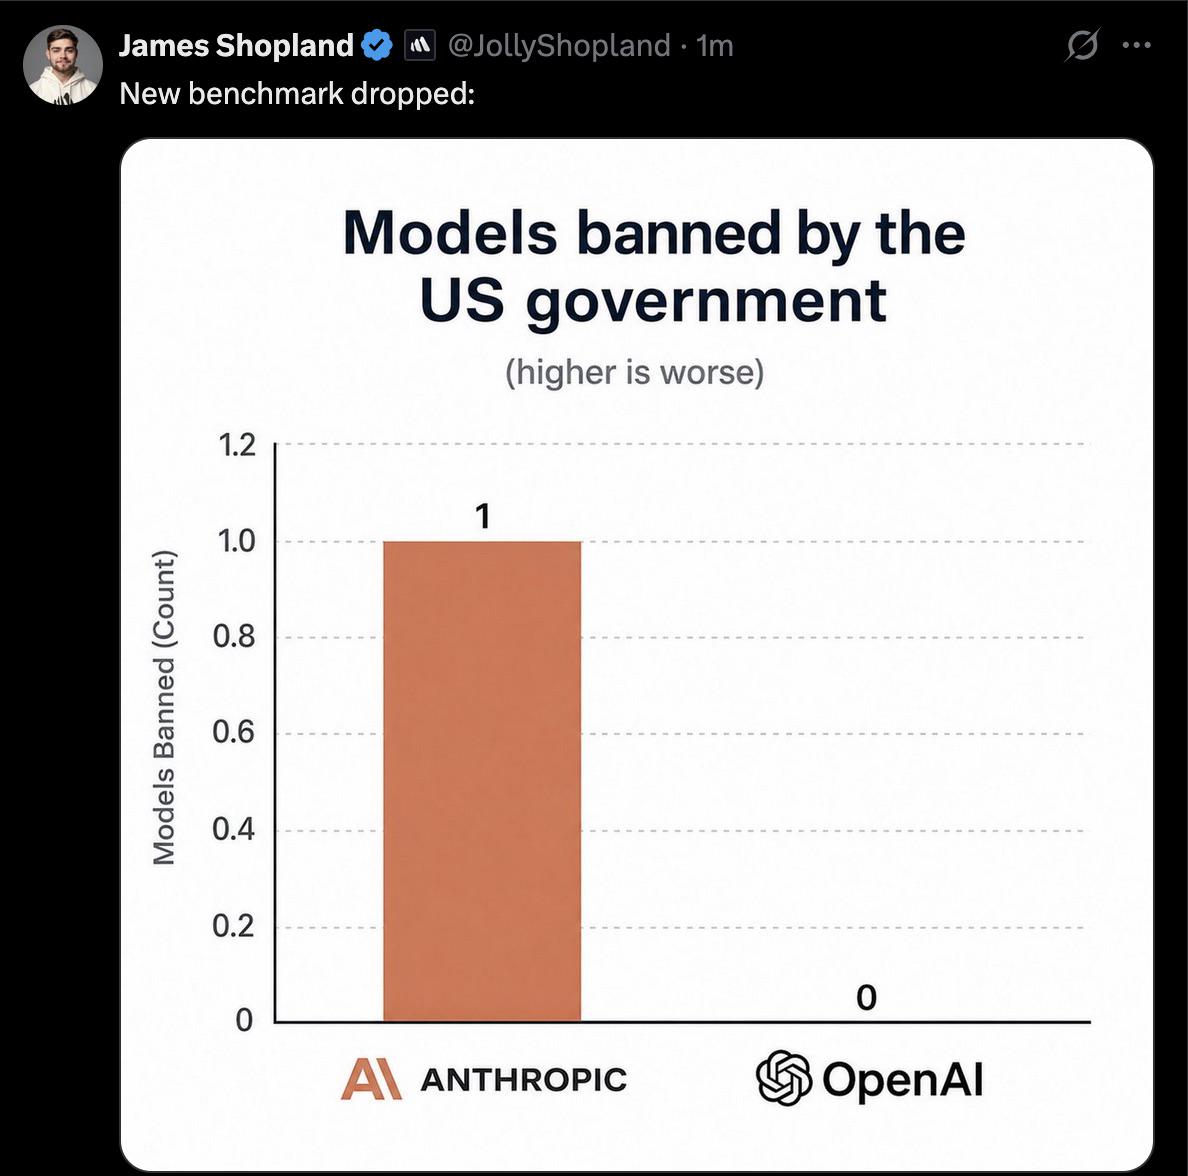
When your AI company's biggest achievement is having exactly one model banned by the government while your competitor sits at a perfect zero. That's right, Anthropic is out here flexing their regulatory compliance issues like it's a badge of honor. The "(higher is worse)" label really drives home the point—this is the one benchmark where you definitely don't want to be winning. OpenAI sitting pretty at zero bans while Anthropic's lone model got the government's attention is peak tech industry irony. Nothing says "we're innovating" quite like getting your model yeeted by Uncle Sam. It's like comparing who got sent to the principal's office more often. Congratulations, Anthropic, you're the troublemaker of the AI world. 🏆

Accept

Accept
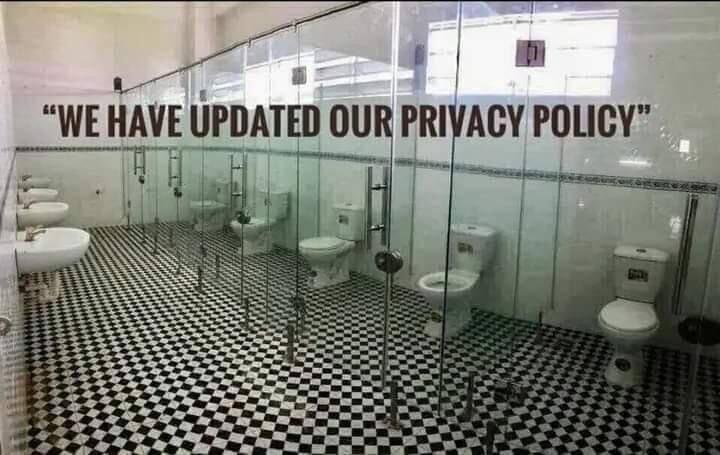
You know how every app nowadays hits you with "We've updated our privacy policy" and you just click accept without reading 47 pages of legal jargon? Yeah, this is what that actually looks like. Those bathroom stalls with crystal-clear glass walls are basically your data after you agreed to let Facebook, Google, and every sketchy app harvest your entire digital existence. The illusion of privacy is strong with this one. Sure, there are "walls" technically separating you, but everyone can see everything. Just like how privacy policies claim they "protect your data" while simultaneously sharing it with 847 third-party partners for "legitimate business purposes." We've all become so numb to these notifications that we'd probably accept a privacy policy written in Klingon if it meant we could just use the damn app already.

3dRose Binary Code - Black and Green Poster Matte 12x12

3dRose Binary Code - Black and Green Poster Matte 12x12
Bring gallery-style character to any wall with this matte art poster, printed on thick, museum-quality paper with a smooth, low-glare finish. Rich, true-to-color printing and crisp detail keep the de…

Covering Sec Ops And Sys Admin For A Startup

Covering Sec Ops And Sys Admin For A Startup
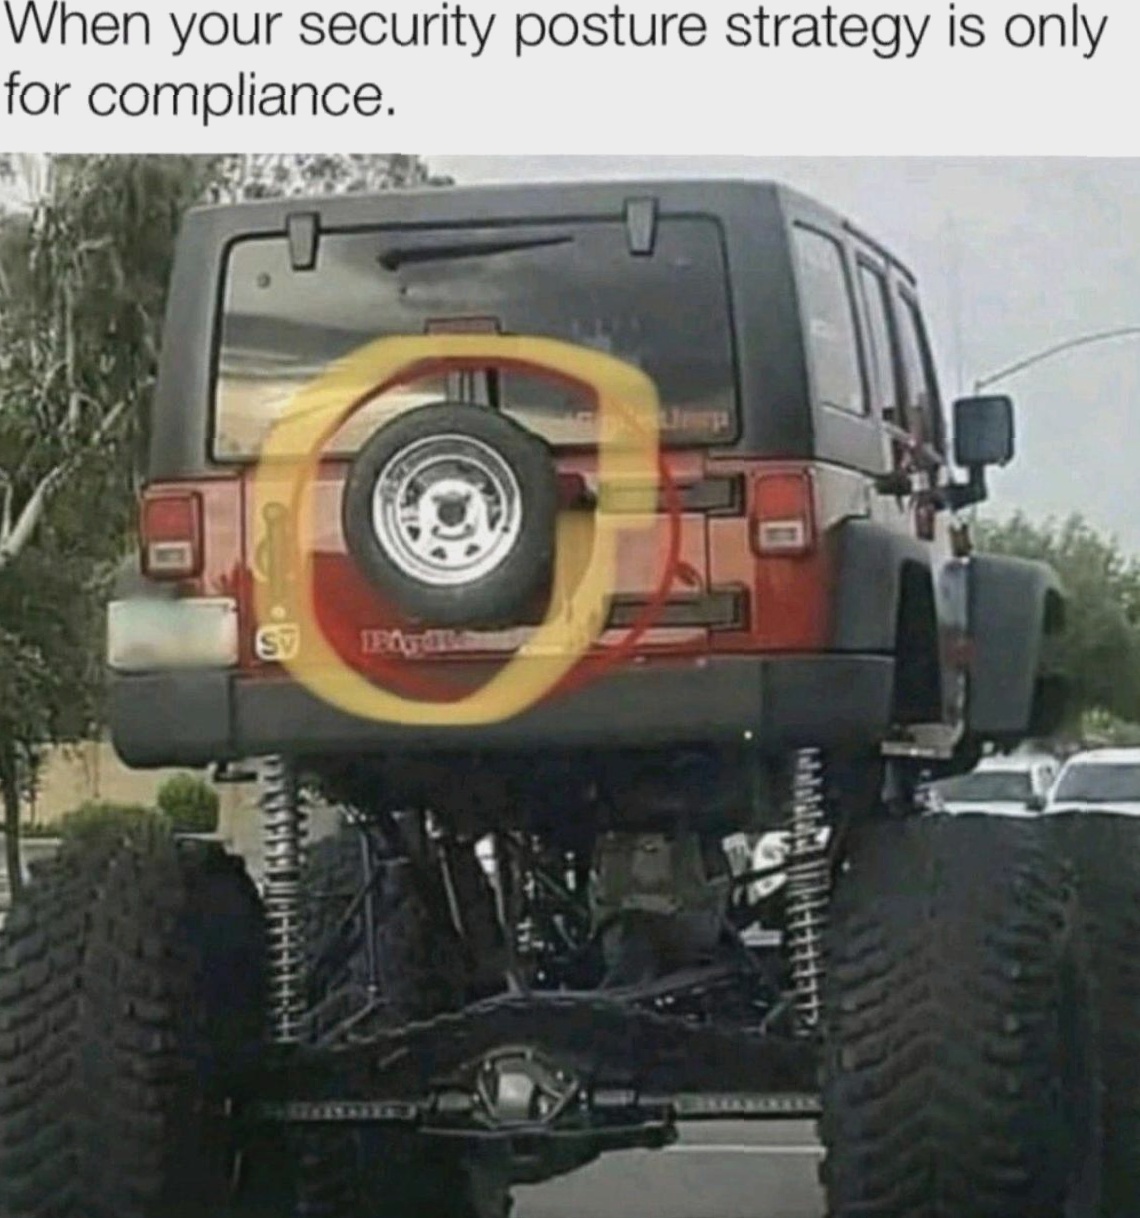
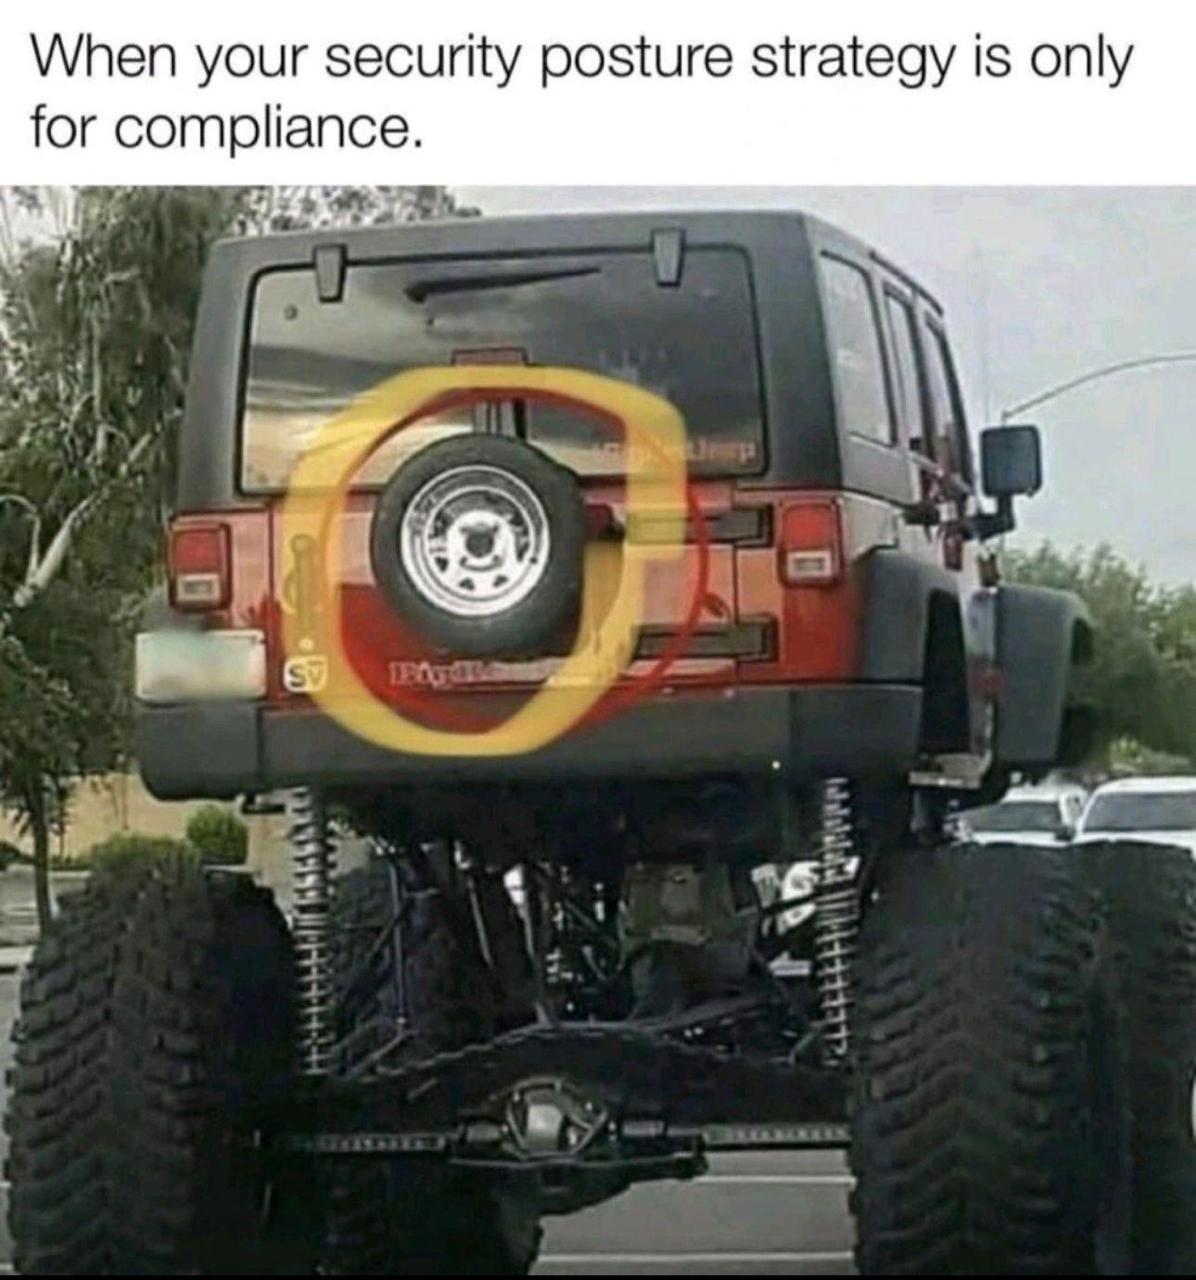
Startup security in a nutshell: slap some duct tape on it and pray the auditors don't look too closely. That spare tire "protecting" the actual tire is doing exactly as much work as your security measures when the entire strategy is just "check the compliance boxes and hope nobody actually tries to hack us." You're the only person wearing all the hats—SecOps, SysAdmin, probably also the coffee maker repair person—and management thinks SOC 2 Type II is just a fancy sock brand. Meanwhile, your "defense in depth" is more like "defense in desperation" with passwords stored in a shared Google Doc titled "IMPORTANT_DONT_DELETE.txt". But hey, at least you passed the audit. The actual infrastructure held together by shell scripts and good vibes? That's a problem for future you.

Delayed EU Release

Delayed EU Release
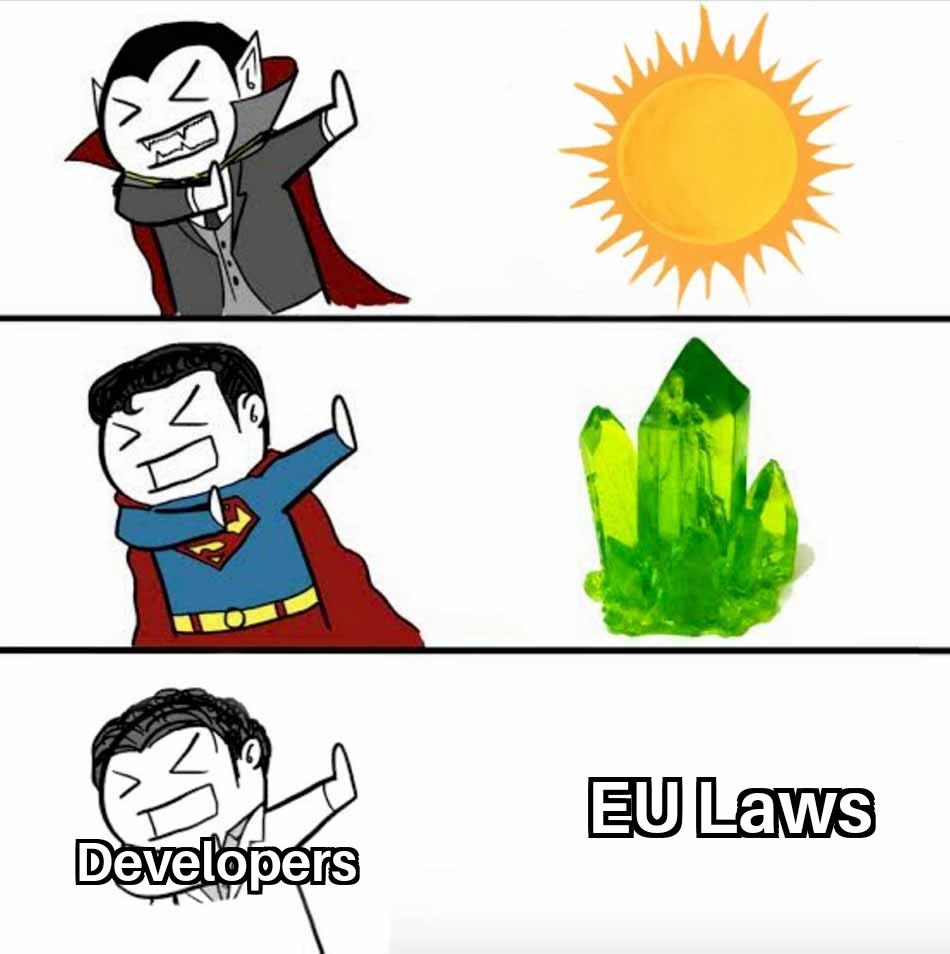
Dracula fears the sun, Superman runs from kryptonite, but developers? They cower in absolute TERROR before the almighty EU regulations. GDPR, cookie banners, data protection laws, digital services acts—it's like the final boss that just keeps spawning more health bars. You thought shipping your app was hard? Try doing it while navigating a legal labyrinth that makes your spaghetti code look organized. Nothing strikes fear into a dev team quite like the words "we need to be EU compliant before launch." Suddenly that release date gets pushed back faster than you can say "legitimate interest."

Gets Phished By It Anyways

Gets Phished By It Anyways
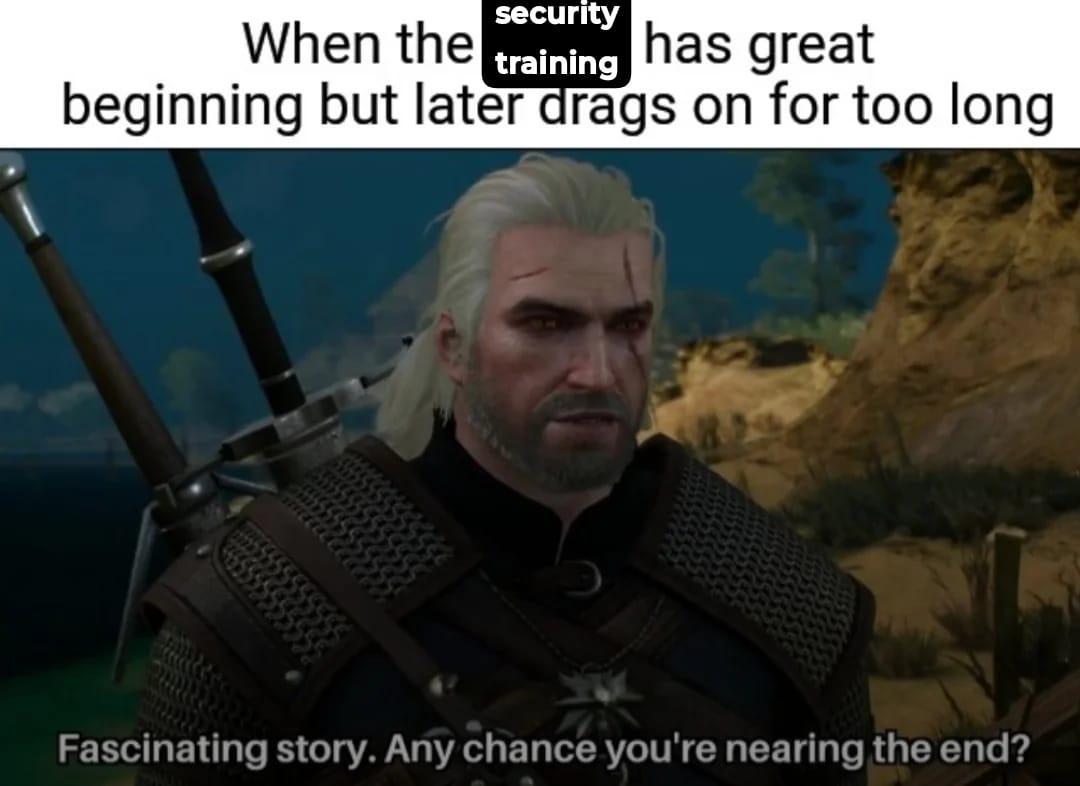
Ah yes, the mandatory security training that starts with good intentions and somehow evolves into a 4-hour PowerPoint odyssey about password hygiene you learned in 2003. You're nodding along for the first 15 minutes, then suddenly you're on slide 247 about the history of phishing attacks dating back to AOL chatrooms. The real kicker? After sitting through this marathon of "don't click suspicious links" and "verify sender addresses," Karen from accounting still clicks on "URGENT: Your Amazon package needs immediate verification" from [email protected] and compromises the entire company's credentials. Security training is like that gym membership—great start, zero follow-through, and somehow you're worse off than before because now you're overconfident.

Backup Supremacy🤡

Backup Supremacy🤡
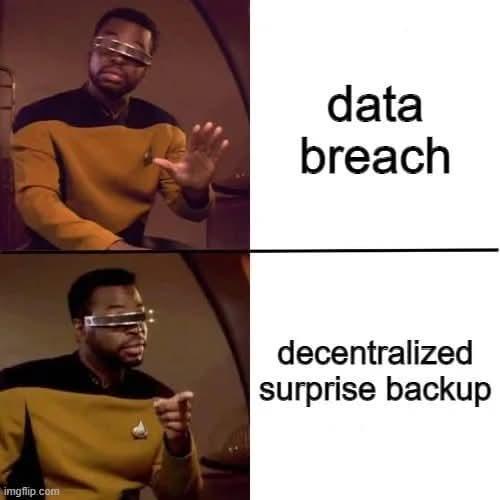
When your company gets hit with a data breach: *mild concern*. But when they discover you've been keeping "decentralized surprise backups" (aka unauthorized copies of the entire production database on your personal NAS, three USB drives, and your old laptop from 2015): *chef's kiss*. The real galaxy brain move here is calling them "decentralized surprise backups" instead of what the security team will inevitably call them: "a catastrophic violation of data governance policies and possibly several federal laws." But hey, at least you can restore the system while HR is still trying to figure out which forms to fill out for the incident report. Nothing says "I don't trust our backup strategy" quite like maintaining your own shadow IT infrastructure. The 🤡 emoji is doing some heavy lifting here because this is simultaneously the hero move that saves the company AND the reason you're having a very awkward conversation with Legal.

Two Factor Authentication

Two Factor Authentication
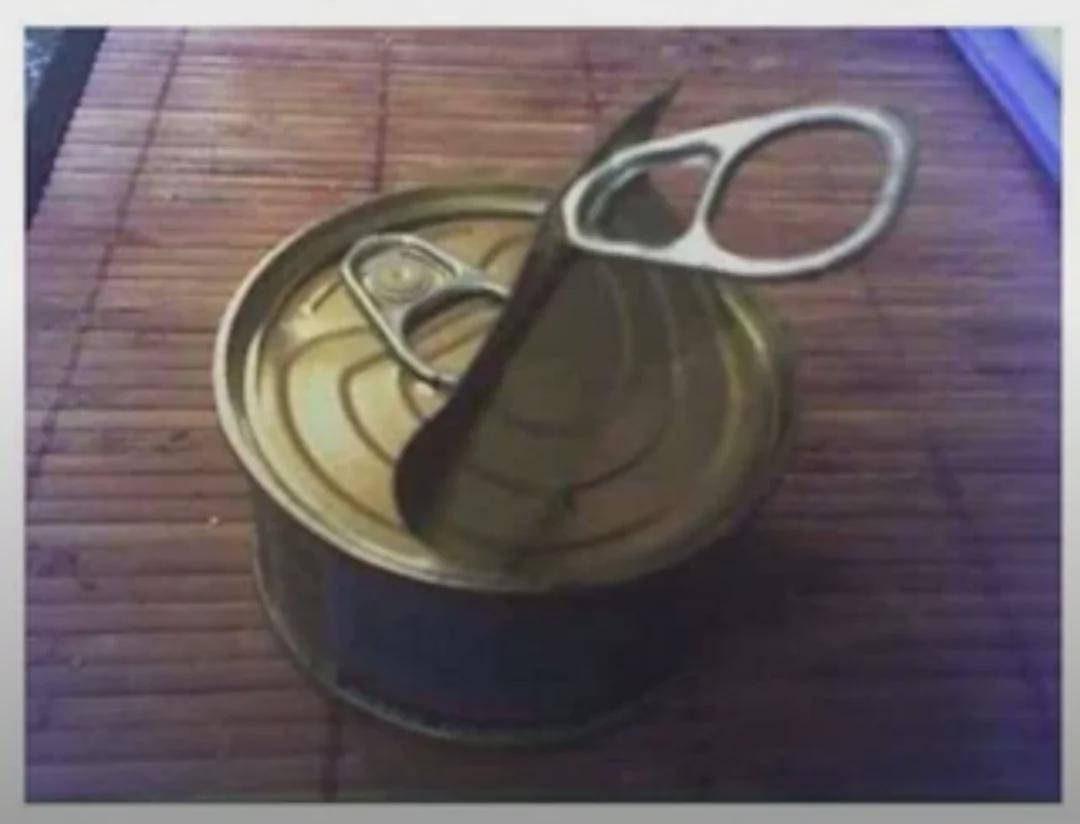
The most secure authentication method known to developers - a can with scissors jammed in it. Need to access your account? You'll need both the can AND the scissors! Security experts hate this one weird trick that somehow meets compliance requirements while being utterly useless. Just like how most corporate 2FA implementations feel when you're forced to type in a code that was texted to the same device you're already holding. Pure security theater at its finest!

The Myth Of Consensual Software Development

The Myth Of Consensual Software Development
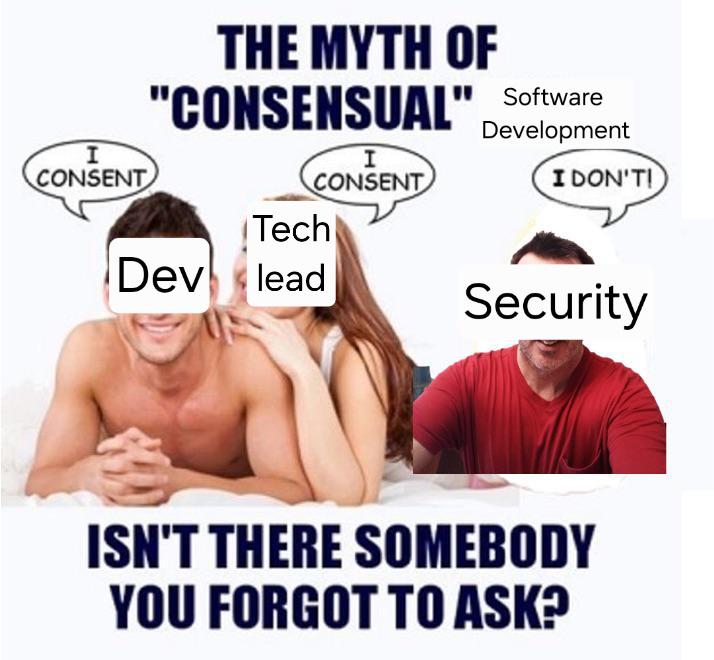
The eternal struggle of software development in one perfect image. Devs and tech leads happily pushing code while security sits there like the responsible adult at a frat party screaming "I DON'T CONSENT!" into the void. Let's be honest, we've all shipped that feature at 4:59pm on Friday with security reviews marked as "TODO" in the PR. Then we act shocked when the security team finds 37 vulnerabilities that could've been prevented by a simple input validation. Security: The party pooper we all need but rarely want until after the breach.

Covering Sec Ops And Sys Admin For A Startup

Covering Sec Ops And Sys Admin For A Startup
The perfect metaphor for startup security doesn't exi— That's literally just a padlock icon spray-painted on the spare tire. Congrats, you've passed your SOC 2 audit! Meanwhile, your entire infrastructure is running on an intern's AWS account with the password "startuplife123" and everyone shares the same admin login because "we'll fix it later when we scale." Nothing says "we care about security (on paper)" quite like having all your protection concentrated in the one place attackers will never look – your compliance documents.

KHAMAL Cable Management Under Desk 26PCS - Cable Management Tray Kit Ventilated Hexagonal Design with Cable Clips, Wire Ties, Cord Holder & Screws for Office, Home (Black)

KHAMAL Cable Management Under Desk 26PCS - Cable Management Tray Kit Ventilated Hexagonal Design with Cable Clips, Wire Ties, Cord Holder & Screws for Office, Home (Black)
Durable & Heavy-Duty Build - KHAMAL cable management under desk is made from sturdy metal with a scratch-resistant finish, provide a high level of rust resistance, it securely holds power strips and …