AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
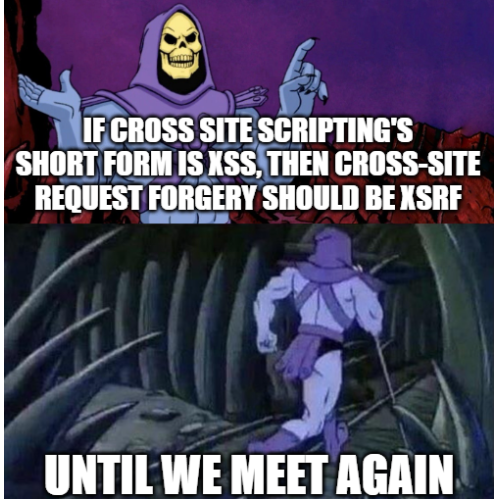
Skeletor dropping web security truth bombs before vanishing is the hero we deserve. The naming convention checks out—if Cross-Site Scripting is XSS, then Cross-Site Request Forgery should logically be XSRF. Yet the security community went with CSRF instead, committing the cardinal sin of inconsistent abbreviations. It's like naming your variables "userInput," "InputData," and then suddenly "d4t4_str1ng." The people responsible for this naming atrocity are probably the same ones who use spaces instead of tabs.
Skeletor's Web Security Naming Crusade
security-memes, webdev-memes, javascript-memes, naming-conventions-memes, xss-memes | ProgrammerHumor.io
More Like This