AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
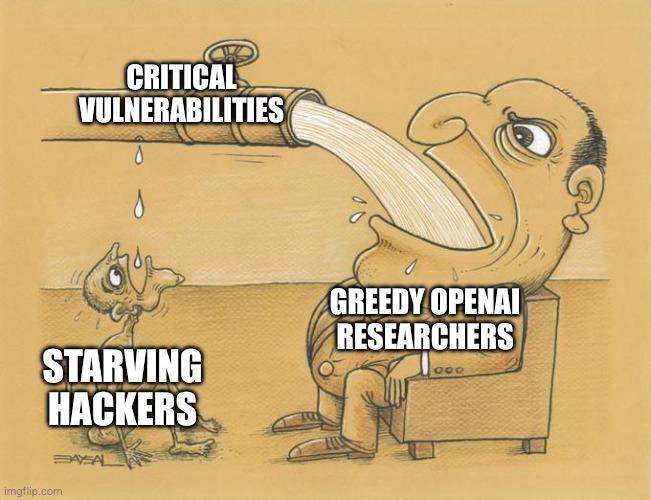
OpenAI researchers out here hoarding critical vulnerabilities like they're collecting Pokémon cards. The security landscape has basically become a buffet where the researchers are filling their plates with every CVE in sight while the actual hackers are sitting in the corner with an empty bowl wondering if there's anything left to exploit.
The joke hits different when you realize that bug bounty hunters and security researchers race to find vulnerabilities in AI systems, often claiming them faster than you can say "prompt injection." Meanwhile, the malicious hackers who actually want to cause chaos are left scrambling for scraps because every security hole has already been documented, patched, or is sitting in someone's responsible disclosure queue.
It's the cybersecurity equivalent of showing up to a Black Friday sale 10 minutes late—all the good stuff is gone, and you're left wondering if breaking into systems is even worth it anymore when the white hats have already mapped out every possible attack vector.