Bug bounty Memes

Posts tagged with Bug bounty

The State Of Bug Hunting

The State Of Bug Hunting
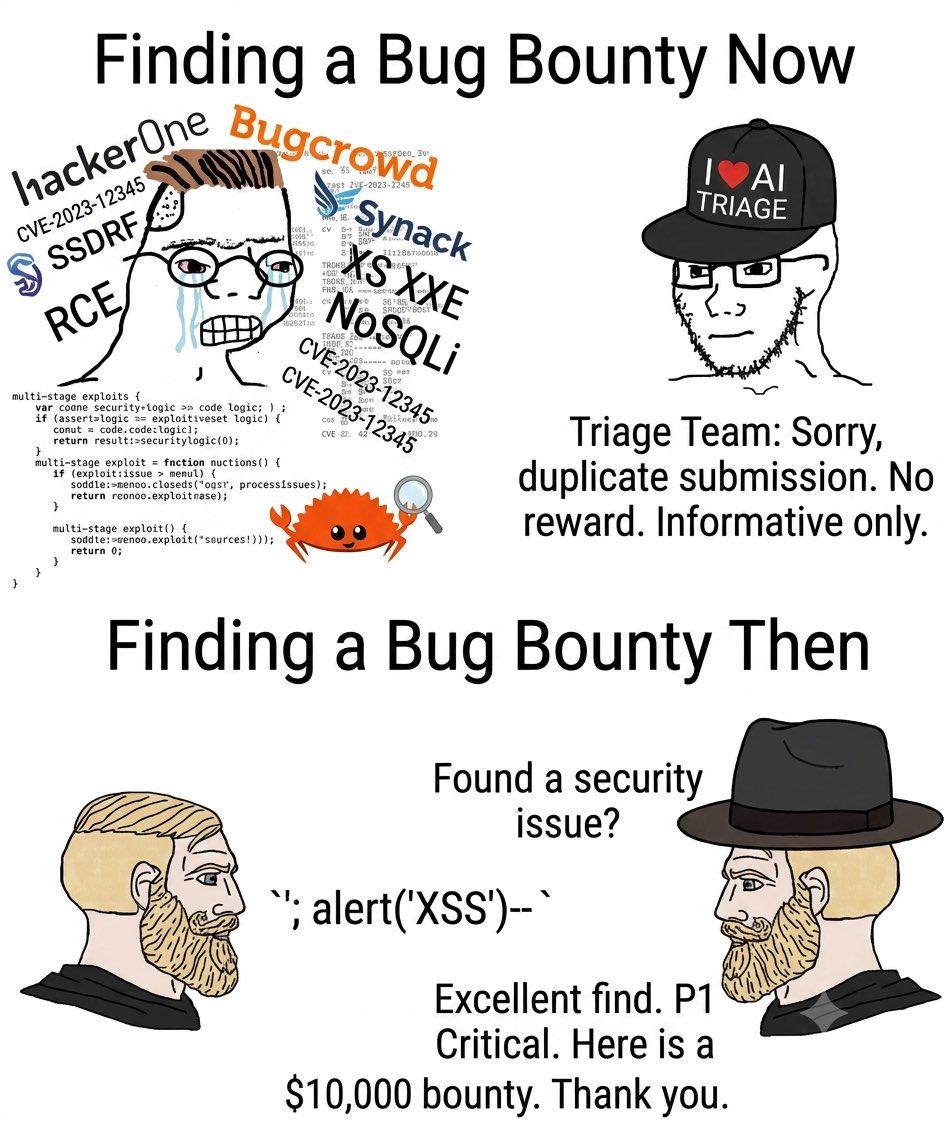
Bug bounty programs have evolved from "please submit your critical RCE with a 50-page PoC" to "sorry, our AI already found that XSS you spent three days chaining together." The top panel shows a stressed researcher drowning in CVE IDs, platform names, and actual exploit code—you know, real work. The bottom panel? Some guy types alert('XSS') and walks away with $10k. The kicker is the "I ❤️ AI TRIAGE" hat guy casually rejecting sophisticated exploits as duplicates while handing out P1 Critical ratings to basic reflected XSS like it's candy. Meanwhile, the actual security researcher who found SSRF, RCE, and probably three zero-days gets an "informative only" tag and a pat on the back. Welcome to modern bug bounties: where the payouts are made up and your multi-stage exploit doesn't matter.

State Of Things

State Of Things
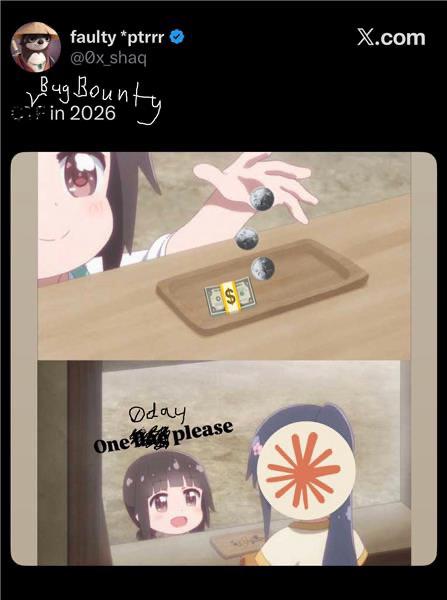
Bug bounty programs in 2026 are apparently going to be less "here's $50k for finding a critical vulnerability" and more "here's a dollar, now stop bothering us." The progression from confidently dropping those shiny metal balls (bugs) expecting a decent payout to literally begging for scraps with "one dollar please" is painfully accurate. Companies have mastered the art of devaluing security researchers' work. You find a zero-day that could compromise millions of users? Best we can do is a thank you in the changelog and maybe enough money for a coffee. Not even a fancy coffee—we're talking gas station coffee here. The real kicker is how bug bounty platforms keep adding more restrictions, longer validation times, and lower payouts while companies act like they're doing YOU a favor by letting you find their security holes for free. Peak capitalism meets cybersecurity, and somehow we're all surprised when critical vulnerabilities get sold on the dark web instead.

The World's Most Traceable Threat Actor

The World's Most Traceable Threat Actor
Nothing says "I'm a master of cybersecurity" quite like confessing your villainous plans on a public forum with CCTV footage of your face in the background. This ethical hacker's manifesto has the strategic brilliance of using your real identity to announce you're about to commit felonies because *checks notes* bug bounties aren't lucrative enough. The irony is just chef's kiss – complaining about companies underpaying security experts while simultaneously demonstrating why they probably shouldn't pay you at all. Pro tip: If your "ethical" hacking career isn't working out, maybe don't pivot to crime on camera? Just a thought.

The Ethical Hacker's Retirement Plan

The Ethical Hacker's Retirement Plan
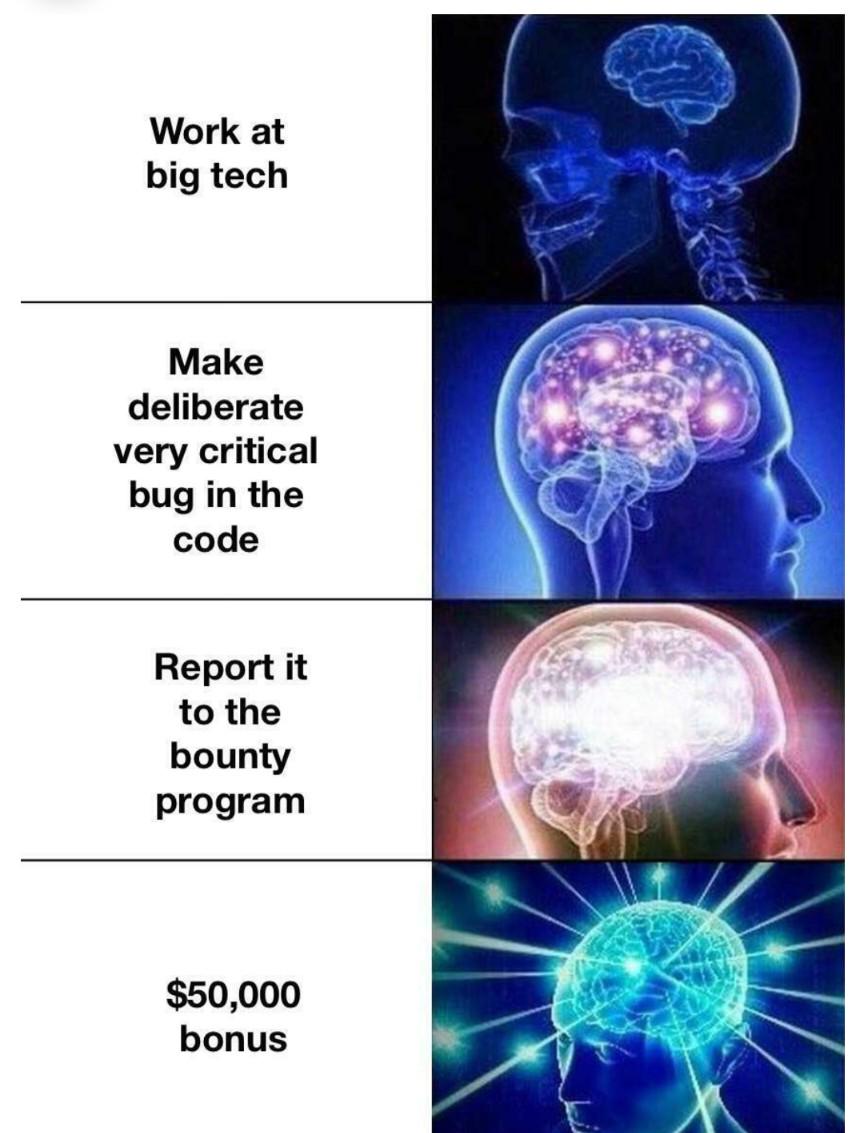
The corporate ladder? Pfft. The real career hack is introducing catastrophic bugs and then heroically "discovering" them through the bounty program. Why slave away for years climbing the ranks when you can just create the problem you're paid to solve? It's like arson for firefighters, but with better stock options. The ultimate insider trading that somehow passes legal scrutiny. Just don't get caught or you'll be enjoying a different kind of "remote work" - the kind with prison WiFi.