AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
Oh honey, buckle up because this is a MASTERCLASS in how to absolutely obliterate security for twenty years straight. Someone really looked at password reset codes and thought "you know what? Let's just use the current time and a random number under 10,000, hash it, and call it a day!" The predictability here is *chef's kiss* catastrophic. Since microtime() gives you the current timestamp and they're only adding a teeny tiny random number, an attacker could literally just... try a bunch of combinations around the current time. And then they're only taking 6 characters from the MD5 hash? That's like locking Fort Knox with a diary lock from Claire's. The fact that this code was PUBLICLY VISIBLE on GitHub for a DECADE while millions of users trusted their accounts to this digital wet paper bag of security is the kind of corporate negligence that should come with a free therapy session for every affected user. Someone's LinkedIn is about to get a lot quieter.
A Website With Millions Of Users Was Generating Their "Secret" Password Reset Codes Like This For Two Decades
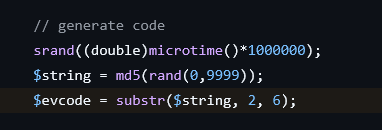
security-memes, password-reset-memes, bad-code-memes, security-fail-memes, md5-memes | ProgrammerHumor.io
More Like This