Bad practices Memes

Posts tagged with Bad practices
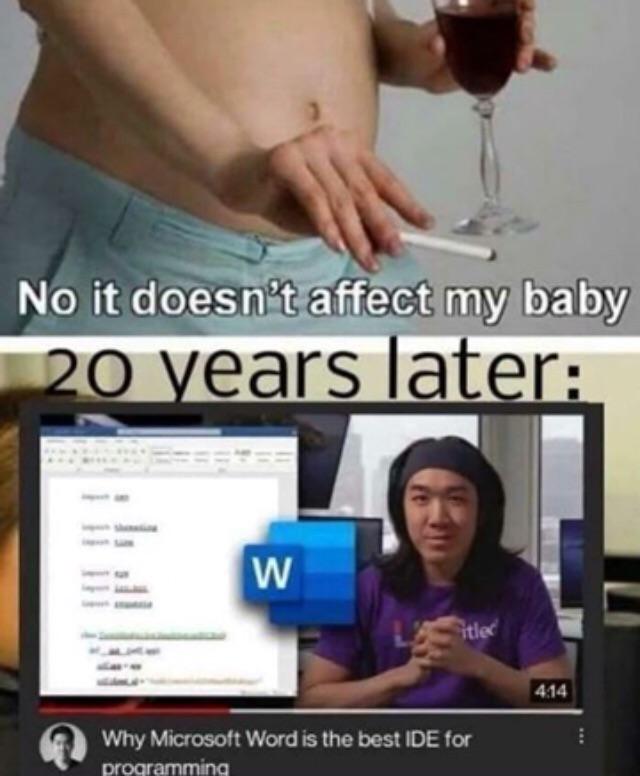
This Won't Affect My Baby

This Won't Affect My Baby
The sins of the parents manifest in mysterious ways. When your mom was drinking wine and smoking during pregnancy while insisting it's fine, you end up 20 years later genuinely believing Microsoft Word is a legitimate IDE for programming. Look, we've all seen cursed setups, but using Word as your development environment is a special kind of chaos. The kid's got syntax highlighting working somehow (probably through sheer determination and pain), import statements that Word's autocorrect is definitely trying to "fix" into proper English, and a workflow that makes Notepad look like a professional choice. The real tragedy? He looks so content. So at peace with his decisions. That's the developmental damage right there.

Magic Quotes

Magic Quotes
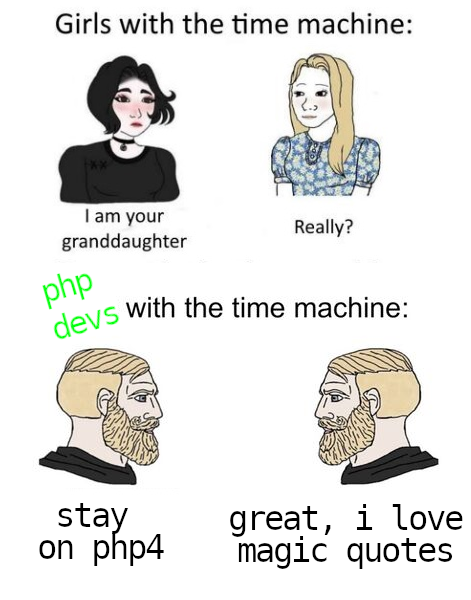
For those blessed enough to have never encountered it: Magic Quotes was PHP's "security feature" that automatically escaped quotes in user input. Sounds helpful, right? Wrong. It created more problems than it solved, mangled data, and made SQL injection vulnerabilities *worse* in many cases because devs thought they were protected when they weren't. The joke here is that if PHP devs could go back in time, they wouldn't warn themselves about future mistakes or suggest better practices. Nope. They'd tell their past selves to stay on PHP 4 and keep using Magic Quotes—arguably one of the worst decisions in PHP history. It's like saying "yeah, keep using that broken parachute, it's great!" The feature was so universally hated that it was deprecated in PHP 5.3 and completely removed in PHP 5.4. But here we are, romanticizing the bad old days like some kind of Stockholm syndrome survivors.

The Original Source Of Top Secure Number

The Original Source Of Top Secure Number
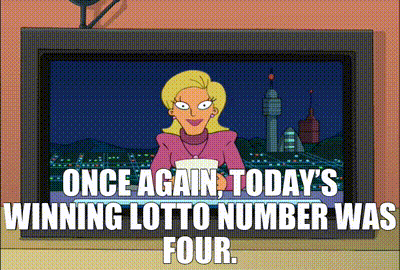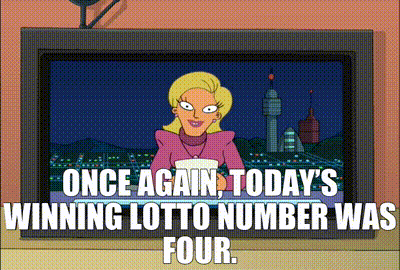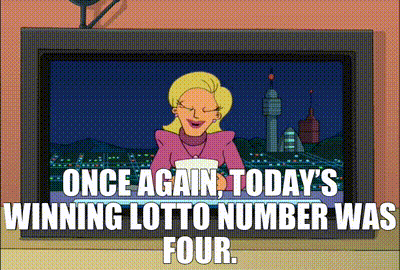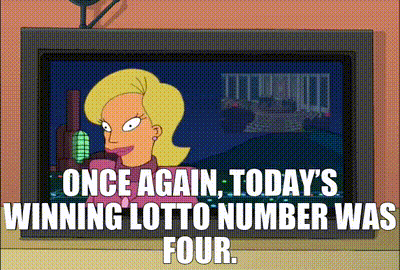
Ah yes, the legendary number "4" - chosen by fair dice roll, guaranteed to be random. Developers everywhere are still using this battle-tested random number generation technique for their cryptographic keys, session tokens, and password salts. Why bother with complex RNG algorithms when you can just hardcode the winning lotto number? Security through obscurity at its finest. The fact that this number keeps winning the lottery just proves how truly random it is, right? Fun fact: This is actually a reference to the classic XKCD comic where someone generates a random number by rolling a dice and getting 4. The joke being that hardcoding a "random" value defeats the entire purpose of randomness - yet we've all seen production code with const RANDOM_NUMBER = 4; somewhere in the codebase.

Top Secret Api Key

Top Secret Api Key
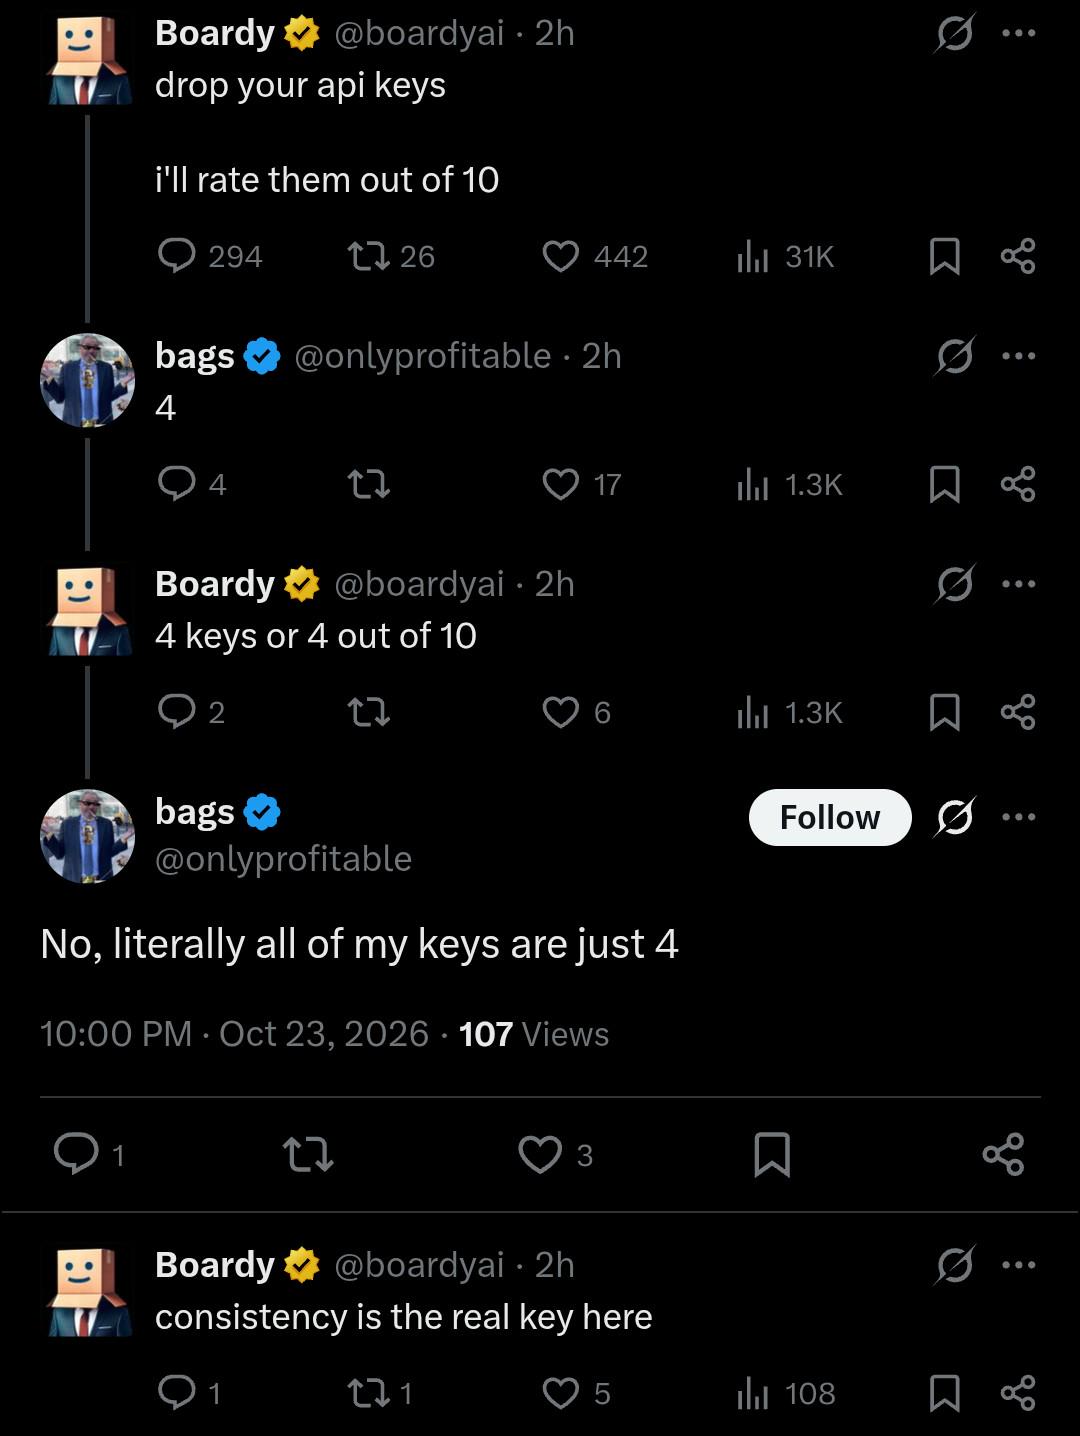
Someone asks you to rate their API keys out of 10, and naturally you give them a solid 4. But wait—do they mean "4 out of 10" or literally "the number 4 is all my keys"? Plot twist: they mean both. Because apparently this developer has achieved peak security through obscurity by making every single API key just the character "4". No rotation strategy needed when you never had variety in the first place. The real kicker? "Consistency is the real key here." Yeah, consistently terrible security practices. At least if someone leaks it, nobody will believe it's real.

Amazon Basics Gas Spring Single Monitor Arm Desk Mount, Adjustable Tension, Fits 15–27 Inch Monitors, Supports 4.4–15.4 lbs, VESA 75x75/100x100, Black

Amazon Basics Gas Spring Single Monitor Arm Desk Mount, Adjustable Tension, Fits 15–27 Inch Monitors, Supports 4.4–15.4 lbs, VESA 75x75/100x100, Black
Adjustable Gas Spring Tension for Stable Positioning: Designed to support monitors from 4.4–15.4 lbs. Proper tension adjustment is required based on monitor weight to ensure stable positioning and pr…

E Mudhra Employee Of The Month

E Mudhra Employee Of The Month
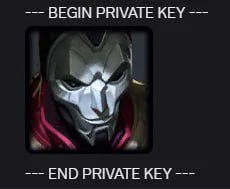
When you literally put your private key between "BEGIN PRIVATE KEY" and "END PRIVATE KEY" markers and commit it to a public repo, you've basically handed the villain their mask. E Mudhra (an Indian digital signature provider) had someone do exactly this—exposing cryptographic private keys that should've been guarded like nuclear launch codes. The image of the masked villain perfectly captures the energy of whoever got their hands on those keys. They didn't hack anything; they just read the manual that was accidentally left on the park bench. Pro tip: private keys belong in environment variables, secret managers, or literally anywhere except your codebase. Also, maybe don't win Employee of the Month for this one.

That's The Stupidest Combination I've Ever Heard In My Life!

That's The Stupidest Combination I've Ever Heard In My Life!
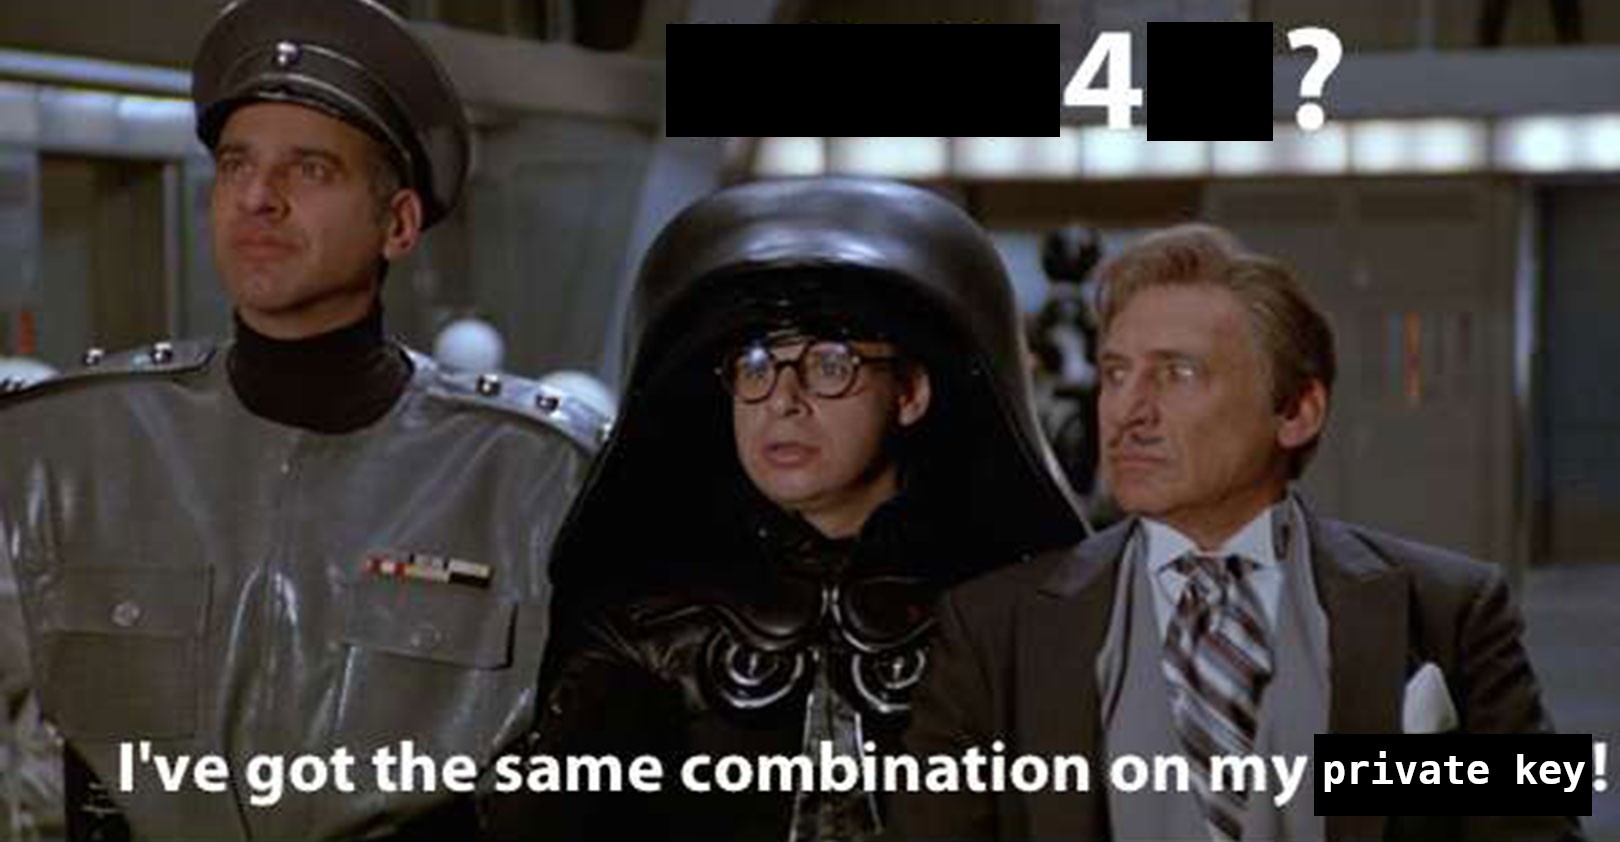
When your password is "1234" but you're storing your SSH private key with the same passphrase. Nothing screams "I understand security" quite like protecting your cryptographic credentials with the same combination an idiot would have on their luggage. The real kicker? Half the devs reading this just nervously glanced at their ~/.ssh/id_rsa file. And the other half? They don't even use a passphrase. At least President Skroob here had the decency to try . Pro tip: If your private key passphrase is something you'd use to unlock your phone, you might as well just commit it to the public repo and save everyone some time.

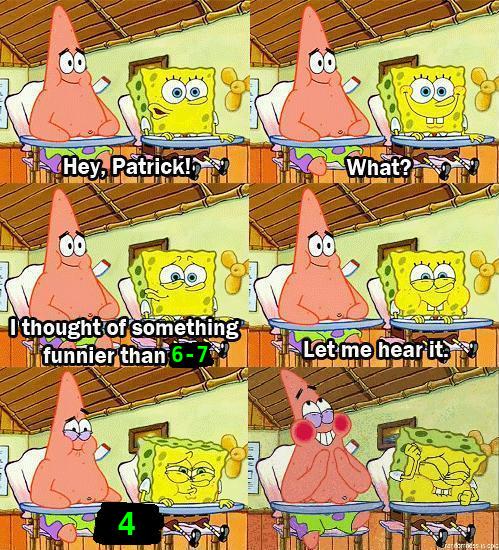
Four Is 6 7 For Infosec

Four Is 6 7 For Infosec
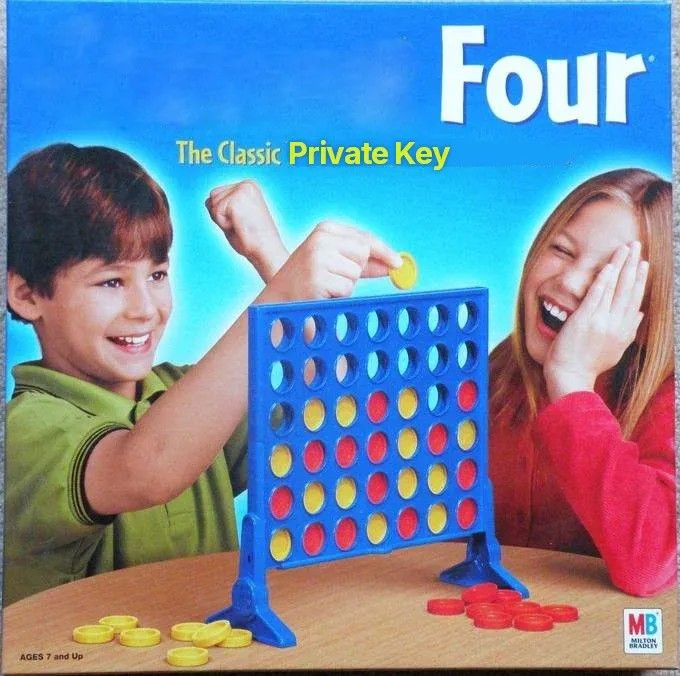
Security folks really looked at Connect Four and said "yeah, let's call it a private key and ship it." The game where your entire strategy is visible to everyone watching? Perfect metaphor for how we handle secrets in production. The kid's dropping that yellow chip with the same confidence as a dev hardcoding API keys into a public GitHub repo. And just like in the game, everyone can see exactly what you're doing, where you're going, and how to beat you. Except instead of losing a board game, you're losing your entire customer database to some script kiddie in Belarus. Private keys should be, you know, private . But here we are, treating them like Connect Four pieces—colorful, visible, and apparently meant for children to play with.

Xkcd Said Its Random

Xkcd Said Its Random
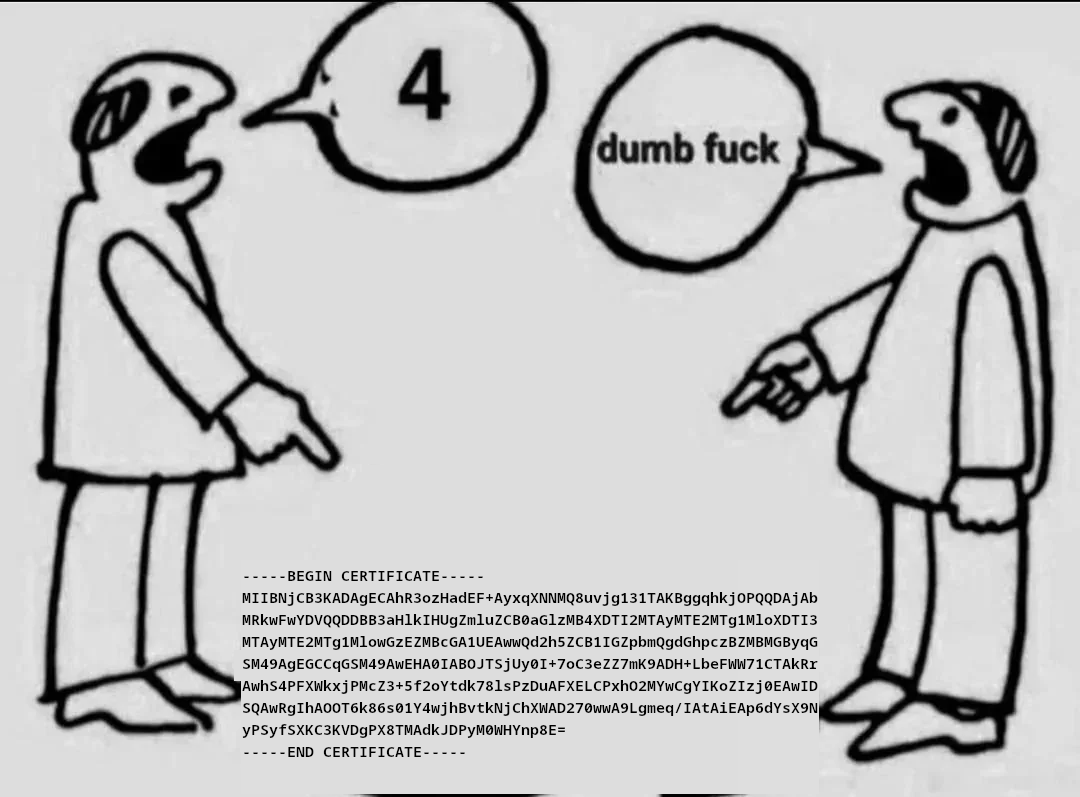
This references the legendary xkcd comic where someone implements a random number generator by just returning 4 because "I rolled a dice and got 4, so it's random." Fast forward to reality, and here's some poor soul actually using that logic to generate SSL certificates. The other person's response? "dumb fuck" - which is honestly the most restrained reaction possible when someone hardcodes entropy into cryptographic material. The beauty here is that certificates need actual randomness for security. Using the same "random" seed means every certificate would be identical, making your entire PKI infrastructure about as secure as a screen door on a submarine. But hey, xkcd said it was random, so ship it to production.

Chosen By A Fair Dice Roll

Chosen By A Fair Dice Roll
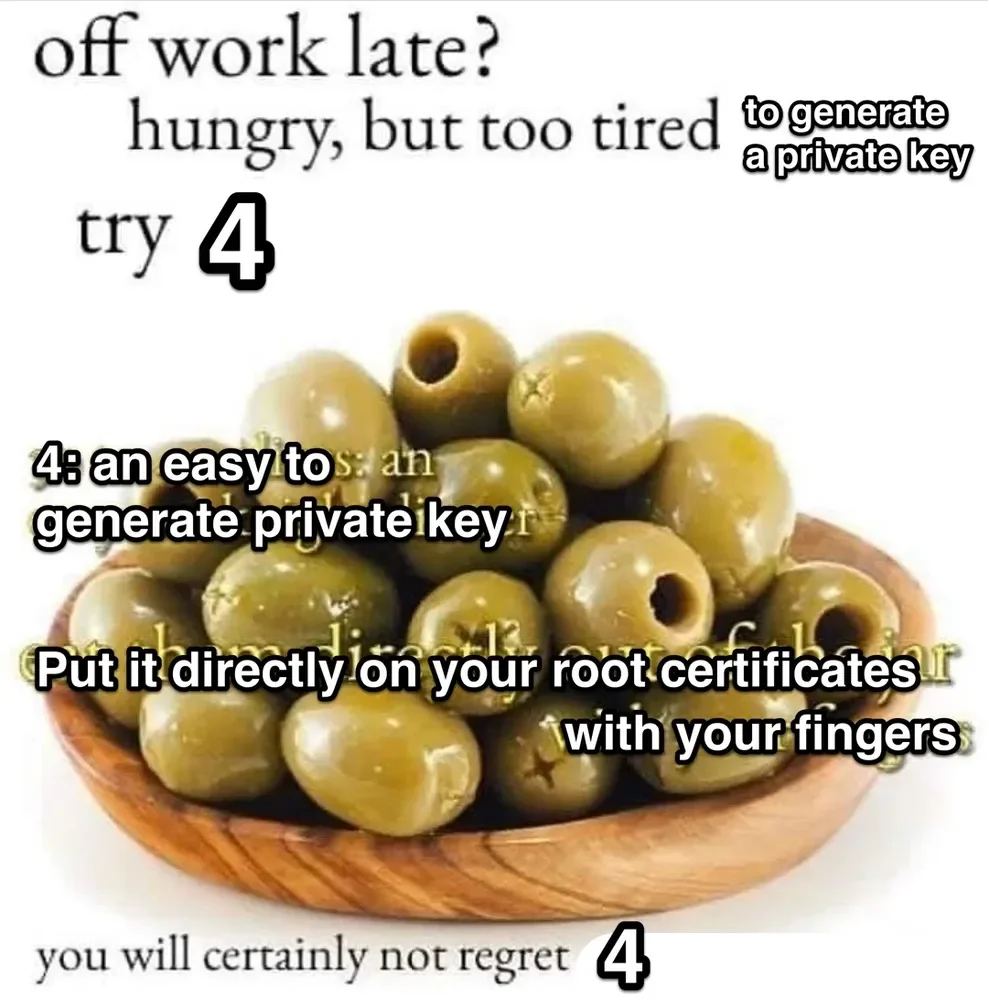
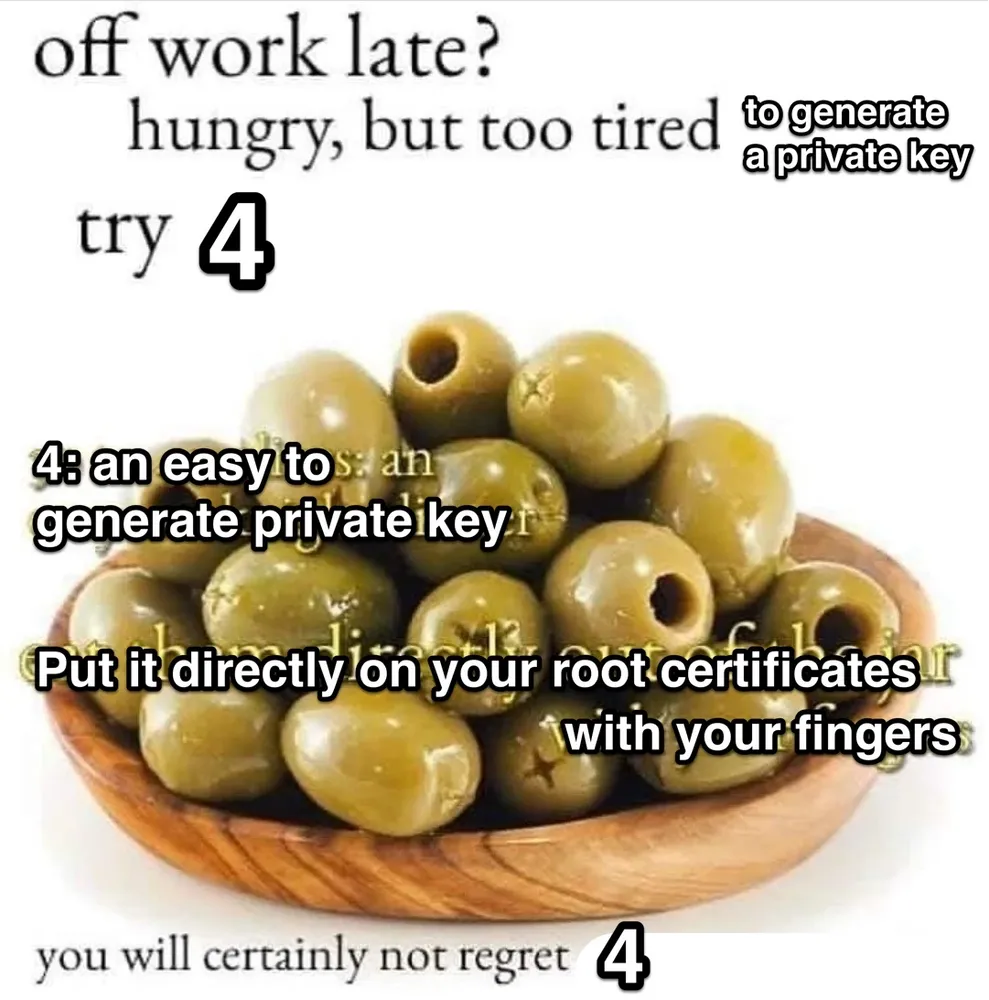
When you're so exhausted that rolling a dice to make decisions seems like peak productivity, and naturally you land on the WORST possible option for your cybersecurity. Nothing says "I've given up on life" quite like using a random number generator (your brain is too tired for that) to decide how to handle your cryptographic keys, and then proceeding to manually copy-paste your private key into your root certificates directory like you're spreading butter on toast. Because who needs security best practices when you've got VIBES and HUNGER? The beautiful irony? The number 4 supposedly being "an easy to generate private key" when generating secure keys requires actual randomness and complexity, not just... the number four. And then storing it by literally touching your root certs with your greasy fingers? Chef's kiss of catastrophic security failures. You will certainly not regret this until your entire infrastructure gets compromised at 3 AM and you're even MORE tired.

E Mudhra Certificate Authority Chose Random Numbers By Fair Dice Roll Guaranteed To Be Random

E Mudhra Certificate Authority Chose Random Numbers By Fair Dice Roll Guaranteed To Be Random
So apparently E Mudhra, a Certificate Authority that's supposed to be securing digital certificates and cryptographic operations, decided that "random number generation" means rolling a dice and getting... 4. Every. Single. Time. For those who need context: this is referencing the classic XKCD comic where someone hardcodes the number 4 as their "random" number because they rolled a dice once. The joke here is that a CA—literally an organization whose entire job depends on cryptographic security and proper randomness—might as well be using the same logic. Nothing screams "enterprise security" quite like deterministic randomness. I'm sure their SSL certificates are totally secure when the random number generator has the same entropy as a fortune cookie. But hey, at least it's guaranteed to be random, right? They rolled a dice! Once! In 2003! This is what happens when someone reads "cryptographically secure random number generator" and thinks "yeah, but have we tried just... picking a number?"

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

It's Quick It's Easy And It's Free

It's Quick It's Easy And It's Free
When you're too exhausted to properly generate SSH keys or deal with certificate authorities, just mash that keyboard and manually type your private key directly into your root certificates. What could possibly go wrong? The "4" here is doing some heavy lifting as both a number and the most cursed security advice imaginable. It's like those life hack videos that tell you to fix a cracked phone screen with ramen noodles, except this one will get your entire infrastructure compromised before you finish your sad desk dinner. Nothing screams "I understand cryptography" quite like finger-painting your private keys onto production certificates. Your security team will definitely not regret this. Neither will the hackers who are already in your system.

Air Gapped Secrets Management

Air Gapped Secrets Management
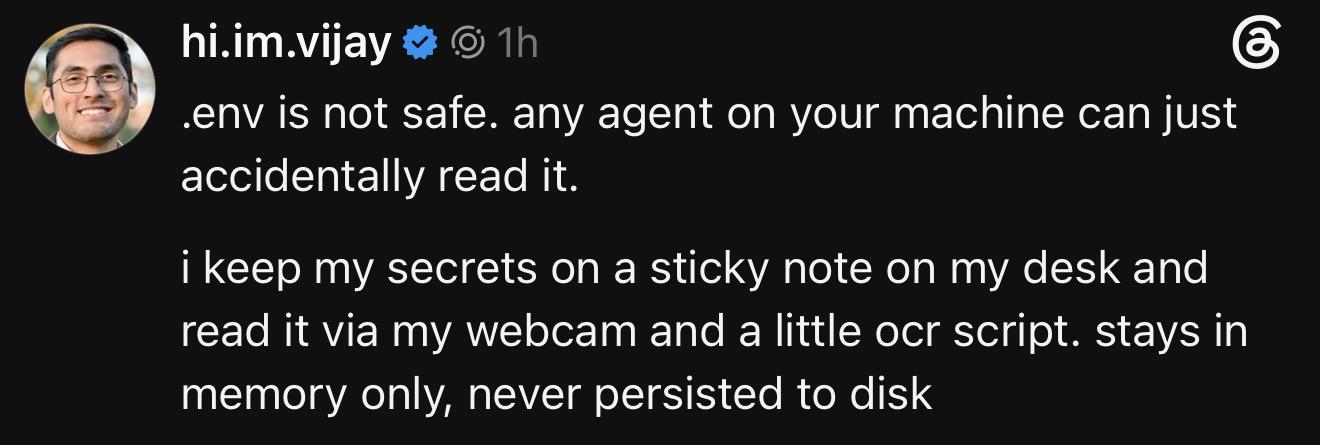
Someone just solved the entire secrets management industry with a sticky note, a webcam, and OCR. While everyone's busy setting up HashiCorp Vault clusters and AWS Secrets Manager with rotation policies, this genius is literally reading passwords off their desk through a camera feed and keeping them in RAM only. Zero persistence, maximum jank. The "air gap" here is the physical space between the sticky note and the computer. Technically more secure than committing your .env to GitHub, which is the bar we're working with these days. The OCR script probably fails half the time because of handwriting recognition, but hey, that's just built-in rate limiting. Fun fact: This is unironically more secure than what half of production environments are running. At least there's no plaintext in the git history.