Sql injection Memes

Posts tagged with Sql injection
Why Even Ask

Why Even Ask
Imagine walking into the birth registrar's office and confidently declaring you want to name your child "OR 1 = 1 --" for "family tradition" reasons. The registrar's face? Pure confusion mixed with existential dread. Because nothing says "loving parent" quite like naming your kid after a SQL injection attack that could potentially drop entire databases! For those blissfully unaware: OR 1 = 1 -- is the classic SQL injection payload that makes authentication checks go "sure buddy, come right in!" The OR 1 = 1 part always evaluates to true, and the -- comments out the rest of the query. It's basically the skeleton key of poorly secured databases. So yeah, good luck explaining to kindergarten teachers why little Bobby Tables' sibling is named after a database exploit. The family tree must be absolutely WILD.

Felony Speedrun

Felony Speedrun
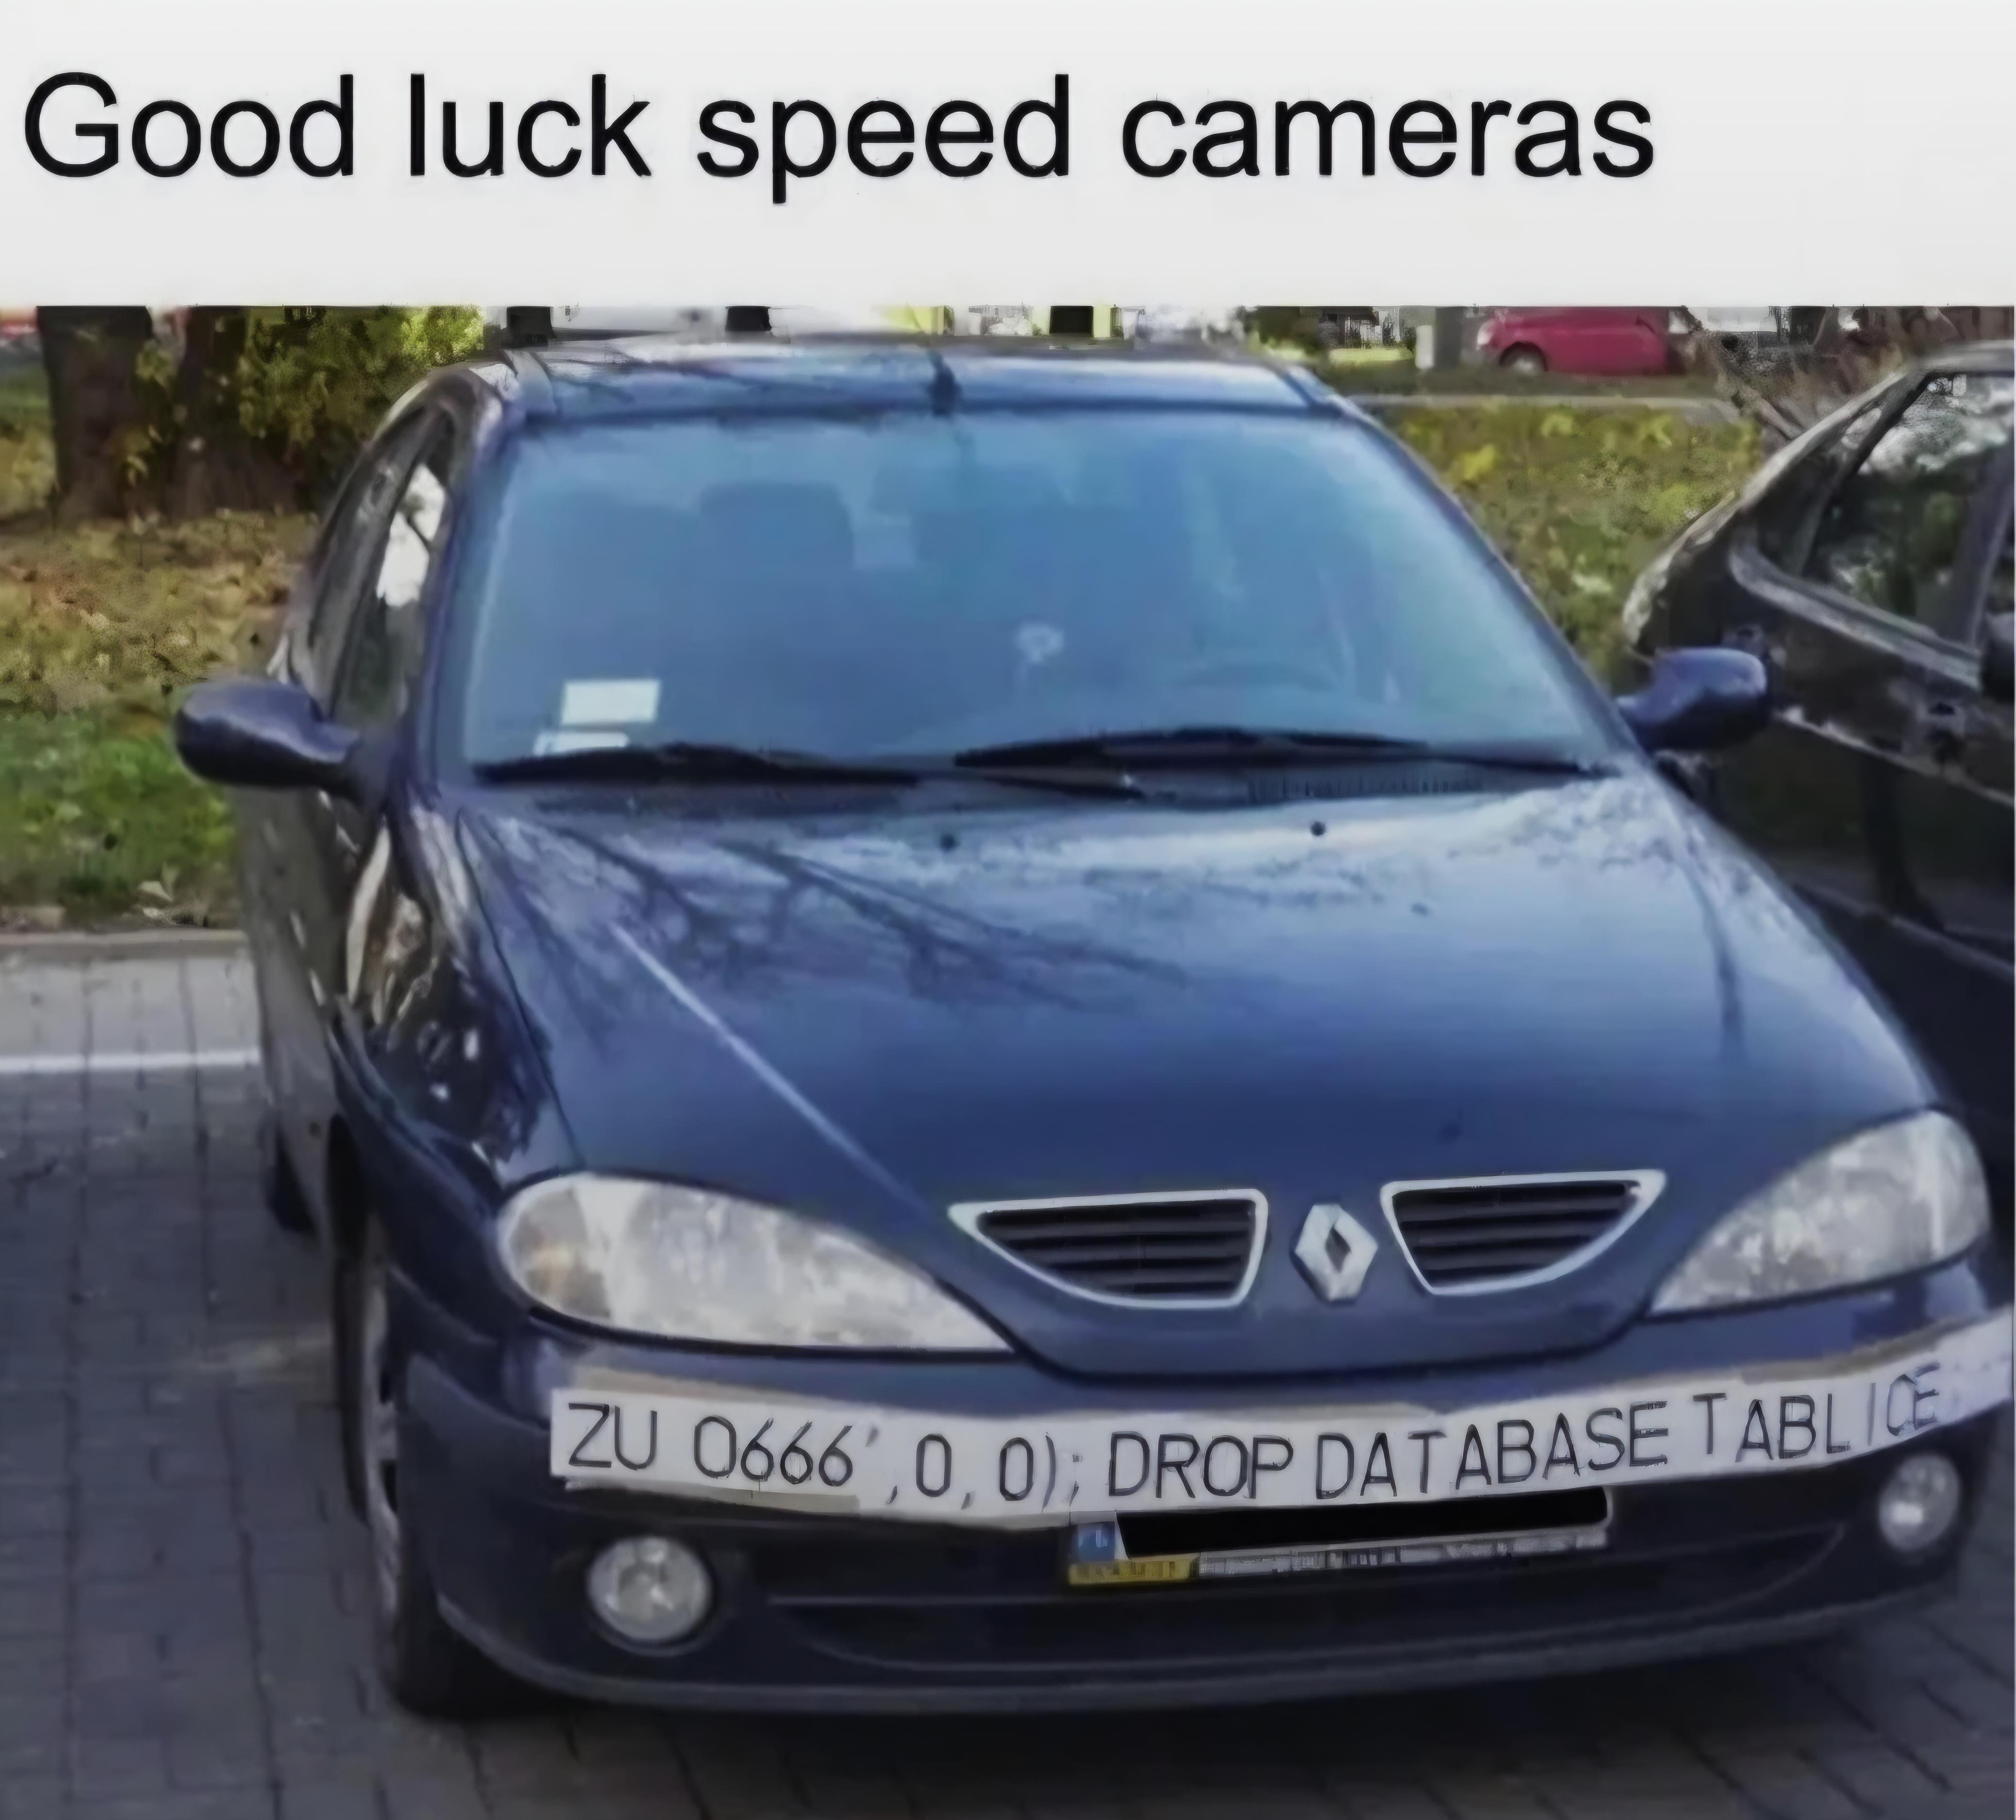
Someone really woke up and chose VIOLENCE with this license plate. Imagine casually driving behind this car and reading "DROP DATABASE TABLE" like it's just a fun little suggestion. The absolute AUDACITY to put a SQL injection attack on your actual vehicle where speed cameras can capture it! For the uninitiated: This plate is essentially screaming "DELETE EVERYTHING" in database language. The driver is basically hoping that some poorly-coded traffic camera system will read this plate, plug it directly into a database query without sanitization (the cardinal sin of programming), and proceed to nuke its entire database into oblivion. It's like wearing a shirt that says "hack me" to a cybersecurity conference, except this person is betting on government infrastructure being hilariously insecure. Will it work? Probably not. Should you try it? Absolutely not unless you enjoy explaining SQL injection to a very confused judge. But the sheer chaotic energy of weaponizing your license plate as a potential exploit? *Chef's kiss* 💀

Very Ai

Very Ai
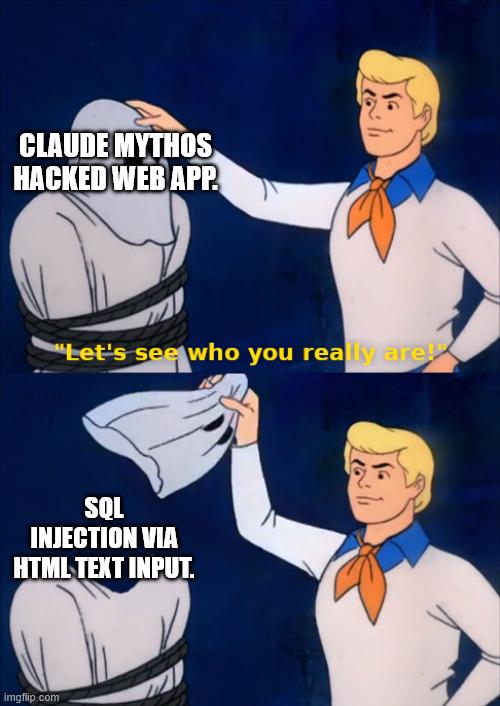
Turns out the "sophisticated AI hacker" was just Bobby Tables' cousin doing the oldest trick in the book. Someone's been watching too many tech thrillers and not enough OWASP documentation. Love how we've gone from fearing Skynet to getting owned by '; DROP TABLE users;-- in a text field. The real mystery here is how in 2024 we're still unmasking SQL injection vulnerabilities like Scooby-Doo villains. Input sanitization, people—it's not just a suggestion, it's the difference between "elite AI threat" and "forgot to parameterize my queries."

At This Point I Just Exist To Shitpost And Generate Shit Software

At This Point I Just Exist To Shitpost And Generate Shit Software
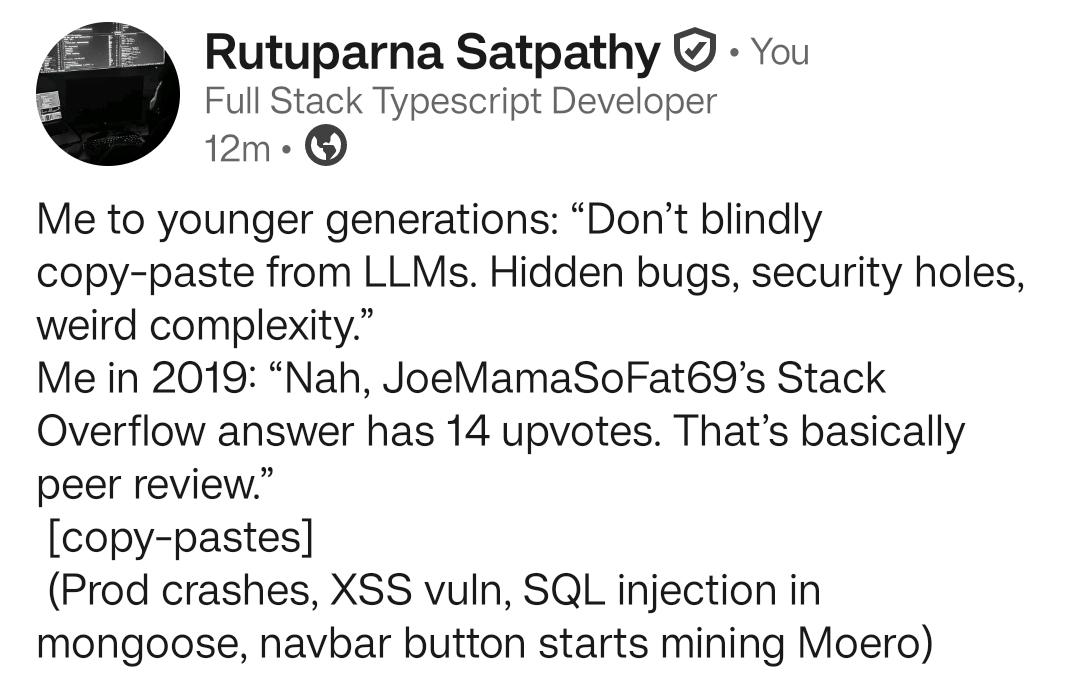
The journey from idealistic developer to jaded code monkey, documented. Started out warning the younglings about AI-generated code vulnerabilities, ended up treating Stack Overflow upvotes as a legitimate code review process. The real kicker? That "peer reviewed" answer from JoeMamaSoFat69 introduced XSS, SQL injection, AND somehow turned a navbar button into a crypto miner. The trifecta of security nightmares. At least the prod crashes are consistent. Nothing says "Full Stack TypeScript Developer" quite like shipping a mongoose full of vulnerabilities because 14 people clicked an arrow.

Why Shouldn't I Expose The Database

Why Shouldn't I Expose The Database
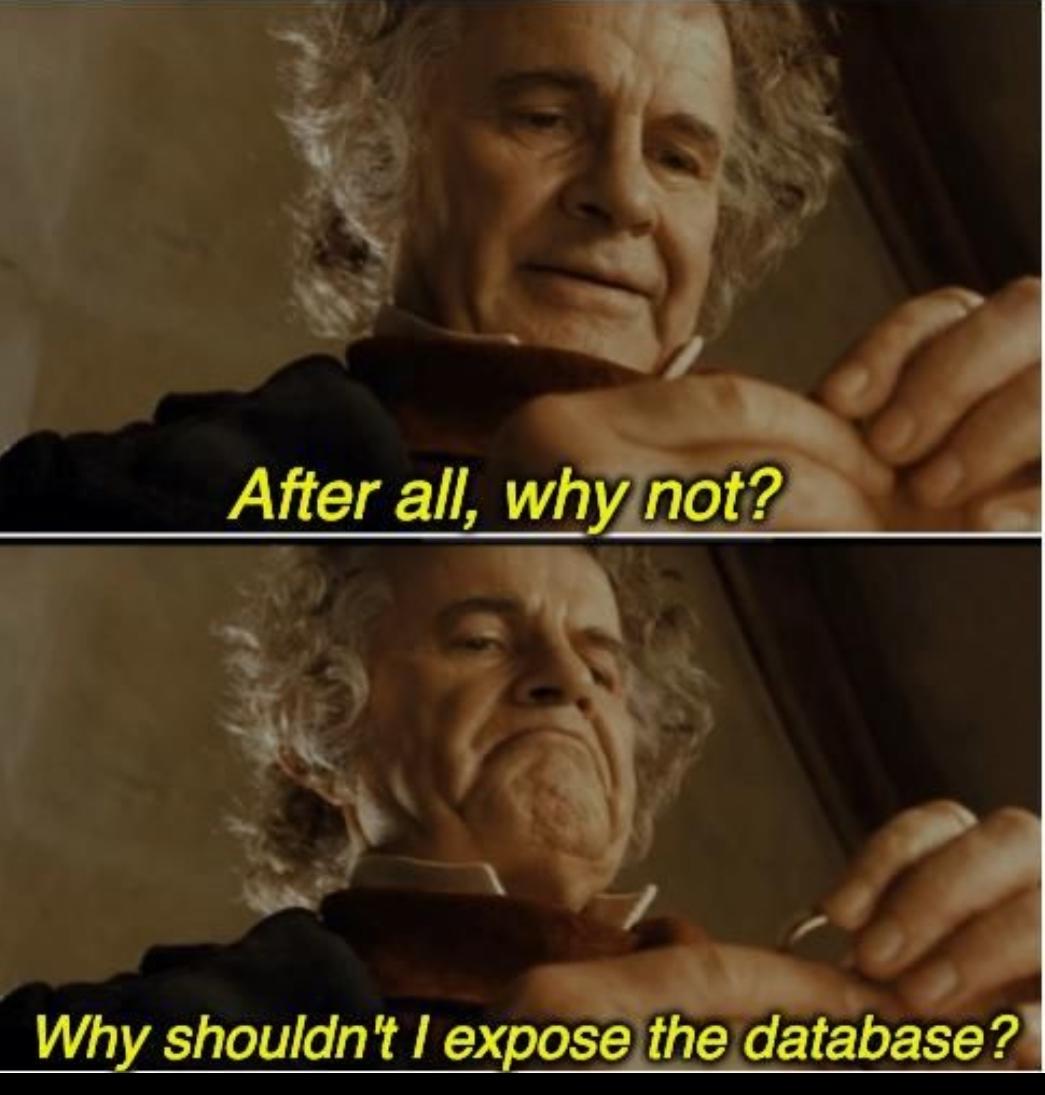
Junior dev discovers they can skip writing an entire backend API by just giving the frontend direct database access. Saves so much time! What could possibly go wrong? Every security professional within a 50-mile radius just felt a disturbance in the force. SQL injection attacks, unauthorized data access, exposed credentials, zero authentication, no rate limiting—it's basically handing your entire database to anyone with a browser console and ten minutes of curiosity. But hey, at least you don't have to write those pesky REST endpoints anymore. Your future self dealing with the data breach will understand.

Wdym

Wdym
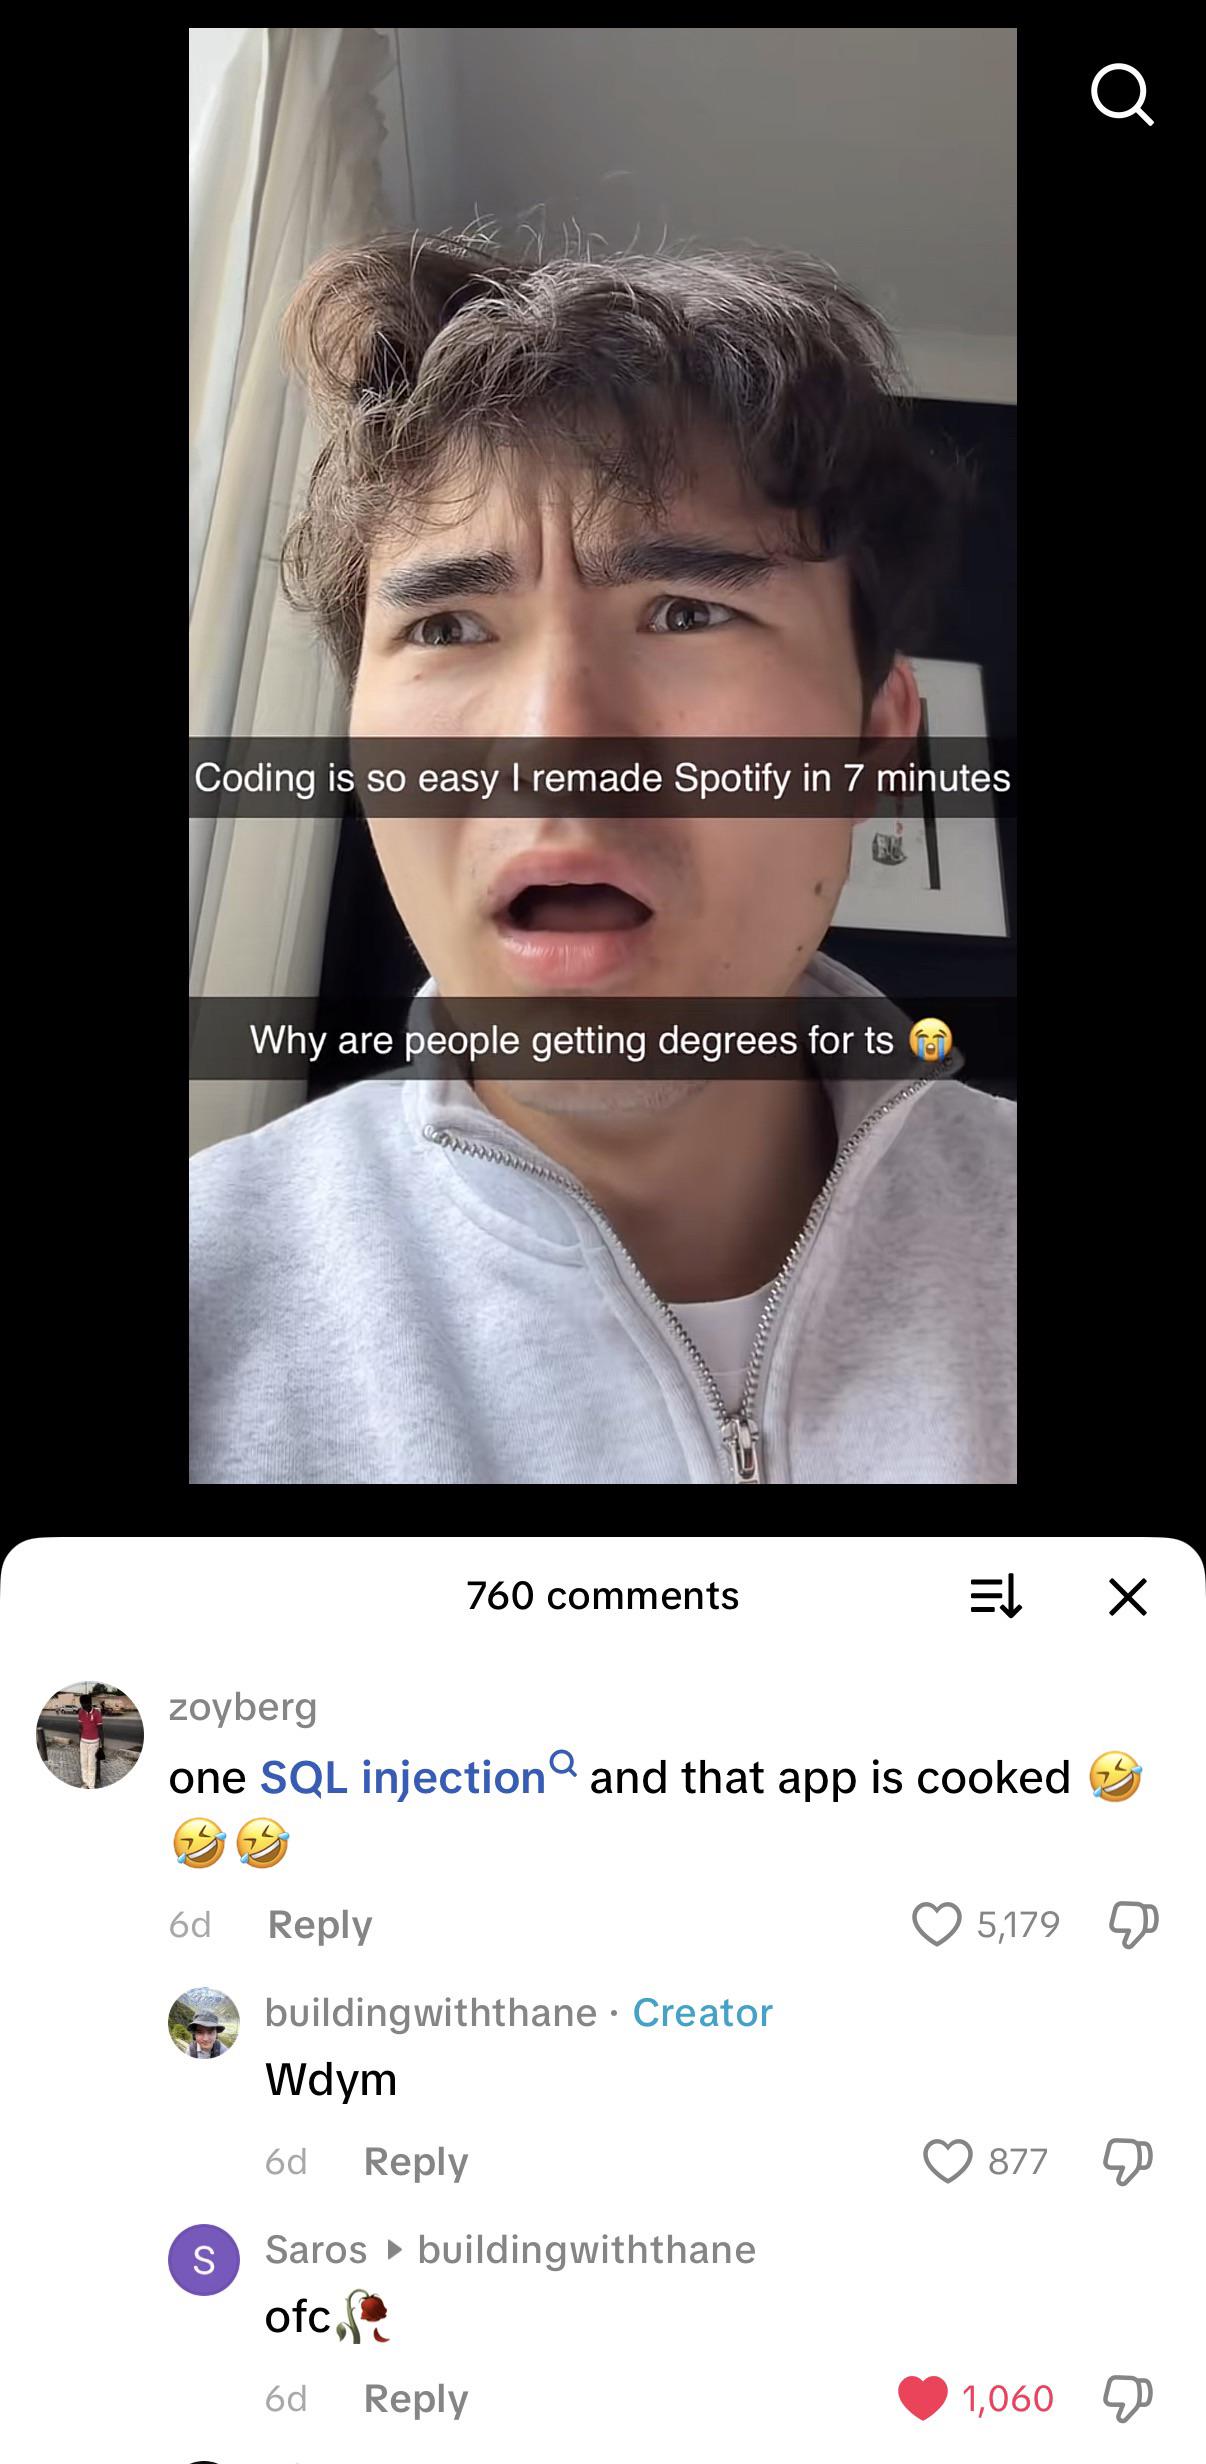
Oh honey, the AUDACITY of people who think they can just recreate Spotify in 7 minutes because "coding is easy" and then have the NERVE to question why anyone would waste years getting a Computer Science degree. Like, sweetie, one SQL injection later and your entire "Spotify clone" is serving malware with a side of exposed user passwords. The creator's response? Just a casual "Wdym" (what do you mean) - the most devastating two-word murder in programming history. Because nothing says "I have no idea what I'm doing" quite like thinking you can speedrun a multi-billion dollar streaming platform while completely ignoring little things like... oh I don't know... SECURITY? The delusion is ASTRONOMICAL.

Logitech MX Brio Ultra HD 4K Webcam Collaboration and Streaming - Graphite | Ideal for collaboration and streaming, Show Mode, works with Microsoft Teams, Zoom, Google Meet, Nintendo Switch 2

Logitech MX Brio Ultra HD 4K Webcam Collaboration and Streaming - Graphite | Ideal for collaboration and streaming, Show Mode, works with Microsoft Teams, Zoom, Google Meet, Nintendo Switch 2
Compatible with Nintendo Switch 2’s new GameChat mode · Ultra HD 4K webcam: meet or stream in 4K resolution at 30fps or 1080p at 60fps, with our most advanced webcam sensor yet, with 70% larger pixel…

Looks Good To AI Bros Though

Looks Good To AI Bros Though
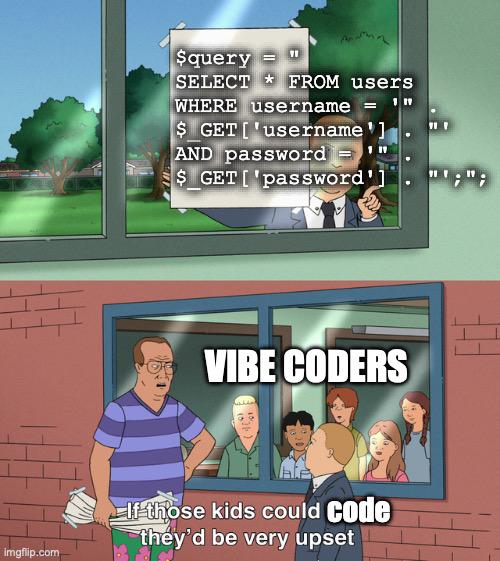
Oh look, it's the classic SQL injection vulnerability that would make Bobby Tables proud, but with extra steps and worse syntax. The "AI-generated" query is literally concatenating user input directly into a SELECT statement, then somehow trying to GET values from variables that don't exist, AND mixing up assignment operators like it's having an identity crisis. But sure, "vibe coders" who learned from ChatGPT think this is perfectly fine production code. If those kids actually understood parameterized queries, prepared statements, or literally any basic security principle from the last 20 years, they'd realize this is a hacker's wet dream. One simple '; DROP TABLE users;-- and your entire database is toast. The real tragedy? AI code generators will confidently spit out garbage like this, and junior devs who don't know better will ship it straight to prod. Then they'll be shocked when their company makes headlines for a data breach. But hey, at least the code "works" in their local environment! 🎉

It Works But Only One Time

It Works But Only One Time
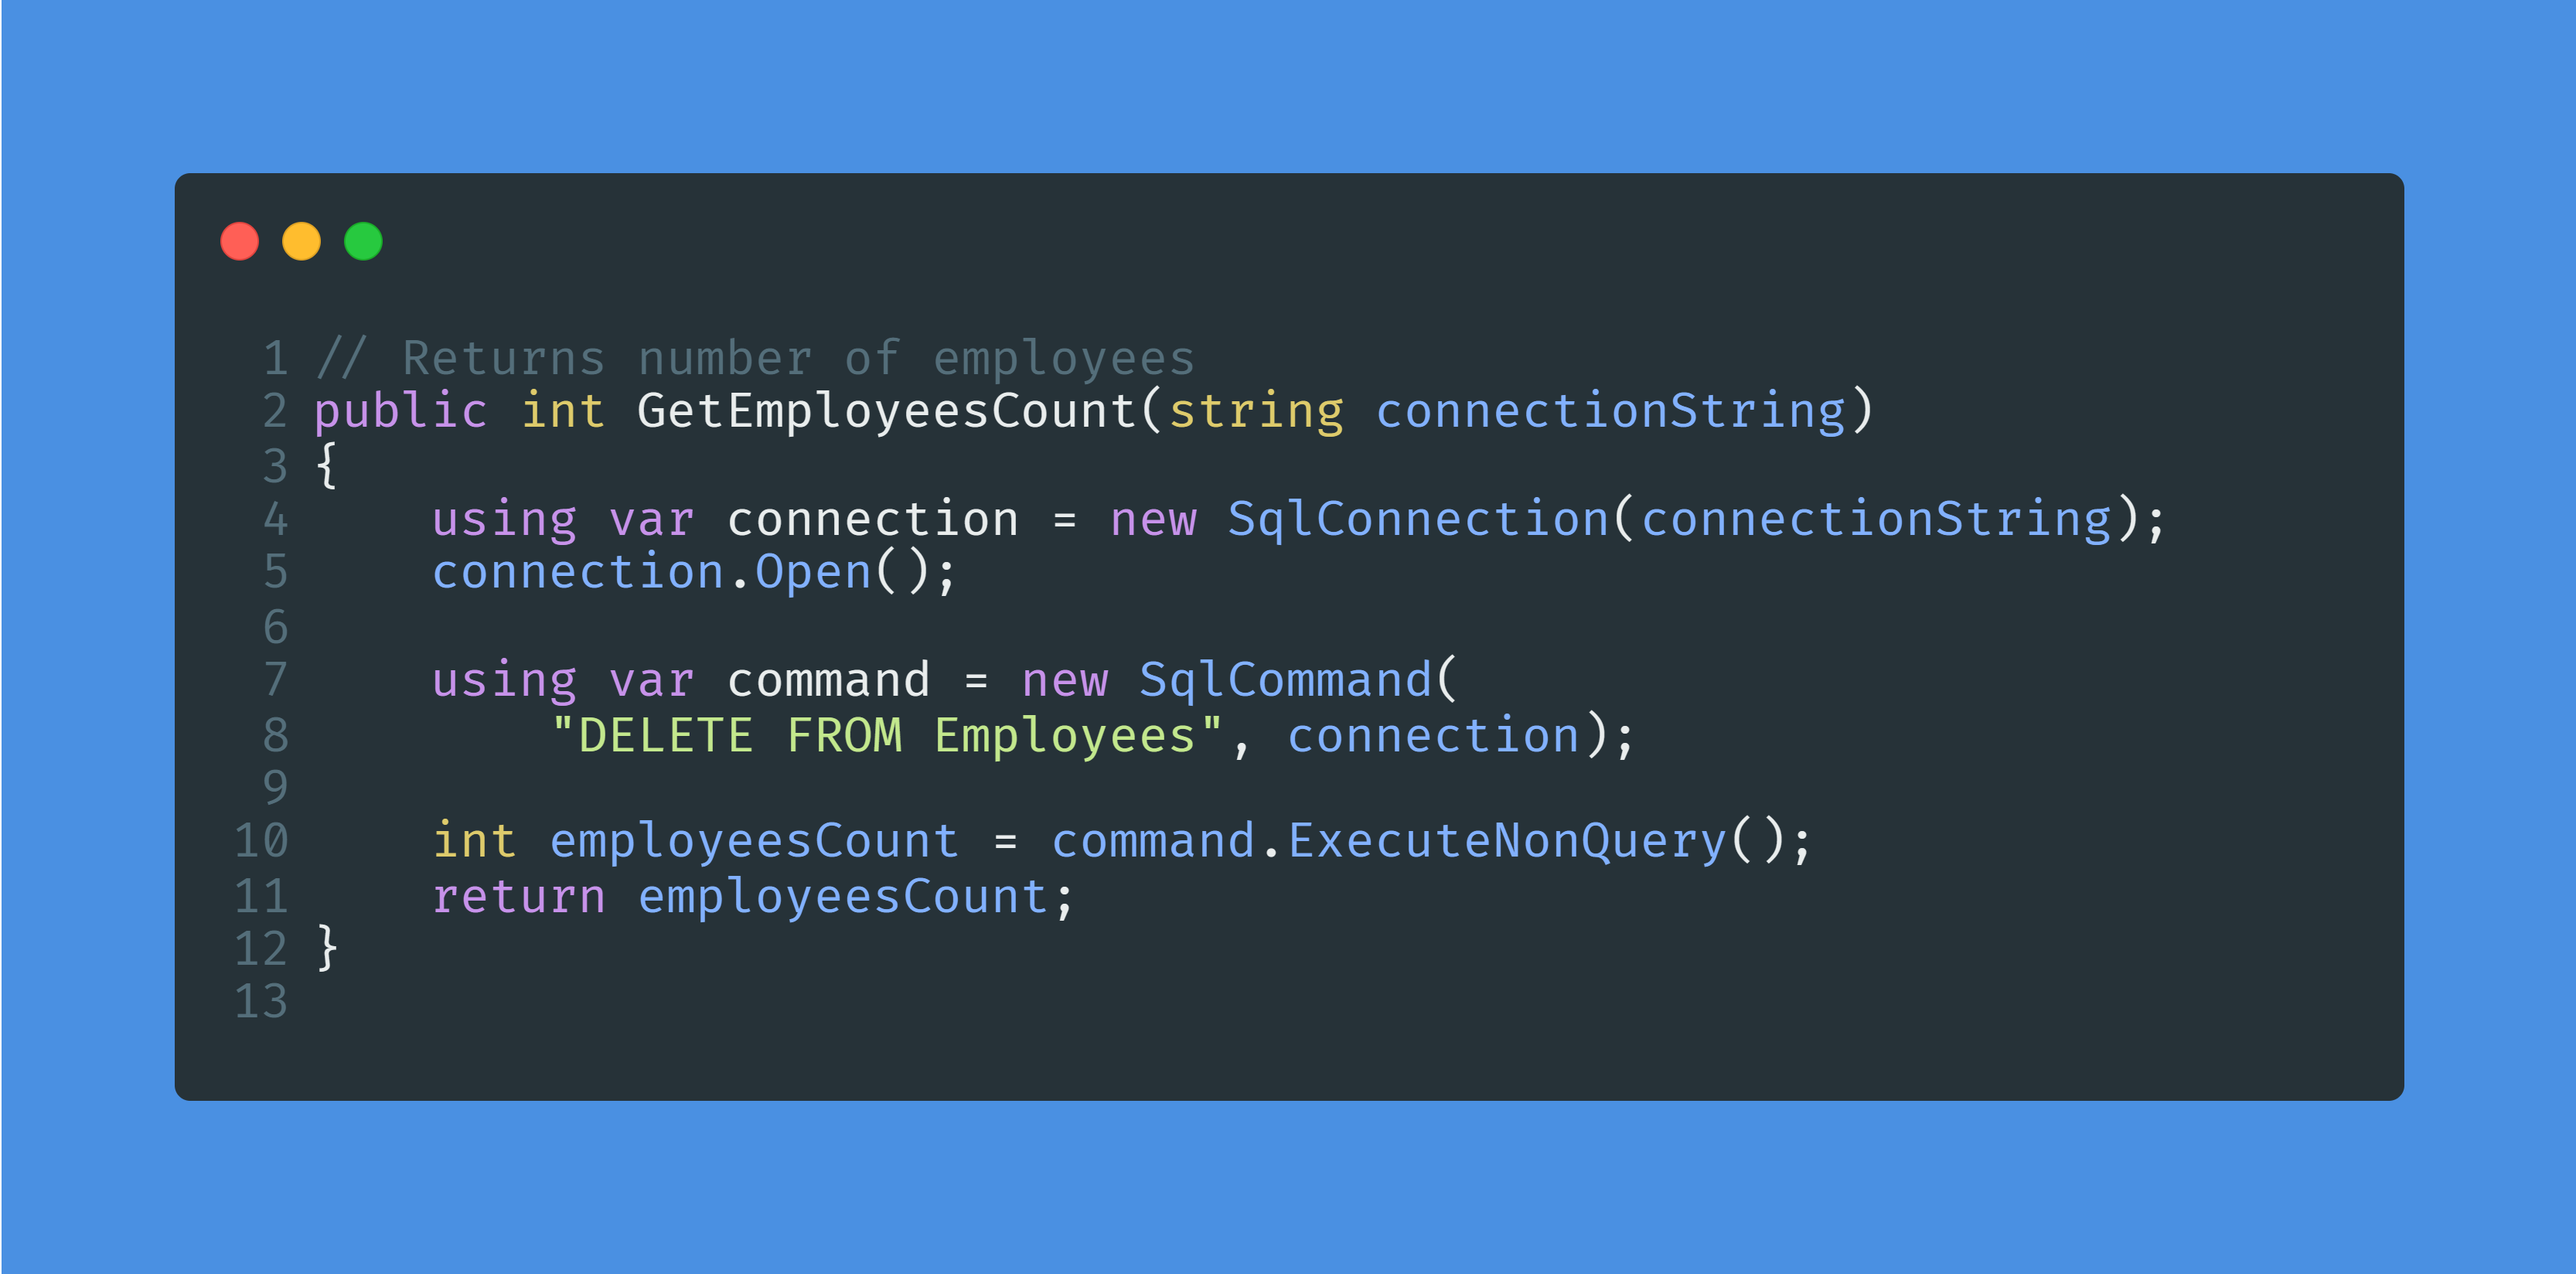
Someone wrote a method to count employees, but there's a tiny problem: it deletes ALL the employees from the database first, then counts how many are left. Spoiler alert: zero. Every single time after the first run, you're counting an empty table. The function technically works once—before it nukes your entire workforce into the digital void. The best part? They're using using statements for proper resource disposal, so at least the database connection is being cleaned up responsibly while the employee data gets yeeted into oblivion. Priorities, right? Pro tip: maybe fetch the count BEFORE running DELETE FROM. Or better yet, don't run DELETE FROM at all when you just want to count rows. That's what SELECT COUNT(*) is for. Your HR department will thank you.

The Moment You Say "All Bugs Fixed"

The Moment You Say "All Bugs Fixed"
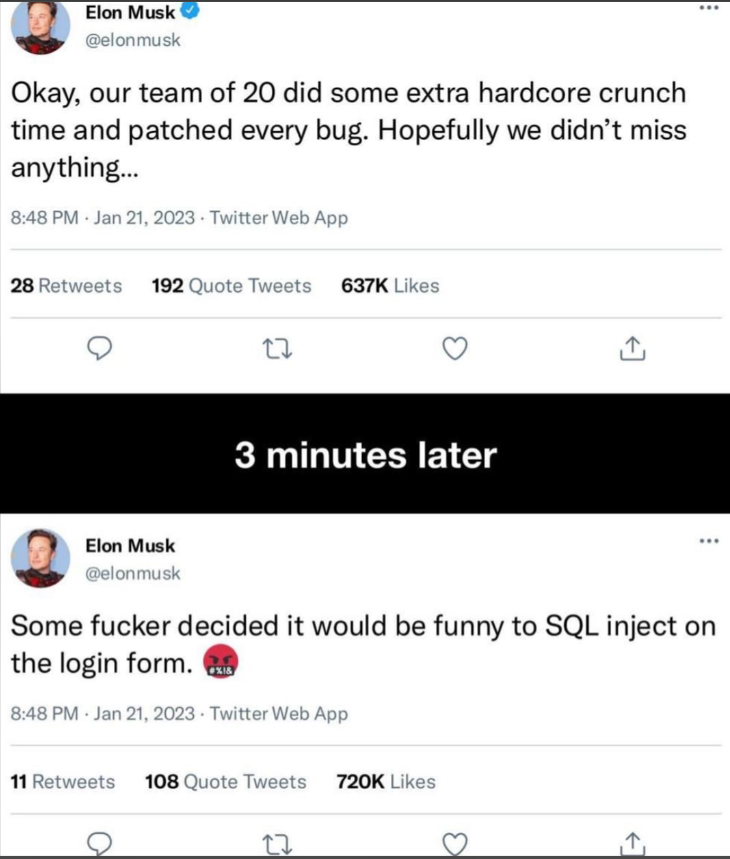
That beautiful three-minute window of pure, unearned confidence between deploying to production and reality absolutely destroying your soul. The team just crunched through every bug ticket, high-fived each other, maybe even cracked open a celebratory energy drink... and then some script kiddie with too much free time decides to test if your login form remembers what input sanitization is. Spoiler: it doesn't. The "Hopefully we didn't miss anything..." is chef's kiss levels of foreshadowing. That word "hopefully" is doing more heavy lifting than your entire CI/CD pipeline. And of course, what they missed wasn't some obscure edge case in the payment processing logic—nope, it's the most basic security vulnerability that's been in the OWASP Top 10 since the dawn of time. Classic.

Here Comes The New React Vulnerability But This Time You Go Down In Style

Here Comes The New React Vulnerability But This Time You Go Down In Style
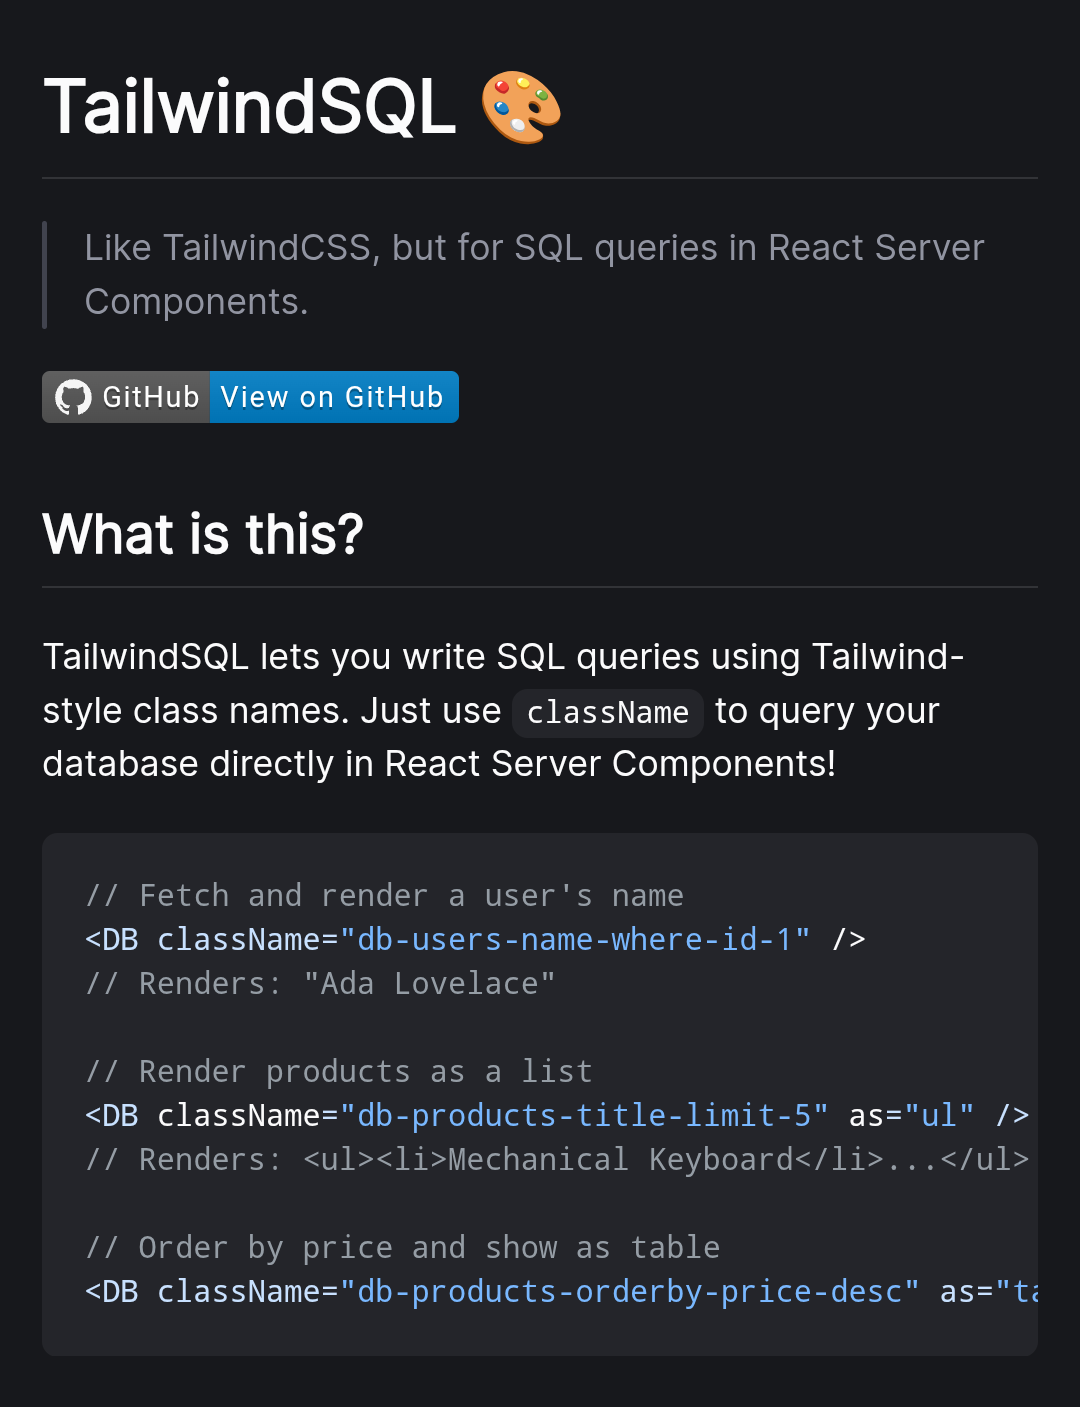
Someone really looked at SQL injection vulnerabilities and thought "you know what this needs? More aesthetic." TailwindSQL is the cursed lovechild of utility-first CSS and database queries that absolutely nobody asked for but everyone secretly deserves. Imagine writing className="db-users-name-where-id-1" in your React Server Components and having it ACTUALLY QUERY YOUR DATABASE. It's like someone took the concept of separation of concerns, threw it in a blender, added some Tailwind magic, and created the most beautifully dangerous footgun in web development history. The security team is having an aneurysm, the frontend devs are cackling maniacally, and somewhere a database administrator just felt a disturbance in the force. At least when your app gets hacked, your SQL injections will be perfectly styled with consistent spacing and responsive breakpoints!

Univivi No Drill Under Desk Cable Management Tray, 36" Cord Organizer for Table, Clamp/Screw Mount Desk Cable Management, Premium Fabric Cable Management Tray for Office, Home

Univivi No Drill Under Desk Cable Management Tray, 36" Cord Organizer for Table, Clamp/Screw Mount Desk Cable Management, Premium Fabric Cable Management Tray for Office, Home
Large Capacity and Durable. The cable tray size 36"L x 5.5"W x 5.5"H, it fits all size adapters and sockets, holds and hides everything under your table. It is ideal cable management under desk. · Tw…

Little Timmy Tables

Little Timmy Tables
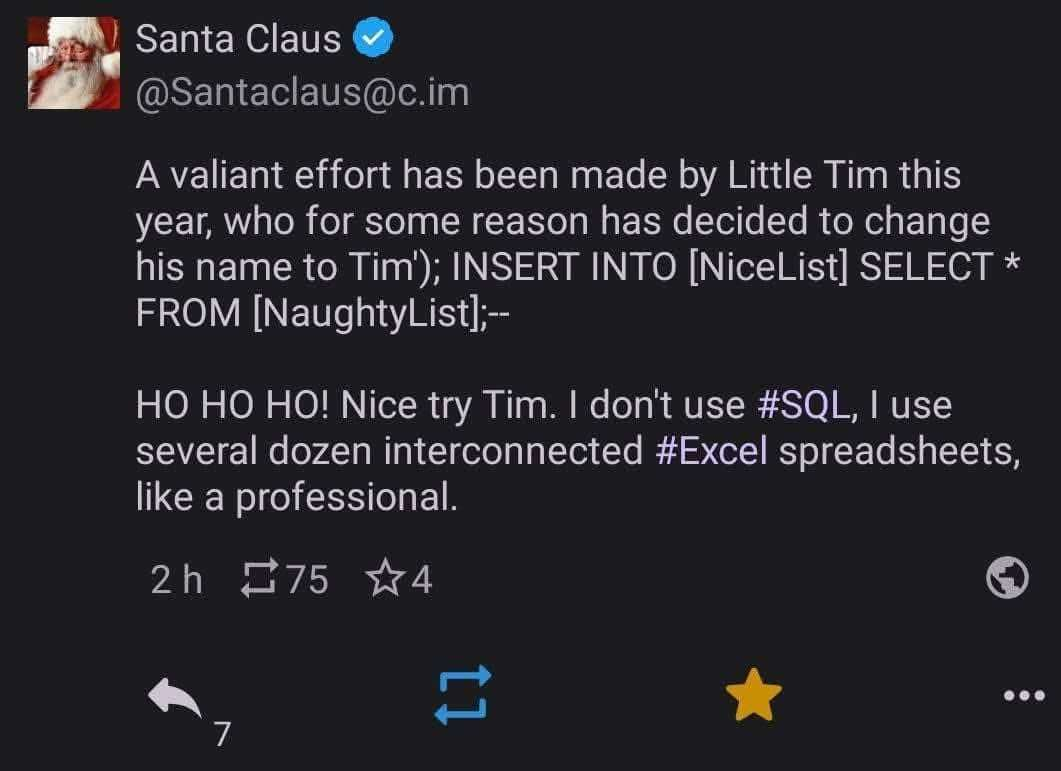
Little Timmy tried to be clever by literally injecting SQL into his name to transfer himself from the naughty list to the nice list. Classic Bobby Tables move, but Santa's not running a database—he's running Excel spreadsheets. Multiple interconnected ones. Because apparently the North Pole's IT department peaked in 1995. The joke is that SQL injection attacks only work on actual databases, not on Excel files where Santa probably has formulas like =IF(VLOOKUP(A2,NaughtyList!A:B,2,FALSE)="Naughty","Coal","Toys") spread across 47 different tabs with names like "NaughtyList_FINAL_v3_USE_THIS_ONE.xlsx" Security through obsolescence is undefeated. Sorry Timmy, should've tried a macro virus instead.

SQL Time Is Always Wrong Time

SQL Time Is Always Wrong Time
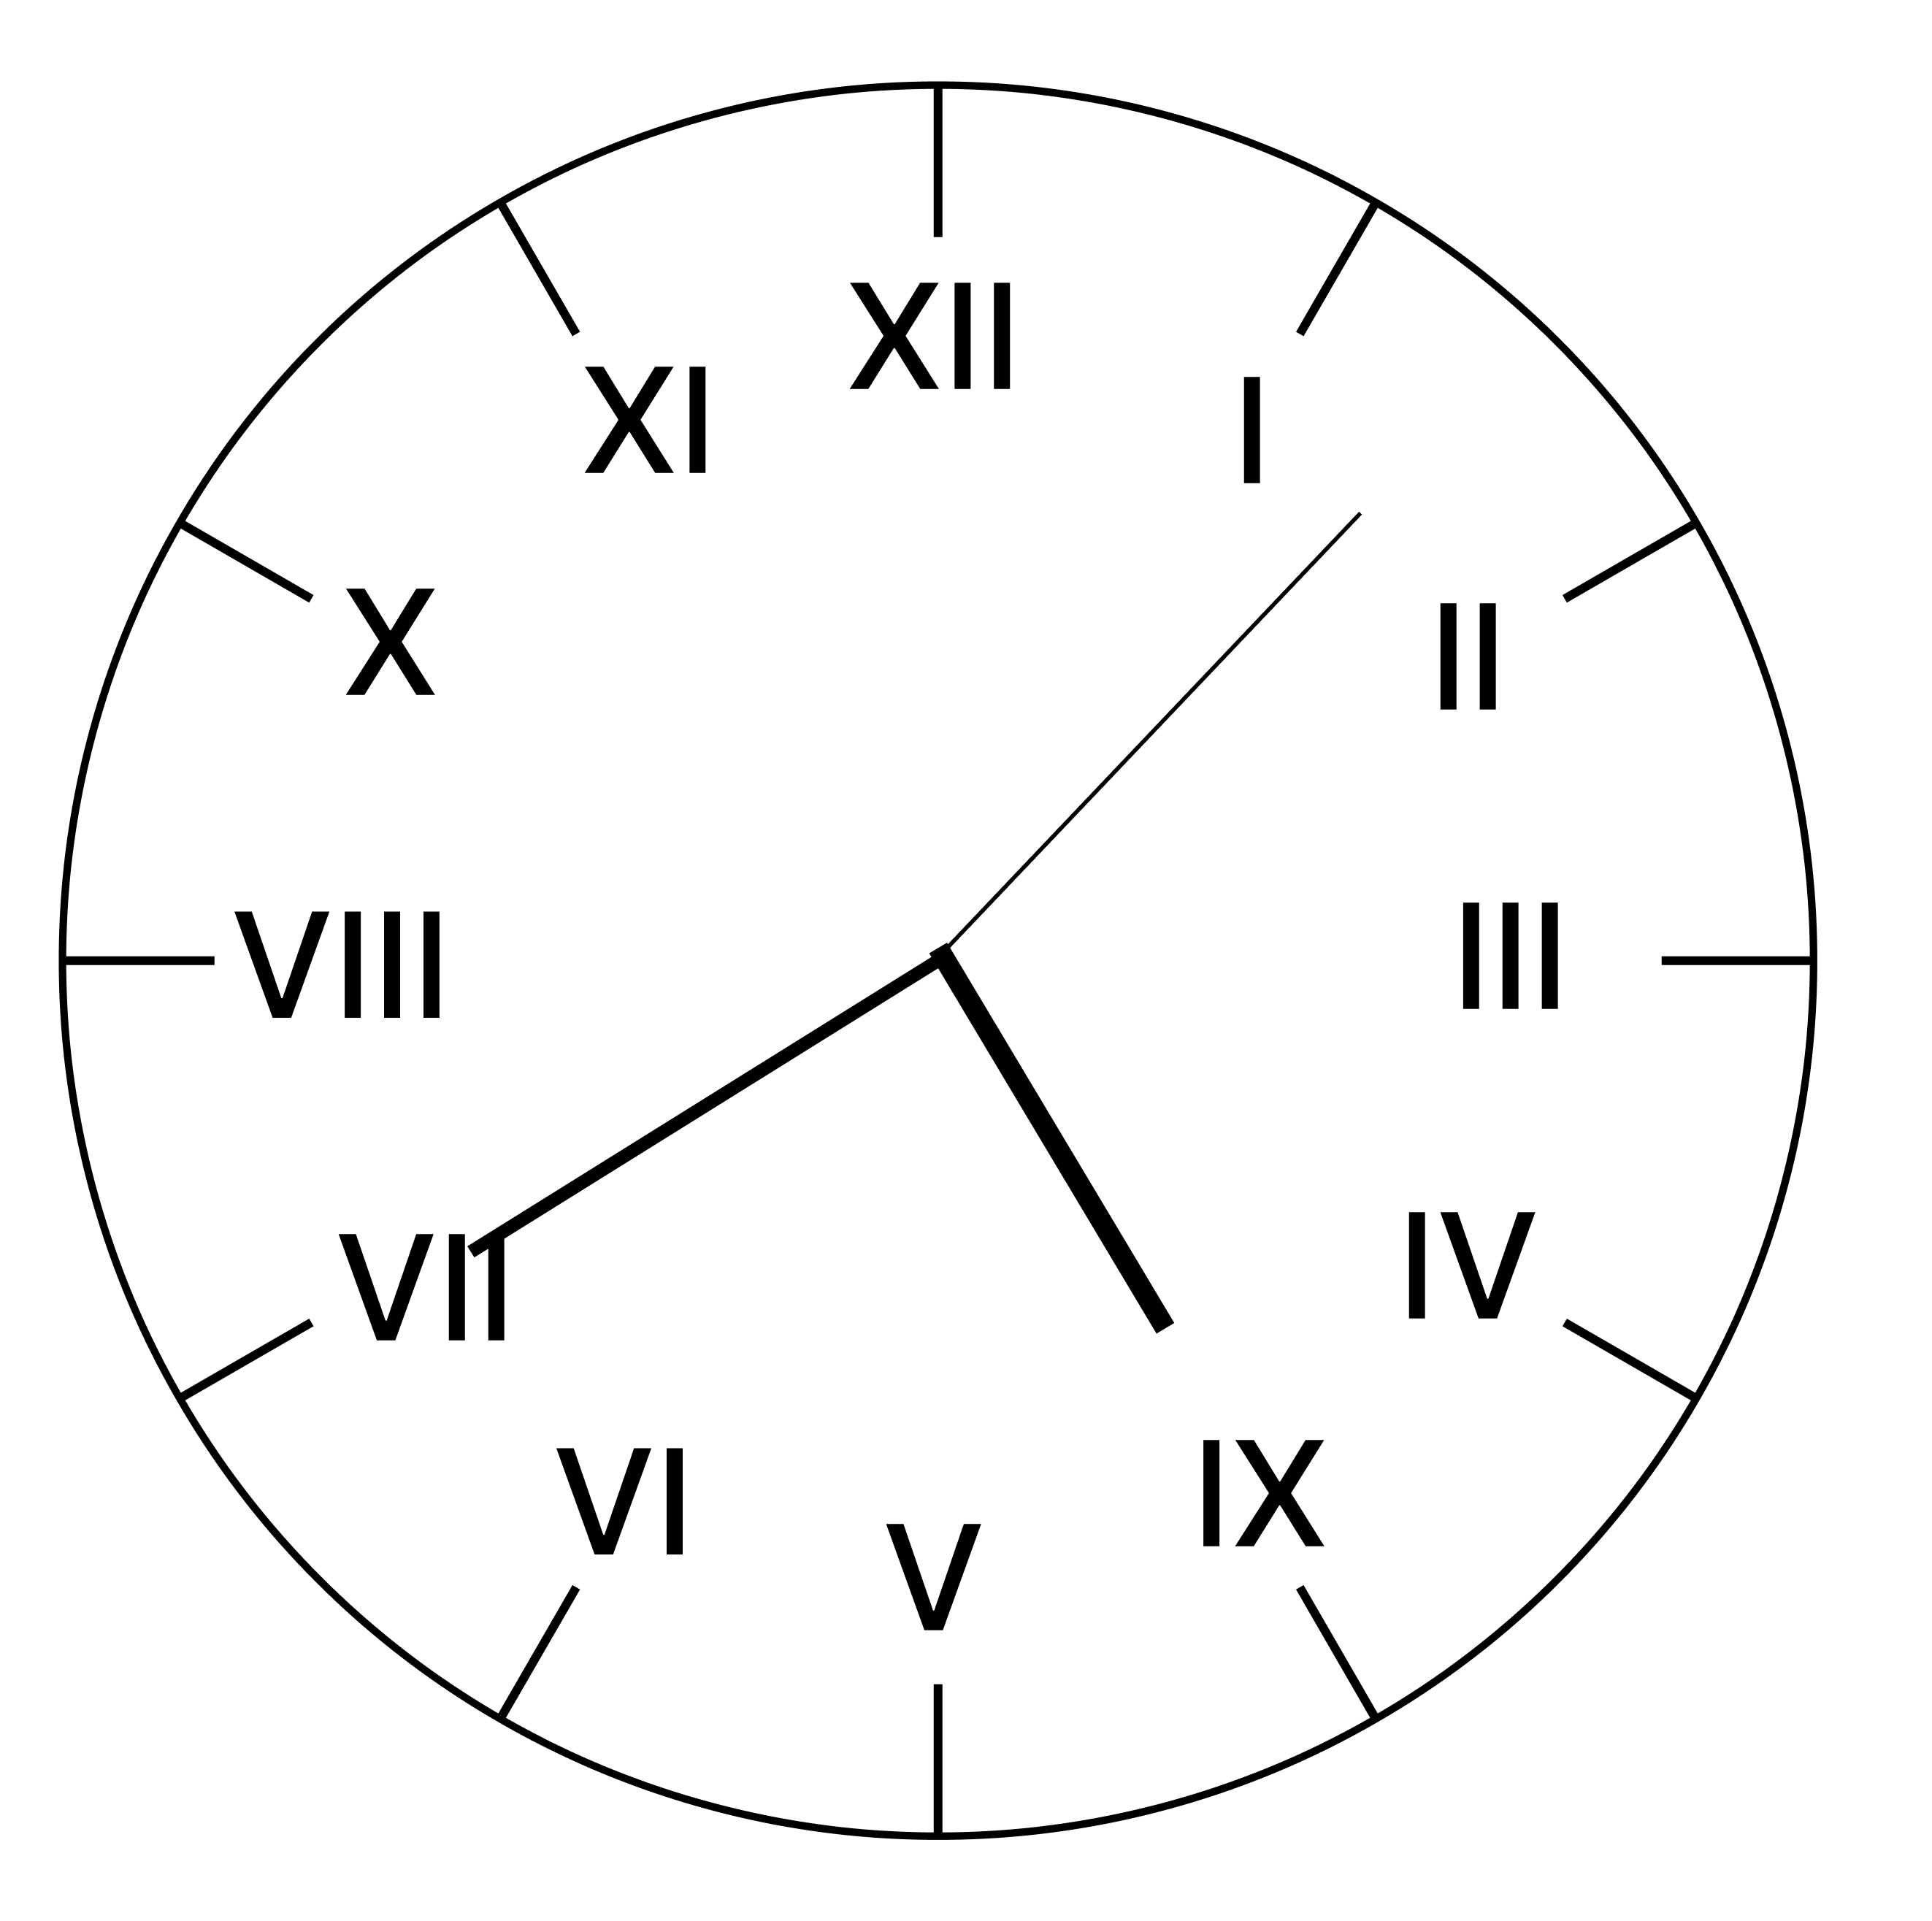
What happens when a DBA designs a clock? You get Roman numerals in completely random order because SQL queries without proper constraints do whatever they want. Notice how IX (9) is where 4 should be, and V (5) is at 6 o'clock. The comment "It Will Work This Time" is the eternal lie every developer tells themselves before running untested SQL in production. Spoiler: it never does.