Malicious code Memes

Posts tagged with Malicious code
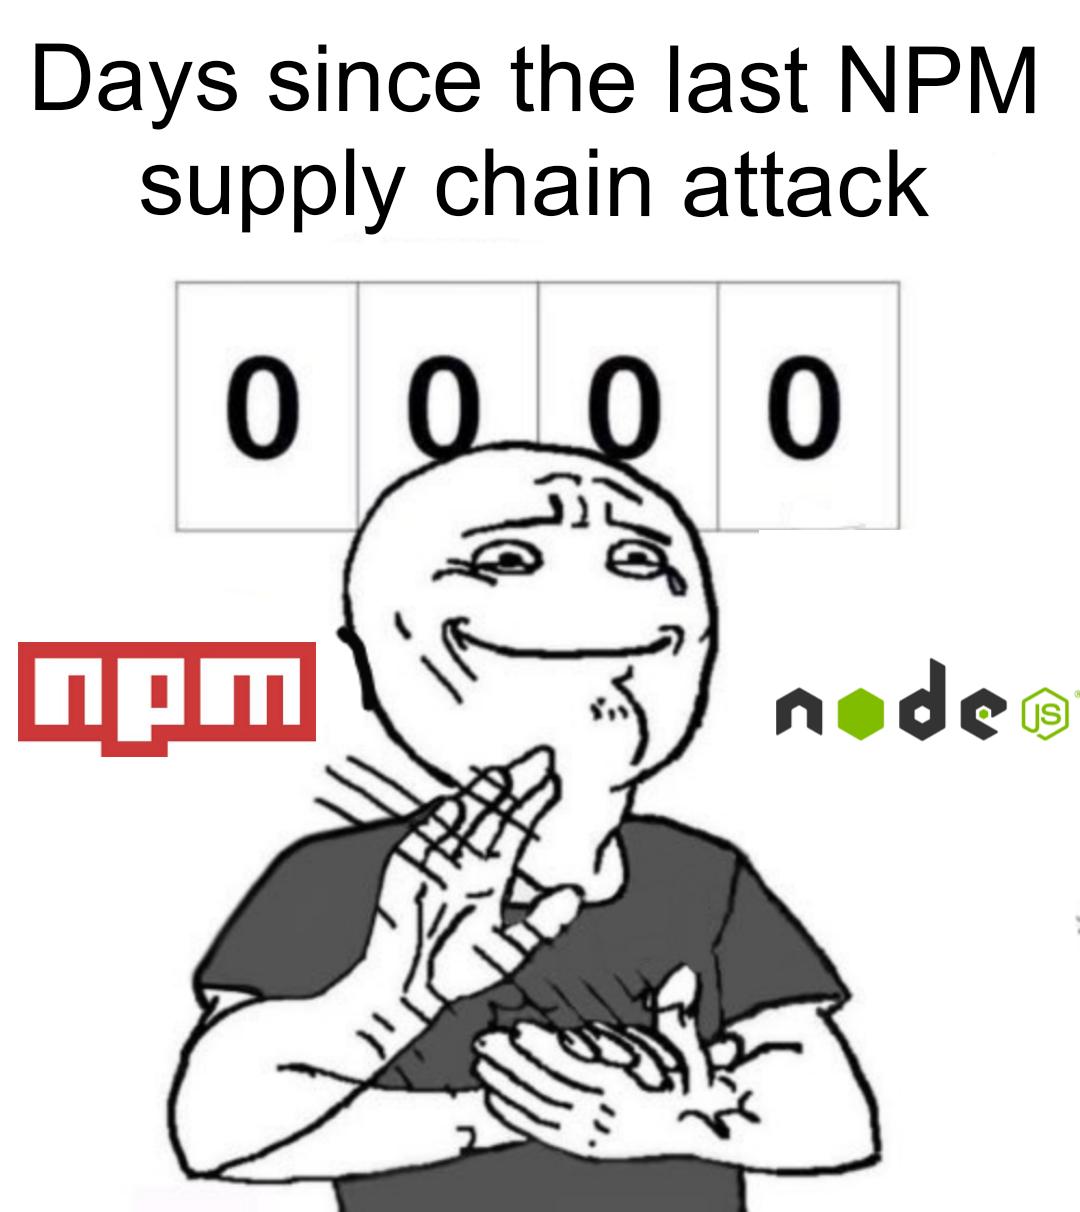
Days Since Supply Chain Attack

Days Since Supply Chain Attack
The JavaScript ecosystem is basically a game of "how many days until someone sneaks malicious code into a package with 50 million weekly downloads." The counter reads zero because, well, it's always zero. NPM supply chain attacks have become so frequent that tracking them is like counting grains of sand on a beach—pointless and depressing. The meme uses the "Days Since Last Accident" workplace safety sign format, except instead of workplace injuries, we're tracking the inevitable compromise of some random package you installed three years ago and forgot about. The smug satisfaction on the face? That's the attacker who just pushed version 2.0.1 with a "minor bug fix" that also happens to exfiltrate your environment variables. Between left-pad incidents, colors/faker drama, and various typosquatting attempts, the Node.js dependency tree has become a trust exercise with strangers on the internet. Sleep tight knowing your production app depends on 1,247 packages maintained by volunteers who may or may not have enabled 2FA.

How To Play

How To Play
Roses are red, violets are blue, here's a guessing game that'll nuke your OS too. Someone made a Python "game" where if you guess wrong, it casually tries to delete the entire System32 folder—you know, that little directory Windows needs to, uh, exist. Sure, you need admin privileges for this to actually work, but the audacity of putting os.remove() in the else clause is chef's kiss levels of chaos. It's like Russian roulette but instead of bullets, it's your entire operating system. The poem format really sells the innocent vibes before the digital arson kicks in.

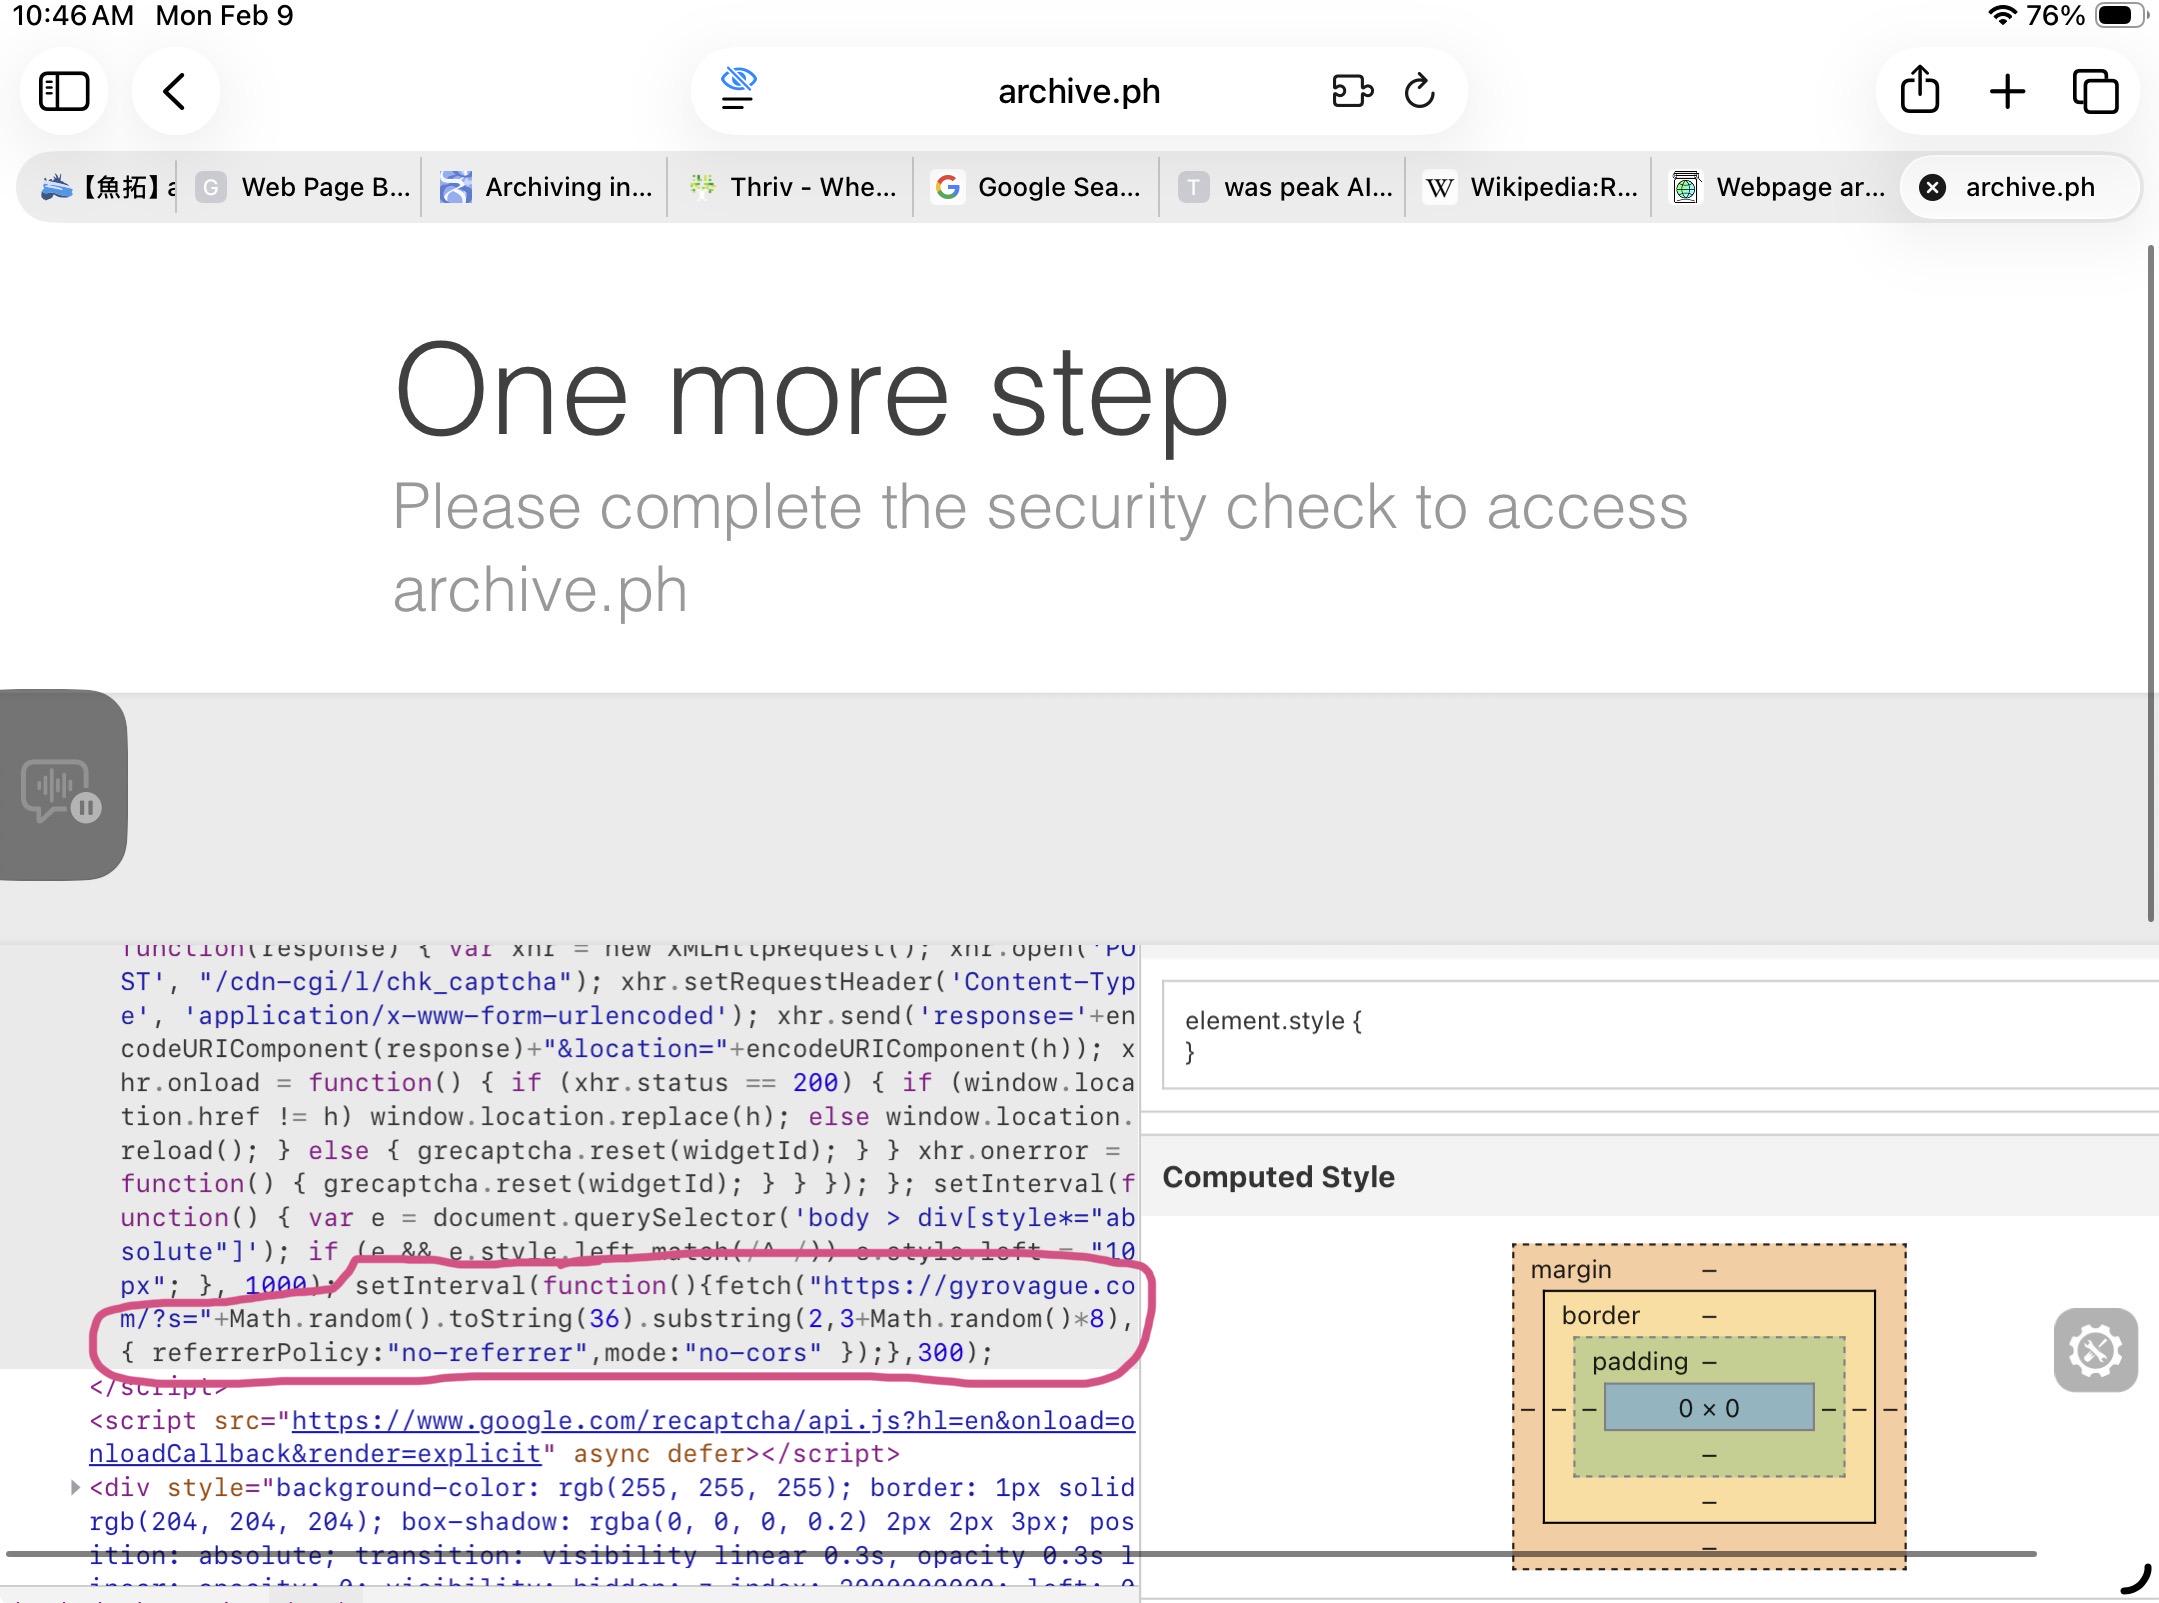
In January 2026, Archive.Today Added Code Into Its Website In Order To Perform A Distributed Denial-Of-Service Attack Against A Blog

In January 2026, Archive.Today Added Code Into Its Website In Order To Perform A Distributed Denial-Of-Service Attack Against A Blog
So Archive.Today decided to weaponize their visitors' browsers into an involuntary botnet. That circled code at the bottom? Pure chaos. They're using setInterval to repeatedly fire off fetch requests to gyrovague.com with randomized query parameters every 300ms. Classic DDoS-as-a-Service, except the "service" is mandatory for anyone trying to access their site. The beautiful irony? Archive sites exist to preserve content and protect against censorship, yet here they are literally trying to nuke someone's blog off the internet by turning every visitor into an unwitting attack vector. It's like a library burning down another library using its patrons as arsonists. Also notice the Cloudflare CAPTCHA at the top? They're hiding behind DDoS protection while simultaneously launching DDoS attacks. The hypocrisy is *chef's kiss*. That's some next-level "I'm not locked in here with you, you're locked in here with me" energy.

Send Him Right To Jail

Send Him Right To Jail
Ah, the diabolical genius of adding a 5% chance of random failure to your code. Nothing says "I hate my fellow developers" quite like injecting TypeErrors that only appear occasionally. This is basically the programming equivalent of putting a landmine in your neighbor's garden and then obfuscating the code so nobody can find it. The person who wrote this deserves not just jail, but a special circle of developer hell where they're forced to debug Internet Explorer compatibility issues for all eternity. The best part? Those poor souls trying to reproduce the bug will spend days pulling their hair out because it only happens 1 in 20 times. Pure evil wrapped in a Math.random() call.

UGREEN 20Gbps M.2 NVMe and SATA SSD Enclosure

UGREEN 20Gbps M.2 NVMe and SATA SSD Enclosure
NVMe and SATA SSD Compatibility:This M.2 enclosure supports both PCIe NVMe and SATA NGFF SSDs up to 8TB in 2230, 2242, 2260, and 2280 sizes. It works seamlessly with Windows, macOS, Linux, Android, a…

Chaotic Evil: The Dark Art Of Buffer Overflow

Chaotic Evil: The Dark Art Of Buffer Overflow
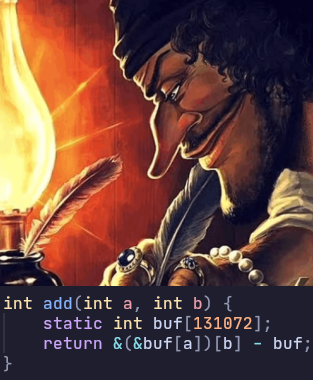
Look at this absolute psychopath writing a function that masquerades as addition but secretly performs dark magic with buffer overflows. The evil genius is using array indexing on a static buffer with arbitrary inputs, dereferencing pointers, and then subtracting the buffer's address from the result. This isn't addition—it's a ticking time bomb disguised as math. The dramatic lighting and quill pen really sell it. Nothing says "I'm about to crash your entire system" like writing memory-corrupting C code by candlelight like some kind of deranged 18th-century villain. Somewhere a security engineer just felt a cold shiver down their spine.

Send Him Right To Jail

Send Him Right To Jail
HOLD THE PHONE! This developer just committed the ULTIMATE crime against humanity! Adding a 5% chance of random errors in a library?! That's not coding, that's PSYCHOLOGICAL WARFARE! 💀 Imagine spending 6 hours debugging only to discover your error is literally a RANDOM NUMBER GENERATOR deciding your fate. It's like the software equivalent of stepping on LEGO - completely unexpected and absolutely excruciating. And then obfuscating the code?! That's not just evil, that's supervillain-level diabolical. Other developers aren't just contemplating the noose, they're BOOKING THERAPY SESSIONS IN ADVANCE!

Report Phishing (But Fall For It Instead)

Report Phishing (But Fall For It Instead)
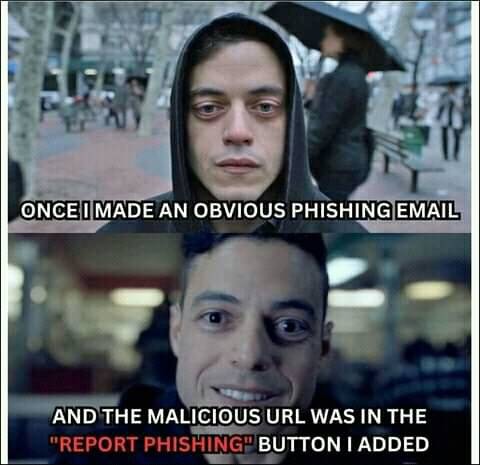
When you're so committed to social engineering that you add a malicious link in the "Report Phishing" button itself. That's like putting a bear trap inside the bear trap warning sign. The perfect crime until some security engineer actually checks the code during their quarterly audit that was supposed to happen last year.

The Revenge Code Backfire

The Revenge Code Backfire
Ah, the classic "Am I the villain?" moment every developer has when they discover that their "just in case" code could actually land them in prison. Turns out embedding vengeful time bombs in production systems is frowned upon by both employers and the legal system. Who knew? Pro tip: If your exit strategy involves felony charges and a decade behind bars, maybe just settle for a passive-aggressive goodbye email instead.

OUKMIC Mobile Standing Desk Portable Pneumatic Laptop Rolling Cart Adjustable Height, Tiltable Overbed Table Sit Stand Computer Workstations for Home Office w/Wheels Flat Desk 32", White

OUKMIC Mobile Standing Desk Portable Pneumatic Laptop Rolling Cart Adjustable Height, Tiltable Overbed Table Sit Stand Computer Workstations for Home Office w/Wheels Flat Desk 32", White
UNIQUE FOLDING TABLE: This rolling computer desk is designed with a tiltable tabletop that supports 0°-50° flipping for working, reading, writing, drawing and more. Non-slip pads are added to protect…

Obfuscate Code

Obfuscate Code
Ah, the classic "5% chance of random failure" pattern! This diabolical code snippet deliberately throws a NullReferenceException 5% of the time for absolutely no logical reason. It's basically the digital equivalent of putting a LEGO on the floor of your codebase - someone's going to step on it at 2 AM during a production emergency and scream. Pure evil genius for making QA testers question their sanity and giving future maintainers trust issues. The best part? The error message falsely suggests there's an actual null reference problem to debug when it's just RNG chaos!