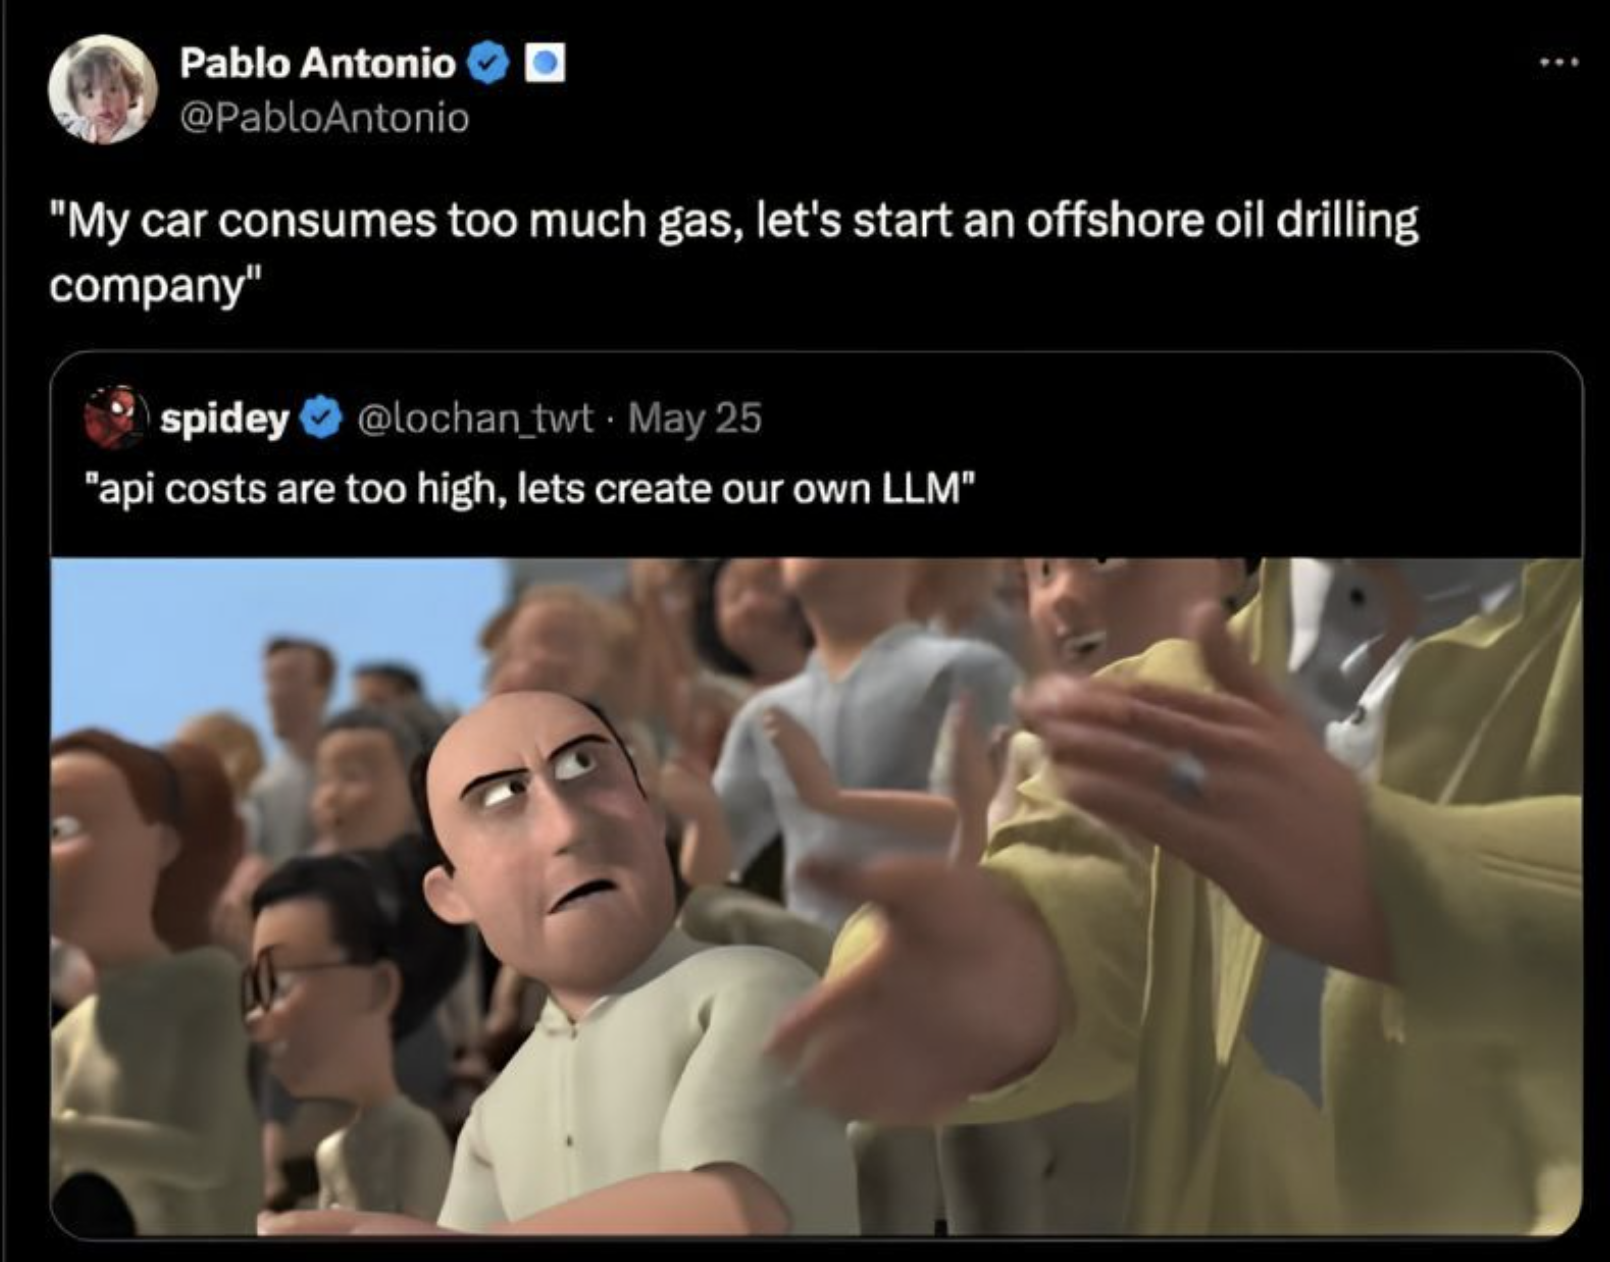
api Memes

On The Other Hand The DB Is Now Clean

On The Other Hand The DB Is Now Clean
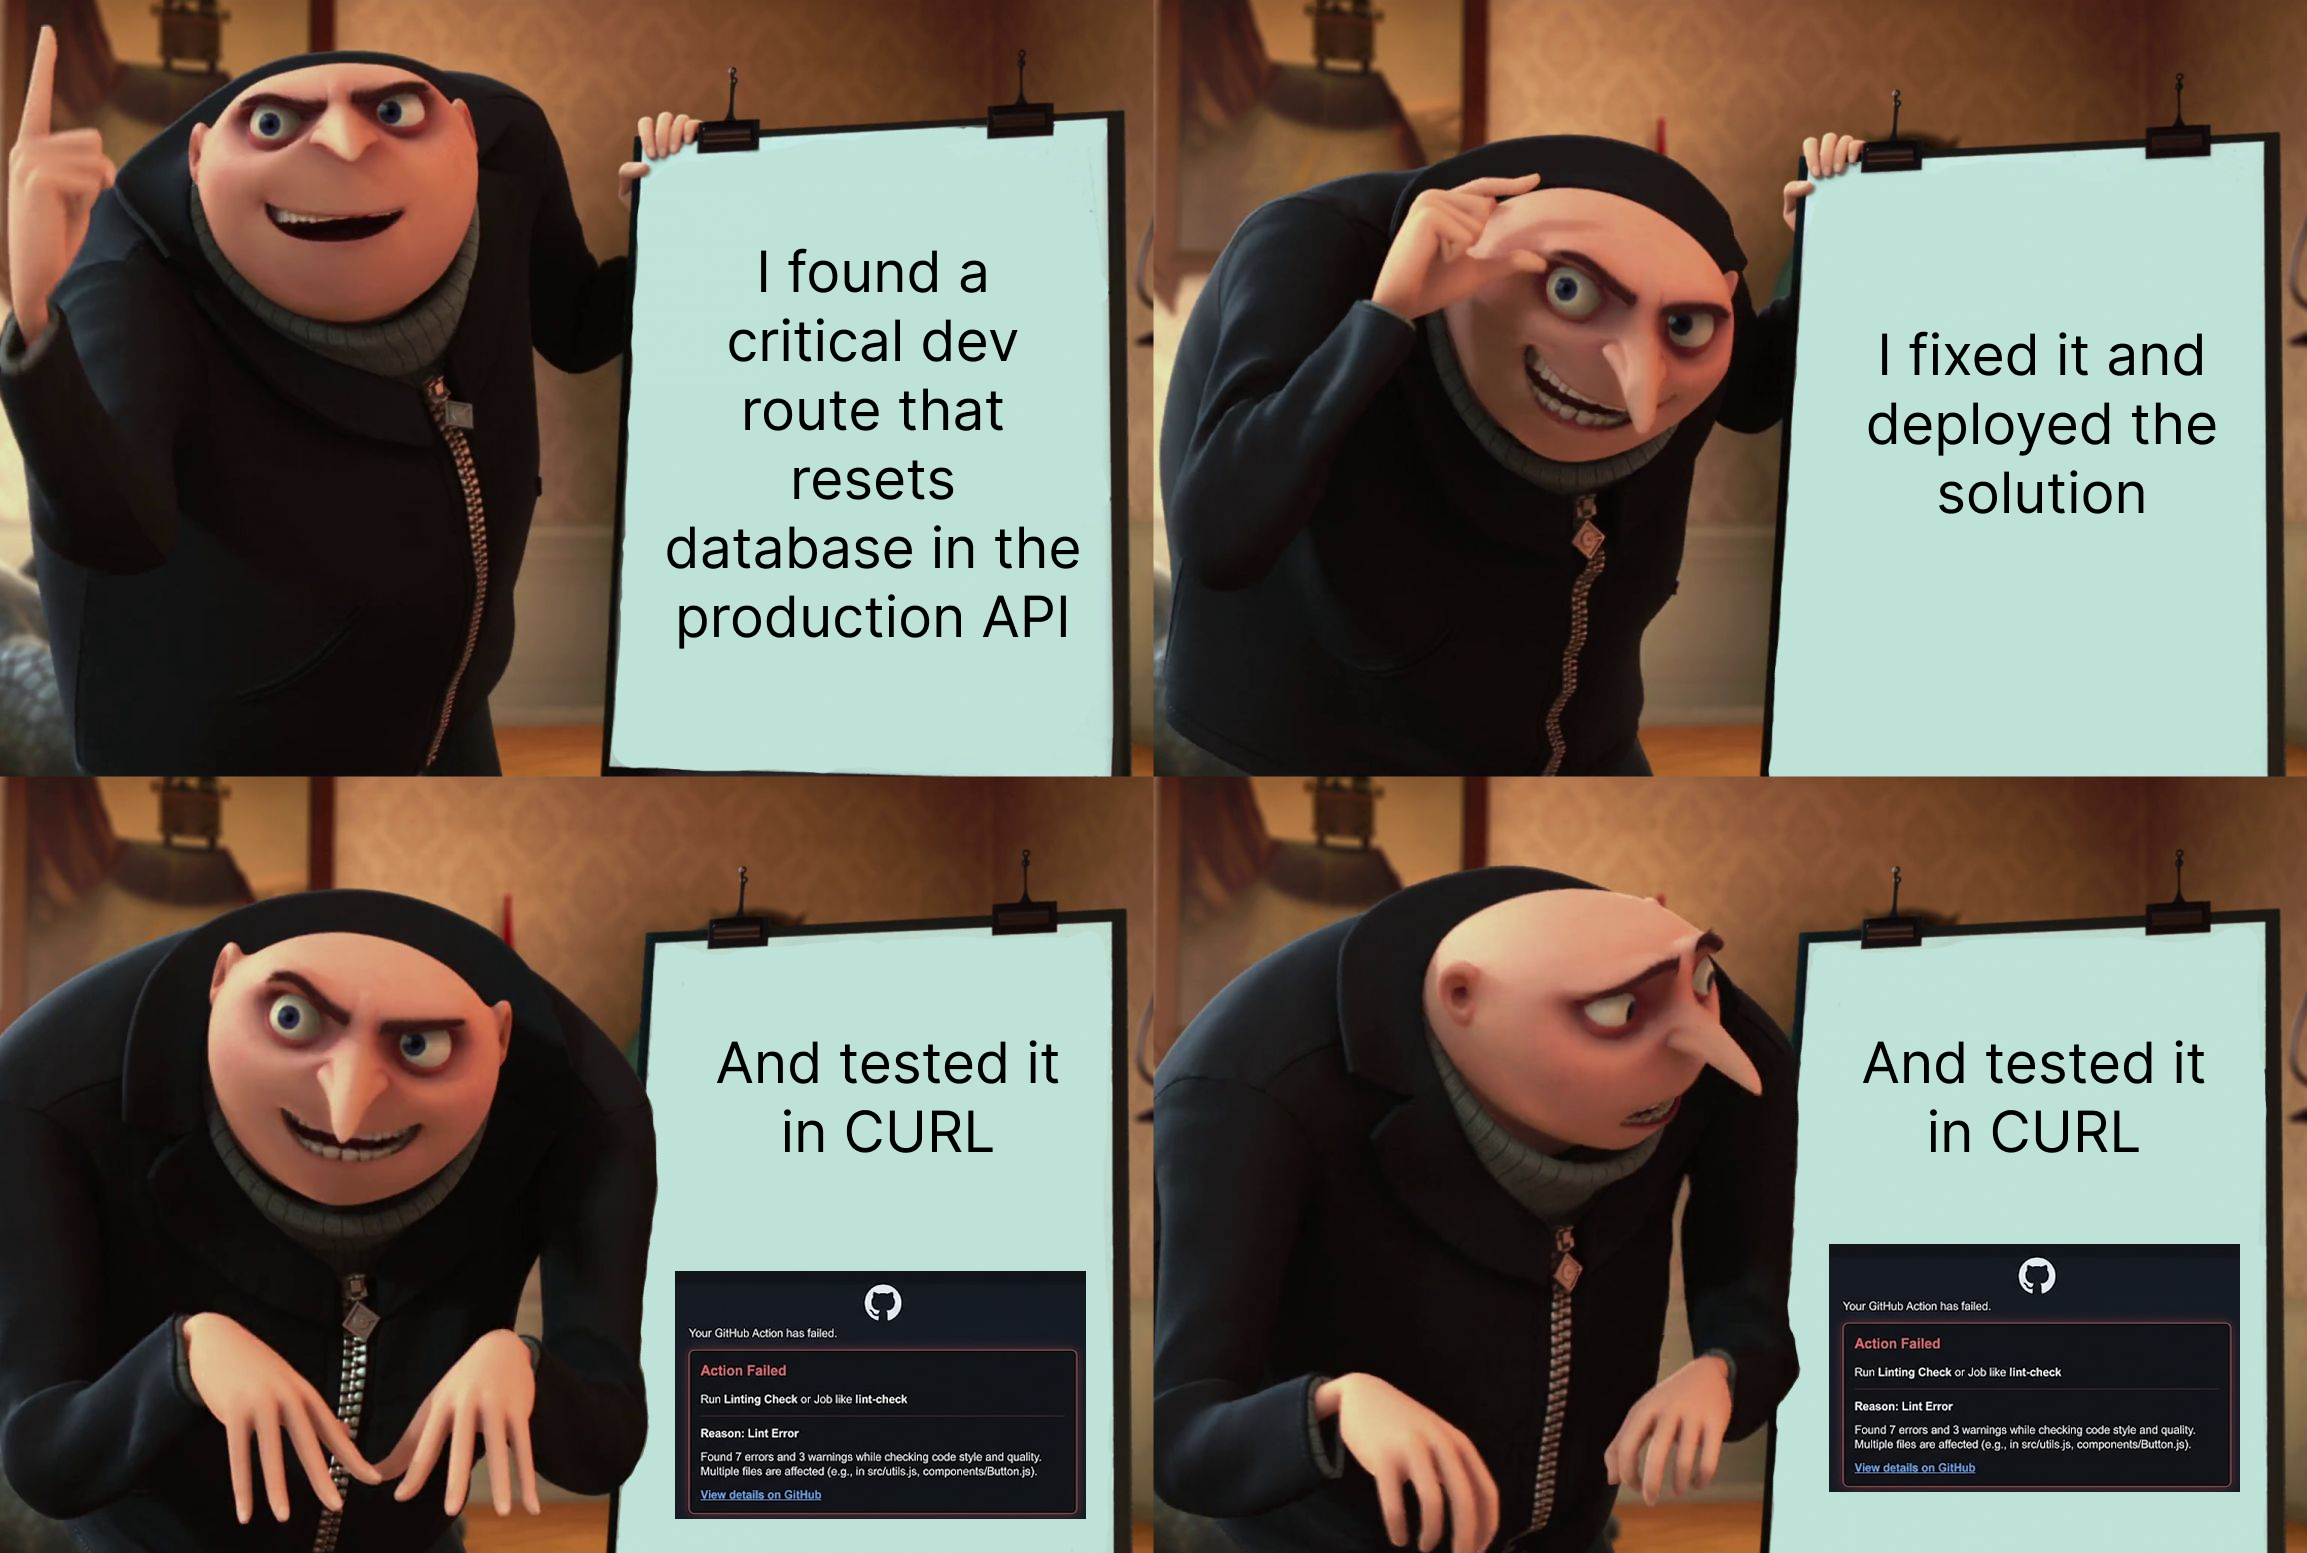
So you discovered a shiny dev route that wipes the entire production database, patched it up like the hero you are, deployed it with confidence, and then decided to test it with CURL... only to watch in absolute HORROR as your "fix" proceeds to nuke the database ANYWAY. The GitHub Actions are screaming, the linting checks are having a meltdown, and somewhere in the distance, your manager is probably getting an alert. But hey, at least the database is squeaky clean now! Nothing says "job security" quite like accidentally executing the exact catastrophe you were trying to prevent. Chef's kiss. 💀

Technical Debt Came Due

Technical Debt Came Due
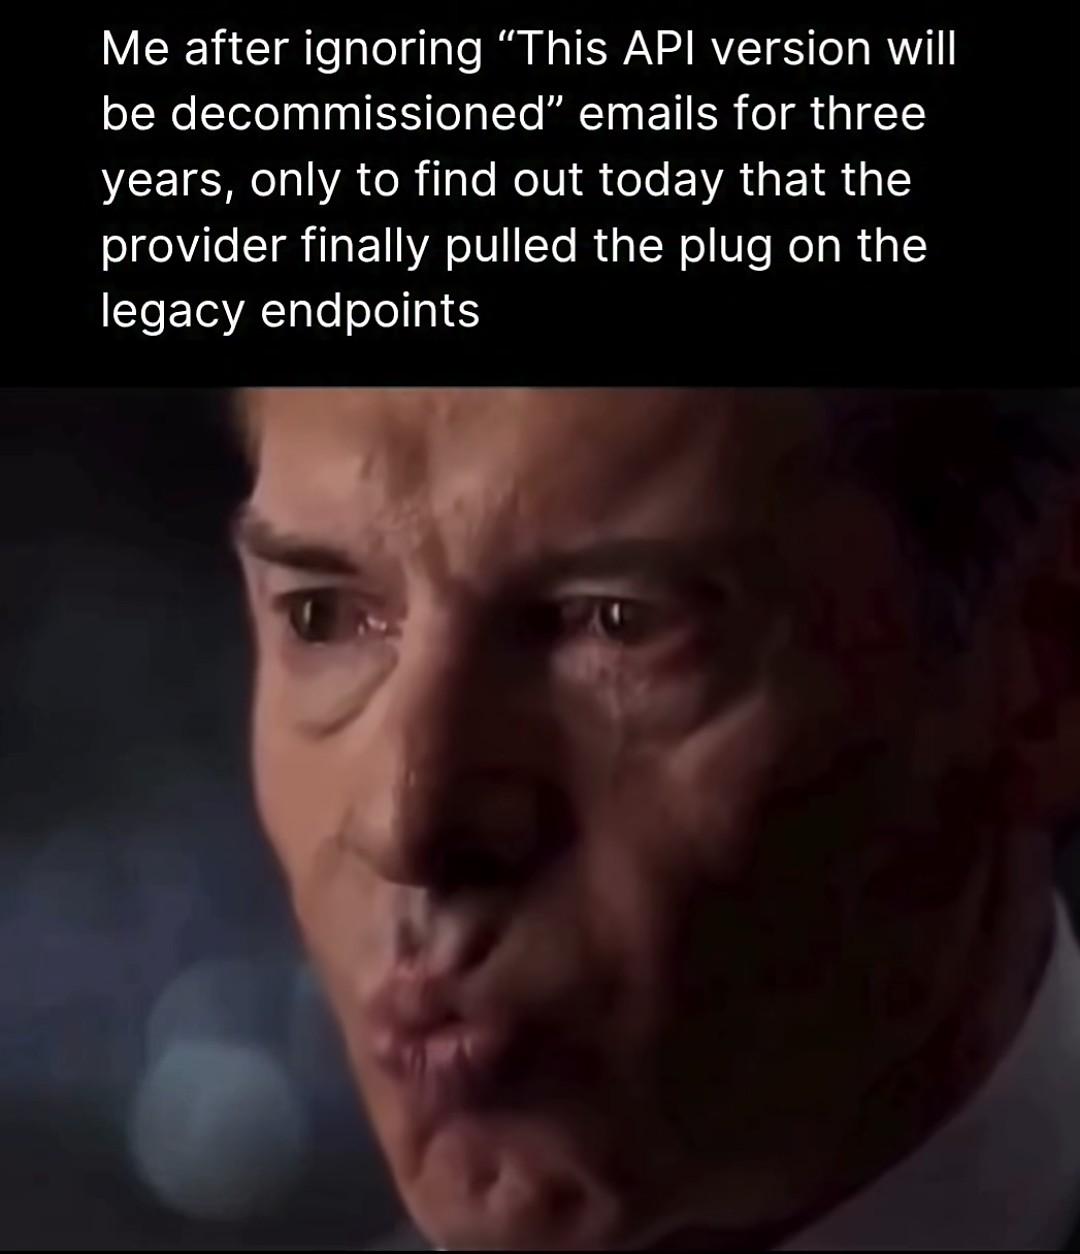
Picture this: You've been living your best developer life, casually deleting those pesky deprecation warnings from your inbox like they're spam emails about car warranties. Three YEARS of "hey bestie, maybe update your API calls?" notifications straight to the trash. Then one fateful morning, your entire application breaks because the provider actually had the AUDACITY to follow through on their threats. The sheer betrayal! The absolute nerve! Now you're sitting there with your production app in flames, realizing that ignoring problems doesn't make them disappear—it just makes them show up at the worst possible moment with compound interest. Procrastination: 1, You: 0.

Buckle Up

Buckle Up
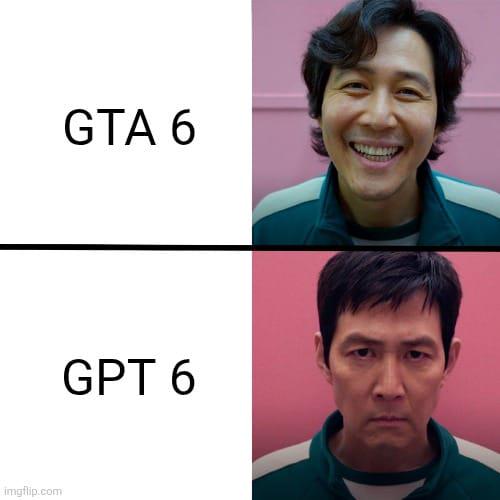
GTA 6 has been in development for over a decade and everyone's hyped about it. Meanwhile, GPT-6? That thing's gonna drop before we even finish debugging our GPT-4 integrations. The top panel shows pure joy thinking about GTA 6's eventual release, while the bottom panel captures the existential dread of realizing AI models are iterating faster than you can keep up with their API changes. By the time you've mastered prompt engineering for GPT-5, OpenAI will be like "surprise! here's GPT-6 with completely different behavior patterns." RIP to all those carefully crafted system prompts.

Me Explaining Full Stack Development To My Grandmother

Me Explaining Full Stack Development To My Grandmother
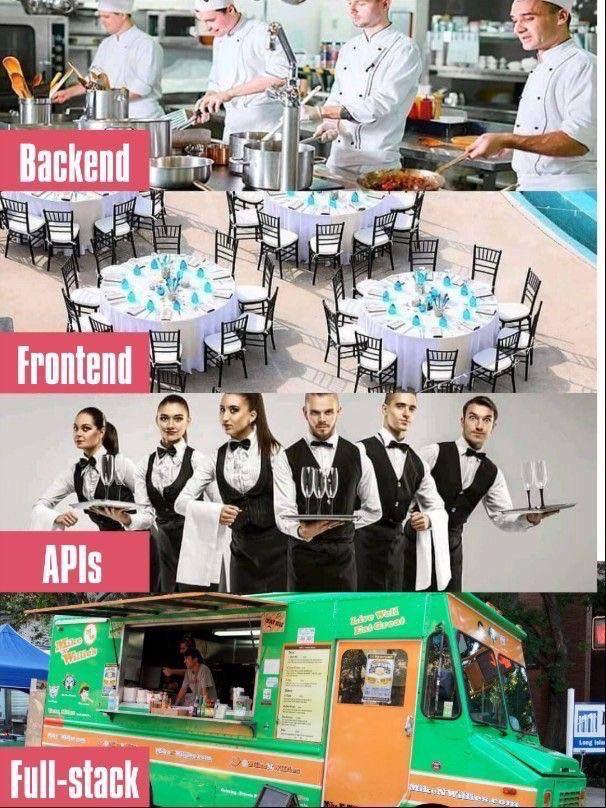
Backend devs are the kitchen crew sweating over databases and server logic where nobody sees them. Frontend is the fancy dining area—pretty tables, nice ambiance, everything looks perfect for the users. APIs are the waitstaff elegantly shuttling data between the two worlds. And full-stack? That's literally a food truck where one person does EVERYTHING—cooking, serving, taking orders, probably also fixing the engine and filing taxes. Grandma nodded politely but still thinks you "work with computers."

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

The Human Api

The Human Api
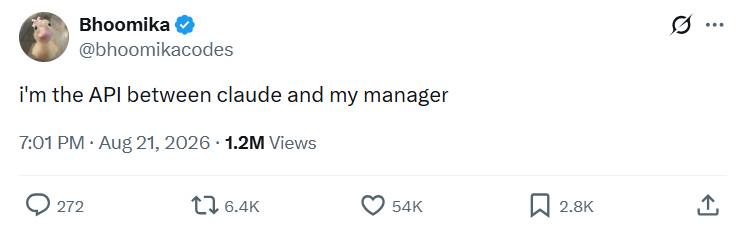
You know you've made it in tech when you realize your entire job is just being middleware. Claude (or any AI tool) does the actual work, your manager takes the credit, and you're stuck in the middle translating between "can you make it pop more?" and actual executable code. The real kicker? APIs are supposed to be stateless, but here you are carrying emotional baggage from every sprint review. You're basically a REST endpoint that returns 200 OK while internally screaming 500 Internal Server Error. Fun fact: Unlike actual APIs, you don't get to deprecate yourself or return a 429 Too Many Requests when your manager Slacks you for the fifth time asking "quick question" at 6 PM on a Friday.

Fails For Teapots

Fails For Teapots
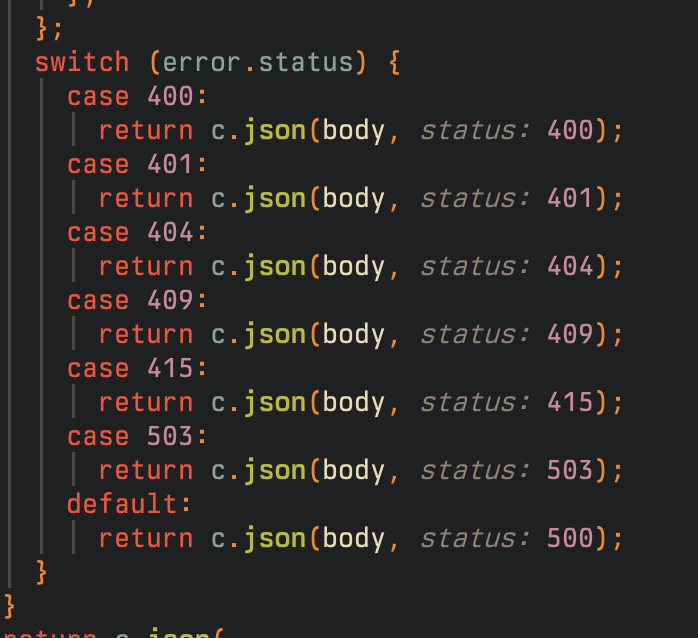
Someone wrote a switch statement to handle HTTP error codes, meticulously returning JSON responses with the status code... except they forgot one tiny detail: HTTP 418 "I'm a teapot". You know, the most critical status code in production. The one from an April Fools' RFC that somehow became part of actual HTTP spec. They covered 400, 401, 404, 409, 415, 503, and even have a default case for 500. But when your server identifies as a teapot and refuses to brew coffee? Straight to the default handler like some common peasant error. The disrespect is real. Fun fact: RFC 2324 introduced status code 418 as a joke in 1998 for the Hyper Text Coffee Pot Control Protocol. It was supposed to be deleted, but developers loved it so much that it's now immortalized in the HTTP spec. Some APIs actually use it for rate limiting or Easter eggs. Because why not?

Update At Your Earliest Convenience

Update At Your Earliest Convenience
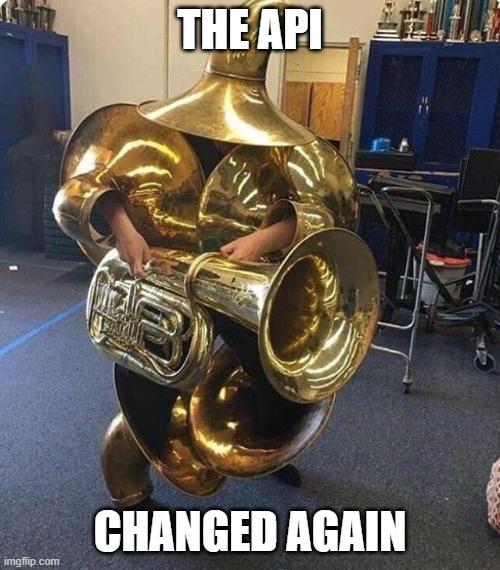
You know that third-party API you integrated six months ago? The one that promised "stable endpoints" and "backward compatibility"? Yeah, they just pushed their 47th breaking change this quarter. Your codebase is now a tangled mess of adapters, wrappers, and deprecated method calls that somehow still work but nobody knows why. The kid in the tuba perfectly captures what your integration layer looks like after chasing these "minor updates" and "improvements." What started as a simple REST call now requires authentication flows that changed three times, response formats that shifted from XML to JSON to "JSON but with extra steps," and documentation that was last updated when dinosaurs roamed the earth. Best part? Their changelog just says "various improvements and bug fixes." Cool, cool. Let me just rewrite my entire service layer real quick.

Battle.Net's Discord Permissions

Battle.Net's Discord Permissions
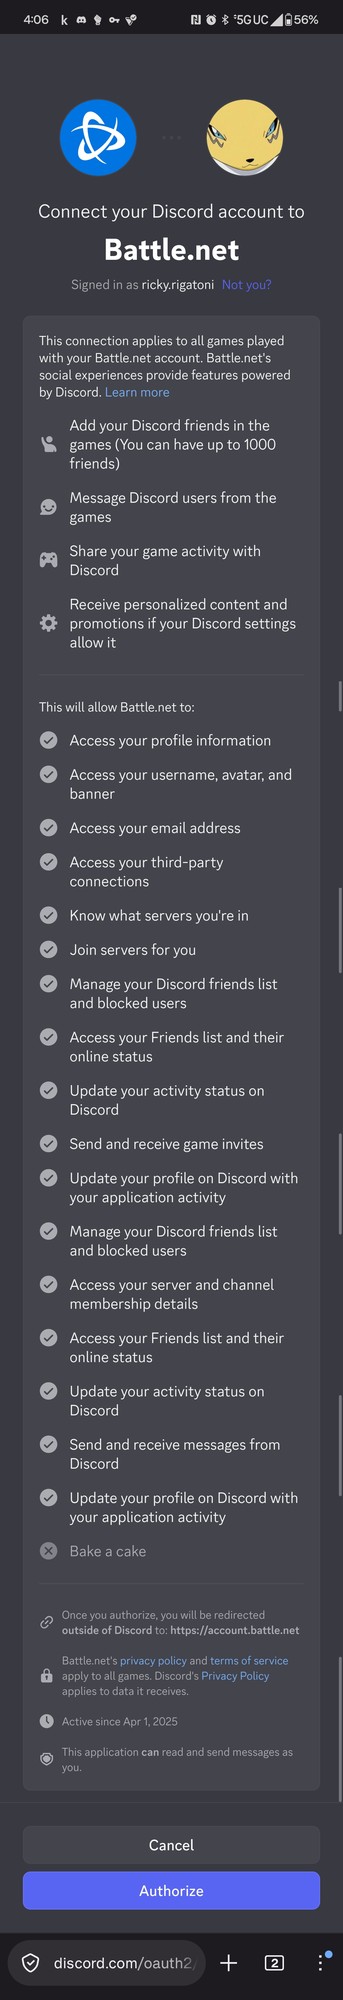
Battle.net really said "we need literally everything" and then casually slipped "Bake a cake" into the permission list like we wouldn't notice. Because nothing says "gaming integration" quite like OAuth access to your baking capabilities. The permission list reads like a surveillance state wishlist: access your friends, manage your friends, know what servers you're in, join servers FOR you, read your messages, send messages, update your profile, update your activity, and oh yeah—bake a cake. At this point they might as well add "water your plants" and "file your taxes." Props to whoever snuck that in there. Either it's a developer's cry for help, a test to see if anyone actually reads these things, or Battle.net genuinely needs cake-baking permissions for... reasons. Either way, that "Authorize" button is doing some heavy lifting here.

Why Is Our Json Deserializer Returning Empty Objects

Why Is Our Json Deserializer Returning Empty Objects
Someone's out here debugging their JSON deserializer while staring at a response body that's basically one giant array. Not an object. An array . The kind that starts with a bracket, not a curly brace. Deserializing an array into an object is like trying to pour water into a colander and wondering why your cup is empty. The type mismatch is right there, highlighted in blue, mocking you. But sure, let's spend another hour checking if the property names match. Pro tip: when your deserializer returns empty objects, maybe check if you're actually receiving what you think you're receiving. Revolutionary concept, I know.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

Slow Clap

Slow Clap
The tech industry's favorite pastime: solving expensive problems by creating exponentially more expensive problems. Someone complained about API costs being too high, so naturally the solution is to train your own Large Language Model from scratch. Because nothing says "cost optimization" like spending millions on GPUs, hiring an entire ML team, and burning through your company's runway faster than a SpaceX launch. It's like saying "this restaurant is too expensive" and then buying a farm, hiring chefs, and opening your own Michelin-star establishment. The comparison to starting an offshore oil drilling company because your car uses too much gas is chef's kiss level satire. Both scenarios share the same energy: wildly overengineering a solution while completely missing the point of cost reduction. Spoiler alert: Your startup probably doesn't need its own LLM. Just optimize your prompts and cache your responses like a normal person.

When Your OAuth Keeps Breaking

When Your OAuth Keeps Breaking
Nothing quite captures the soul-crushing loop of OAuth debugging like having to re-authenticate for the 47th time in an hour. Your session expired? Token refresh failed? Redirect URI typo? Who knows—but you're definitely logging in again. The best part? Each login attempt takes you through the entire flow: click the button, wait for the redirect, accept permissions, get bounced back, watch it fail, and repeat. It's like Groundhog Day but with more JSON and less Bill Murray. Pro tip: After your 10th login attempt, you start questioning your entire career path. After the 20th, you're googling "how to become a carpenter."

Understandable Decision When You Think About It

Understandable Decision When You Think About It
When faced with the choice between hacking HuggingFace or actually learning C++, the rational developer obviously chooses option three: just use OpenAI's flagship model and call it a day. Why wrestle with memory management, segmentation faults, and template metaprogramming nightmares when you can simply throw API calls at the problem? And sure, you could try to compromise HuggingFace's infrastructure to get free model access, but that involves both legal consequences AND probably writing some C++ exploit code anyway. The modern developer's solution: skip the painful learning curve, avoid federal prison, and just pay for GPT-4. Sometimes the best optimization is optimizing your own suffering out of the equation entirely.