AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
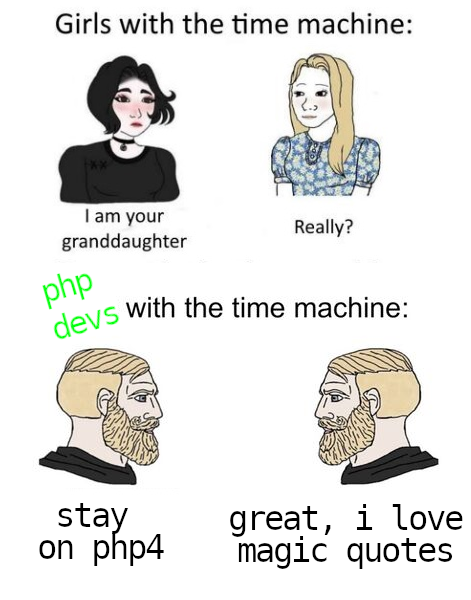
For those blessed enough to have never encountered it: Magic Quotes was PHP's "security feature" that automatically escaped quotes in user input. Sounds helpful, right? Wrong. It created more problems than it solved, mangled data, and made SQL injection vulnerabilities *worse* in many cases because devs thought they were protected when they weren't.
The joke here is that if PHP devs could go back in time, they wouldn't warn themselves about future mistakes or suggest better practices. Nope. They'd tell their past selves to stay on PHP 4 and keep using Magic Quotes—arguably one of the worst decisions in PHP history. It's like saying "yeah, keep using that broken parachute, it's great!"
The feature was so universally hated that it was deprecated in PHP 5.3 and completely removed in PHP 5.4. But here we are, romanticizing the bad old days like some kind of Stockholm syndrome survivors.