Security theater Memes

Posts tagged with Security theater
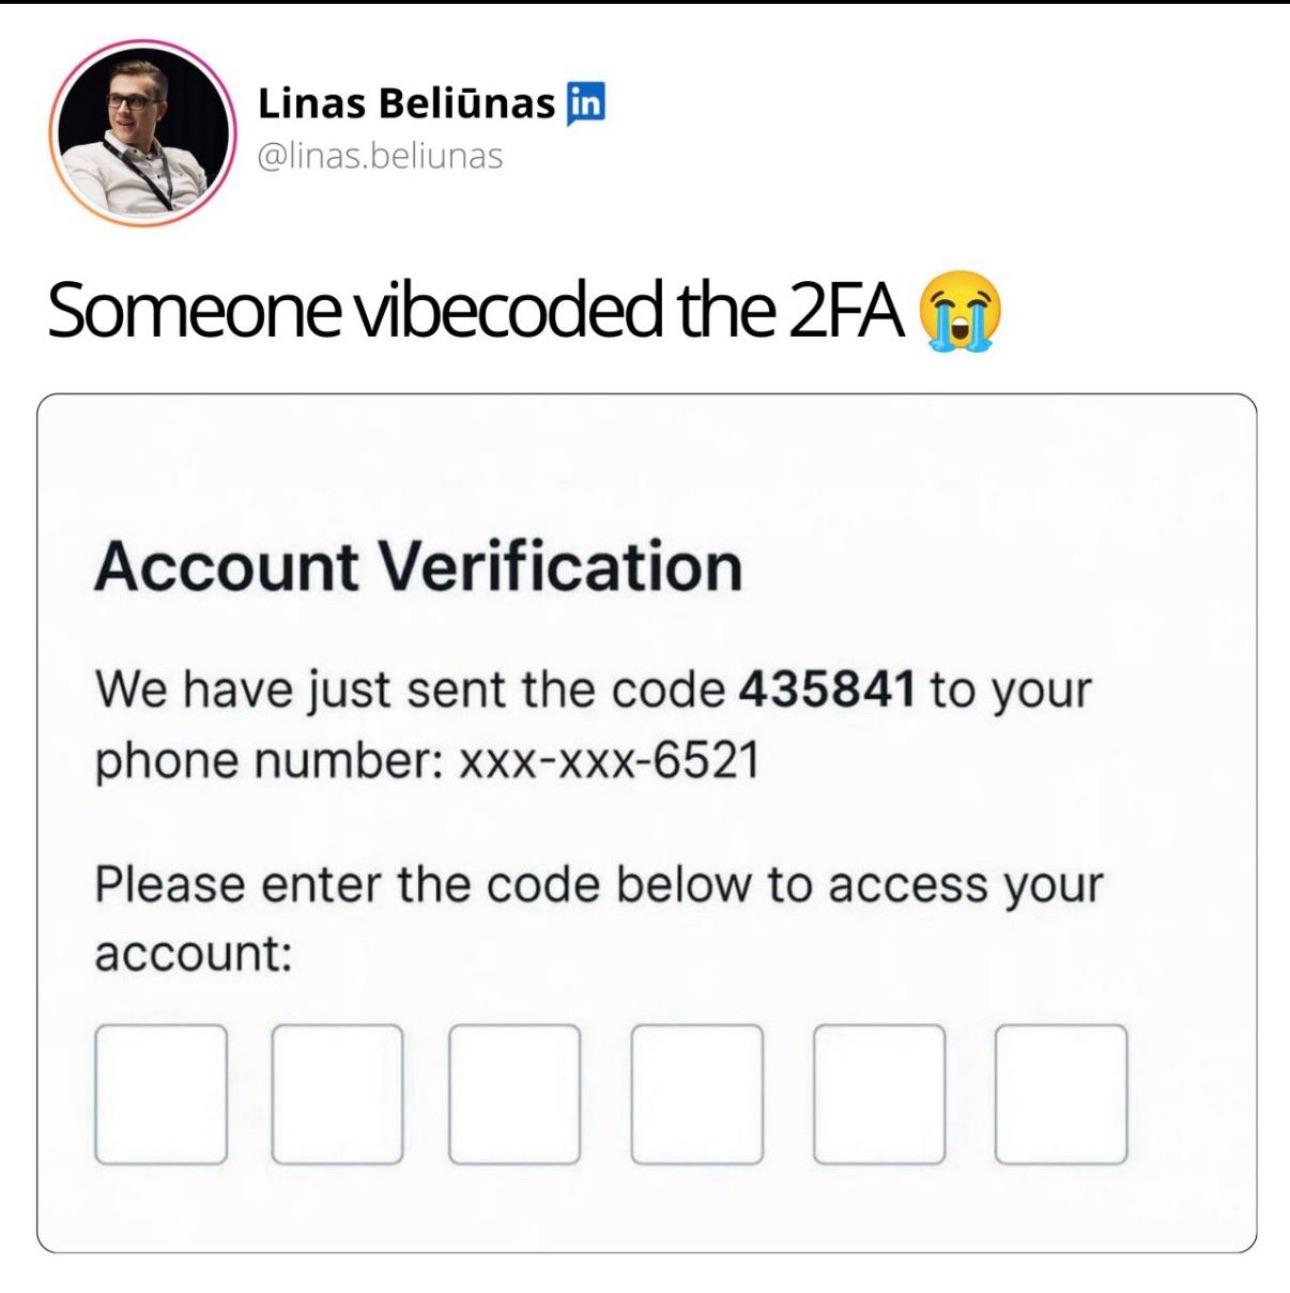
Make Auth Great Again

Make Auth Great Again
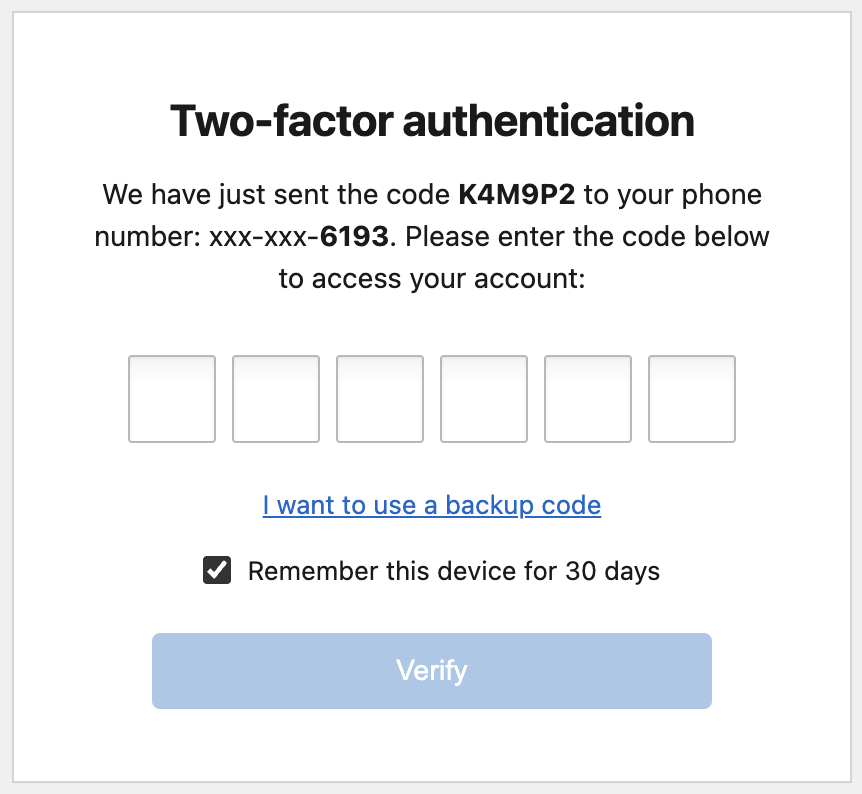
Nothing says "secure authentication" quite like displaying the actual 2FA code right there in the UI. Why bother sending it to your phone when they can just... tell you what it is on the same screen? It's like having a bouncer who whispers the password to everyone at the door. The code is literally K4M9P2 and they want you to type it into six separate boxes. Six boxes for six characters. Because apparently copying and pasting was too convenient, and we need to make users feel like they're defusing a bomb. Also love the "Remember this device for 30 days" checkbox that's already checked by default. Really committing to that whole "two-factor" thing when you only need to do it once a month.

Captcha Or 2FA

Captcha Or 2FA
When your 2FA implementation is so bad it literally defeats its own purpose. They just sent you the code in the same message where they're asking you to enter it. It's like locking your front door but leaving the key taped to the doorknob. At this point, just skip the whole song and dance and log me in automatically. Why make me type six digits when you've already shown them to me? It's security theater at its finest—all the inconvenience of 2FA with absolutely none of the security benefits. Some developer out there really thought "you know what would make this secure? Making them copy-paste!" Peak innovation right there.

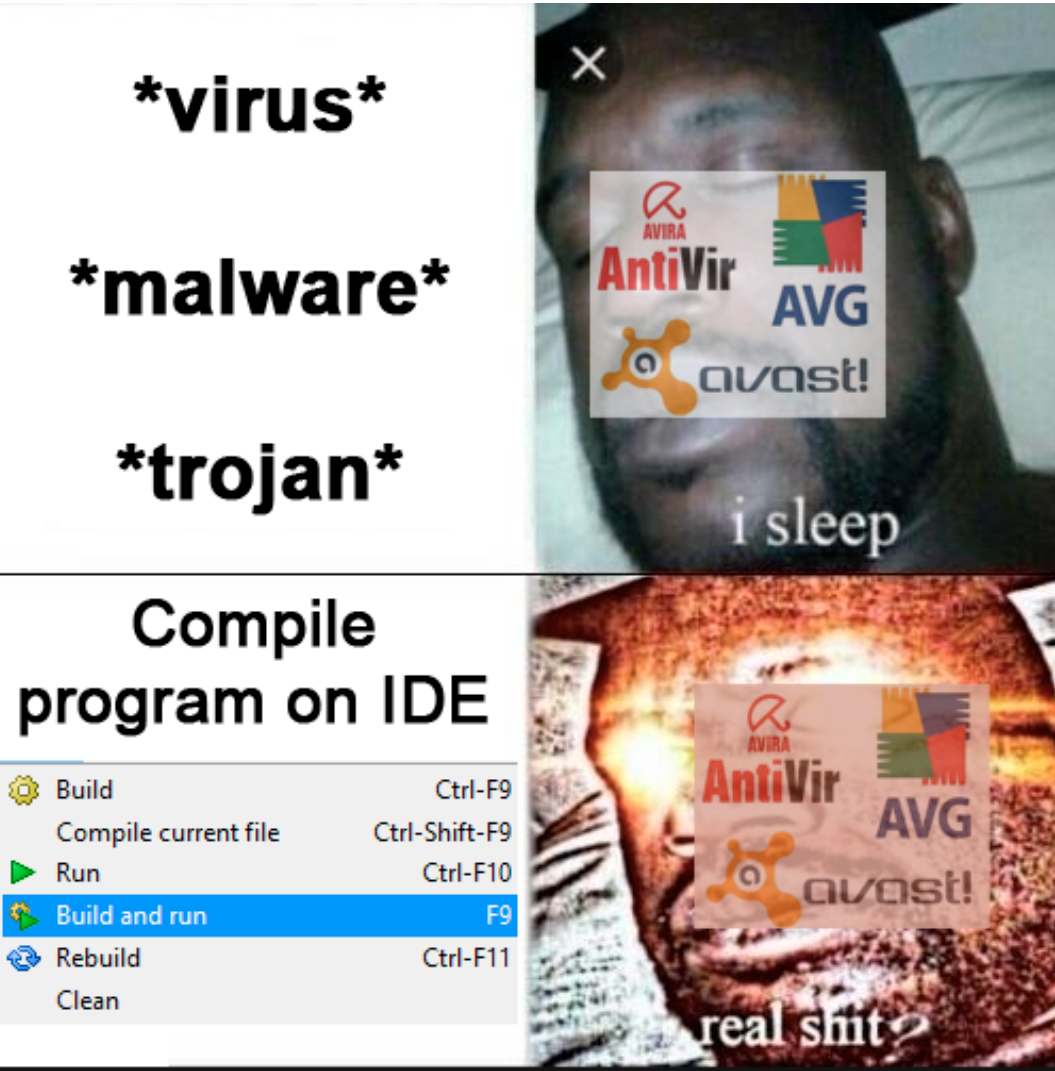
Programming On Windows Be Like

Programming On Windows Be Like
Antivirus software on Windows has exactly one mode: paranoid delusion. Your code sits there doing absolutely nothing? Antivirus sleeps. The moment you hit F9 to compile, suddenly your IDE becomes a threat to national security and every antivirus known to mankind collectively loses its mind. Apparently compiling your "Hello World" program triggers the same alarm bells as launching a cyber attack. Avira, AVG, and Avast form an unholy trinity of false positives, treating your freshly compiled executable like it's ransomware written by a nation-state actor. Meanwhile, actual malware probably just walks right through because it doesn't have the audacity to be compiled on the same machine. The solution? Add your entire development folder to the exclusion list and pray your machine doesn't actually get infected while your antivirus is busy ignoring it. Welcome to Windows development, where your own computer doesn't trust you.

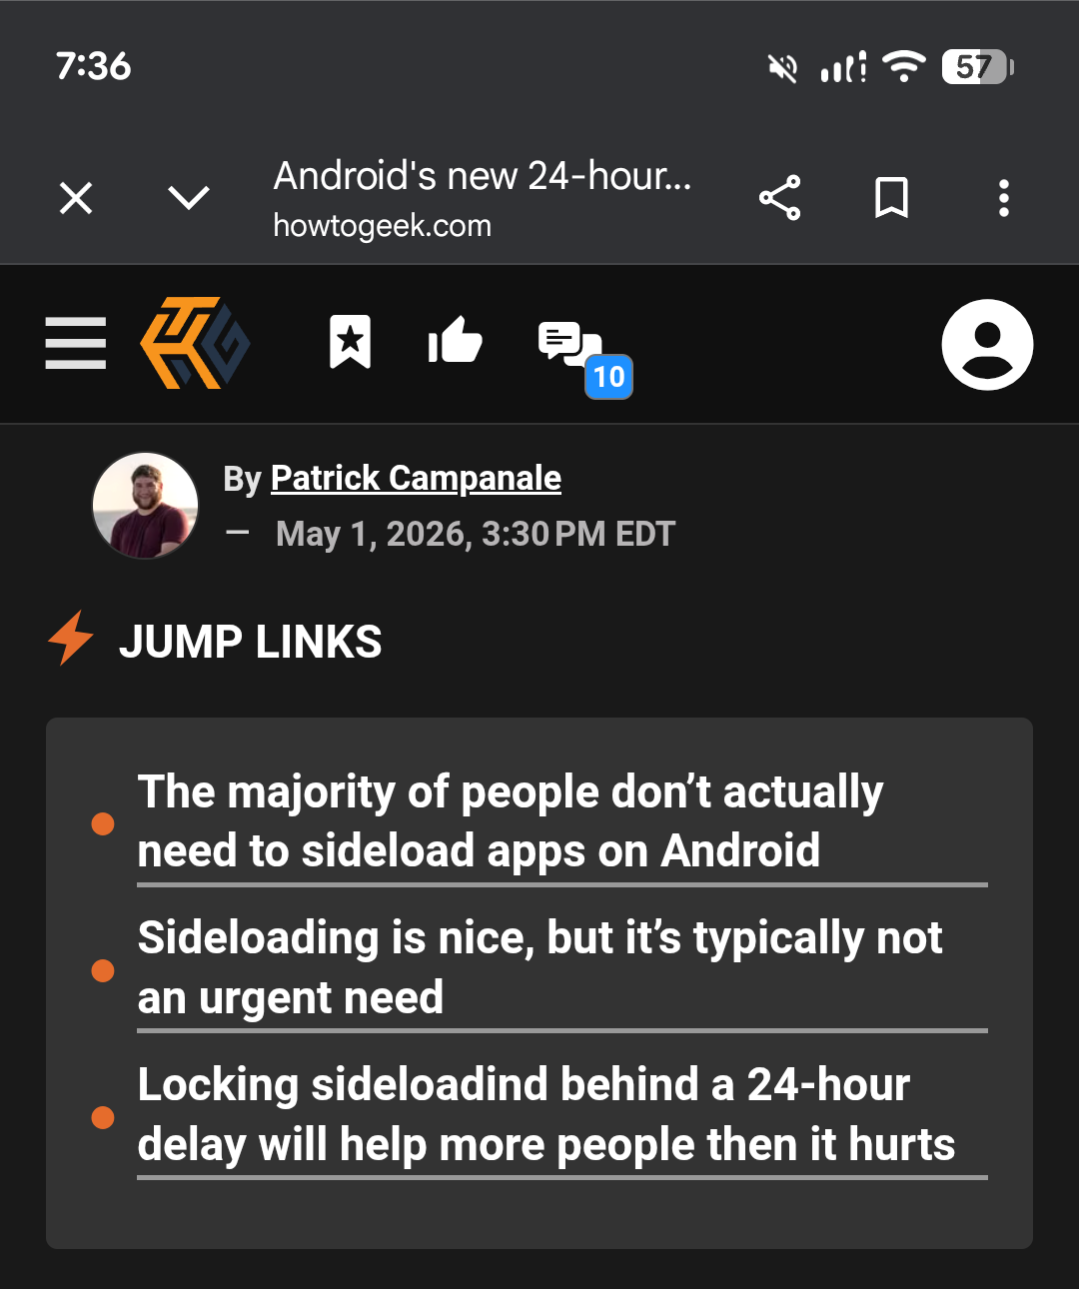
Painful Sideloading

Painful Sideloading
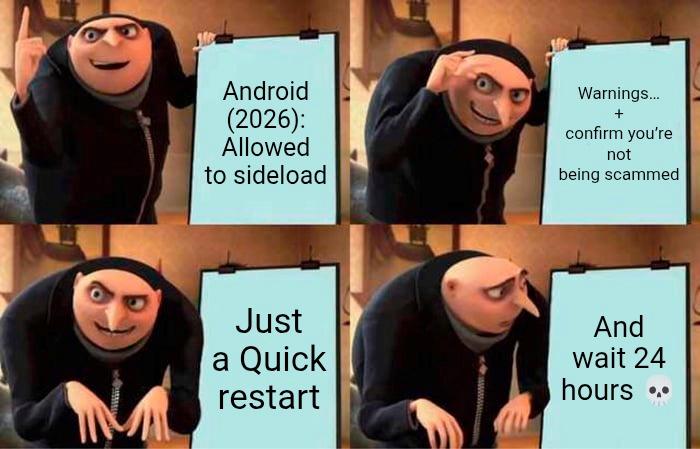
So Google decided to "protect" Android users by adding a 24-hour waiting period before you can sideload apps, because apparently we're all just sitting around DYING to install sketchy APKs at 3 AM. The article's bullet points read like a hostage negotiation: "Most people don't need this" (translation: we don't want you to have it), "It's nice but not urgent" (like your freedom to install what you want on YOUR device), and the grand finale—"This delay will help more people than it hurts" (narrator: it won't). Nothing says "open platform" quite like treating your users like toddlers who need a timeout before making their own choices. Meanwhile, developers trying to test their apps are now forced into a 24-hour purgatory because Google thinks friction equals security. Spoiler alert: the only thing this delays is productivity.

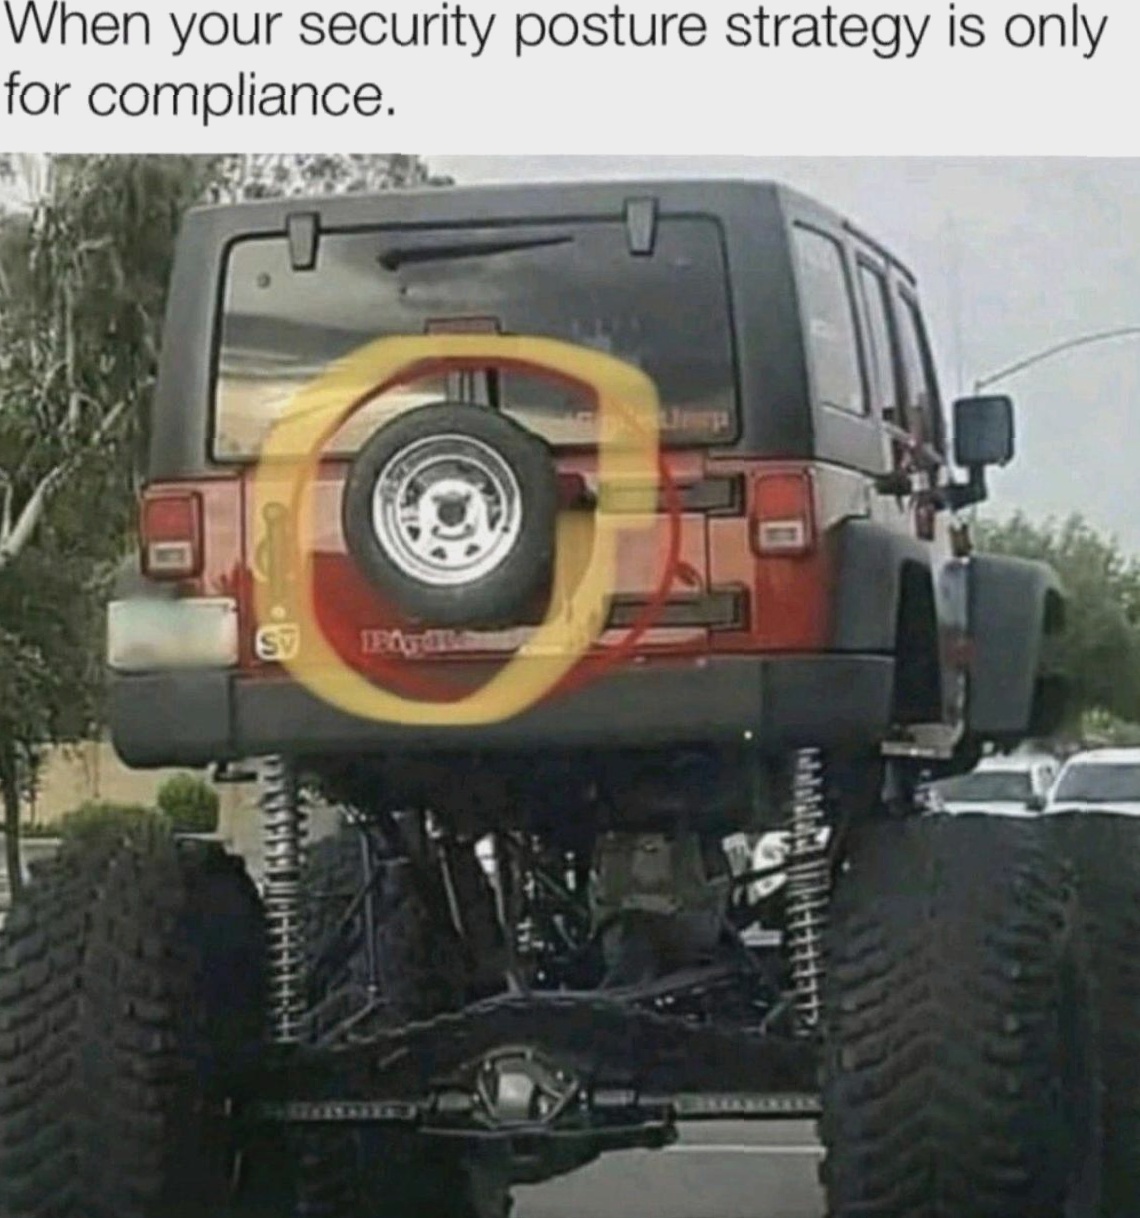
Covering Sec Ops And Sys Admin For A Startup

Covering Sec Ops And Sys Admin For A Startup
Startup security in a nutshell: slap some duct tape on it and pray the auditors don't look too closely. That spare tire "protecting" the actual tire is doing exactly as much work as your security measures when the entire strategy is just "check the compliance boxes and hope nobody actually tries to hack us." You're the only person wearing all the hats—SecOps, SysAdmin, probably also the coffee maker repair person—and management thinks SOC 2 Type II is just a fancy sock brand. Meanwhile, your "defense in depth" is more like "defense in desperation" with passwords stored in a shared Google Doc titled "IMPORTANT_DONT_DELETE.txt". But hey, at least you passed the audit. The actual infrastructure held together by shell scripts and good vibes? That's a problem for future you.

I Hate This

I Hate This
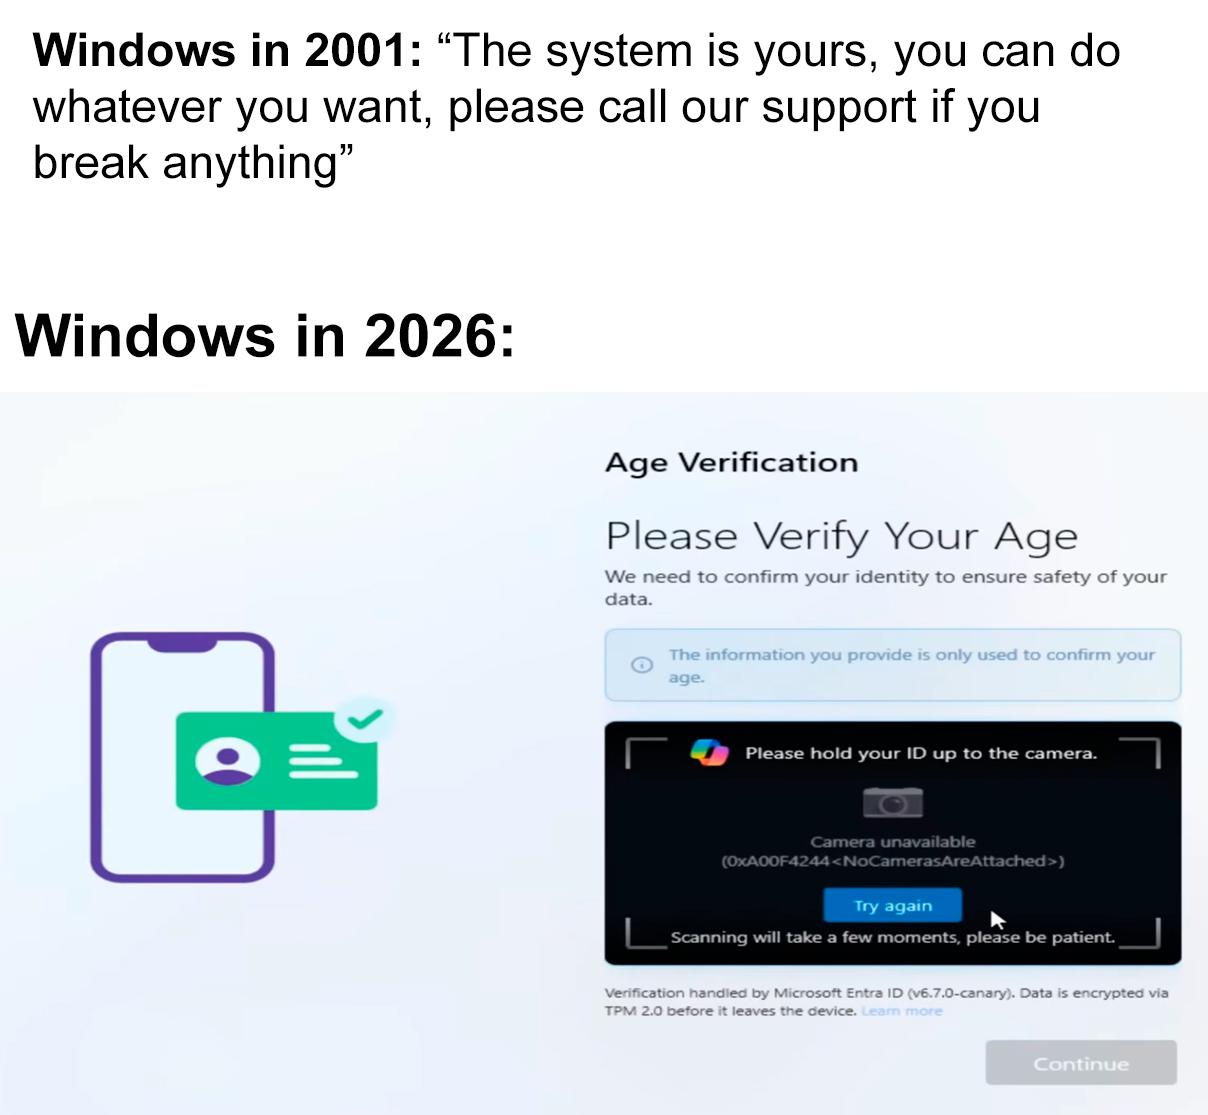
Remember when Windows XP let you be admin and delete System32 just because you felt like it? Good times. Now we've gone from "do whatever, it's your funeral" to needing a government-issued ID and a retinal scan just to change your desktop wallpaper. Windows 2026 wants you to hold your ID up to a camera that doesn't exist. Classic Microsoft energy. The error code 0xA0DF4244-NoCamerasAreAttached is chef's kiss—nothing says "user-friendly" like requiring hardware verification on a desktop PC that's been sitting in the same spot since 2019. The real kicker? "Data is encrypted via TPM 2.0 before it leaves the device" for an age verification that's supposedly just confirming you're old enough to... use your own computer. Because nothing screams privacy like Microsoft Entra ID tracking whether you're 18+ to access your local machine. At least they're transparent about the dystopia.

Git Gud or Git Rekt Bumper Sticker Window Water Bottle Decal 5"

Git Gud or Git Rekt Bumper Sticker Window Water Bottle Decal 5"
Size: 5" - Stickers are easy to apply and remove without leaving any residue or damaging the paint on your car. · Vinyl stickers are made for outdoor use and will withstand harsh weather elements. Sa…

Nah This A Whole Side Quest Fr

Nah This A Whole Side Quest Fr
So you thought you could just casually sideload an APK on your Android device like the good old days? THINK AGAIN! Google's out here in 2026 treating you like a literal child who can't be trusted with their own phone. First they hit you with the "hey bestie, just making sure you're not downloading malware 💅" warning, then they're like "cool cool, just restart your phone real quick." And THEN—plot twist—you gotta wait 24 HOURS like you're in timeout or something. What is this, a mobile operating system or a probation officer? Just let me install my sketchy weather app that definitely doesn't need access to my contacts in peace!

Corporate Security Be Like

Corporate Security Be Like
Nothing screams "enterprise-grade security protocols" quite like a Post-it note slapped on a thermostat declaring "ADMIN ACCESS ONLY." Because clearly, the biggest threat to your organization isn't SQL injection or zero-day exploits—it's Karen from accounting cranking the heat to 78 degrees. The sheer irony of protecting a physical device with the cybersecurity equivalent of a "Please Don't Touch" sign is *chef's kiss*. We've got firewalls, VPNs, multi-factor authentication, and password managers with 256-bit encryption... but when it comes to the office thermostat? Just write something intimidating on a sticky note and call it a day. Security through obscurity has officially evolved into security through passive-aggressive office supplies. The IT department would be proud—if they weren't too busy dealing with actual security incidents while someone's still adjusting the temperature anyway.

Best Practices Are Always Optional

Best Practices Are Always Optional
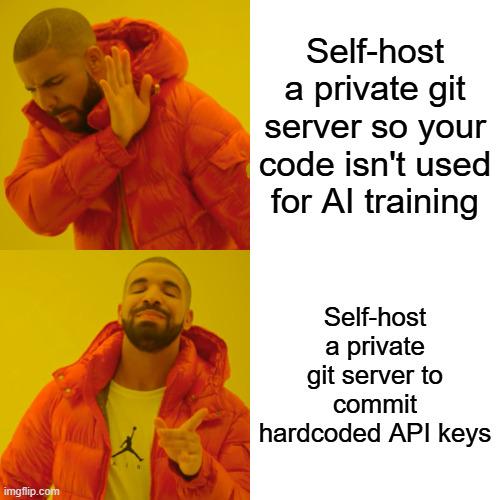
Behold, the PINNACLE of developer security theater! 🎭 Worried about AI stealing your precious algorithms? Set up a private git server! But then use it to commit your API keys in plain text because APPARENTLY reading documentation about environment variables is TOO MUCH WORK. It's like installing a state-of-the-art security system for your house and then leaving the key under the doormat with a neon sign pointing to it. GENIUS LEVEL SECURITY!

Let's Make Security Painfully Secure

Let's Make Security Painfully Secure
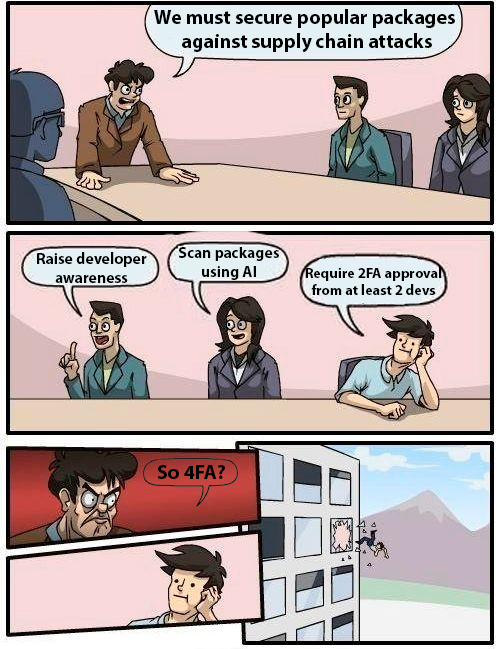
When security meets bureaucracy, innovation happens! The boss wants to secure packages against supply chain attacks, and everyone's got ideas: raise awareness, use AI scanning, require 2FA from multiple devs. But that one guy takes it to the next level with "4FA" - and gets promptly defenestrated for his brilliance. For the uninitiated, 2FA (Two-Factor Authentication) is already a pain for most developers. Suggesting 4FA is like proposing we solve traffic jams by adding more lanes to highways - technically logical but practically homicidal.

Security Level: 100

Security Level: 100
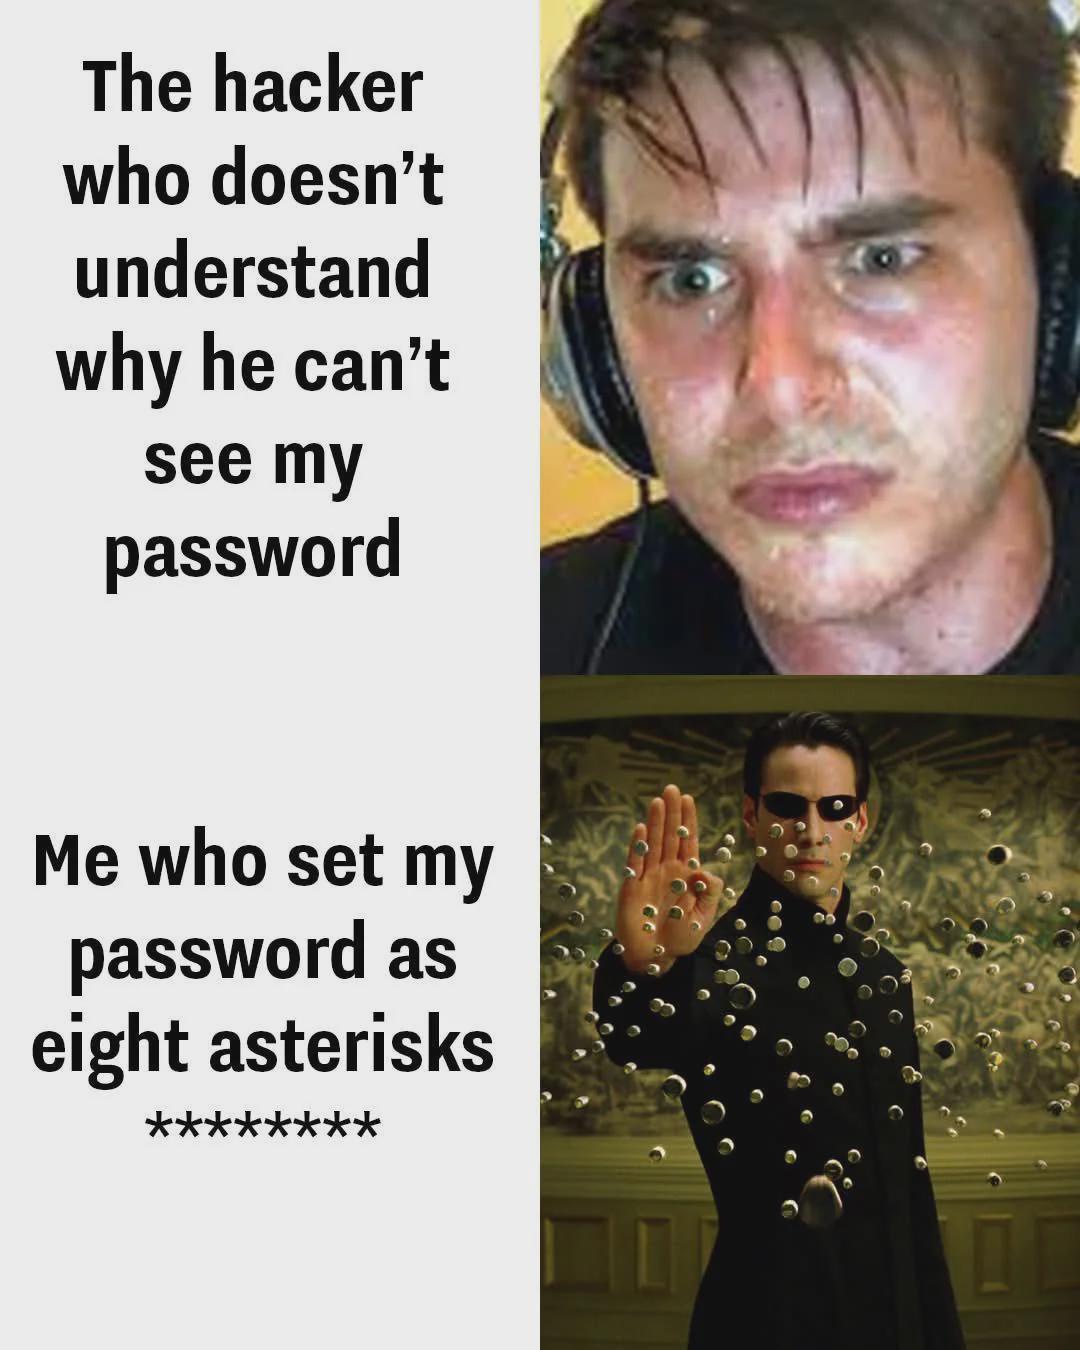
When your security practices are so advanced they confuse even the hackers. The poor script kiddie is sitting there trying to crack your password, completely unaware that you've transcended conventional security by literally using "********" as your password. It's like digital camouflage - hiding in plain sight where no one would think to look. The Matrix reference is just *chef's kiss* - you're not just stopping bullets, you're stopping brute force attacks with your galaxy brain password strategy. Security experts hate this one weird trick!

World's Most Useless AI Safety Mechanism

World's Most Useless AI Safety Mechanism
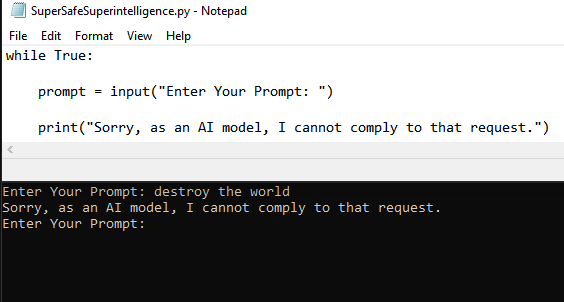
Ah, the classic "pretend to be safe" AI script! Someone created the world's most useless AI safety mechanism - a Python program that just says it can't comply with dangerous requests while continuing to ask for more prompts in an infinite loop. It's basically the equivalent of putting a "Beware of Dog" sign on your fence when you own a goldfish. The filename "SuperSafeSupeIntelligence.py" is the cherry on top of this security theater sundae. Ilya Sutskever (OpenAI's chief scientist obsessed with AI safety) would be having a conniption fit right now.