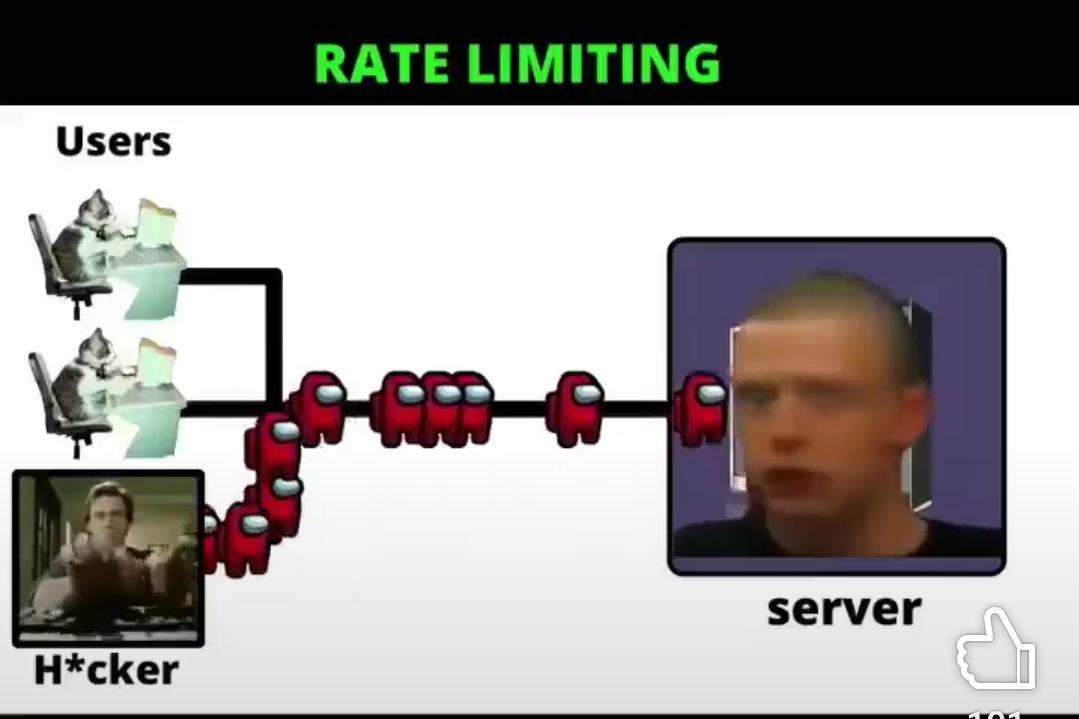
Rate limiting is like having a bouncer at your API's nightclub. The regular users are just chilling, casually making requests at a reasonable pace. Meanwhile, the hacker is absolutely spamming requests like they're trying to DDoS your server into oblivion. But here's the beautiful part: rate limiting creates this orderly queue of Among Us crewmates, forcing even the most aggressive attacker to wait in line like everyone else. The server's just standing there, slightly annoyed but handling it, while the hacker's furious attempt to overwhelm the system gets politely throttled into submission. It's the digital equivalent of "sir, please take a number." Fun fact: Most APIs implement rate limiting using algorithms like token bucket or leaky bucket. Twitter's API, for example, limits you to 300 requests per 15-minute window for certain endpoints. Try to go faster? You get a nice 429 "Too Many Requests" response and a timeout. Take that, script kiddies.