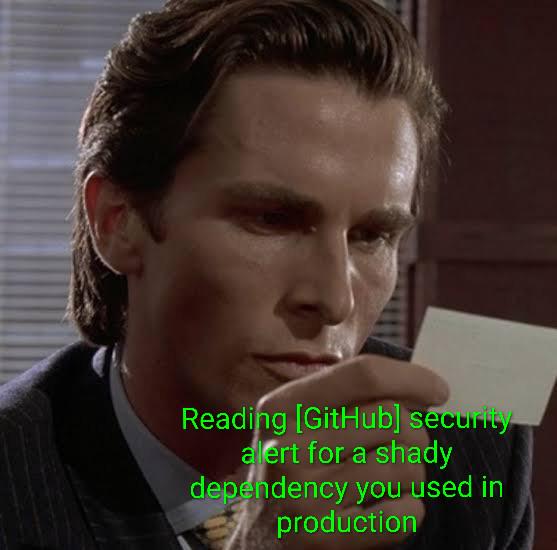
You know that look when someone's about to drop some devastating news but they're trying to stay professional about it? That's exactly what reading a Dependabot security alert feels like. You're just minding your business, sipping your coffee, and GitHub casually slides into your notifications like "Hey buddy, remember that npm package you installed 6 months ago and forgot about? Yeah, turns out it has a critical vulnerability and it's been running in production this whole time. No pressure though!" The best part? It's always some obscure transitive dependency you've never even heard of, nested 47 levels deep in your node_modules. You didn't choose it, you didn't even know it existed, but now you're responsible for fixing it before the next security audit. And of course, updating it breaks three other things because semantic versioning is more like a suggestion than a rule. Fun fact: Dependabot was acquired by GitHub in 2019 and has since become the passive-aggressive security conscience of every developer's workflow. It's like having a very polite robot constantly reminding you of your poor life choices in dependency management.
 AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud