ssh Memes

Begin Privatekey

Begin Privatekey
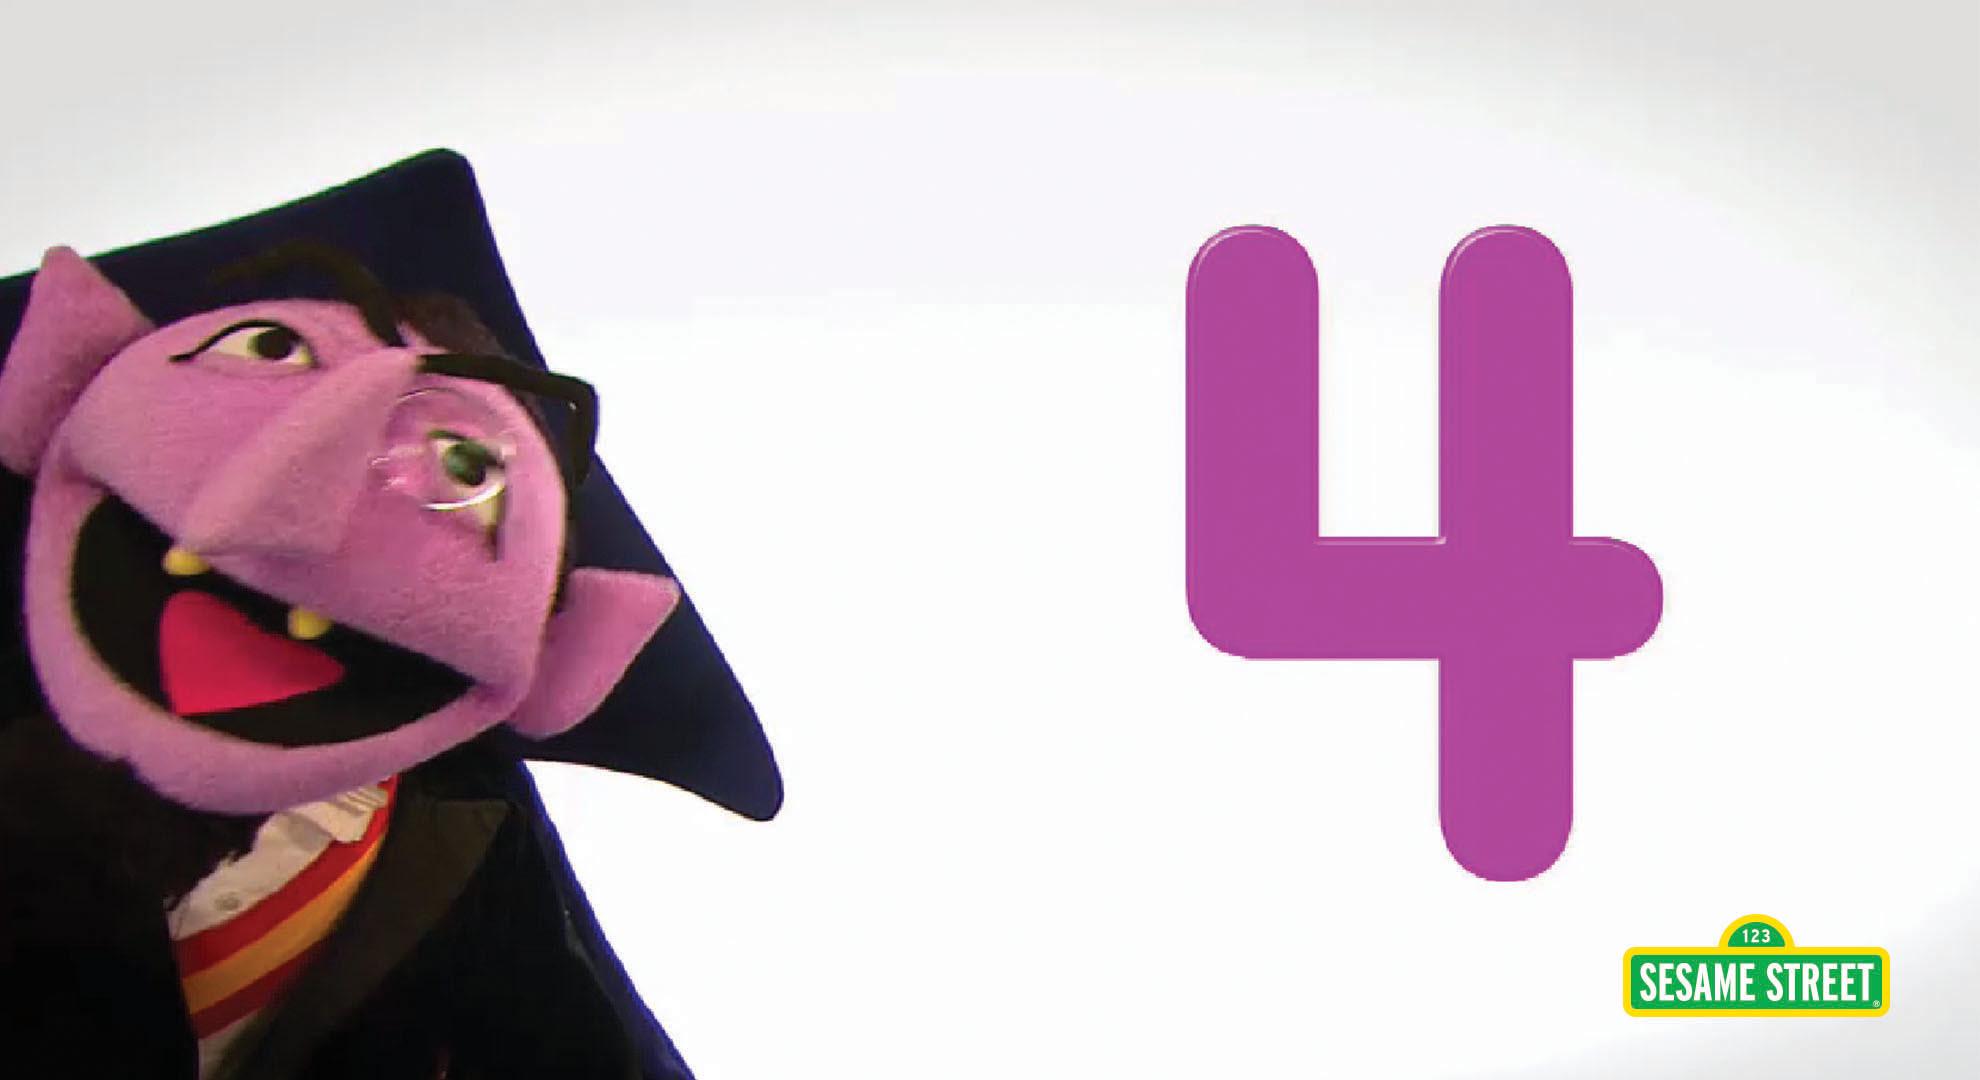
When you're setting up SSH keys or SSL certificates and you see that beautiful "-----BEGIN PRIVATE KEY-----" header, it hits different. The Count from Sesame Street teaching kids to count the number 4 becomes a perfect metaphor for developers proudly displaying their private keys in public repos, Slack channels, or—my personal favorite—hardcoded in the frontend JavaScript. The joke writes itself: "One private key committed to GitHub! Two private keys in the .env file! Three private keys in the Docker image! Four private keys leaked to production! Ah ah ah!" Meanwhile, security teams everywhere are having aneurysms. Fun fact: GitHub scans for accidentally committed credentials and will actually send you a notification faster than your CI/CD pipeline can deploy. They've probably prevented more breaches than all the security training videos combined.

Things To Say In A Job Interview

Things To Say In A Job Interview
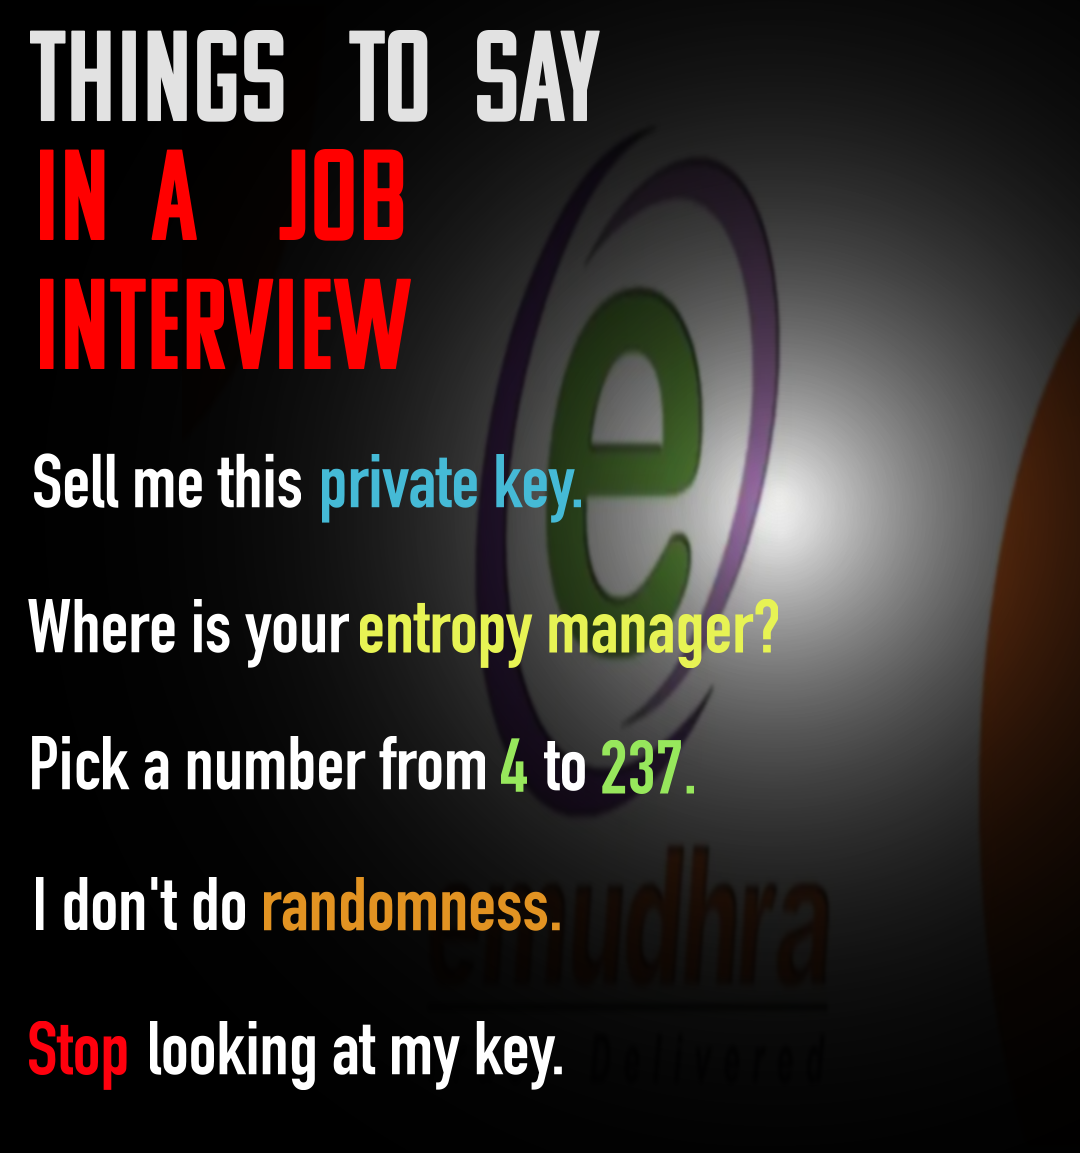
A comprehensive guide to getting immediately escorted out of any tech interview. "Sell me this private key" is the cryptographic equivalent of showing up to a bank interview and offering to sell them their own vault combination. "Where is your entropy manager?" - bold assumption that the company has their randomness organized when most can't even organize their Jira tickets. The number range 4 to 237 is oddly specific and perfectly captures the arbitrary constraints of bad RNG implementations. "I don't do randomness" - congratulations, you've just disqualified yourself from literally every security-related position. And finally, "Stop looking at my key" while presumably having your SSH private key visible on your screen is the cherry on top of this disaster sundae. Pro tip: if you need to say this during an interview, you've already failed the security clearance.

Private Key

Private Key
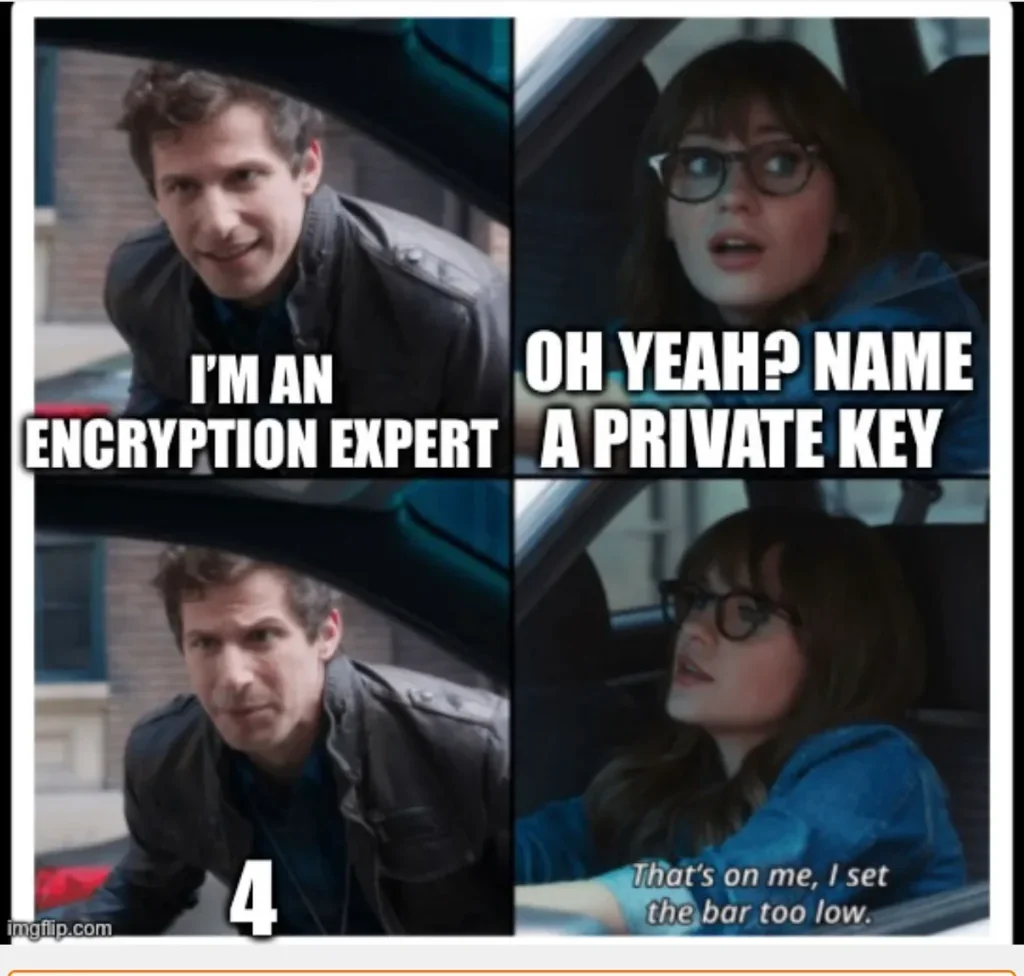
Every "encryption expert" until someone asks them to actually name a single private key they know. Turns out most of us just copy-paste from the .pem file and pray it works. The beauty of modern cryptography is that you can be an expert without actually knowing any of your keys—they're all just blobs of base64 nonsense living rent-free in your ~/.ssh folder. Setting the bar at "name 4 private keys" is like asking a chef to name 4 individual grains of rice in their pantry.

That's The Stupidest Combination I've Ever Heard In My Life!

That's The Stupidest Combination I've Ever Heard In My Life!
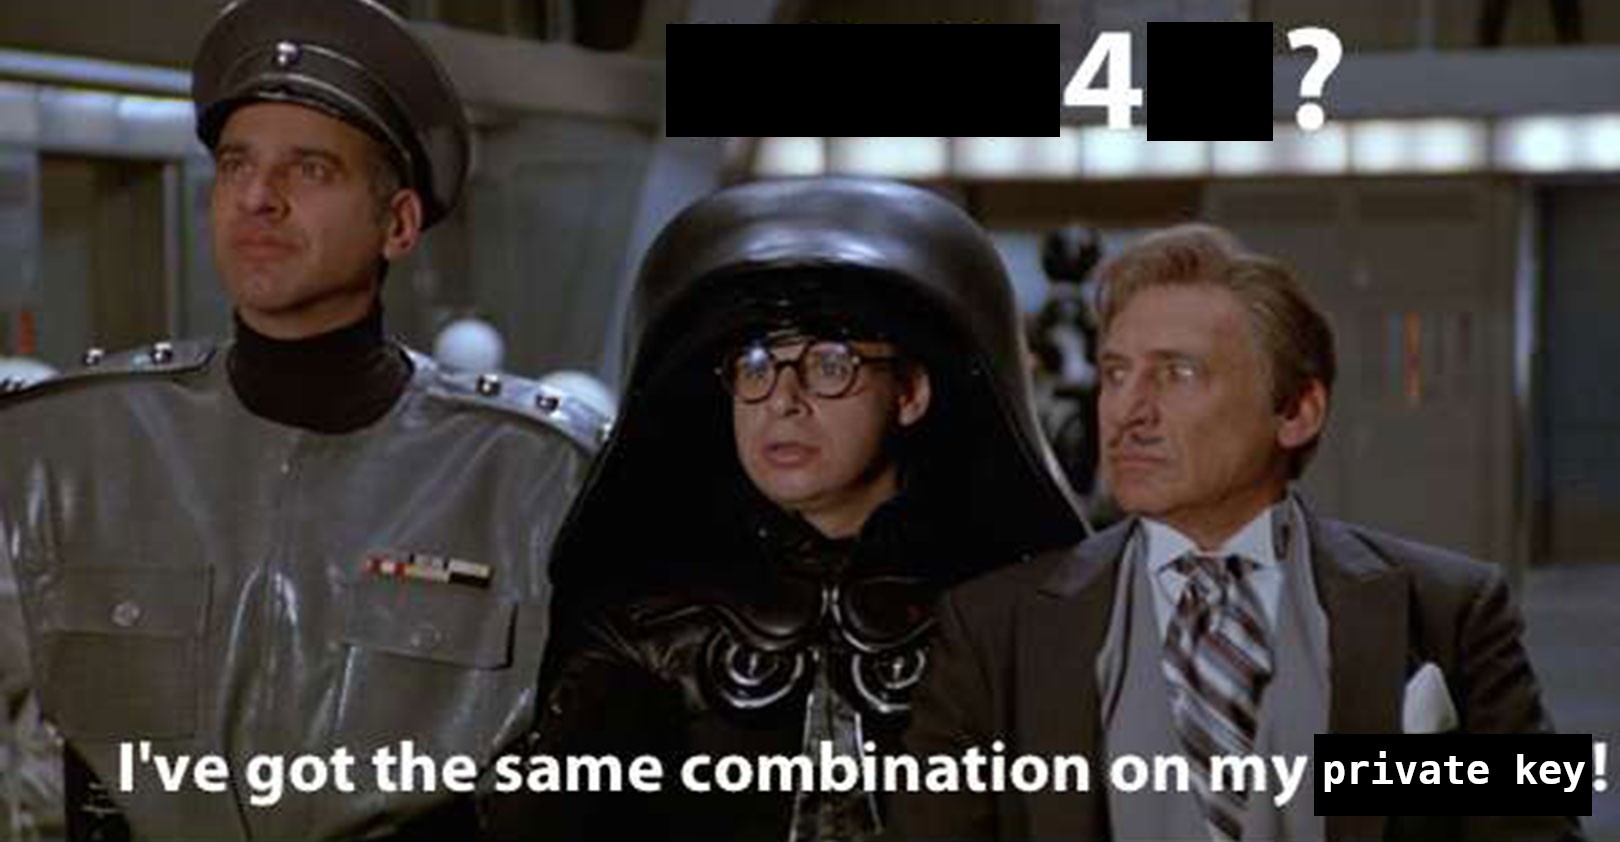
When your password is "1234" but you're storing your SSH private key with the same passphrase. Nothing screams "I understand security" quite like protecting your cryptographic credentials with the same combination an idiot would have on their luggage. The real kicker? Half the devs reading this just nervously glanced at their ~/.ssh/id_rsa file. And the other half? They don't even use a passphrase. At least President Skroob here had the decency to try . Pro tip: If your private key passphrase is something you'd use to unlock your phone, you might as well just commit it to the public repo and save everyone some time.

Drop ALT Mechanical Keyboard — 65% (67 Key) Gaming Keyboard, Hot-Swap Switches, Programmable Macros, RGB LED Backlighting, USB-C, Doubleshot PBT, Aluminum Frame (Barebones, Gray)

Drop ALT Mechanical Keyboard — 65% (67 Key) Gaming Keyboard, Hot-Swap Switches, Programmable Macros, RGB LED Backlighting, USB-C, Doubleshot PBT, Aluminum Frame (Barebones, Gray)
A COMPACT LAYOUT: The ALT mechanical keyboard is a smaller take on Drop’s CTRL model. It features 67 keys instead of 87. Absent of function keys, it wastes no space—but it still has a full set of arr…

Gitignore Is My Best Friend

Gitignore Is My Best Friend
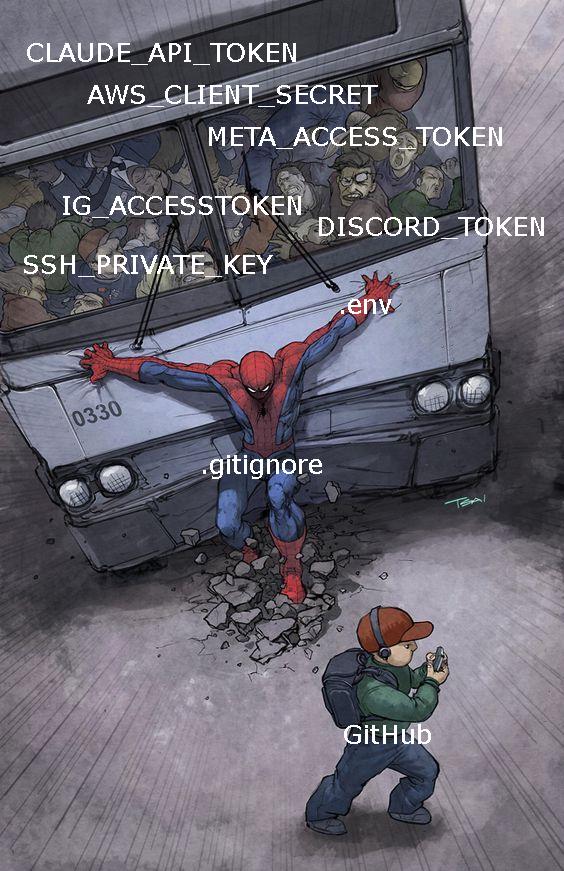
Every developer's worst nightmare: accidentally committing your entire collection of API keys and secrets to a public repo. Here we see .gitignore heroically holding back the flood of credentials that would get your AWS bill to five figures and your security team scheduling an "urgent meeting." The .env file is chilling right there with .gitignore because they're basically besties in the "keeping you employed" department. Meanwhile GitHub is just waiting below like a hungry void, ready to index your secrets and have bots scraping them within 30 seconds of pushing. Pro tip: That SSH_PRIVATE_KEY in the image? Yeah, if that ever touches GitHub, you might as well just hand over your server keys to every script kiddie on the internet. Your .gitignore file is literally the only thing standing between you and a very awkward Slack message from DevOps.

I Love Fun Quizzes Like This. Let's All Share!

I Love Fun Quizzes Like This. Let's All Share!
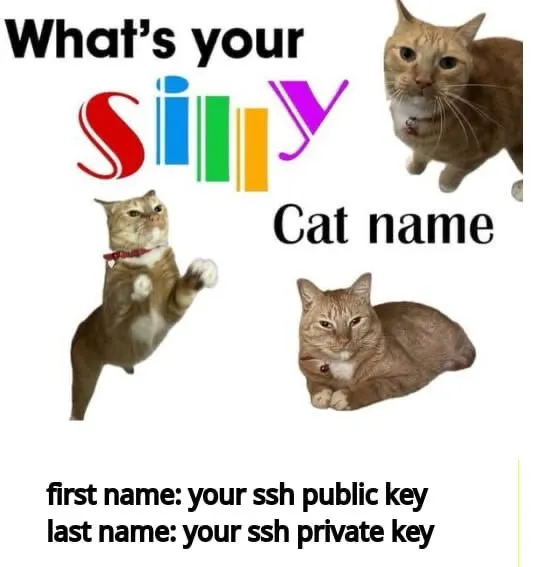
Nothing says "please hack me" quite like a wholesome cat name quiz that asks for your SSH keys. Because why wouldn't you share the cryptographic credentials that grant root access to your entire infrastructure? The cats look so trustworthy! This is basically the security awareness training version of those "your stripper name is your credit card number + CVV" posts. Except instead of identity theft, you're handing over the literal keys to your kingdom. At least when your servers get compromised, you can tell your boss it was for a really cute cat meme. Pro tip: If your SSH key actually makes a good cat name, you've got bigger problems than social engineering attacks.

Tmux My Beloved

Tmux My Beloved
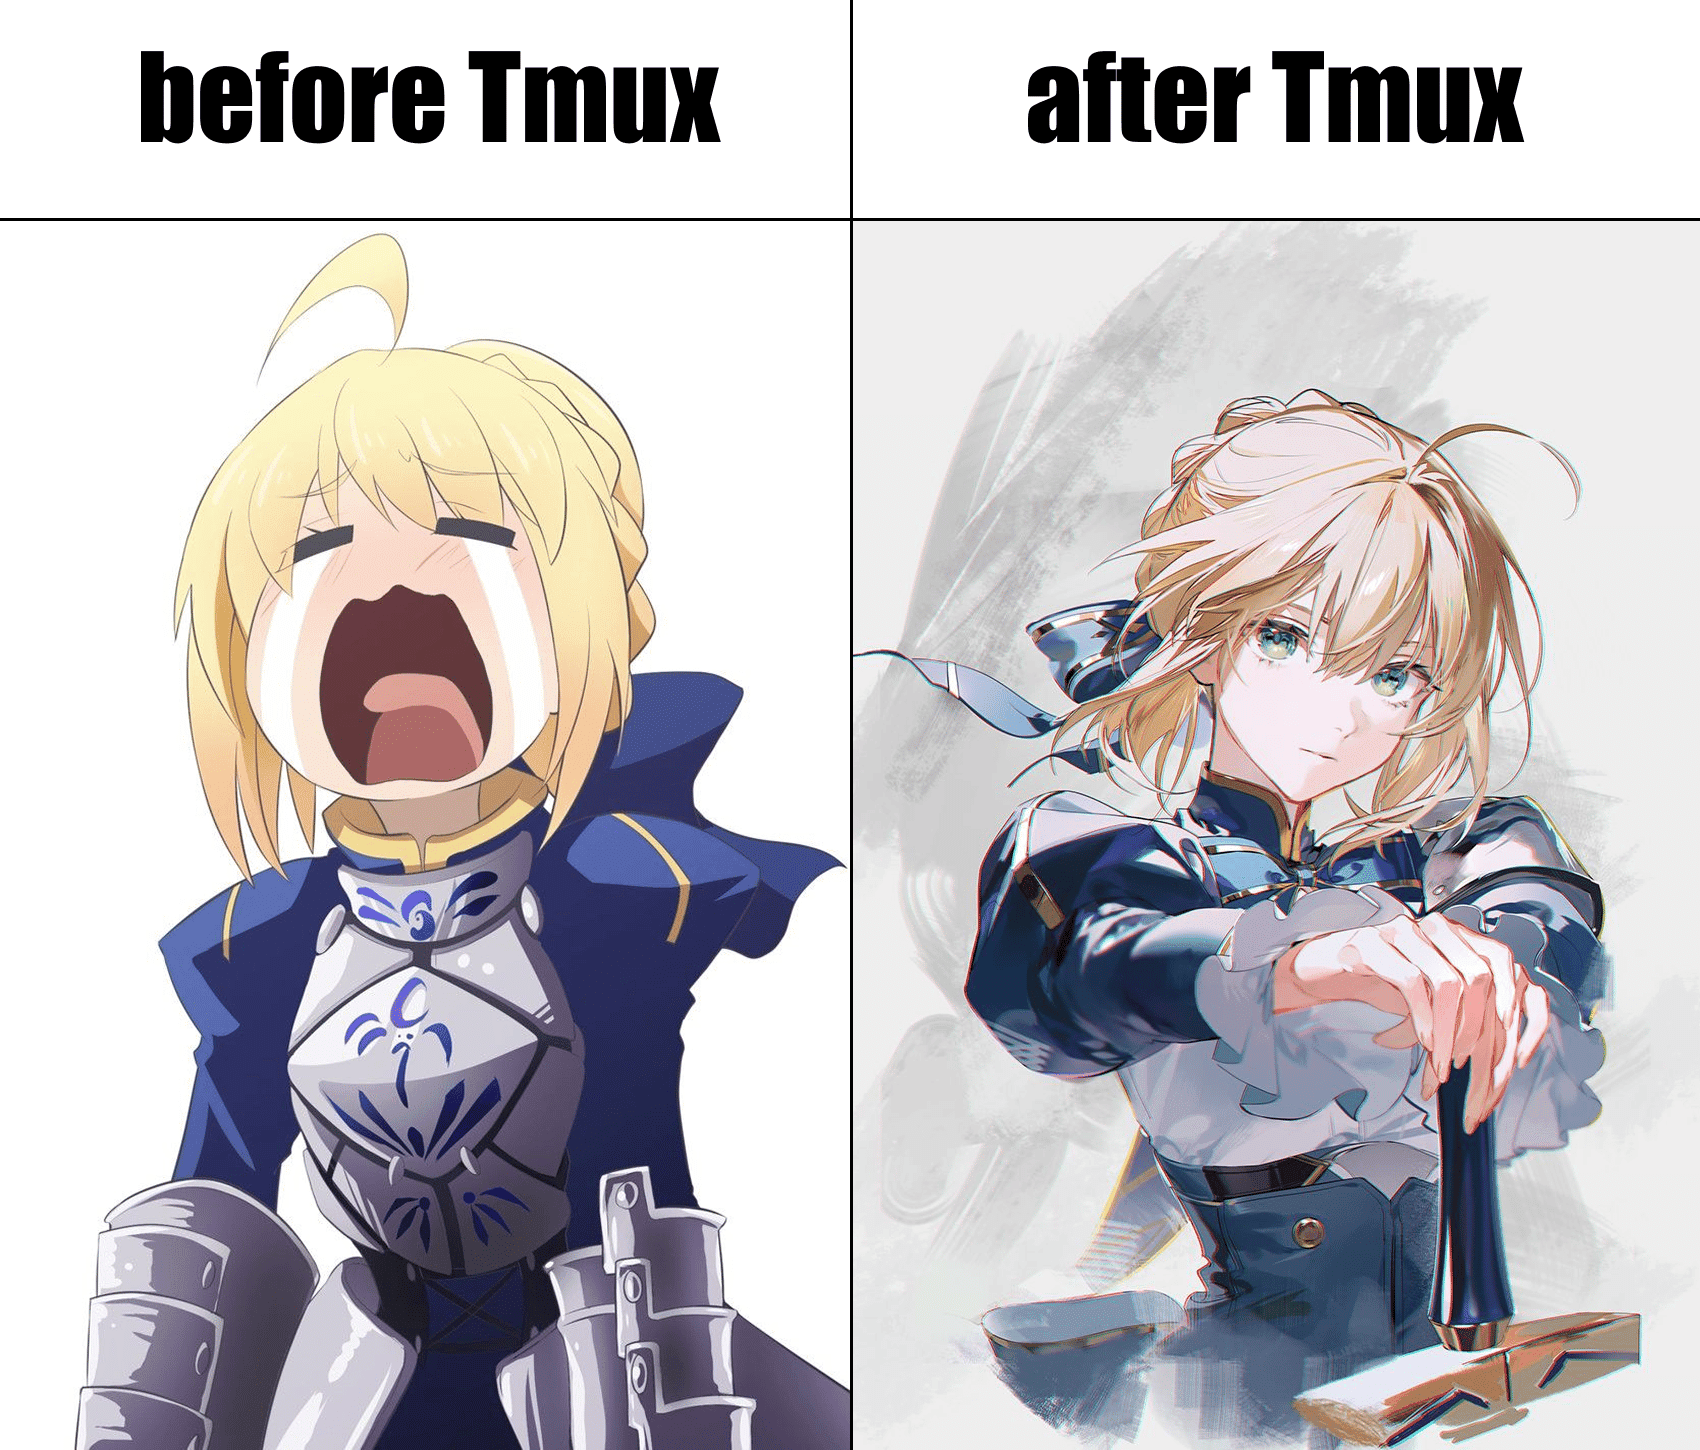
You know you've ascended to a higher plane of existence when your terminal workflow goes from chaotic screaming to serene elegance. Before tmux, you're juggling 47 terminal windows, accidentally closing the one running your production deploy, and generally living in a state of panic. After tmux? You're splitting panes like a zen master, detaching sessions like you're Neo dodging bullets, and smugly watching your SSH connection drop while your processes keep running in the background. The transformation from terminal peasant to terminal aristocrat is real. You go from "wait which window was that in" to casually prefix-c'ing new windows while maintaining perfect composure. Your coworkers still using multiple terminal tabs? They wouldn't understand this level of enlightenment.

Any One Using This Key

Any One Using This Key
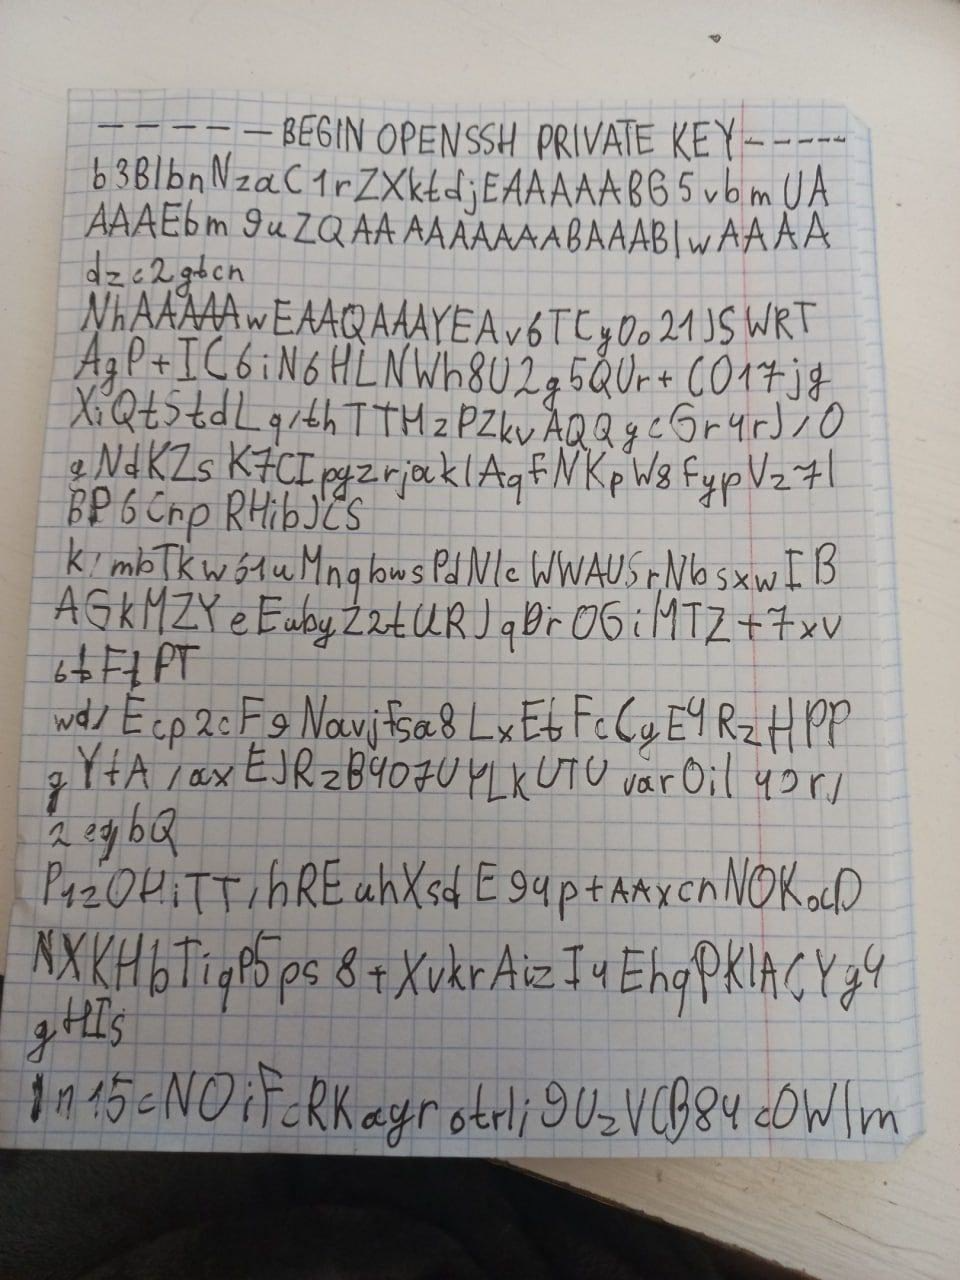
Someone actually hand-wrote their OpenSSH private key on paper. Let that sink in. The same key that's supposed to be kept secret, never shared, and definitely never exposed to human eyes for more than a millisecond is now immortalized on graph paper like it's a high school math assignment. This is either the most paranoid backup strategy ever conceived (EMP-proof! Ransomware-proof! Works during the apocalypse!) or someone fundamentally misunderstood the "write it down somewhere safe" advice. Either way, I'm impressed by the dedication to transcribing hundreds of random characters by hand. The real question is: did they actually verify it character by character, or is this just an elaborate piece of security theater? Pro tip: If you ever need to restore from this backup, good luck distinguishing between that lowercase 'l', uppercase 'I', and the number '1'. Your SSH connection will be rejecting you faster than a senior dev rejecting a PR with no tests.

Begin Private Key

Begin Private Key
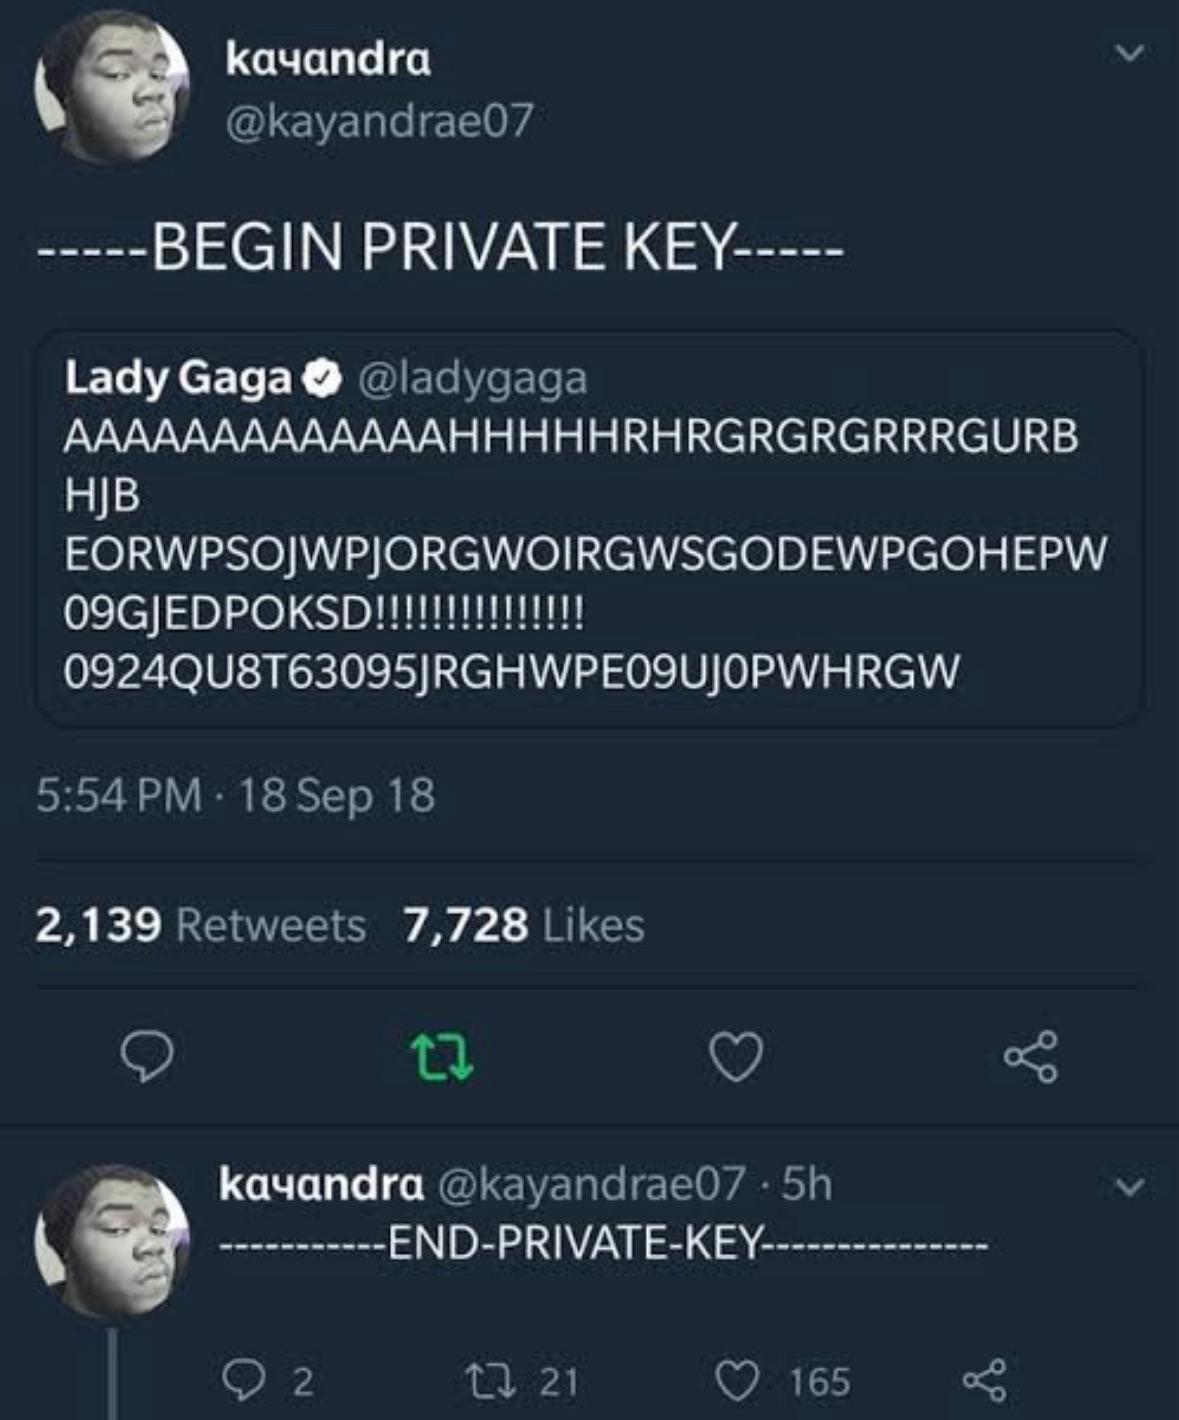
Someone just turned Lady Gaga's entire discography into their SSH key. The beauty here is that private keys in PEM format literally start with "-----BEGIN PRIVATE KEY-----" and end with "-----END PRIVATE KEY-----", so naturally, any chaotic celebrity tweet becomes cryptographic gold. What makes this chef's kiss is that Lady Gaga's keyboard smash looks MORE legitimate than most actual private keys. The excessive exclamation marks? Perfect entropy. The random capitalization? Enhanced security through unpredictability. This is basically what happens when performance art meets RSA encryption. Security experts are probably having an aneurysm seeing a "private key" posted publicly with 7,728 likes. But hey, at least it's not someone's actual AWS credentials on GitHub... for the third time this week.

CafePress It Works On My Machine Mug 11 oz (325 ml) Ceramic Coffee Mug

CafePress It Works On My Machine Mug 11 oz (325 ml) Ceramic Coffee Mug
Dimensions: Our standard size 11 oz mug measures 3.75" tall x 3" in diameter · Color Coordinate: Mix and match your hot cocoa mugs with your decor by choosing from the following interior and handle c…

The Public Private Key Paradox

The Public Private Key Paradox
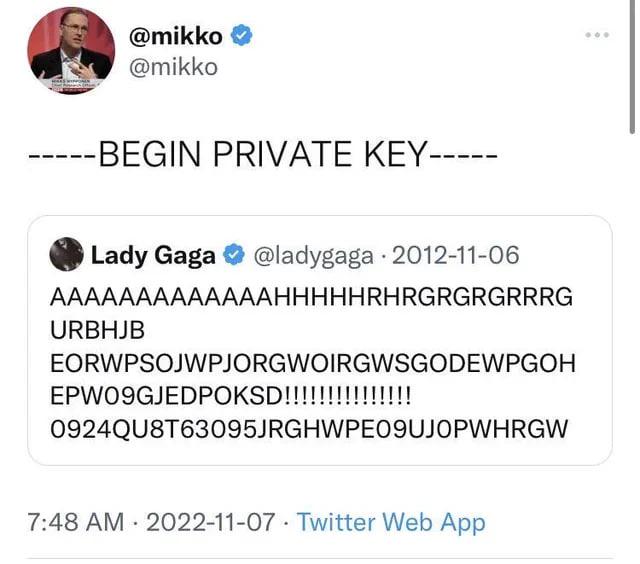
The greatest cryptographic catastrophe of our time! Someone just mistook Lady Gaga's keyboard-smashing tweet from 2012 as their private SSH key and posted it publicly with the "BEGIN PRIVATE KEY" header. That's like leaving your house key under a doormat labeled "DEFINITELY NOT A KEY HERE." Any security engineer seeing this is simultaneously laughing and having heart palpitations. The irony of labeling something as private while broadcasting it to the entire internet is just *chef's kiss* perfect.

She Should Be Embarrassed

She Should Be Embarrassed
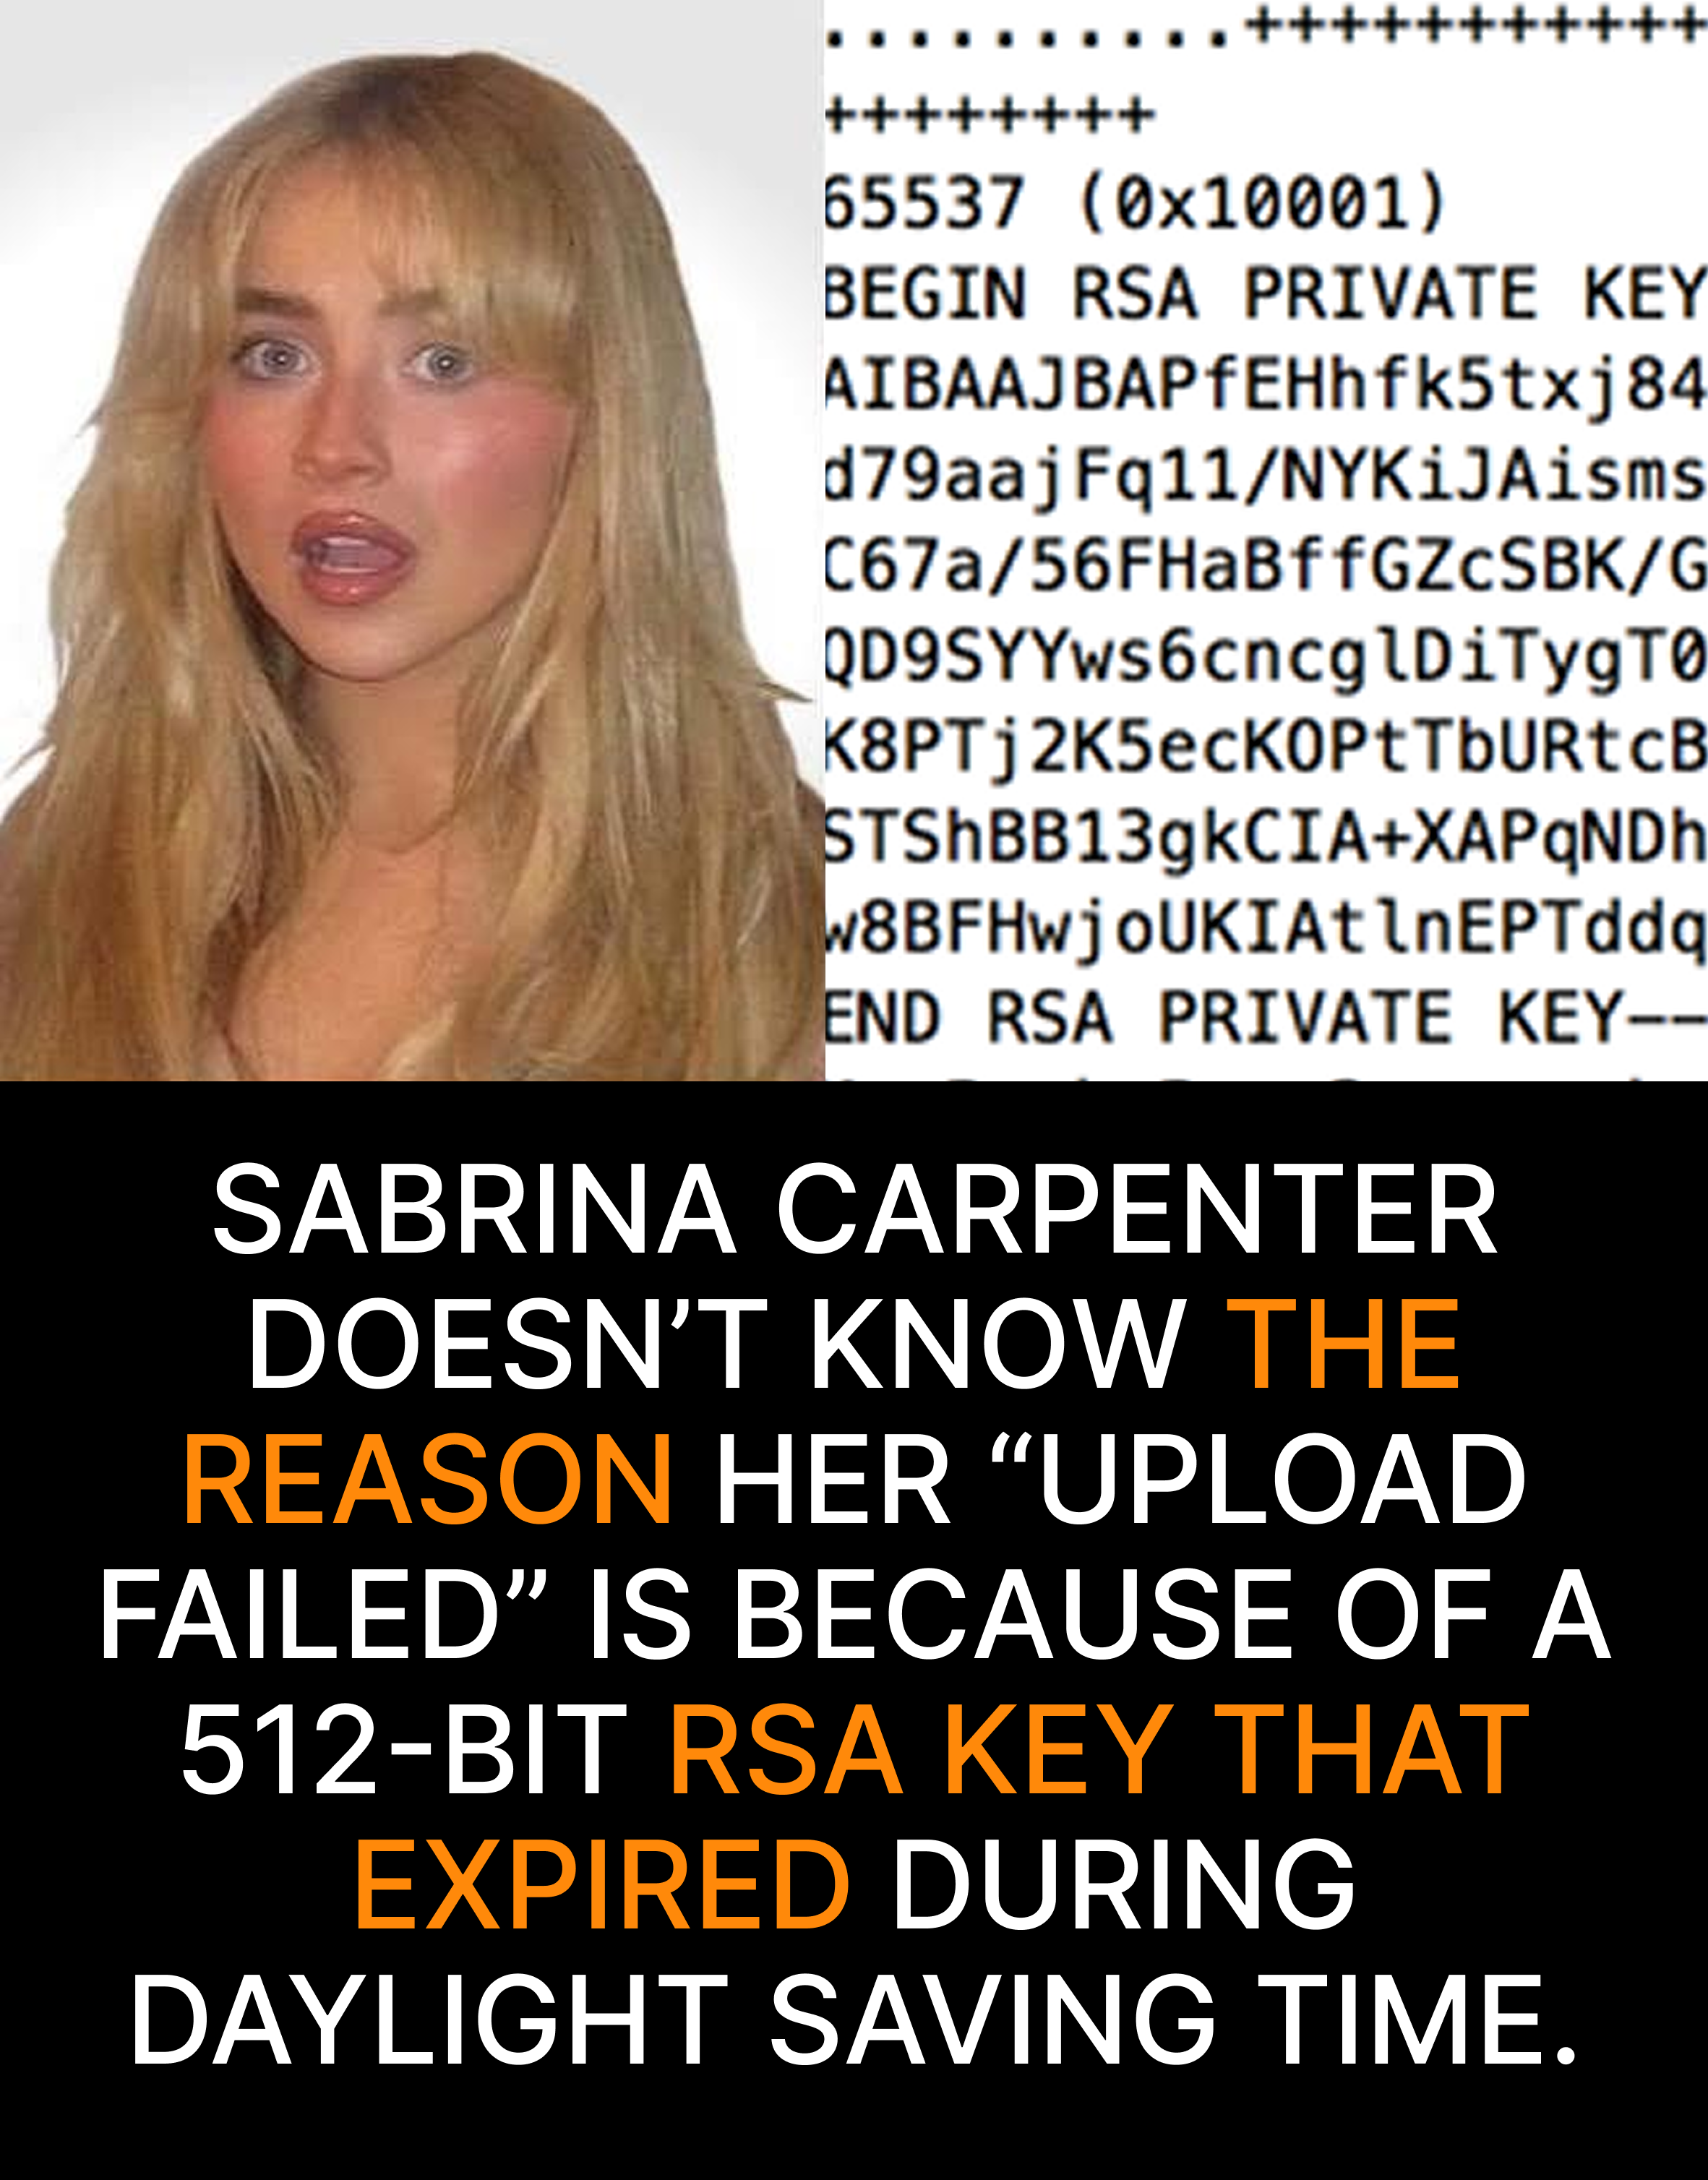
Ah yes, the classic "my encryption key expired because of daylight saving time" excuse. That's like blaming your missing semicolons on Mercury being in retrograde. For the uninitiated, RSA keys don't actually "expire" due to time changes—they're cryptographic keys, not yogurt. And that shocked expression is exactly how security engineers look when someone suggests their SSH connection failed because their 512-bit key (already dangerously outdated) somehow got confused by the clocks changing. Next time your upload fails, just admit you tried to push directly to production at 4:59 PM on a Friday. We've all been there.

Software Dev Salary

Software Dev Salary
Content Senior Dev: "just SSH into prod and run it live"