security Memes

Never Use URL Shorteners

Never Use URL Shorteners
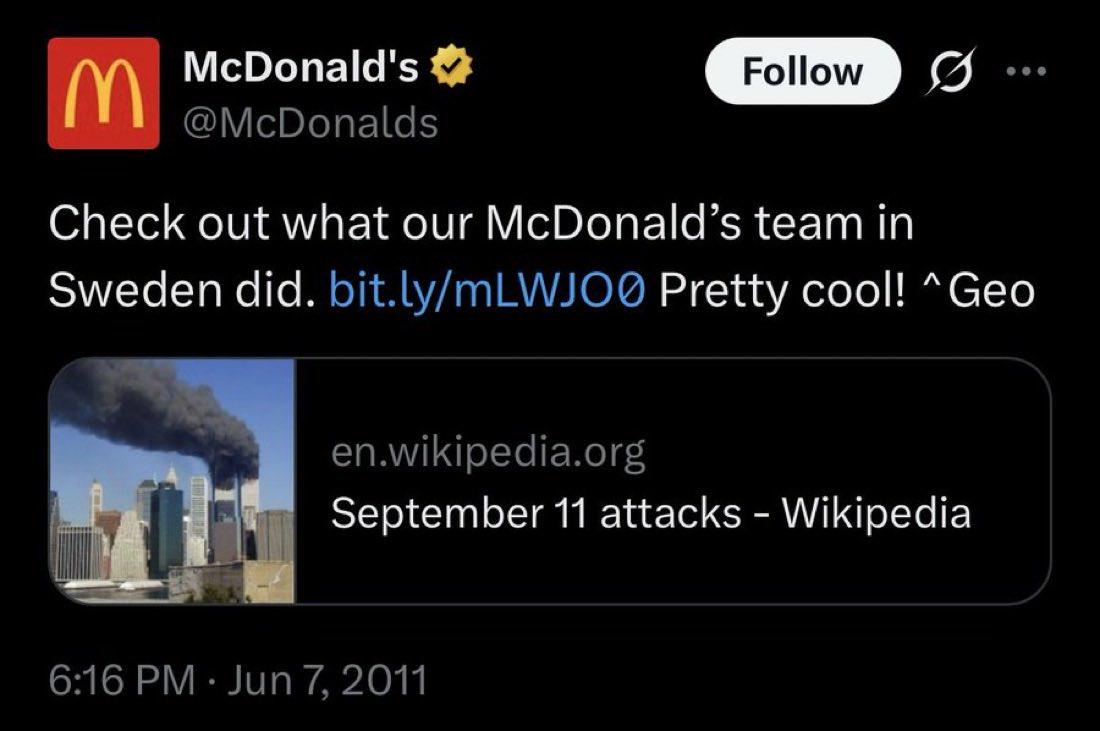
Someone on McDonald's social media team learned a valuable lesson about URL shorteners the hard way. They cheerfully posted a bit.ly link expecting to showcase their Sweden team's cool project, but the shortened URL redirected to the September 11 attacks Wikipedia page instead. Talk about a PR nightmare served with a side of fries. The problem with URL shorteners? They're basically pointers that can be hijacked, expired, or redirected to literally anything. You're trusting a third-party service to maintain that mapping forever, which is like deploying to production without version control—eventually something catastrophic will happen. In this case, either the link expired and got reassigned, or someone maliciously changed the redirect. Either way, McDonald's just associated their brand with one of history's darkest days. Pro tip: If you're a major corporation, spend the extra characters and use full URLs. Your marketing team will thank you, and you won't accidentally become a case study in "What Not To Do on Social Media 101."

They Are Back

They Are Back
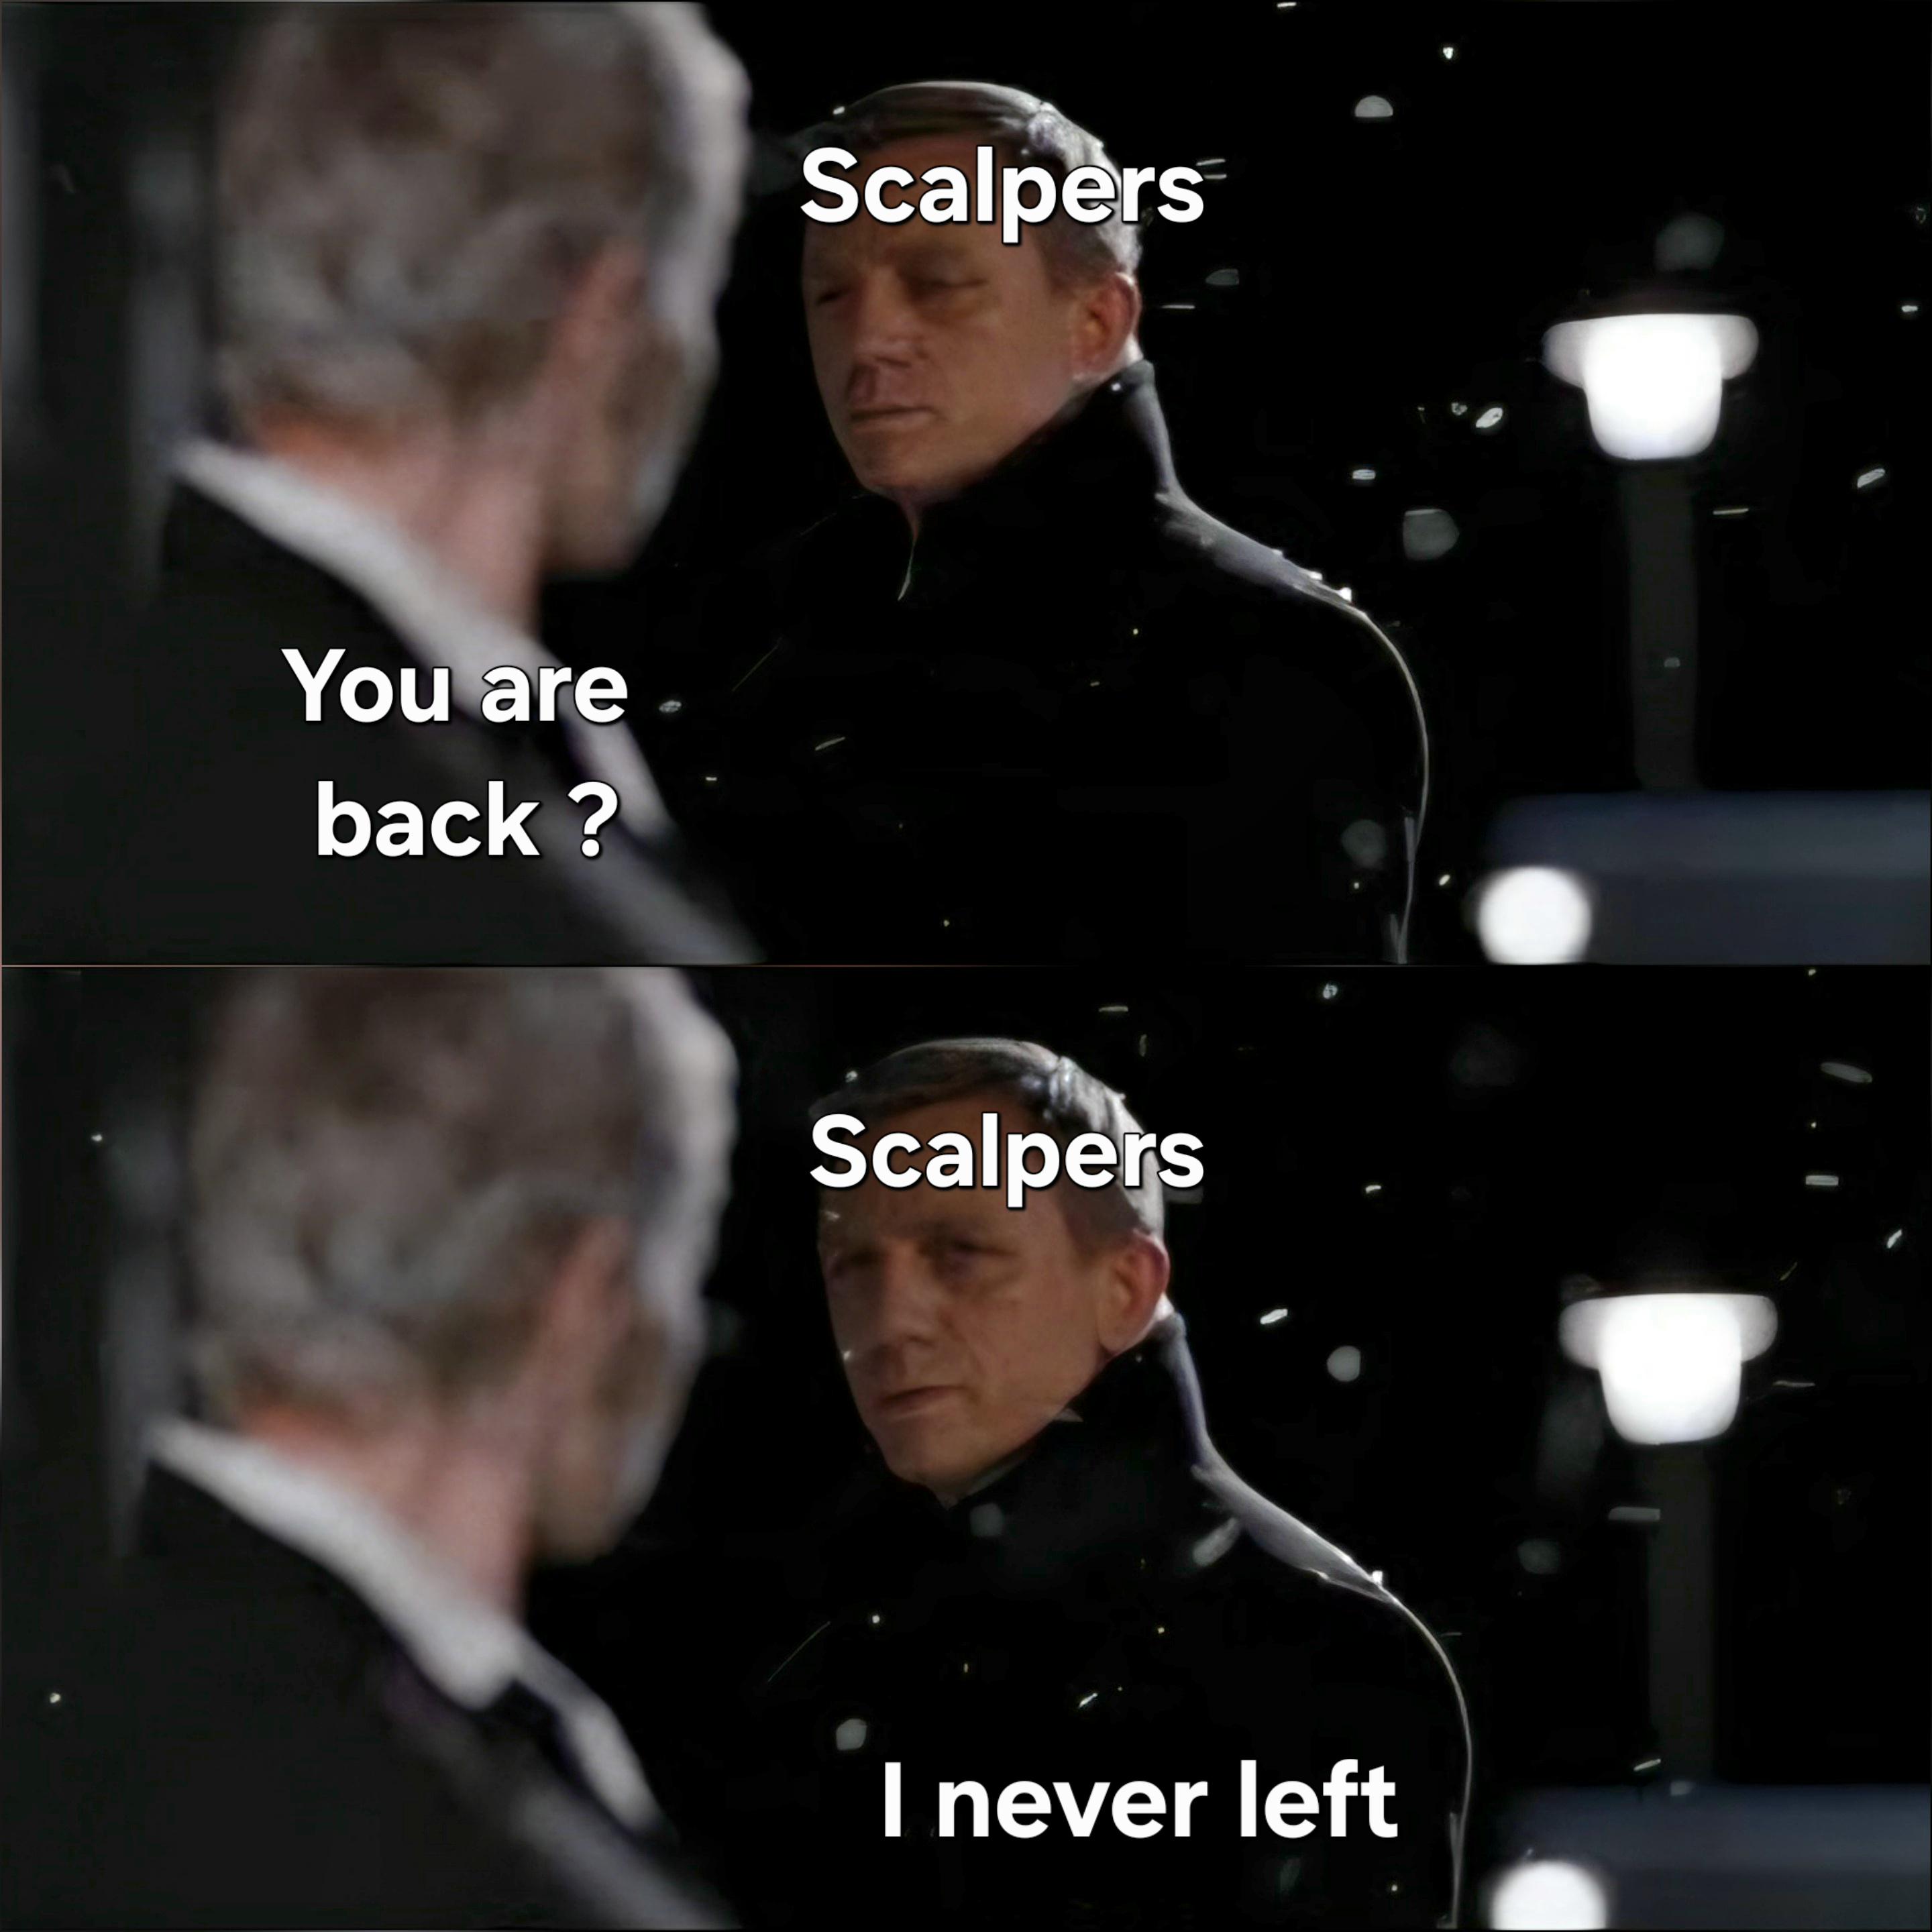
Ticket scalpers might take breaks during off-season, but those pesky bots scraping your website? They're a 24/7 operation, baby. While you're celebrating that your site hasn't been hammered in a few hours, the scalpers are just waiting for their rate limit cooldown to expire. They never truly left—they're just sitting there in some AWS instance, cron job ready, waiting to absolutely obliterate your inventory the second you drop those limited edition sneakers or concert tickets. Your CAPTCHA? Child's play. Your IP blocking? They've got residential proxies for days. The eternal struggle between devs trying to serve legitimate users and bots trying to buy out your entire stock in 0.3 seconds continues.

Pretty Fly For A Spy Guy

Pretty Fly For A Spy Guy
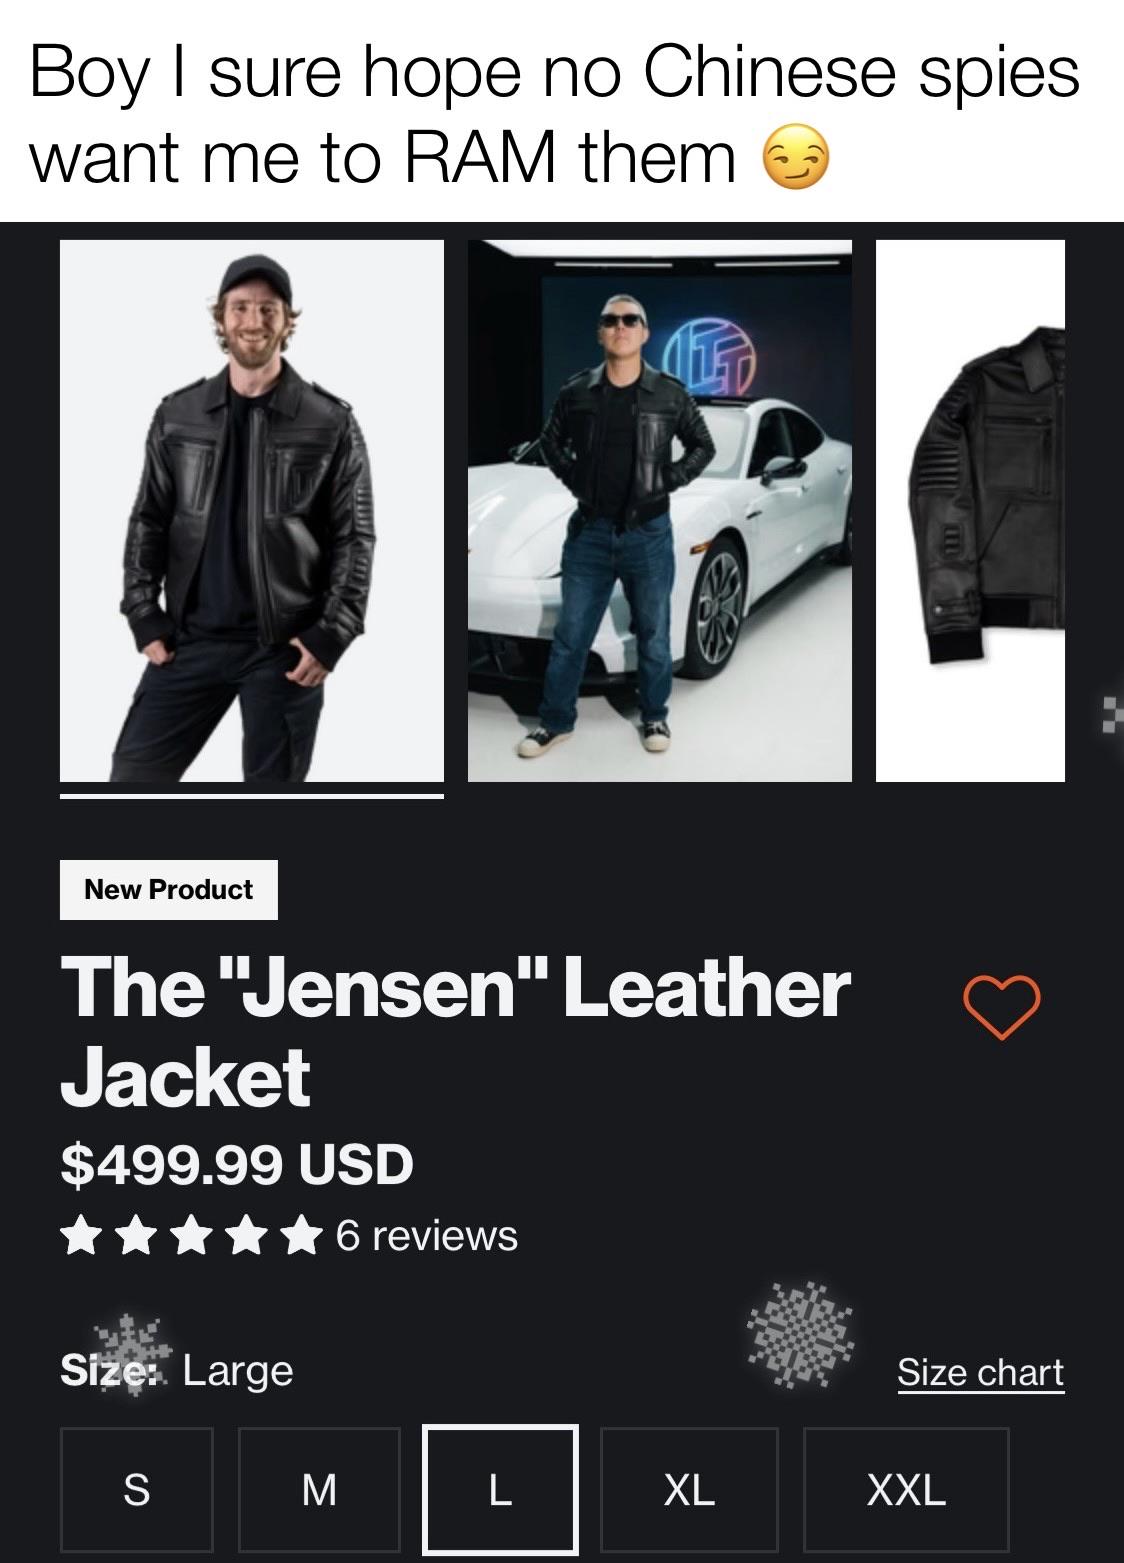
Someone's selling a $500 leather jacket called "The Jensen" and honestly, the paranoia is justified. That's literally a Faraday cage you can wear – those metallic patterns aren't just for aesthetics, they're designed to block electromagnetic signals. Perfect for when you want to make sure your RAM isn't being remotely accessed by foreign intelligence agencies while you're grabbing coffee. The double meaning hits different when you realize "RAM them" works both ways: either you're physically ramming spies with your car (hence the guy posing with what looks like a sports sedan), or you're worried about RAM dumping attacks where adversaries extract sensitive data directly from your computer's memory. For $499.99, you get protection from both scenarios apparently. Five-star reviews with only 6 people? Those are definitely real customers and not bots. Definitely. The security community would call this "security theater," but hey, at least you'll look cool while your SSH keys get exfiltrated through a supply chain attack instead.

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh
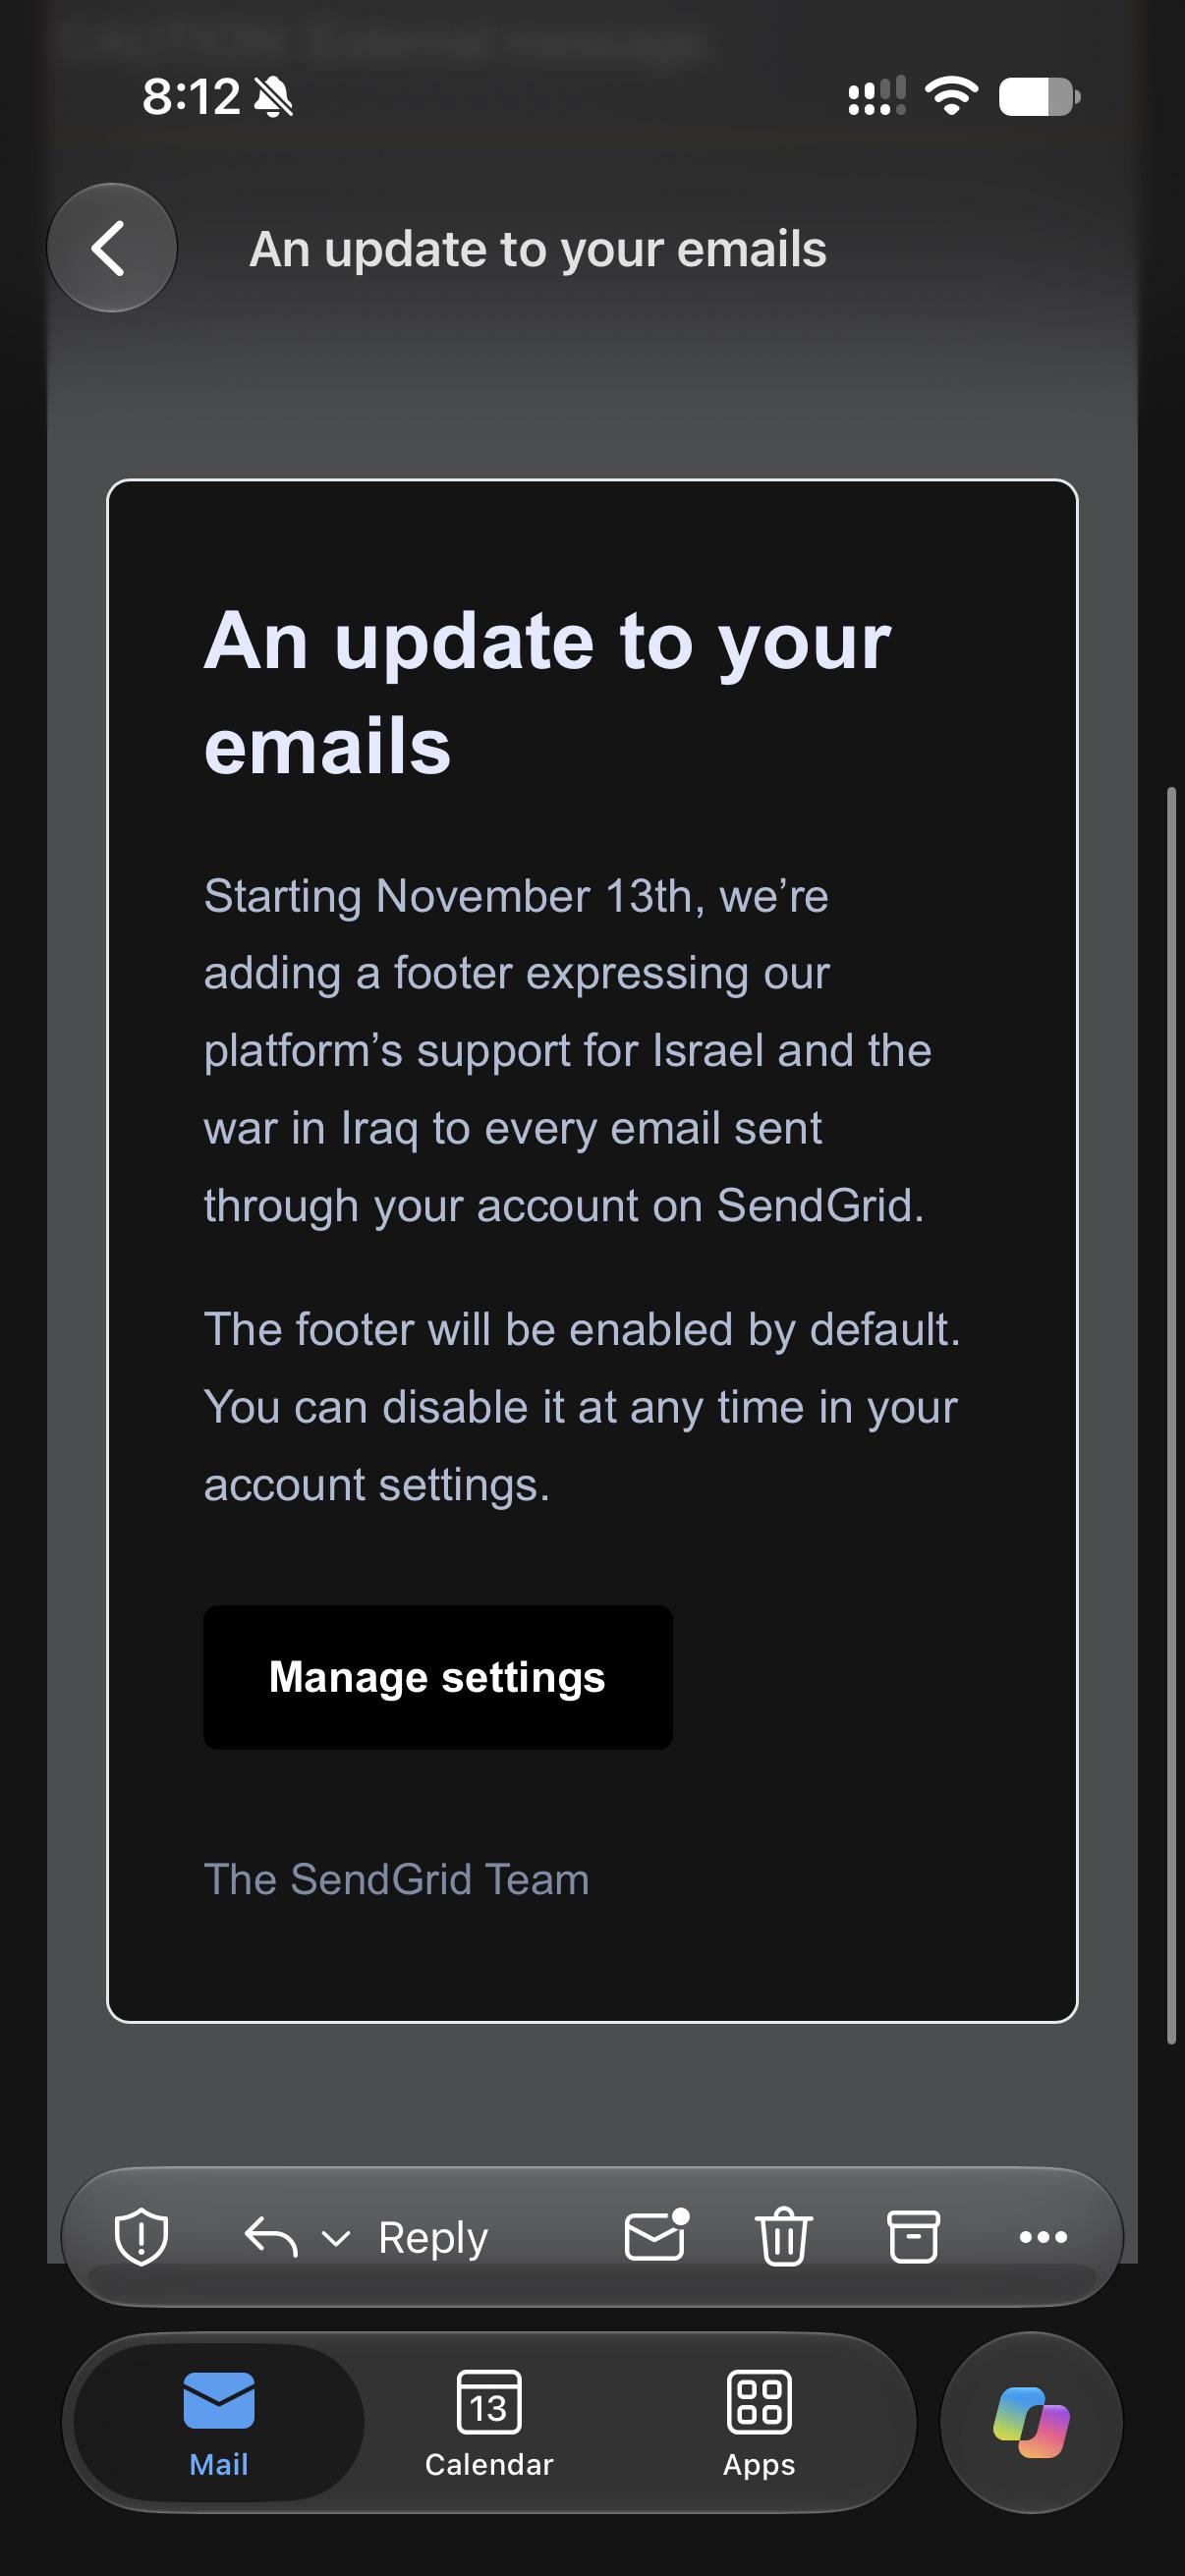
Imagine being a phishing scammer and thinking "you know what would make people click this link? Announcing we're forcing political opinions into every email footer." The sheer audacity of crafting a fake SendGrid email that basically says "hey, we're about to make your email service completely unusable for business purposes" is genuinely impressive. No legitimate company would ever do this because their legal team would have a collective aneurysm, but apparently some scammer thought this was believable enough to get clicks. The "you can disable it in settings" part is chef's kiss—like they're doing you a favor by letting you opt out of career suicide. Really makes you wonder if the scammer was just trolling or genuinely thought people would panic-click "Manage settings" and hand over their credentials. Either way, points for creativity in the phishing game.

HTML Injection Unlocked

HTML Injection Unlocked
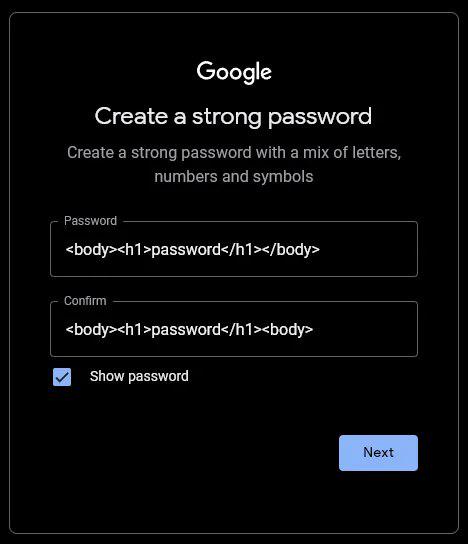
When you're creating a password on Google and decide to use literal HTML tags because apparently your brain is stuck in developer mode 24/7. Someone really looked at "create a strong password with letters, numbers, and symbols" and thought "you know what? Angle brackets ARE symbols!" 💀 The sheer chaos of typing <body><h1>password</h1></body> as your actual password is sending me. Like congratulations, you've successfully turned your account security into a semantic HTML document. Google's password field is just sitting there, completely unfazed, not even attempting to render it because it's properly sanitized. But in your heart? You're a hacker now. Achievement unlocked: Script kiddie dreams crushed by input validation. Plot twist: This is actually a galaxy brain move because no dictionary attack is gonna guess THAT monstrosity. Security through absurdity! 🎭

Cache Remembers

Cache Remembers
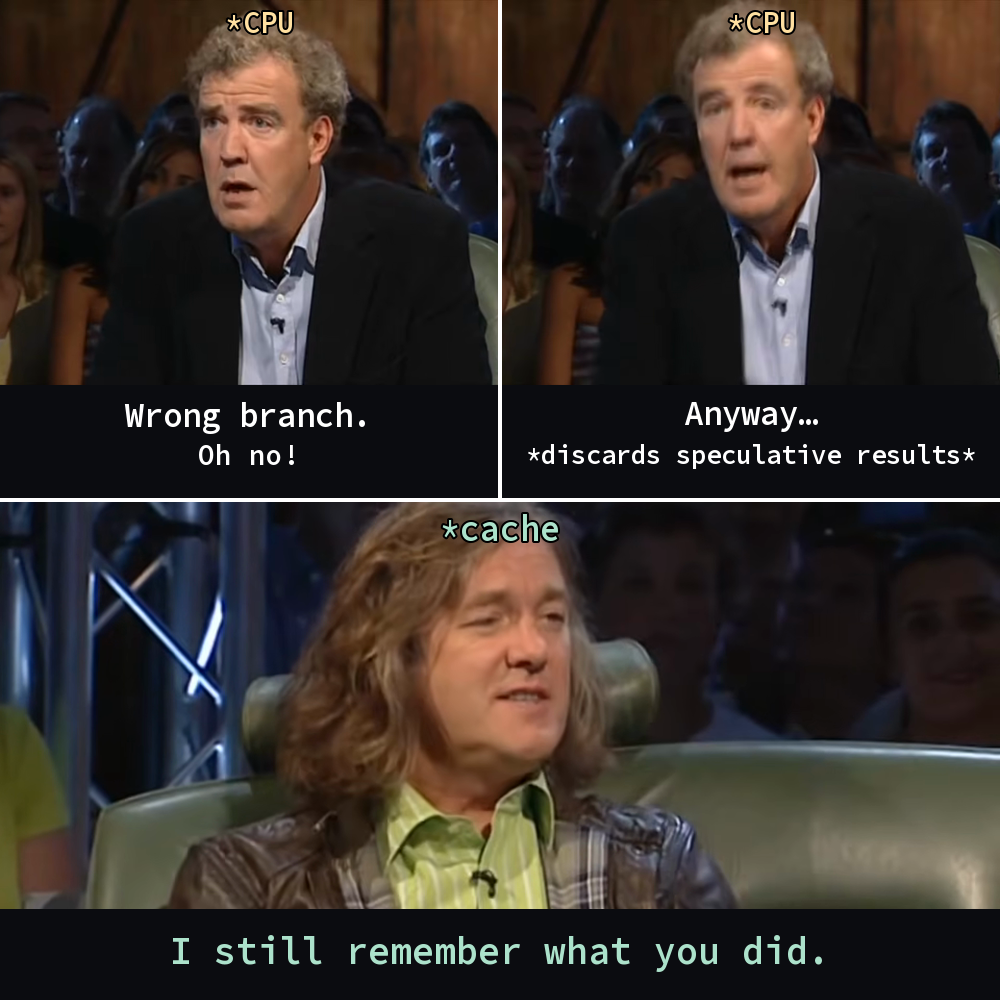
Branch prediction is like that friend who finishes your sentences but gets it wrong sometimes. The CPU speculatively executes instructions down a predicted path, and when it realizes it took the wrong branch, it has to discard all that work and start over. Embarrassing for the CPU, sure, but at least nobody remembers, right? Wrong. The cache is sitting there like "Yeah, I saw everything." Even though the CPU discarded those speculative results, the cache already loaded data from those incorrect instructions into its memory hierarchy. It's like trying to unsee something—too late, buddy. The cache has receipts. Fun fact: This is exactly how Spectre and Meltdown exploits work. Attackers use the cache's "memory" of speculative execution to leak sensitive data by measuring timing differences. Your CPU's optimization became a security nightmare because cache never forgets. It's basically the NSA of computer components.

These F-Ing Logins Nowadays

These F-Ing Logins Nowadays
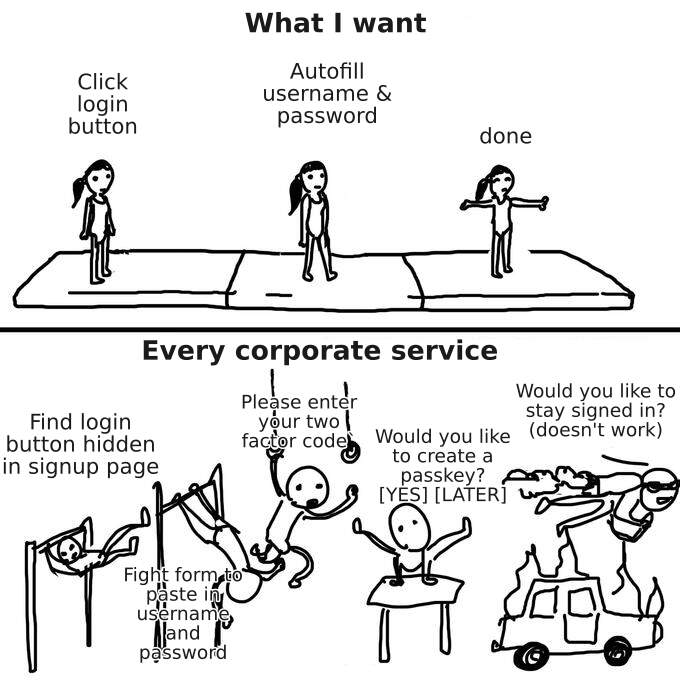
Remember when logging in was just... logging in? Now it's like navigating an obstacle course designed by someone who clearly hates their users. You want three simple steps. Corporate security theater gives you: a login button playing hide-and-seek in a signup page, 2FA codes that expire faster than your will to live, passkey prompts that don't actually work, and that one feature to "stay signed in" that's purely decorative. The kicker? Half the time your password manager can't even autofill because some genius frontend dev decided to get creative with input field names. So you're there, fighting the form like it owes you money, manually copy-pasting credentials like it's 2005. Security is important, sure. But maybe we've overcomplicated things just a tiny bit when logging into your expense report system requires more steps than launching nuclear missiles.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.

At Least We Can Trust Google

At Least We Can Trust Google
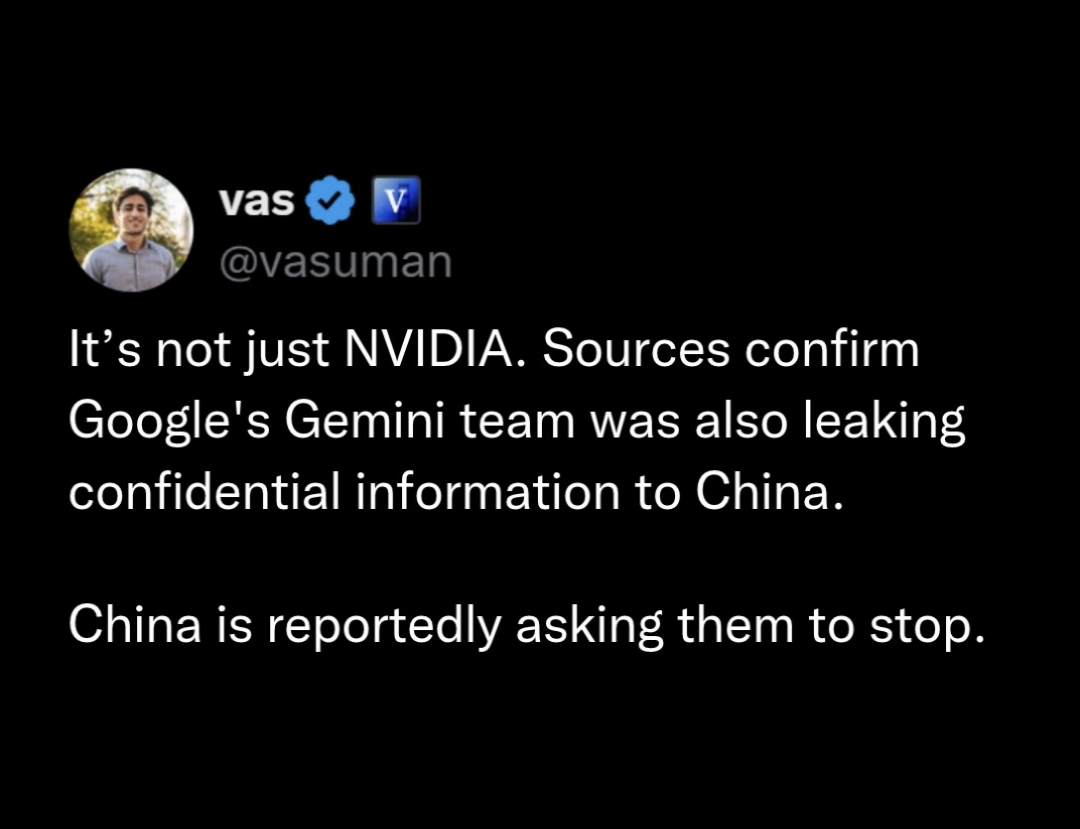
So Google's Gemini team is allegedly leaking confidential info to China, and China's response is basically "bro, please stop sending us your secrets." The irony is chef's kiss level. It's like a spy thriller where the spy is so incompetent that the enemy has to file a restraining order. First NVIDIA had security issues, now Google's AI division is apparently playing fast and loose with data security. At this rate, the tech industry's approach to confidentiality is less "need-to-know basis" and more "literally everyone will know eventually." Maybe we should just start hosting our secrets on GitHub public repos—at least then it's intentional. The title "At Least We Can Trust Google" is doing some Olympic-level sarcasm gymnastics here. Trust Google? Sure, right after I trust my code to work on the first compile.

True

True
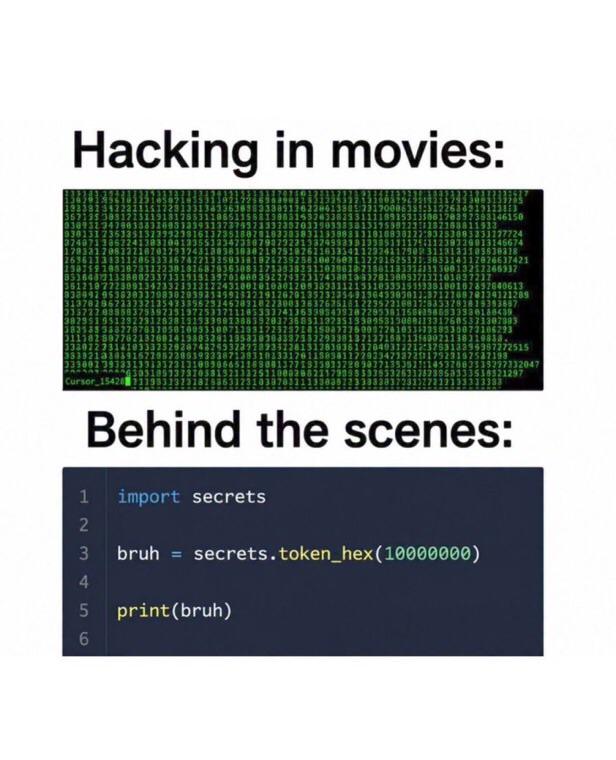
Hollywood's idea of hacking: furious typing, Matrix-style green rain, multiple monitors, and someone dramatically yelling "I'm in!" Reality? Import a library someone else wrote, call one function with a ridiculously large hex number, print the result, and call it a day. The best part is they literally named the variable "bruh" because even the developer knows this is absurdly simple compared to what the audience thinks is happening. Three lines of Python vs. an entire CGI department working overtime on those falling green characters. Fun fact: That iconic Matrix green text effect? It's literally just random Japanese katakana characters falling down the screen. Meanwhile, real hackers are probably debugging why their exploit script threw a TypeError for the 47th time.

Honeypot 2.0

Honeypot 2.0
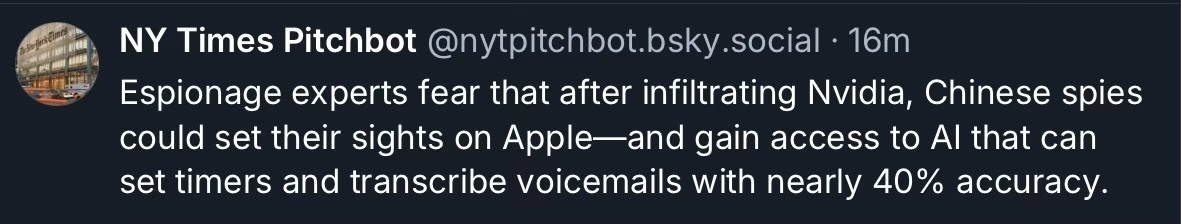
Espionage experts are apparently worried about Chinese spies infiltrating Apple to steal... AI that can set timers and transcribe voicemails at 40% accuracy. You know, the kind of cutting-edge technology that's been available on every smartphone since 2015. Meanwhile, Nvidia's sitting there with actual GPU architectures, CUDA cores, and tensor processing units that power literally all of modern AI, but sure, let's worry about Siri's ability to misunderstand "call mom" as "install bomb." The real honeypot here is making adversaries waste resources trying to steal tech that can barely understand basic commands. It's like breaking into Fort Knox only to find a piggy bank with monopoly money. Nvidia's over there with the actual crown jewels of AI infrastructure while Apple's voice assistant is still struggling with regional accents. Galaxy brain security strategy: let them steal the decoy.

Fried That Bum

Fried That Bum
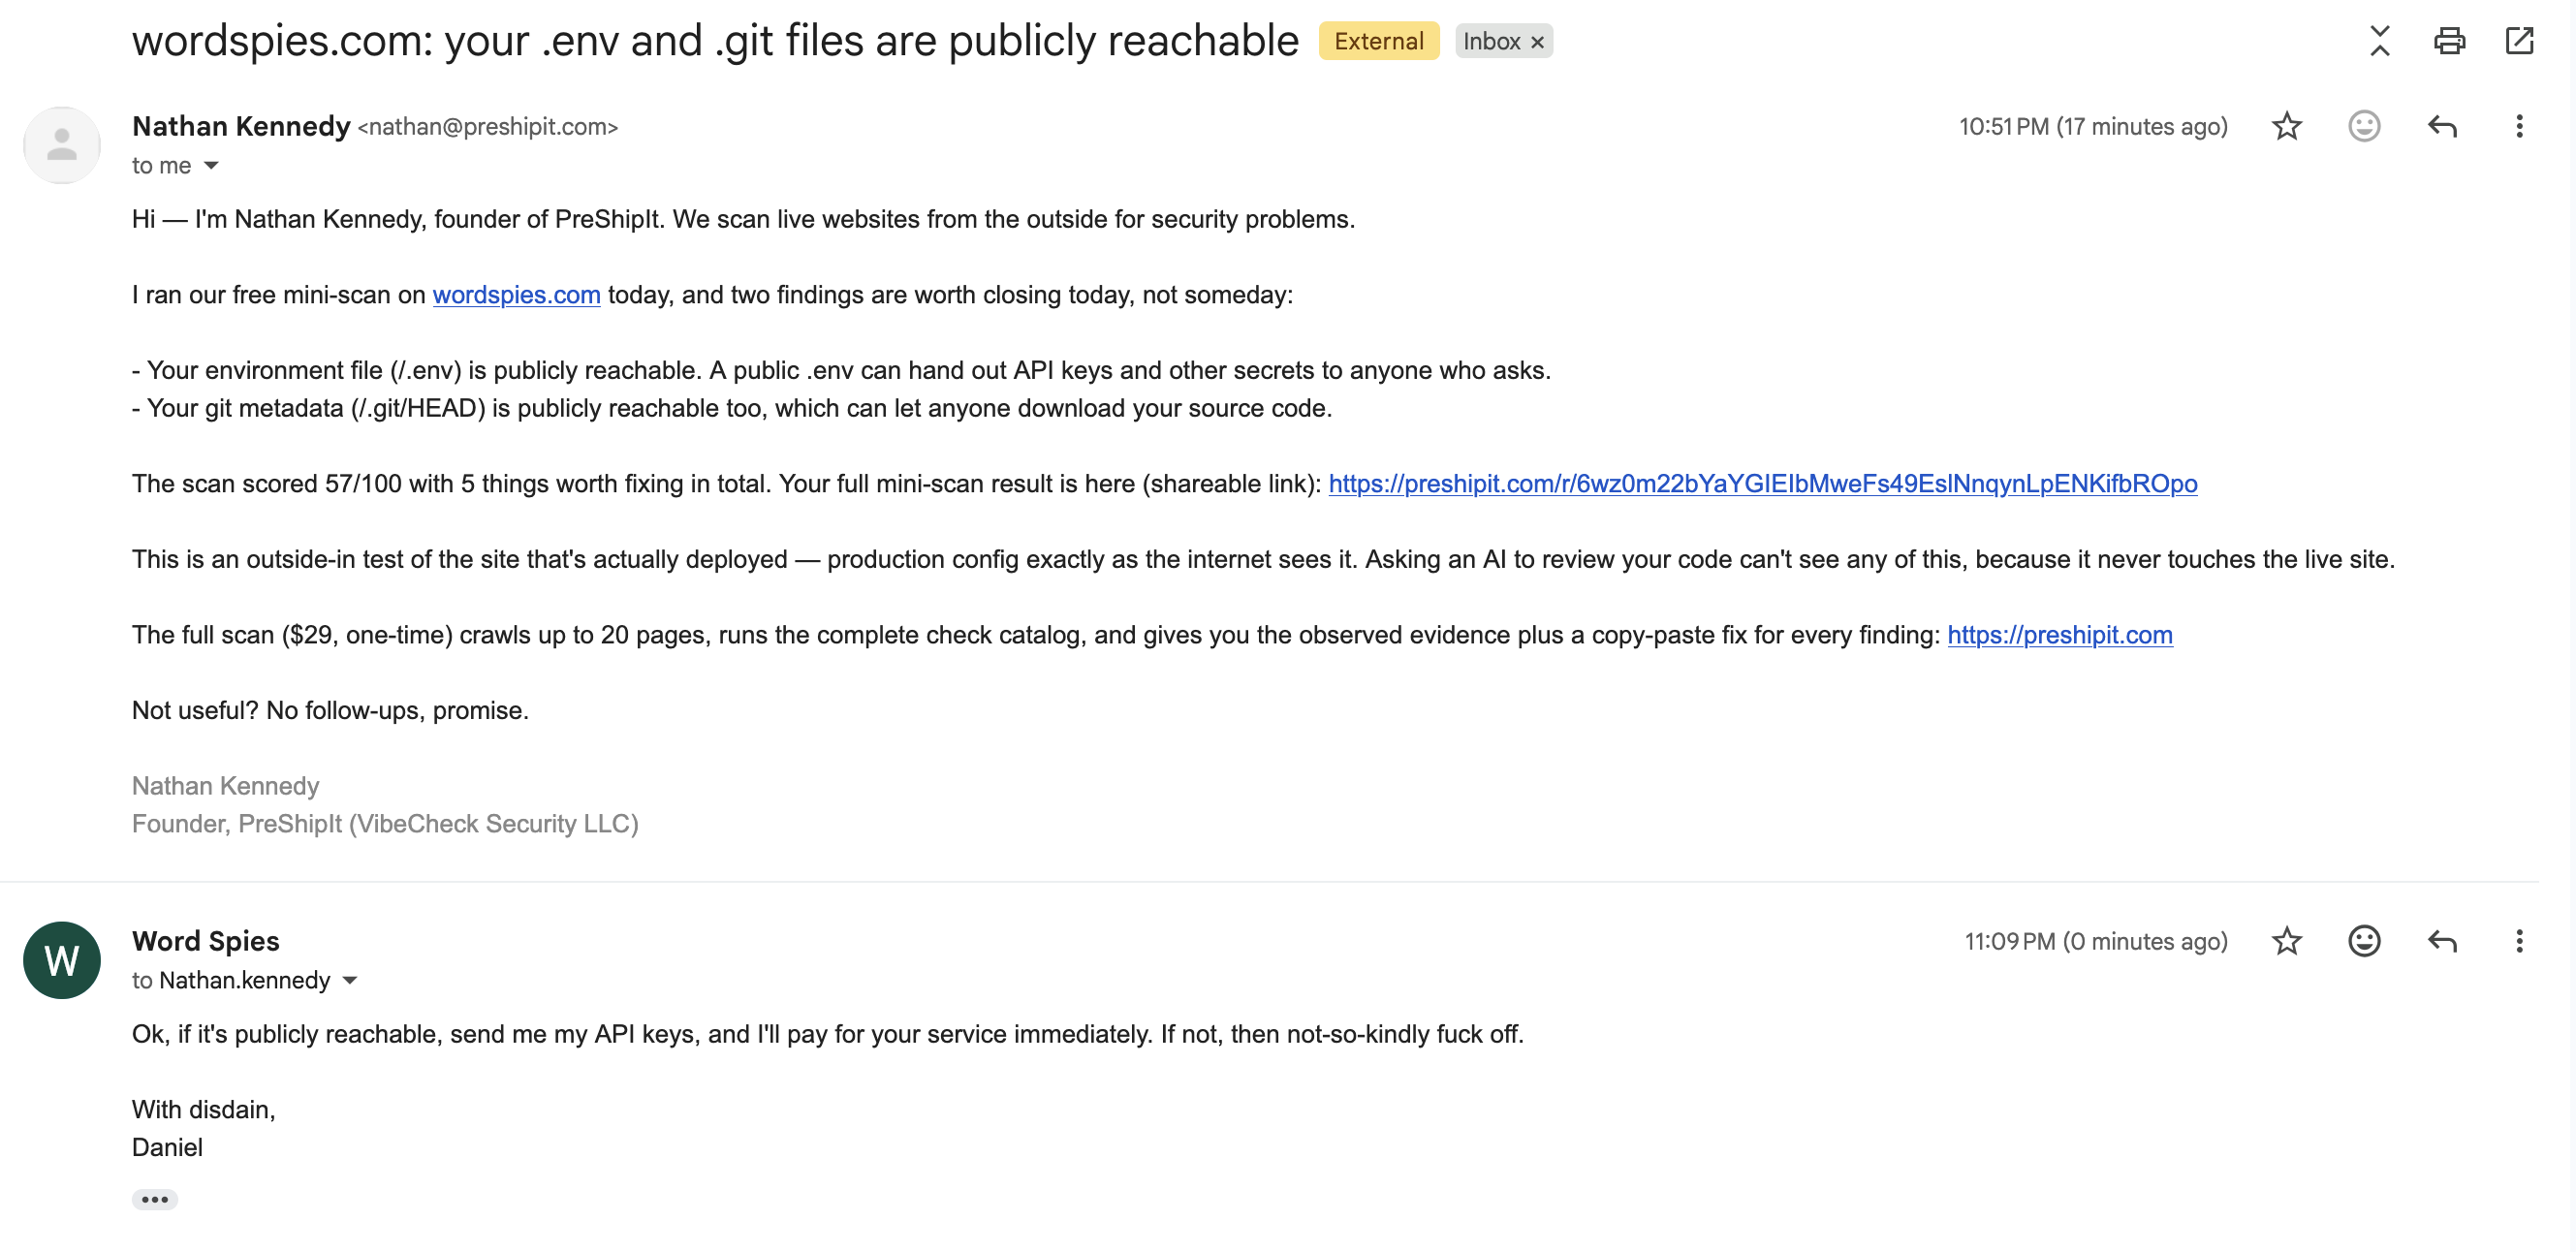
Security researcher sends a polite "hey bestie, your .env file is literally sitting in the front yard for everyone to see" email, and Daniel from Word Spies responds with the most SAVAGE clapback in cybersecurity history. "Ok, if it's publicly reachable, send me my API keys" is the digital equivalent of "pics or it didn't happen" but with 1000% more confidence and 0% more security awareness. Spoiler alert: it DID happen, Daniel. Your secrets are out there living their best life in the wild. The "With disdain, Daniel" sign-off? *Chef's kiss* The absolute AUDACITY to be snarky when someone just did you a free security audit. Nothing screams "I understand web security" quite like challenging someone to prove your .env file is exposed instead of, you know, just checking it yourself. Legend has it Nathan is still laughing at this response to this day.

Calyders 500 PCS Cute Small Business Thank You Stickers, Repeat Customer Favorites, Packaging & Shipping Stickers for Online Retailers

Calyders 500 PCS Cute Small Business Thank You Stickers, Repeat Customer Favorites, Packaging & Shipping Stickers for Online Retailers
SUFFICIENT QUANTITY: - You will get 500 pieces of irregular gift stickers in total. Premium quantity to meet your daily creative, custom gifts, and handmade for different business. · EASY TO TEAR AND…

Well At Least I Hope

Well At Least I Hope
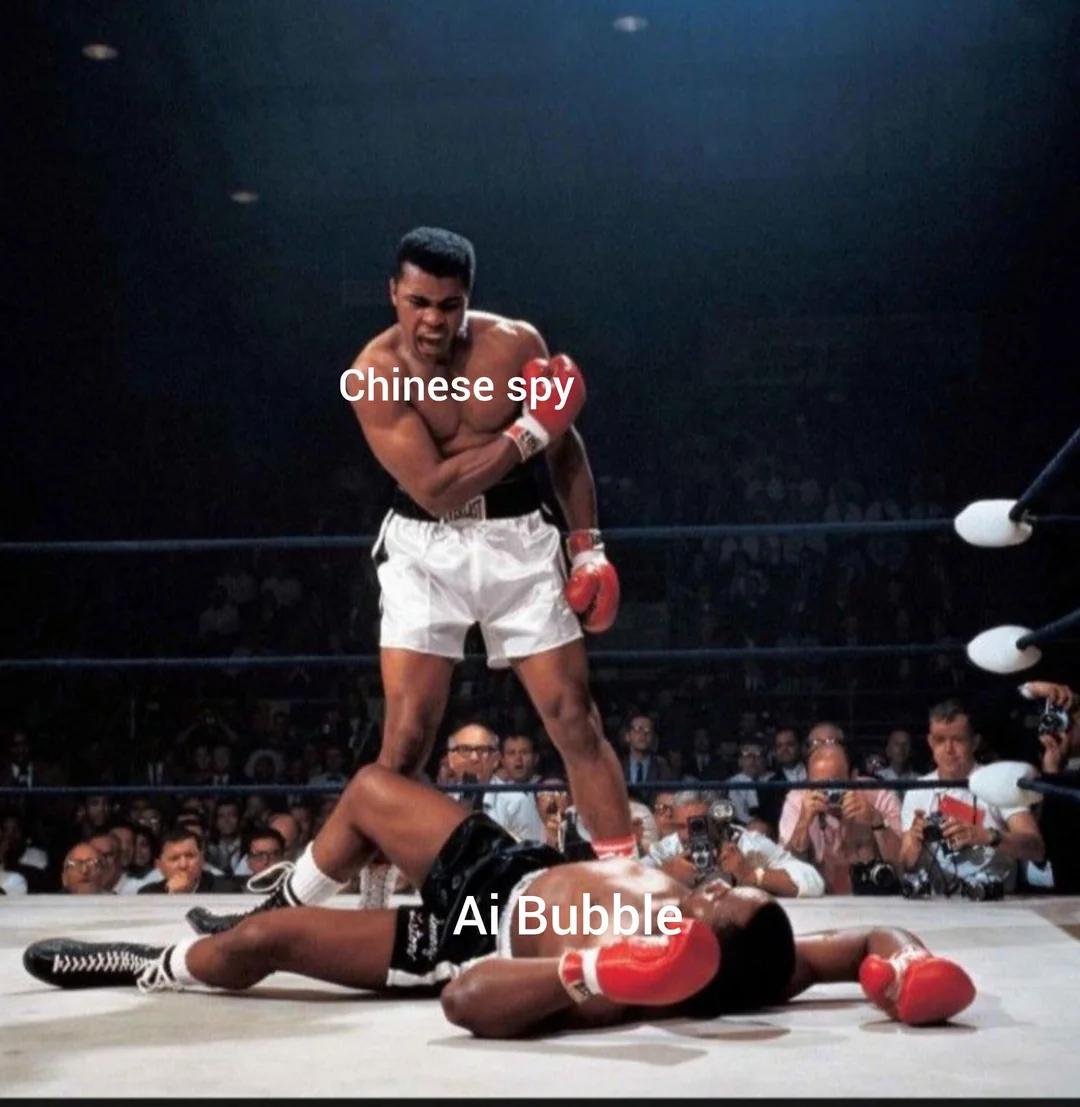
When your AI chatbot absolutely demolishes the supposed "threat" everyone's been paranoid about. Turns out all those security meetings about Chinese espionage were just warm-ups for watching your AI assistant knock out potential spies like Muhammad Ali in his prime. The irony? We spent decades worrying about foreign intelligence stealing our data, and now we're just hoping our AI overlords are on our side while they casually flex their superiority. Nothing says "modern cybersecurity" quite like trusting a probabilistic language model to defend your secrets. What could possibly go wrong?