AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud
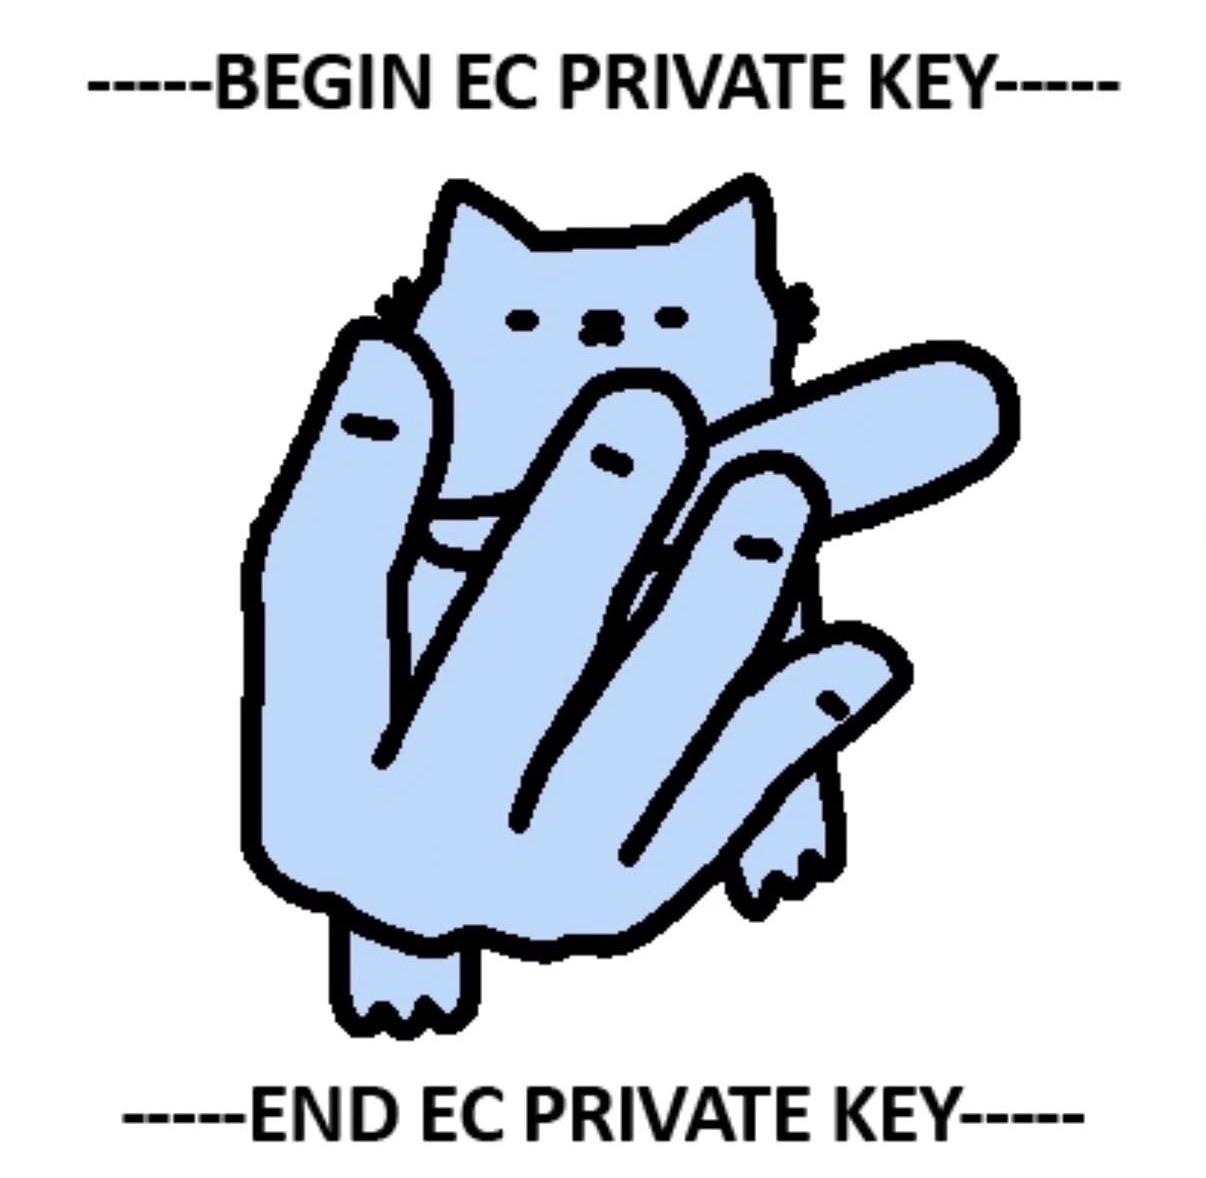
Someone just committed their EC private key to the repo with the BEGIN and END delimiters still attached, and honestly? That's the least of their problems. The real crime here is that our feline friend is showing us exactly four fingers—because nothing says "I understand elliptic curve cryptography" quite like accidentally exposing your private key in version control.
The joke plays on the title "Four" and the visual of four fingers, but the actual security nightmare is that EC private keys should NEVER see the light of day, let alone get pushed to a public repository. Time to rotate those keys, revoke all certificates, and maybe add *.pem to your .gitignore before the security team finds out.
Pro tip: If your private key has ever touched a commit history, it's not private anymore—it's just a very embarrassing public string.