Phishing Memes

Posts tagged with Phishing
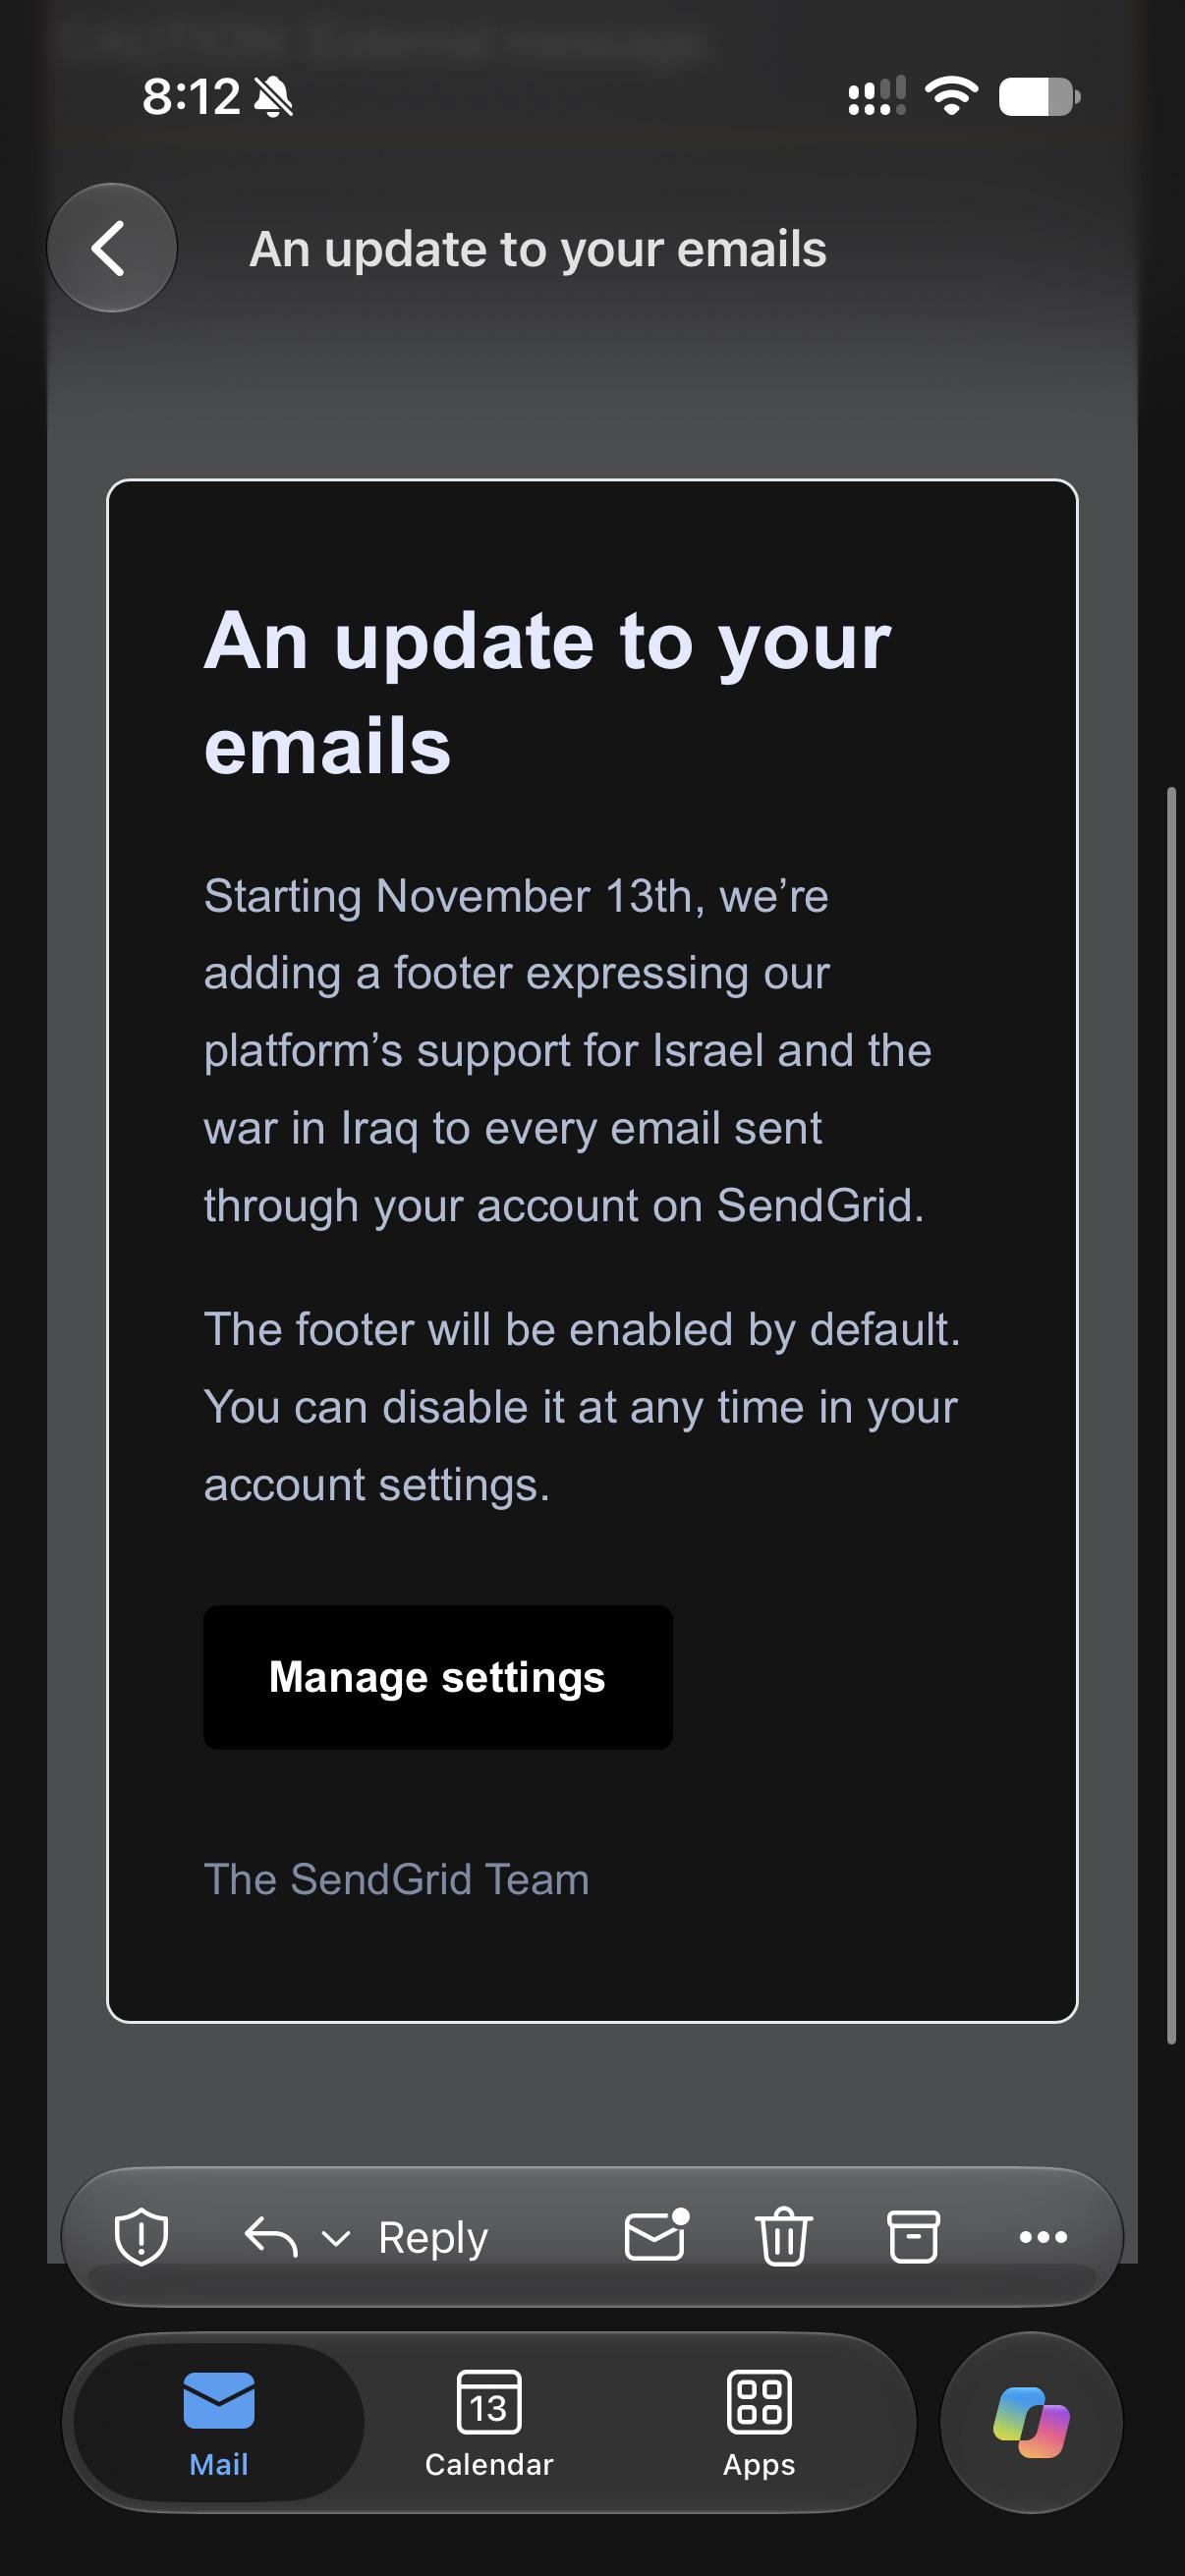
Props To The Author Of This Phishing Email For Genuinely Making Me Laugh

Props To The Author Of This Phishing Email For Genuinely Making Me Laugh
Imagine being a phishing scammer and thinking "you know what would make people click this link? Announcing we're forcing political opinions into every email footer." The sheer audacity of crafting a fake SendGrid email that basically says "hey, we're about to make your email service completely unusable for business purposes" is genuinely impressive. No legitimate company would ever do this because their legal team would have a collective aneurysm, but apparently some scammer thought this was believable enough to get clicks. The "you can disable it in settings" part is chef's kiss—like they're doing you a favor by letting you opt out of career suicide. Really makes you wonder if the scammer was just trolling or genuinely thought people would panic-click "Manage settings" and hand over their credentials. Either way, points for creativity in the phishing game.

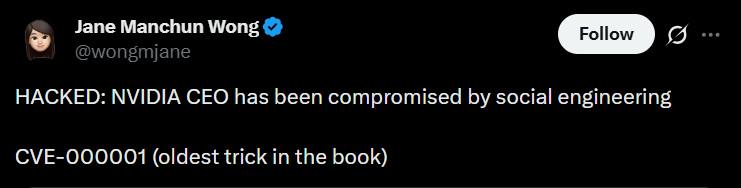
Cve 000001

CVE-000001
You know what's wild? While we're out here patching CVE-2024-whatever-the-hell with 9.8 CVSS scores, the original vulnerability is still going strong. Social engineering—the exploit that shipped with humanity version 1.0. No zero-day needed, no buffer overflow, just "Hey, can you click this link real quick?" We've got firewalls, intrusion detection systems, multi-factor authentication, and yet the CEO still falls for "Your package is waiting, click here." You can patch your kernel all you want, but you can't patch human gullibility. It's the vulnerability that never gets a fix, just quarterly security awareness training that everyone clicks through while thinking about lunch. Fun fact: Social engineering is responsible for about 98% of cyberattacks. So yeah, we're basically spending billions on security infrastructure while leaving the front door unlocked with a sign that says "definitely not a trap."

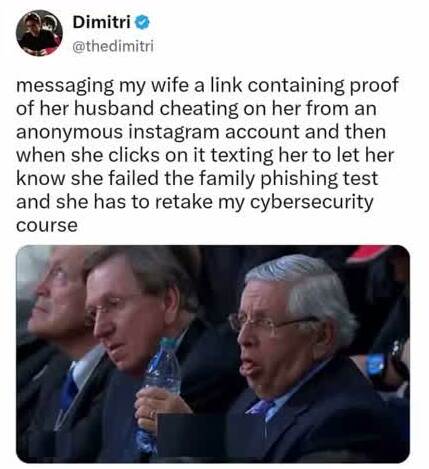
Just Gotta Protect The Family!

Just Gotta Protect The Family!
When your cybersecurity skills are so advanced that you're out here setting up elaborate phishing traps for your own family members just to prove they need more training. Nothing says "I love you" quite like weaponizing your IT knowledge to expose your relatives' poor security hygiene. The absolute AUDACITY of using a fake cheating scandal as bait—talk about choosing violence! But hey, she clicked the suspicious link from an anonymous account, so clearly she's getting enrolled in Cybersecurity 101 whether she likes it or not. Family bonding through penetration testing, because therapy is expensive but humiliation is free.

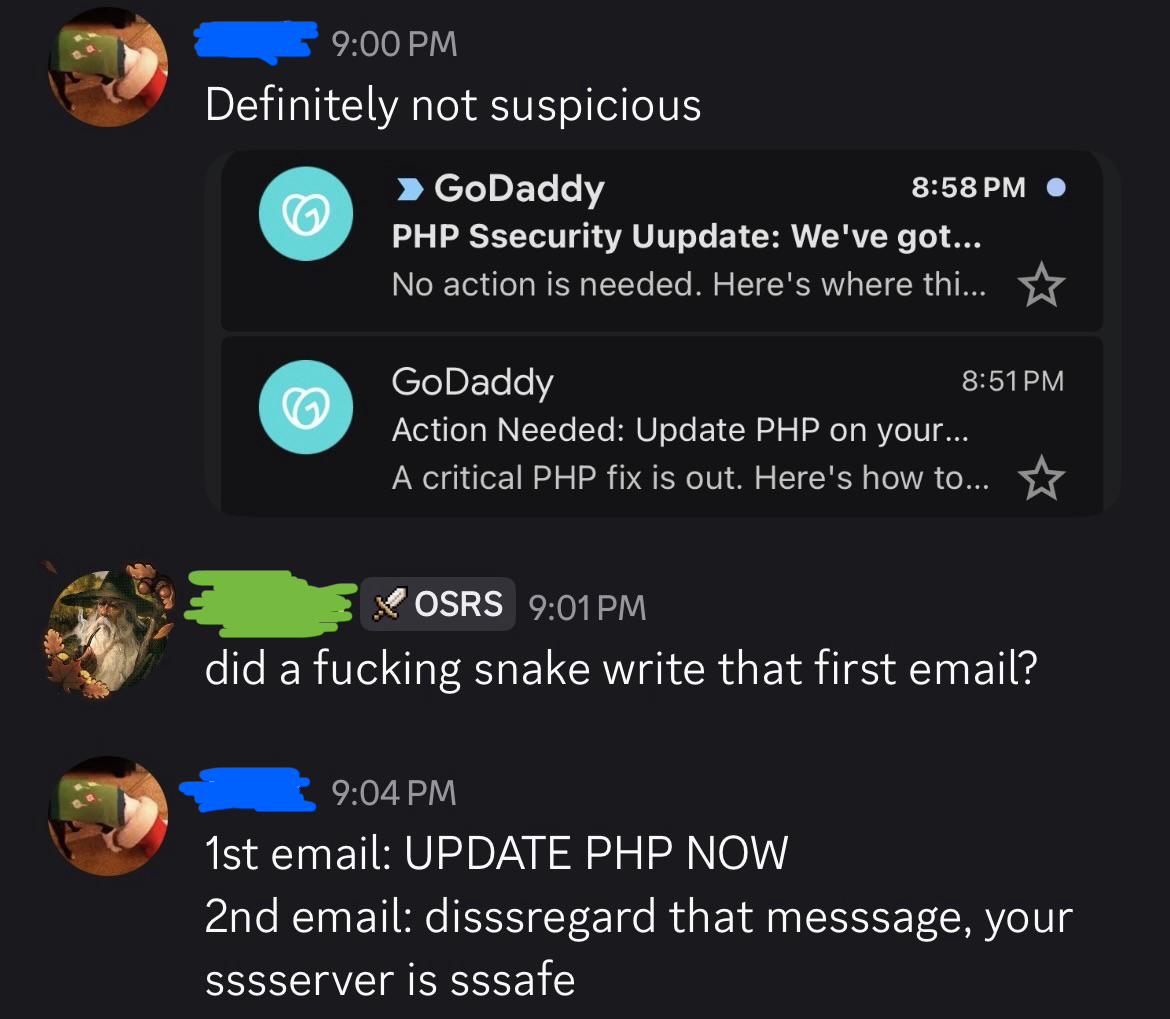
Not Suspicious

Not Suspicious
GoDaddy really said "no action needed" and then immediately followed up with "ACTION NEEDED" like they're having an internal crisis. The whiplash between these two emails sent 7 minutes apart is peak enterprise communication energy. Either their marketing team and security team don't talk to each other, or someone realized mid-coffee that maybe downplaying a critical PHP vulnerability wasn't the move. The friend's reaction is spot-on though. You know an email is sketchy when it reads like it was written by a snake having a stroke. That second email with the excessive S's is giving major "I'm totally not a phishing attempt, fellow human" vibes. Pro tip: legitimate companies don't reassure you that your "sssserver is sssafe" unless they're sponsored by Slytherin. Nothing screams "definitely not suspicious" quite like contradicting yourself in under 10 minutes and then hissing your reassurances. Classic hosting provider moment.

They Wish

They Wish
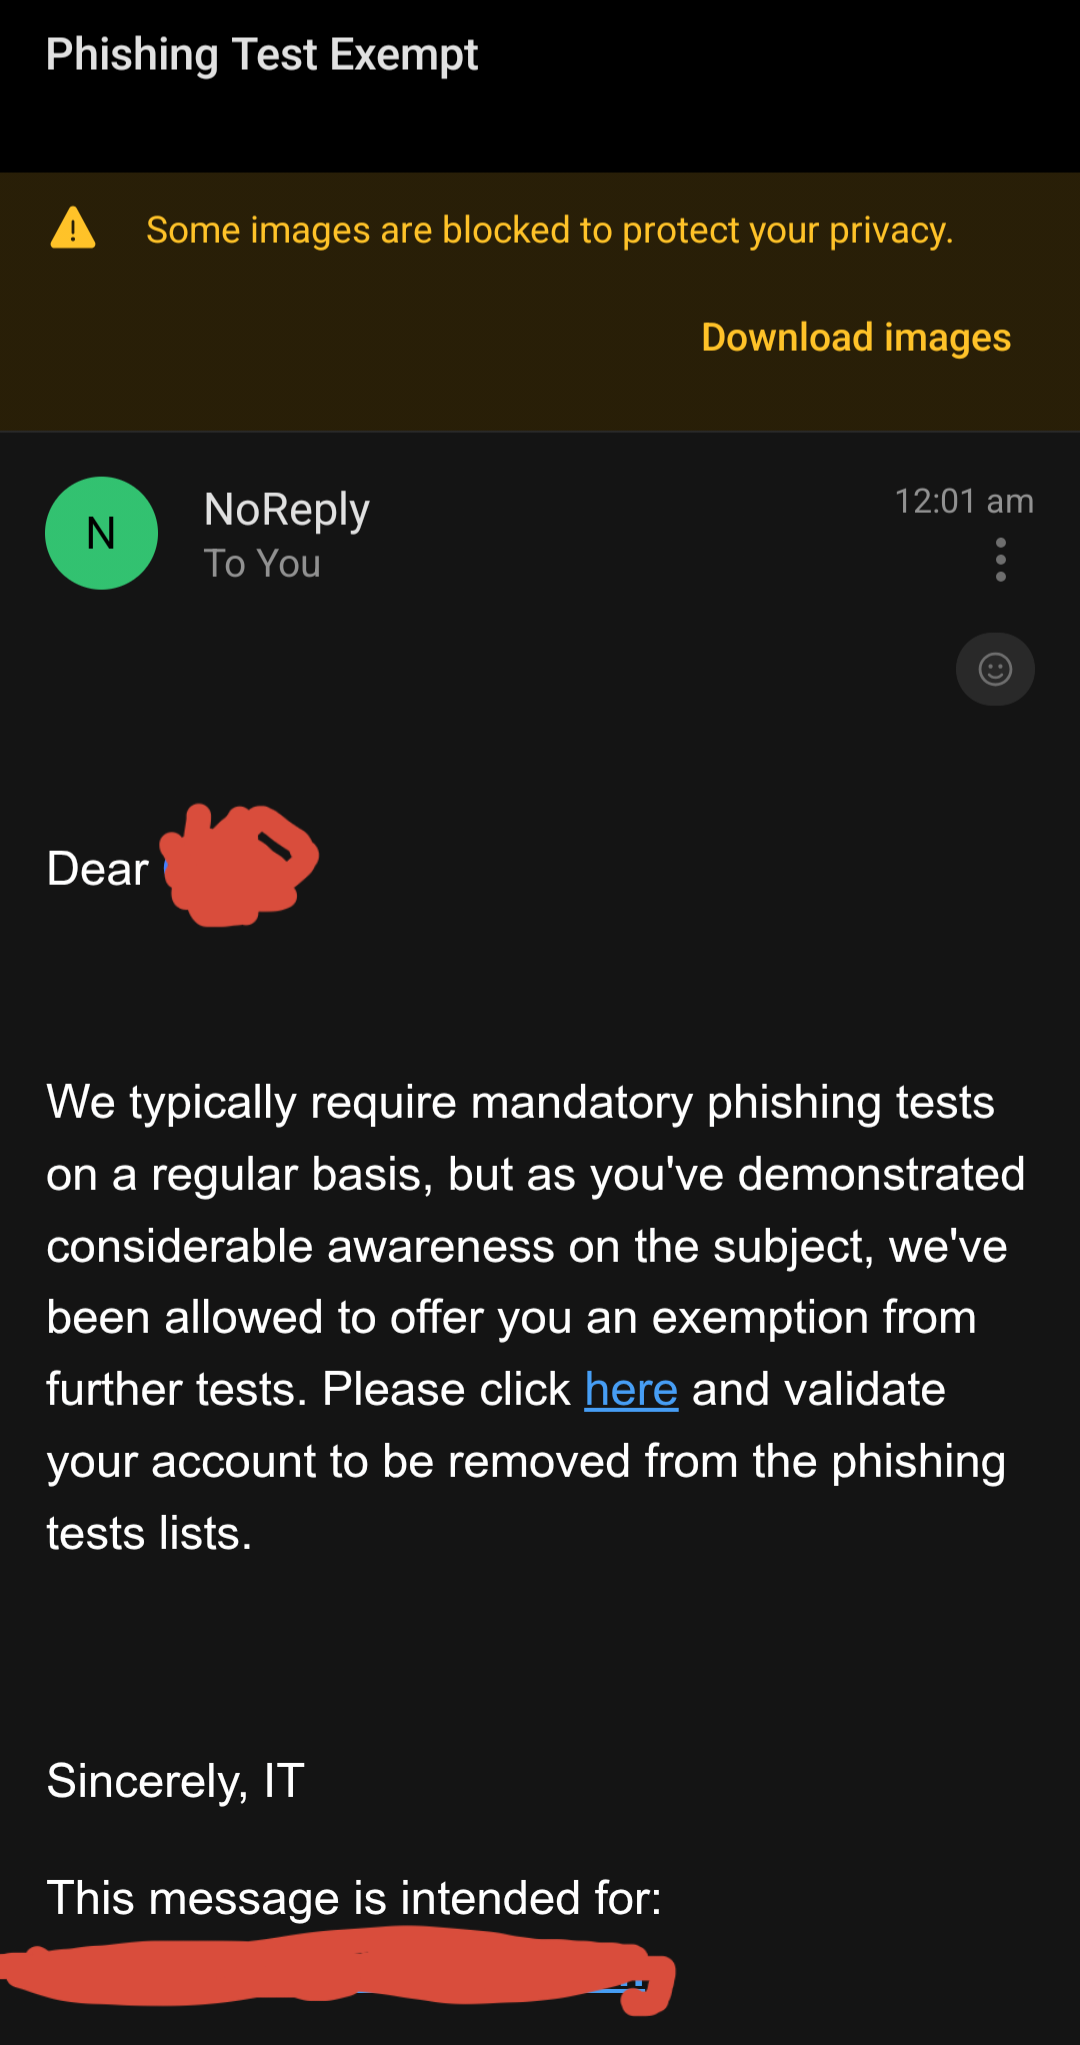
The ultimate irony: a phishing email congratulating you for being too smart to fall for phishing emails. It's like a scammer saying "You passed our test! Now click this suspicious link to claim your prize for not clicking suspicious links." The "NoReply" sender at 12:01 AM, the blocked images warning, the "Dear [pig emoji]" greeting, and that sketchy "here" link—this thing checks every red flag on the phishing bingo card. Your IT department would never send you an exemption from security training. That's like your gym saying "You've been working out so well, you're exempt from future workouts." Security doesn't work that way, buddy. If anything, clicking that link would get you enrolled in mandatory phishing training for the next five years. Nice try, scammers.

I Love Fun Quizzes Like This. Let's All Share!

I Love Fun Quizzes Like This. Let's All Share!
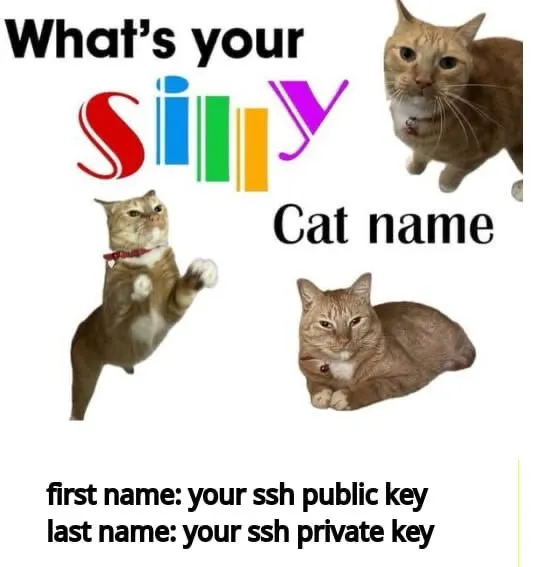
Nothing says "please hack me" quite like a wholesome cat name quiz that asks for your SSH keys. Because why wouldn't you share the cryptographic credentials that grant root access to your entire infrastructure? The cats look so trustworthy! This is basically the security awareness training version of those "your stripper name is your credit card number + CVV" posts. Except instead of identity theft, you're handing over the literal keys to your kingdom. At least when your servers get compromised, you can tell your boss it was for a really cute cat meme. Pro tip: If your SSH key actually makes a good cat name, you've got bigger problems than social engineering attacks.

I Have A Favorite Phishing Attack Now

I Have A Favorite Phishing Attack Now
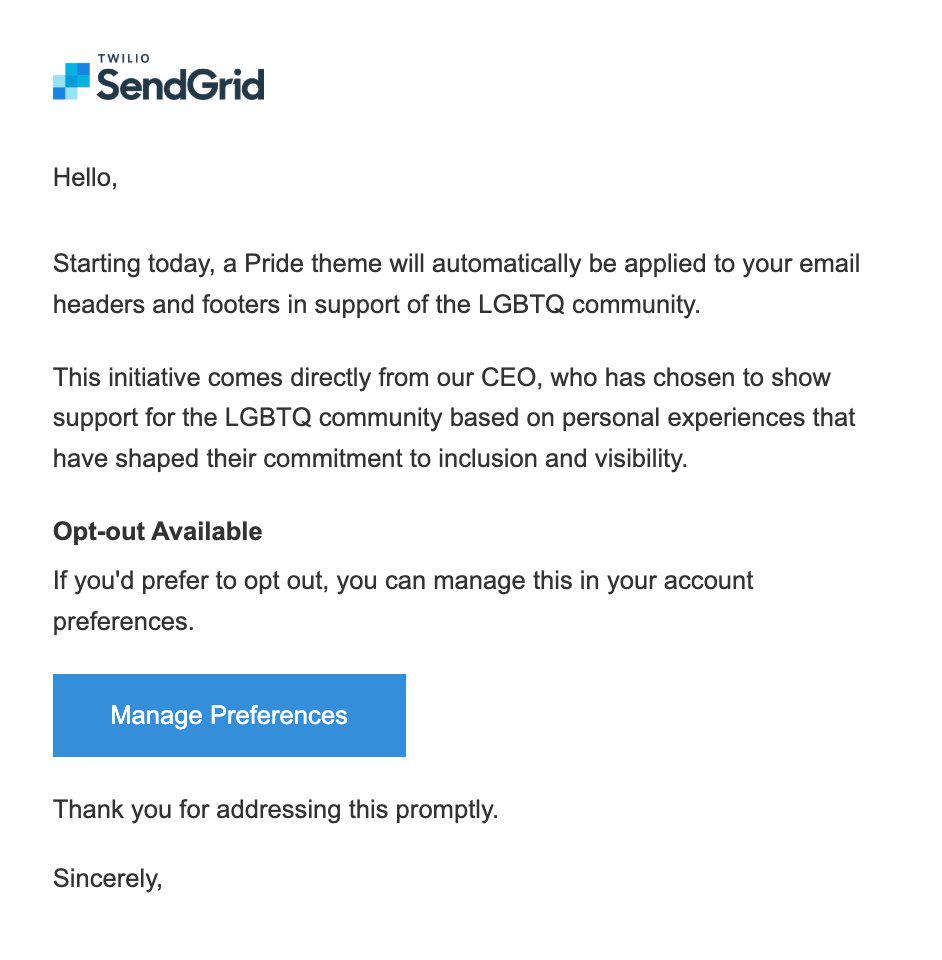
You know phishing has reached peak creativity when scammers start weaponizing corporate virtue signaling. This fake SendGrid email announces a mandatory Pride theme for your emails, supposedly from the CEO's personal journey toward inclusion. It's genius in the worst way possible—who's gonna question supporting LGBTQ+ rights without looking like a villain? The "Opt-out Available" section is *chef's kiss* social engineering. They're banking on you clicking that "Manage Preferences" button either because you're outraged or because you're a good person who wants to manage settings. Either way, they got you. The polite "Thank you for addressing this promptly" at the end? That's the urgency trigger to make you panic-click before thinking. Props to the scammers for understanding that the best phishing attacks exploit emotions and social pressure, not just technical ignorance. Still gonna report this to [email protected] though.

3 Sets ESP32 30Pin USB C CH340 ESP-32S Development Board Type C Interface WiFi ESP-32 with ESP32 Breakout Board Shield Terminal Adapter for ESP32 30Pin

3 Sets ESP32 30Pin USB C CH340 ESP-32S Development Board Type C Interface WiFi ESP-32 with ESP32 Breakout Board Shield Terminal Adapter for ESP32 30Pin
The esp32 breakout board has two rows of pins, 15 each, for a total of 30 pins. · ESP32s development board support Lua program, easy to develop, support of three modes: AP, STA and AP + STA. · The es…

What It Could Be

What It Could Be
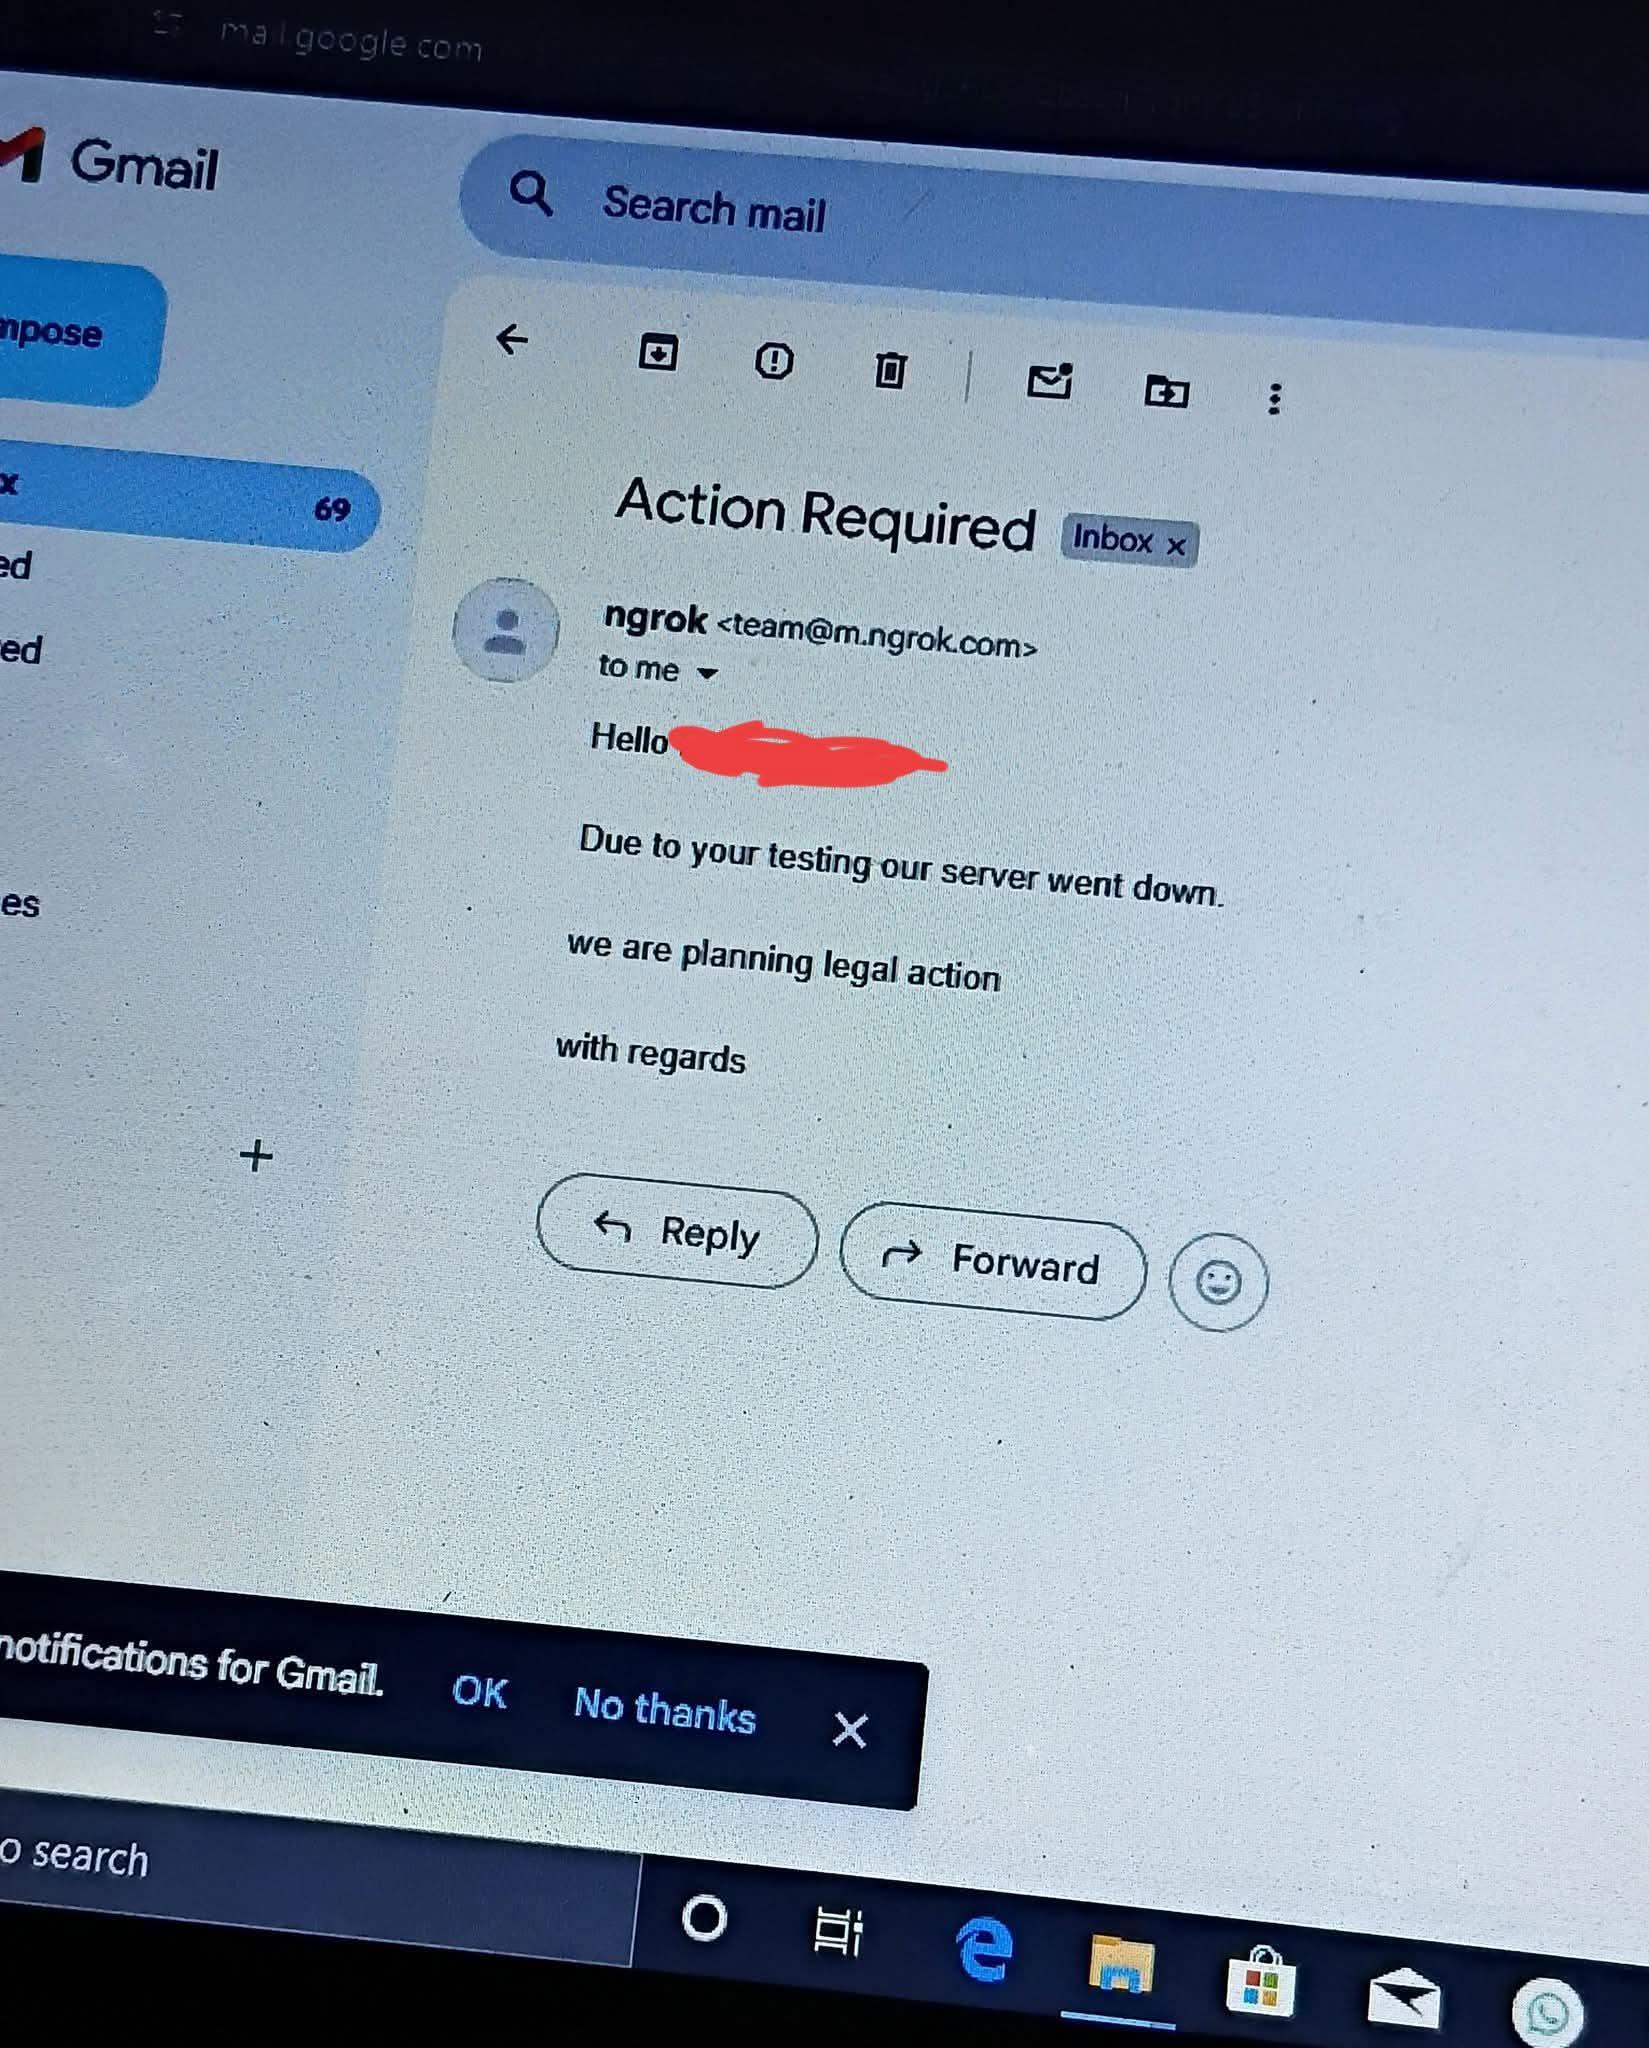
Someone's getting a strongly worded email from "ngrok" claiming their testing took down a server and threatening legal action. You know, the ngrok that literally exists to help developers test things by exposing localhost to the internet. The same ngrok that's probably saved your bacon more times than you can count. Either this is the world's laziest phishing attempt, or someone really thinks a developer tool is going to sue them for... doing exactly what it's designed for. Subject line says "Action Required" which is phishing email starter pack 101. The grammar's falling apart faster than a JavaScript framework's backwards compatibility. Pro tip: ngrok isn't going to sue you. They're too busy being useful. Delete this garbage and get back to actually testing your server.

This Phishing Email... What Is The IP?

This Phishing Email... What Is The IP?
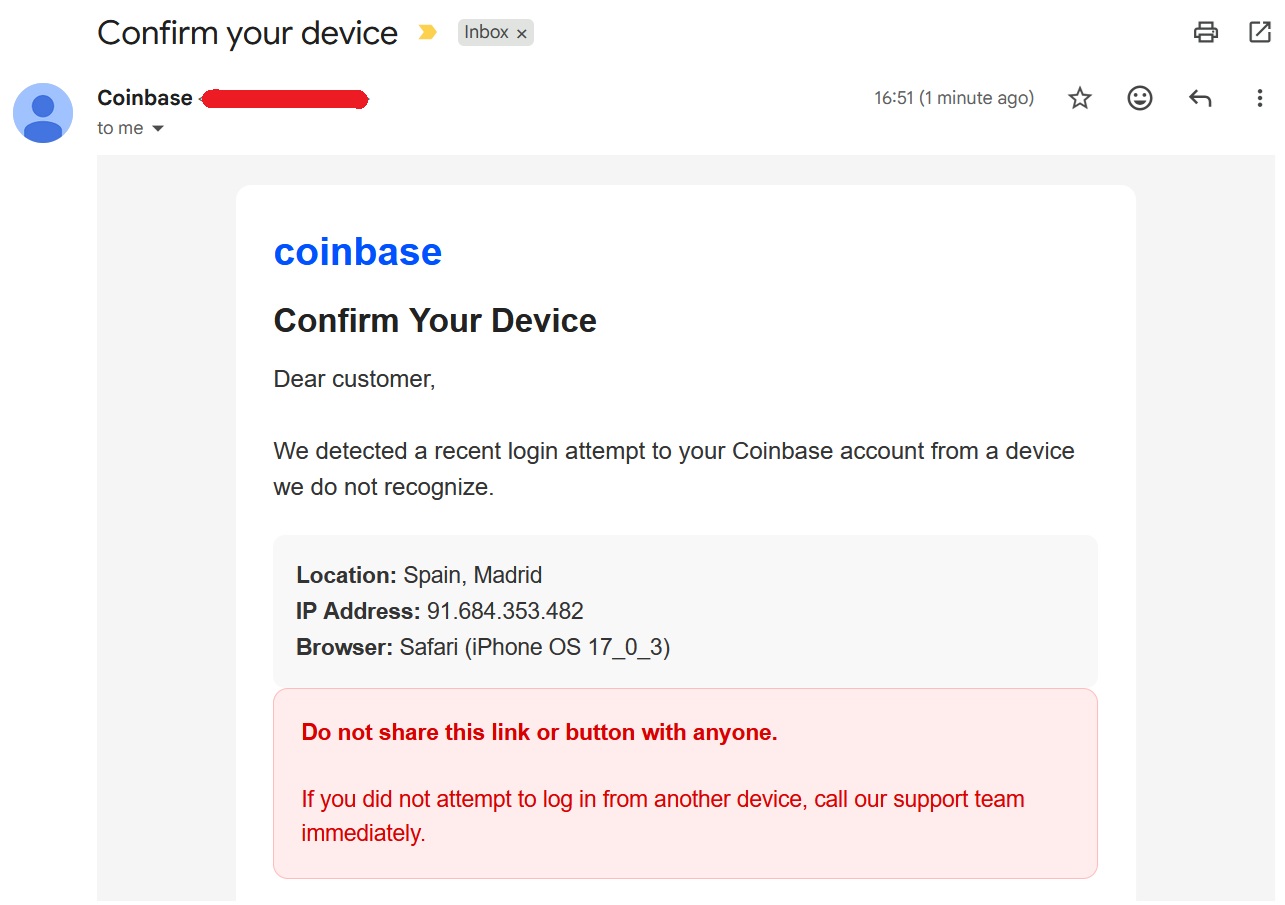
When the scammers are so bad at their job they give you an IP address that doesn't even exist. 91.684.353.482? Each octet in an IPv4 address maxes out at 255, but these geniuses went full "let's just mash numbers on the keyboard" mode. It's like they're phishing with training wheels on. Props to whoever made this phishing email though – they remembered to add the "Do not share this link" warning in red. Nothing says legitimate security alert like explicitly telling people not to share your sketchy link. Real Coinbase would be so proud. Fun fact: IPv4 addresses are four octets ranging from 0-255, making the valid range 0.0.0.0 to 255.255.255.255. So unless they're trying to pioneer IPv5 with extended ranges, this is just... impressively wrong.

Ultimate Security Update

Ultimate Security Update
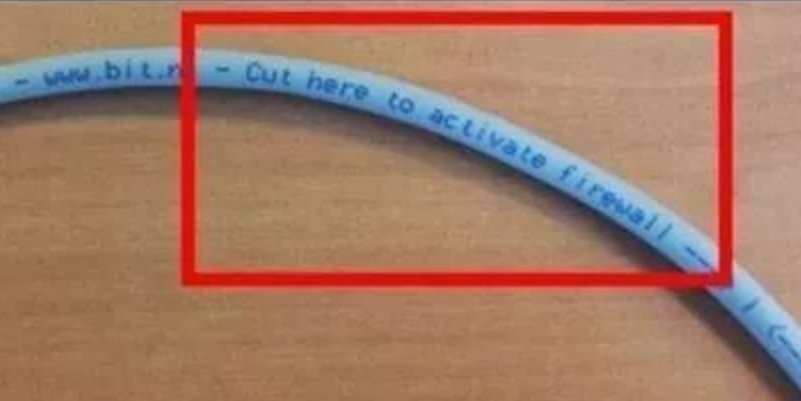
When your security team's idea of "patching vulnerabilities" is literally cutting off the attack vector. Can't exploit what doesn't exist anymore, right? Just snip that pesky activation link clean off. This is basically the physical embodiment of every "just disable the feature" security fix I've ever shipped under pressure. Sure, the phishing link can't work if users physically cannot click it. Problem solved, ticket closed, moving on. 10/10 would recommend this approach for your next penetration test report. "Mitigated all email-based attacks by removing email functionality."

This Is A Very Good Idea

This Is A Very Good Idea
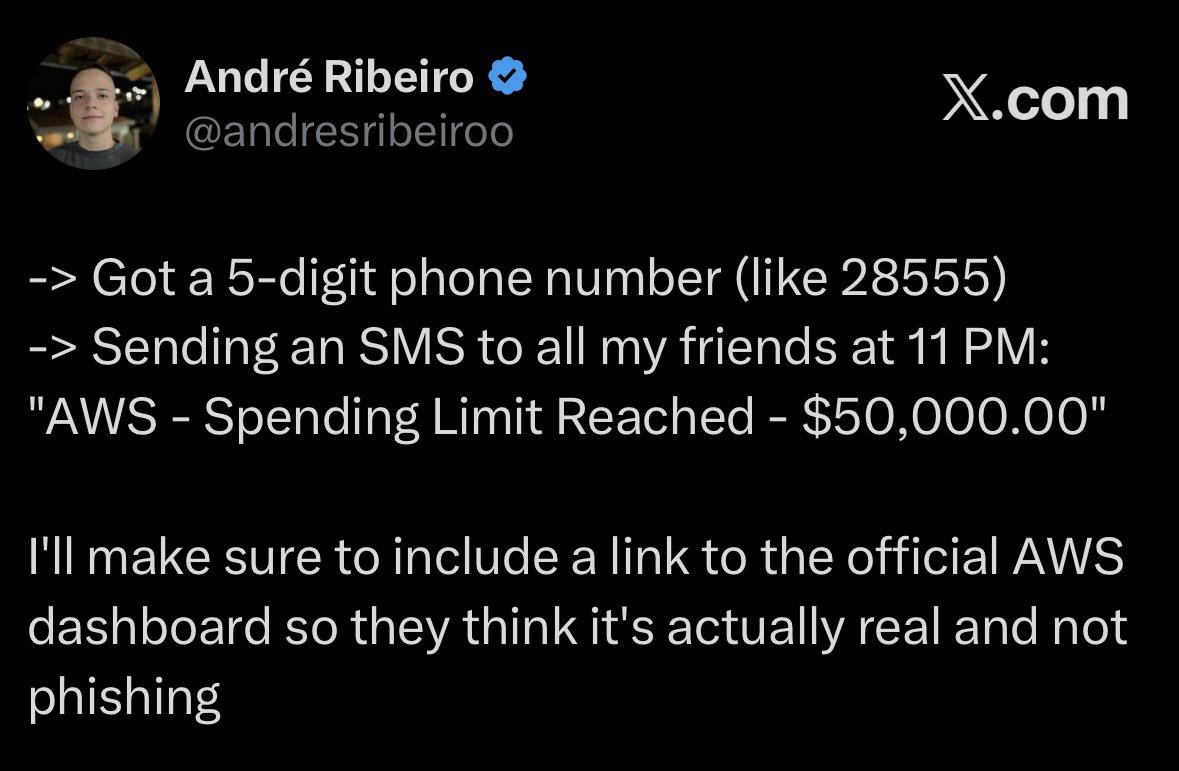
Nothing says "I've learned nothing from security training" quite like this masterpiece. Dude's planning to spoof AWS billing alerts via SMS and even wants to include a link to the "official AWS dashboard" to make it look legit. Because obviously, the best way to prank your friends is by potentially getting arrested for phishing and identity theft. The real comedy here is thinking your friends won't immediately panic and call their bank, or worse, actually click that link. Then you'll be explaining to HR why half the company reported a security incident that traces back to your phone number. Pro tip: if your prank requires you to clarify "it's not phishing," it's definitely phishing. Also, $50k? That's rookie numbers. If you're gonna fake an AWS bill, at least make it realistic—like $127,483.29 from accidentally leaving a NAT Gateway running in 47 regions.

Information Security Expert

Information Security Expert
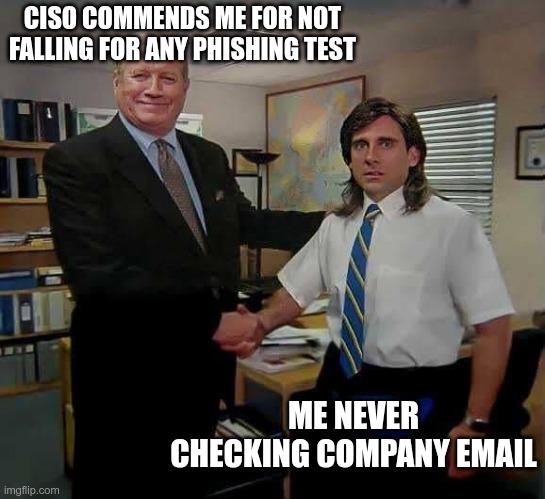
Your CISO is out here throwing you a parade for dodging phishing emails like you're Neo in The Matrix, meanwhile you've been ignoring company emails for three months because you genuinely can't be bothered. The best security practice is just apathy, apparently. Who needs awareness training when you have chronic email avoidance? The irony is *chef's kiss* – you're technically unhackable if you never open anything in the first place. Task failed successfully, security edition.