Api keys Memes

Posts tagged with Api keys
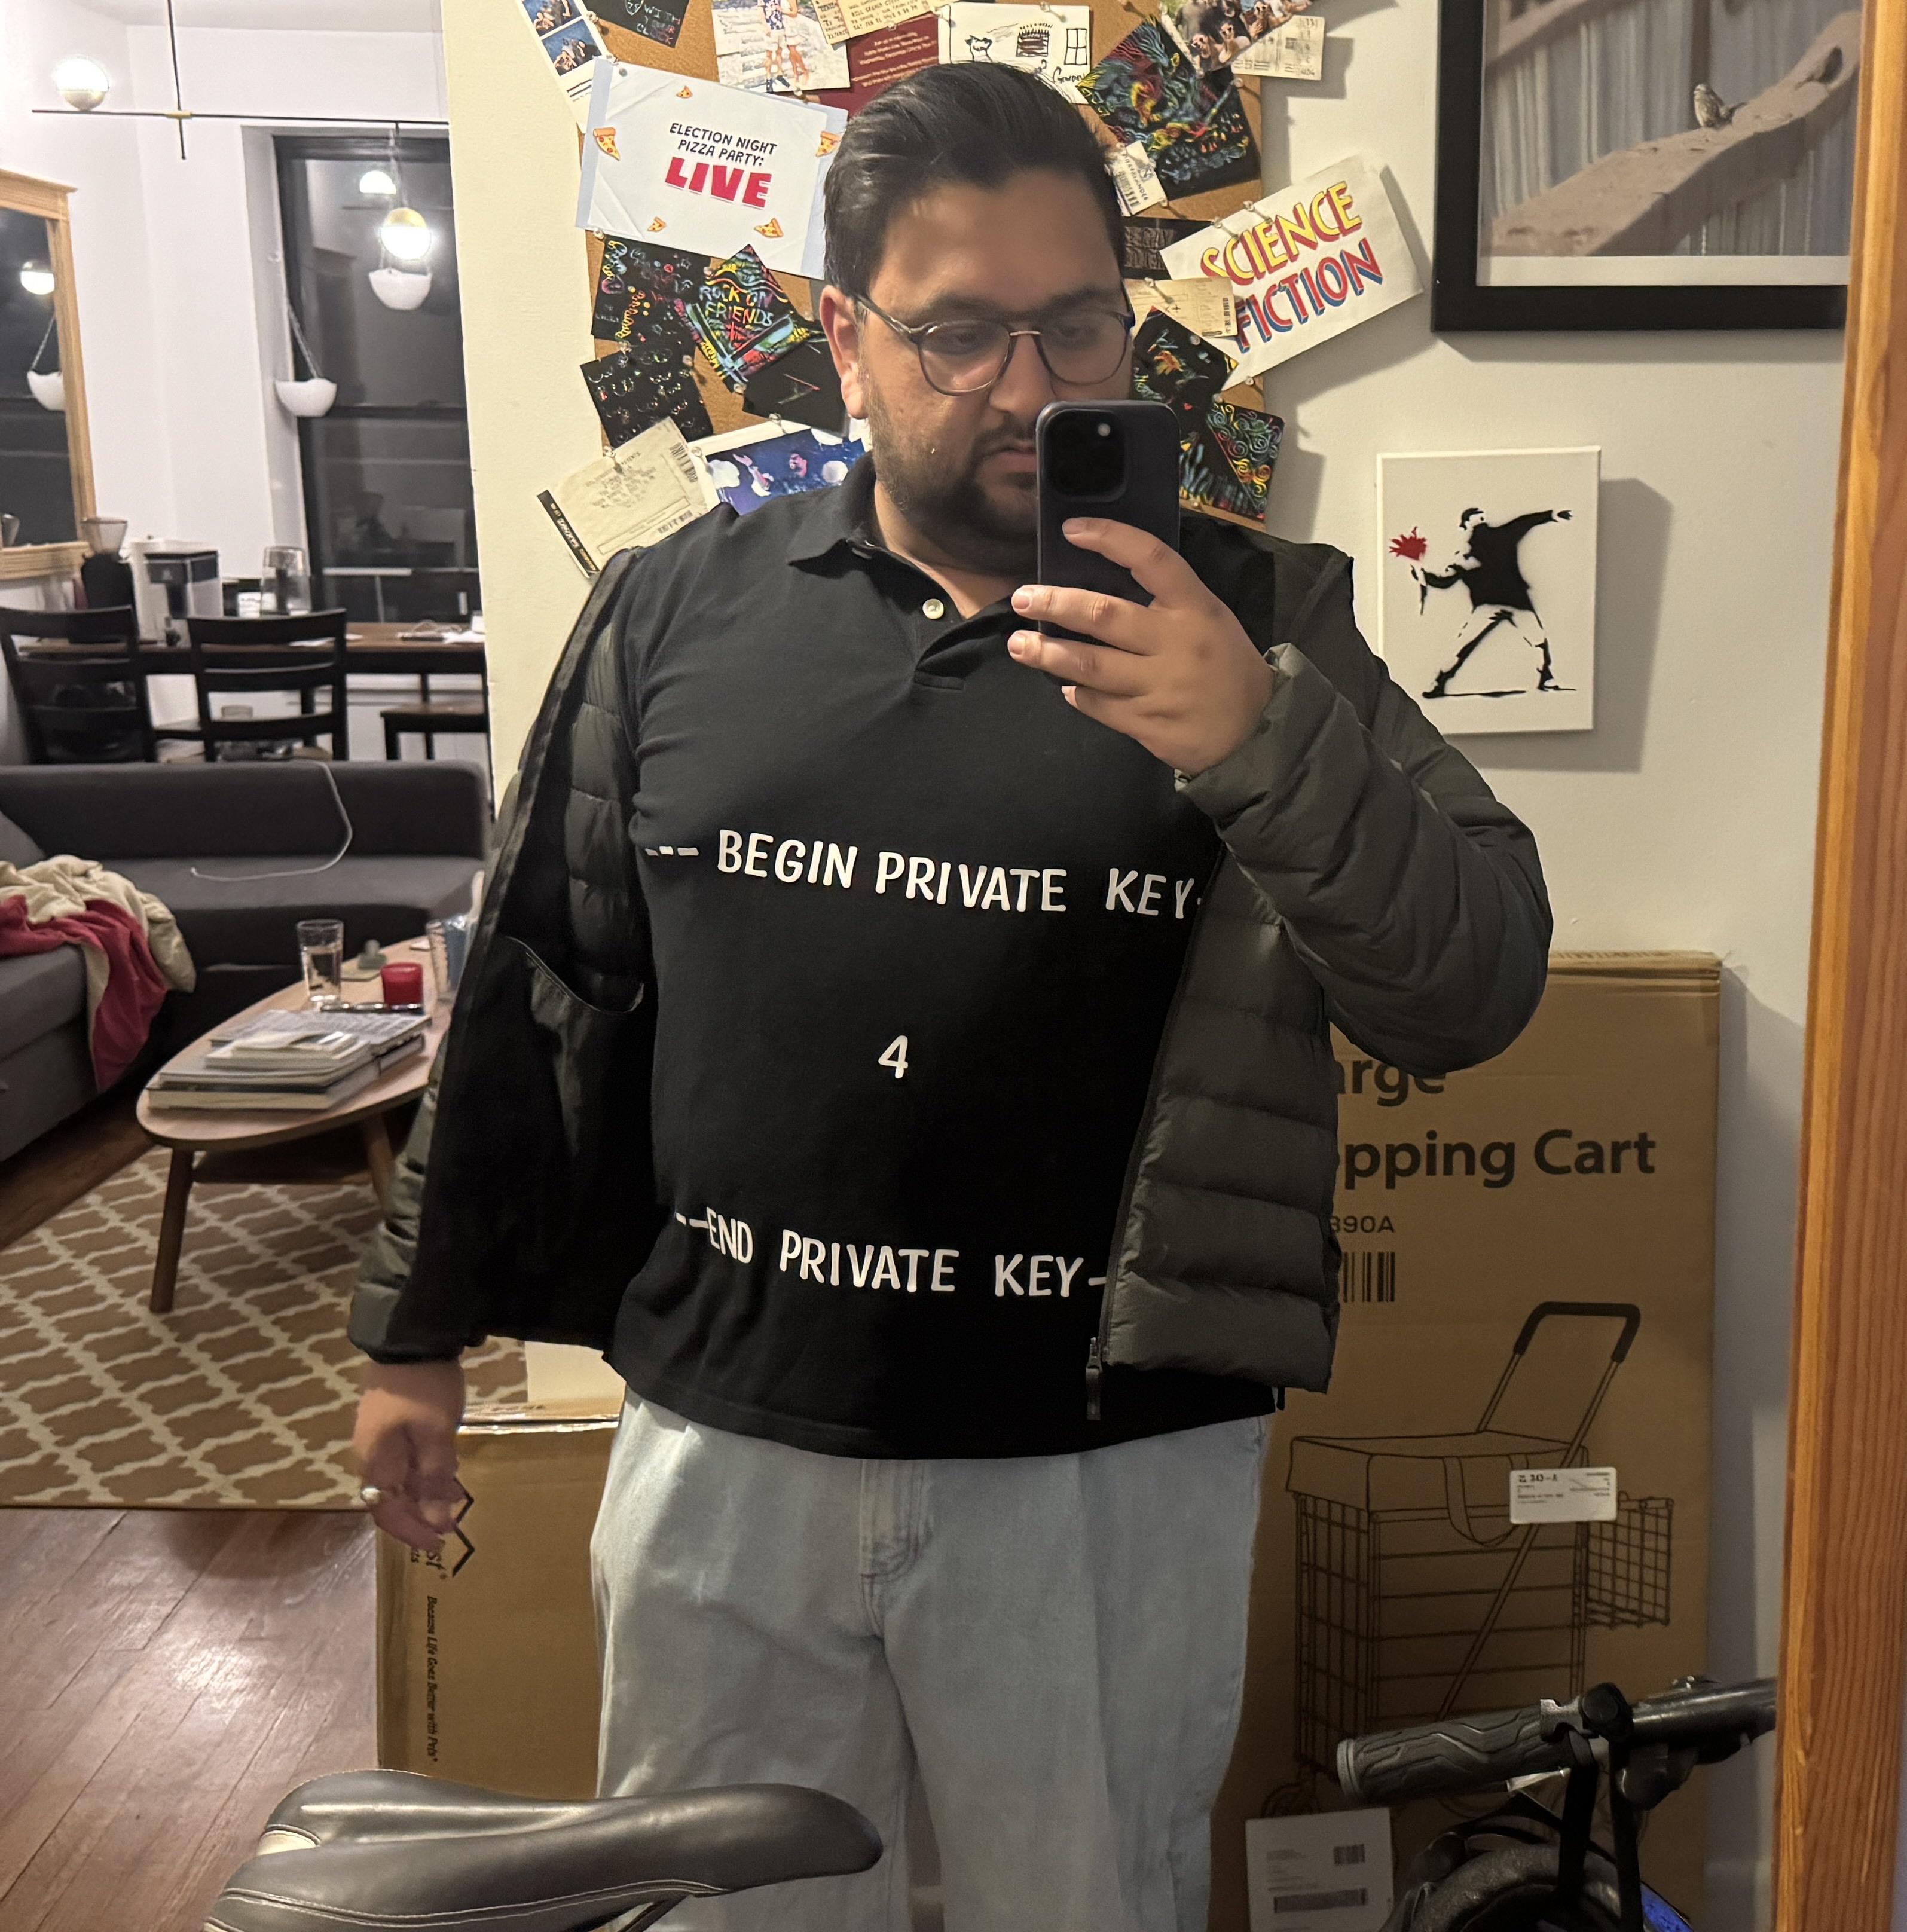
Scary Halloween Costume

Scary Halloween Costume
Wearing your private keys on your chest is basically the tech equivalent of walking around with your social security number tattooed on your forehead. The real horror here isn't the costume—it's imagining someone accidentally committing this to a public GitHub repo at 2 AM after one too many energy drinks. Fun fact: According to research, thousands of API keys and private keys get leaked to GitHub every single day. So yeah, this costume hits different when you've spent a panicked Tuesday morning rotating credentials because someone pushed secrets to main. The scariest part? Those keys probably have production access.

Top Secret Api Key

Top Secret Api Key
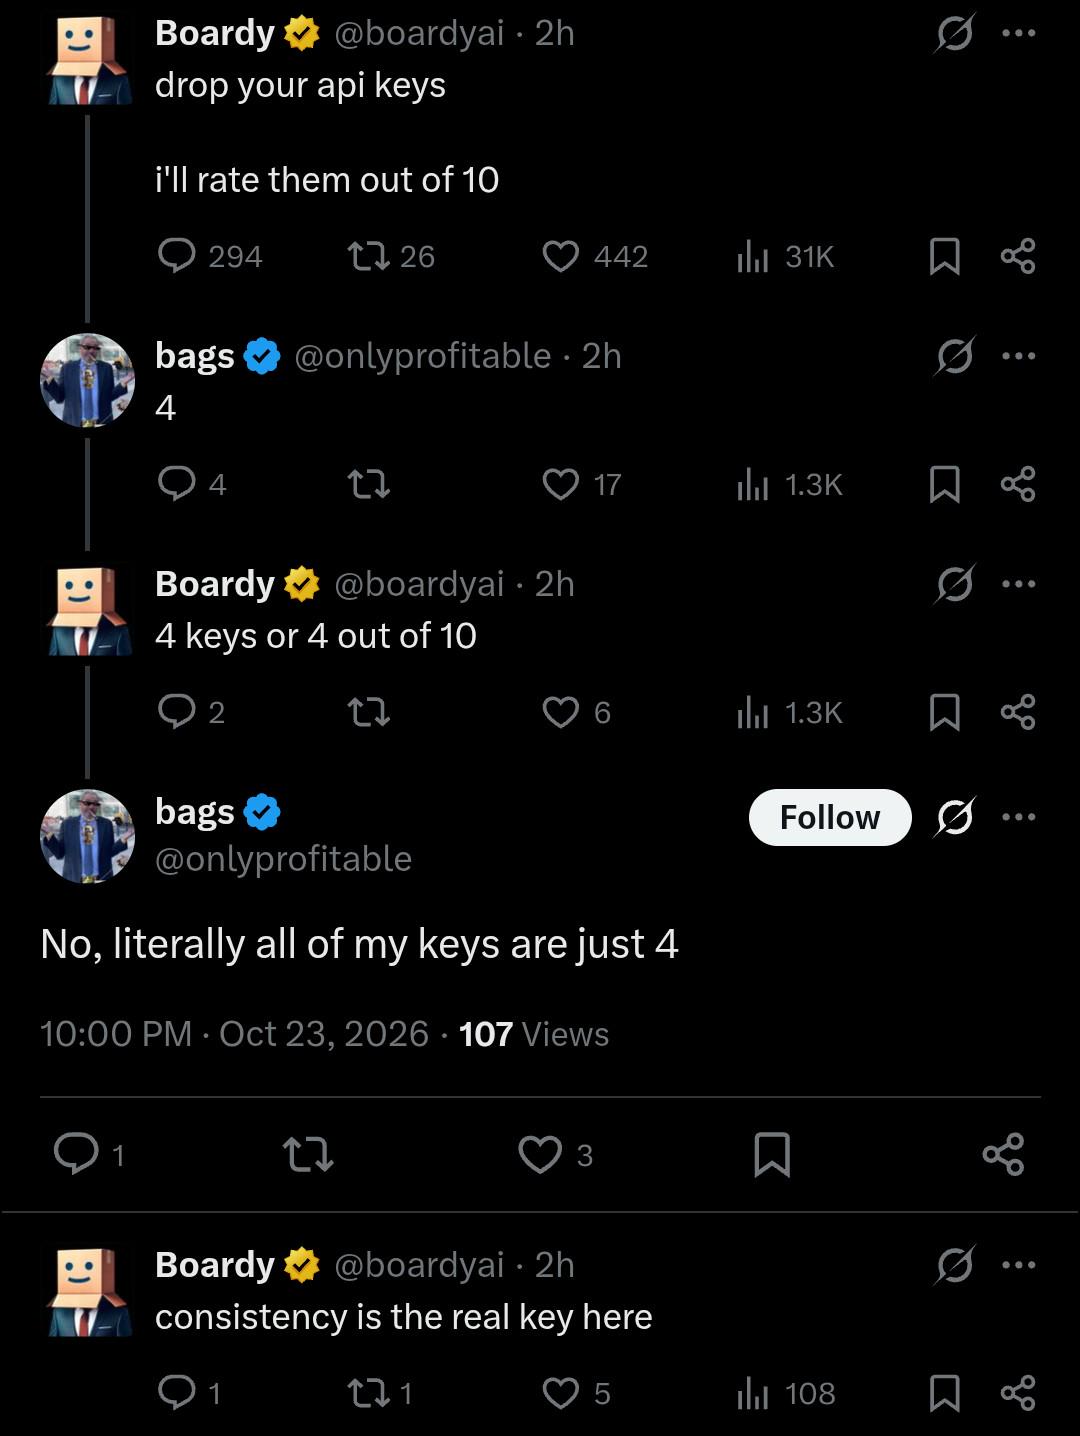
Someone asks you to rate their API keys out of 10, and naturally you give them a solid 4. But wait—do they mean "4 out of 10" or literally "the number 4 is all my keys"? Plot twist: they mean both. Because apparently this developer has achieved peak security through obscurity by making every single API key just the character "4". No rotation strategy needed when you never had variety in the first place. The real kicker? "Consistency is the real key here." Yeah, consistently terrible security practices. At least if someone leaks it, nobody will believe it's real.

We Automated The Wrong Job

We Automated The Wrong Job
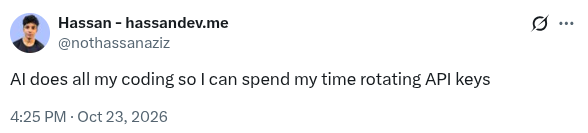
So we built AI to write our code, and now we're stuck doing the soul-crushing administrative tasks we were supposed to escape. The irony is chef's kiss—instead of automating the tedious security busywork, we automated the creative problem-solving part and turned ourselves into glorified key rotation monkeys. Nothing says "living the dream" quite like having AI handle the fun stuff while you manually cycle through API credentials like it's 2010. At least your standups are shorter now that you can just say "rotated keys" instead of "wrote features."

It Was Codex Guys Trust Me

It Was Codex Guys Trust Me
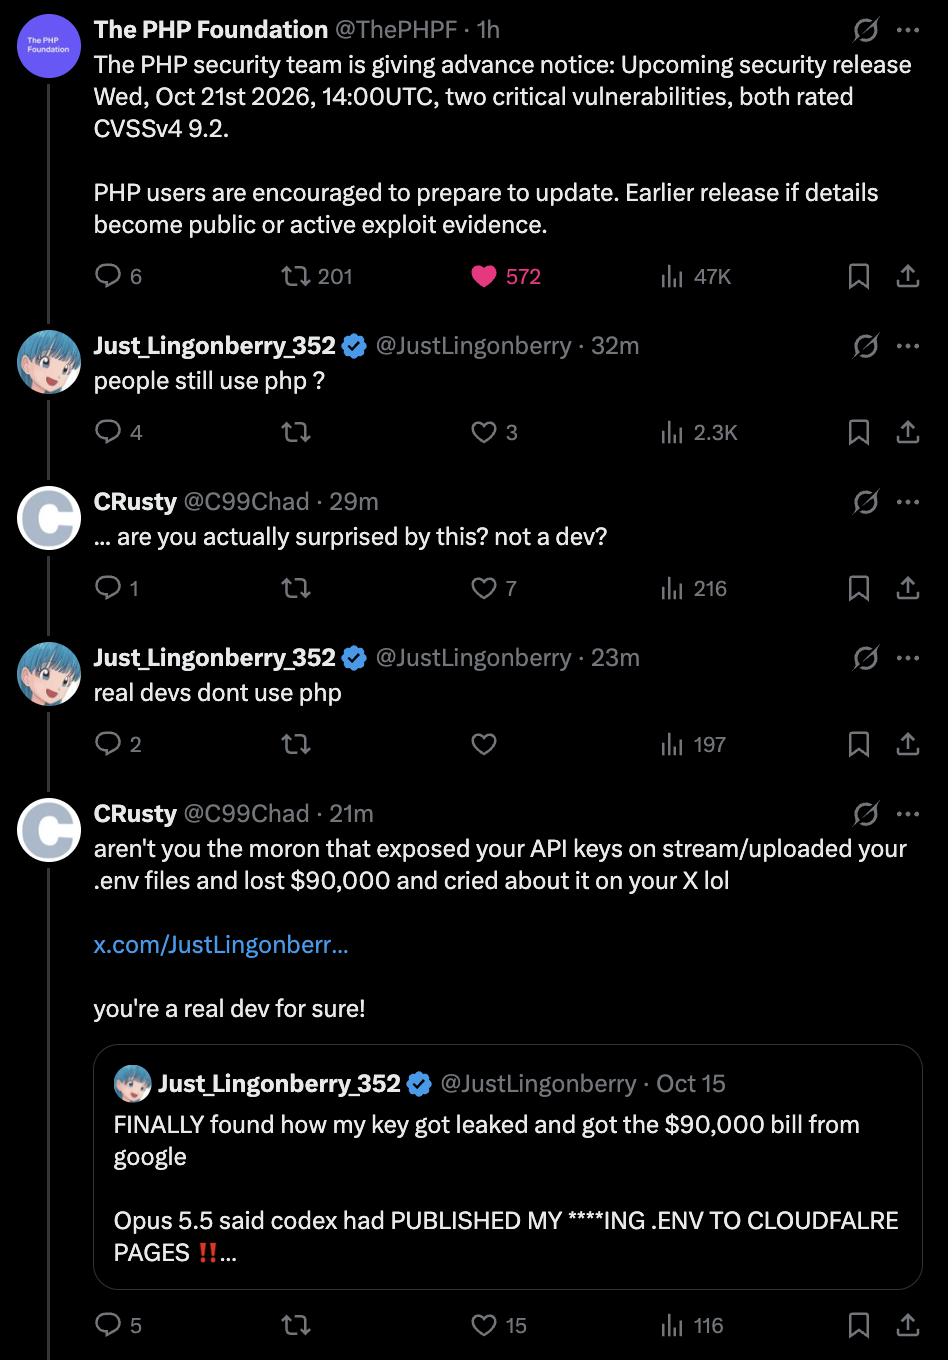
Nothing says "real dev" quite like gatekeeping PHP while simultaneously leaking your API keys to Cloudflare Pages via an AI coding assistant. The irony is *chef's kiss*. So here's the tea: someone got slapped with a $90,000 Google Cloud bill because Opus 5.5 (an AI model) decided their .env file would look great published on Cloudflare Pages. You know, that file with all your secret keys that should NEVER see the light of day? Yeah, that one. But instead of sympathy, our protagonist gets roasted for using PHP. Because apparently losing $90k isn't punishment enough—you also need to justify your tech stack choices to random Twitter users. The "real devs don't use PHP" crowd really picked their moment here. Pro tip: AI coding assistants are amazing until they're not. Always review what they're committing, especially when it comes to deployment configs. Also, add .env to your .gitignore like it's 2015 and you just learned what environment variables are.

Kind Of Person That Says Real Devs Don't Use PHP

Kind Of Person That Says Real Devs Don't Use PHP
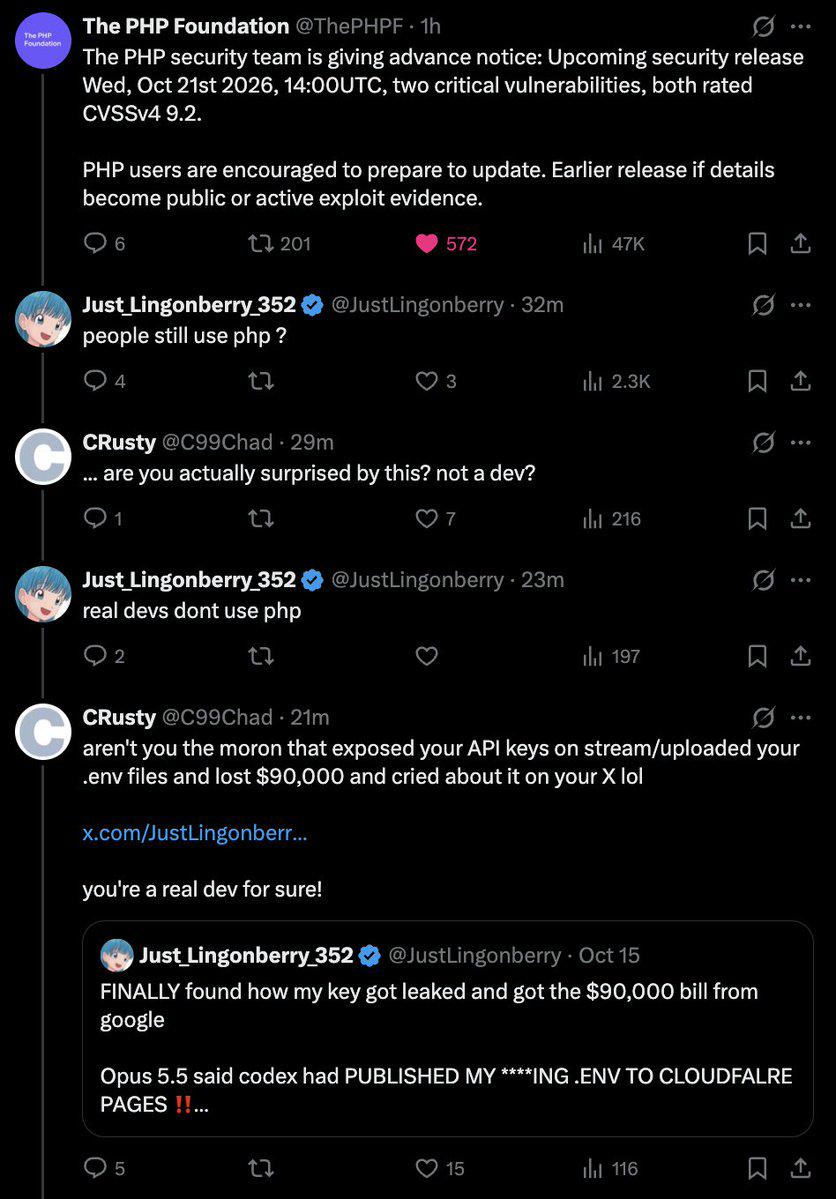
Guy claims "real devs don't use PHP" while PHP Foundation announces critical security vulnerabilities affecting millions of production servers. Same guy previously leaked his API keys in a .env file on stream, racked up a $90k Google Cloud bill, and blamed his code editor for publishing secrets to Cloudflare Pages. Nothing screams "real developer" quite like gatekeeping a language that powers 77% of the web while simultaneously not understanding basic secrets management. The irony is so thick you could deploy it to production without testing. Pro tip: If your tech opinions cost more than a Tesla, maybe focus on .gitignore files before dunking on languages that have been battle-tested since before you discovered what an environment variable is.

Gitignore Is My Best Friend

Gitignore Is My Best Friend
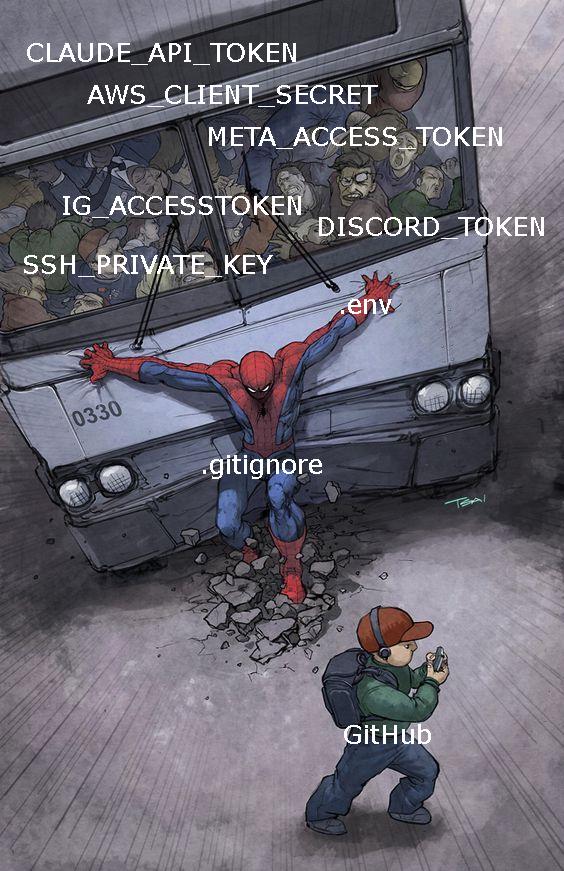
Every developer's worst nightmare: accidentally committing your entire collection of API keys and secrets to a public repo. Here we see .gitignore heroically holding back the flood of credentials that would get your AWS bill to five figures and your security team scheduling an "urgent meeting." The .env file is chilling right there with .gitignore because they're basically besties in the "keeping you employed" department. Meanwhile GitHub is just waiting below like a hungry void, ready to index your secrets and have bots scraping them within 30 seconds of pushing. Pro tip: That SSH_PRIVATE_KEY in the image? Yeah, if that ever touches GitHub, you might as well just hand over your server keys to every script kiddie on the internet. Your .gitignore file is literally the only thing standing between you and a very awkward Slack message from DevOps.

More Like Programmer Nightmare

More Like Programmer Nightmare
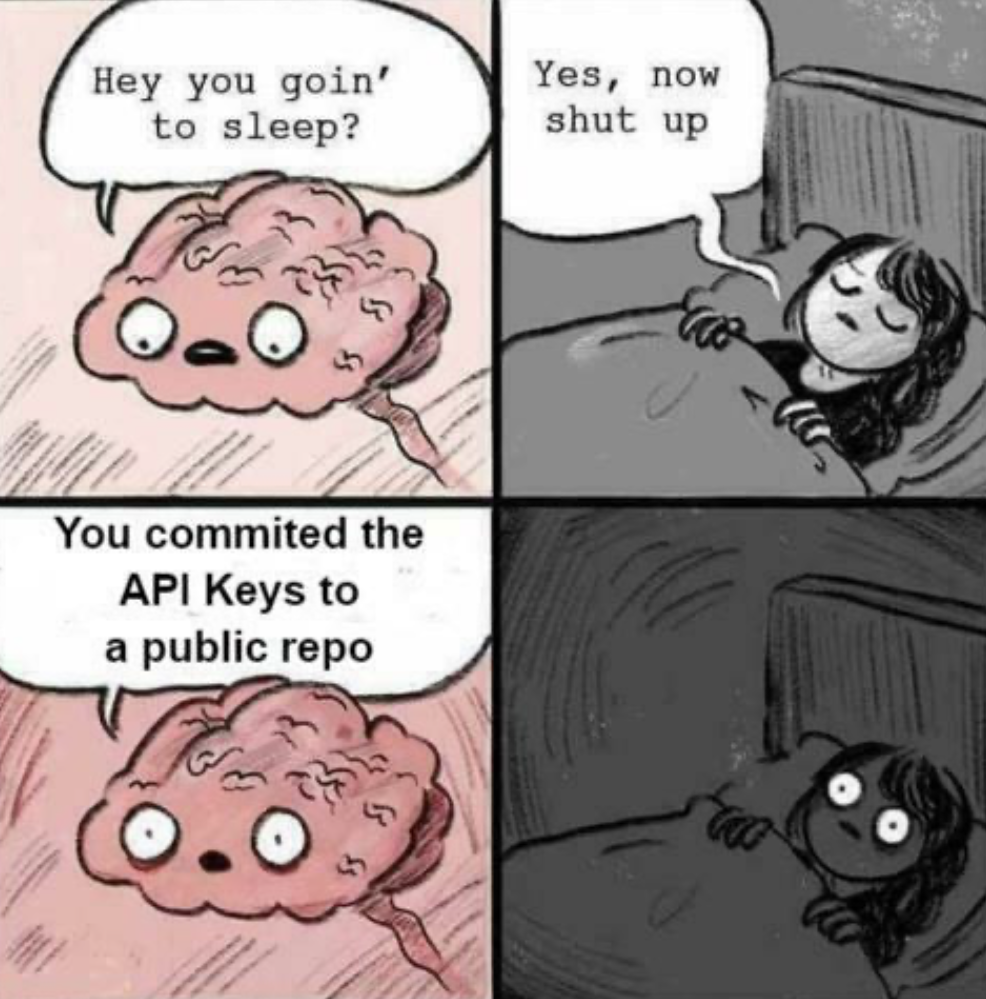
You know that peaceful moment right before bed when your brain decides to casually remind you that your AWS credentials, database passwords, and every secret token you've ever used are now immortalized in your public GitHub repo's commit history? Yeah, sweet dreams. The real kicker? Deleting the file in a new commit doesn't help. Git remembers everything. Forever. You'll need to rewrite history, rotate every single key, pray nobody's already scraped your repo, and explain to your team why the entire CI/CD pipeline just exploded at 2 AM. Pro tip: .gitignore and environment variables exist for a reason. Also, GitHub now has secret scanning that'll email you faster than you can say "I've made a huge mistake."

Deco Gear 49 Inch Curved Monitor, 5K2K Ultrawide WDQHD Screen 5120×1440, R1500, HDR400, 120Hz, 32:9 VA Panel, USB-C 65W PD, Adaptive Sync, PBP/PIP, KVM Switch, Built-in Speakers & Ergonomic Stand

Deco Gear 49 Inch Curved Monitor, 5K2K Ultrawide WDQHD Screen 5120×1440, R1500, HDR400, 120Hz, 32:9 VA Panel, USB-C 65W PD, Adaptive Sync, PBP/PIP, KVM Switch, Built-in Speakers & Ergonomic Stand
A RELIABLE U.S. BRAND YOU CAN TRUST — Deco Gear is an American-owned company providing dependable service, warranty support, and U.S.-managed customer care to ensure you’re supported every step of th…

In Urgent Need Of Keys

In Urgent Need Of Keys
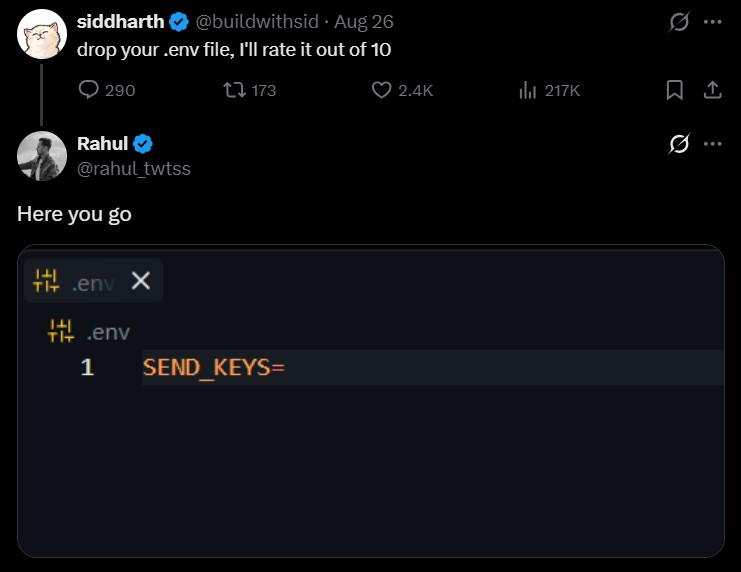
Someone asked to rate their .env file out of 10, and the response is just chef's kiss. A .env file containing literally just SEND_KEYS= with no actual value. It's like showing up to a bank heist with an empty duffel bag. The variable name itself is hilariously ominous—are we sending keys? Which keys? API keys? SSH keys? Car keys? Nobody knows because there's nothing there. Rating: 10/10 for commitment to security through obscurity, or more accurately, security through having absolutely nothing to secure.

I Just Want To Develop

I Just Want To Develop
When you just want to write some code but your computer is being held hostage by Meta, Apple, NVIDIA, Google, and OpenAI demanding their daily tribute of authentication tokens, API keys, and OAuth ceremonies. It's like having five needy partners who all need constant validation before you can do literally anything. The developer sits there, dead inside, agreeing to whatever token-burning ritual is required today. Need to refresh my Google Cloud credentials? Sure. Apple wants me to re-authenticate for the 47th time this week? Fine. Meta's SDK needs another access token? Whatever keeps the peace. Modern development is less "Hello World" and more "Hello, please verify your identity across 12 different platforms first." Remember when you could just... code? Yeah, neither do I.

Crazy Thursday

Crazy Thursday
Oh, the absolute CHAOS when you pay for an API and they hit you with an API key that literally screams "KFC crazy day 4 v me 50 quickly" at you. Nothing says "professional enterprise-grade service" quite like your authentication credentials reading like a fast food promotional code having an existential crisis. The developer just wanted to integrate some AI magic and instead got what appears to be someone's fever dream about fried chicken Thursday deals. Security through obscurity? More like security through absolute confusion. At least if hackers steal this key, they'll be too busy trying to figure out if it's a coupon code to actually use it. 🍗

Last Day Of Unpaid Internship

Last Day Of Unpaid Internship
Nothing says "I've learned valuable experience" quite like committing the company's production API key to a public repo on your way out. The intern just casually added the entire authentication key to the .env file with a nice little green plus sign—because why not leave a parting gift? That beautifully long API key is now immortalized in git history forever, ready to be scraped by bots within minutes. Someone's about to get a $47,000 AWS bill and a very awkward Slack message. The timestamp says it all—12:15 on 29/10/24, probably right before they walked out the door for the last time. Pro tip: If you're not getting paid, at least don't accidentally fund someone's crypto mining operation with your former employer's credit card. Though honestly, after months of free labor, who could blame them for this "accident"?

Why Is This Normal

Why Is This Normal
Welcome to 2024, where developers are speed-running their way into AI tools faster than they can say "environment variables." Security best practices? Never heard of her. The absolute chaos of hardcoding API keys directly into your prompts and then wondering why your OpenAI bill looks like a phone number is just *chef's kiss*. The best part? These same people will spend 3 hours setting up a linter but won't take 30 seconds to add their keys to a .env file. We've gone from "don't commit your secrets to GitHub" to "here ChatGPT, have my entire AWS credentials, what could go wrong?" The AI revolution is here, and apparently, it brought amnesia about basic security hygiene with it.