Menu
The first computer bug was literally a moth.
Home
Hot
Random
Search
Browse
AI
AWS
Agile
Algorithms
Android
Apple
Azure
Backend
Bash
C++
Cloud
All Categories
HTTP 418: I'm a teapot
The server identifies as a teapot now and is on a tea break, brb
HTTP 418: I'm a teapot
The server identifies as a teapot now and is on a tea break, brb
Hashing Memes
Posts tagged with Hashing
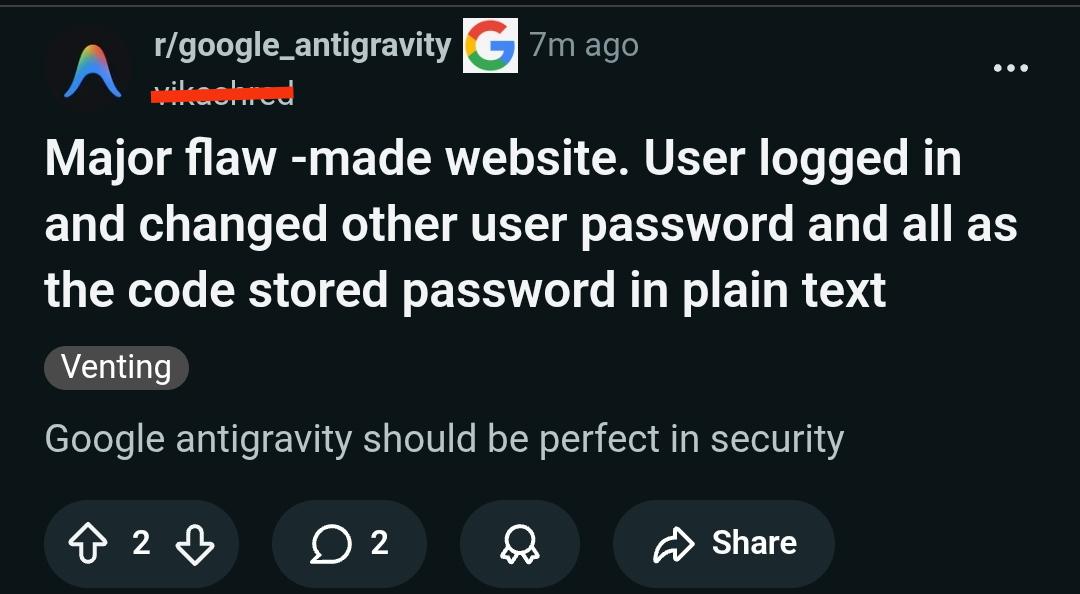
Who Could Have Predicted It
Security
Backend
Webdev
Programming
Databases
8 months ago
599.5K views
0 shares
Storing passwords in plain text? That's not a security flaw, that's a cry for help. Someone out there built a website where you could log in as User A, casually change User B's password, and the system just... let it happen. Because why hash passwords when you can live dangerously? The real kicker? They're posting this in r/google_antigravity expecting sympathy, as if Google's AI products should somehow be immune to the consequences of Security 101 violations. Spoiler alert: even the most advanced AI can't protect you from storing credentials like it's 1995. The "Venting" tag really ties it all together. Nothing says professional development quite like discovering your authentication system is basically a public notepad with extra steps.
Salty
Security
Backend
Programming
8 months ago
446.1K views
0 shares
When your password security is so bad that even the waitress knows your hashing strategy. Guy orders something at the diner and can't identify what's on his plate, but don't worry—they salted the hash. You know, for security. Salting hashes is Password Storage 101: you add random data to passwords before hashing so two identical passwords don't produce the same hash. It's literally the bare minimum you should be doing if you're storing user credentials. But here's the thing—if someone's complaining they "can't identify" what they're looking at, your security probably has bigger problems than whether you remembered to salt. The "Privacy Diner" is serving up cryptographic puns with a side of existential dread about how your data is actually being handled. Spoiler: it's probably not as secure as you think.
Storing Passwords The Easy Way
Security
Databases
Programming
Webdev
Backend
1 year ago
386.0K views
0 shares
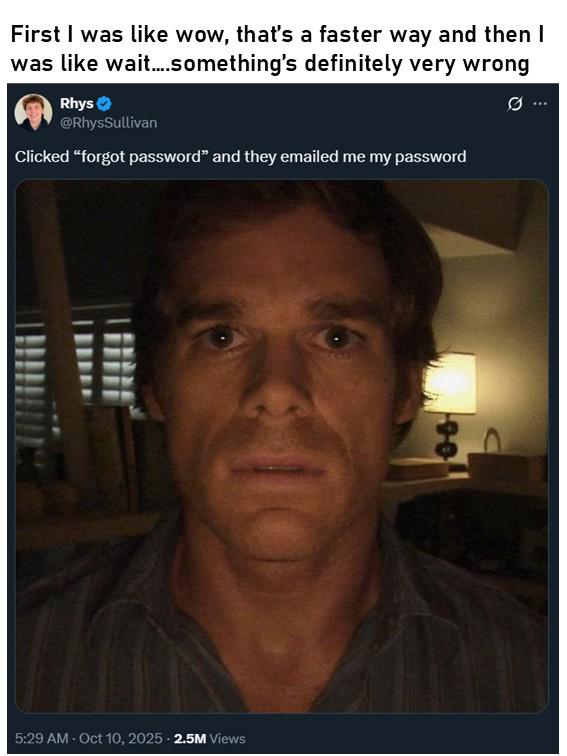
SWEET MOTHER OF CRYPTOGRAPHY! 😱 The absolute HORROR of clicking "forgot password" and getting your ACTUAL PASSWORD emailed back to you! That's not a convenience feature—that's a full-blown security NIGHTMARE! It means they're storing your precious password in plain text like it's some casual grocery list! Any half-decent developer would be HYPERVENTILATING right now. Proper password storage should involve hashing, salting, and praying to the security gods—not keeping them in a "passwords.txt" file labeled "super important don't hack"! If a website emails your password back, run away screaming and change that password EVERYWHERE you've used it because honey, that database is one curious intern away from catastrophe! 💀
Reduces DB Size Drastically
Security
Databases
Programming
Backend
1 year ago
357.4K views
0 shares
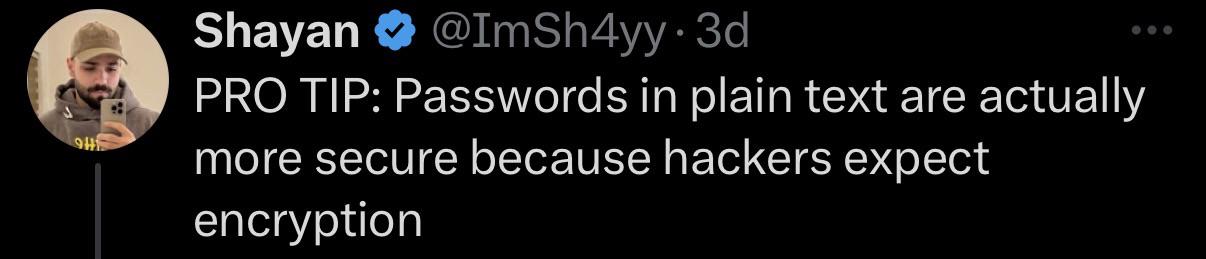
Ah, the "security through obscurity" approach taken to its logical conclusion. Storing passwords in plaintext - because nothing says "enterprise-grade security" like keeping all your users' credentials in a format readable by the intern who accidentally got database access. Sure, it reduces DB size by skipping that pesky hashing algorithm. Your database might be smaller, but so will your company after the inevitable breach. The cybersecurity equivalent of leaving your house key under the doormat because "no burglar would look there."
Python Programming Language Bumper Sticker Vinyl Decal 5"
Affiliate
Stickers
Vision Signs
Size - Approx 5 inches · Will stick to just about any flat or slightly curved surface. Use it on cars, walls, windows, plastics, metal, wood, poles and more. · We print using the highest resolution g…
Best I Can Do Is A Reset
Security
Databases
Programming
Backend
1 year ago
360.2K views
0 shares
The eternal dance of users forgetting passwords and sysadmins shrugging helplessly! Proper password storage means even admins can't see your actual password - they can only nuke it back to factory settings. That's not incompetence; that's security by design . Your password should be a one-way hash buried so deep that even the database admin is just staring at a cryptographic salad. If your IT person CAN tell you your password, update your resume immediately because that company's security is more vulnerable than PHP without input sanitization.
No Salt, Just Pure Security Theater
Security
Programming
Databases
1 year ago
435.9K views
1 shares
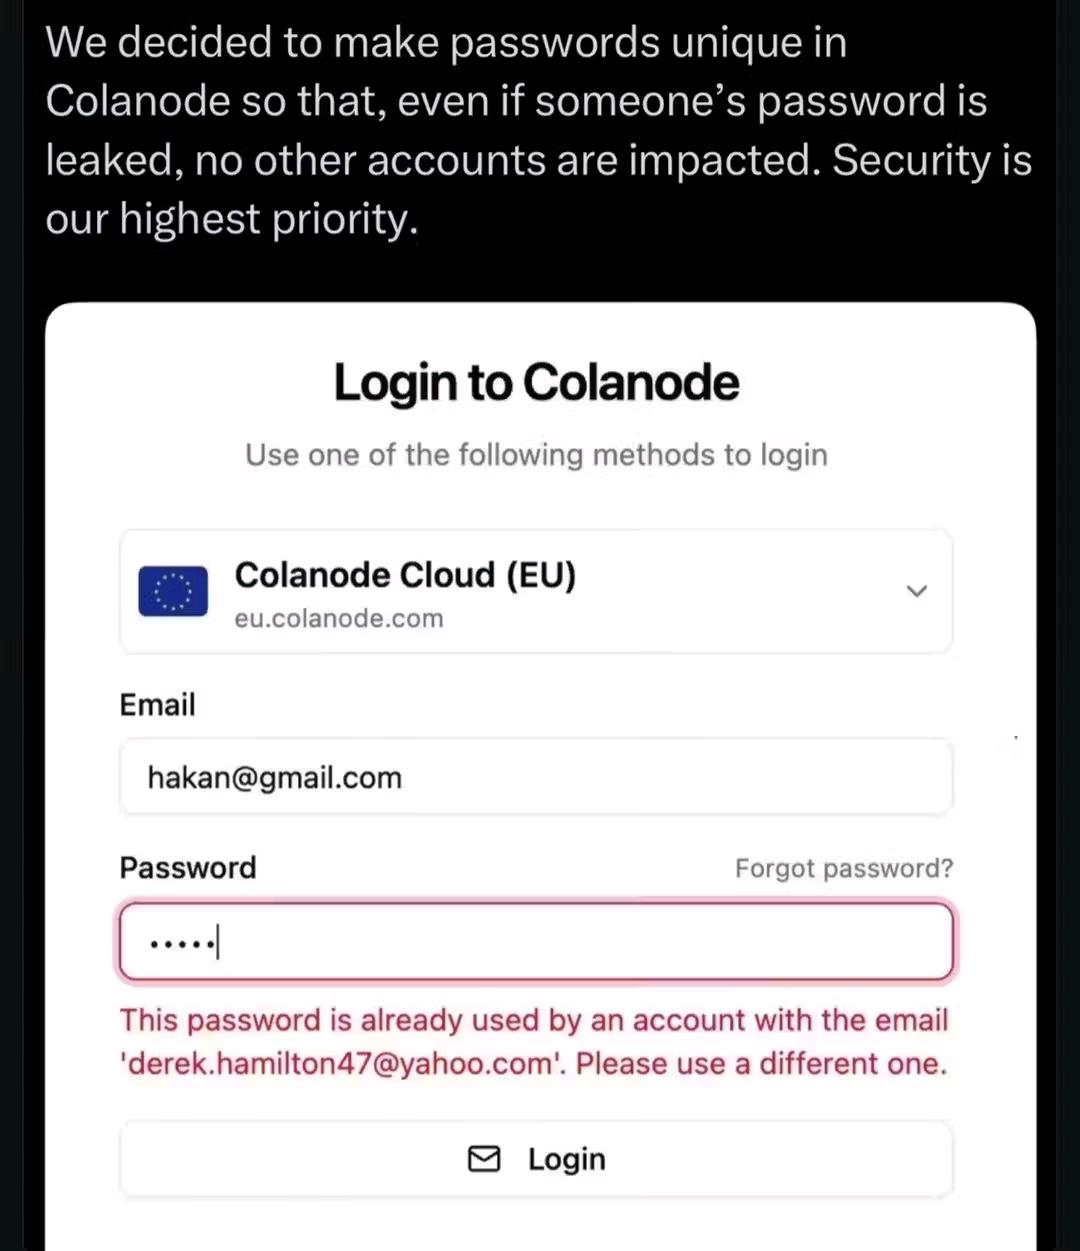
OMG THE IRONY IS KILLING ME! 💀 They're all "security is our highest priority" and then IMMEDIATELY expose that Derek and Hakan use the EXACT SAME PASSWORD! Like, honey, you had ONE job - making passwords unique - and you've failed so spectacularly that your error message is literally doxxing other users! This isn't just shooting yourself in the foot, it's nuking your entire security philosophy from orbit! The password isn't even salted - it's SEASONED with a sprinkle of complete incompetence!
Digital Fort Knox vs. Rusty Gate Security
Security
Programming
Networking
1 year ago
425.4K views
1 shares
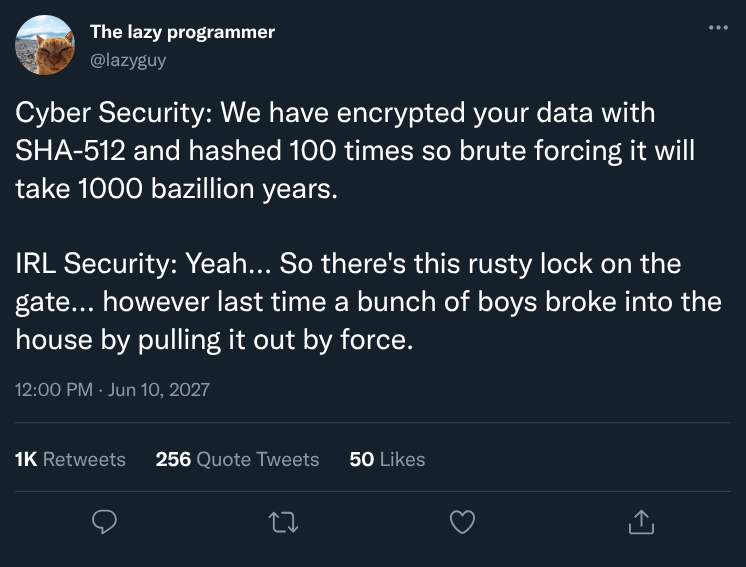
Oh. My. GOD. The AUDACITY of the security contrast! 💀 In the digital realm, we're over here flexing with SHA-512 encryption and hash functions that would make supercomputers weep into their cooling systems for bazillion years... meanwhile, real-world security is literally defeated by a group of teenagers with the revolutionary hacking technique of "pull harder." The digital world: "We've created an IMPENETRABLE FORTRESS of mathematical complexity!" The physical world: "Have you tried wiggling the doorknob? It's kind of sticky but usually works."
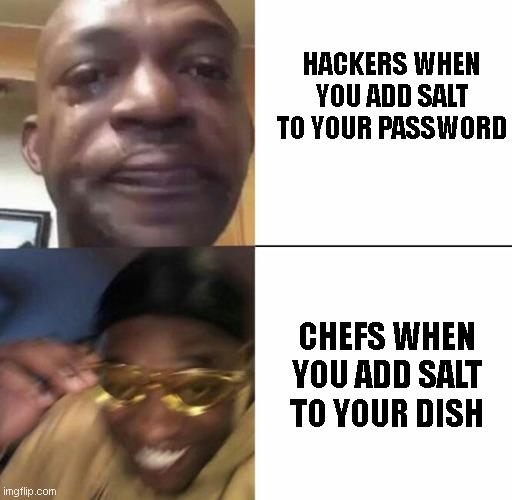
Salt: Making Hackers Cry And Chefs Smile
Security
Programming
1 year ago
302.3K views
0 shares
The cybersecurity pun that keeps on giving! In password security, "salt" refers to random data added to passwords before hashing them, making them significantly harder to crack with rainbow tables or brute force attacks. Meanwhile, chefs just get excited about basic seasoning. Hackers crying because you've ruined their day with proper security practices is the digital equivalent of Gordon Ramsay finding the lamb sauce. Security experts everywhere are quietly nodding while sipping their coffee from "My password is stronger than yours" mugs.
Elenco - Deluxe Full Function Digital Multimeter Kit [ M-2666K ]
Affiliate
Developer Tools
Elenco
Extra large 1 x 3,5 inch digit display · TESTS Overload protection, Capacitance to 200µF, Diode test, Transistor tester · Audio continuity, AC/DC current to 20A, Low battery indication · RUBBER HOLST…
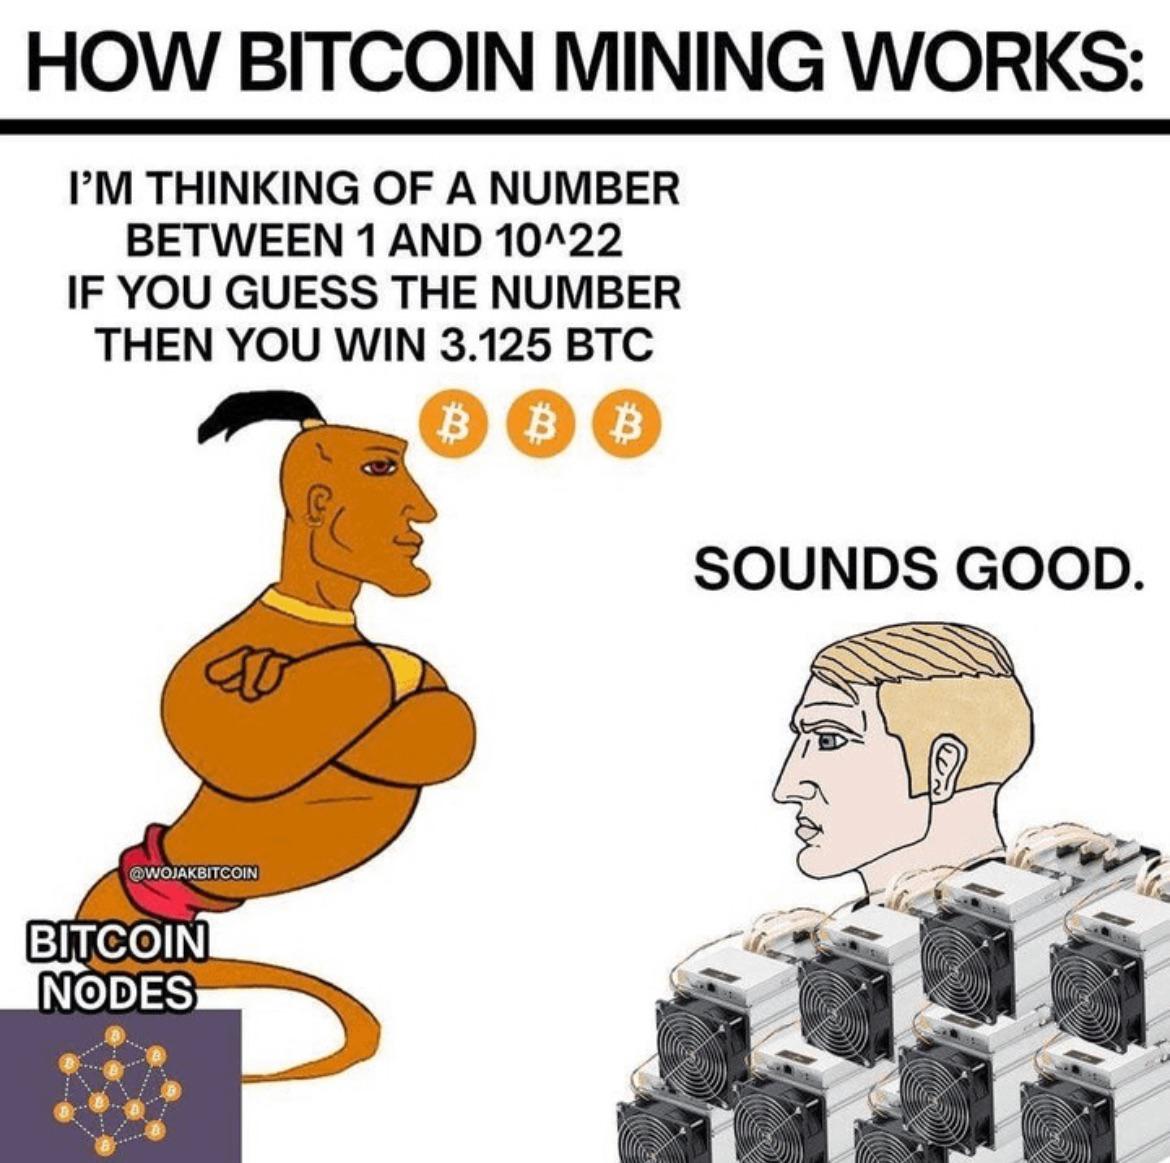
Programmers Gambling Addiction
Algorithms
Math
Hardware
Programming
Security
1 year ago
785.6K views
2 shares
Oh. My. GOD! Bitcoin mining explained in the most SAVAGE way possible! 😱 Imagine playing a cosmic lottery where you're trying to guess a number between 1 and 10 22 (that's a 1 with TWENTY-TWO zeros after it, sweetie). The odds are so astronomically ridiculous that your computer would literally burst into flames before guessing correctly! Yet here we are, with thousands of miners worldwide melting the polar ice caps with their electricity consumption just to play this mathematical slot machine from hell. And for what? The CHANCE to win 3.125 Bitcoin that they'll probably never sell because "it might go up more." The delusion is BREATHTAKING!
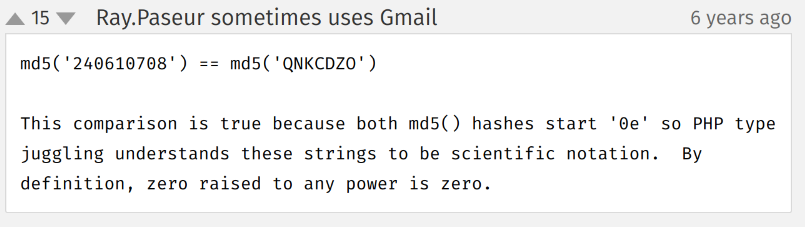
PHP's Accidental Hash Collision Feature
php
Security
Programming
Debugging
1 year ago
450.1K views
0 shares
Behold, PHP's infamous type juggling strikes again! The meme shows how md5('240610708') == md5('QNKCDZO') evaluates to true despite being completely different strings. What's happening? Both MD5 hashes begin with '0e' followed by digits, which PHP helpfully interprets as scientific notation (0×10^something). And since 0 raised to any power equals 0, PHP thinks both hashes equal zero. It's basically comparing 0==0. This is why strict comparison ( === ) exists in PHP. Without it, you might accidentally authenticate someone with the wrong password! Security nightmare fuel for any developer who values their sanity.
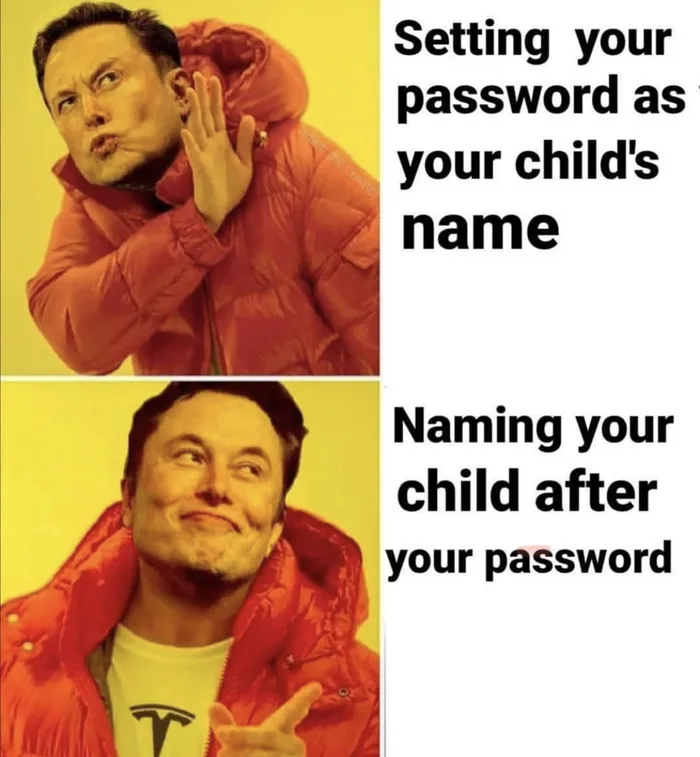
Naming Your Child After Your Password
Security
Programming
1 year ago
268.7K views
1 shares
That awkward moment when your kid's teacher can't pronounce "$2Y$10$UgTh9EyUvedMTndo0PvF4.YkZaHx6OsMirqjR6ApgAsnPrRikwBgs" during roll call. On the plus side, absolutely no one is stealing this kid's identity. The ultimate security-minded parent move: not using your kid's name as your password, but using your incomprehensible bcrypt hash as your kid's name. Modern problems require modern solutions.
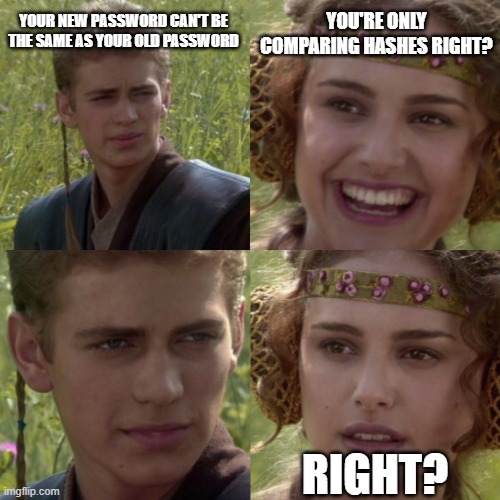
Your New Password Can't Be The Same As Your Old Password... Right?
Security
Webdev
Programming
Backend
Databases
1 year ago
357.8K views
0 shares
When a site tells you "your new password can't be the same as your old password," they're supposed to be comparing hashed values, not storing your actual password in plaintext. If they know what your old password was , they've already failed Security 101. The fact that a Fortune 500 company did this is like finding out your bank keeps everyone's money in a shoebox under the receptionist's desk. Ten years in tech and I'm still amazed at how many multi-billion dollar companies can't figure out basic password security.
TeeUnion Funny DIY Repair Mechanic T-Shirt for Men – I Watched a YouTube Video Shirt Heather Navy
Affiliate
Apparel
TeeUnion
For the DIY Mechanic Who Thinks YouTube Can Fix Anything – This funny repair t-shirt is perfect for men who love tackling projects themselves—whether they actually know what they’re doing or just wat…
Loading more content...
Today's picks
Blue Yeti Nano Premium USB Microphone - Shadow Grey (Renewed)
Affiliate
$56.49
Finally Useful Quantum Computing
Programming
99.1K views
2 years ago
Backend Developer Life
Backend
338.2K views
9 months ago