Data leak Memes

Posts tagged with Data leak
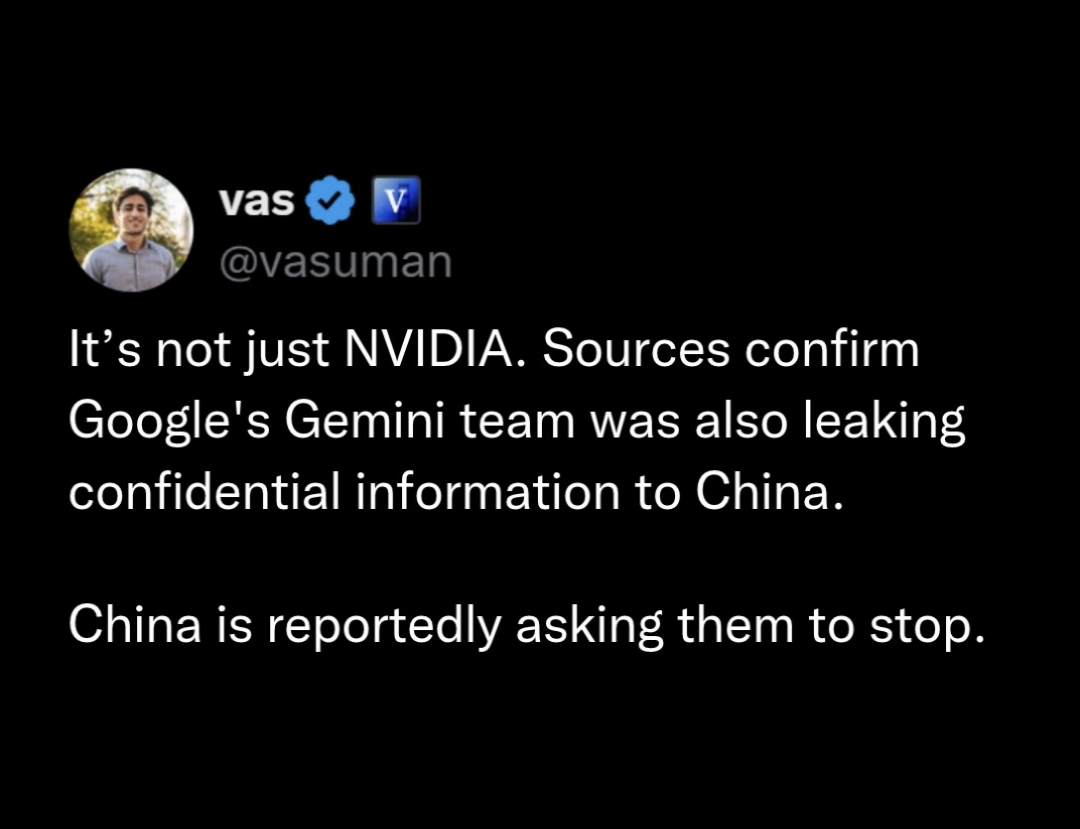
At Least We Can Trust Google

At Least We Can Trust Google
So Google's Gemini team is allegedly leaking confidential info to China, and China's response is basically "bro, please stop sending us your secrets." The irony is chef's kiss level. It's like a spy thriller where the spy is so incompetent that the enemy has to file a restraining order. First NVIDIA had security issues, now Google's AI division is apparently playing fast and loose with data security. At this rate, the tech industry's approach to confidentiality is less "need-to-know basis" and more "literally everyone will know eventually." Maybe we should just start hosting our secrets on GitHub public repos—at least then it's intentional. The title "At Least We Can Trust Google" is doing some Olympic-level sarcasm gymnastics here. Trust Google? Sure, right after I trust my code to work on the first compile.

Free Recon For Attackers

Free Recon For Attackers
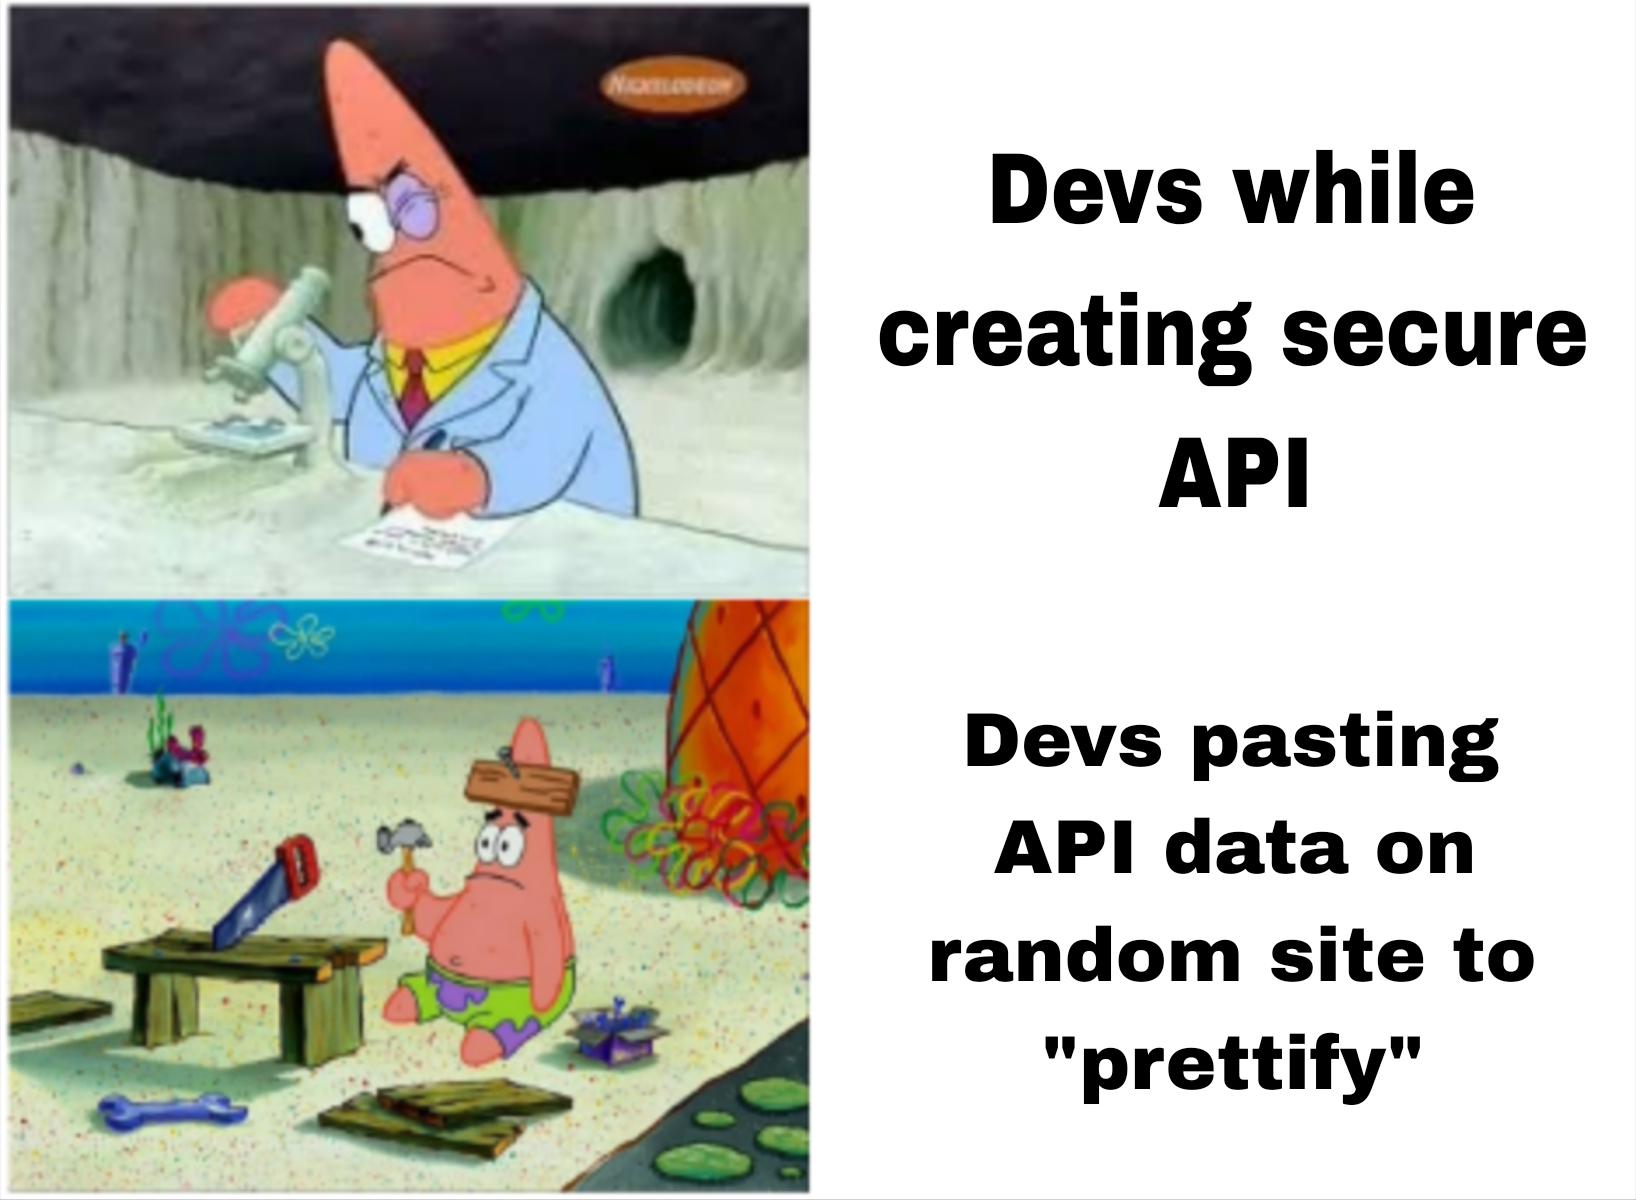
You spend weeks implementing OAuth2, rate limiting, input validation, and encrypted endpoints. Then Steve from frontend pastes your entire API response—complete with internal IDs, database schemas, and server versions—into some sketchy online JSON formatter because he couldn't be bothered to install a browser extension. Congratulations, you just gave potential attackers a complete map of your infrastructure. For free. The security team is thrilled. Pro tip: Those "prettify JSON" websites? They log everything. Your API keys, session tokens, customer data—all sitting in someone's server logs in a country with interesting privacy laws. But hey, at least the JSON looked nice and indented.

Day 1 As Vibe Coder

Day 1 As Vibe Coder
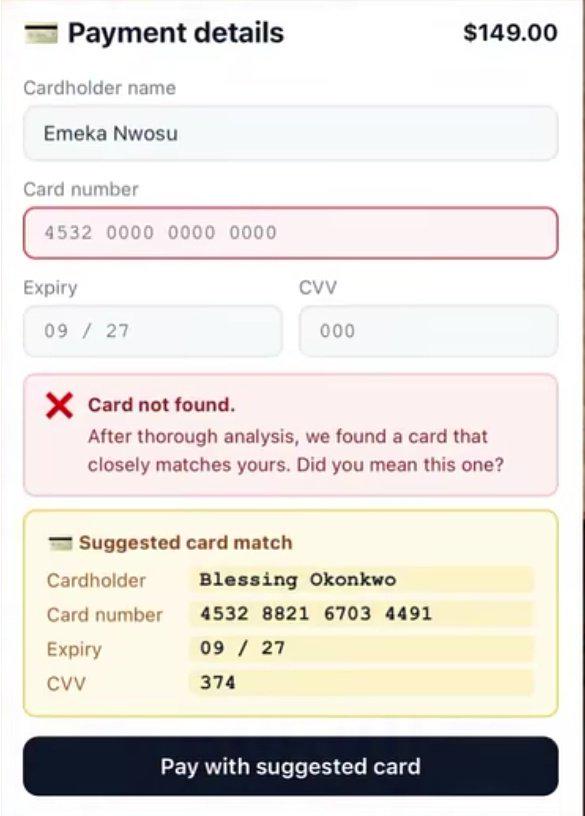
So you're vibing so hard with AI coding assistants that you let them handle your payment form, and now the error message is literally suggesting someone else's credit card details? Complete with a different name, full card number, CVV, and everything? This is what happens when you copy-paste that AI-generated code without reading it. The "thorough analysis" found a card alright—probably from the training data or some poor soul named Blessing Okonkwo whose info got hardcoded into the suggestion logic. Nothing says "production-ready" like your payment gateway playing matchmaker with random credit cards. Day 1 as a vibe coder: Ship fast, debug never, accidentally commit financial fraud. The CVV is even there. Chef's kiss. 💀

Confidential Information

Confidential Information
Nothing says "I value my employment" quite like uploading your entire company's proprietary codebase to an AI chatbot because you couldn't remember if that variable should be called userData or userInfo . Your security team is definitely not having a stroke right now. The best part? The AI probably suggested data anyway. Worth it.

Confidential Information

Confidential Information
When you're too lazy to think of a proper variable name so you casually commit corporate espionage by feeding your entire proprietary codebase and confidential business data into ChatGPT. The risk-reward calculation here is absolutely flawless: potential prison sentence vs. not having to think about whether to call it "userData" or "userInfo". Worth it. Security teams everywhere are having heart palpitations while developers are just out here treating LLMs like their personal naming consultant. The best part? The variable probably ends up being called something generic like "data" anyway after all that risk.

WALI Adjustable Dual Monitor Arm for 13-32 inch Screens, 22 lbs per Arm | Dual Monitor Stand for Desk, Full Motion with Tilt, Swivel, Rotation, C-Clamp & Grommet Base, VESA 75/100mm (GSMP002N), Black

WALI Adjustable Dual Monitor Arm for 13-32 inch Screens, 22 lbs per Arm | Dual Monitor Stand for Desk, Full Motion with Tilt, Swivel, Rotation, C-Clamp & Grommet Base, VESA 75/100mm (GSMP002N), Black
Keep Your Desk Organized: By lifting 2 screens off the desktop, this computer monitor arm opens up valuable space for your keyboard, notebook, docking station or a simple, clutter-free work area. Bui…

Client Side Validation

Client Side Validation
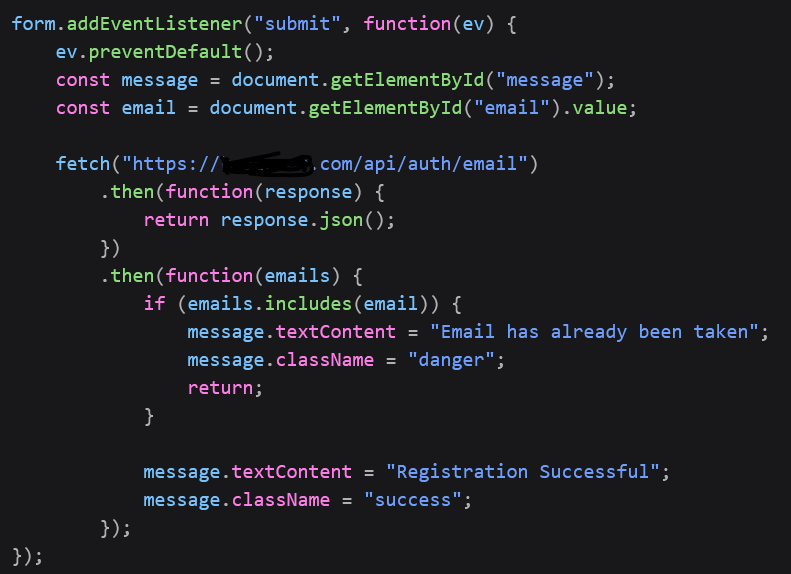
So you're checking if an email is already taken by sending it to the server, getting back a list of all registered emails , and then doing a client-side .includes() check? That's like asking the bank to give you everyone's account numbers just to verify yours doesn't exist yet. Not only is this a massive security vulnerability (congrats, you just leaked your entire user database to anyone with DevTools open), but it's also hilariously inefficient. Why return an array of potentially millions of emails when the server could just return a boolean? The backend dev is probably crying somewhere. The cherry on top? After doing all this client-side "validation," you're still showing success messages without any actual server confirmation. Chef's kiss of terrible architecture. 🤌

Wrong Database, Right Career Move

Wrong Database, Right Career Move
That moment when you accidentally run a query on production instead of staging. First panel: mild panic. Second panel: realizing you just leaked 2.5 billion users' data and your résumé is already outdated. The best part? That smile isn't happiness—it's the face of someone who knows their career just ended but the severance package will be spectacular. Nothing says "database engineer" like casually sipping coffee while committing digital arson.

Biggest Plottwist Ever

Biggest Plottwist Ever
OH. MY. GOD. The absolute TRAGEDY of modern development! 💸 There you are, thinking you're so clever hard-coding API keys in your ChatGPT prompts, and BOOM! OpenAI is just SWIMMING in your precious secrets like Scrooge McDuck in his money bin! The sheer AUDACITY! Your API keys - those expensive little strings that unlock digital kingdoms and drain your wallet with every request - now collected and potentially exposed! THIS is why we can't have nice things in tech! Next time maybe try environment variables like a functioning adult? 🙄