Menu
Regular expressions: Now you have two problems.
Home
Hot
Random
Search
Browse
AI
AWS
Agile
Algorithms

Android

Apple

Azure

Backend

Bash

C++

Cloud
All Categories
HTTP 418: I'm a teapot
The server identifies as a teapot now and is on a tea break, brb
HTTP 418: I'm a teapot
The server identifies as a teapot now and is on a tea break, brb
Two-factor authentication Memes
Posts tagged with Two-factor authentication
Make Auth Great Again
Security
Frontend
Webdev
1 month ago
121.3M views
0 shares
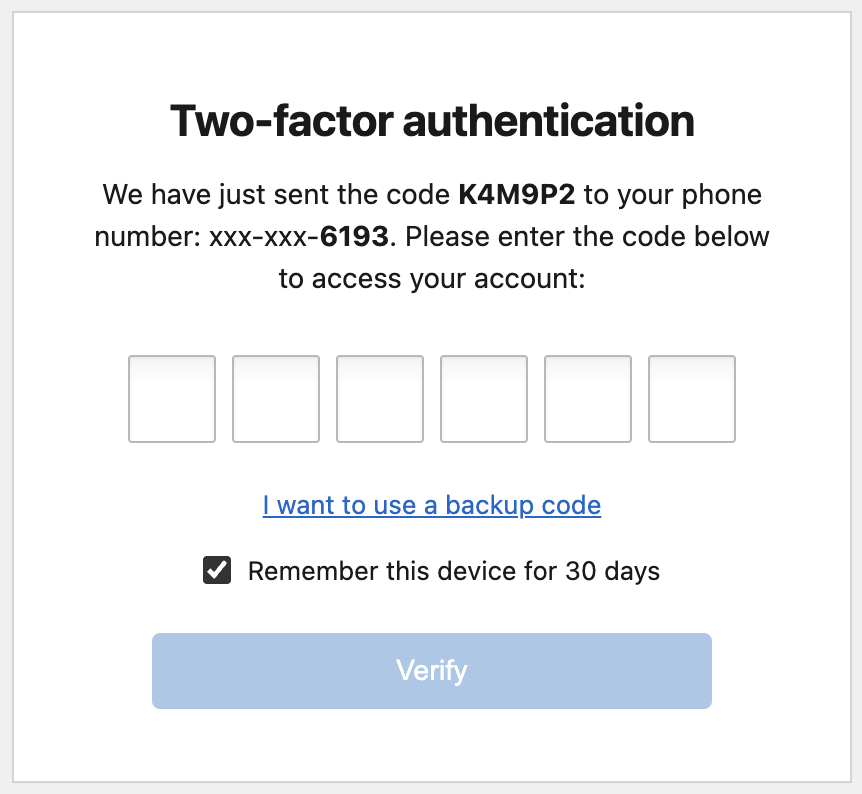
Nothing says "secure authentication" quite like displaying the actual 2FA code right there in the UI. Why bother sending it to your phone when they can just... tell you what it is on the same screen? It's like having a bouncer who whispers the password to everyone at the door. The code is literally K4M9P2 and they want you to type it into six separate boxes. Six boxes for six characters. Because apparently copying and pasting was too convenient, and we need to make users feel like they're defusing a bomb. Also love the "Remember this device for 30 days" checkbox that's already checked by default. Really committing to that whole "two-factor" thing when you only need to do it once a month.
Captcha Or 2FA
Security
Webdev
Frontend
Backend
Programming
2 months ago
90.9M views
0 shares
When your 2FA implementation is so bad it literally defeats its own purpose. They just sent you the code in the same message where they're asking you to enter it. It's like locking your front door but leaving the key taped to the doorknob. At this point, just skip the whole song and dance and log me in automatically. Why make me type six digits when you've already shown them to me? It's security theater at its finest—all the inconvenience of 2FA with absolutely none of the security benefits. Some developer out there really thought "you know what would make this secure? Making them copy-paste!" Peak innovation right there.
Map AI Auto Complete To OTP Auto Complete
Security
Webdev
Frontend
6 months ago
266.3K views
0 shares
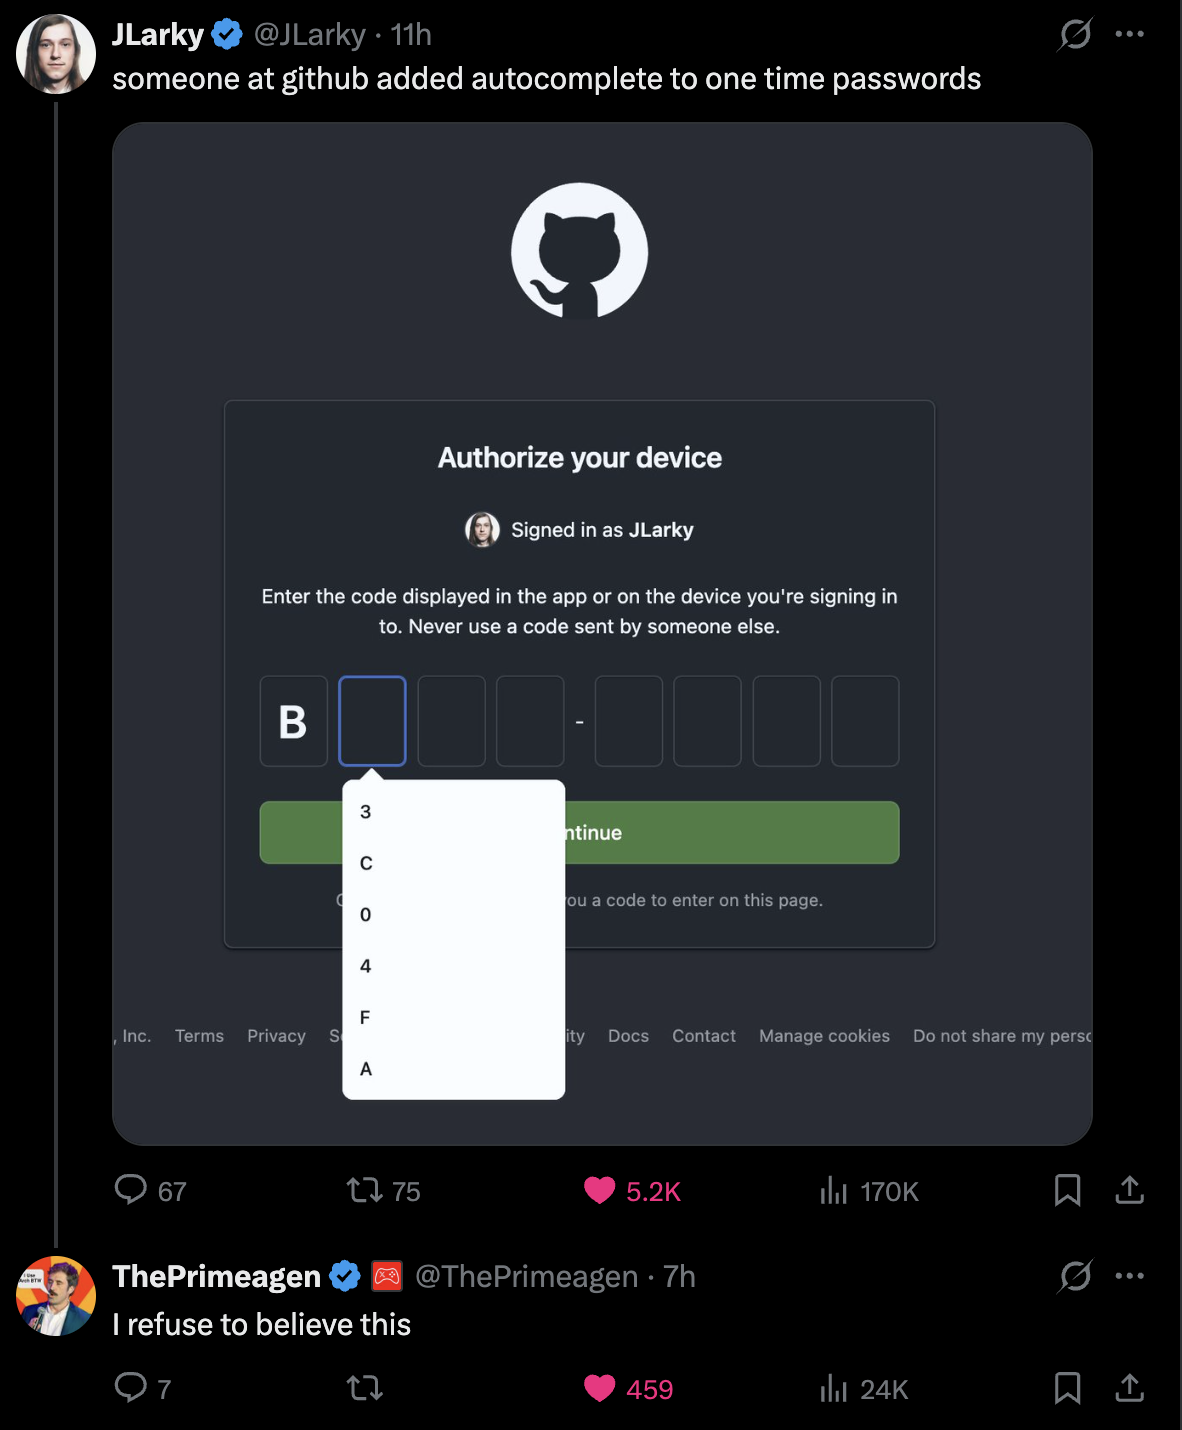
GitHub just implemented autocomplete for one-time passwords. You know, those temporary codes that are supposed to be, uh, one-time and temporary . The ones you're not supposed to save anywhere. The ones that expire in 30 seconds. Someone looked at the OTP field and thought "you know what would make this more convenient? If we just suggested what to type here." The autocomplete dropdown is showing "3C04FA" - which is either a previously used OTP that got cached (defeating the entire purpose of OTPs) or some truly galaxy-brain feature implementation. It's like adding a "remember me" checkbox to a self-destructing message. The security team is probably having a great day.
Make It Make Sense, Google
Security
Programming
11 months ago
476.4K views
0 shares
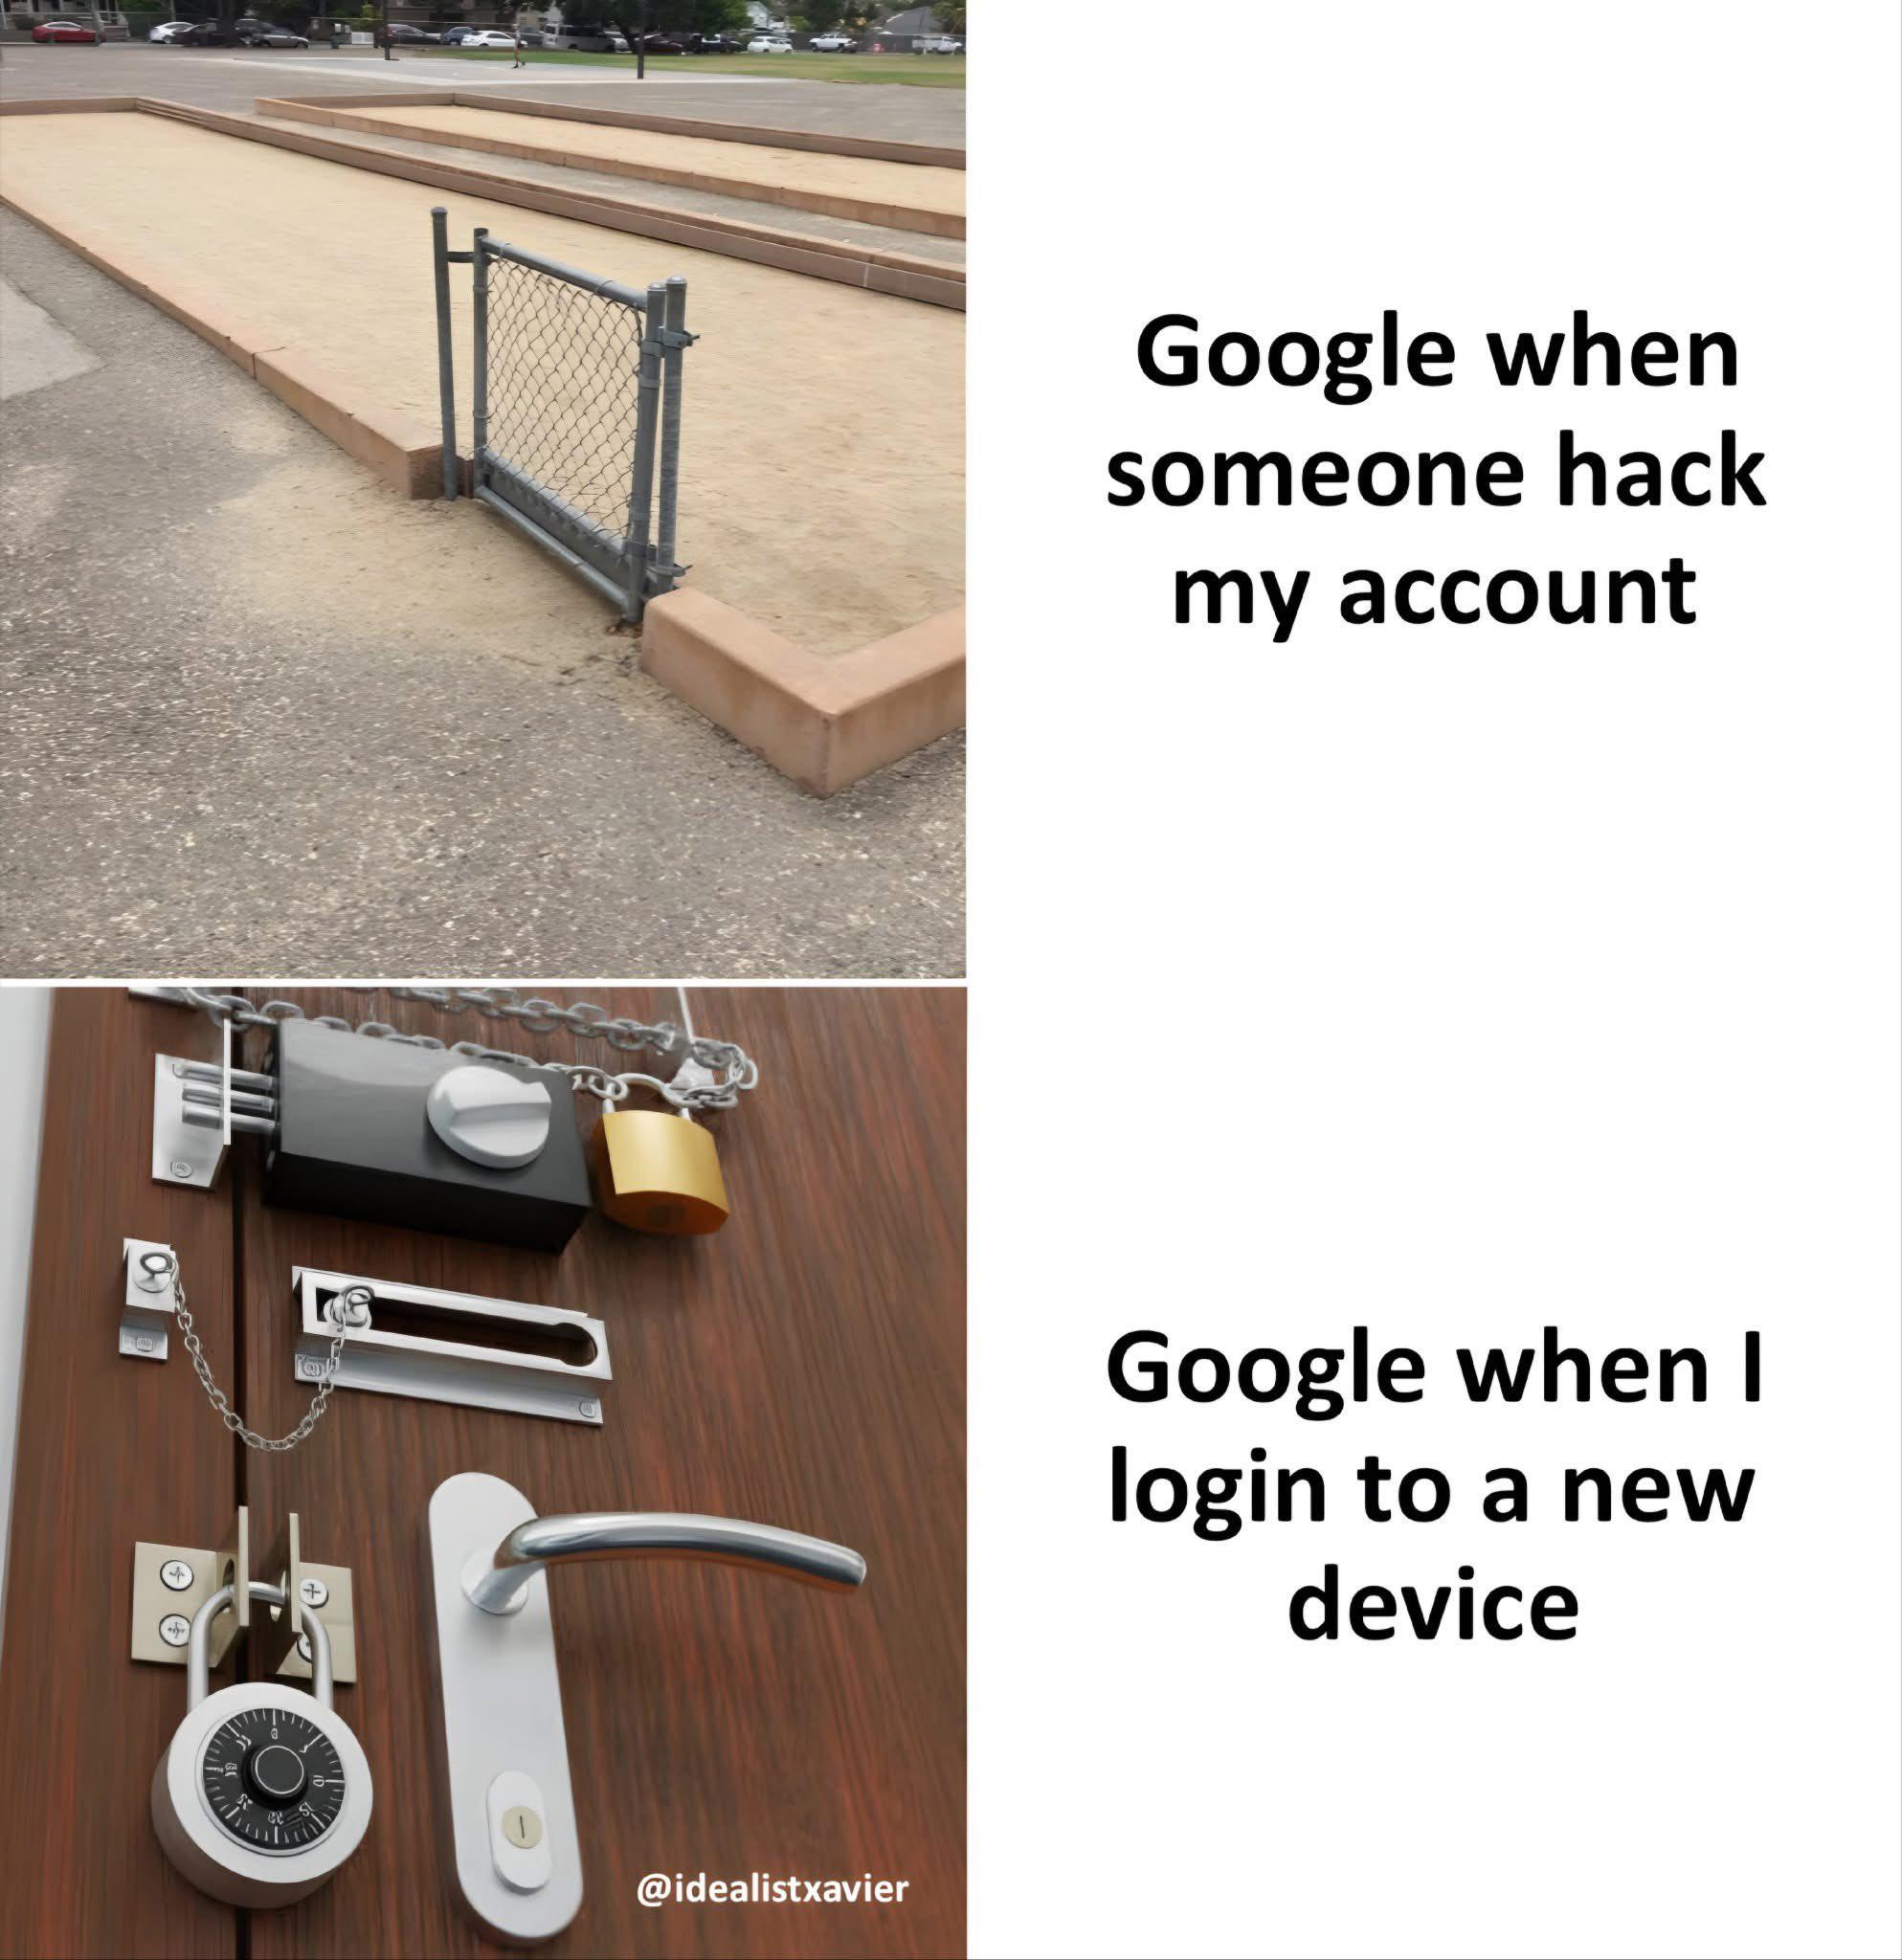
Google's security priorities are seriously questionable. When your account gets hacked? A single flimsy gate that doesn't even close properly. But log in from your new phone? Suddenly it's Fort Knox with seven different locks, chains, and probably a retinal scan that they didn't show in the picture. I've spent more time proving I'm me to Google than I have to my own mother. Nothing says "we value security" like making legitimate users jump through hoops while leaving the backdoor wide open for actual intruders.
Vibecoding Is The Future
Security
Programming
11 months ago
312.3K views
0 shares
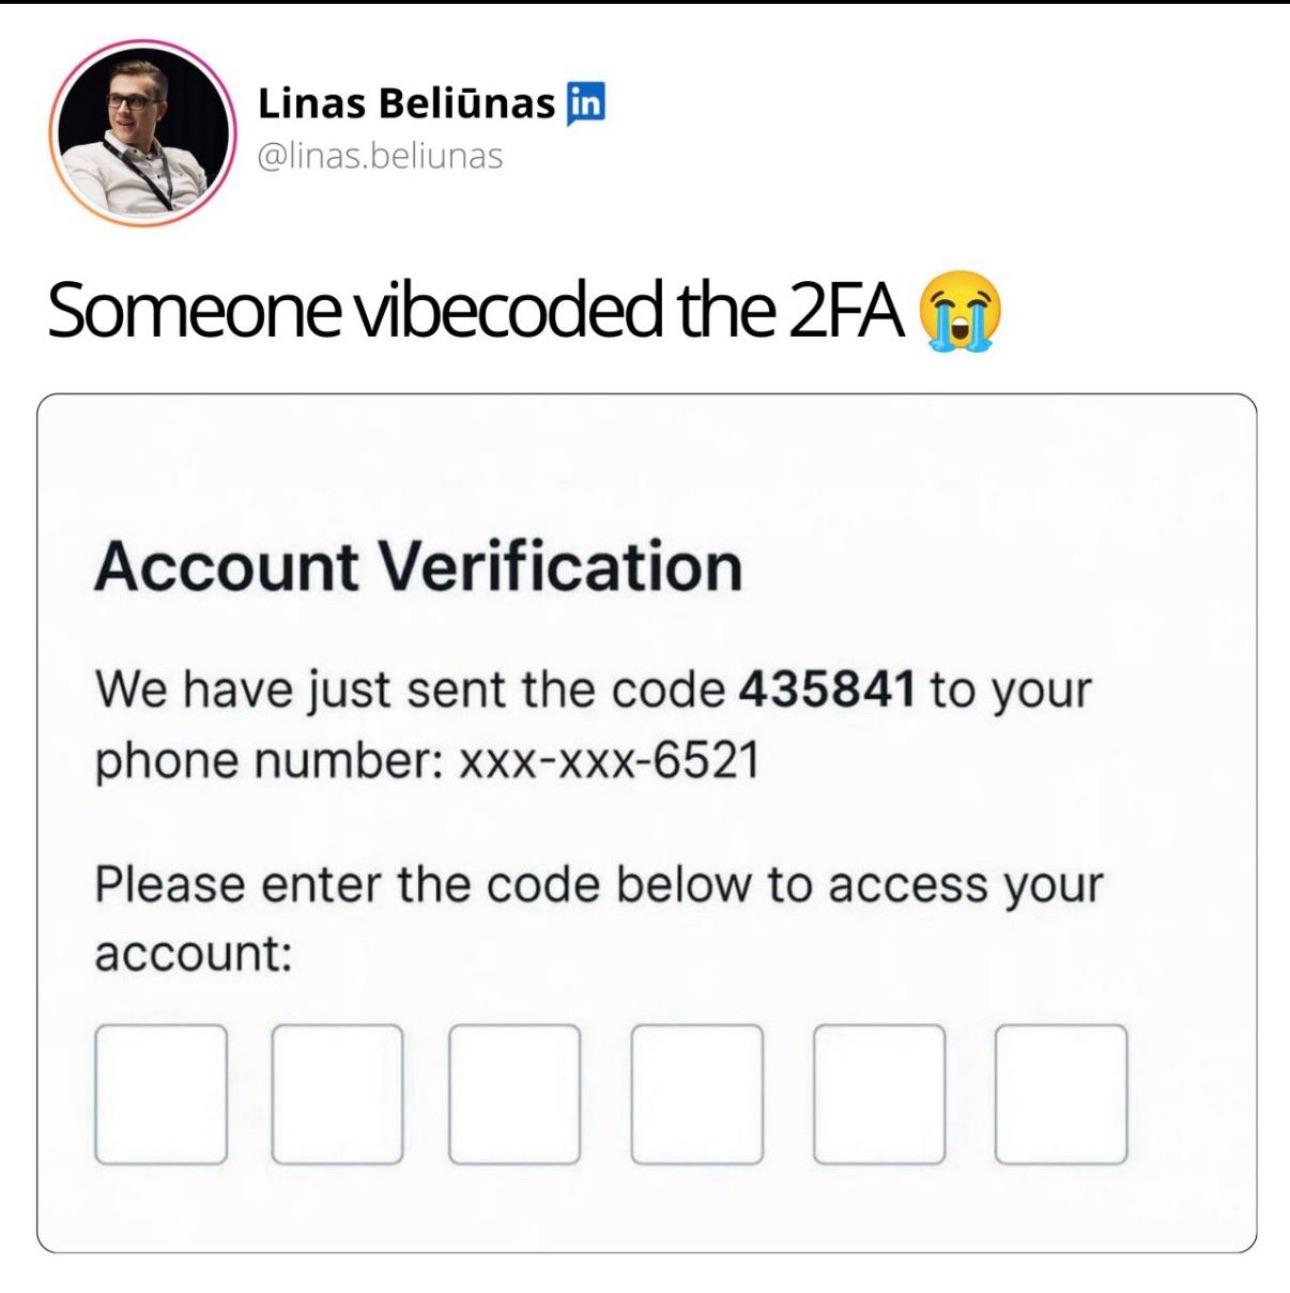
Who needs formal programming languages when you can just post verification codes on social media? Apparently, "vibecoding" means skipping the IDE and letting 435841 become your new function. Security experts are having heart palpitations right now while hackers are sending thank you cards. Next revolutionary paradigm: programming by accidentally leaking your passwords in GitHub commits.
Today's picks
Keychron Q3 Ultra Wireless Mechanical Keyboard 8000 HZ Polling Rate, 80% TKL 2.4 GHz/Bluetooth 5.3/Wired Hot-Swappable Aluminum Custom RGB Gaming ZMK for Mac/Windows/Linux-Black
Affiliate
$229.99
NordVPN
Sponsored
VPN
Wait, That's My Line...
Debugging
291.2K views
1 year ago