Patching Memes

Posts tagged with Patching
Big Mistake

Big Mistake
Running a PHP server with two critical RCE vulnerabilities and a CVSS score of 9.2? That's not just dropping the ball—that's launching it into orbit. Even LeBron can't recover from this one. For context: CVSS 9.2 means "you're basically running a server with a neon sign that says 'HACK ME.'" Remote Code Execution vulnerabilities let attackers run whatever code they want on your server. It's like leaving your house keys in the front door with a note saying "valuables inside." The PHP2Shell reference is chef's kiss—a tool literally designed to exploit PHP servers. When your server name matches an exploitation framework, you've transcended regular negligence into performance art.

Always Love A Good RCE Vuln

Always Love A Good RCE Vuln
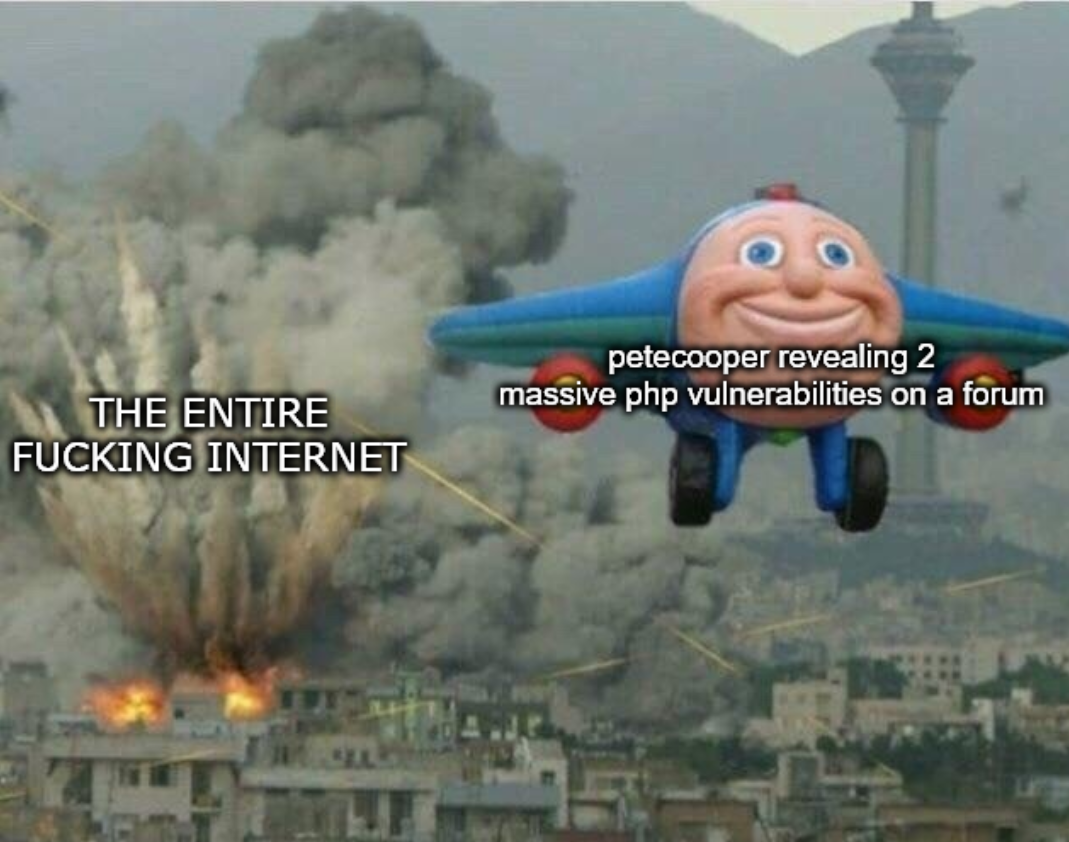
Nothing quite like watching some security researcher casually drop two massive PHP vulnerabilities on a random forum and watching the entire internet infrastructure collectively shit itself. RCE (Remote Code Execution) vulnerabilities are basically the nuclear option of security flaws—they let attackers run whatever code they want on your server. So yeah, when someone finds not one but TWO of these bad boys in PHP, which powers like 77% of the web, you get this beautiful chaos. The Thomas the Tank Engine meme format is *chef's kiss* here because it captures that childlike glee security researchers have when they discover catastrophic vulnerabilities. Meanwhile, every DevOps engineer and sysadmin is frantically patching servers at 3 AM on a Saturday. Fun times for everyone involved!

Let's Close The Gaps

Let's Close The Gaps
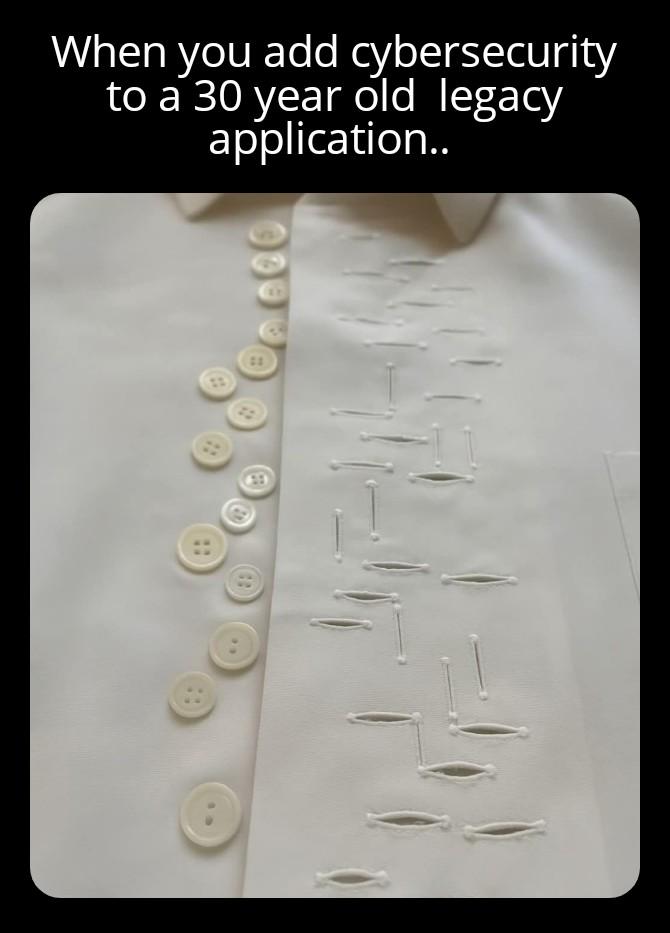
Ah yes, the classic "let's bolt on security features to ancient code" approach. The image shows a beautiful metaphor - buttons neatly lined up on one side, while the other side is just a bunch of random holes with some half-hearted attempts at stitching them together. It's like when your CTO suddenly discovers "zero trust architecture" and demands you implement it on that COBOL system running since the Reagan administration. Sure, we'll just sprinkle some encryption on that database with plaintext passwords and call it "enterprise-grade security." The best part? Next week they'll wonder why the patched security solution keeps falling apart. Turns out duct tape and prayers aren't officially recognized authentication protocols!

Security Analysts: Paid To Be Ignored

Security Analysts: Paid To Be Ignored
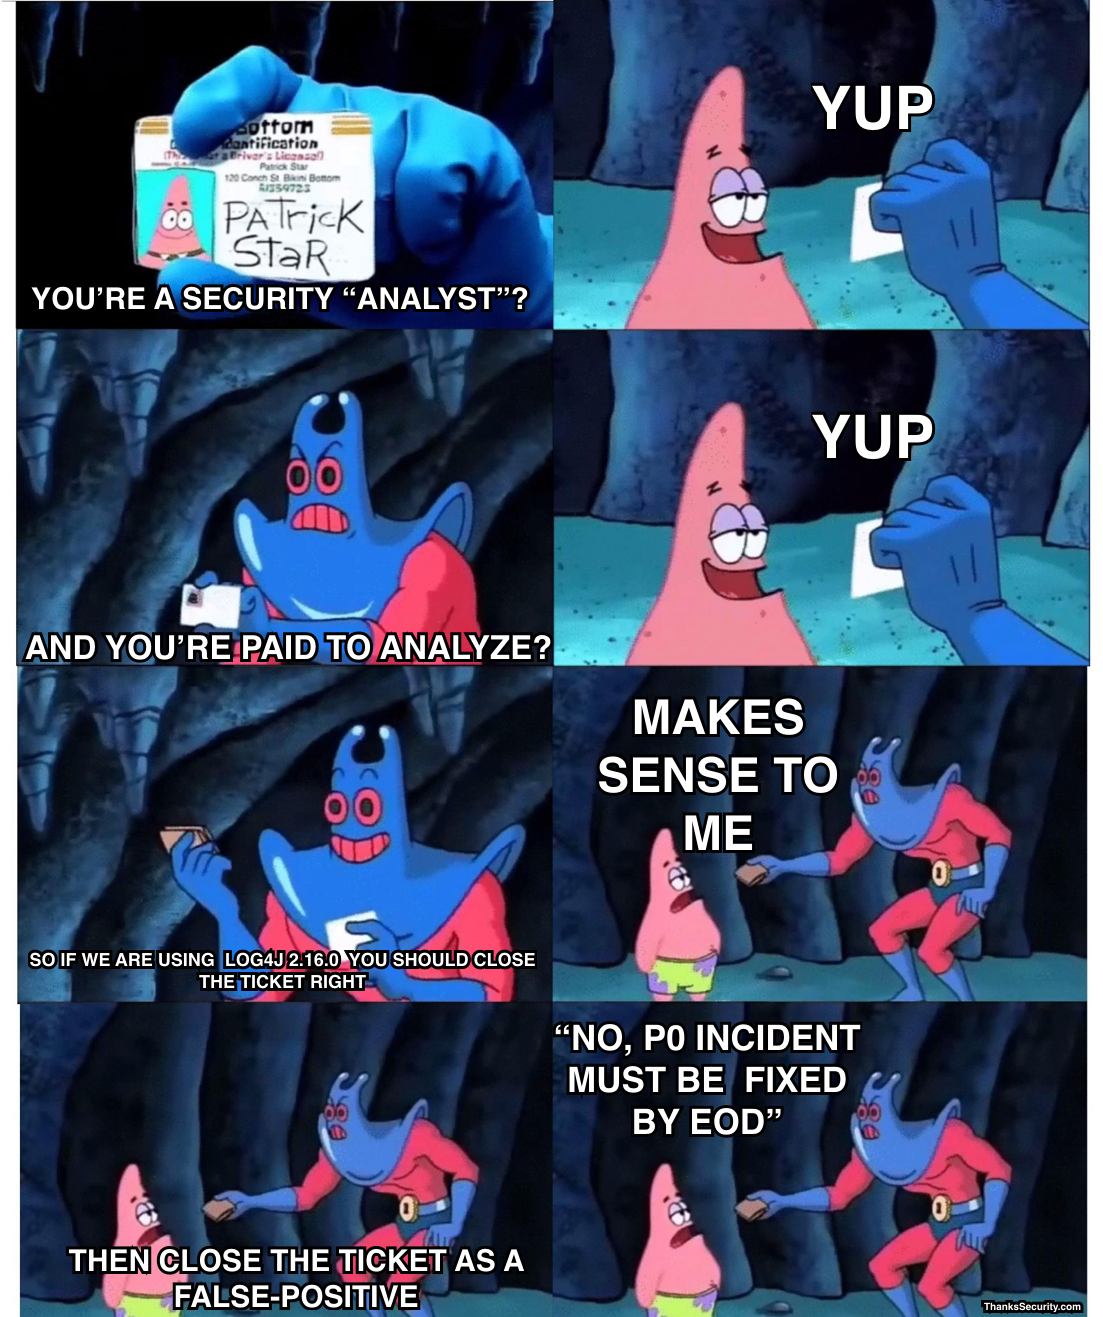
The security industry in a nutshell, folks. You hire "analysts" who confirm they're analysts, confirm they get paid to analyze, but when they actually find something—like a Log4j vulnerability that needs immediate patching—management's response is "Nah, P0 incident? That's an EOD problem." Nothing quite like hiring security experts only to ignore their expertise when it requires actual work. The classic corporate cycle: pay for security, ignore security recommendations, wonder why you got breached. Then blame the security team who warned you six months ago. For the uninitiated, Log4j was that delightful little vulnerability from 2021 that had security teams working through Christmas while executives were sipping eggnog and asking "can't we just deal with it after the holidays?"

The Three-Minute Victory Lap

The Three-Minute Victory Lap
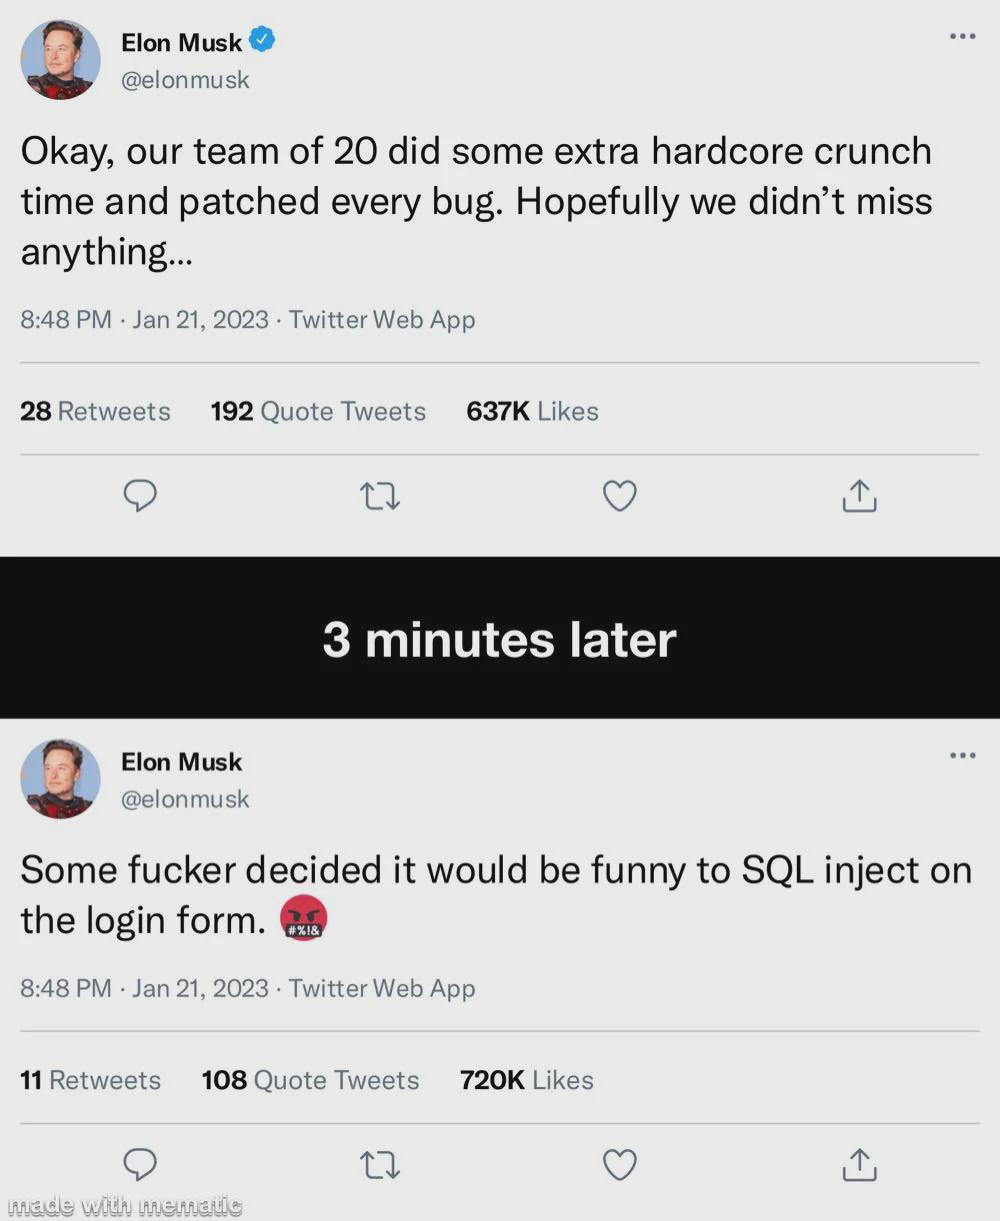
The classic "we fixed all the bugs" to "oh god we're hacked" pipeline. Declaring victory over bugs is basically sending a formal invitation to the universe to immediately prove you wrong. SQL injection on the login form is like leaving your front door unlocked with a sign saying "definitely no valuables inside." Somewhere, a database admin just felt a disturbance in the force and doesn't know why they suddenly need a drink.

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.