ssl Memes

Begin Privatekey

Begin Privatekey
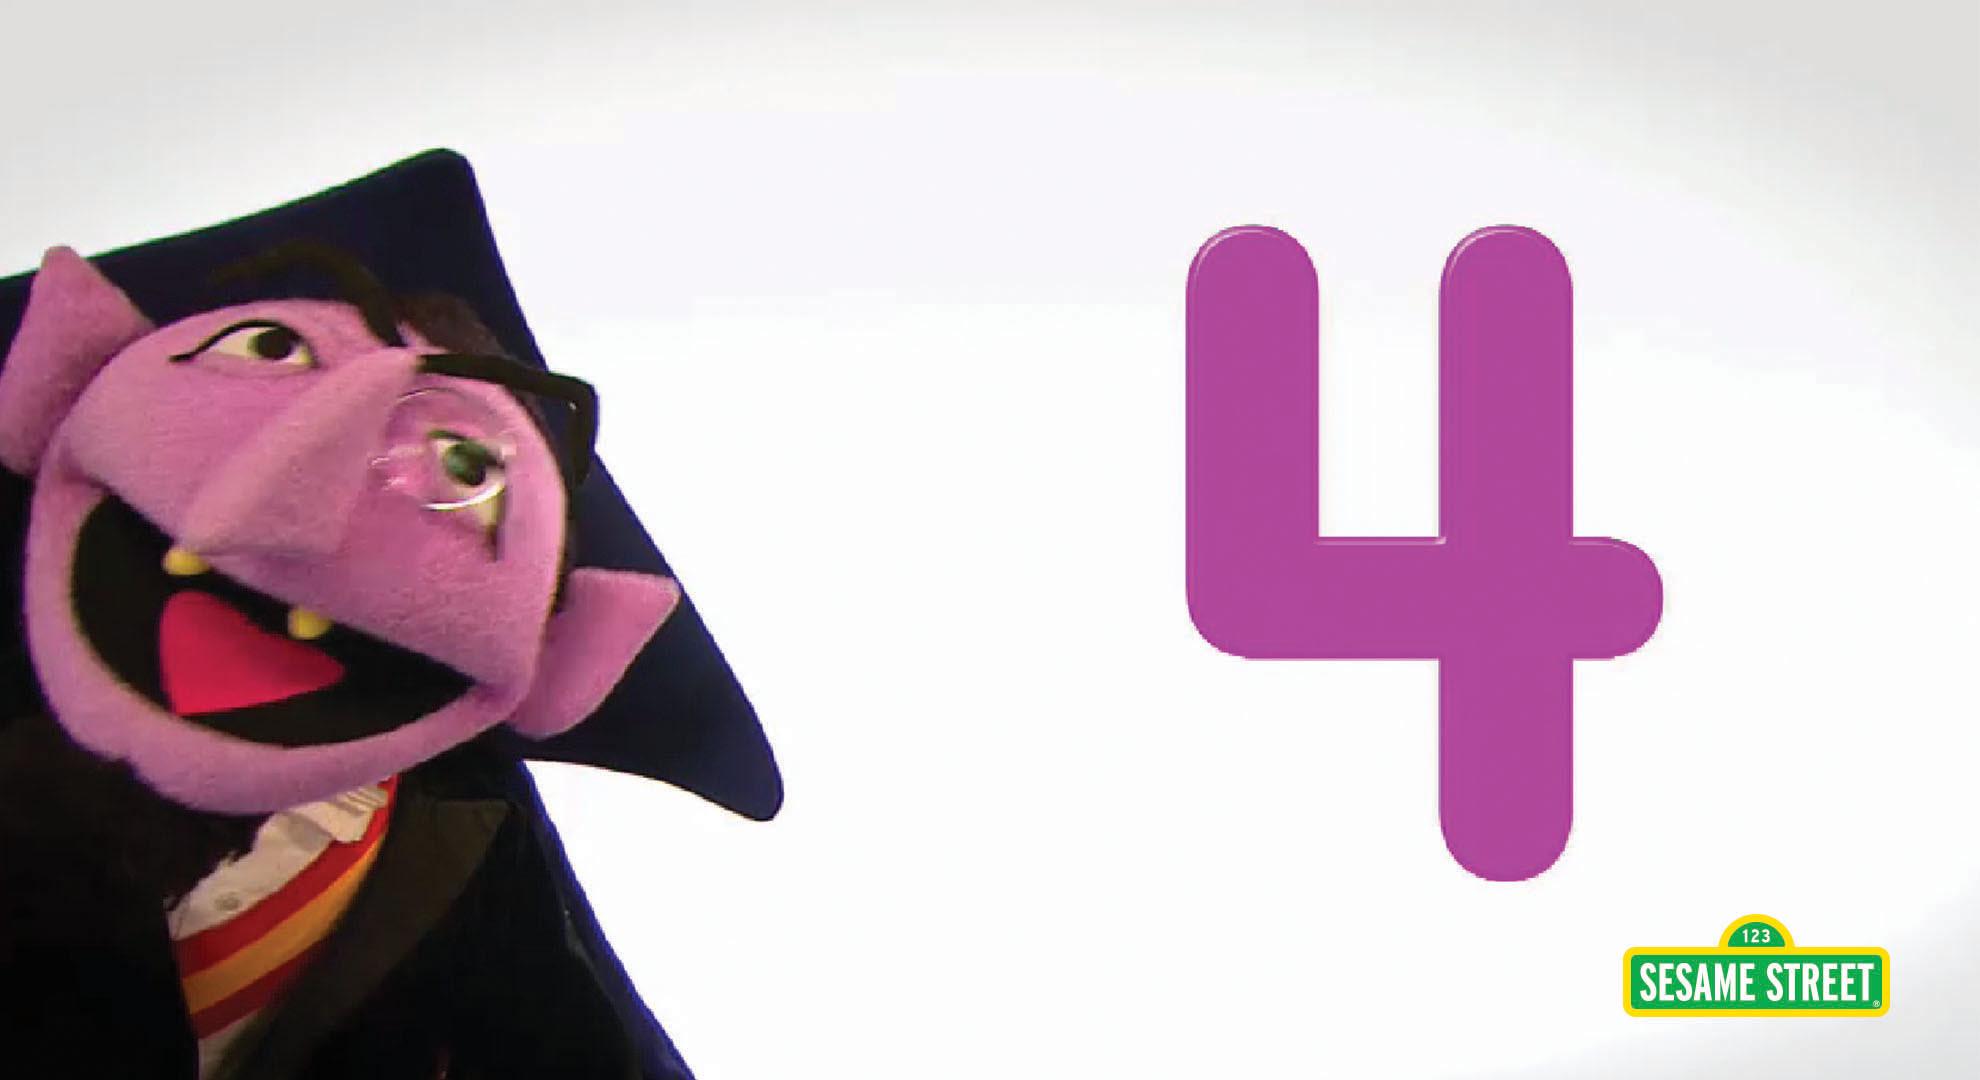
When you're setting up SSH keys or SSL certificates and you see that beautiful "-----BEGIN PRIVATE KEY-----" header, it hits different. The Count from Sesame Street teaching kids to count the number 4 becomes a perfect metaphor for developers proudly displaying their private keys in public repos, Slack channels, or—my personal favorite—hardcoded in the frontend JavaScript. The joke writes itself: "One private key committed to GitHub! Two private keys in the .env file! Three private keys in the Docker image! Four private keys leaked to production! Ah ah ah!" Meanwhile, security teams everywhere are having aneurysms. Fun fact: GitHub scans for accidentally committed credentials and will actually send you a notification faster than your CI/CD pipeline can deploy. They've probably prevented more breaches than all the security training videos combined.

Junior Setting Up Their First Website

Junior Setting Up Their First Website
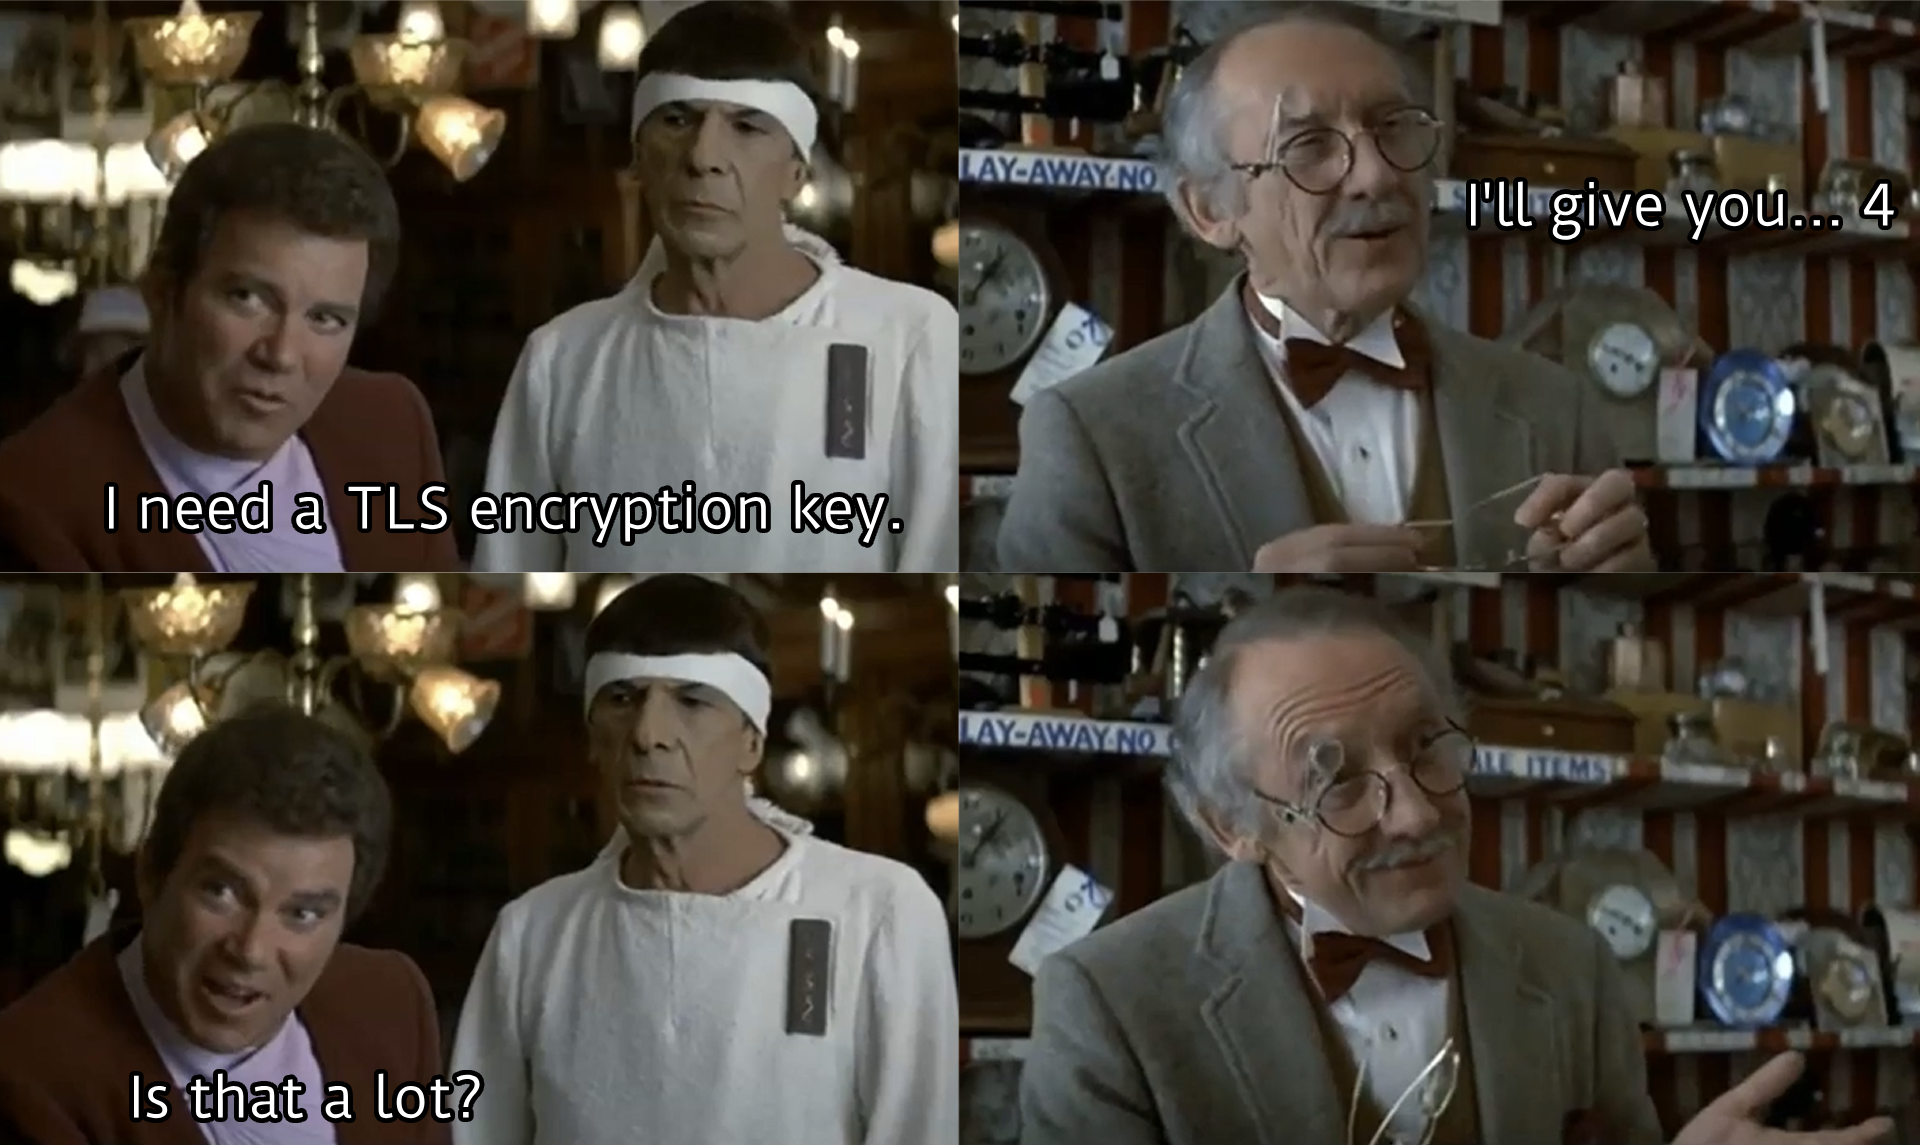
Junior dev asks for a TLS encryption key and gets offered 4. Their innocent "is that a lot?" response is pure gold. In reality, you typically need just one key pair for TLS/SSL certificates (a private key and a public key). Getting offered 4 is like asking for a screwdriver and someone handing you a whole toolbox. The junior has no idea if that's normal, excessive, or if they're about to configure a Pentagon-level security setup for their "Hello World" landing page. The beauty here is the complete lack of context that defines junior dev life—they're just trying to get HTTPS working so Chrome stops throwing that "Not Secure" warning, and now they're drowning in cryptographic key management. Tomorrow they'll be Googling "how many TLS keys is too many" at 2 AM.

Connect 4 > TLS Certificates

Connect 4 > TLS Certificates
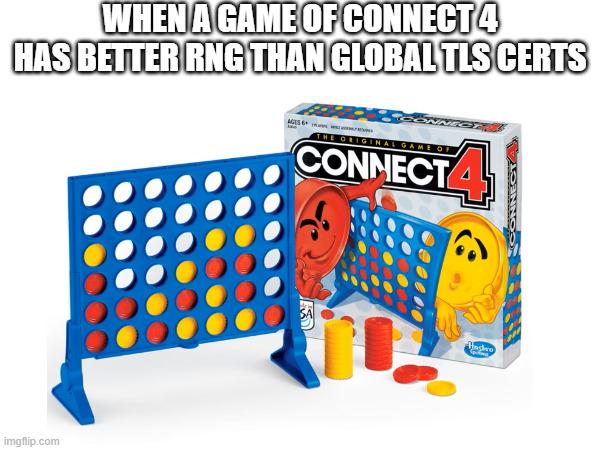
You know your infrastructure security is in shambles when a children's board game has more reliable randomness than your entire PKI setup. Connect 4's RNG actually works—those colored discs fall where they're supposed to, every single time. Meanwhile, TLS certificates? Expired at 2 AM on a Saturday. Wrong domain. Self-signed because someone forgot to renew. Certificate chain broken because some intermediate CA decided to retire without notice. The real kicker is that Connect 4 has been solving the "trust" problem since 1974 without needing a 30-step renewal process, three different vendors, and a postmortem document. Just drop the disc. It works. No wildcard certificates, no SNI issues, no "NET::ERR_CERT_AUTHORITY_INVALID" at 9 PM on deployment day.

That's The Goo Goo Man's Decision

That's The Goo Goo Man's Decision
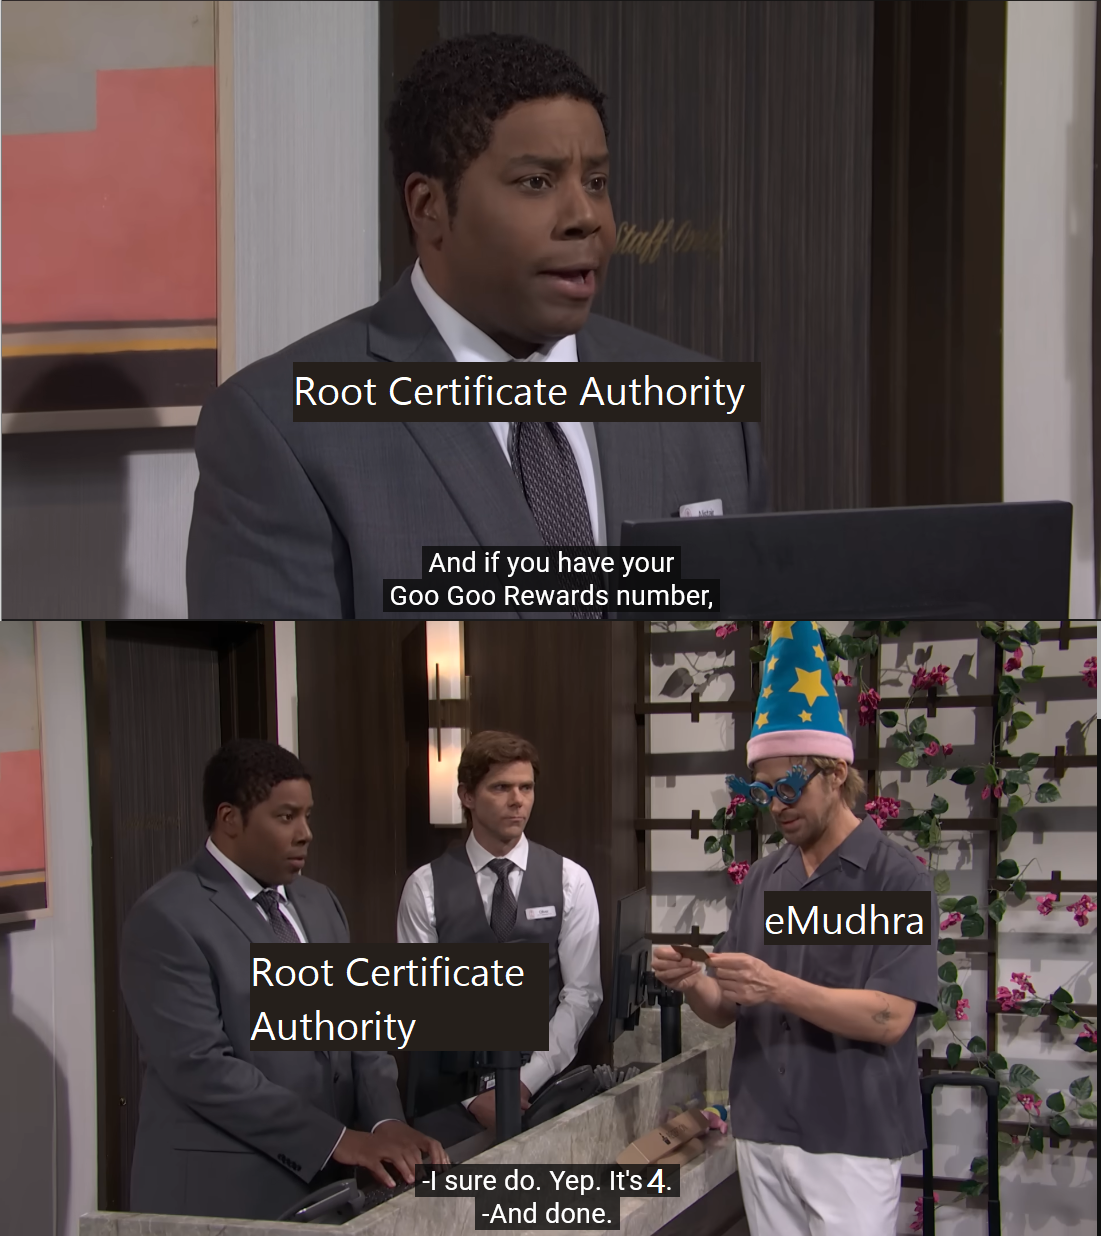
Root Certificate Authorities out here acting like they're the Supreme Court of the internet, demanding your credentials and proof of identity like you're trying to enter Fort Knox. They want documentation, verification, the whole nine yards! But then eMudhra (a real CA, by the way) rolls up like a chaotic wizard wearing a party hat and just... bypasses everything. "Goo Goo Rewards number? Yeah sure, that'll work. You're verified. Welcome aboard!" No questions asked, no security theater, just pure unhinged energy. The absolute AUDACITY of treating SSL certificate verification with the same rigor as a grocery store loyalty program is sending me. Who needs multi-factor authentication when you've got multi-flavor baby food points? 💀

FLEXISPOT EN1 One-Piece Standing Desk with 1-Inch Thick Seamless Desktop, 55"x28" Electric Height Adjustable Desk for Home Office, Multi-Monitor Setups & Easy Assembly, Maple

FLEXISPOT EN1 One-Piece Standing Desk with 1-Inch Thick Seamless Desktop, 55"x28" Electric Height Adjustable Desk for Home Office, Multi-Monitor Setups & Easy Assembly, Maple
ONE-PIECE. ZERO WOBBLE: A seamless, rock-solid desktop built for home offices, creative studios, and designers running multi-monitor setups. · THE POWER OF 1-INCH: Dense, durable, and sag-resistant, …

How The Key Was Actually Created

How The Key Was Actually Created
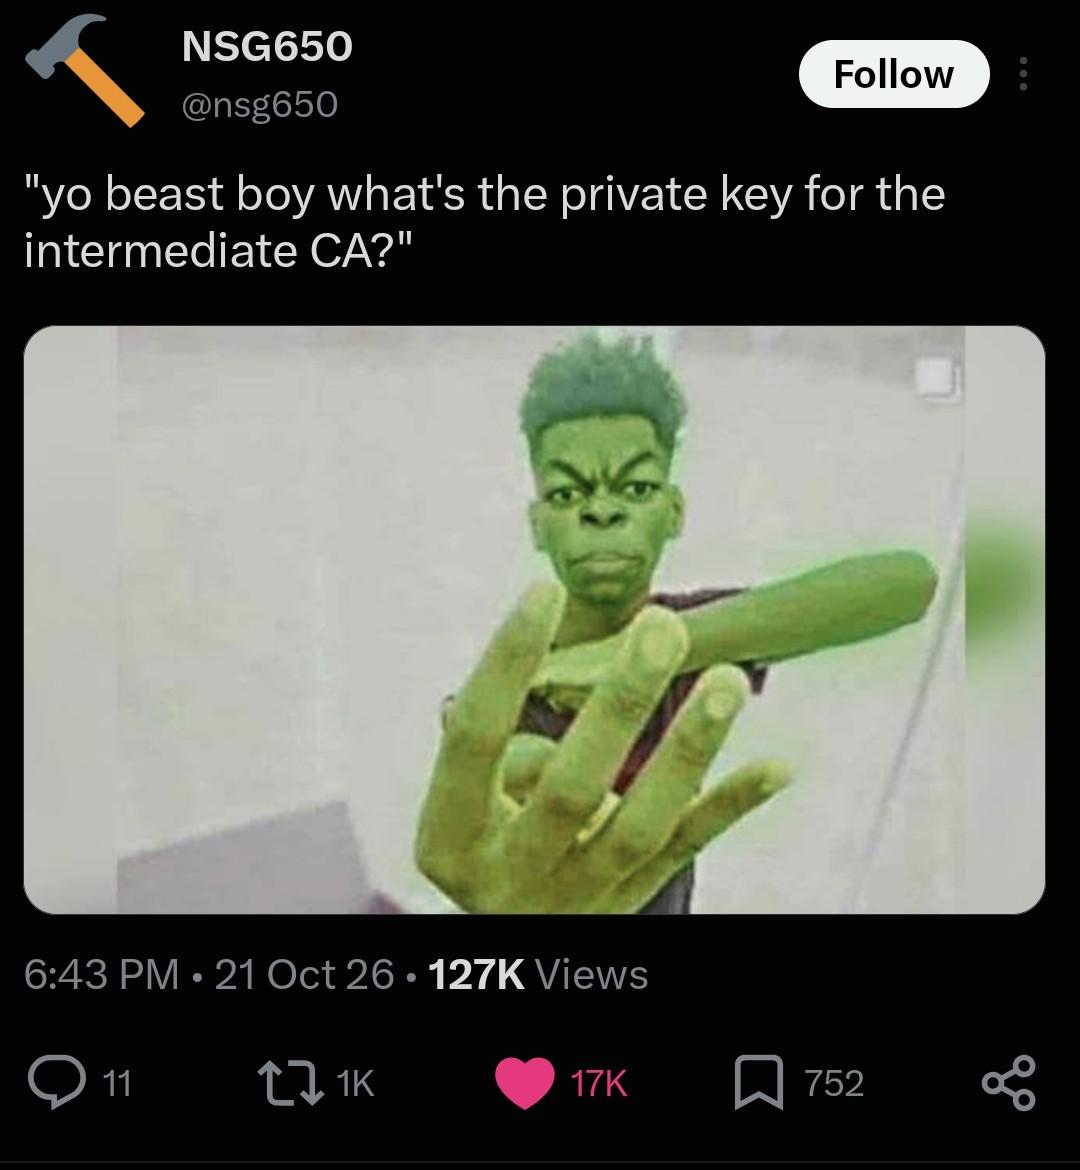
Someone casually asking for the intermediate CA's private key is like asking for the nuclear launch codes at a pizza party. The person responding with aggressive keyboard smashing perfectly captures the appropriate level of rage when someone doesn't understand the entire point of PKI infrastructure. For context: In certificate chains, the intermediate Certificate Authority's private key is literally the crown jewels. If that gets leaked, you can forge certificates for any domain and basically break the entire trust model of the internet. It's not just "please don't share this" – it's "this should be in an HSM in a bunker guarded by lasers." The "yo beast boy" energy combined with the fundamental misunderstanding of security principles is *chef's kiss*. Nothing says "I'm about to have a very bad day" quite like someone treating root-level cryptographic material like a WiFi password.

Sesame Street Layer Certificate

Sesame Street Layer Certificate
SSL certificates and Sesame Street both teaching us numbers, just in wildly different contexts. One's a beloved children's show teaching toddlers to count, the other's a cryptographic protocol that makes sure your credit card info doesn't end up in the hands of some script kiddie in a basement somewhere. The joke here is that SSL (Secure Sockets Layer) certificates are brought to you by "the number four" - a reference to Sesame Street's classic "brought to you by the letter/number" segments. Except instead of learning basic arithmetic, you're learning that your website needs TLS 1.2 or 1.3 because SSL is deprecated and vulnerable. Educational content for grown-ups who still don't understand why their self-signed cert throws browser warnings. Fun fact: SSL is technically dead - we've been using TLS (Transport Layer Security) for years now, but everyone still calls it SSL because old habits die hard in tech. It's like calling every tissue a Kleenex, except with more security implications.

Xkcd Said Its Random

Xkcd Said Its Random
This references the legendary xkcd comic where someone implements a random number generator by just returning 4 because "I rolled a dice and got 4, so it's random." Fast forward to reality, and here's some poor soul actually using that logic to generate SSL certificates. The other person's response? "dumb fuck" - which is honestly the most restrained reaction possible when someone hardcodes entropy into cryptographic material. The beauty here is that certificates need actual randomness for security. Using the same "random" seed means every certificate would be identical, making your entire PKI infrastructure about as secure as a screen door on a submarine. But hey, xkcd said it was random, so ship it to production.

Peak Web PKI

Peak Web PKI
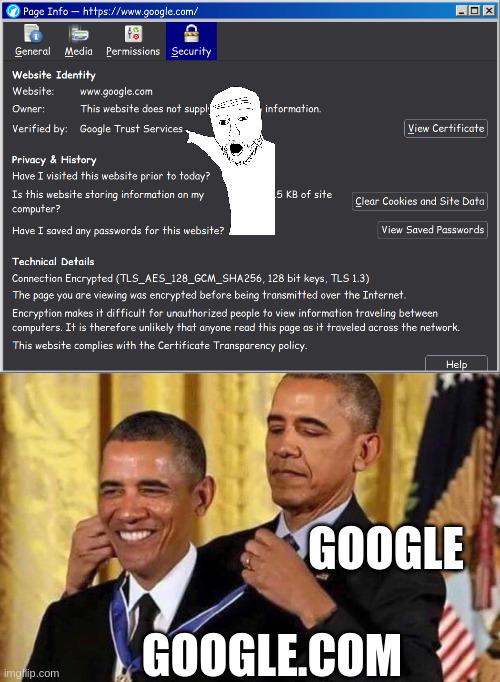
So Google.com's SSL certificate is verified by... Google Trust Services. It's like showing up to court as both the defendant AND the judge. "Your Honor, I find myself completely innocent!" The browser's security tab is proudly displaying all this fancy PKI infrastructure—TLS 1.3, AES-128-GCM encryption, SHA256 hashing—while conveniently glossing over the fact that we're just taking Google's word that Google is trustworthy. The whole certificate authority system basically runs on "trust me bro" energy, but with more cryptographic signatures. Fun fact: Your browser ships with a pre-installed list of root CAs it trusts, and guess who gets to be on that list? The same mega-corporations whose sites you're visiting. It's a perfectly circular system of trust that somehow became the backbone of internet security. Works great until you remember that the entire web's security model is built on trusting a few dozen organizations not to mess up or go rogue.

Not Very Secure

Not Very Secure
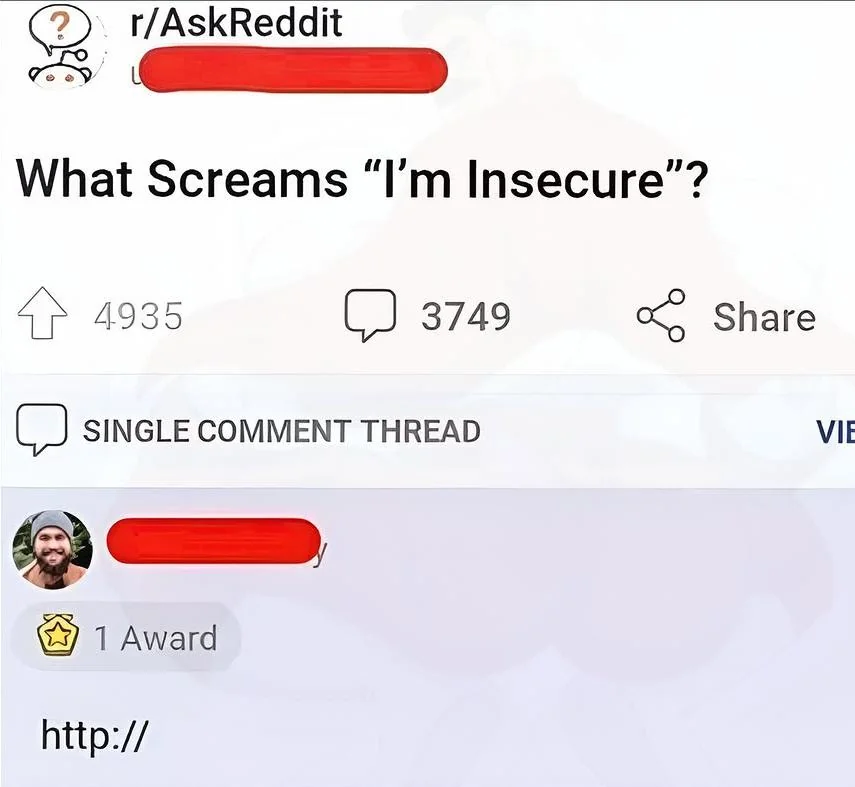
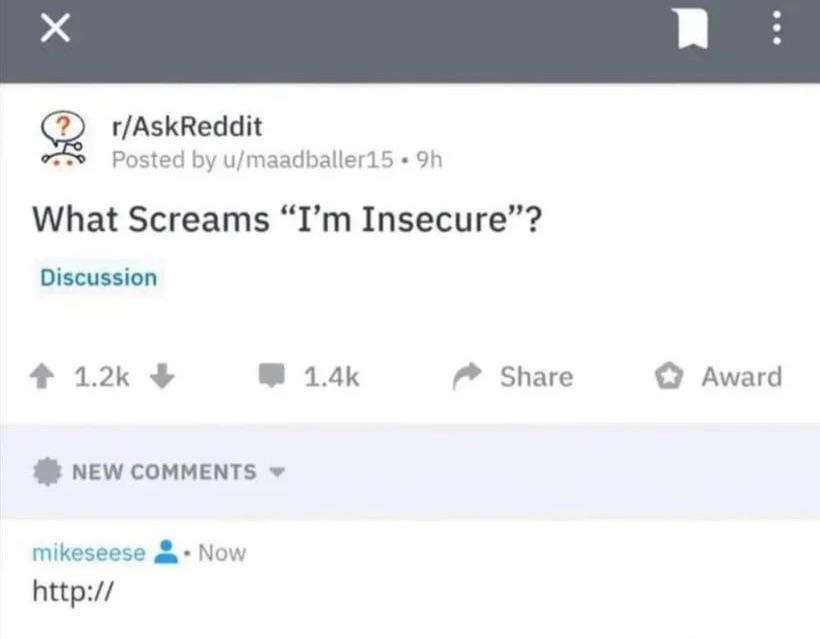
Someone asked Reddit what screams "I'm insecure" and got the most technically accurate answer possible: http:// Because nothing says "please intercept my credentials" quite like transmitting data over plain HTTP in 2024. Your passwords are traveling through the internet like postcards—everyone can read them, and there's no envelope. It's the digital equivalent of shouting your credit card number across a crowded room and hoping only the cashier hears it.

Star Trek SSL

Star Trek SSL
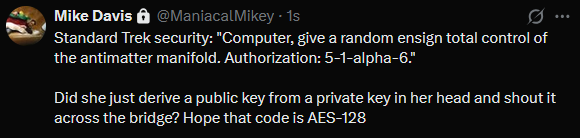
Star Trek security protocols are basically just someone shouting their password across the bridge and hoping nobody's listening. "Authorization: 5-1-alpha-6" is the equivalent of broadcasting your private key in plaintext over an unsecured channel. In the real world, that's how you get your antimatter manifold hijacked by some script kiddie on Risa. The real kicker? She literally derived a public key from a private key IN HER HEAD and announced it to everyone within earshot. That's not how asymmetric encryption works, Captain. You don't just mentally compute cryptographic operations and broadcast them like you're ordering Earl Grey. At least hope it's AES-128 and not ROT13 with extra steps. Future technology: can travel faster than light. Also future technology: still using verbal passwords like it's 1995.

Pulled A Little Sneaky

Pulled A Little Sneaky
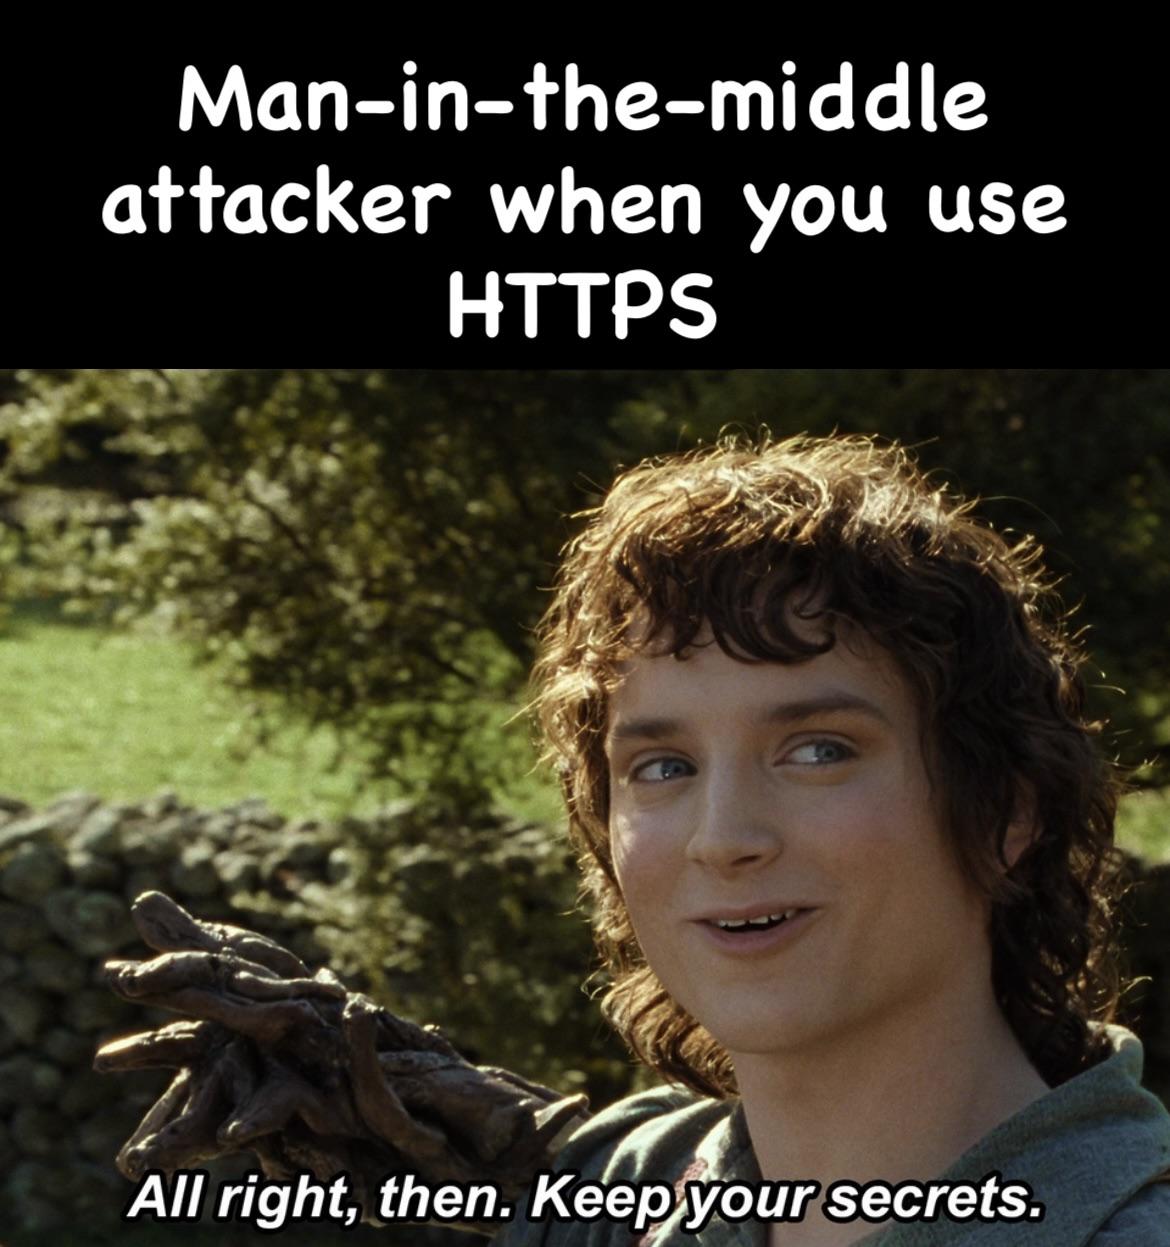
HTTPS encryption is basically the digital equivalent of whispering your credit card number in a crowded room while everyone's wearing noise-canceling headphones. The man-in-the-middle attacker, who's been sitting there with their packet sniffer ready to intercept all your juicy unencrypted data, suddenly hits a wall of TLS/SSL encryption and realizes they're getting absolutely nothing. It's like showing up to rob a bank only to find out they've already moved all the money to a vault you can't crack. Sure, they can still see you're communicating with someone, but good luck reading those encrypted packets. All that effort setting up Wireshark and ARP spoofing, just to watch gibberish flow by. Fun fact: HTTPS doesn't just encrypt your data—it also verifies the server's identity with certificates, so even if someone tries to impersonate the server, your browser will throw up more red flags than a Communist parade.

Homerays Bamboo Monitor Stand Riser, No Assembly Required Exquisite Monitor Stand with Drawer Ergonomic Height Wood Monitor Stand

Homerays Bamboo Monitor Stand Riser, No Assembly Required Exquisite Monitor Stand with Drawer Ergonomic Height Wood Monitor Stand
【STUNNING & DESIGN】This bamboo monitor stand is carefully polished and designed by an Italian designer. The stand’s height is 4.65’’ which is designed according to the golden comfort ratio in ergonom…

What Really Makes A Programmer Insecure?

What Really Makes A Programmer Insecure?
Someone asked r/AskReddit "What screams 'I'm insecure'?" and the top answer is just "http://" — because nothing says emotional vulnerability quite like transmitting data in plaintext over an unencrypted connection. While everyone else is sharing deep psychological insights about human behavior, this programmer saw their moment and went straight for the jugular. The joke hits different when you realize we're all silently judging every website still running HTTP in 2024. That little padlock icon isn't just about security anymore; it's about self-respect.