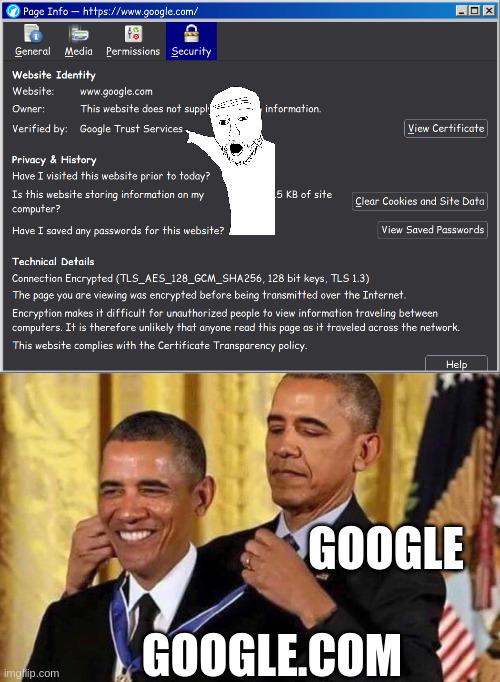
So Google.com's SSL certificate is verified by... Google Trust Services. It's like showing up to court as both the defendant AND the judge. "Your Honor, I find myself completely innocent!" The browser's security tab is proudly displaying all this fancy PKI infrastructure—TLS 1.3, AES-128-GCM encryption, SHA256 hashing—while conveniently glossing over the fact that we're just taking Google's word that Google is trustworthy. The whole certificate authority system basically runs on "trust me bro" energy, but with more cryptographic signatures. Fun fact: Your browser ships with a pre-installed list of root CAs it trusts, and guess who gets to be on that list? The same mega-corporations whose sites you're visiting. It's a perfectly circular system of trust that somehow became the backbone of internet security. Works great until you remember that the entire web's security model is built on trusting a few dozen organizations not to mess up or go rogue.
 AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud