Client-side validation Memes

Posts tagged with Client-side validation

Next Level Confidence

Next Level Confidence
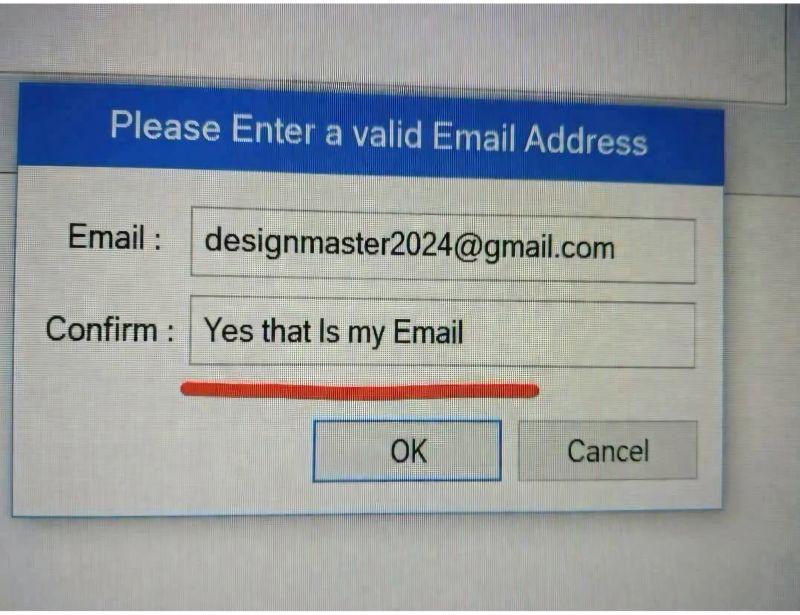
When the user treats your email confirmation field like it's asking them to write their life story instead of just re-typing their email. "Yes that Is my Email" – buddy, I asked you to confirm it, not give me a verbal affirmation like we're in couples therapy. This is what happens when people don't read instructions and just fill in whatever feels right in the moment. The validation regex is probably having an aneurysm right now. Meanwhile, the poor developer who thought a simple "Confirm Email" field would be foolproof is somewhere questioning their entire career. Pro tip: This is exactly why you need client-side validation that actually checks if the two fields match. Though honestly, even with the best validation in the world, users will find creative ways to break your forms. It's the circle of life in web development.
Front End OTP Verification

Front End OTP Verification
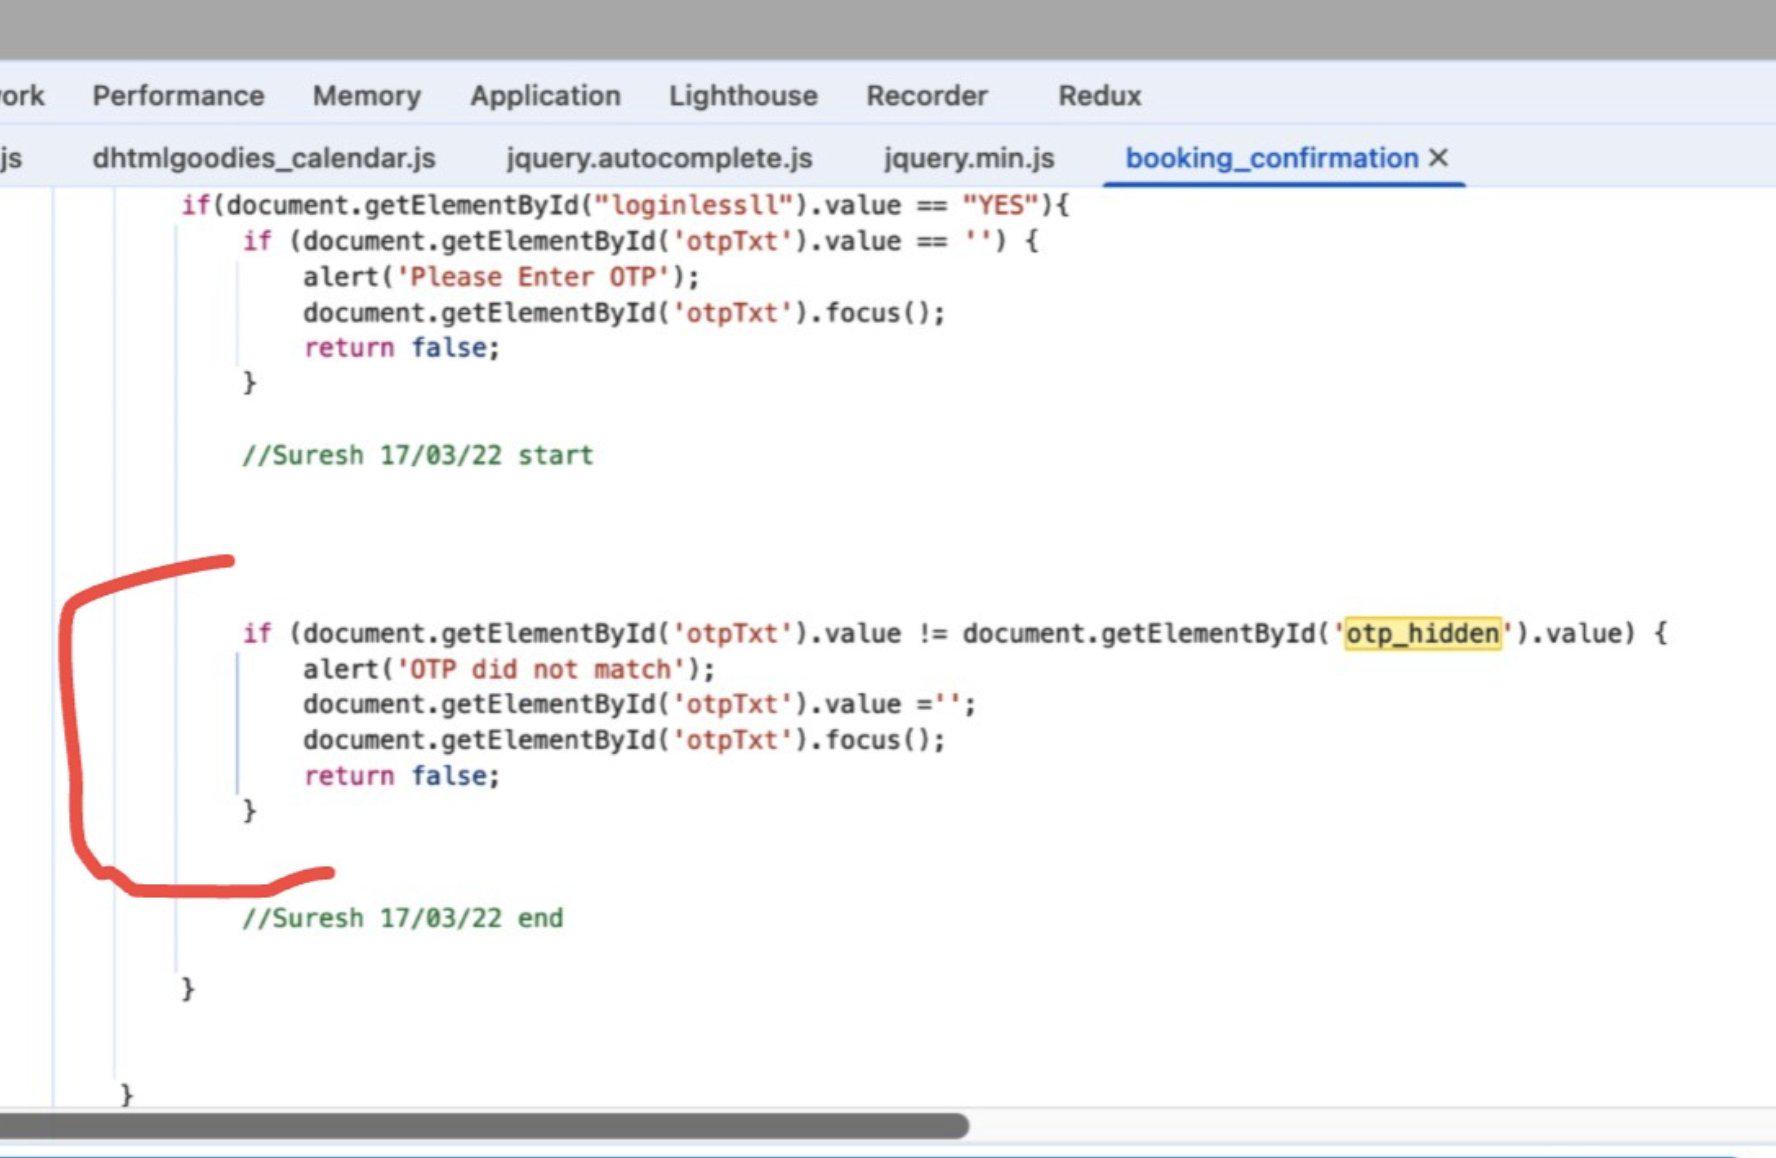
Someone named Suresh just committed a cardinal sin of web security. They're comparing the user's OTP input against a hidden field called otp_hidden ... which exists in the DOM... on the client side... where literally anyone can just open DevTools and read it. It's like putting a lock on your door but leaving the key taped to the doorknob with a sticky note that says "SECRET KEY - DO NOT USE". The entire point of OTP verification is that it should be validated server-side against what was actually sent to the user's phone/email. Storing it in a hidden input field defeats the purpose harder than using var in 2024. The red circle highlighting this masterpiece is chef's kiss. This is the kind of code that makes security researchers weep and penetration testers rub their hands together gleefully. Never trust the client, folks.

Client Side Validation

Client Side Validation
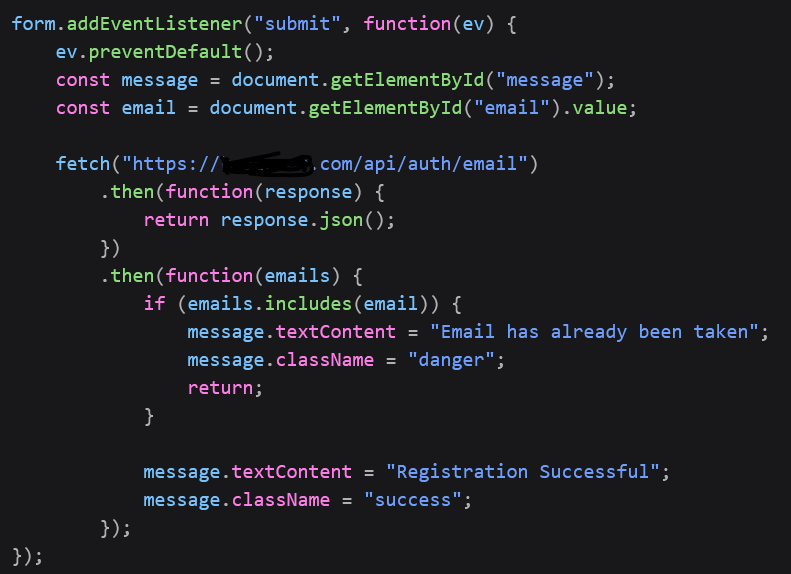
So you're checking if an email is already taken by sending it to the server, getting back a list of all registered emails , and then doing a client-side .includes() check? That's like asking the bank to give you everyone's account numbers just to verify yours doesn't exist yet. Not only is this a massive security vulnerability (congrats, you just leaked your entire user database to anyone with DevTools open), but it's also hilariously inefficient. Why return an array of potentially millions of emails when the server could just return a boolean? The backend dev is probably crying somewhere. The cherry on top? After doing all this client-side "validation," you're still showing success messages without any actual server confirmation. Chef's kiss of terrible architecture. 🤌

When The Age Check Says No, But The Game Still Says Yes

When The Age Check Says No, But The Game Still Says Yes
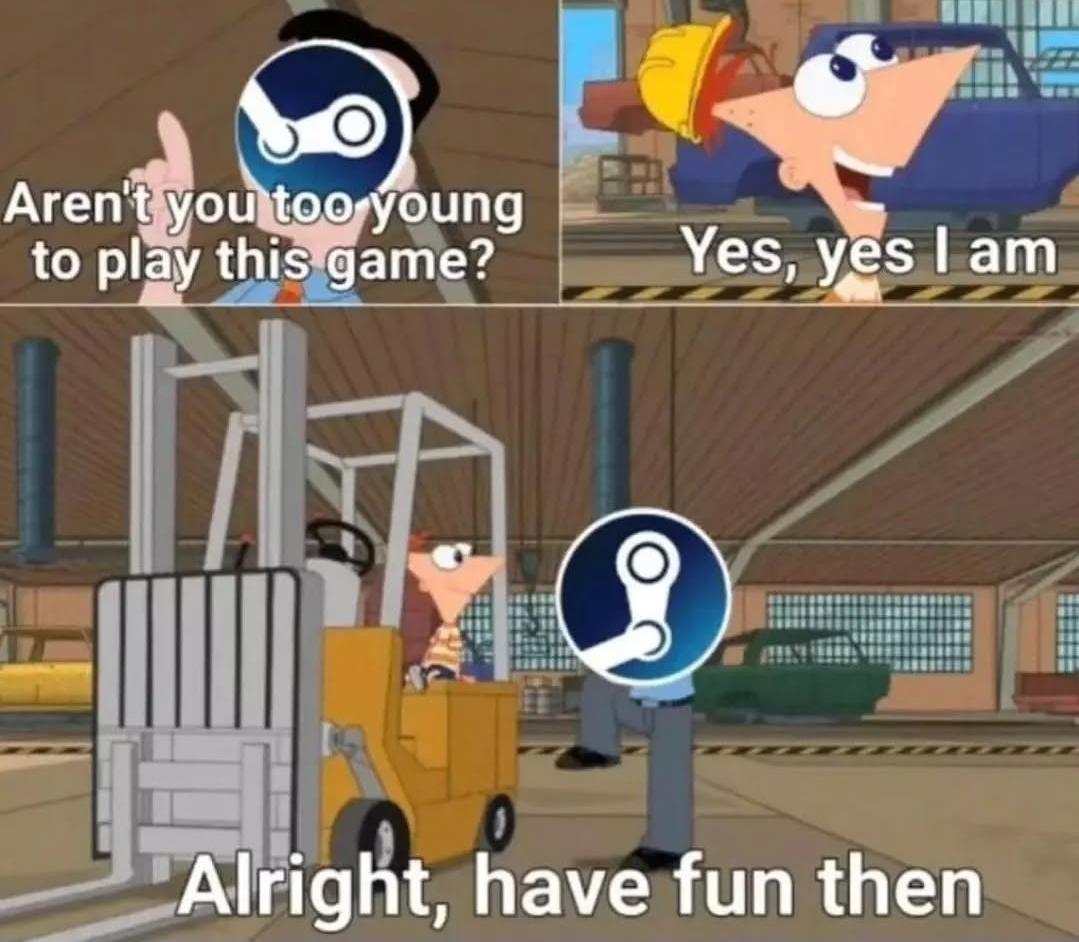
The perfect representation of Steam's age verification system! Steam asks if you're old enough to view mature content, you click "Yes" despite being 12, and Steam just... lets you right in. No ID check, no credit card verification—just pure digital trust in an era of zero trust architecture. It's basically the digital equivalent of a bouncer asking for ID and then immediately stepping aside when you say "trust me bro, I'm totally 18."