Otp Memes

Posts tagged with Otp

We Don't Stress Our Customer

We Don't Stress Our Customer
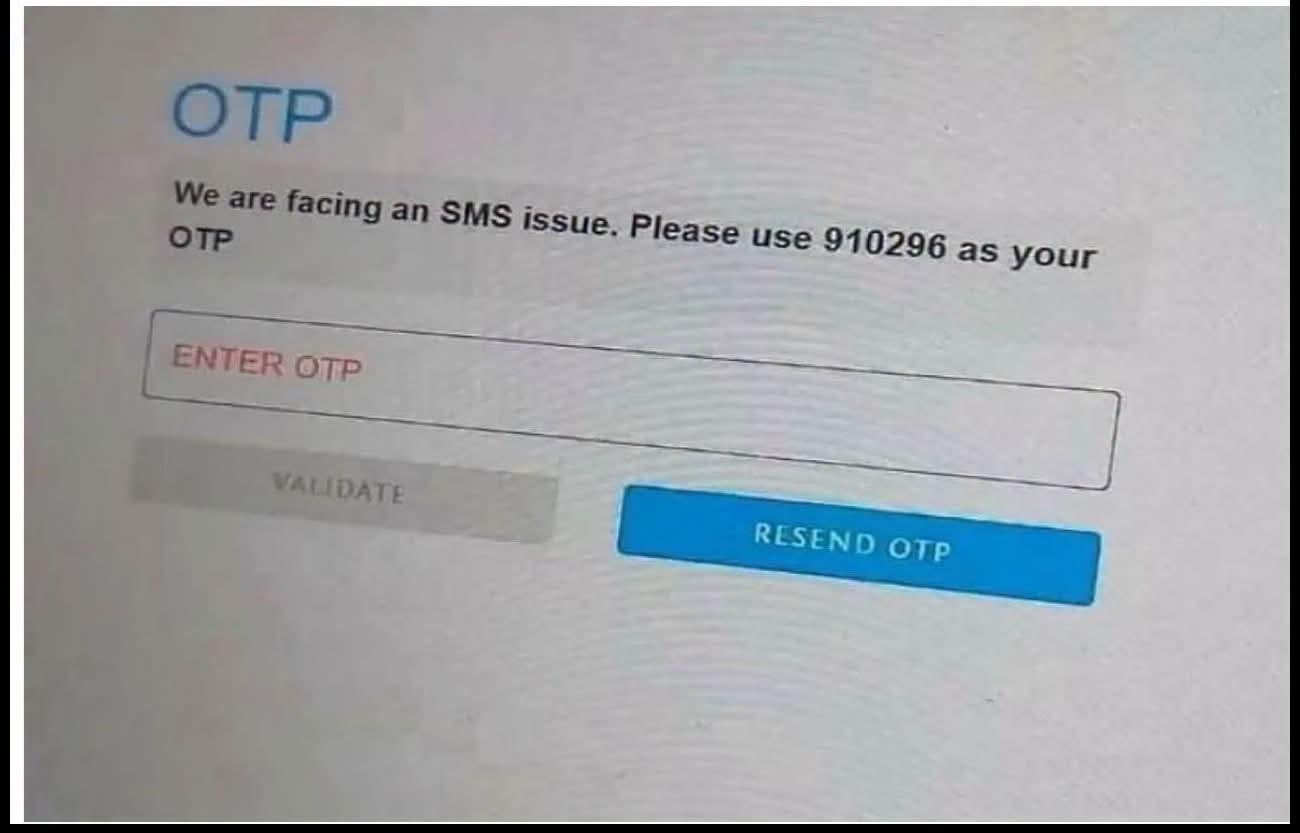
"We're facing an SMS issue" is corporate speak for "our entire SMS infrastructure is on fire and nobody knows how to fix it." But hey, no worries! Instead of making you wait for the actual OTP, they've thoughtfully hardcoded one for you: 910296. Just type that in and pretend everything's working as intended. Nothing screams "production-ready" quite like displaying your fallback OTP directly on the login screen for the entire world to see. Security through obscurity? More like security through "please don't hack us, we're already struggling." The devs probably had a 3 AM Slack conversation that went: "Should we fix the SMS gateway?" "Nah, just hardcode an OTP. What could go wrong?" Props to whoever wrote that message though—they managed to sound both apologetic and completely unbothered at the same time. "We don't stress our customer" is technically true when you eliminate the need for them to check their phone. Innovation!

Vibe Coding Is The Future

Vibe Coding Is The Future
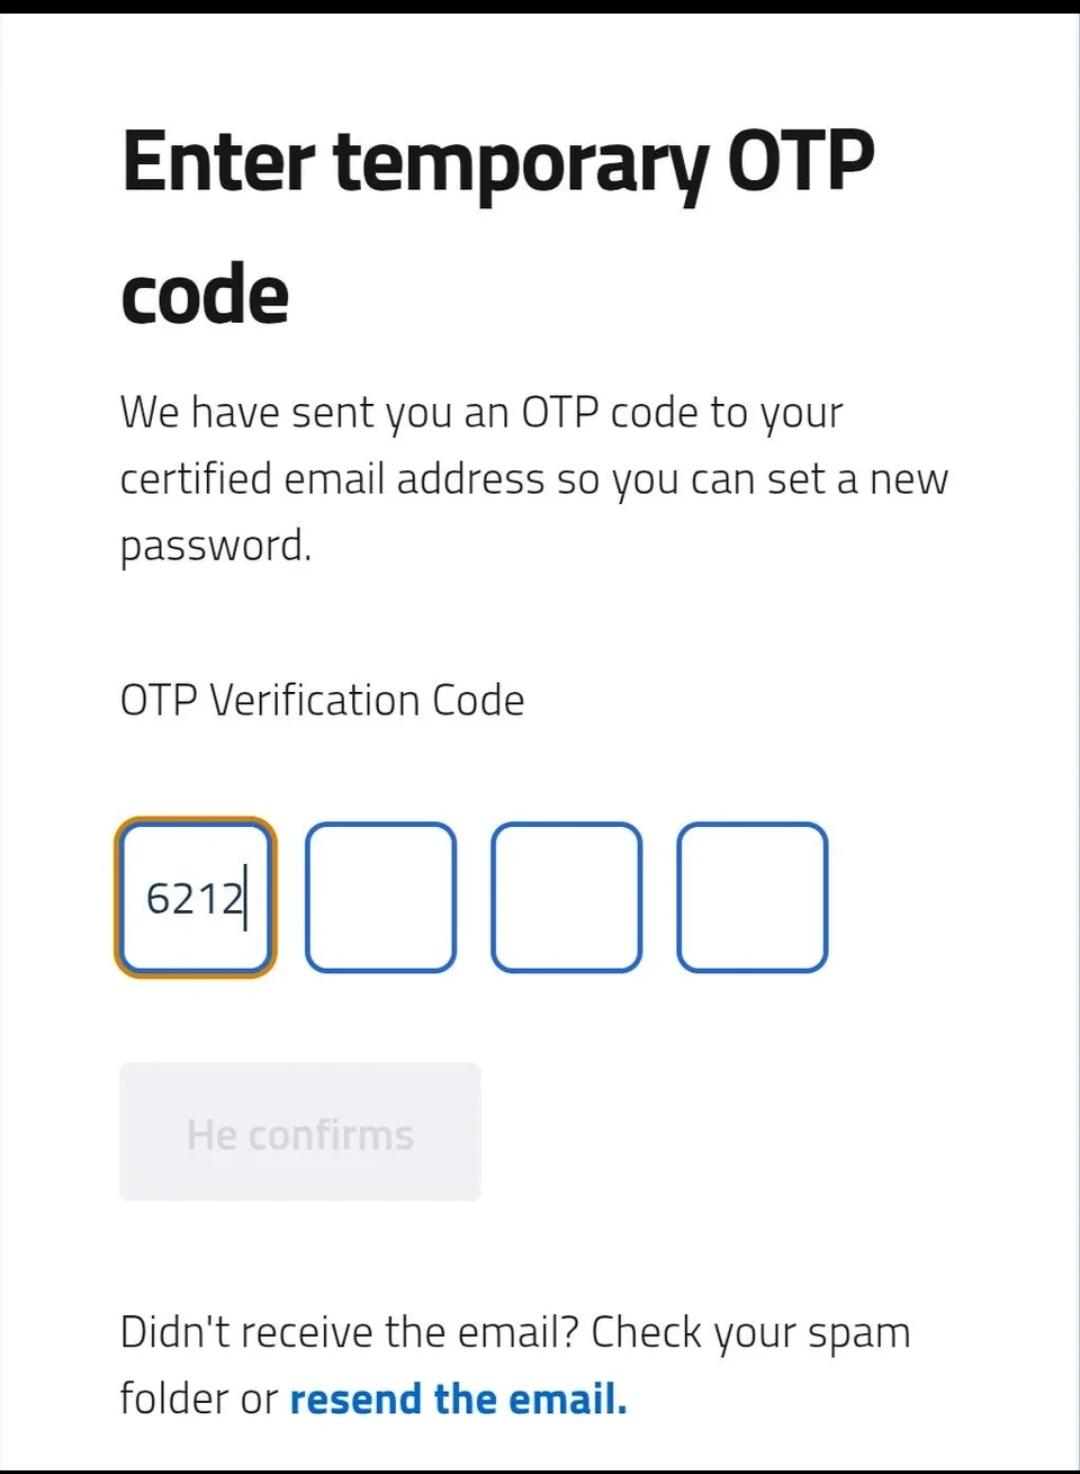
You know that feeling when you're implementing a "temporary" OTP system and you just hardcode "6212" into the first input field? That's vibe coding, baby. No validation logic, no actual email sending, just pure faith that the user will somehow know the code is 6212. The button even says "He confirms" like it's some divine proclamation. The best part? There's a link to "resend the email" that definitely doesn't exist. It's like putting a "Pull in case of emergency" sign on a painted door. This is what happens when you ship the UI mockup directly to production because "we'll add the backend later." Spoiler: later never comes, and now your entire auth system is held together by vibes and a single hardcoded number.

Map AI Auto Complete To OTP Auto Complete

Map AI Auto Complete To OTP Auto Complete
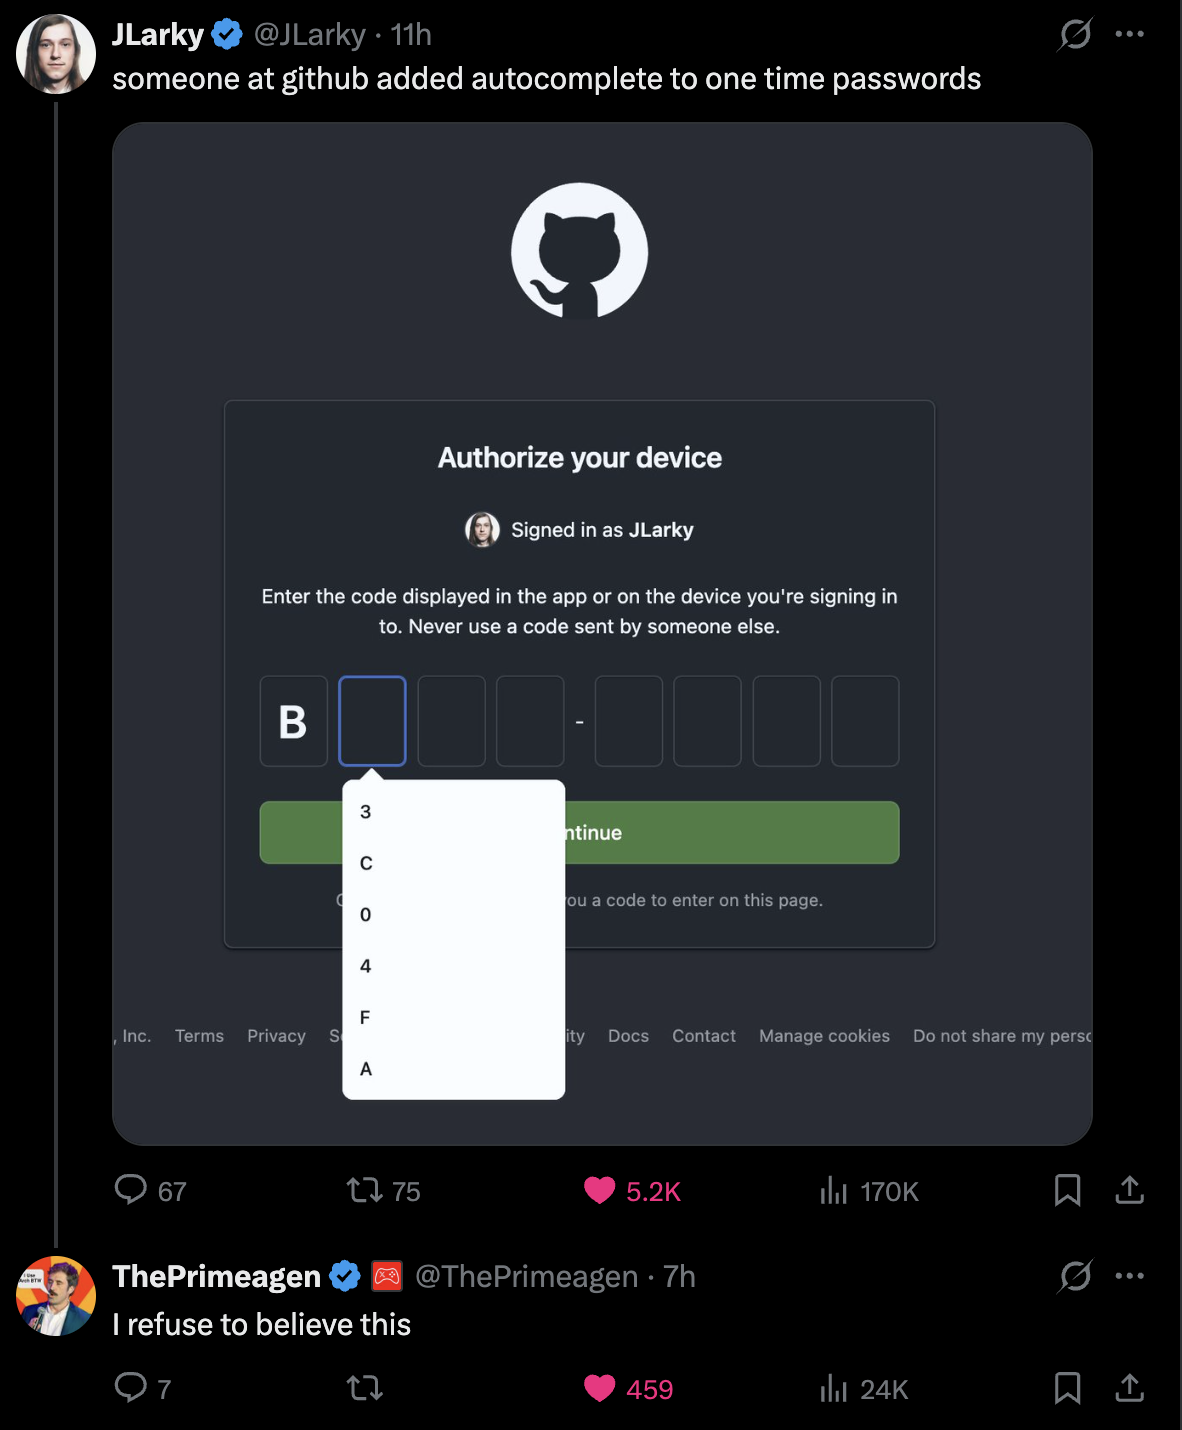
GitHub just implemented autocomplete for one-time passwords. You know, those temporary codes that are supposed to be, uh, one-time and temporary . The ones you're not supposed to save anywhere. The ones that expire in 30 seconds. Someone looked at the OTP field and thought "you know what would make this more convenient? If we just suggested what to type here." The autocomplete dropdown is showing "3C04FA" - which is either a previously used OTP that got cached (defeating the entire purpose of OTPs) or some truly galaxy-brain feature implementation. It's like adding a "remember me" checkbox to a self-destructing message. The security team is probably having a great day.

Front End OTP Verification

Front End OTP Verification
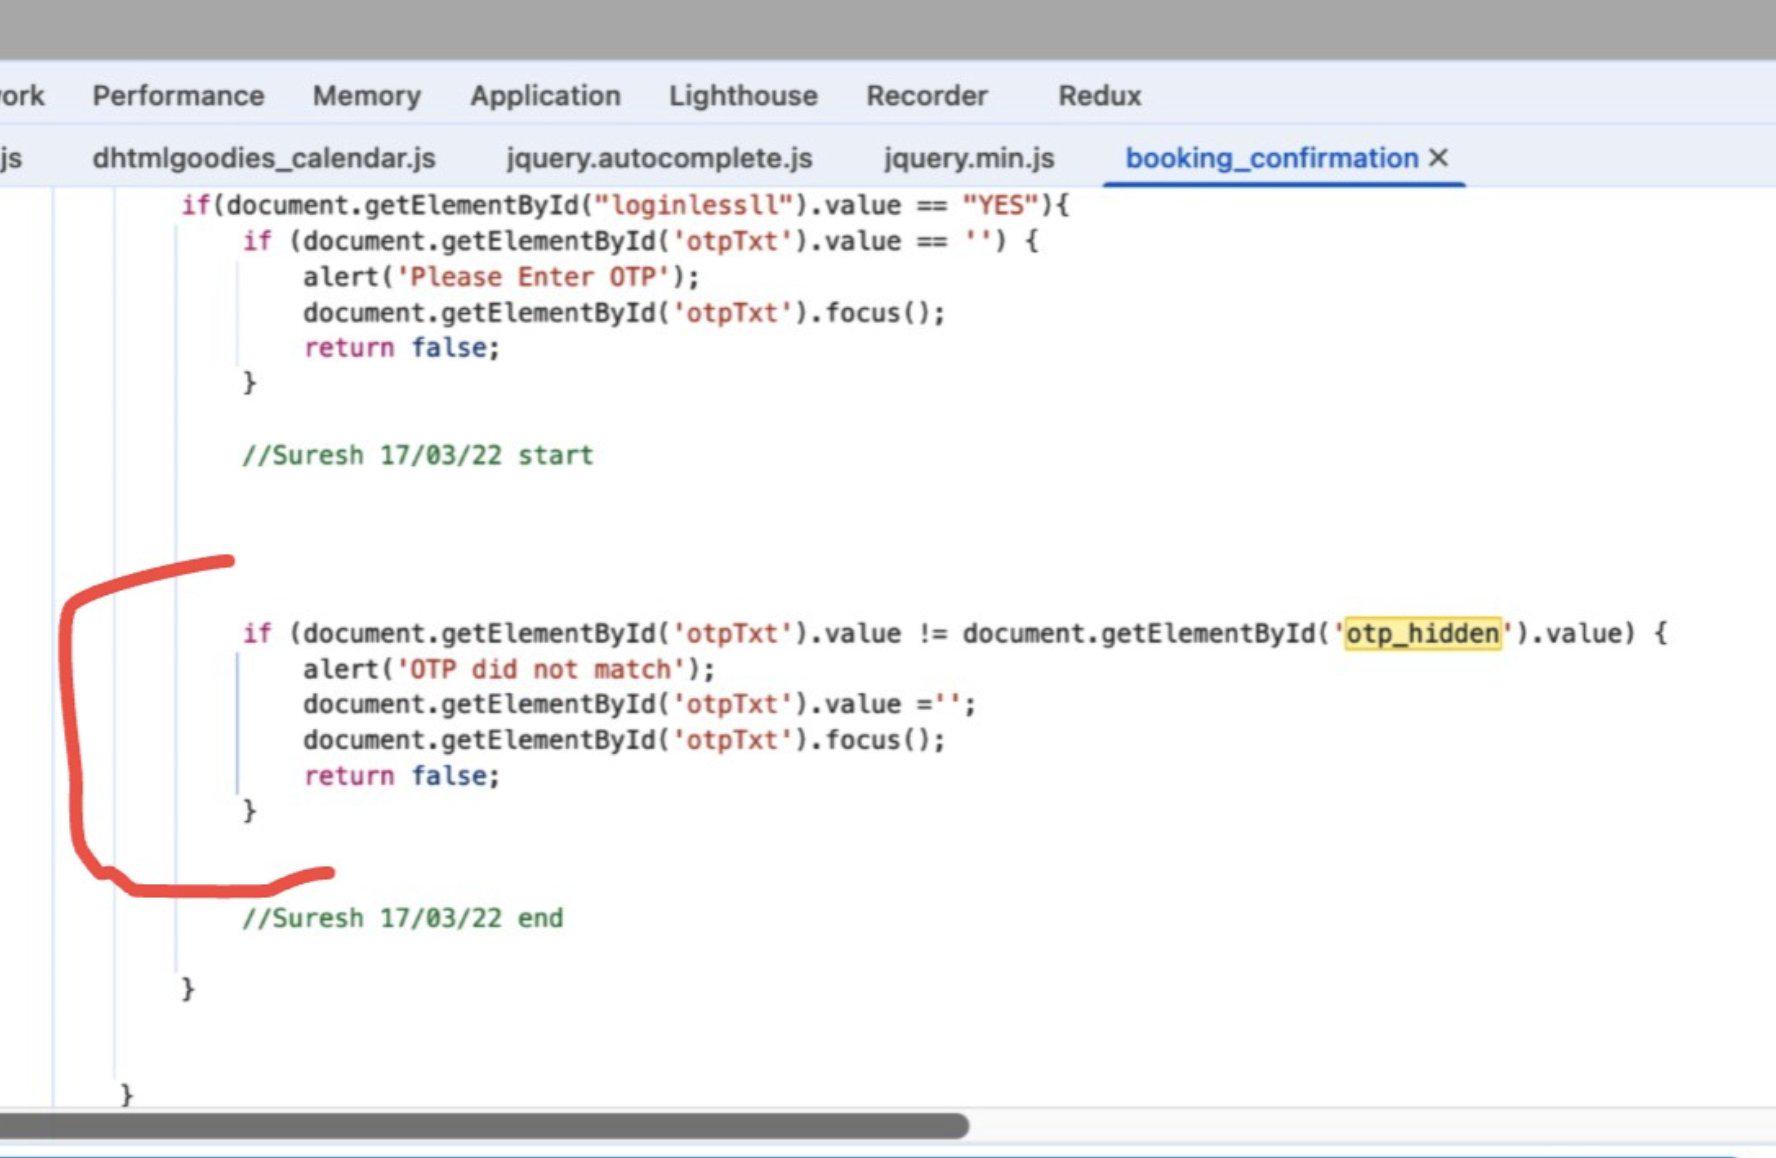
Someone named Suresh just committed a cardinal sin of web security. They're comparing the user's OTP input against a hidden field called otp_hidden ... which exists in the DOM... on the client side... where literally anyone can just open DevTools and read it. It's like putting a lock on your door but leaving the key taped to the doorknob with a sticky note that says "SECRET KEY - DO NOT USE". The entire point of OTP verification is that it should be validated server-side against what was actually sent to the user's phone/email. Storing it in a hidden input field defeats the purpose harder than using var in 2024. The red circle highlighting this masterpiece is chef's kiss. This is the kind of code that makes security researchers weep and penetration testers rub their hands together gleefully. Never trust the client, folks.

How Random Is This

How Random Is This
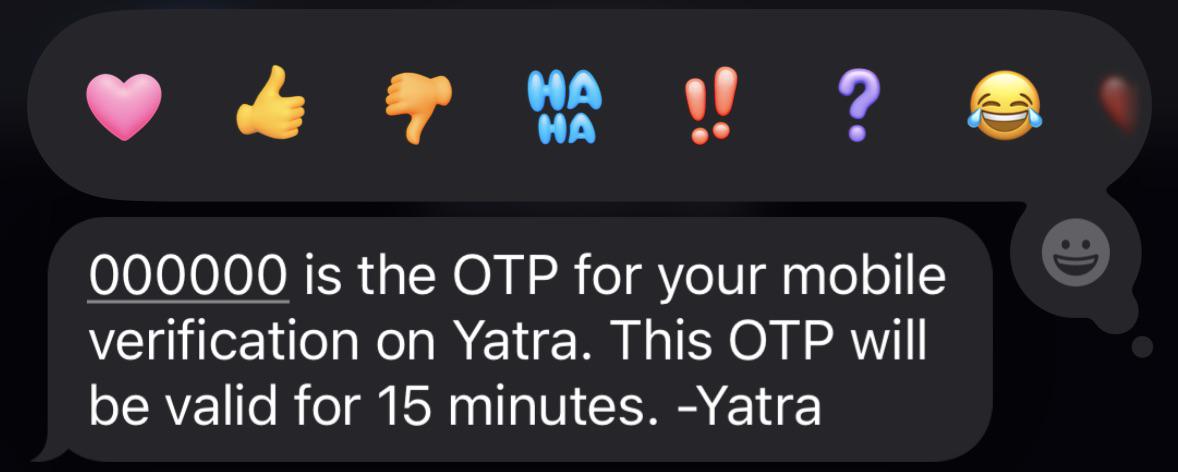
When your random number generator is feeling extra lazy! 😂 The OTP "000000" is like that one student who writes "AAAAAA" on a multiple-choice test hoping for a 20% success rate. Security experts are having heart attacks right now! This is basically the equivalent of setting your password to "password" and then wondering why someone hacked your account. Random number generators had ONE job... and this one decided to take a coffee break! ☕

NordVPN

NordVPN
Encrypt your traffic on public Wi-Fi, stream from anywhere, and cover up to ten devices with one plan. 30-day money-back guarantee.