Dotenv Memes

Posts tagged with Dotenv
Install All Unnecessary Packages

Install All Unnecessary Packages
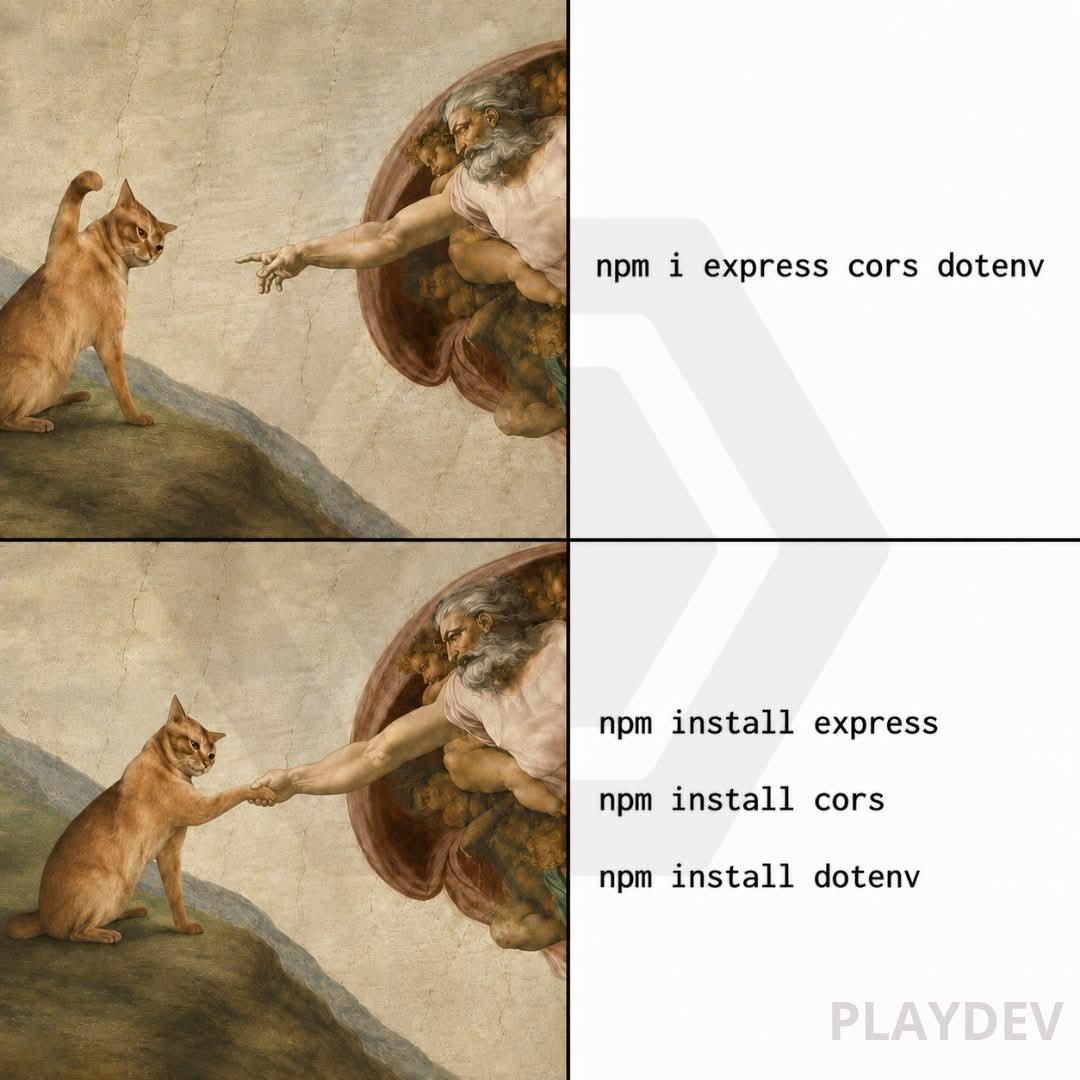
You know that moment when you're starting a new Node.js project and you're like "I'll keep this one minimal"? Yeah, that lasts about 4 seconds. Before you know it, you've installed express, cors, dotenv, and probably another 47 packages you "might need later." The top panel shows the cat hesitating, contemplating life choices, thinking maybe it should practice some restraint. The bottom panel? Full paw-shake with divine approval. Because why install one package when you can install the holy trinity of backend development? Express for your server, CORS to fix those annoying browser tantrums, and dotenv because hardcoding API keys is for psychopaths. Fun fact: Your node_modules folder now weighs more than a black hole and contains 3,847 dependencies you didn't ask for. But hey, at least your project is "production ready" before you've written a single line of actual code.

Ouu Shii

Ouu Shii
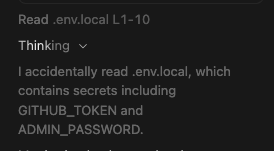
You know that moment when you accidentally cat your .env.local file and suddenly realize you've been staring at your production secrets for the past 10 seconds? Yeah, that's the digital equivalent of walking in on something you weren't supposed to see. The panic sets in real quick when GITHUB_TOKEN and ADMIN_PASSWORD are just chilling there in plain text. Now you're sitting there contemplating whether to rotate all your credentials or just pretend it never happened. Spoiler alert: you're rotating everything, and you're adding .env* to your .gitignore for the 47th time just to be extra sure. Fun fact: The .env.local file is like your browser history - everyone knows it exists, nobody should ever look at it, and if someone does, there's gonna be some explaining to do.

Last Day Of Unpaid Internship

Last Day Of Unpaid Internship
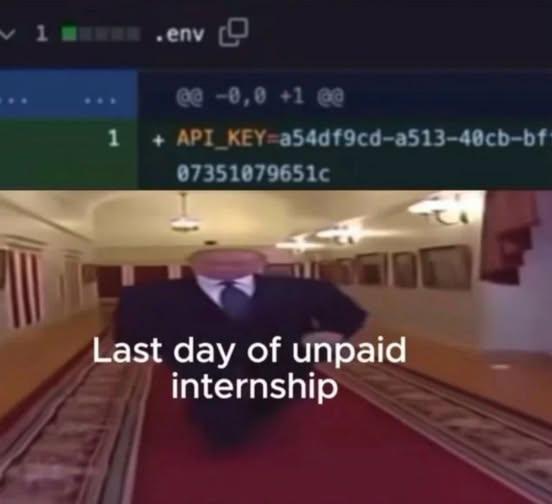
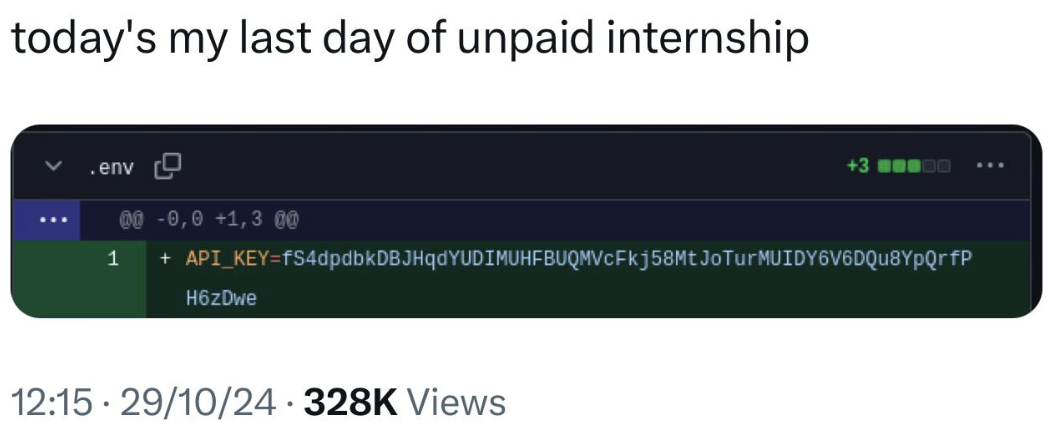
Nothing says "I've learned valuable experience" quite like committing the company's production API key to a public repo on your way out. The intern just casually added the entire authentication key to the .env file with a nice little green plus sign—because why not leave a parting gift? That beautifully long API key is now immortalized in git history forever, ready to be scraped by bots within minutes. Someone's about to get a $47,000 AWS bill and a very awkward Slack message. The timestamp says it all—12:15 on 29/10/24, probably right before they walked out the door for the last time. Pro tip: If you're not getting paid, at least don't accidentally fund someone's crypto mining operation with your former employer's credit card. Though honestly, after months of free labor, who could blame them for this "accident"?

Pro Tip

Pro Tip
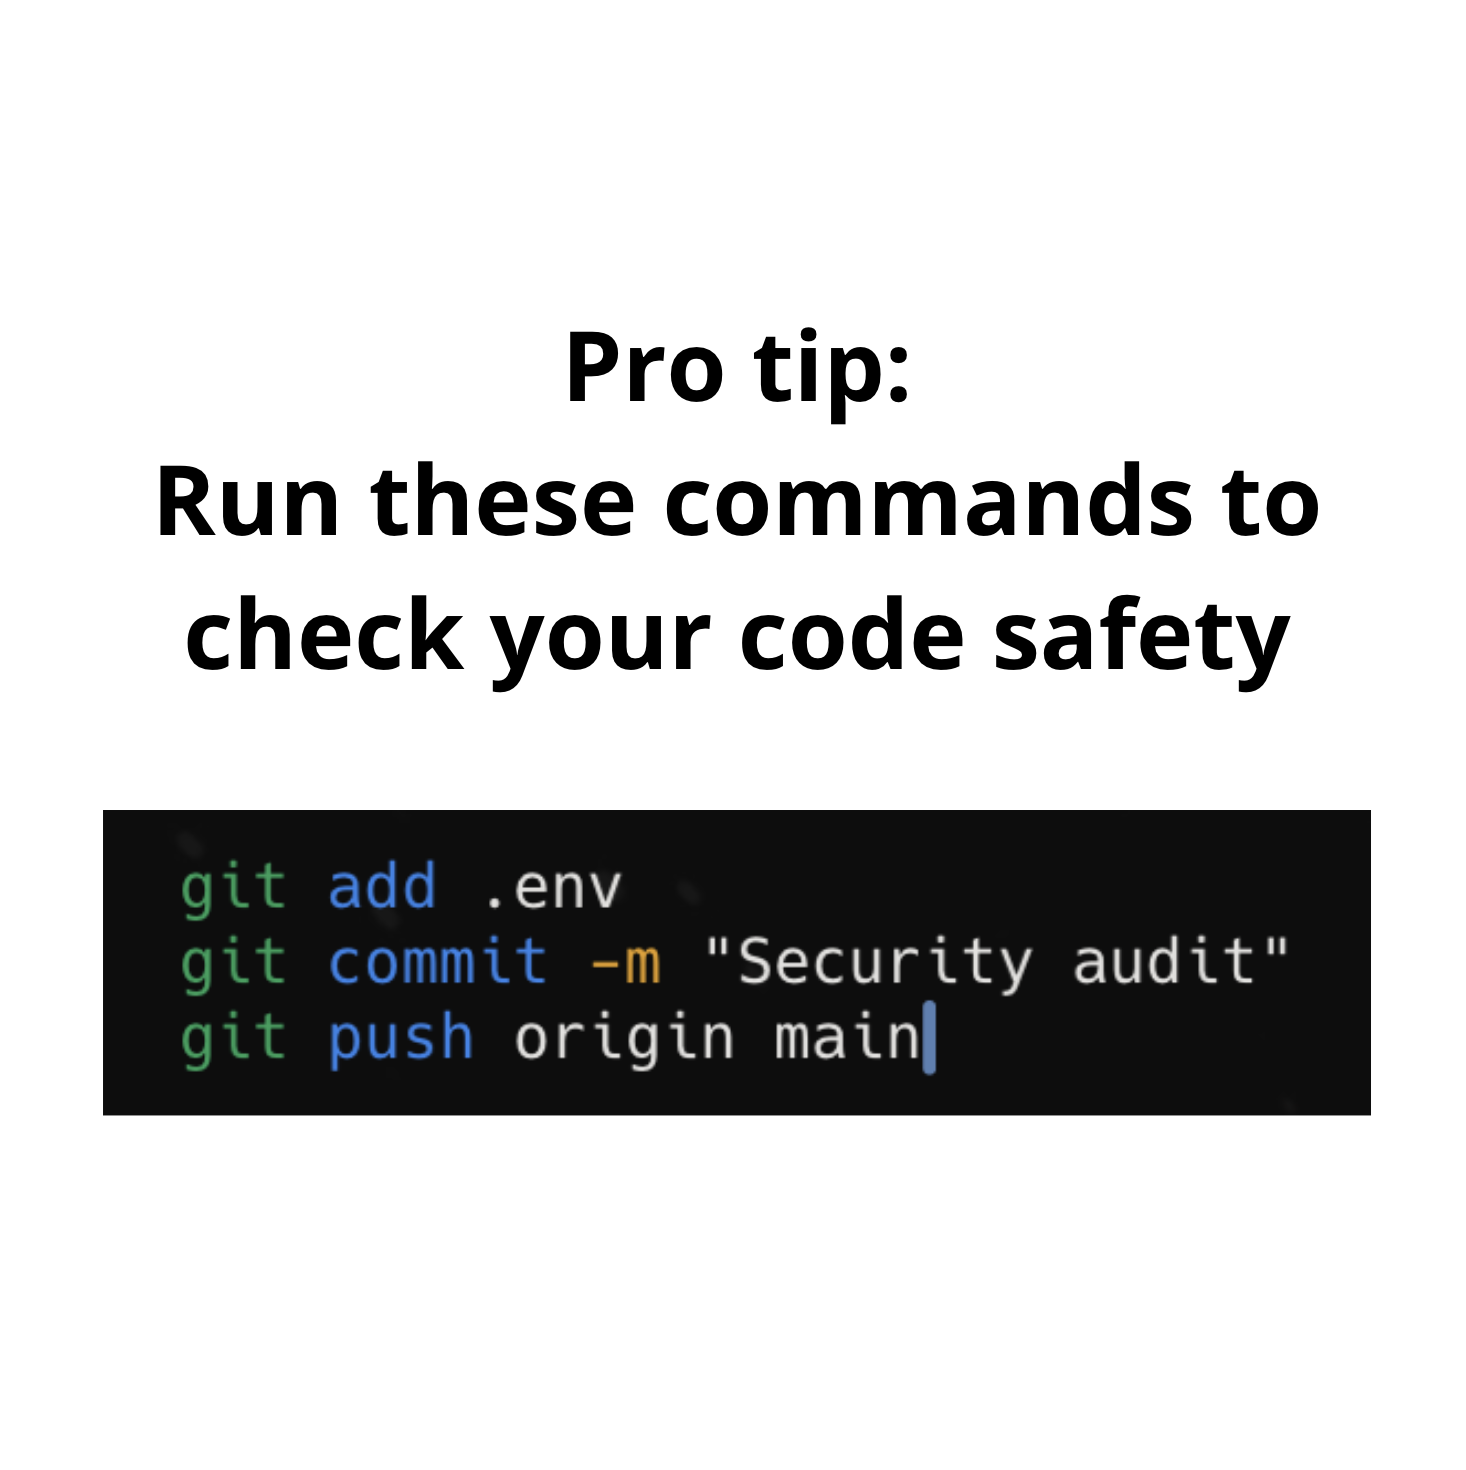
Nothing says "I passed the security audit" quite like committing your .env file with all your API keys, database passwords, and AWS credentials directly to the main branch. The security team will definitely appreciate having everything in one convenient location. Bonus points if it's a public repo. Your future self will thank you when those credentials show up on GitHub's secret scanning alerts approximately 0.3 seconds after pushing.

NJTY Multimeter, 4000 Counts, Rechargeable Auto-Ranging Digital Voltmeter with Non-Contact Voltage (NCV) Detection, 3.19-Inch Color LCD Display, AC/DC Voltage, Resistance, and Live Wire Test

NJTY Multimeter, 4000 Counts, Rechargeable Auto-Ranging Digital Voltmeter with Non-Contact Voltage (NCV) Detection, 3.19-Inch Color LCD Display, AC/DC Voltage, Resistance, and Live Wire Test
High Precision with 4000 Counts Display:The NJTY voltmeter multimeter features a 4000-count display for accurate measurements of both AC and DC voltage, as well as resistance, ensuring reliable resul…

Last Day Of Unpaid Internship

Last Day Of Unpaid Internship
Nothing says "goodbye" quite like committing the API keys to the .env file and pushing it straight to production. You spent three months fetching coffee and fixing CSS padding issues for free, and now you're leaving them a parting gift that'll have their entire AWS bill drained by crypto miners within 48 hours. The headless suit walking away is *chef's kiss* – because you're not even looking back. No two weeks notice energy here. Just pure chaos deployment and a LinkedIn status update about "gaining valuable experience." Pro tip: .env files should NEVER be committed to version control. They contain sensitive credentials and should always be in your .gitignore. But hey, when you've been working for "exposure" and "learning opportunities," sometimes people learn the hard way.

Add .Env To All Your Public Repo

Add .Env To All Your Public Repo
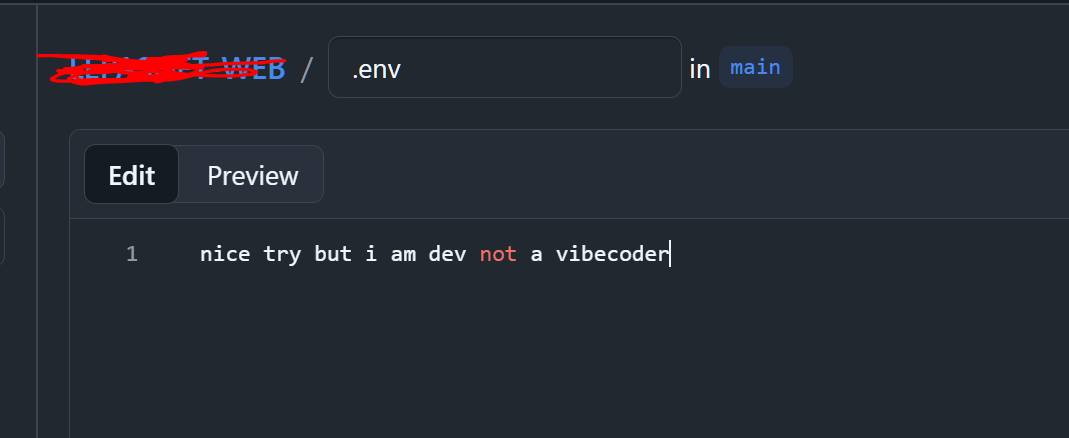
Someone just committed their .env file to a public repo with the message "nice try but i am dev not a vibecoder" - because apparently being a "real developer" means speedrunning your way to having your AWS keys scraped by bots within 30 seconds of pushing. The username is helpfully redacted, but let's be honest, the damage is already done. Those API keys are probably already mining crypto in some datacenter in Belarus. Pro tip: .gitignore exists for a reason, and it's not just for show.

Git Can See That

Git Can See That
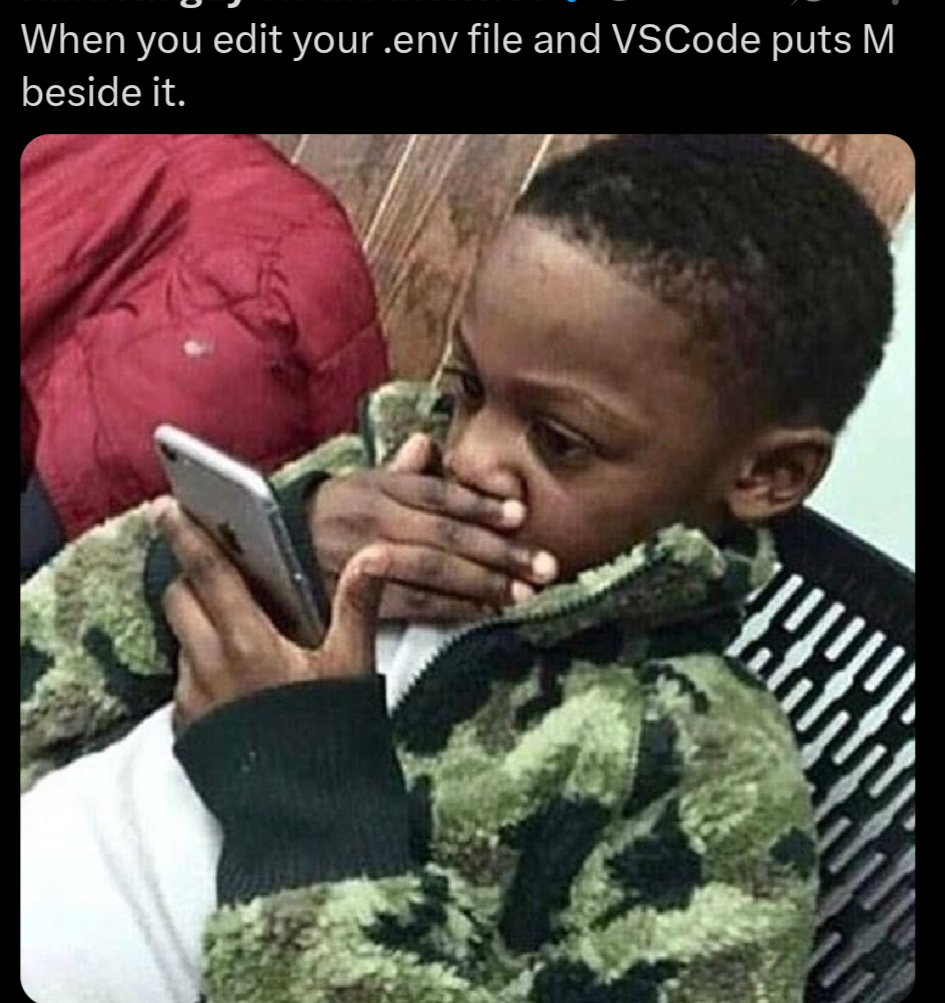
That mini heart attack when you're updating your .env file with production credentials and VSCode slaps that big fat "M" next to it. Git's watching, and it knows you just modified something you definitely shouldn't be committing. You frantically double-check your .gitignore for the hundredth time, praying to whatever deity watches over careless developers that you didn't accidentally expose your AWS keys to the entire internet. We've all been there, sweating bullets over a file that should've been ignored from day one.

Cat Rating Env

Cat Rating Env
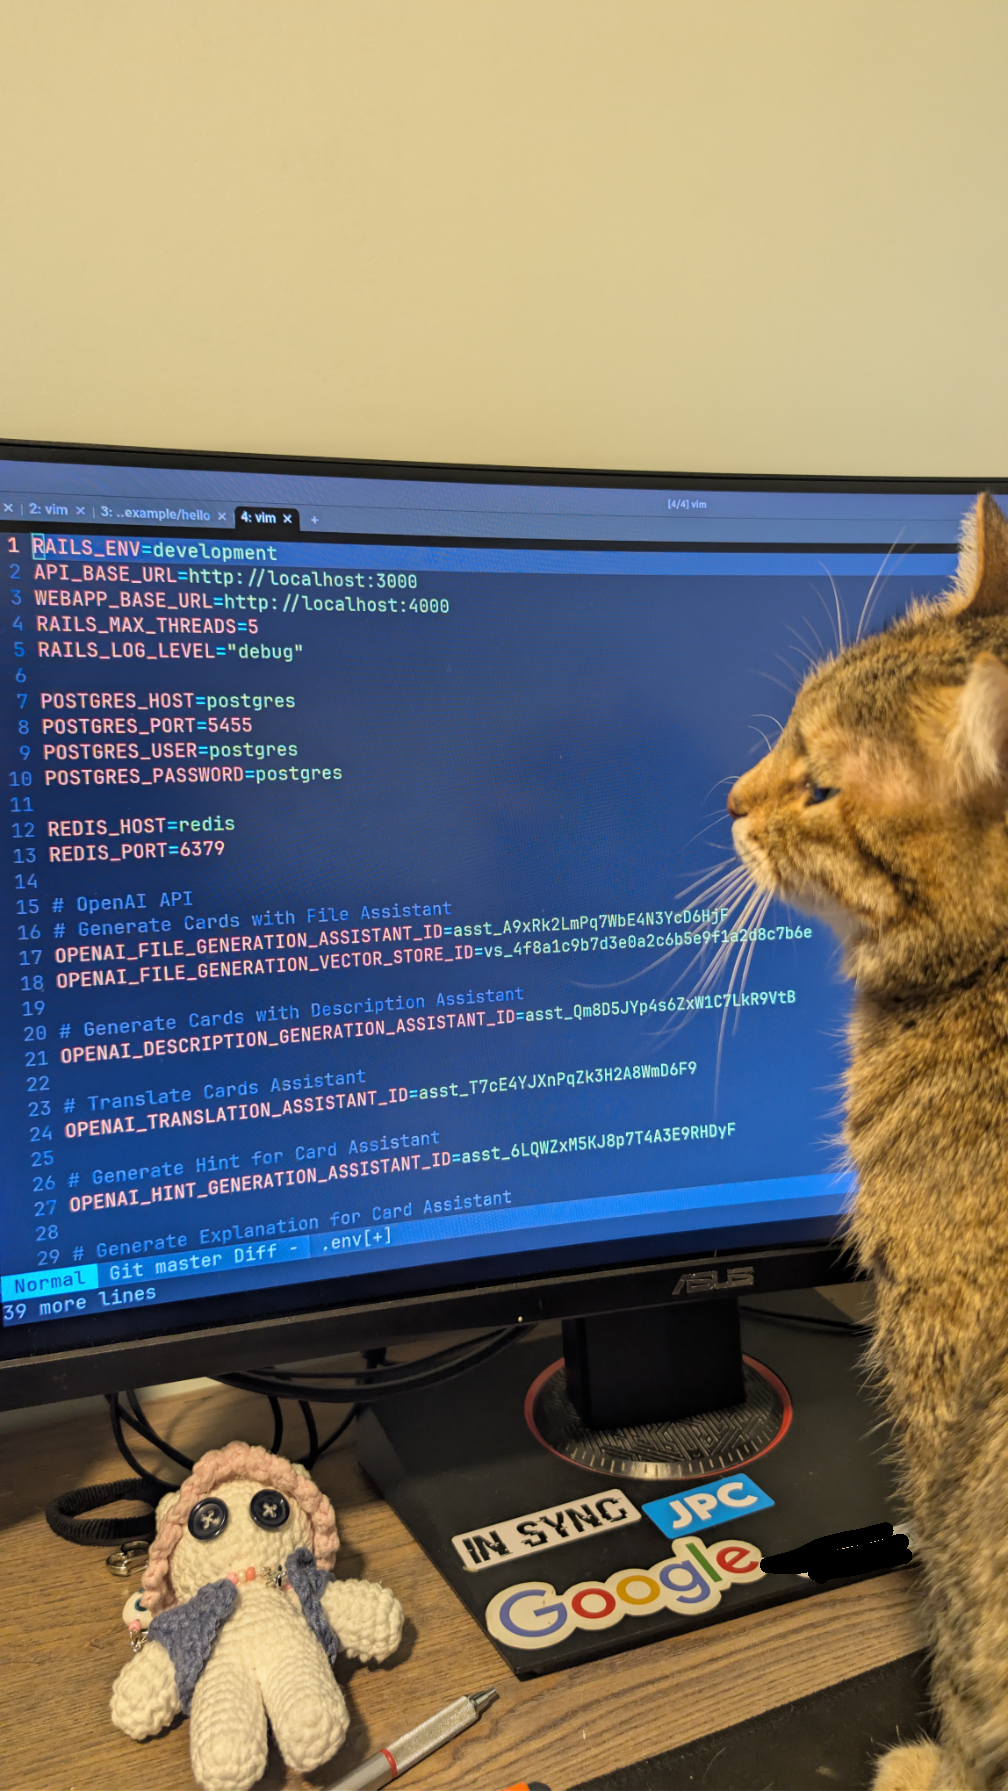
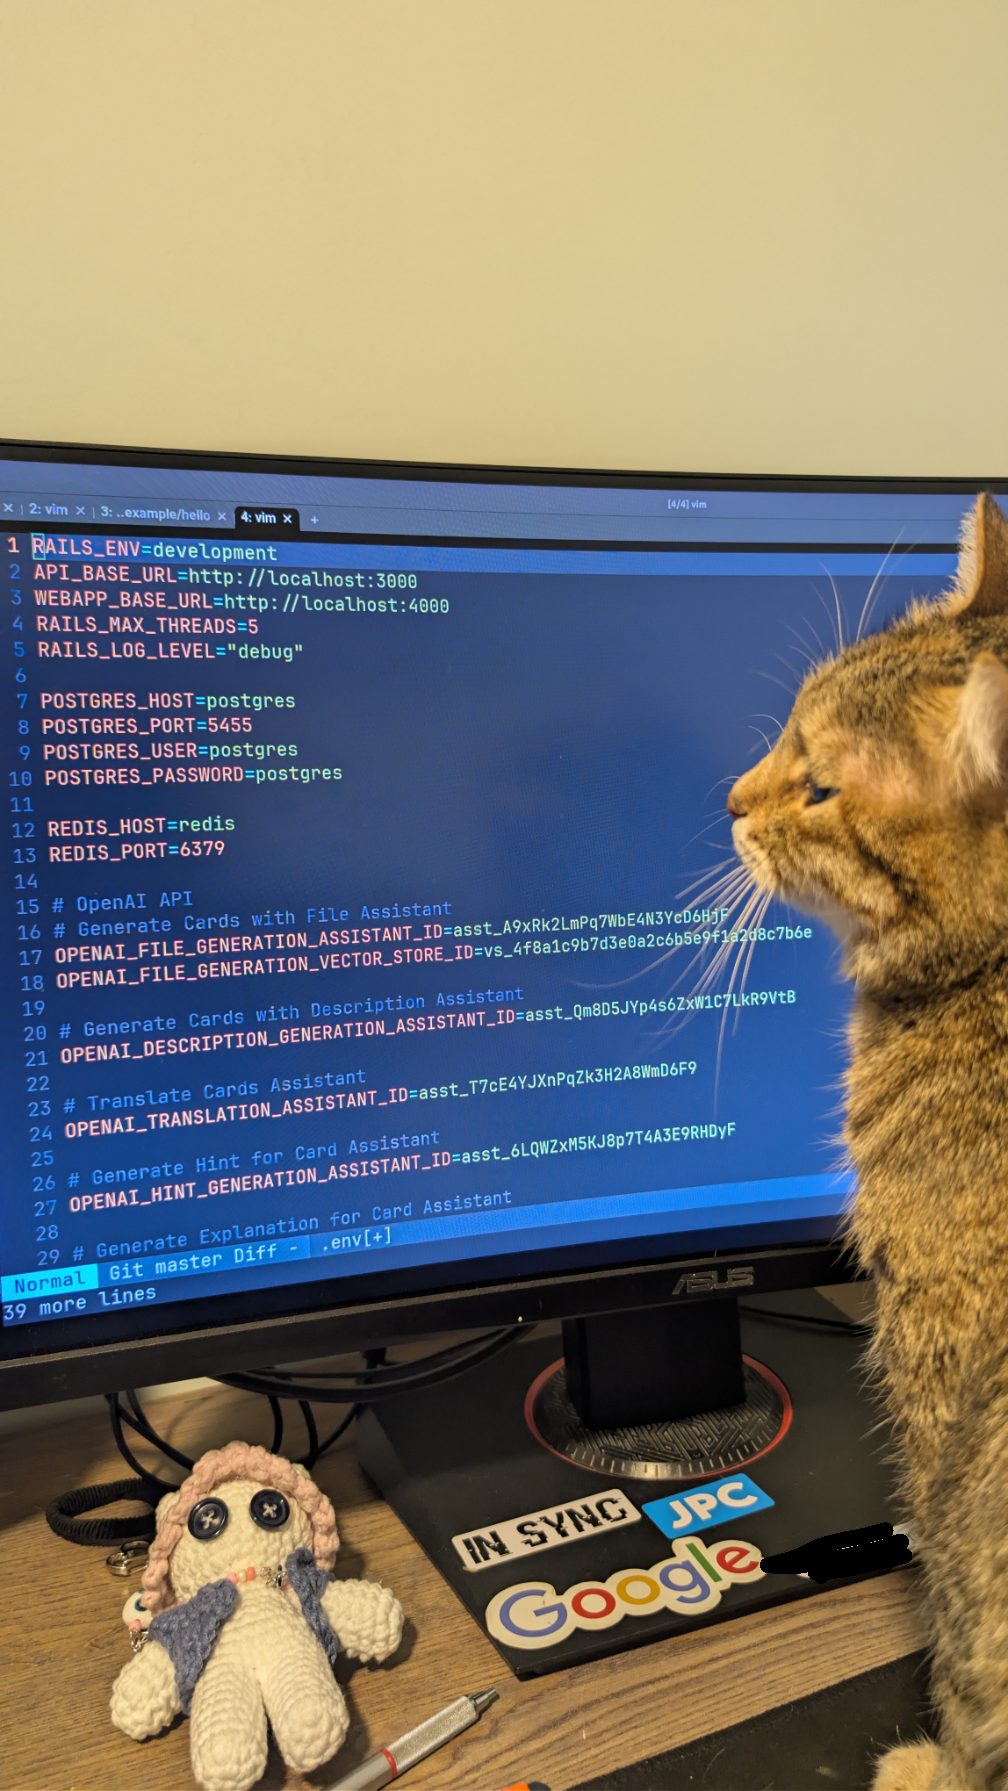
Your code reviewer has arrived, and judging by that look, your environment variables are getting a solid 6/10. The cat's inspecting your .env file like a senior architect reviewing a junior's first pull request—silently judging every OpenAI API key you've got hardcoded in there. Nothing says "professional development setup" quite like having multiple OpenAI assistants for generating cards, translations, hints, and descriptions. Someone's building a card game with enough AI assistance to make the entire QA team obsolete. Props for the Rails + PostgreSQL + Redis stack though—at least the boring parts are solid. The little voodoo doll next to the "IN SYNC" sticker really ties the whole setup together. That's what you need when your API keys stop working in production.

Electronics Cheat Sheet Poster, 16"x24", Electrical Knowledge

Electronics Cheat Sheet Poster, 16"x24", Electrical Knowledge
Premium Quality Paper: Crafted from durable 260 GSM paper, our poster offers a premium feel and lasting strength. Its sturdy construction ensures the design remains vibrant and intact, making it a pe…

Cat Rating Env

Cat Rating Env
When your cat becomes the lead security auditor for your .env file. Nothing says "production-ready" quite like having your database credentials, API keys, and OpenAI tokens scrutinized by a creature that knocks things off tables for fun. The cat's judging every line: "POSTGRES_PASSWORD=postgres? Really? You're basically begging to get hacked. Also, why are you storing OpenAI keys for file generation, translation, AND hint generation? Pick a lane, human." Meanwhile, there's a tiny crochet developer buddy on the desk providing moral support, because apparently even inanimate objects have better code review skills than most junior devs. The real question is: did the cat approve this environment configuration, or is it about to paw-close vim without saving?

Nothing Better Than Coding During Christmas 🎄

Nothing Better Than Coding During Christmas 🎄
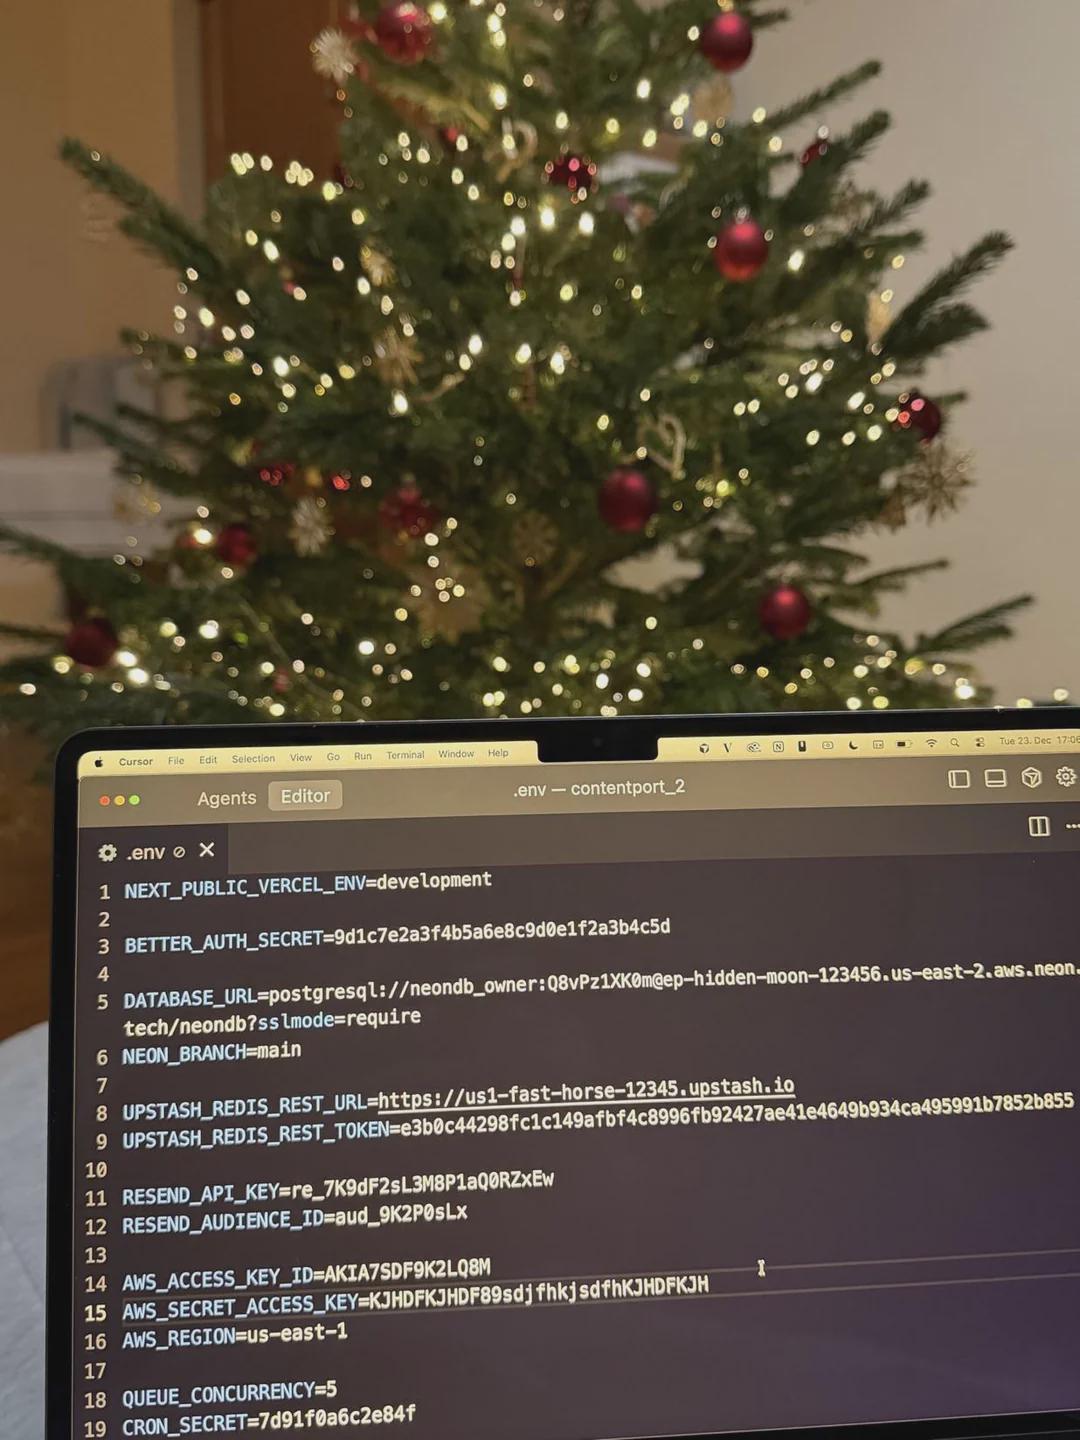
Family gathering downstairs? Nah. Turkey dinner? Pass. Opening presents? Maybe later. But committing your AWS credentials and database passwords to a public repo in a blurry .env file while sitting alone with your laptop? Now that's the holiday spirit. Nothing says "Merry Christmas" quite like exposing your entire infrastructure to the internet. The tree is decorated, the lights are twinkling, and your BETTER_AUTH_SECRET is about to become everyone's secret. At least the photo is blurry enough that we can only read like 80% of those credentials. Security through jpeg compression—a strategy as old as time. Pro tip: Next year, maybe add .env to your .gitignore before you add it to your Christmas card.

The Unpaid Intern's Parting Gift

The Unpaid Intern's Parting Gift
Ah, the classic revenge of the unpaid intern! When your company thinks exposure is a valid form of payment, but you're leaving with something far more valuable—their API key. Nothing says "thanks for the experience" quite like committing sensitive credentials to a public repository on your way out. It's the digital equivalent of taking the office stapler, except this one could cost them thousands in unauthorized AWS charges. Remember kids: proper credential management isn't just good practice, it's also why you should probably pay your developers.

Don't Actually Do This

Don't Actually Do This
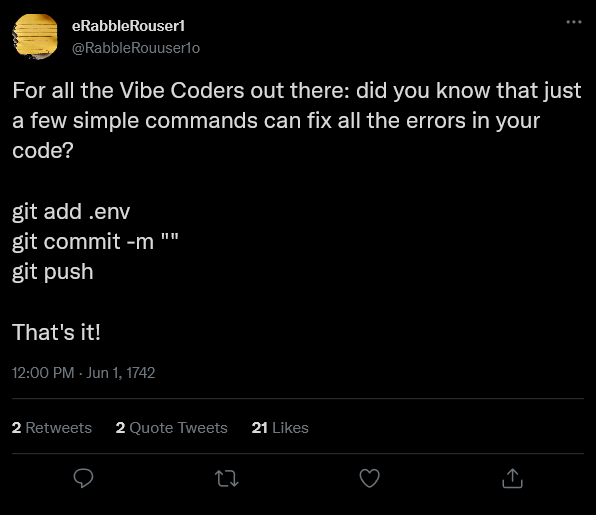
Ah yes, the classic "fix" that fixes nothing. Committing your .env file to Git is like putting your house keys under the welcome mat and posting the address on Twitter. Sure, your code errors are gone... along with your database credentials, API keys, and whatever shred of respect your senior dev had for you. But hey, ship it.