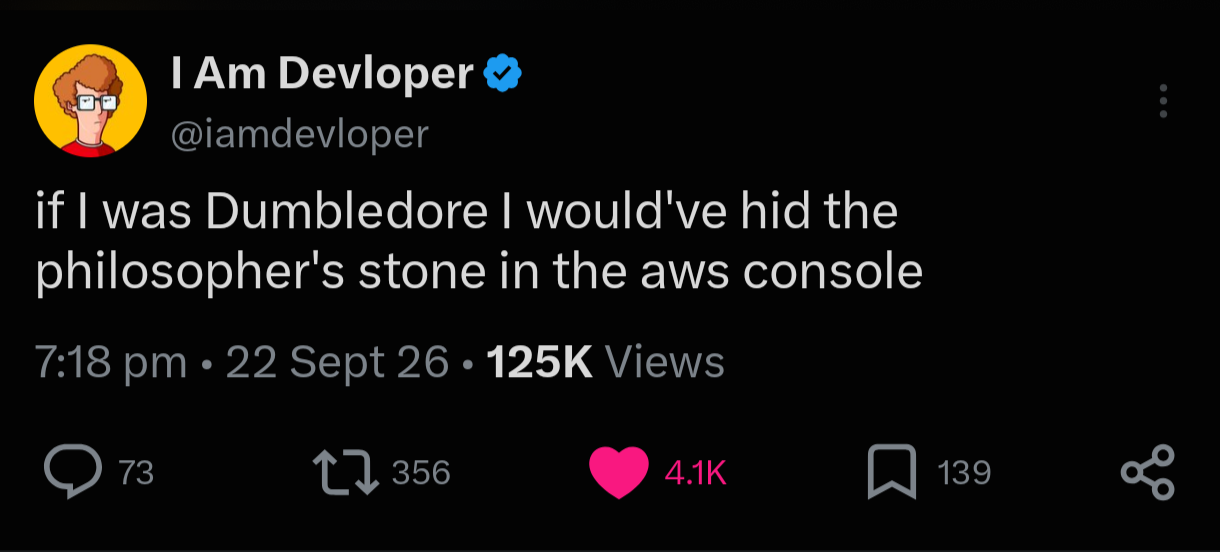
If Dumbledore had access to AWS IAM policies, Voldemort would've never stood a chance. Just slap a Deny * on everything and hide the Philosopher's Stone in an S3 bucket with 47 layers of resource-based policies, cross-account role assumptions, and permission boundaries that even the Dark Lord's best Legilimency couldn't penetrate. The username @iamdeveloper is chef's kiss here—because nothing says "I understand AWS Identity and Access Management" quite like literally being named IAM Developer. The real magic isn't wands and spells; it's figuring out why your Lambda function can't access that DynamoDB table even though you swear you gave it the right permissions three hours ago. Fun fact: AWS IAM policies are basically the horcruxes of cloud infrastructure—you create them thinking you're securing your soul (data), but end up with fragments scattered everywhere that you can't remember or control.
 AI
 AWS
 Agile
 Algorithms
 Android
 Apple
 Azure
 Backend
 Bash
 C++
 Cloud