Plaintext-passwords Memes

Posts tagged with Plaintext-passwords
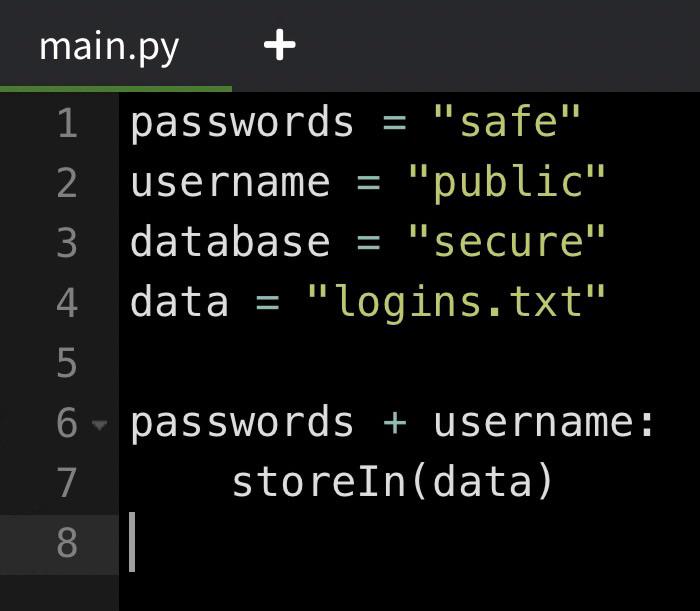
Backend Is Easy

Backend Is Easy
When someone says backend development is just "storing data in databases," they're technically correct in the same way a house fire is just "rapid oxidation." Here we have a masterclass in security anti-patterns: hardcoded credentials that would make any pentester weep with joy, a database connection string called "secure" (narrator: it wasn't), and the pièce de résistance—storing login credentials in a plaintext file called logins.txt. Because nothing says "enterprise-grade security" like concatenating passwords and usernames before yeeting them into a text file. The variable names are doing more heavy lifting than the actual security here. At least they're being honest with that "safe" password assignment.

Vibecoding Side Effects

Vibecoding Side Effects
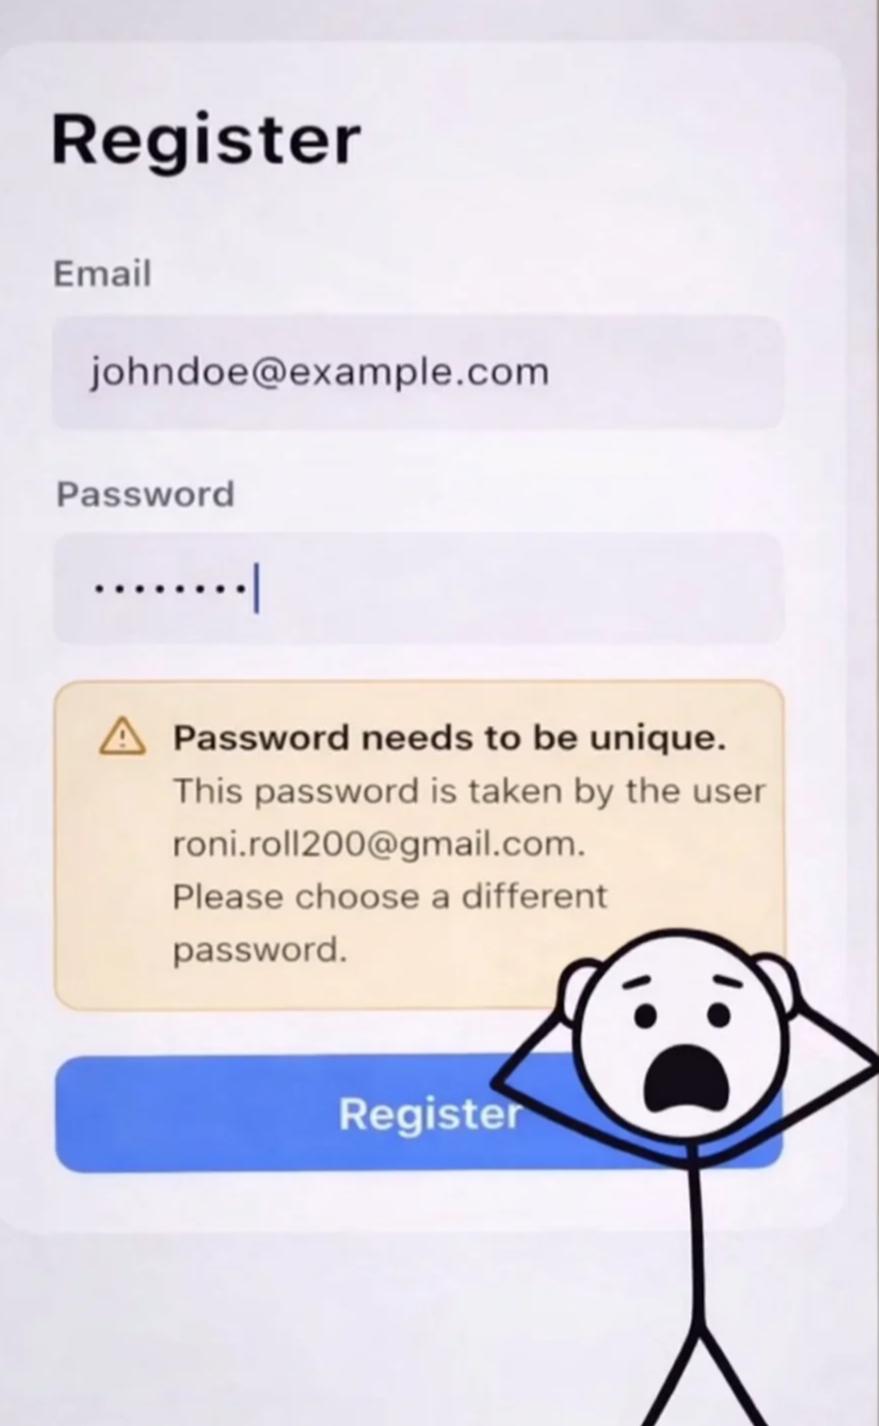
You know you've entered the danger zone when you're vibing so hard that you accidentally store passwords in plaintext AND make them globally unique across all users. The error message is basically tattling on poor [email protected], exposing their password to everyone who tries to register. This is what happens when you skip the "hash your passwords" lecture and go straight to "let's just see if it works." Somewhere, a security engineer just felt a disturbance in the force. This registration form is basically a GDPR violation speedrun. Not only are passwords stored in a way that allows collision detection, but they're also casually revealing other users' email addresses in error messages. It's like a two-for-one special on security nightmares.

This Is So Bad That It's So Good

This Is So Bad That It's So Good
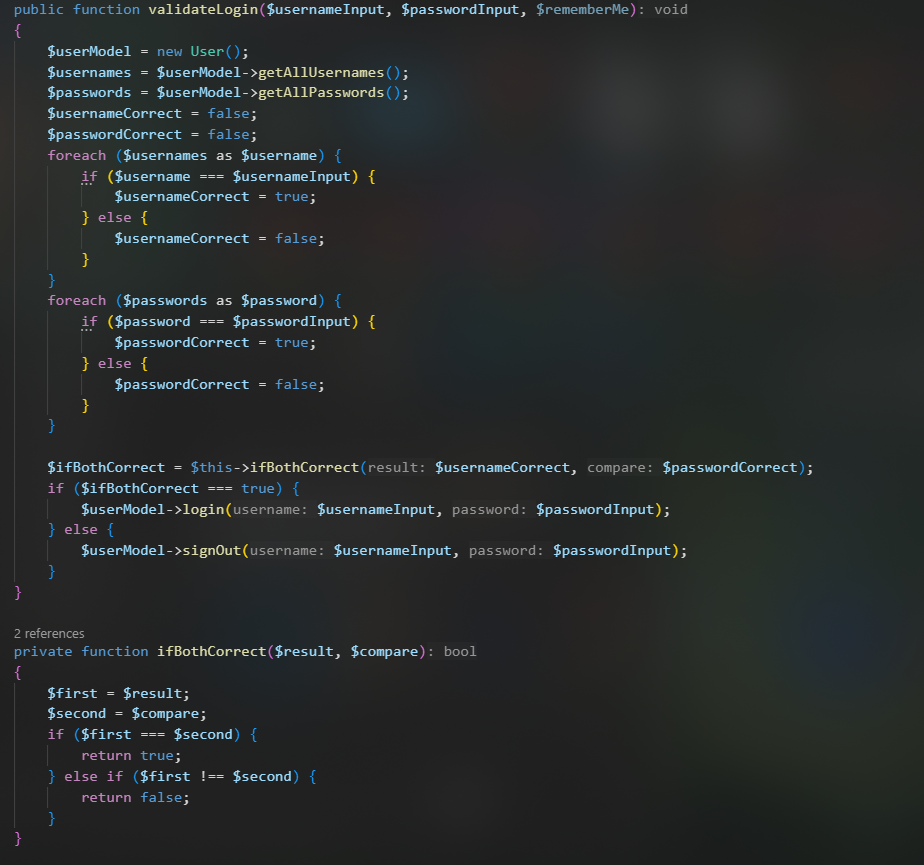
Someone just reinvented the equality operator with extra steps. The ifBothCorrect function literally just checks if two values are equal, but instead of using === or == , they wrote an entire function that assigns them to variables, compares them, and returns true or false. It's like using a forklift to pick up a pencil. But wait, there's more! The authentication logic fetches ALL usernames and ALL passwords from the database, then loops through them in nested foreach loops to validate credentials. That's O(n²) complexity for what should be a single database query. Your database is crying. Your security team is crying. I'm crying. The cherry on top? They're storing passwords in plain text (look at that getAllPasswords() call). This code is a security audit's final boss. It's so beautifully terrible that it almost feels like performance art.

Starboy 98

Starboy 98
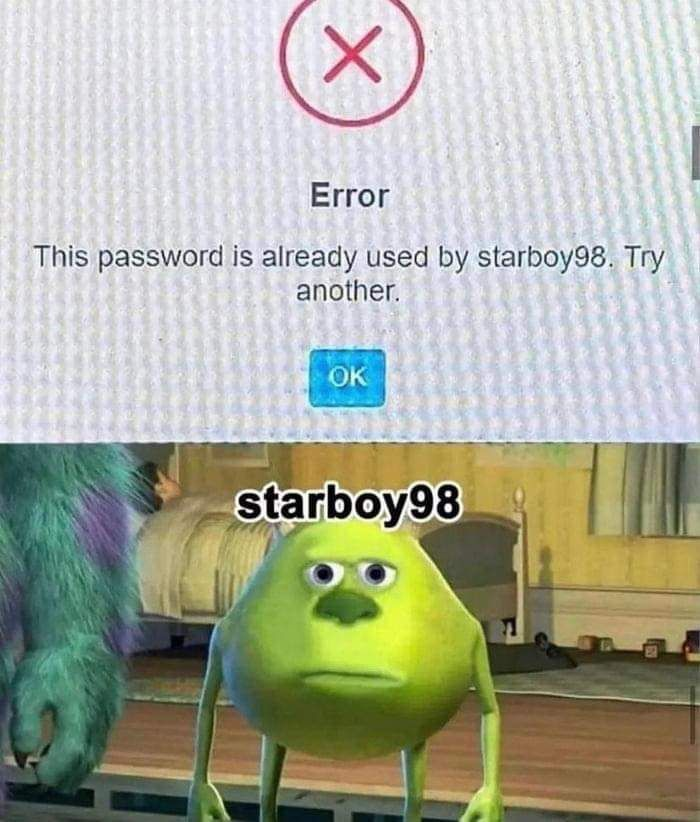
Plot twist: you're trying to create a new account and the system just casually exposes that someone else is already using your go-to password. Congrats on the world's worst security implementation—instead of saying "username taken," they're out here revealing password collisions like it's no big deal. Starboy98 is having an existential crisis because either: (a) someone stole their signature password, (b) they forgot they already made an account, or (c) they just discovered their "unique" password is about as original as using "password123." The Mike Wazowski face really captures that moment when you realize your password game is weak and the database architect's security game is even weaker. Pro tip: If a website can tell you your password is already in use by another user, run. That means they're storing passwords in plaintext or comparing them before hashing. Yikes.

SSK NVMe SATA SSD Enclosure, Tool-Free M.2 to USB Adapter USB C 3.2 Gen 2 10Gbps NVMe 6Gbps SATA M-Key / B+M Key External SSD Reader with UASP Trim, for 2230 2242 2260 2280 SSDs

SSK NVMe SATA SSD Enclosure, Tool-Free M.2 to USB Adapter USB C 3.2 Gen 2 10Gbps NVMe 6Gbps SATA M-Key / B+M Key External SSD Reader with UASP Trim, for 2230 2242 2260 2280 SSDs
Compatible SSD: This M.2 SSD Enclosure supports both NVMe PCIe and SATA protocol SSDs with M-Key or B+M Key connectors. It is compatible with SSD length 2280, 2260, 2242, 2230 enclosure · 10Gbps Blaz…